CybersecuritySOC 2ISO 27001


SOC 2 and ISO 27001 can lower cyber insurance premiums, and the effect shows up in three ways: a lower premium, better terms (lower retentions, fewer ...
Canadian cyber insurers expect five controls before they quote: multi-factor authentication (MFA) on remote access and email, tested backups,...
A vulnerability management policy is the document that sets how an organization finds, rates and fixes vulnerabilities, and how long each severity...
An incident response policy is the set of management-approved rules for security incidents: who must report a suspected incident, how severity is...
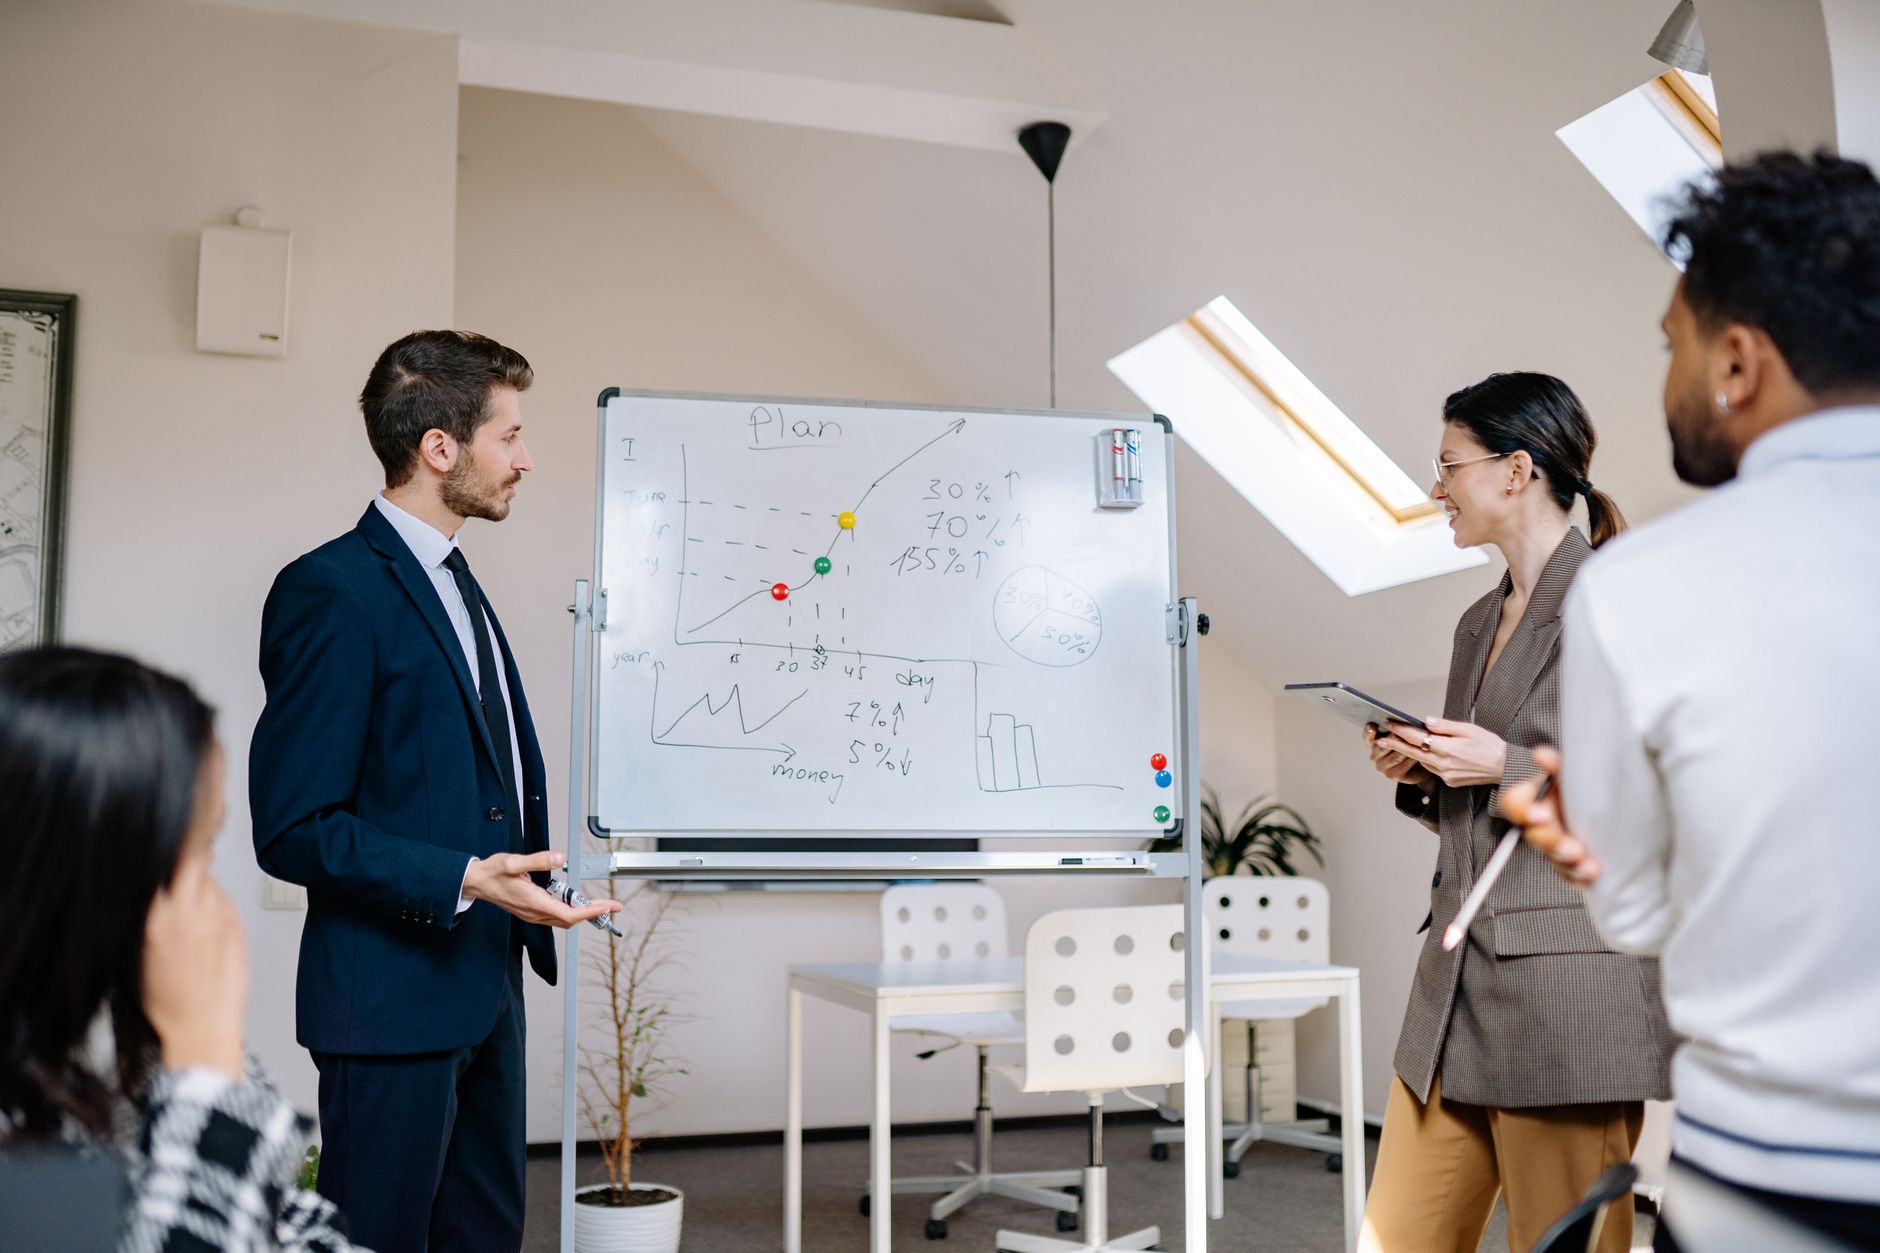
An incident response plan is the document a company follows from the moment a security event is reported until the incident is closed and reviewed....
The Google Cloud IAM gaps that show up most often in baseline reviews come from Google's own defaults. Organizations created before May 2024 never...
SOC 2 CC7 on Google Cloud covers monitoring, incident response and recovery, and Google handles each of these for Google infrastructure under...
Risk-based vulnerability management is the practice of ranking scanner findings by the risk each one carries in a specific environment (exposure,...
Security Command Center (SCC) is Google Cloud's built-in security and risk dashboard, and the Standard tier is free. Premium adds threat detection,...
Google Cloud ships a set of security services that cost nothing or a few dollars a month, and many of them are switched off by default. The best GCP...
SOC 2 CC6 responsibility on Google Cloud depends on the service model. Google's SOC 2 report covers physical access (CC6.4) and storage media...
An AI agent threat model is a written record of what the agent can access, how that access could be misused, and which control limits each case. The...
PHIPA, Ontario's Personal Health Information Protection Act, 2004, is the provincial law that governs how health information custodians, such as...
RPAA compliance means a payment service provider (PSP) in scope of the Retail Payment Activities Act registers with the Bank of Canada, operates a...
OSFI Guideline B-10 (Third-Party Risk Management) sets the rules Canadian banks, insurers, and trust and loan companies follow when they assess,...
OSFI B-13 is the Office of the Superintendent of Financial Institutions' Technology and Cyber Risk Management guideline. B-13 has been in effect...
A vCISO service in Canada is fractional security leadership that owns the security program and also covers the Canadian obligations a US-focused...
HIPAA is a US law that reaches a Canadian company the moment that company creates, receives, maintains, or transmits protected health information...
PIPEDA (the Personal Information Protection and Electronic Documents Act) is Canada's federal privacy law for private-sector organizations that...
ISO 27001 certification in Canada is issued by an accredited certification body, a separate firm from the consultant who helps build the program. A...
The main security considerations for MCP servers and agent skills are supply-chain risks: both deliver instructions and code that an AI agent trusts...
AI agents and identity security meet at one rule: give every AI agent its own identity, manage the agent as an insider with privileged access, and...
Prompt injection is an attack in which someone writes text that a large language model (LLM) treats as instructions, so the model follows the...
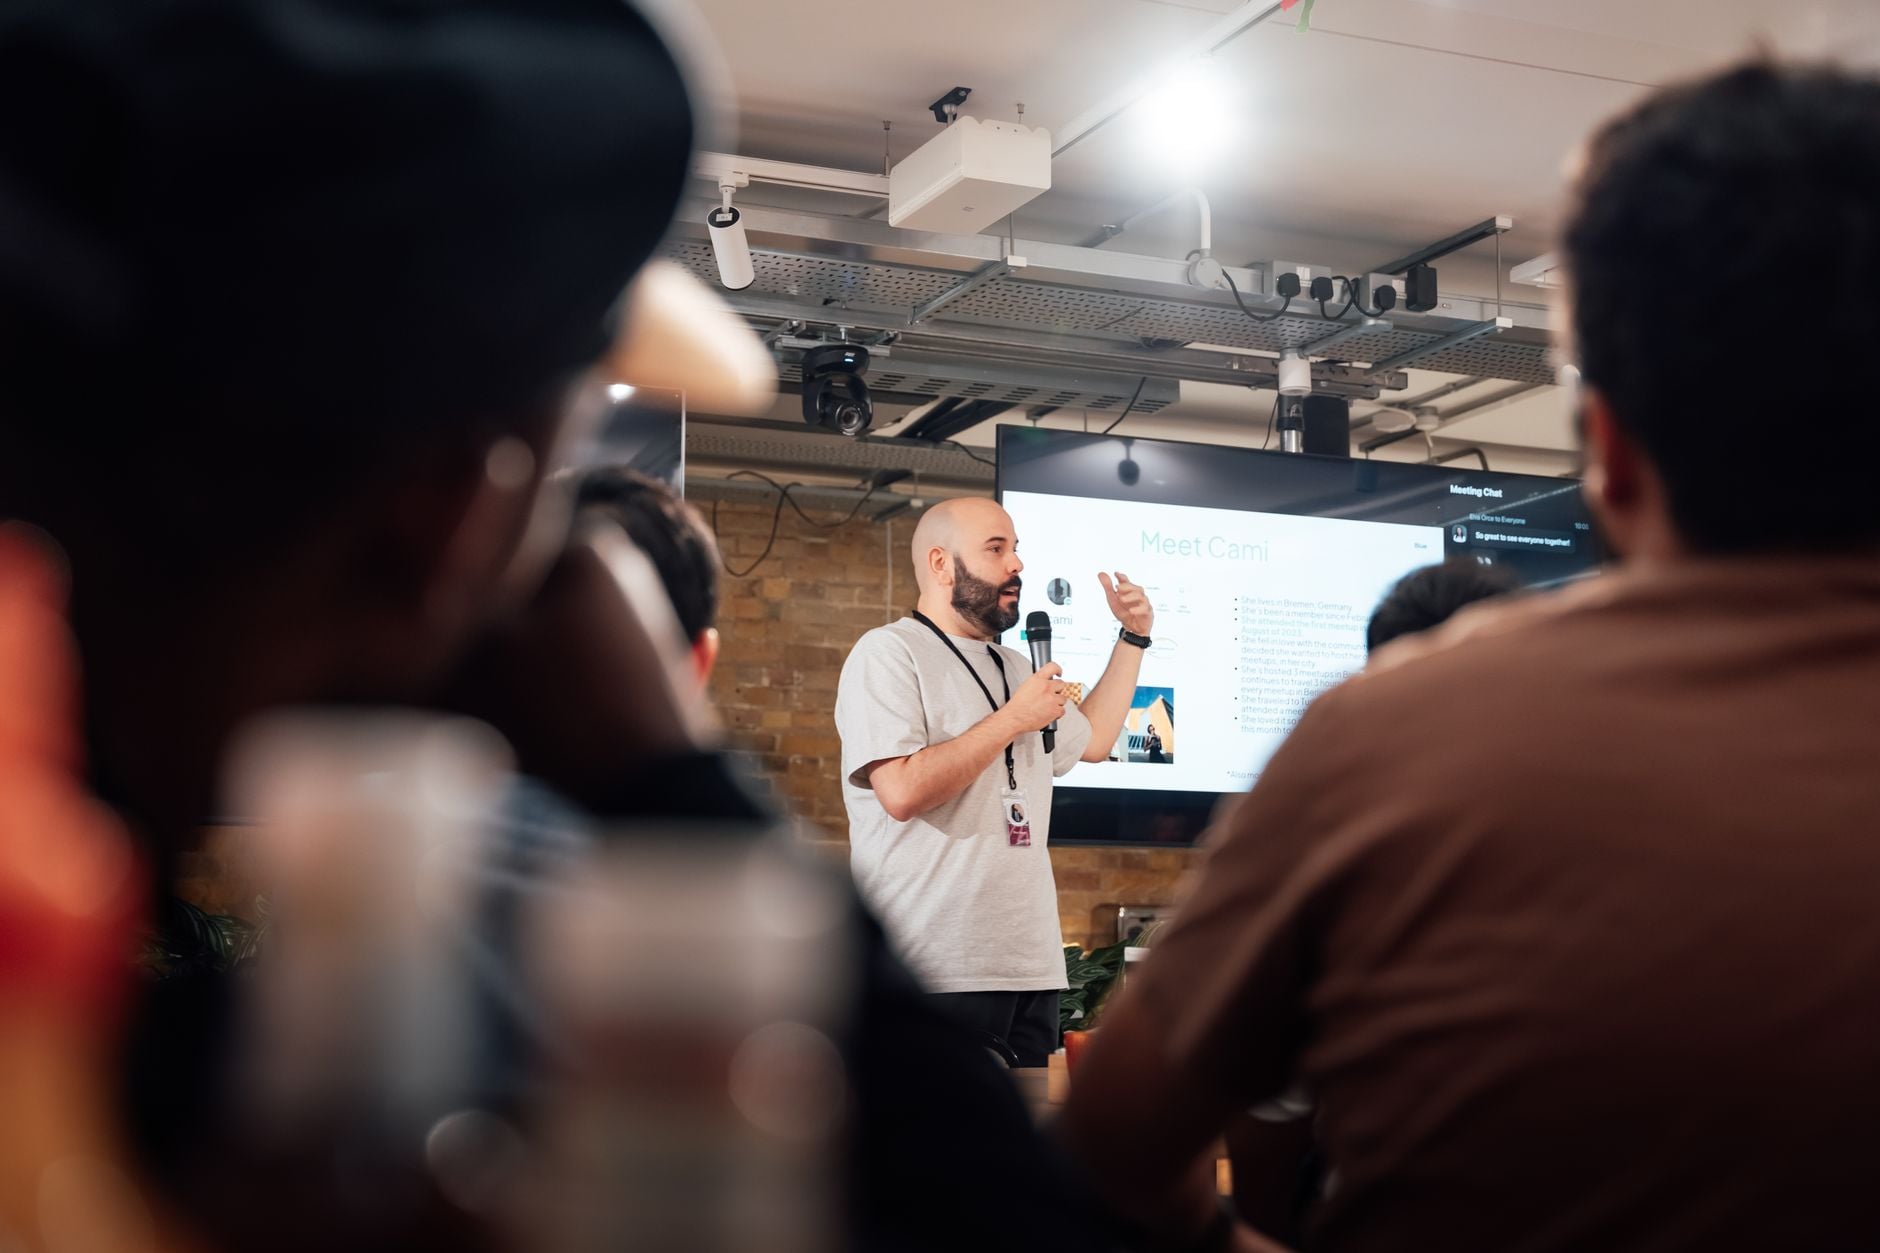
AI Security Engineers Ottawa is the Ottawa chapter of AI Security Engineers (AISecEng), a global community for people who build and secure AI...
By the end of this guide, a complete beginner will be able to open a Linux terminal, move around the file system, and create, copy, and rename files...
To install OpenClaw safely on a Mac, run OpenClaw inside a macOS virtual machine, give the agent dedicated cloud credentials with a spend cap, deny...
OpenClaw is an open-source AI assistant that you host yourself and talk to through chat apps such as Slack, WhatsApp or Telegram. The OpenClaw...
We recently used frontier AI throughout an incident response engagement, from the first log query to the final incident report. This is how it went,...
Truvo Cyber is a Canadian cybersecurity firm that implements ISO/IEC 42001, the AI management system standard, for SaaS and technology companies...
A SOC 2 report must be issued by a licensed CPA firm, and Canadian companies can choose either a Canadian firm reporting under CSAE 3000 or a US firm...