CybersecurityAI


20 posts
An AI agent threat model is a written record of what the agent can access, how that access could be misused, and which control limits each case. The ...
AI agents and identity security meet at one rule: give every AI agent its own identity, manage the agent as an insider with privileged access, and...
AI Security Engineers Ottawa is the Ottawa chapter of AI Security Engineers (AISecEng), a global community for people who build and secure AI...
We recently used frontier AI throughout an incident response engagement, from the first log query to the final incident report. This is how it went,...
Agentic AI security architecture starts with a map of the components of an AI agent system and the connections between them, which sets the scope,...
SOC 2 processing integrity is the optional Trust Services Category (criteria PI1.1 to PI1.5) that tests whether a system processes data completely,...
When any competent team can clone a B2B SaaS product in a weekend, trust as a competitive advantage is the moat that remains: the certifications,...
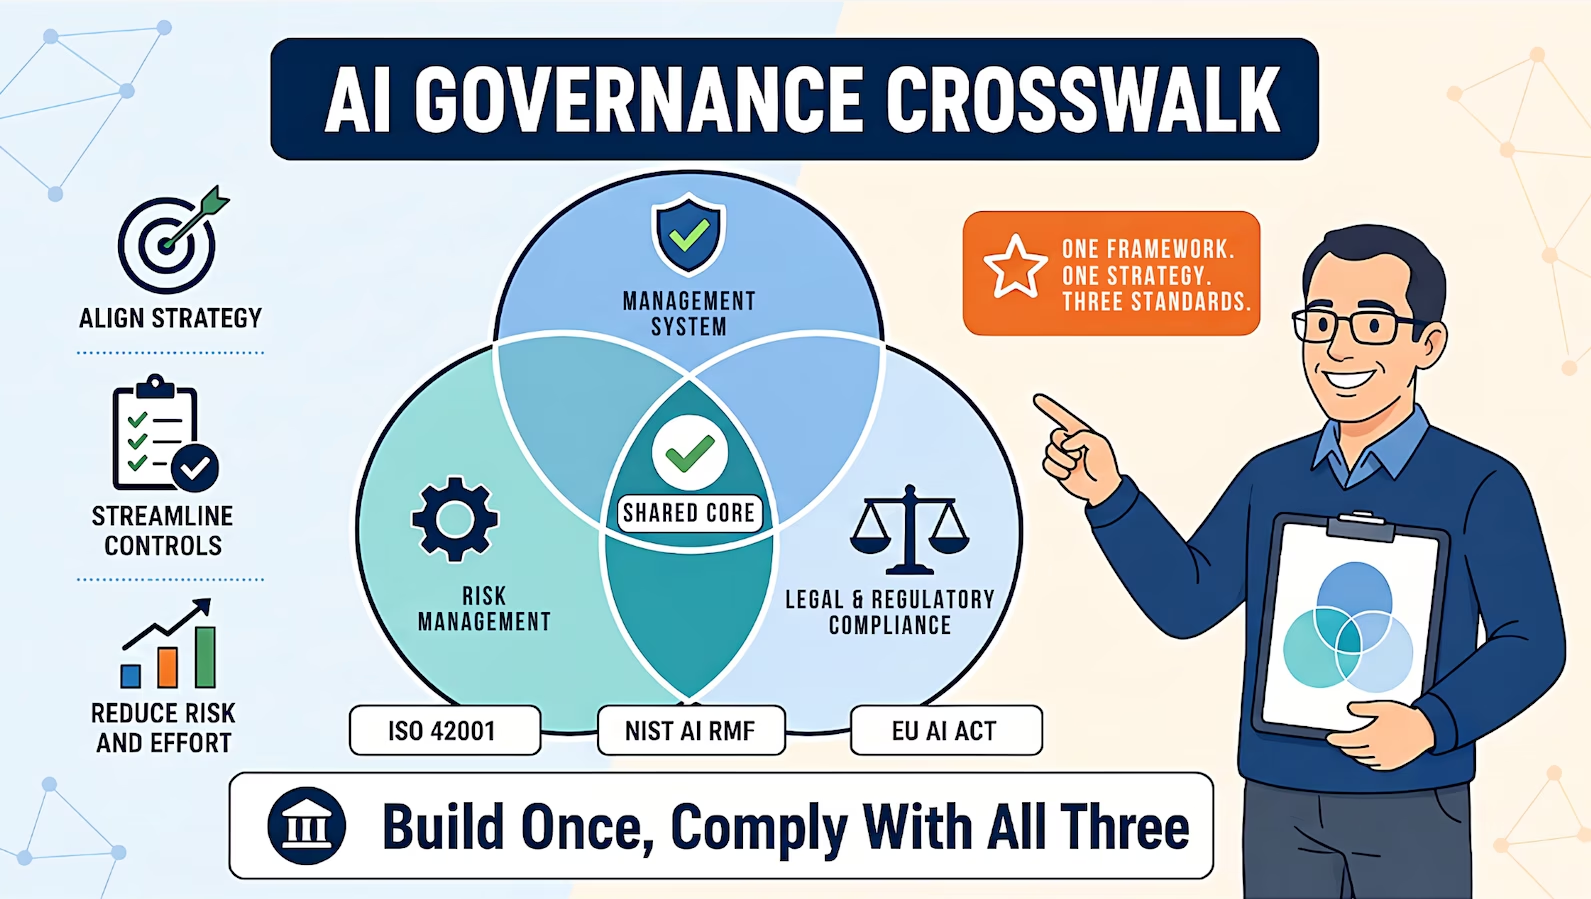
ISO 42001, the NIST AI RMF, and the EU AI Act overlap on roughly two-thirds of their controls. Design one control set against that shared core and...

In Canada, RFPs landing in 2026 include a clause certification must be issued by an SCC-accredited body. SCC is Canada's national accreditation body,...
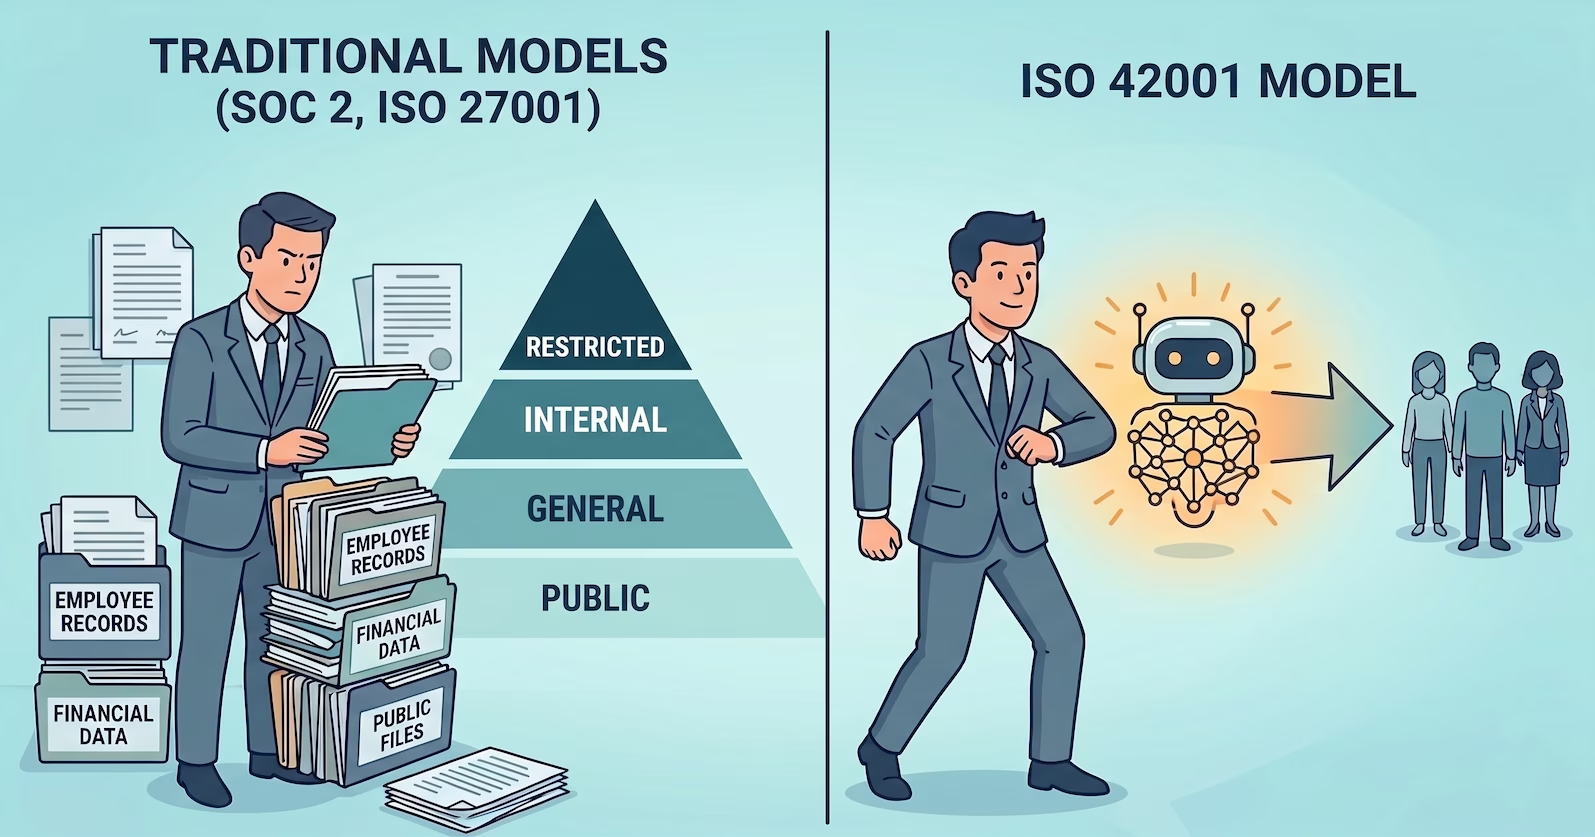
Every traditional compliance framework asks the same opening question. How sensitive is the data, and how well is it protected? SOC 2, ISO 27001,...
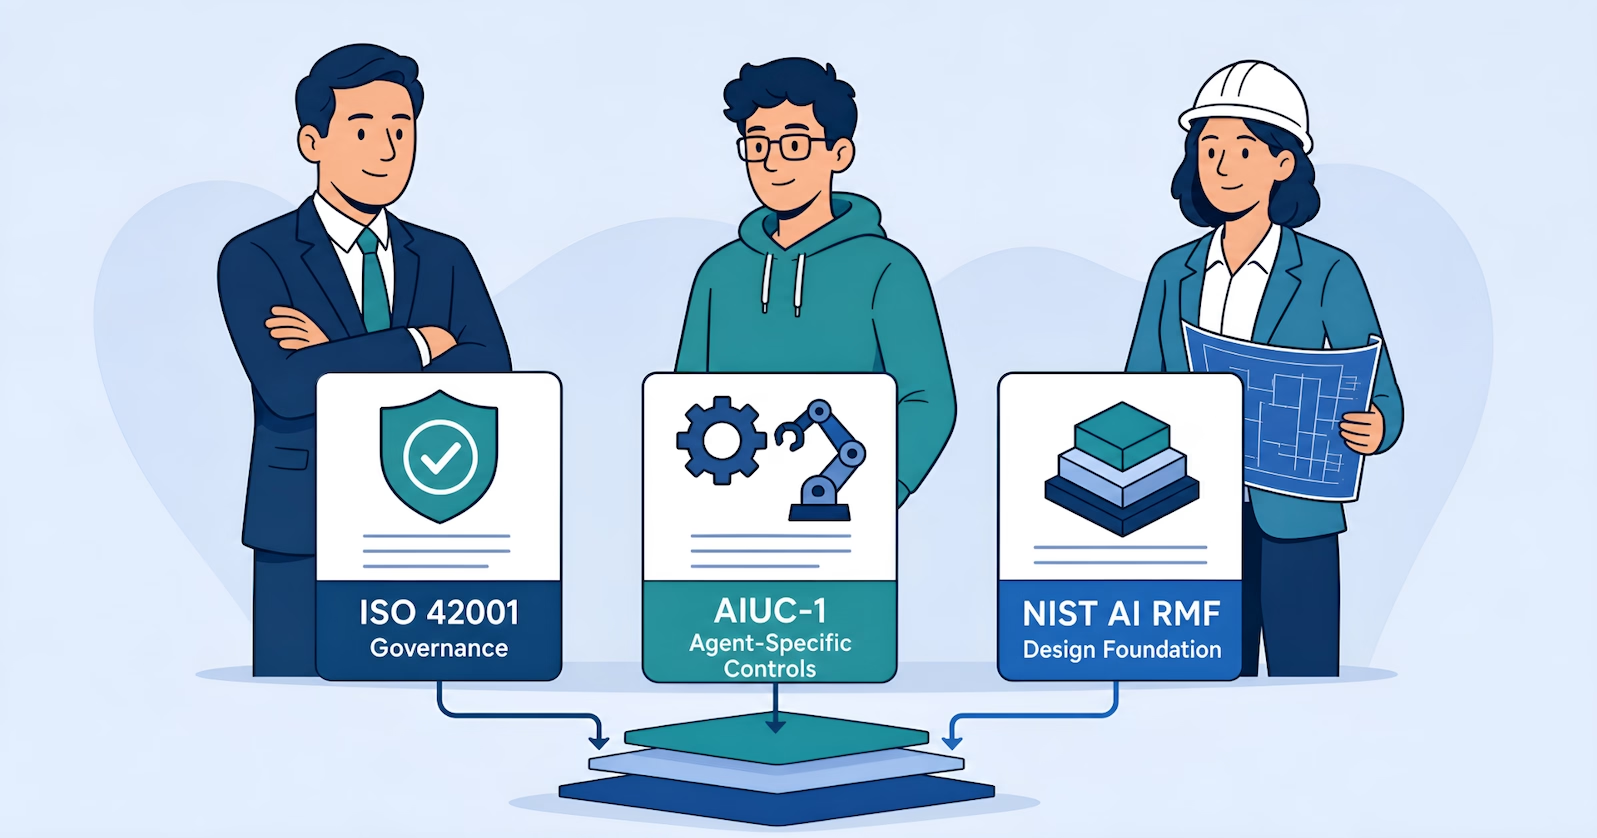
ISO 42001, AIUC-1 and NIST AI RMF serve different buyers, so most companies end up using them as a stack: NIST AI RMF to design the AI risk program,...
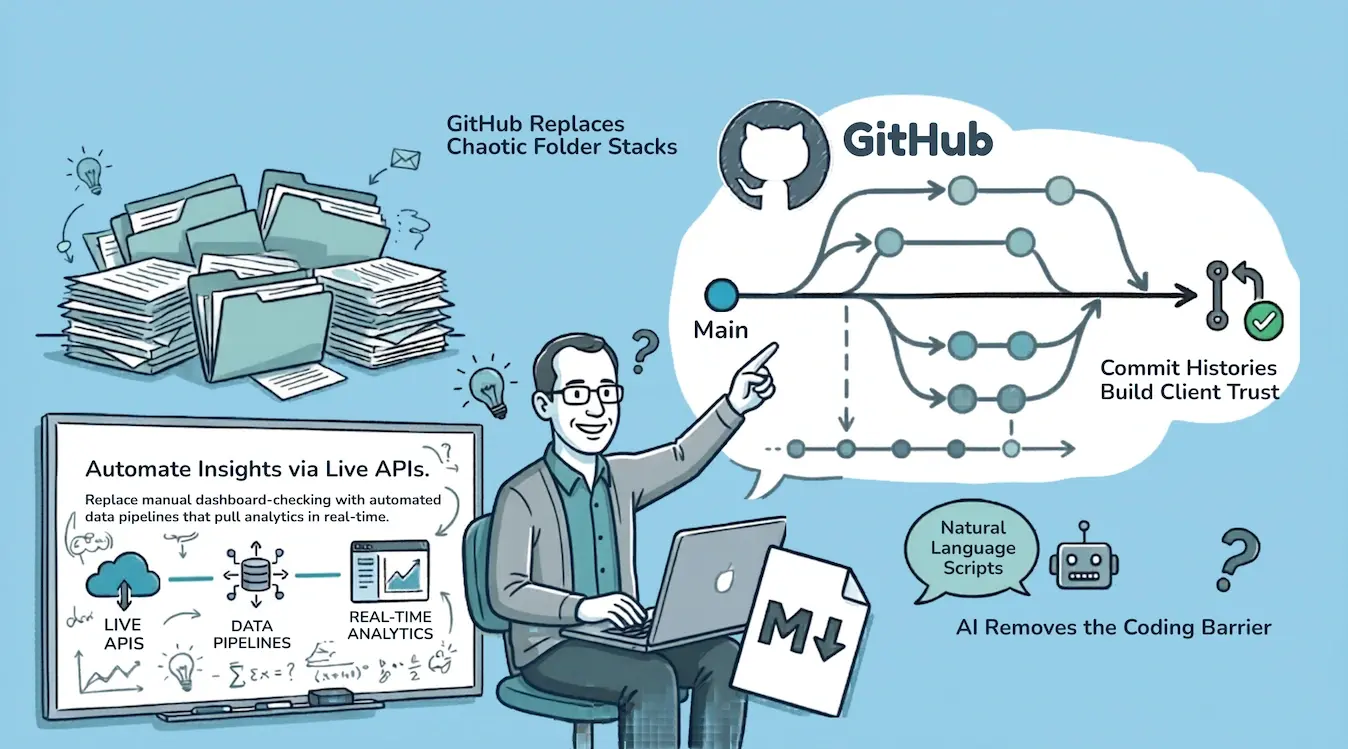
For years, programmers had an unfair advantage over the rest of us.
Not because they could build software. Because they could access data. Rich,...

ISO/IEC 42001:2023 is the world's first international standard for managing artificial...

The EU AI Act entered into force on August 1, 2024, making it the first comprehensive AI...

Implementing ISO/IEC 42001 is a strategic necessity for AI SaaS...

For AI-driven SaaS companies, compliance with ISO/IEC 42001 is...


As artificial intelligence (AI) rapidly embeds itself into core business processes, from customer support to code generation, enterprises face a...

Vanta, Drata, Secureframe, and Scrut have all added dedicated ISO 42001 framework support. All four automate evidence...

Both Drata and Vanta offer dedicated ISO 42001 framework support with automated evidence collection, control cross-mapping to ISO...


