


Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

Ali Aleali

Ali Aleali

Co-Founder & Principal Consultant, CISSP, CCSP

Former security architect for Bank of Canada and Payments Canada. 20+ years building compliance programs for critical infrastructure. Ali leads Truvo's SOC 2, ISO 27001, and CMMC engagements, bringing enterprise-grade security architecture to growing companies.

Follow on LinkedIn →
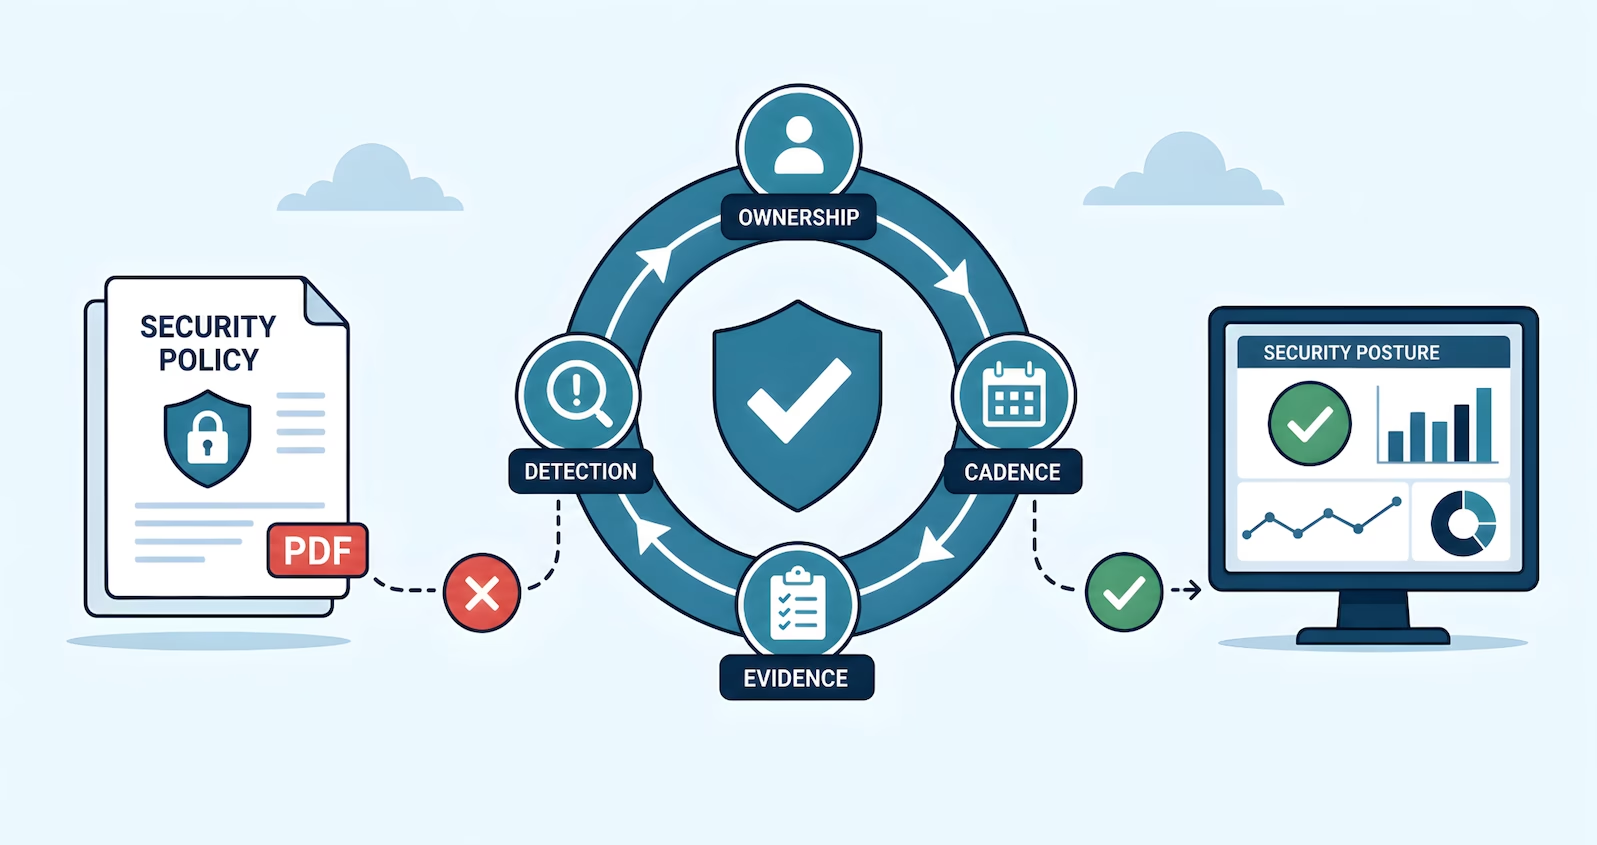
Flat vector illustration showing how security policies become operational processes. A rejected “PDF” policy document leads into a circular workflow of ownership, cadence, evidence, and detection around a security shield, ending with a compliant security posture dashboard.

Operationalizing Security Policies: From PDF to Practice

The moment that usually exposes a security program is not the audit. It is a simple question asked in a meeting.

"Who actually reviews user access...
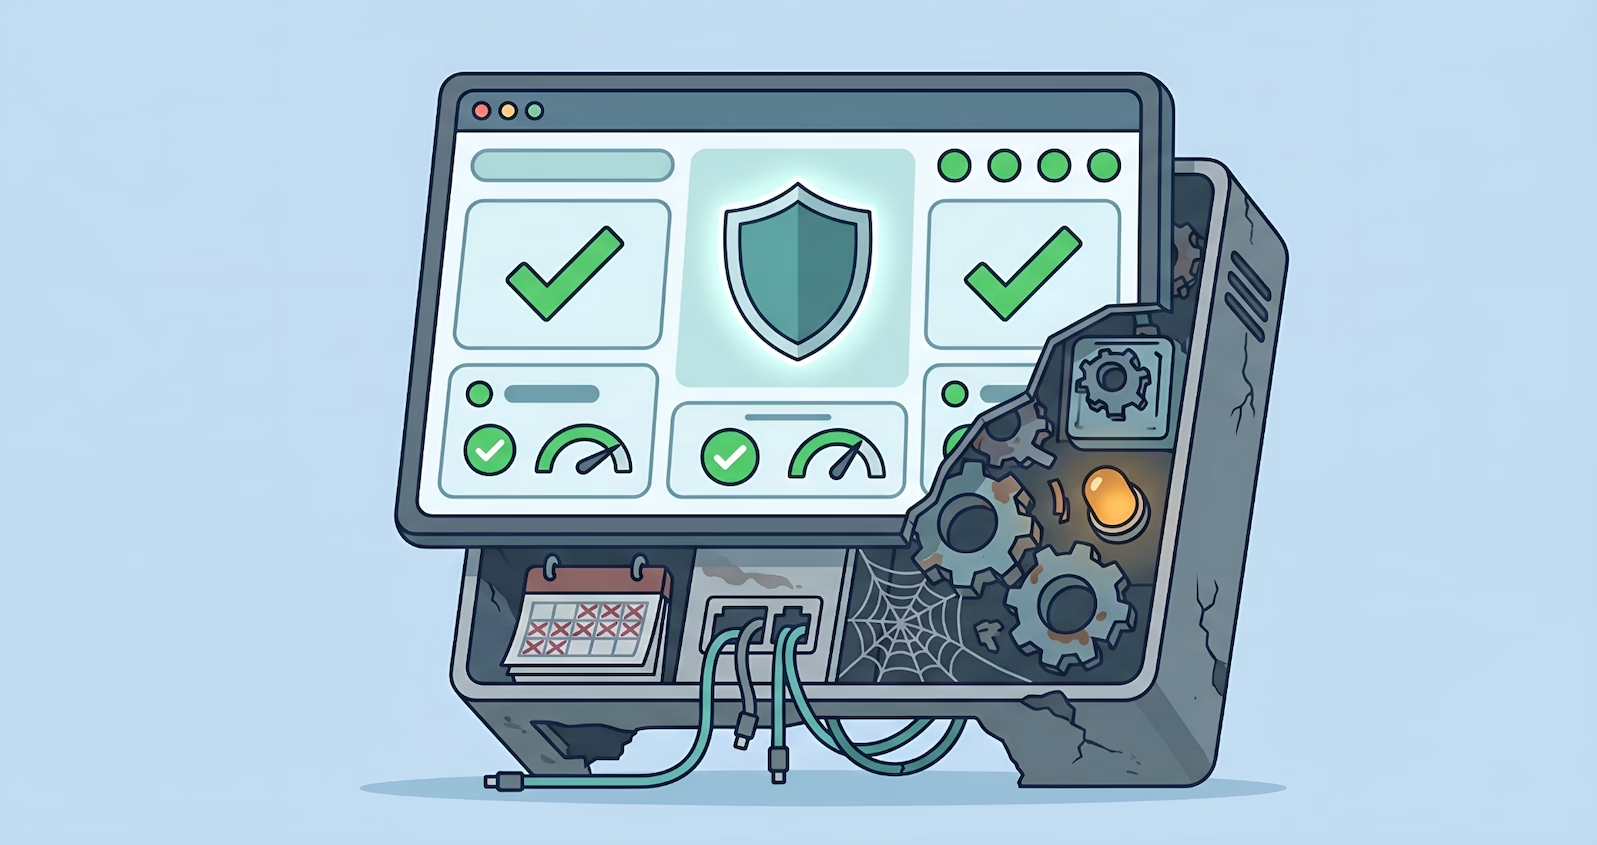
A flat cartoon illustration shows a pristine digital dashboard on a cracked, dilapidated monitor. The screen displays green checkmarks and a shield, while a cutaway reveals internal decay: rusty gears, loose cables, cobwebs, a calendar with crossed-out dates, and an glowing amber bulb.

GRC Platform Managed Services: What You Actually Get

A company subscribes to a GRC platform. A consultant configures it, loads policies, maps controls, connects integrations. The dashboard turns green....
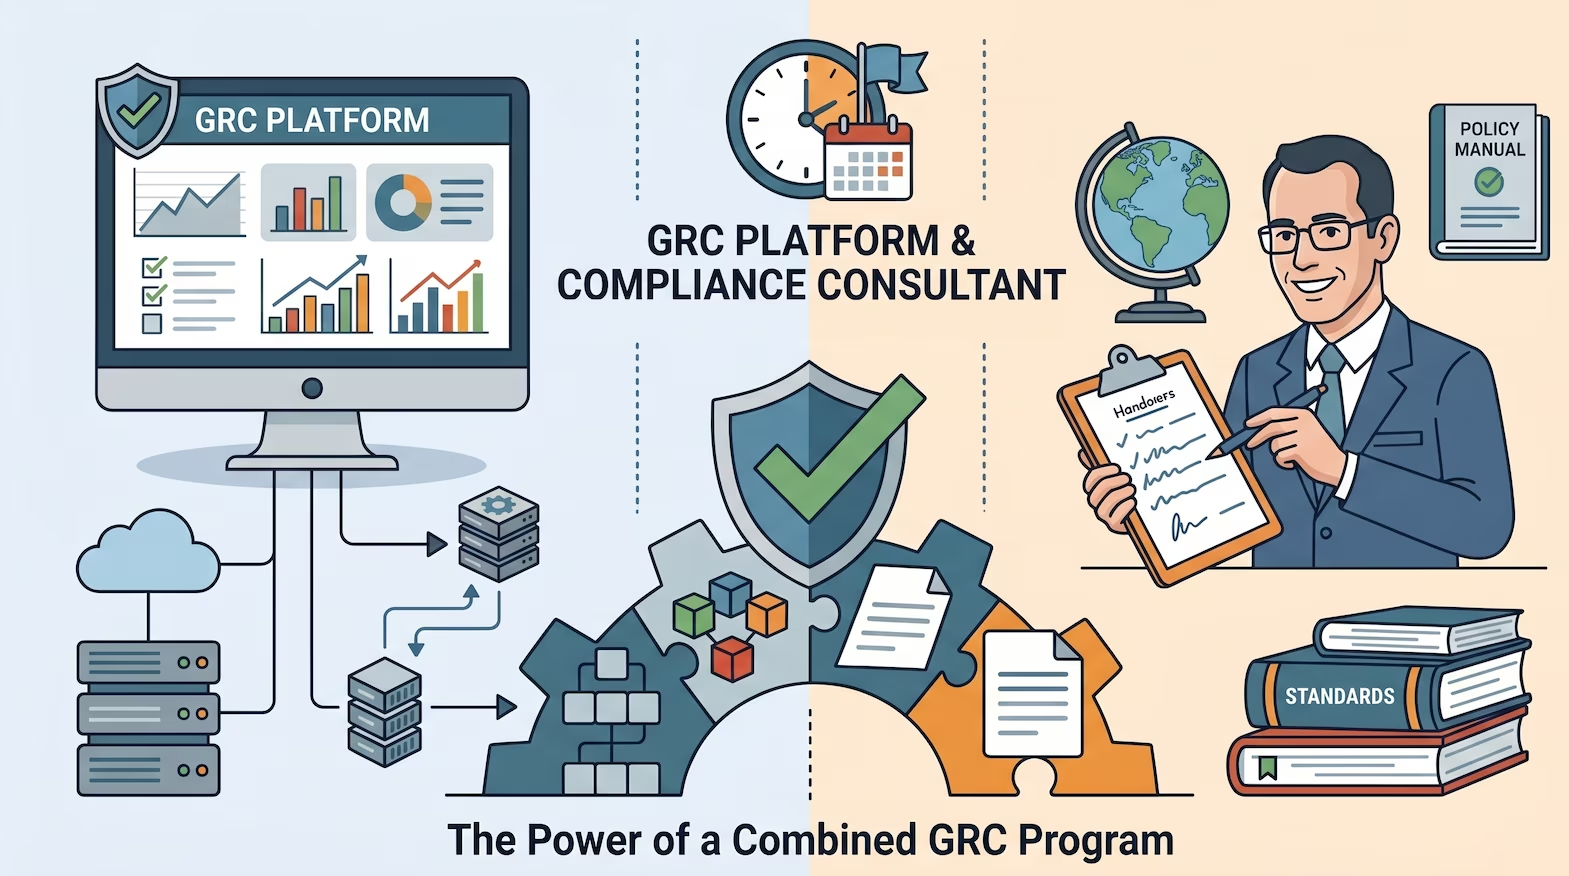
A colorful infographic showing a computer with charts and a man with a clipboard. The central text reads, 'GRC Platform & Compliance Consultant Work Together for The Power of a Combined GRC Program.'

Compliance Consulting vs GRC Platform: You Need Both

A GRC platform such as Vanta or Drata automates evidence collection, roughly 60 to 70 percent of the compliance workload for a cloud-native SaaS...
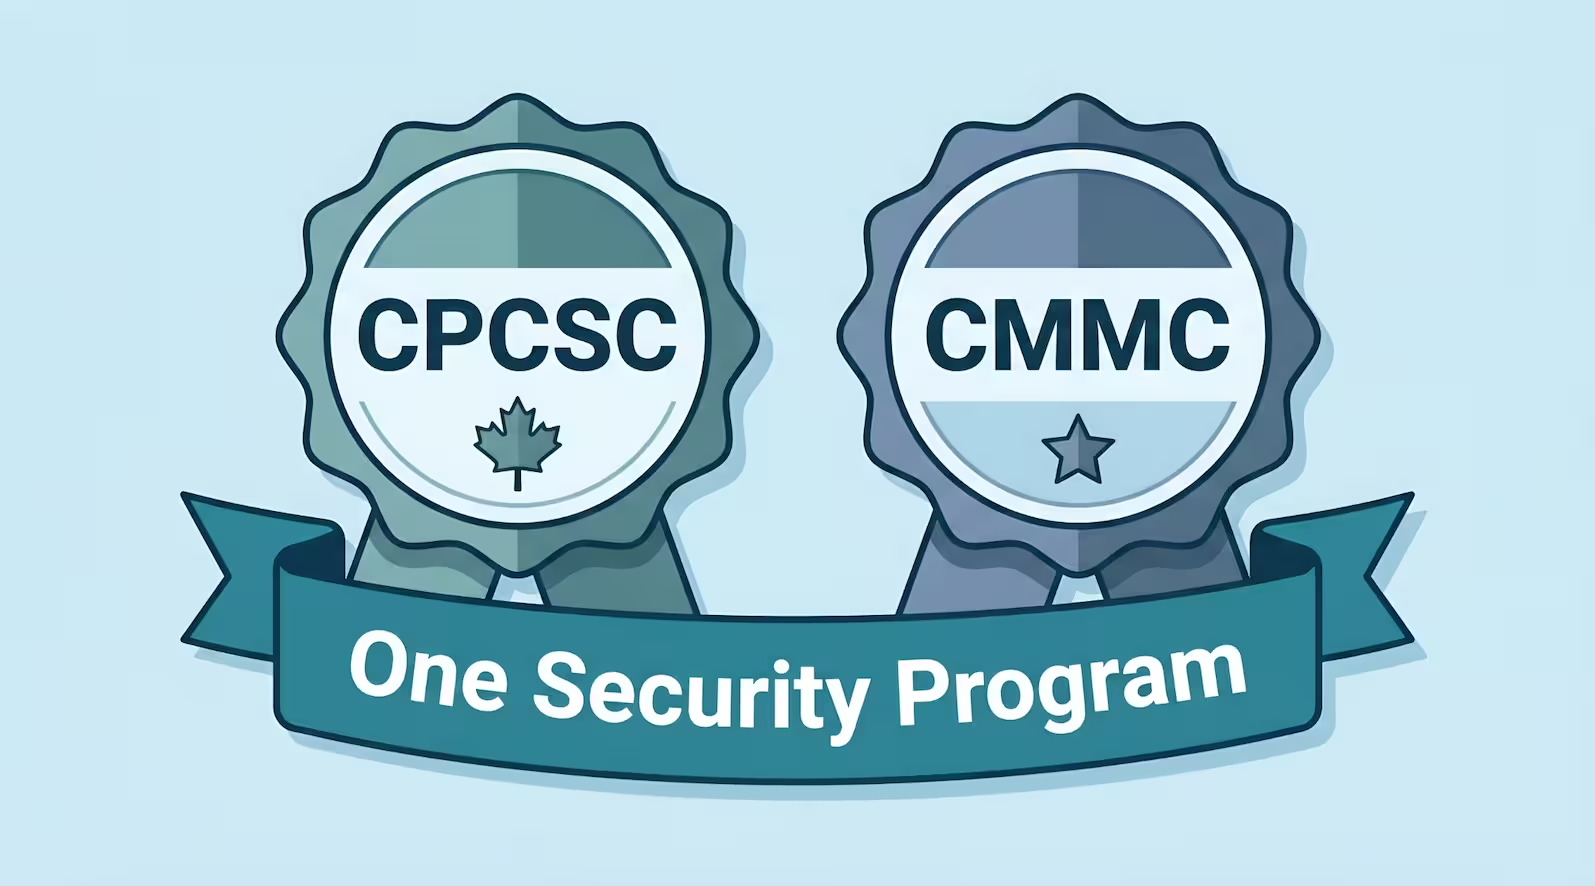
Flat 2D vector illustration of two official badges labeled "CPCSC" (with a maple leaf) and "CMMC" (with a star). They are joined by a single teal banner underneath that reads "One Security Program," set against a light blue background in a clean, professional style.

CMMC Compliance Consulting for Canadian Defence Contractors

Canadian companies selling into the U.S. defence supply chain face a compliance requirement that is no longer theoretical. The Cybersecurity Maturity...
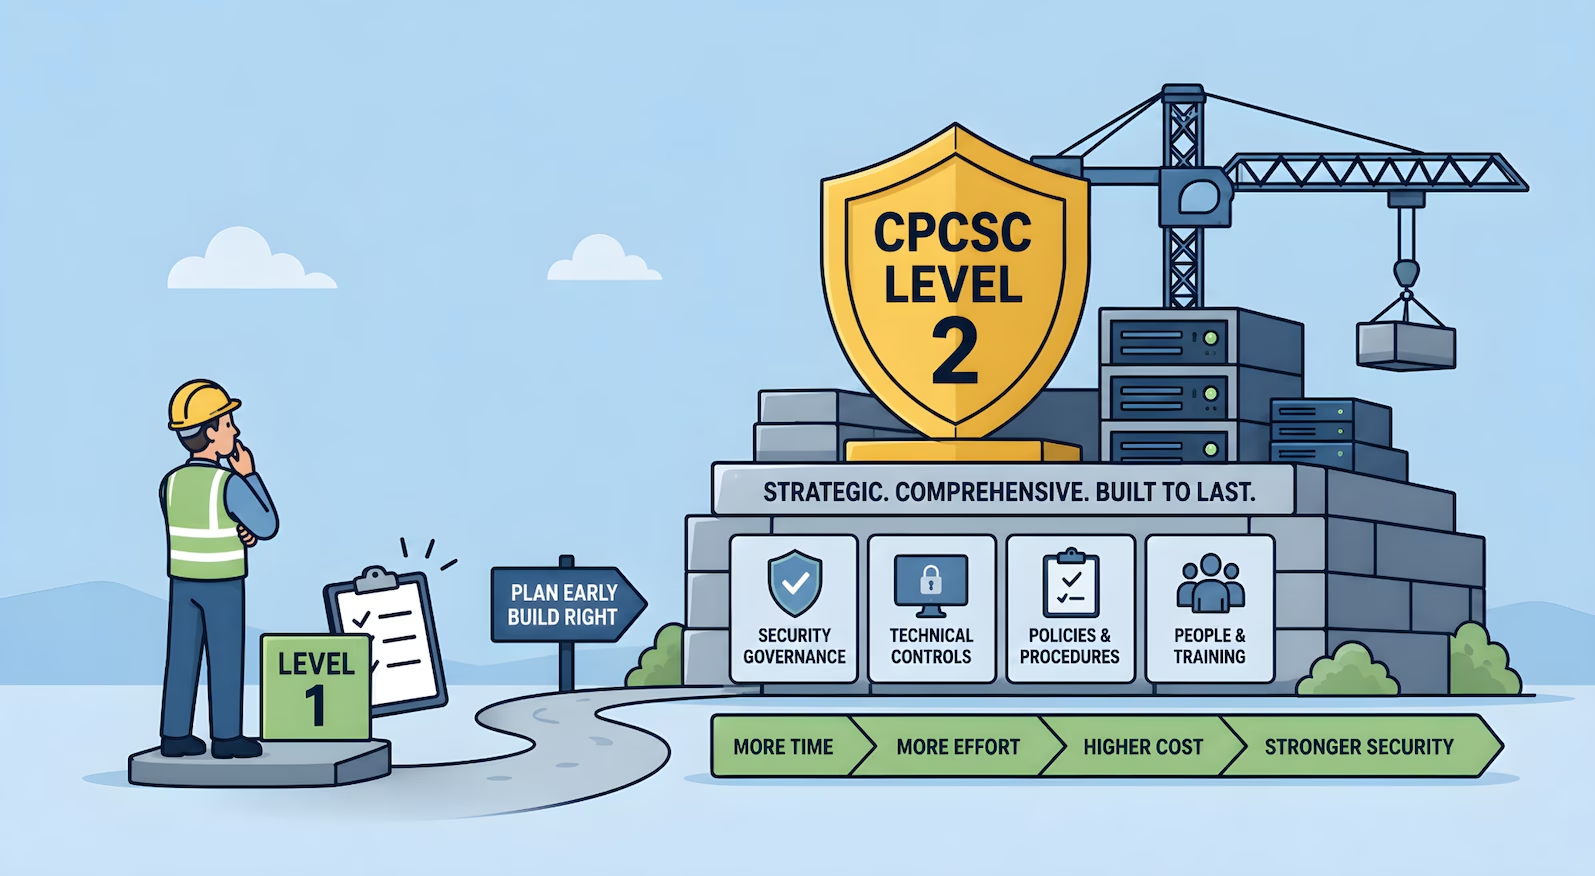
CPCSC Level 2 security compliance as a large-scale strategic program. A worker stands near a simple Level 1 checklist, while Level 2 is shown as a fortified foundation with servers, a crane, governance, technical controls, policies, and training elements.

CPCSC Level 1 vs Level 2: The Cost Cliff Suppliers Miss

Canadian defence-adjacent suppliers keep running into the same pattern. A team clears CPCSC Level 1 in a few weeks, files self-attestation in Canada...
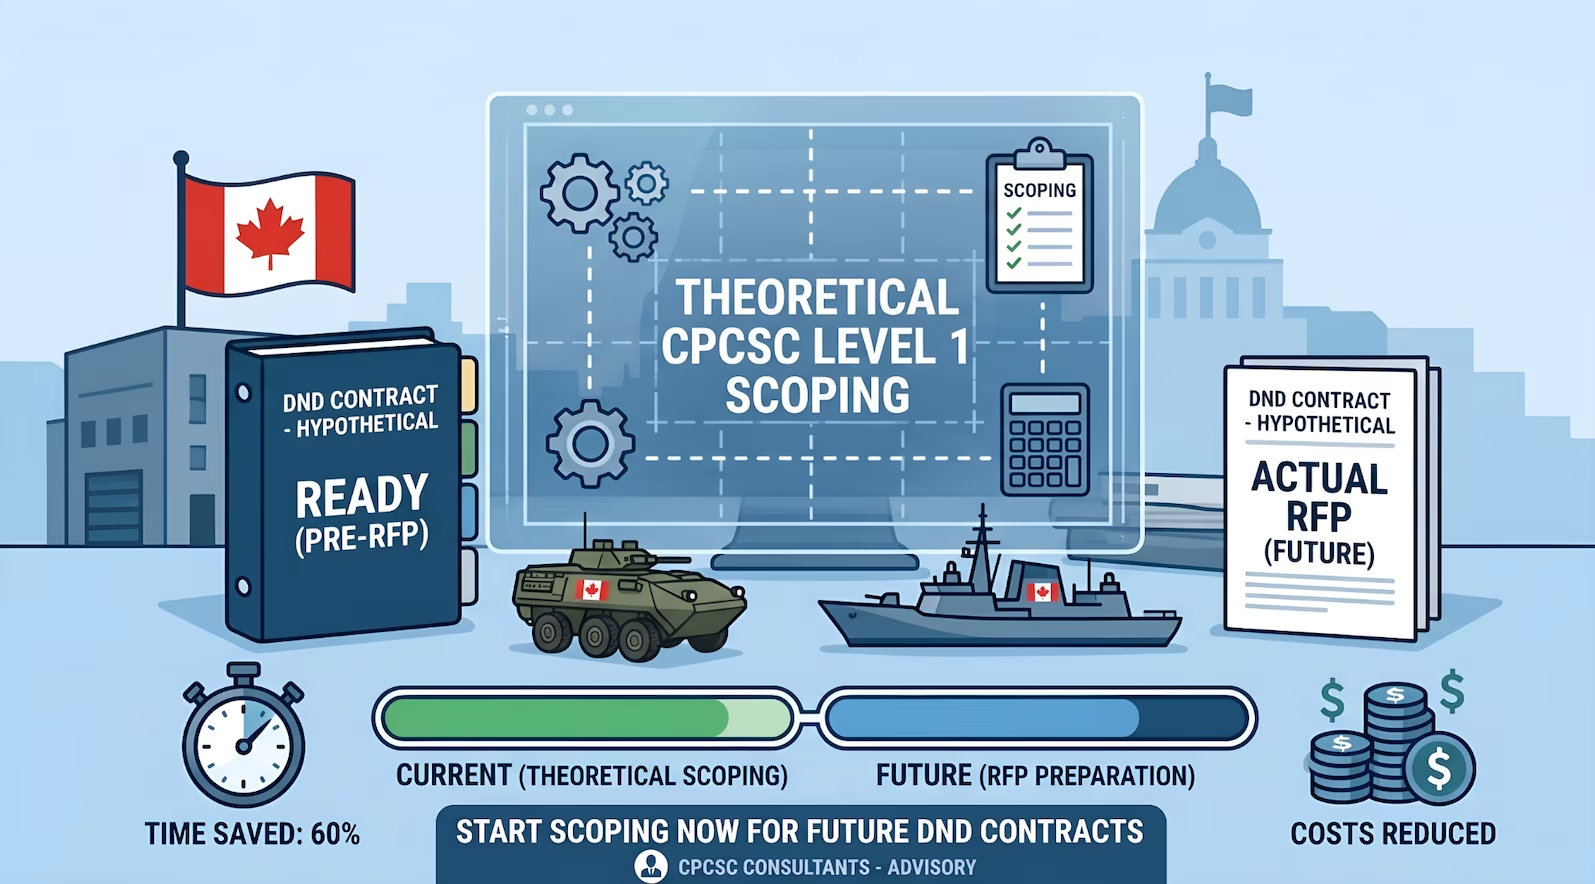
A flat vector illustration in blue and white showing a "Theoretical CPCSC Level 1 Scoping" blueprint. A stopwatch and progress bar highlight time savings, while a binder labeled "Ready (Pre-RFP)" sits next to Canadian military icons, emphasizing preparation for future DND contracts.

CPCSC Level 1 Scoping Before You Have a Contract

DND has been clear about direction and quiet about timing. Canada Buys is collecting expressions of interest, industry days are running, and the...
Flat vector illustration of a calm business professional reviewing a completed checklist at a tidy desk with a laptop and organized documents. Security and compliance icons — shield, lock, clock, and laptop indicators — surround the scene in muted teal and blue tones.

CPCSC Level 1 Self-Assessment: What Apr 14 Actually Requires

On April 14, 2026, the Government of Canada published the CPCSC Level 1 self-assessment guide, the scoping guide, and practical implementation steps....
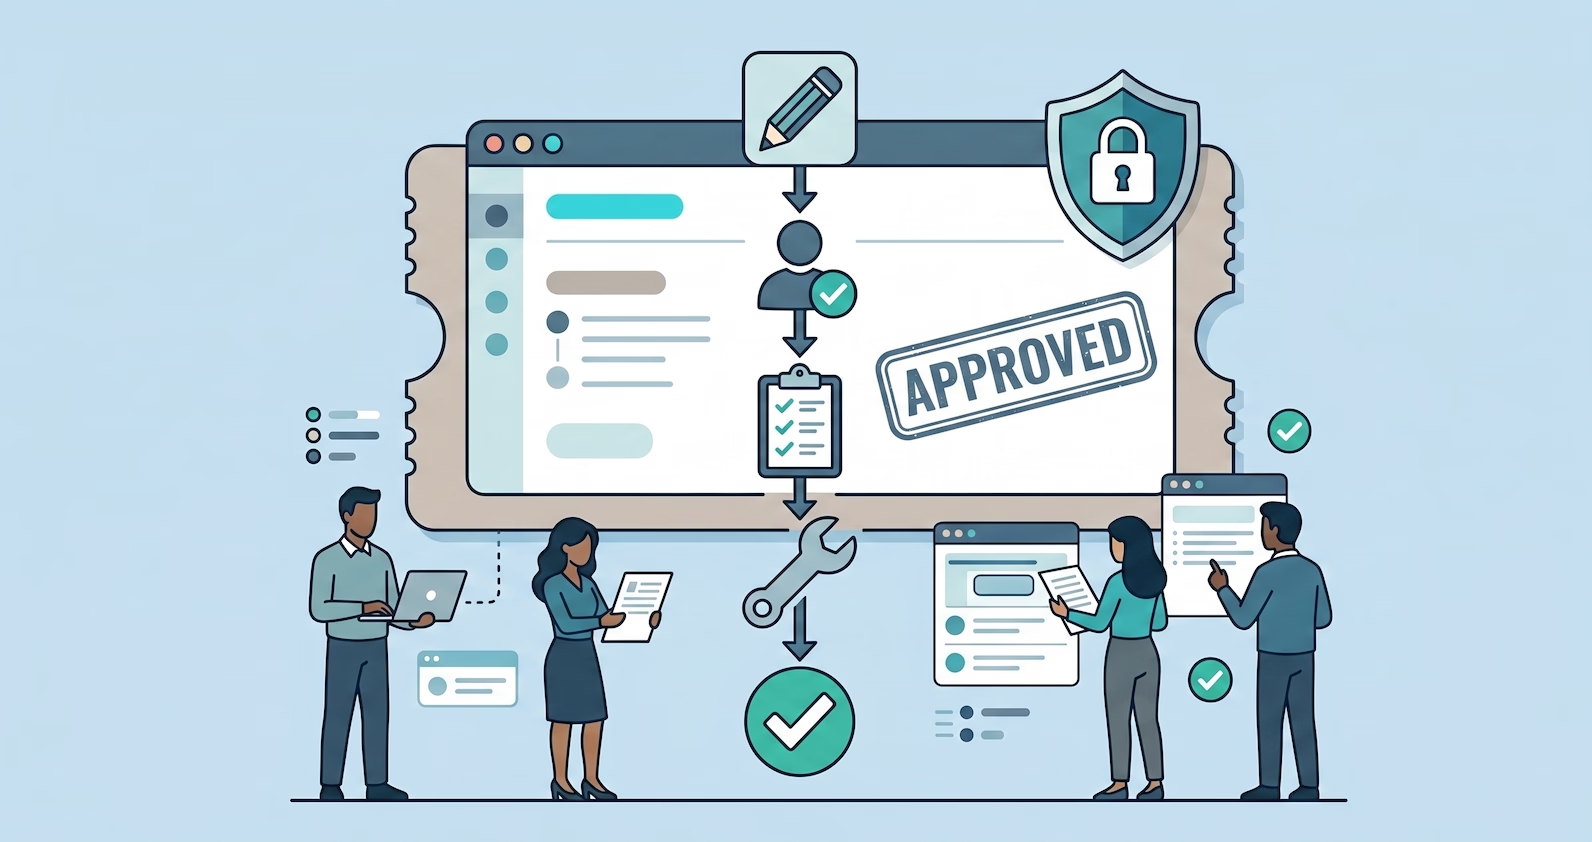
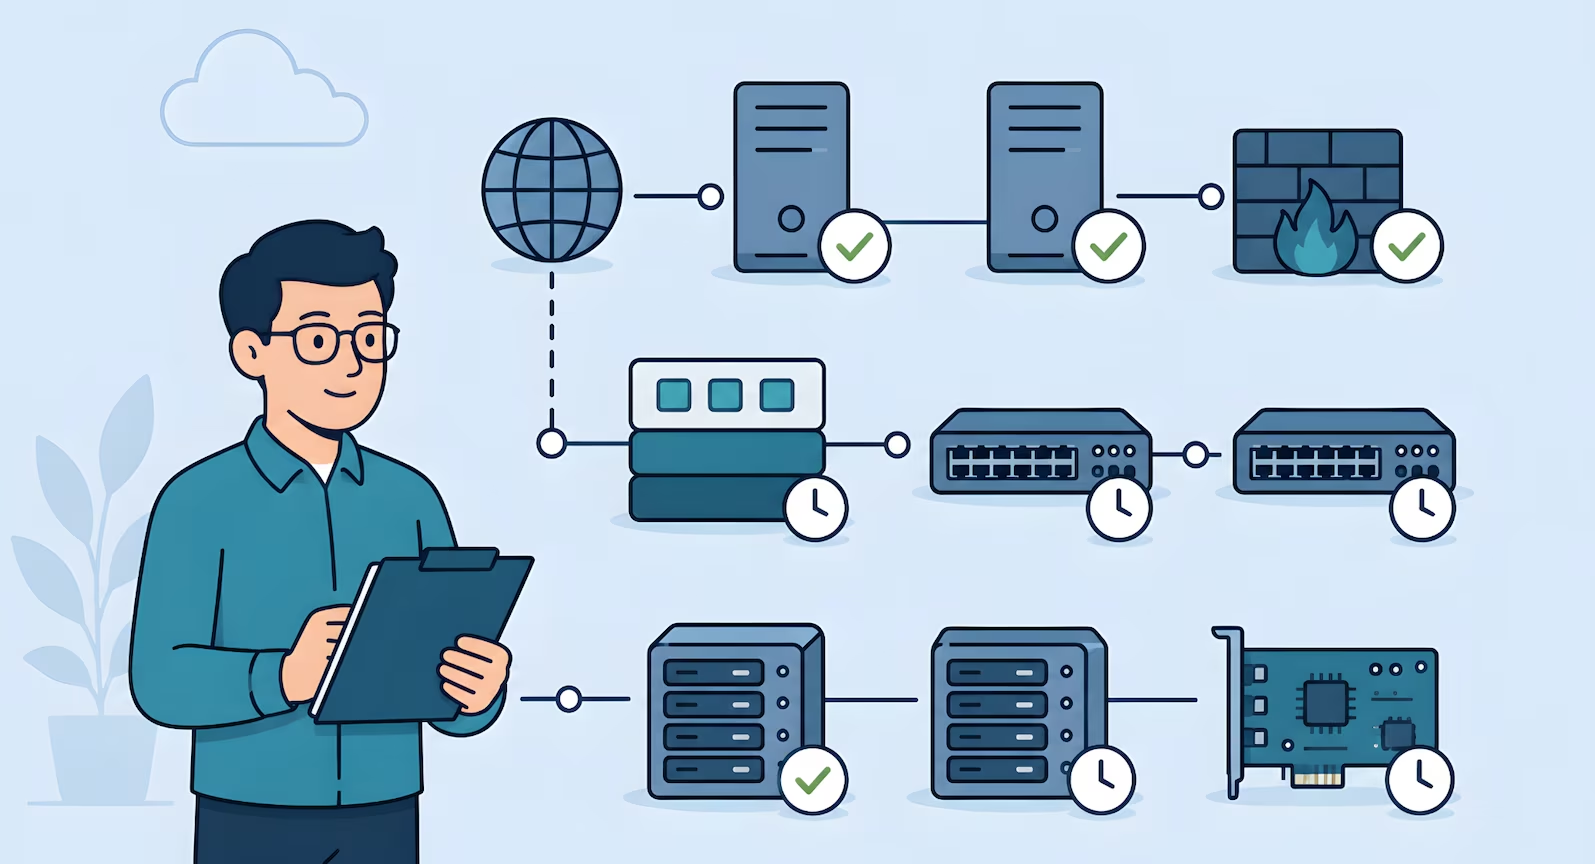
Flat 2D illustration of an IT professional managing organized on-premise infrastructure. Servers, firewalls, switches, storage systems, and management cards are arranged in tiers with patch status icons, showing a calm, repeatable security and maintenance process.

SOC 2 Patch Management for On-Prem Servers and Network Devices

TL;DR

  • Patching is a three-criteria activity in SOC 2: CC8.1 has a Point of Focus literally called Manages Patch Changes, with CC6.8 covering...
A flat 2D illustration showing a horizontal dividing line labeled "OWNERSHIP BOUNDARY". Above, a person with a laptop manages "SaaS USER ENTITY RESPONSIBILITIES," including logical and app controls. Below, a person stands by icons for a building, power, and cooling for "COLOCATION PROVIDER RESPONSIBILITIES." A document links the two.

SOC 2 Vendor Management: Data Center as Subservice

TL;DR

  • When your data center is operated by another organization (a colocation or hosting provider), that organization is a subservice organization...
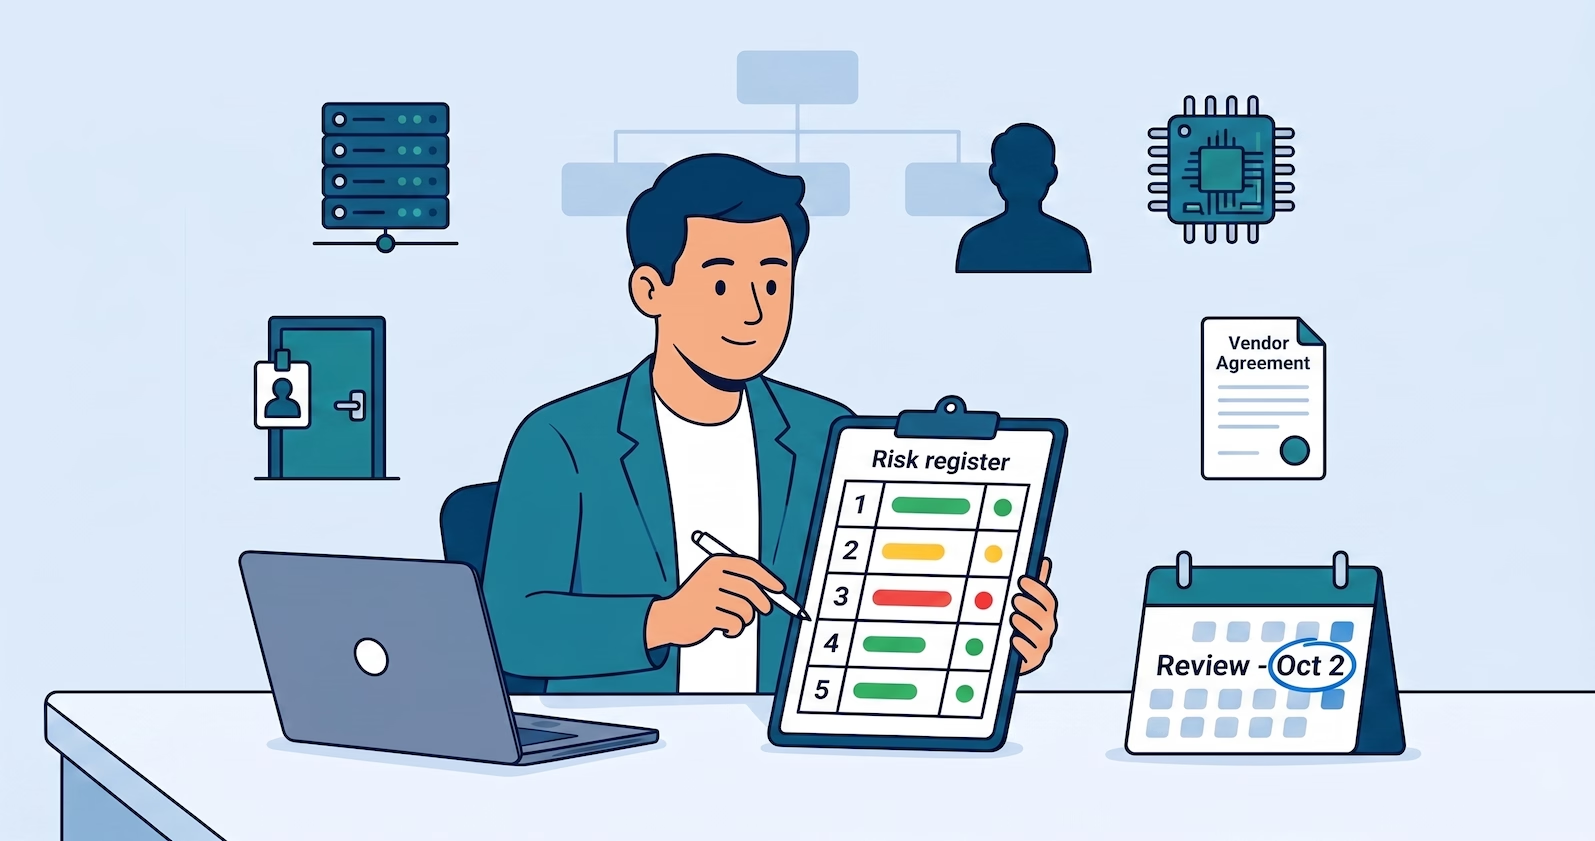
An illustration of a man reviewing a security risk register. Floating icons include a server rack, security badge door, user profile, microchip, and a vendor agreement. A calendar on his desk marks a review date, emphasizing an organized risk management process.

SOC 2 Risk Management for Hybrid and On-Prem Environments

TL;DR

  • Risk management maps to CC3.2 (risk identification and analysis), CC3.3 (fraud risk), and CC3.4 (changes that affect internal control)
  • On-prem...
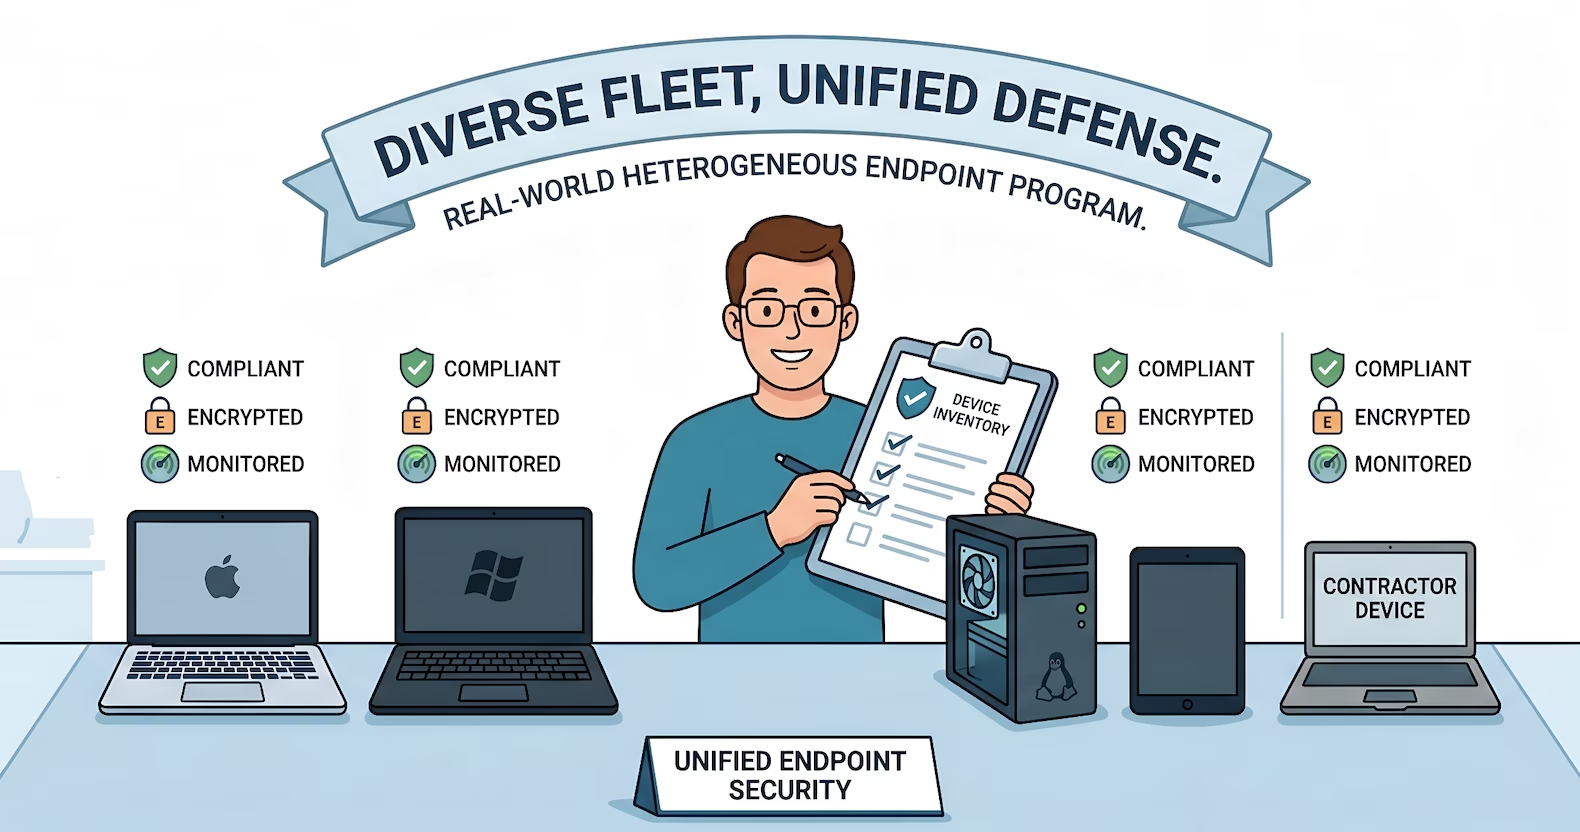
Flat 2D illustration of a smiling IT professional holding a "Device Inventory" clipboard. He manages a diverse fleet of devices—Mac, Windows, Linux, and tablets—each with icons for "Compliant," "Encrypted," and "Monitored." A banner reads "Diverse Fleet, Unified Defense."

SOC 2 Endpoint Security for On-Prem and Hybrid Workforces

TL;DR

  • Endpoint security maps to CC6.1 (logical access architecture, named asset inventory, encryption at rest, MFA where warranted) and CC6.8...
A 2D flat illustration showing an oversized magnifying glass scanning a central server rack, revealing internal network lines. In the background are icons for a firewall appliance, a network switch, a padlock with a cloud, and a cyan shield with a white checkmark, all on a blue background.

SOC 2 Penetration Testing for On-Premise Networks

TL;DR

  • Pen testing maps to CC4.1 (separate evaluations, where the AICPA names penetration testing explicitly) and CC7.1 (vulnerability detection)
  • ...
A flat vector illustration on a light blue background shows a large clipboard with a checkmark on the center. To the left is a key on a ring, and to the right is a closed padlock with a red "X" mark. Below, a dashed arrow links an "enter" door icon on the left with an "exit" door icon on the right.

SOC 2 HR Security Controls Without Automated Provisioning

TL;DR

  • HR security maps to four Trust Services Criteria: CC1.4 (competence), CC1.5 (accountability), CC2.2 (internal communication), and CC6.2 (user...
Flat 2D vector illustration of a central teal server rack protected by three concentric shield layers and an oversized padlock. Beside it are chained tape cartridges and a hard drive. Faint data lines connect to smaller servers in the background. Clean, muted blue and slate color palette.

SOC 2 Data Protection for On-Premise Datastores and Physical Media

TL;DR

  • Data protection maps to CC6.1 (logical access architecture), CC6.6 (data in transit), and CC6.7 (information disposal)
  • Encryption at rest on...
A ticket-based workflow brings order to SOC 2 change management for legacy and hybrid stacks. Every step is documented—from request to approval, testing, implementation, and verification—creating a robust audit trail of approved changes.

SOC 2 Change Management with Tickets Instead of CI/CD

TL;DR

  • Change management maps to CC8.1, which has 14 Points of Focus covering authorization, design, testing, approval, deployment, segregation of...
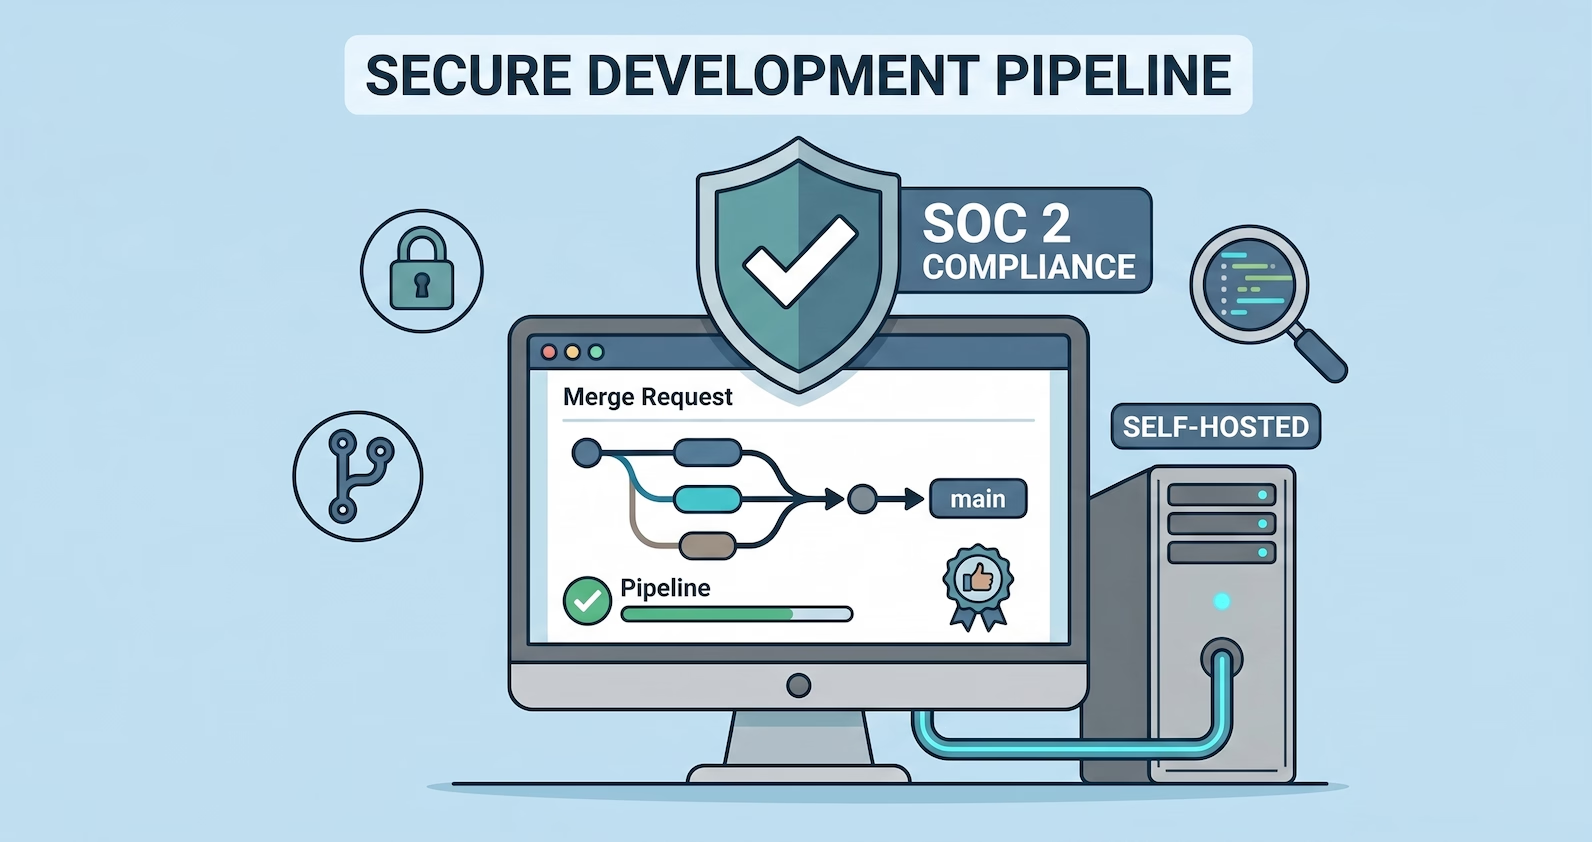
A flat 2D cartoon illustration on a powder blue background, featuring a computer monitor displaying a merge request, branch flow diagram, and a green pipeline status. A server tower is connected to the monitor, and a large shield labeled SOC 2 COMPLIANCE floats above. Icons like a lock and branch symbol orbit the scene.

SOC 2 Secure Development with Self-Hosted GitLab

TL;DR

  • The same Trust Services Criterion that governs infrastructure changes governs code changes: CC8.1, change management
  • Self-hosted GitLab is the...
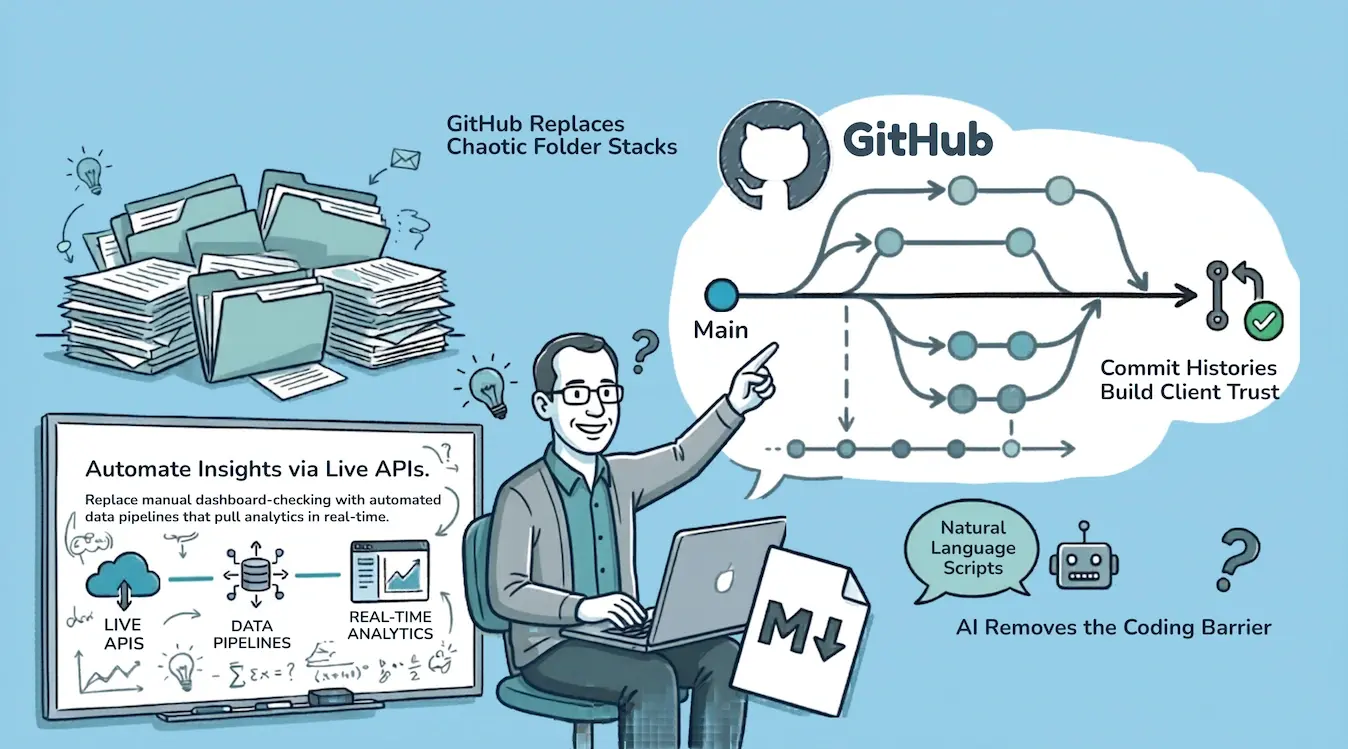
A man points to a GitHub workflow replacing a messy paper stack. Text highlights "Consulting as Code" concepts: GitHub for version control, automated data pipelines via live APIs, and AI-driven scripts. The graphic promotes using software engineering tools to automate and trust-build in consulting.

Consulting as Code: Running Cybersecurity on GitHub

For years, programmers had an unfair advantage over the rest of us.

Not because they could build software. Because they could access data. Rich,...
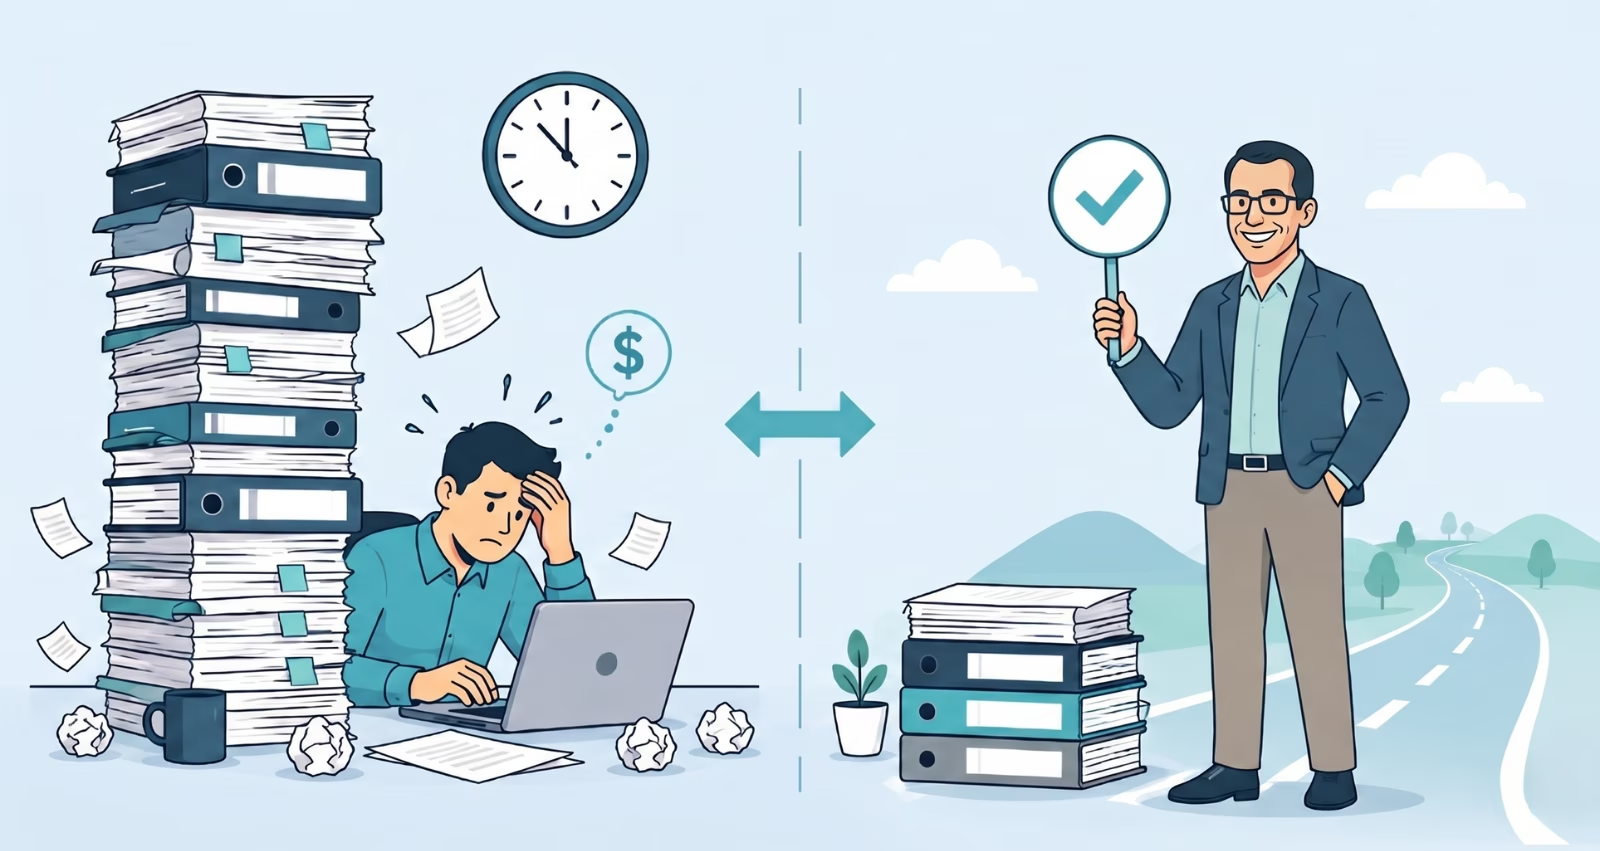
Before-and-after infographic. Left: A stressed man overwhelmed by a giant stack of binders. Right: A smiling professional holding a checkmark next to a small stack and a clear road, representing efficiency.

The Real Cost of DIY Compliance vs. Hiring a Consultant

On paper, DIY compliance looks straightforward. Subscribe to a GRC platform, follow the control library, collect evidence, engage an auditor. The...
Alt text: A man with glasses in a suit holds a checklist in front of a large, open server rack with colorful cables and LED lights. A large shield with a checkmark is behind him. Other staff and servers are visible in the background against a light blue, vector illustration backdrop.

SOC 2 Consultants for On-Prem and Hybrid Infrastructure

Most SOC 2 consultants know AWS. Some know Azure and GCP. Very few know what to do when your stack includes a colocation facility, a bare-metal fleet...
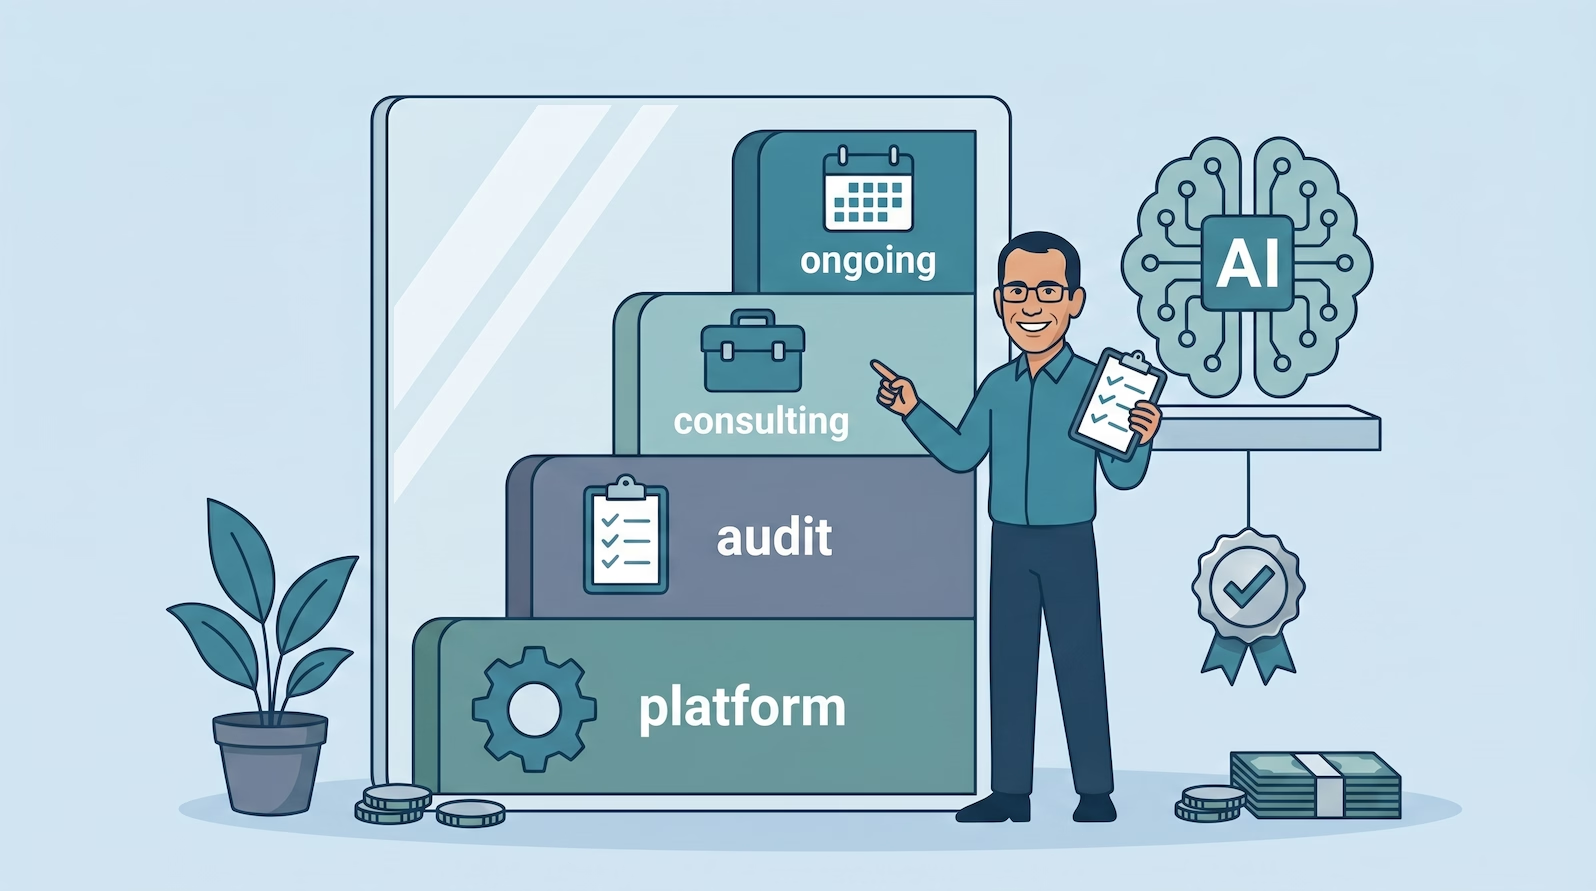
An illustration of a man with glasses pointing at a four-step diagram with sections labeled "platform," "audit," "consulting," and "ongoing." To the right is a brain-shaped AI icon, a badge, and stacks of money.

ISO 42001 Certification Cost: What You'll Pay in 2026

If you are an AI SaaS company looking at ISO 42001, the first question is not what does the standard say. It is what is this going to cost us in...
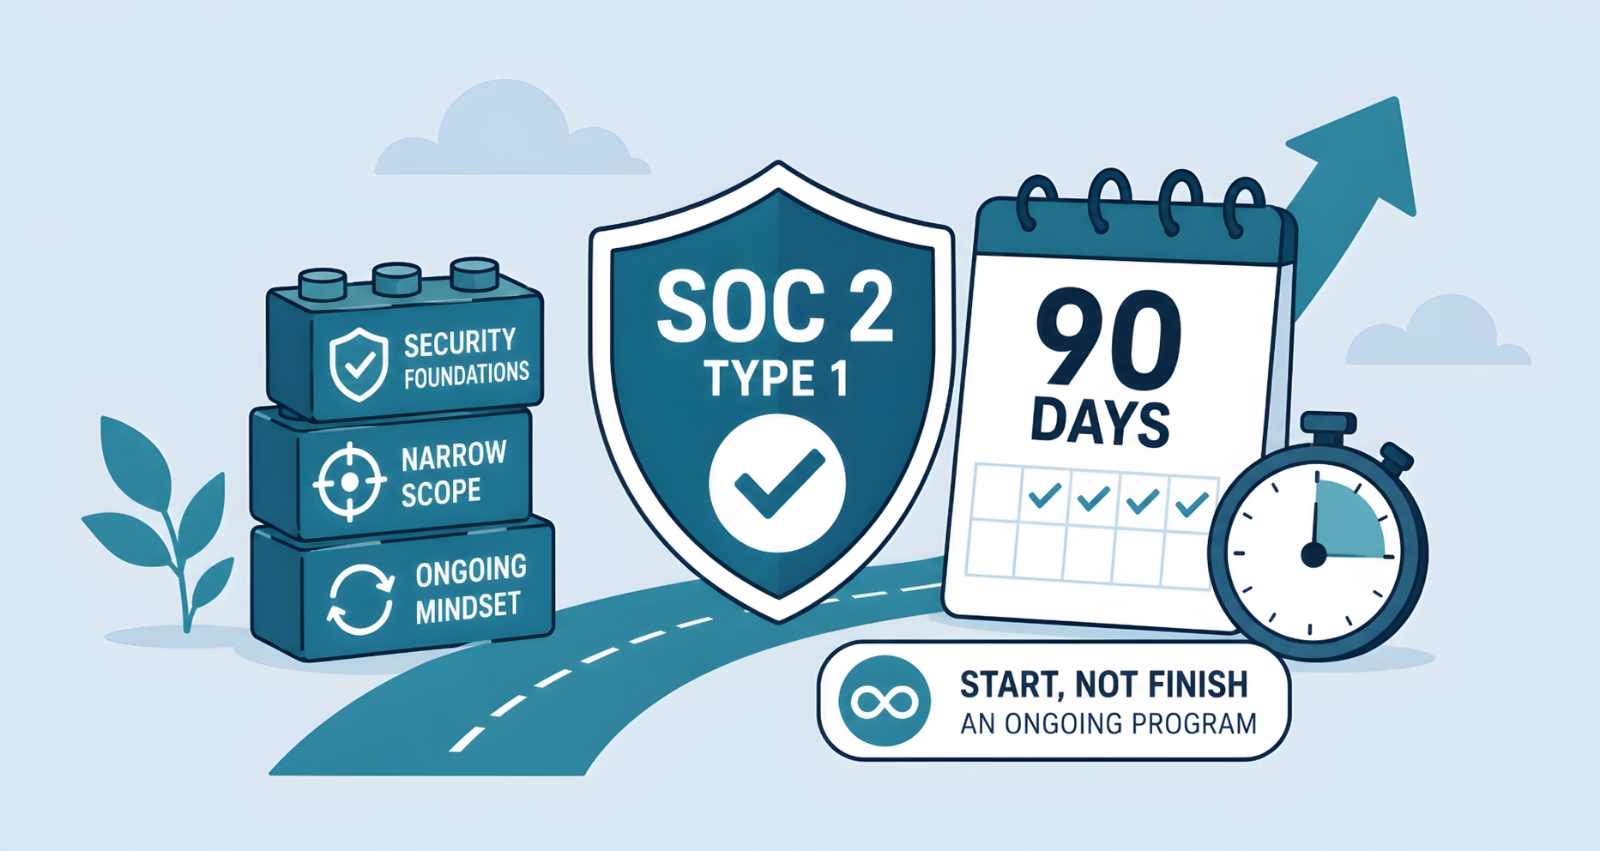
Flat vector illustration of a SOC 2 Type 1 compliance program completed in 90 days, featuring a security shield, calendar, stopwatch, growth arrow, and stacked blocks labeled security foundations, narrow scope, and ongoing mindset.

SOC 2 in 90 Days: What That Timeline Actually Requires

Ninety days from kickoff to a SOC 2 readiness is achievable. It is not achievable for every company, and the companies that hit it make deliberate...
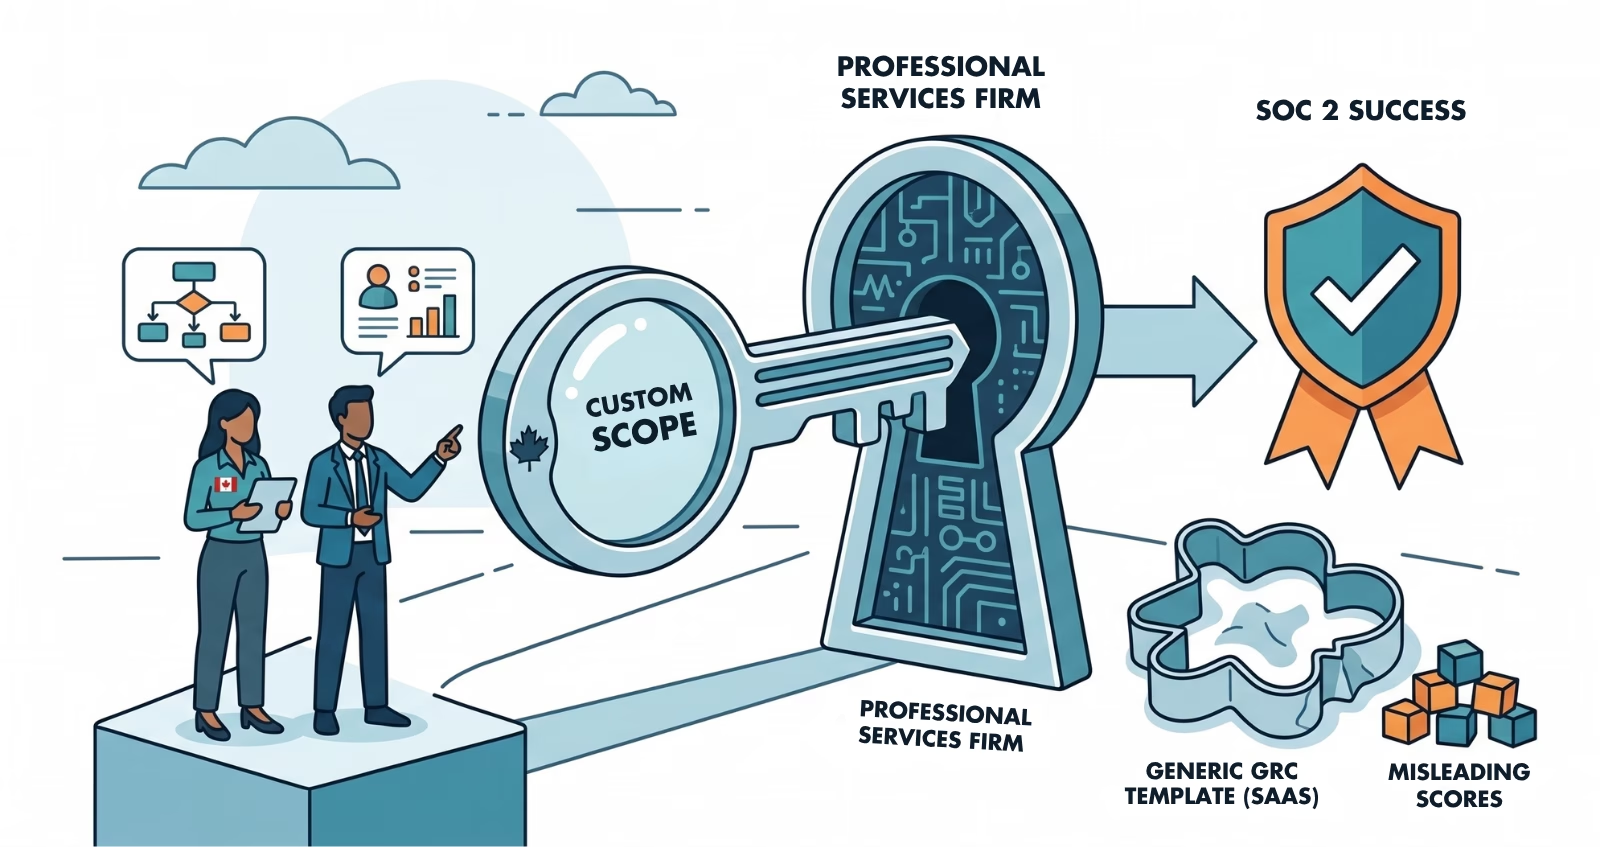
A vector illustration shows two professionals with Canadian flags on their clothing analyzing "SOC 2 SUCCESS." They stand near a large key and magnifying glass labeled "CUSTOM SCOPE" unlocking a specialized "PROFESSIONAL SERVICES FIRM" lock. A "GENERIC GRC TEMPLATE (SAAS)" is rejected nearby with "MISLEADING SCORES."

SOC 2 for Professional Services Firms: The Scoping Problem Nobody Warns You About

A professional services firm starts its SOC 2 process the same way most companies do. An enterprise client puts it in an RFP. The team subscribes to...
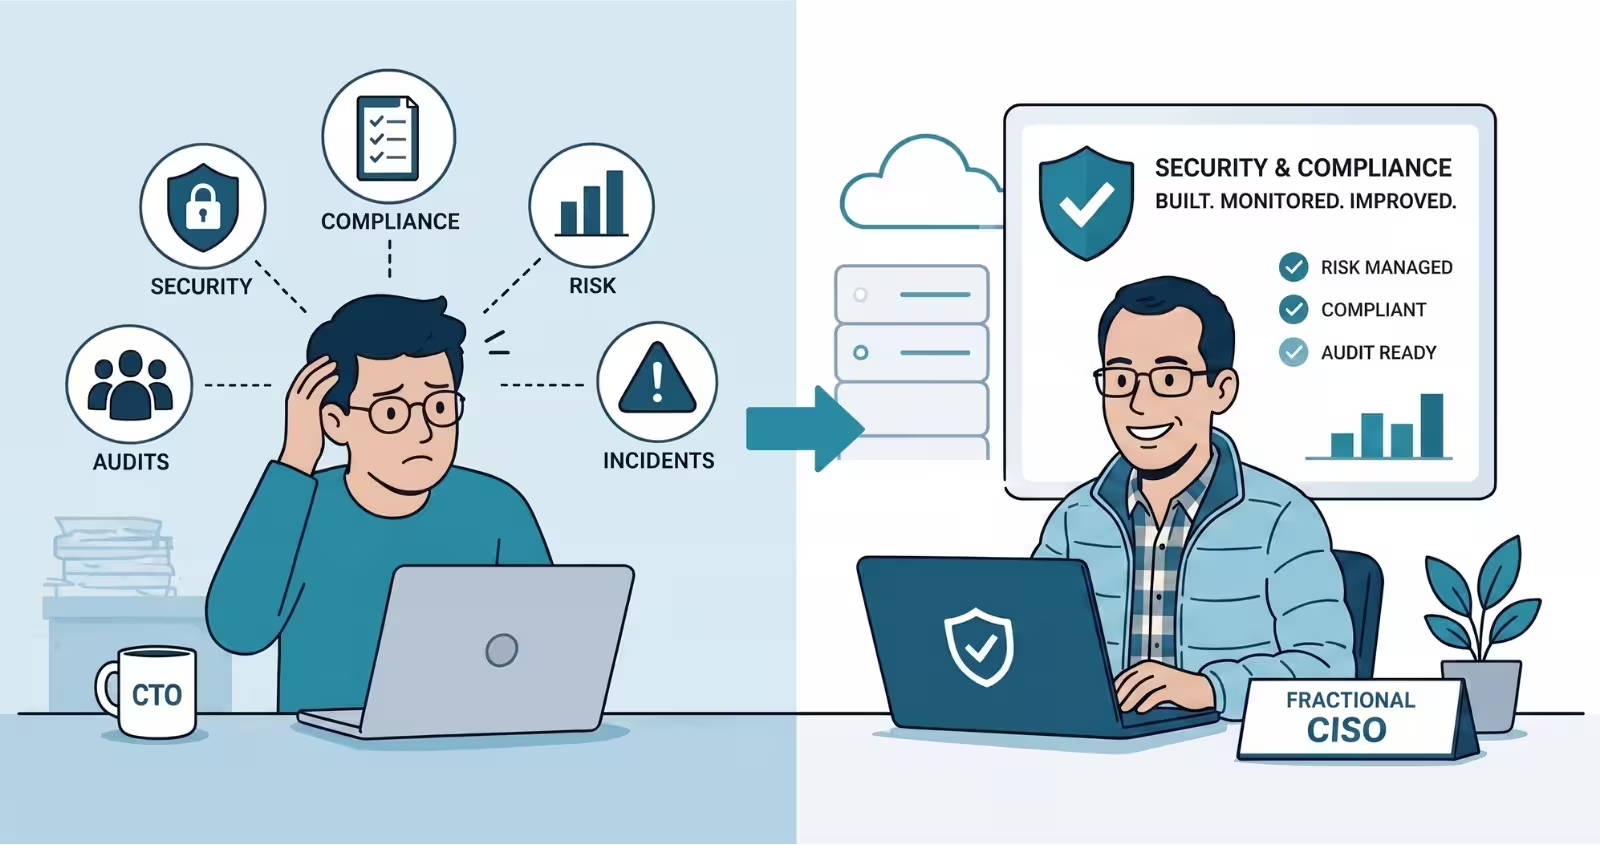
A two-panel illustration comparing a stressed CTO with many security concerns to a calm Fractional CISO who has streamlined security and compliance.

Fractional CISO for SaaS Companies: What the Role Actually Looks Like

Security leadership at most SaaS companies follows a predictable pattern. The CTO handles it. Not because they volunteered, but because nobody else...
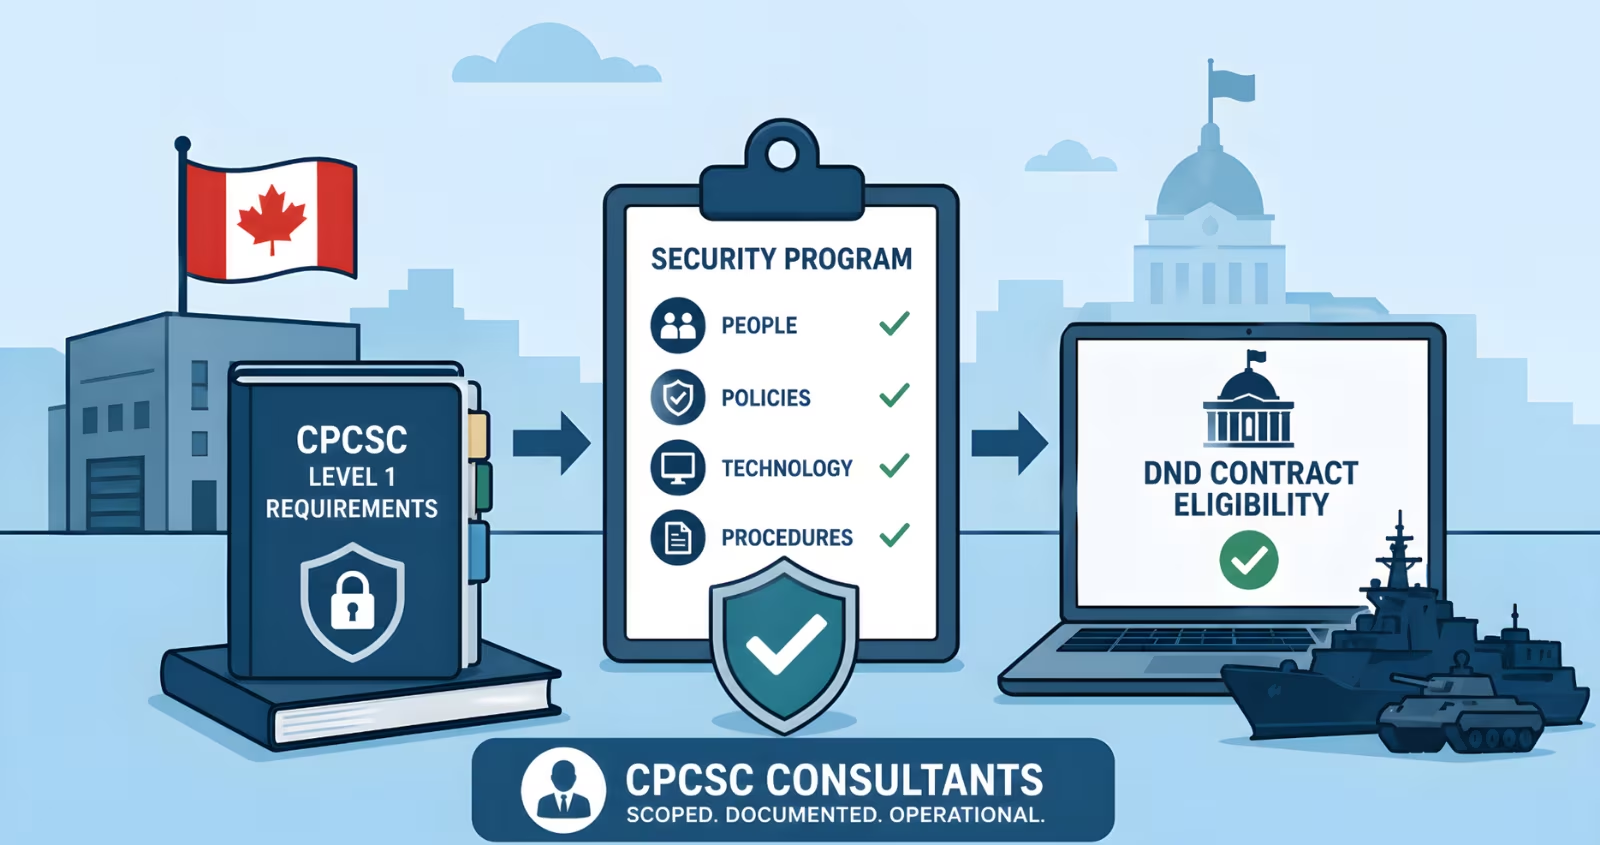
Flat vector illustration showing CPCSC Level 1 requirements turning into a structured security program, leading to DND contract eligibility, with Canadian flag, checklist, shield icon, and defense elements in a clean blue palette.

CPCSC Compliance Consulting for Defence Contractors

CPCSC Level 1 attestation becomes a procurement requirement for Department of National Defence contracts in April 2026. Companies that can't attest...
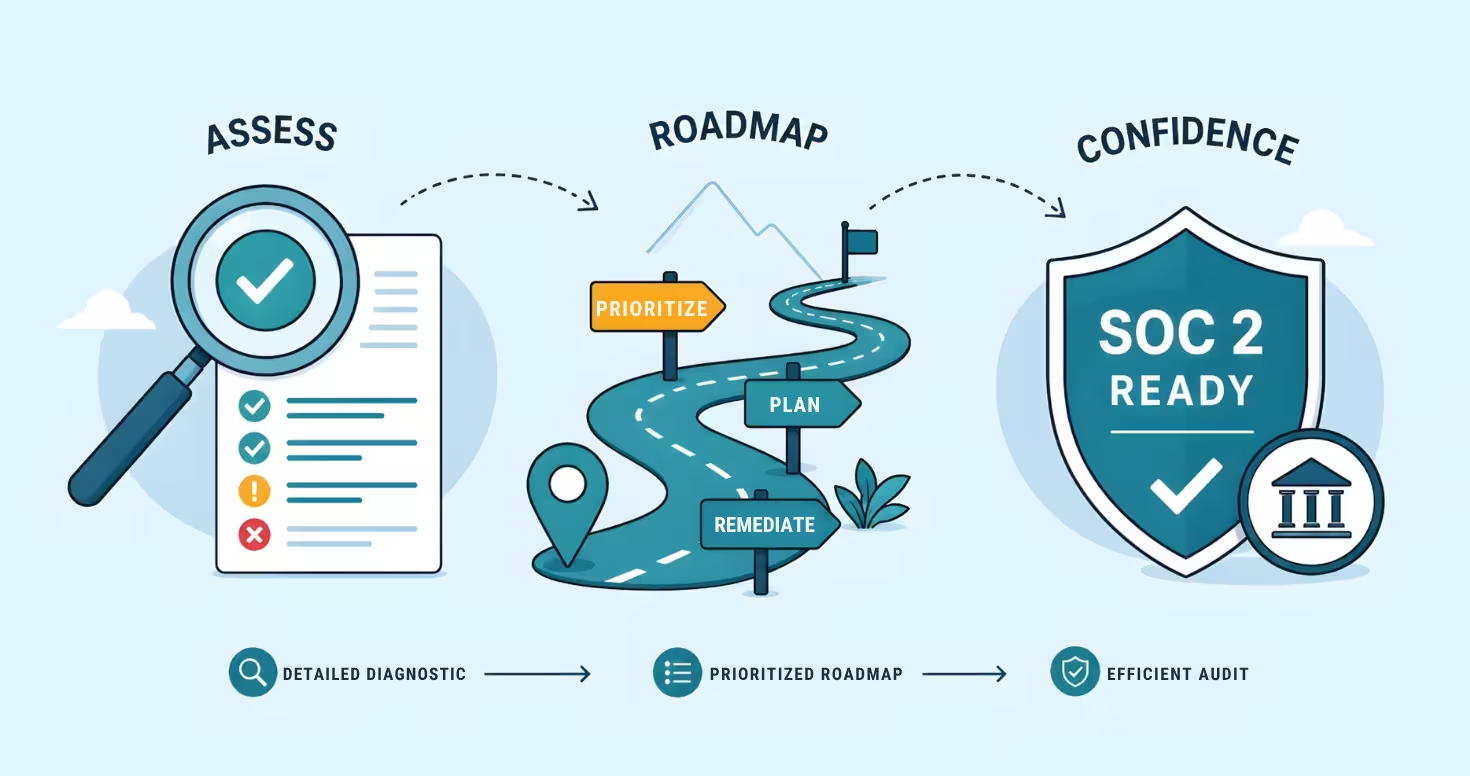
Flat illustration of SOC 2 readiness: a checklist under a magnifying glass (assess), a winding roadmap with prioritize/plan/remediate steps, and a shield labeled “SOC 2 Ready” (confidence), showing gap analysis and audit preparation.

What Does a SOC 2 Readiness Assessment Actually Include?

A SOC 2 readiness assessment is not the audit. It is the diagnostic step that tells a company exactly where it stands before committing budget and...
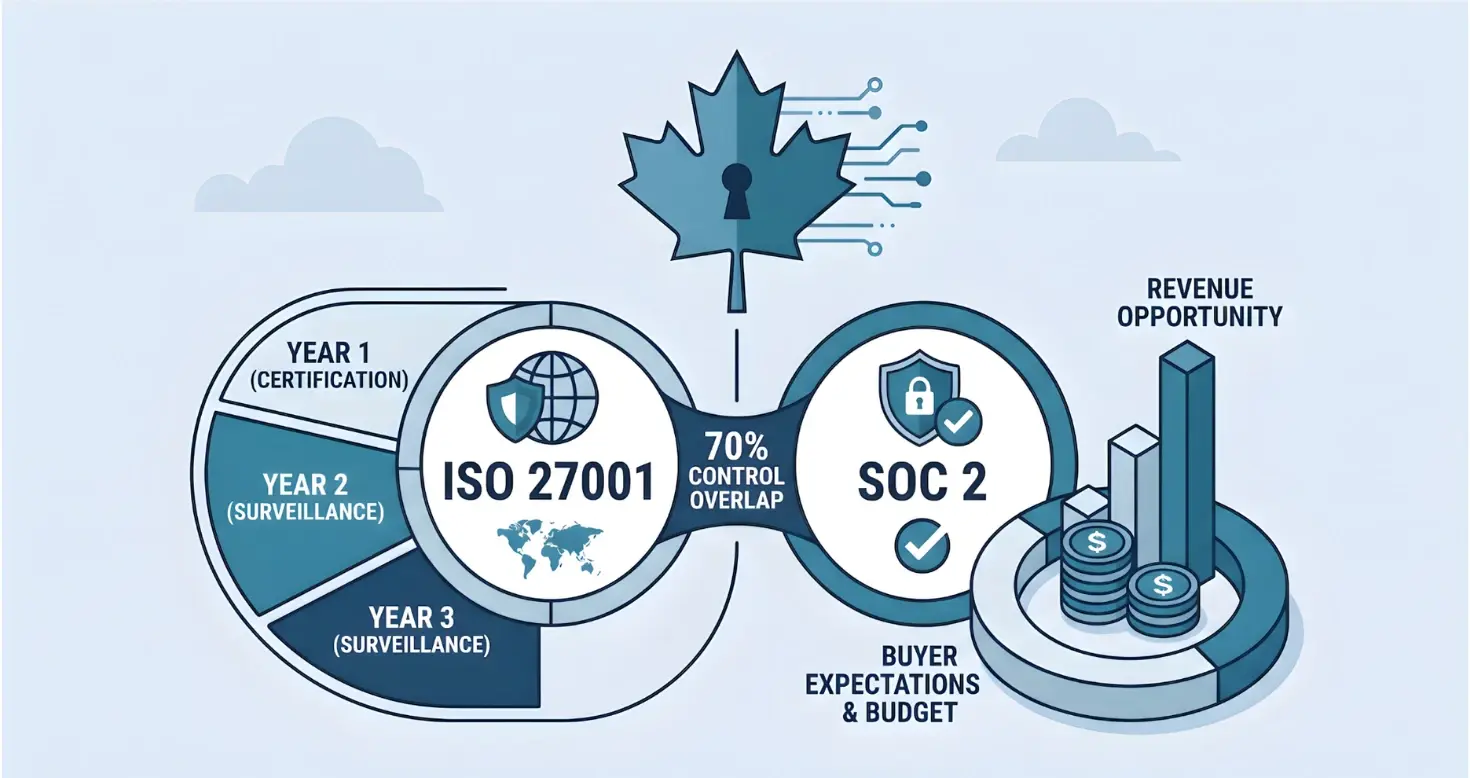
An infographic for Canadian SaaS, in blue vector style, showing how ISO 27001 and SOC 2 frameworks overlap by 70%. It details the 3-year ISO audit cycle and highlights "Revenue Opportunity" tied to "Buyer Expectations & Budget."

ISO 27001 Consultant in Canada: When It Makes Sense and What It Actually Takes

ISO 27001 certification gives you a one-to-two-page certificate. SOC 2 gives you a 40-to-50-page report describing every control, how it was tested,...
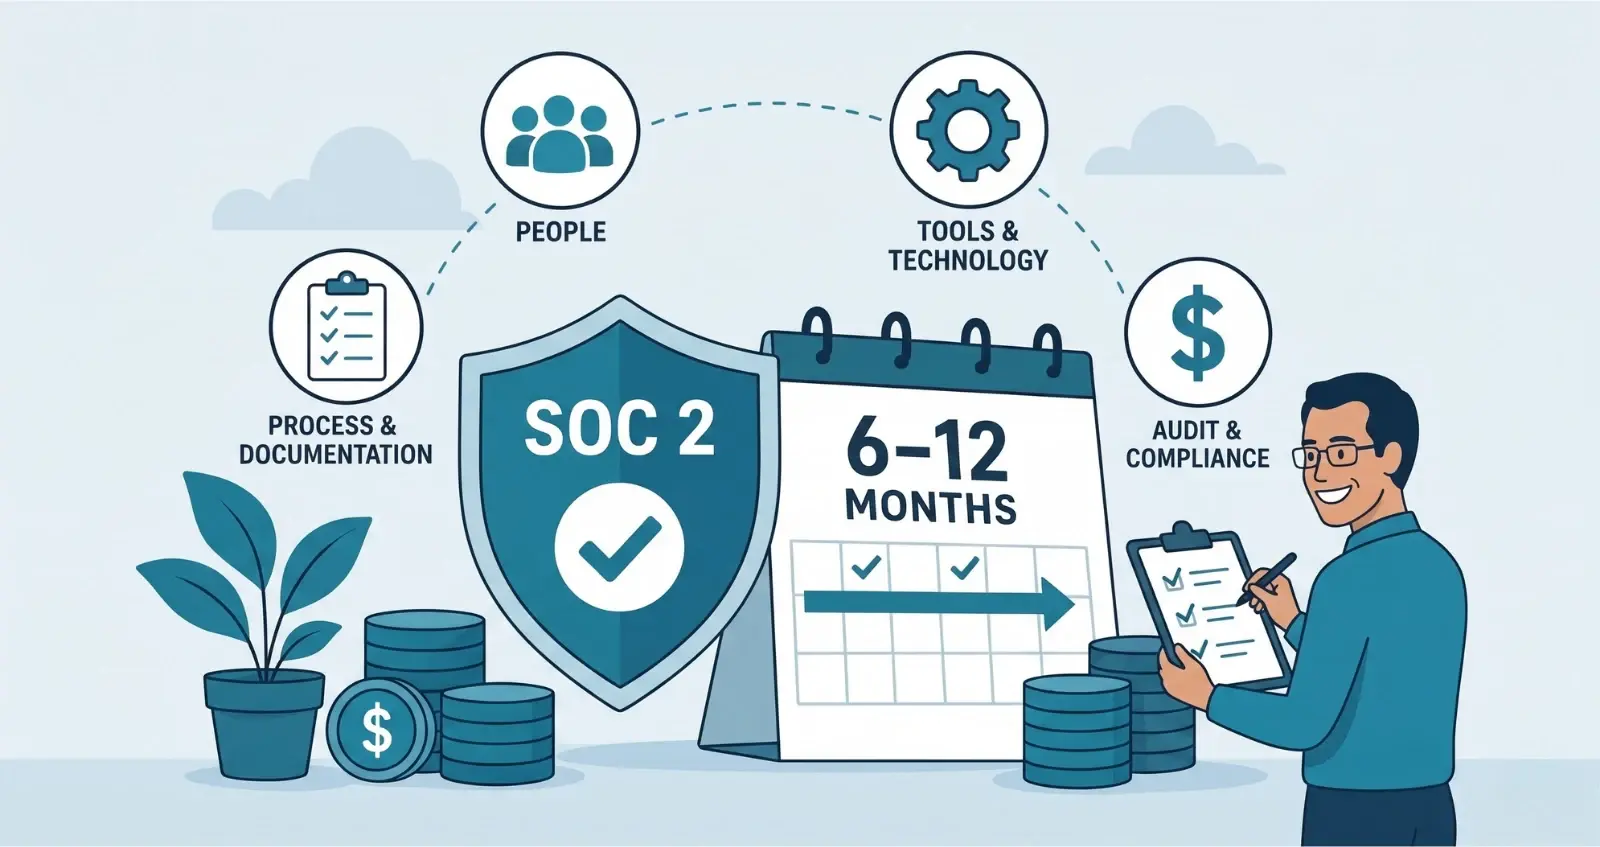
A vector infographic explaining SOC 2 compliance. It features icons for Process, People, Tools, and Audit linked to a shield. A calendar reads "6-12 MONTHS." A man with glasses holds a clipboard.

SOC 2 Implementation Cost and Timeline: What to Actually Budget

SOC 2 has four cost components. Most companies only budget for two of them, then get surprised by the rest halfway through the engagement.

Published...
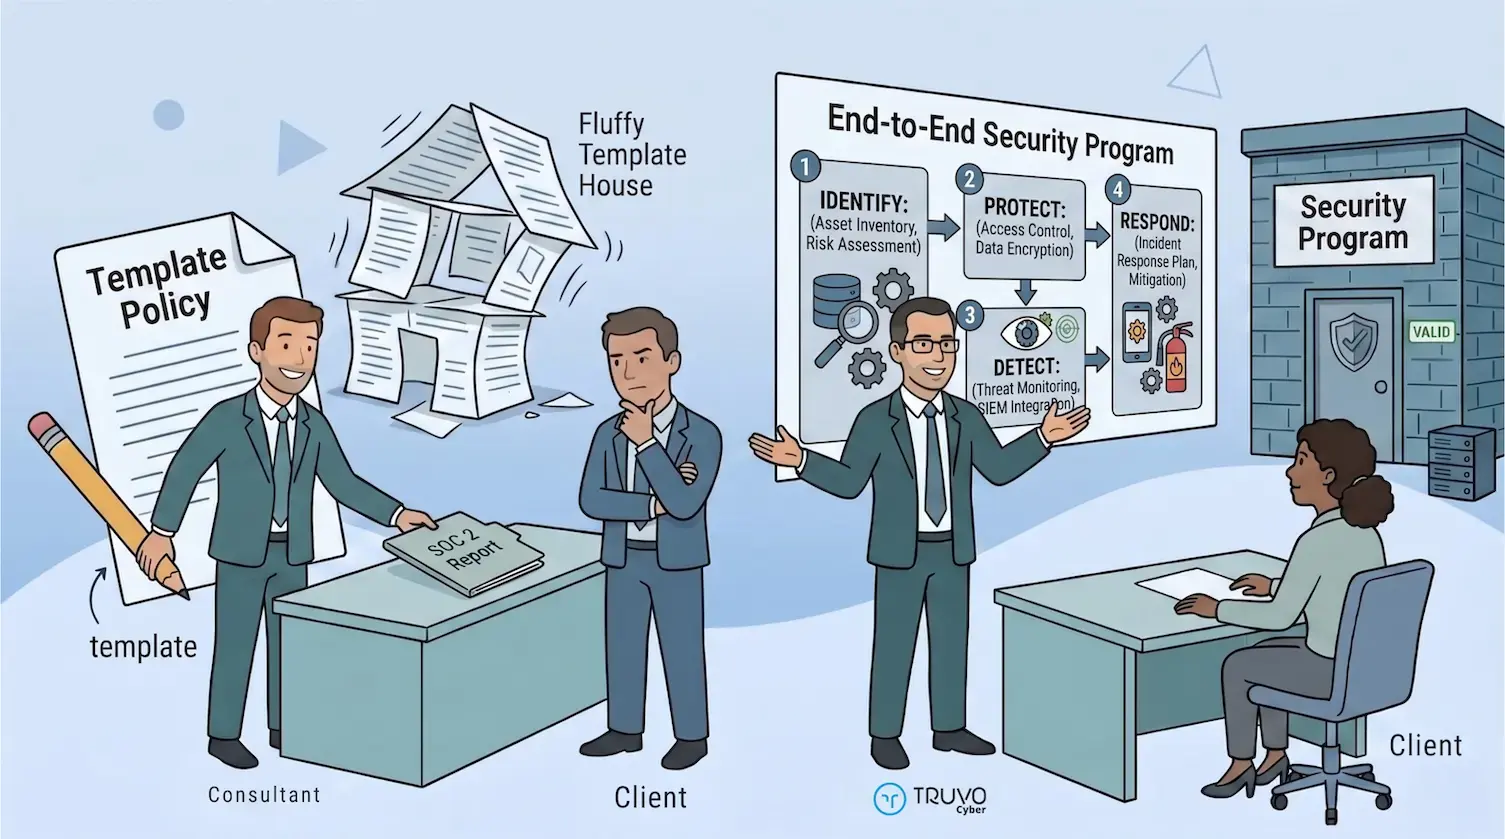
A comparison of two SOC 2 approaches. On the left, a "Consultant" offers a shaky "Fluffy Template House" to a skeptical client. On the right, a Truvo Cyber expert presents a solid "End-to-End Security Program" with Identify, Protect, Detect, and Respond phases to a satisfied client.

How to Choose a SOC 2 Consultant: A Checklist for SaaS Companies

The Two Types of SOC 2 Consultants

Platform-first firms compress the engagement into days or a few weeks. They take a policy template library, swap...
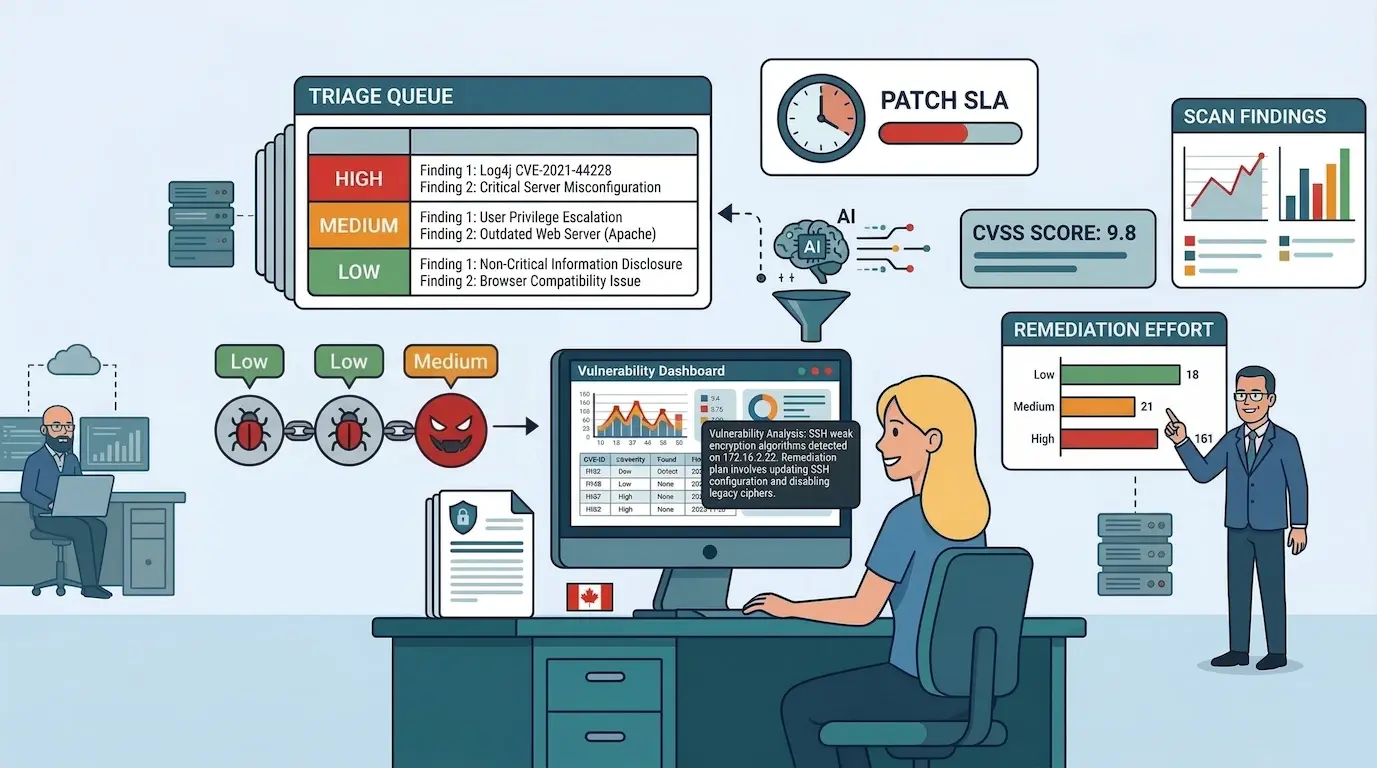
A cybersecurity operations infographic. A triage queue lists high, medium, and low priority findings like Log4j and weak server config. AI analyzes exploits from bugs (Low risk) to a malicious face (Medium). A dashboard displays a 9.8 CVSS score. Two analysts review the data near servers

What Project Glasswing Actually Means for Your Security Program

I have been thinking about what Anthropic's Project Glasswing announcement actually means for the clients we advise. The honest answer is that it...
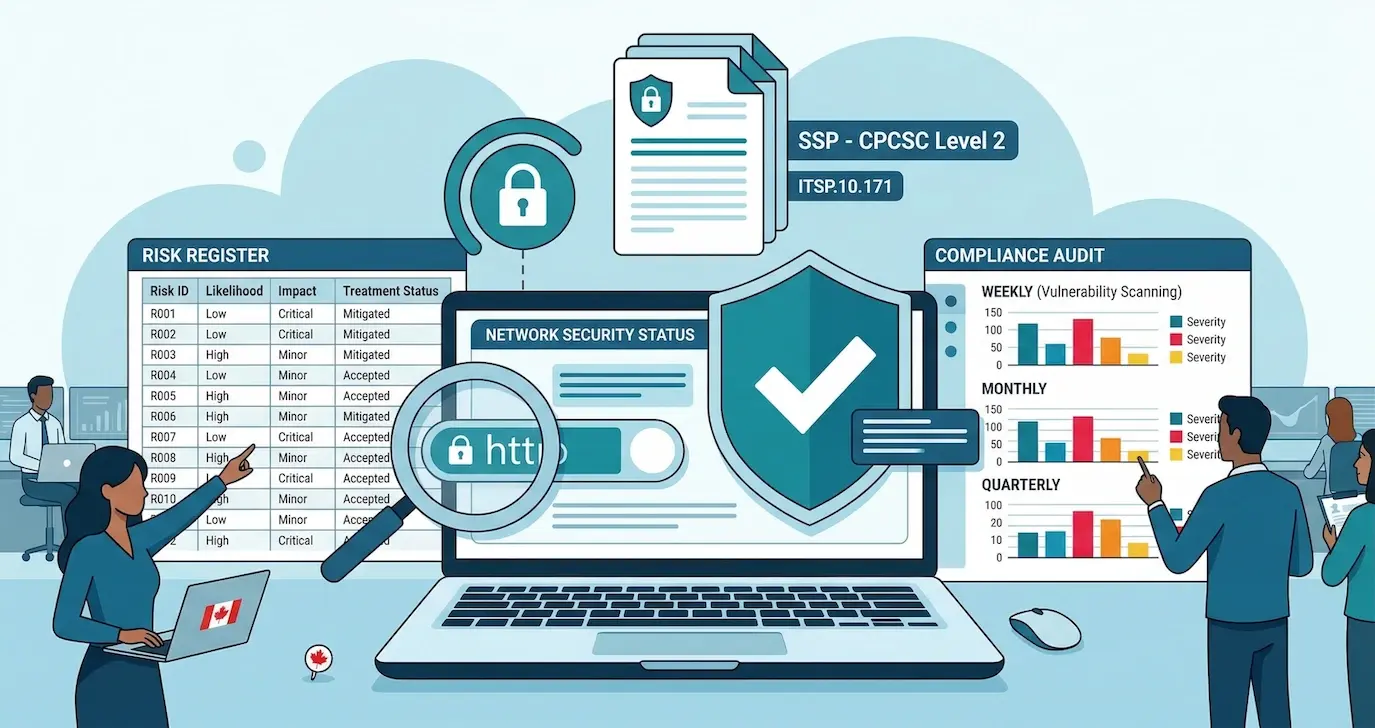
A professional illustration of a cybersecurity dashboard featuring a laptop, risk register, and compliance audit charts. People in an office manage data labeled "SSP - CPCSC Level 2" and "ITSP.10.171." Canadian flags and security icons emphasize a secure, national compliance environment.

Risk Assessment and Security Planning for ITSP.10.171

The majority of ITSP.10.171 control families deal with operational security: how you configure systems, manage access, protect data. The Risk...