SOC 2GRCISMSSecurity Reviews



Co-Founder & Principal Consultant, CISSP, CCSP
Former security architect for Bank of Canada and Payments Canada. 20+ years building compliance programs for critical infrastructure. Ali leads Truvo's SOC 2, ISO 27001, and CMMC engagements, bringing enterprise-grade security architecture to growing companies.
Follow on LinkedIn →
Like in any industry, cyber security and cybercrime is constantly evolving. To keep up, you need to remain familiar with upcoming trends and the...
As a startup navigating the complexities of data security, understanding SOC 2 compliance is essential. SOC 2 (System and Organization Controls 2) is...
New business reality is that companies must prioritize cybersecurity compliance to protect customer data and demonstrate their security posture. The...
For many SaaS companies, achieving SOC 2 compliance is a major milestone, a sign that they take security and customer trust seriously. But the real...
TL;DR: A SOC 2 Type 2 report is an independent audit that evaluates whether an organization's security controls are operating effectively over a...
Every compliance framework, SOC 2, ISO 27001, CMMC, HIPAA, asks the same fundamental question: does this organization have an effective security...
Ransomware attacks are among the most disruptive forms of cybercrime, locking businesses out of their own data and demanding ransom for its release....
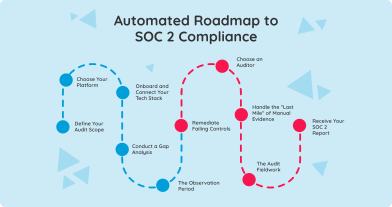
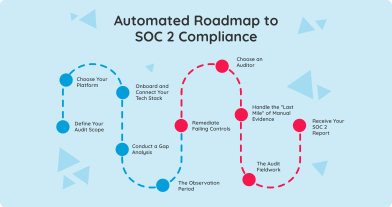
Every SOC 2 roadmap on the internet reads the same way: pick a platform, connect your integrations, run the gap analysis, remediate, audit. Five...
SOC 2 is an attestation report a licensed CPA firm issues against the AICPA's Trust Services Criteria, describing whether a service organization's...
SOC 2 CSOCs (Complementary Subservice Organization Controls) are third-party vendor controls your system depends on but does not operate. You address...
ISO/IEC 42001:2023 is the world's first international standard for managing artificial...
The EU AI Act entered into force on August 1, 2024, making it the first comprehensive AI...
Implementing ISO/IEC 42001 is a strategic necessity for AI SaaS...
For AI-driven SaaS companies, compliance with ISO/IEC 42001 is...
Six months after buying Drata, Vanta, Secureframe, or any other compliance automation platform, a company realizes the dashboard is half-populated,...
In cybersecurity, what you don’t know can hurt you. An unmonitored system is a black box where attackers can operate undetected for weeks or months. ...
AI dominated the conversation at this 2025's Web Summit, and for good...
As of November 2025, CMMC is no longer a concept the DoD is considering. It is a contract requirement. Contracting officers are now including CMMC...
Achieving SOC 2 compliance is a major milestone for SaaS companies and service providers handling sensitive customer data. Yet, for many startups and...
ISO 42001 is the first international standard for AI management systems. Implementing it means building an Artificial Intelligence Management System...
ISO 27001 and ISO 42001 share roughly 60-70% of their controls but govern different risks. ISO 27001 protects information assets through an...
Drata and Vanta are the two most widely adopted SOC 2 compliance automation platforms. Both connect to your cloud, identity, and HR systems to...
As artificial intelligence (AI) rapidly embeds itself into core business processes, from customer support to code generation, enterprises face a...
Vanta, Drata, Secureframe, and Scrut have all added dedicated ISO 42001 framework support. All four automate evidence...
Both Drata and Vanta offer dedicated ISO 42001 framework support with automated evidence collection, control cross-mapping to ISO...