SOC 2



Co-Founder & Principal Consultant, CISSP, CCSP
Former security architect for Bank of Canada and Payments Canada. 20+ years building compliance programs for critical infrastructure. Ali leads Truvo's SOC 2, ISO 27001, and CMMC engagements, bringing enterprise-grade security architecture to growing companies.
Follow on LinkedIn →
SOC 2 CC5.1 requires an organization to select and develop control activities that reduce its risks to an acceptable level, choosing each control...
SOC 2 CC2.3 requires an organization to communicate with external parties about matters that affect how its internal control operates, and to give...
SOC 2 CC3.1 requires an entity to state its objectives clearly enough that the risks to those objectives can be identified and assessed. It opens the...
SOC 2 CC3.2 requires an entity to identify risks to its objectives across the whole organization and to analyze them well enough to decide how each...
SOC 2 CC1.4 requires an organization to attract, develop, and retain people who are competent to carry out their responsibilities, and to hold...
SOC 2 CC2.1 requires an organization to obtain or generate and use relevant, quality information so that its internal controls can function. It opens...
SOC 2 CC1.3 requires management, with board oversight, to set up the organizational structures, reporting lines, and authorities the business needs...
SOC 2 CC1.1 requires an organization to demonstrate a commitment to integrity and ethical values, starting with how the board and management behave...
SOC 2 CC4.2 requires an organization to evaluate the deficiencies its monitoring turns up and communicate them, in a timely way, to the people who...
SOC 2 CC4.1 requires an organization to select, develop, and run a mix of ongoing and separate evaluations to confirm its internal controls are...
SOC 2 CC6.4 requires that physical access to facilities and protected information assets is restricted to authorized personnel. It sits in the CC6...
SOC 2 CC9.2 is the vendor and business partner risk criterion: it requires an organization to assess and manage the risks that come from the third...
SOC 2 CC9.1 is the risk mitigation criterion for business disruptions: it requires an organization to identify, select, and develop activities that...
SOC 2 CC7.2 is the security monitoring criterion in the Trust Services Criteria: it requires an organization to monitor its systems for anomalies and...
SOC 2 CC7.1 is where the vulnerability management program lives inside the Trust Services Criteria: it requires an organization to detect...
SOC 2 CC6.3 is where role design meets audit evidence: it requires that access to protected information assets is authorized, modified, or removed...
SOC 2 CC6.2 is the credential lifecycle criterion in the Trust Services Criteria: it requires an organization to register and authorize new users...
SOC 2 CC8.1 is the change management criterion: the single criterion in the CC8 series, covering how changes to infrastructure, data, software, and...
GRC in cyber security stands for governance, risk, and compliance: the discipline of directing a security program (governance), identifying and...
A vendor risk assessment is the structured evaluation of a vendor's security and compliance posture, scaled to the access and data that vendor holds....
Security architecture is the practice of understanding a system component by component and connection by connection. In practice it comes down to two...
A security architecture diagram is a boxes-and-arrows drawing of a system: boxes for the key components, arrows for the data flows or network flows...
Advice on security architecture and design should come from someone with a deep understanding of cybersecurity practice: ideally ten or more years in...
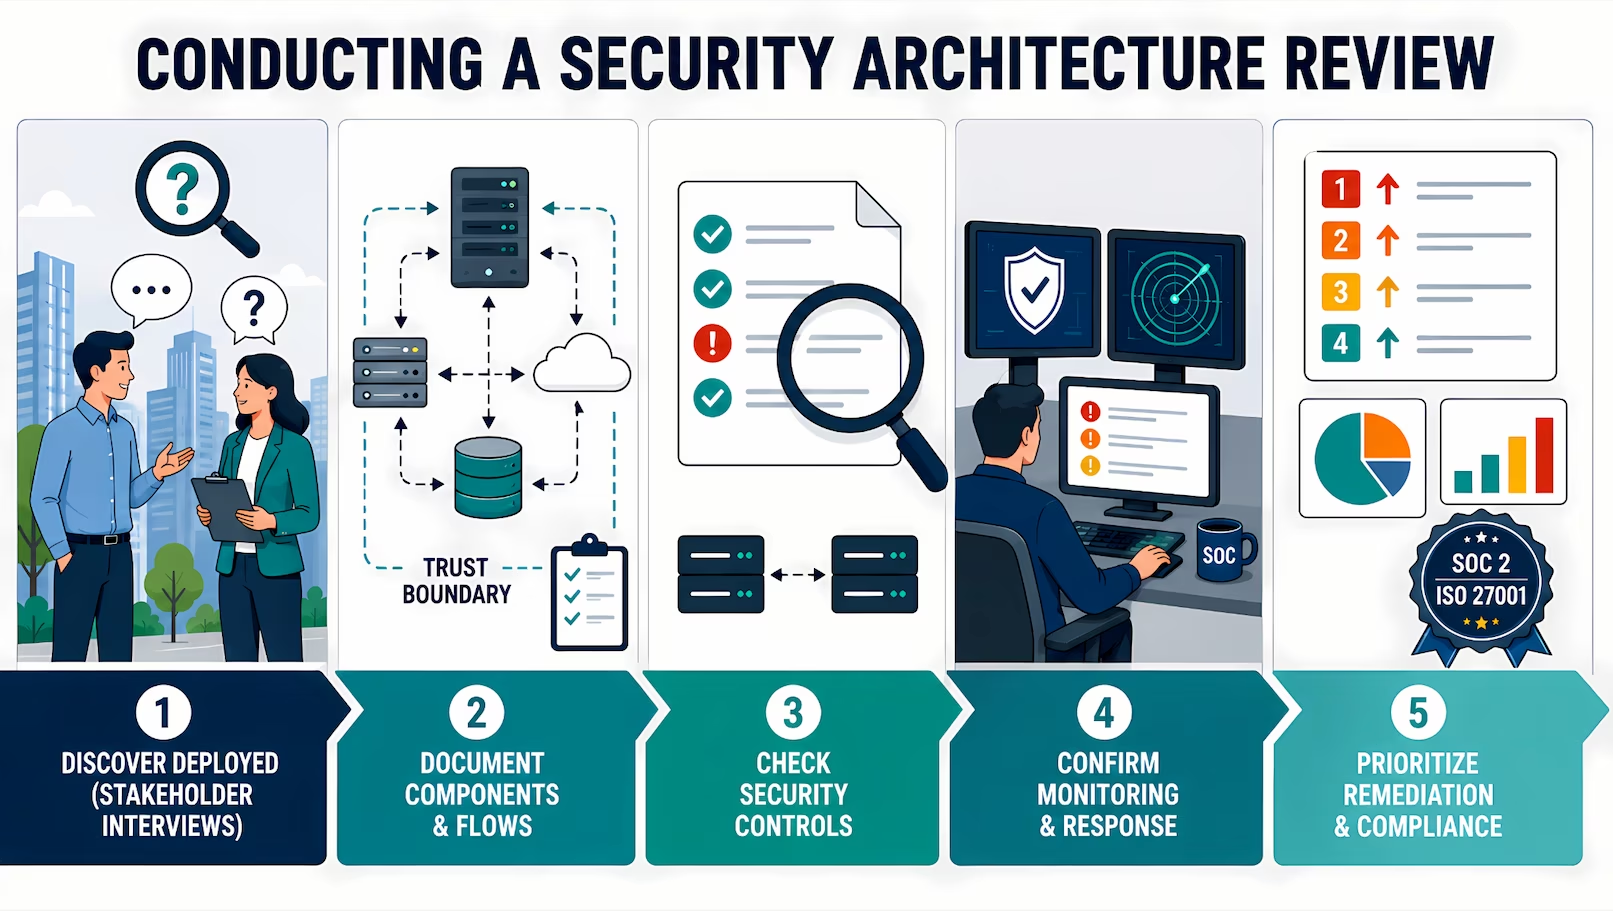
A security architecture review is a structured walk through a system's components and connections, checking each against security best practices and...
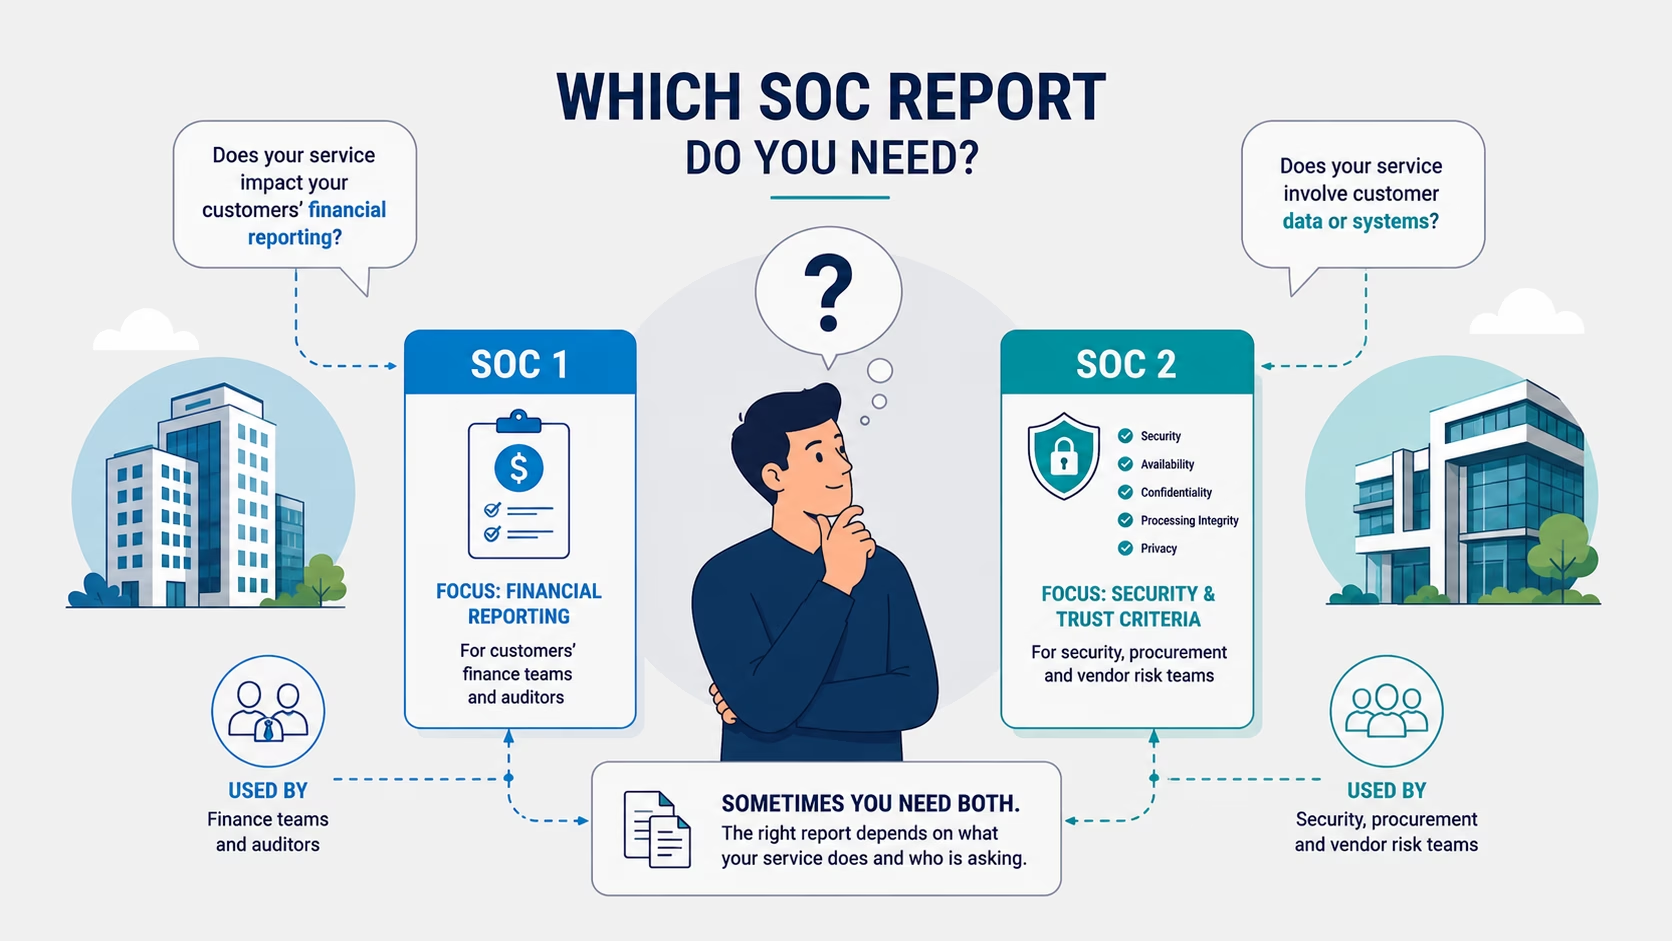
A SOC 1 report covers the controls at a service organization that are relevant to its customers' financial reporting, known as internal control over...
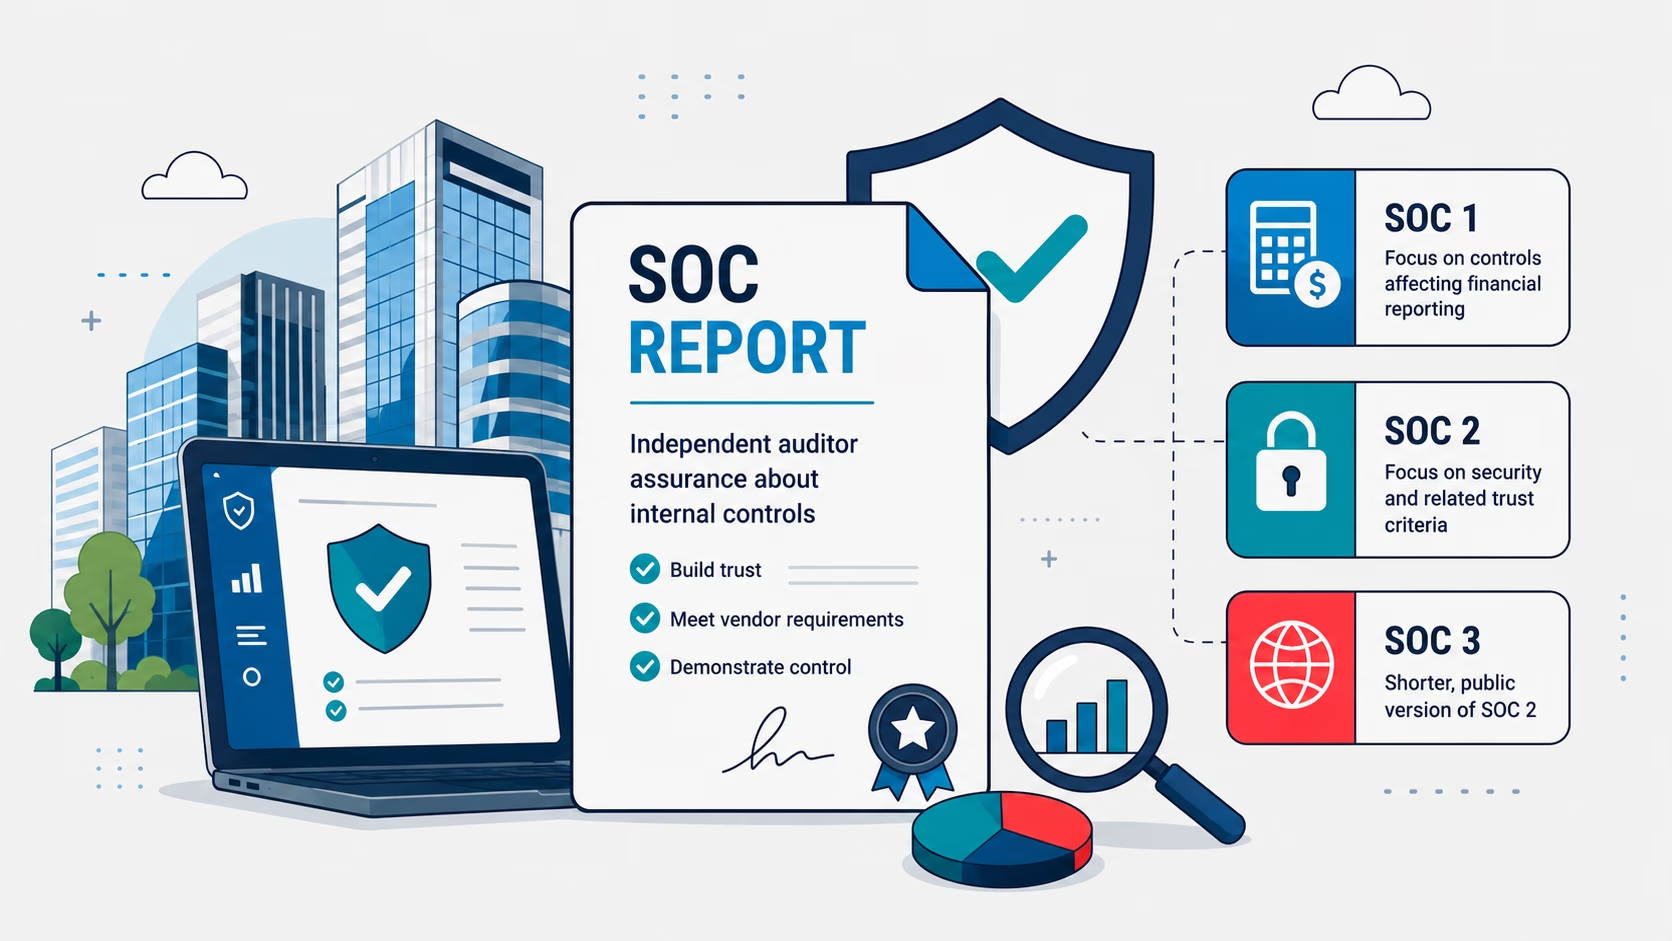
A SOC report (System and Organization Controls report) is an independent auditor's attestation report on a service organization's controls, issued by...
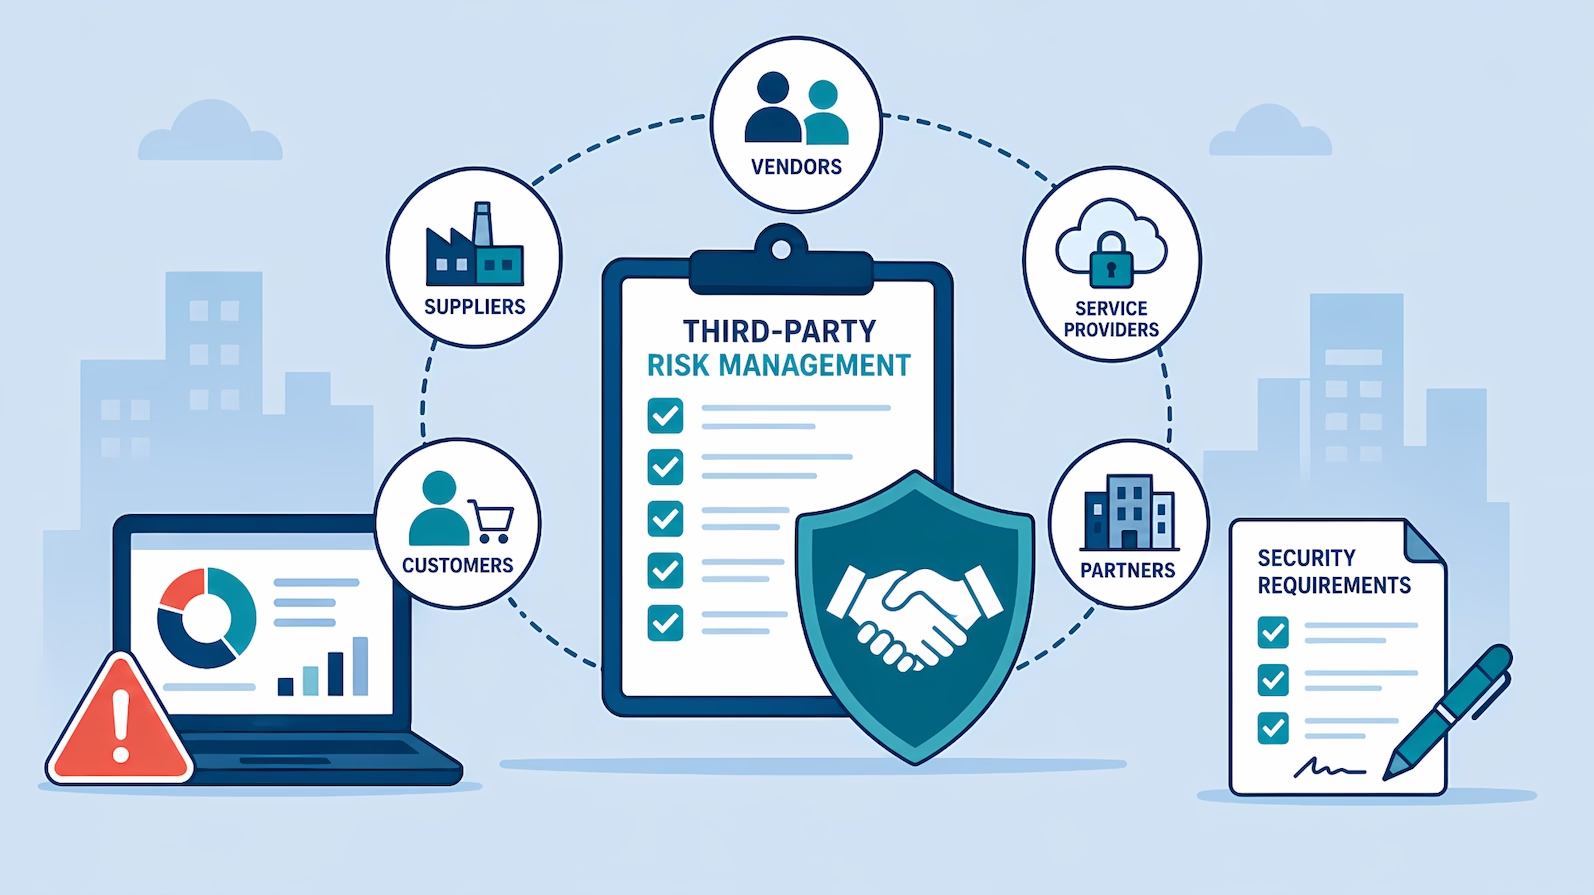
Third party risk management (TPRM) is the discipline of identifying, assessing, and controlling the risks that come from the external organizations a...
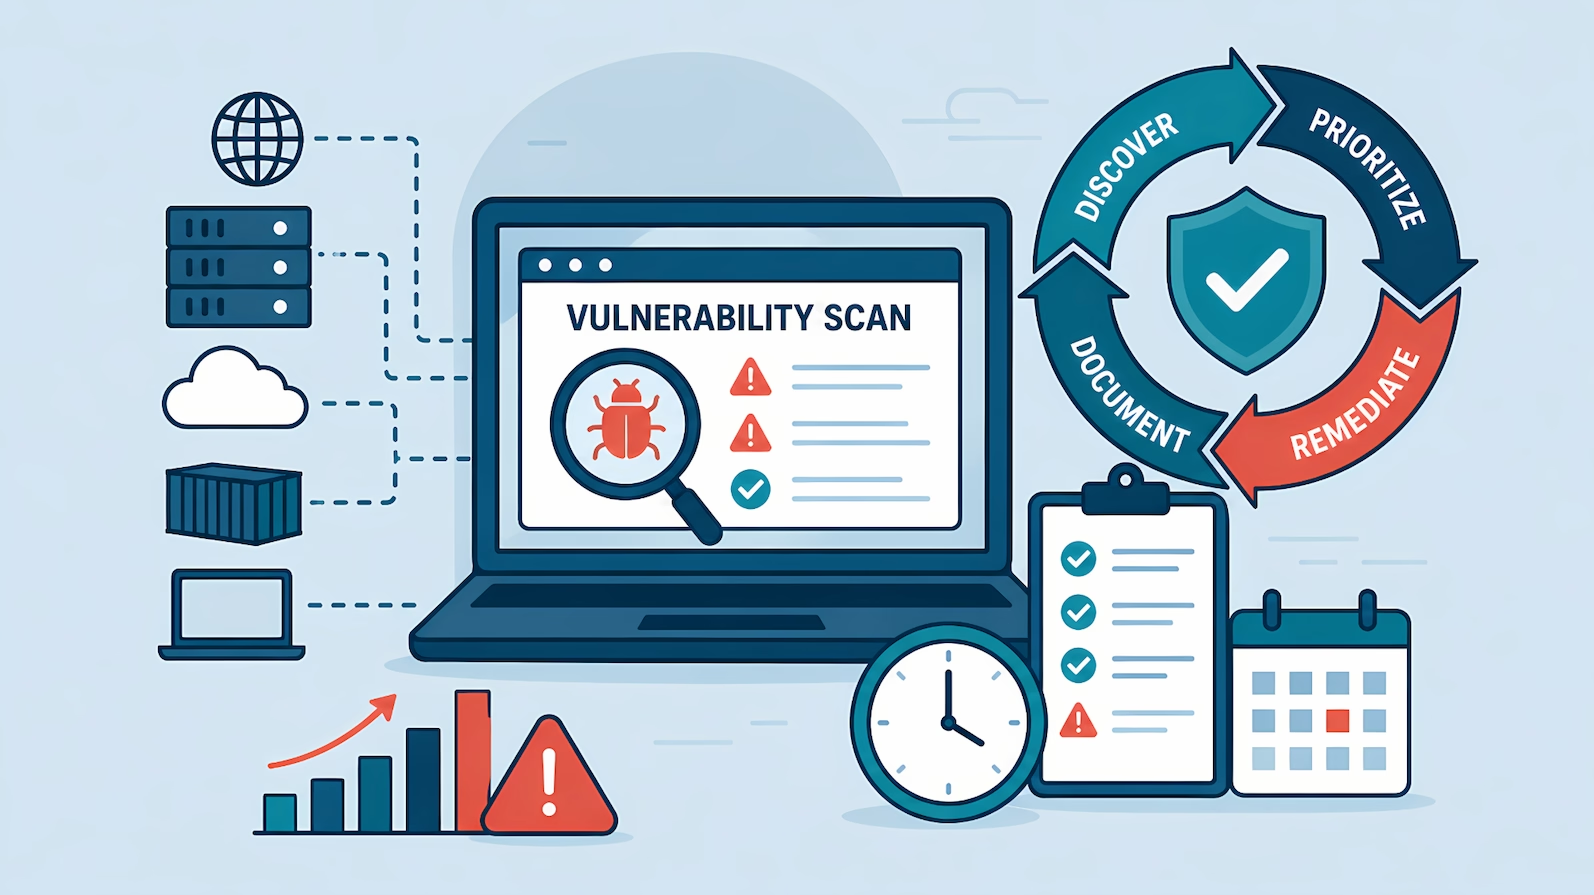
A vulnerability scan is an automated check that compares systems, software, and configurations against a database of known security weaknesses and...
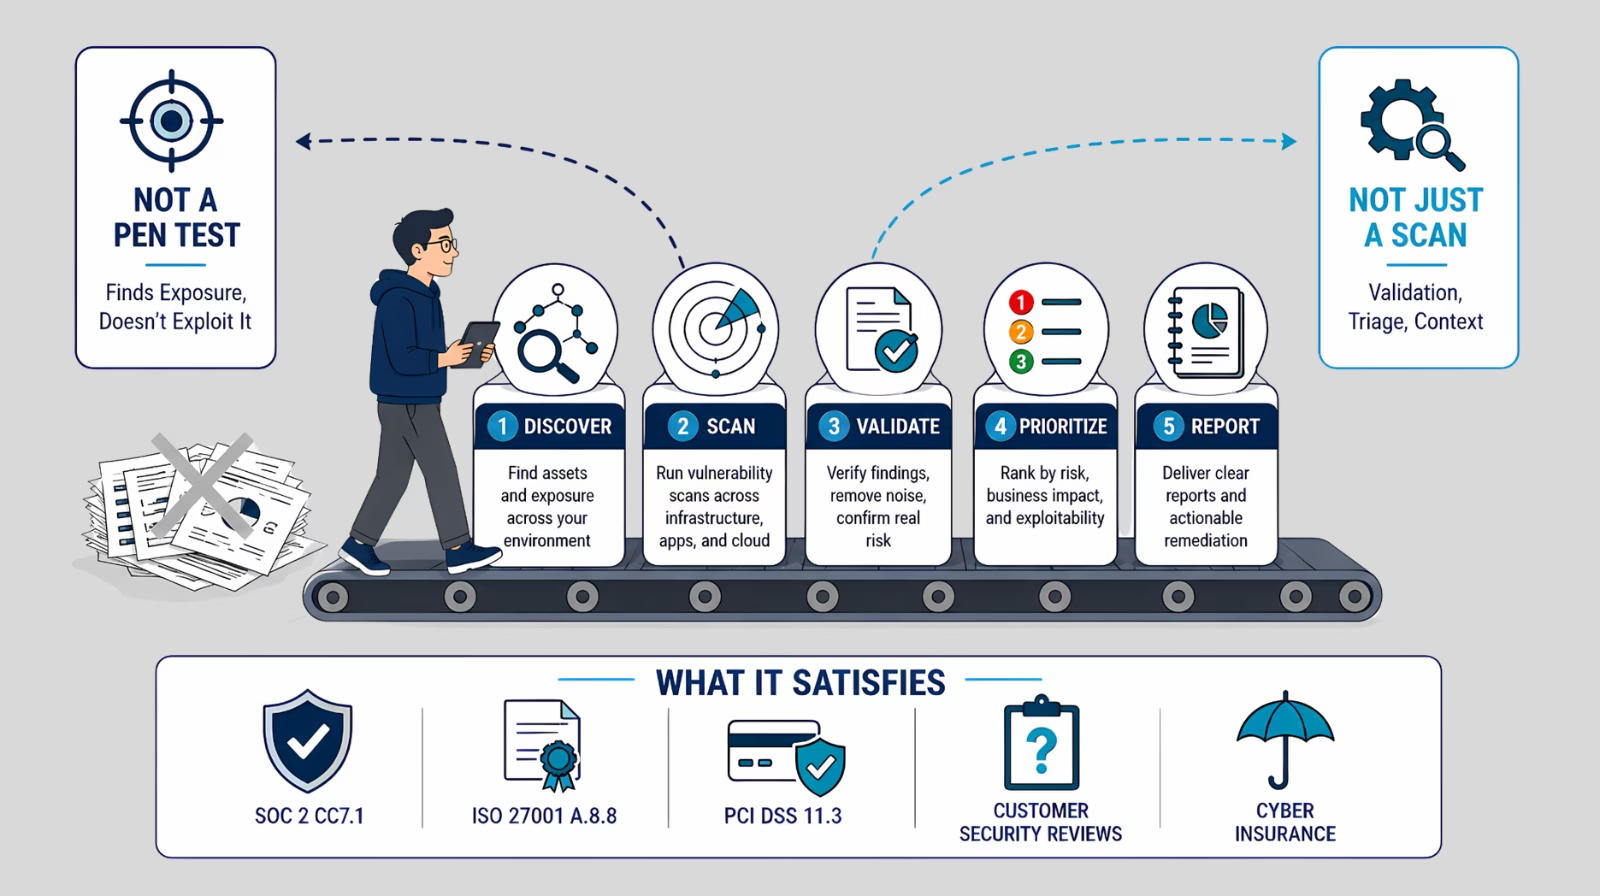
Vulnerability assessment services are engagements where a third party inventories an environment, scans it for known security weaknesses, validates...
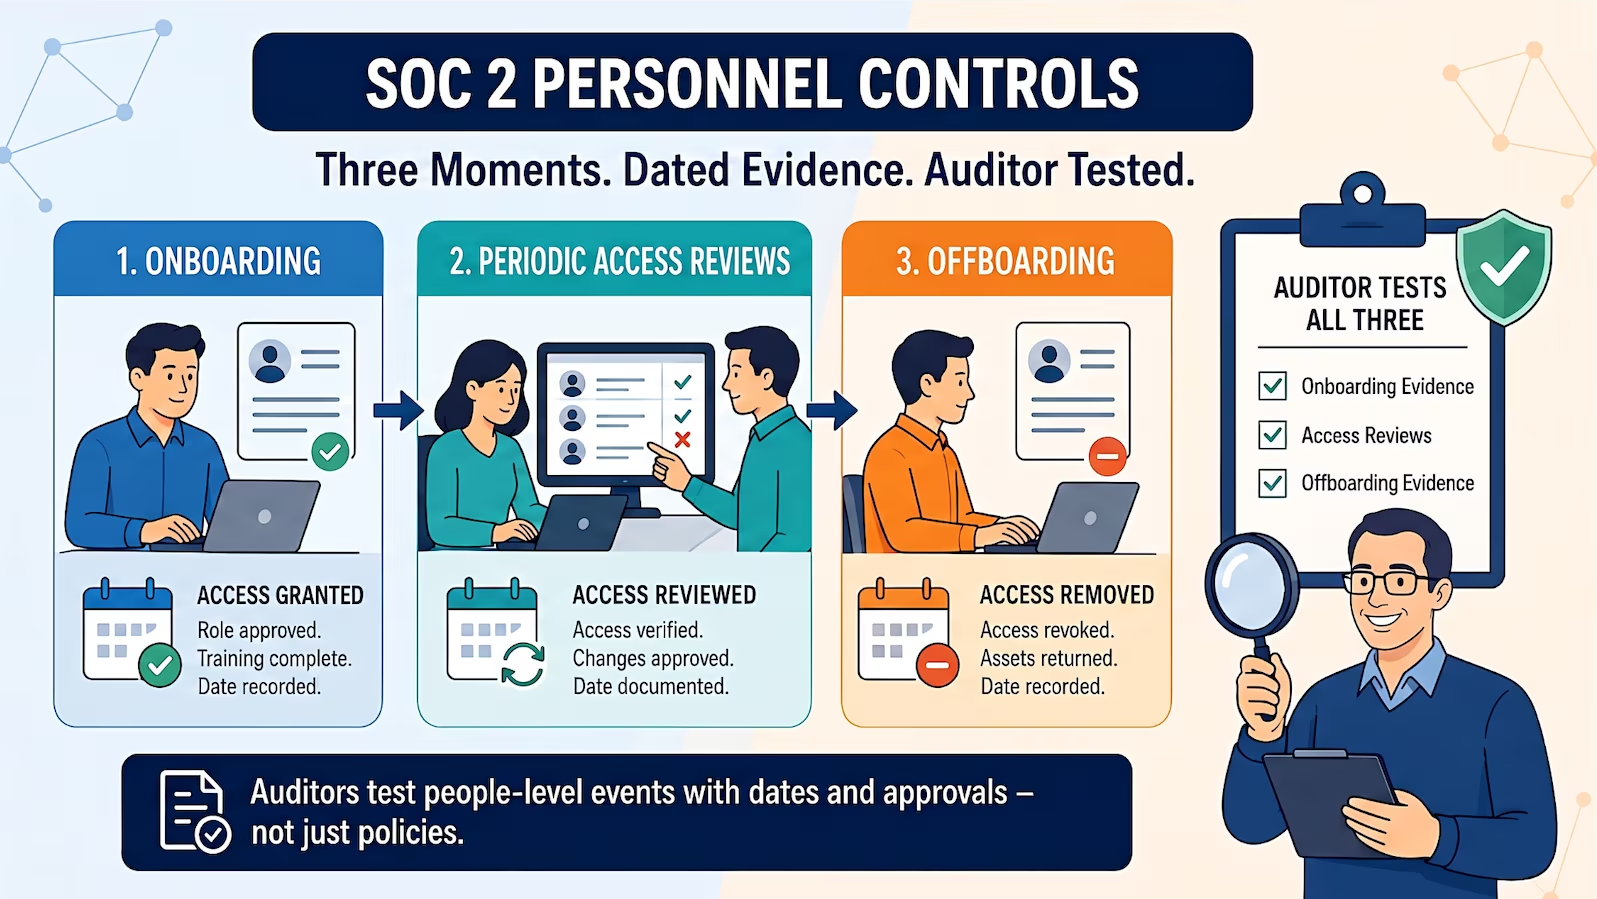
SOC 2 personnel controls come down to three moments: onboarding on day one, the periodic user access review that confirms access still matches the...