


Ali Aleali
Co-Founder & Principal Consultant, CISSP, CCSP
Former security architect for Bank of Canada and Payments Canada. 20+ years building compliance programs for critical infrastructure. Ali leads Truvo's SOC 2, ISO 27001, and CMMC engagements, bringing enterprise-grade security architecture to growing companies.
Follow on LinkedIn →
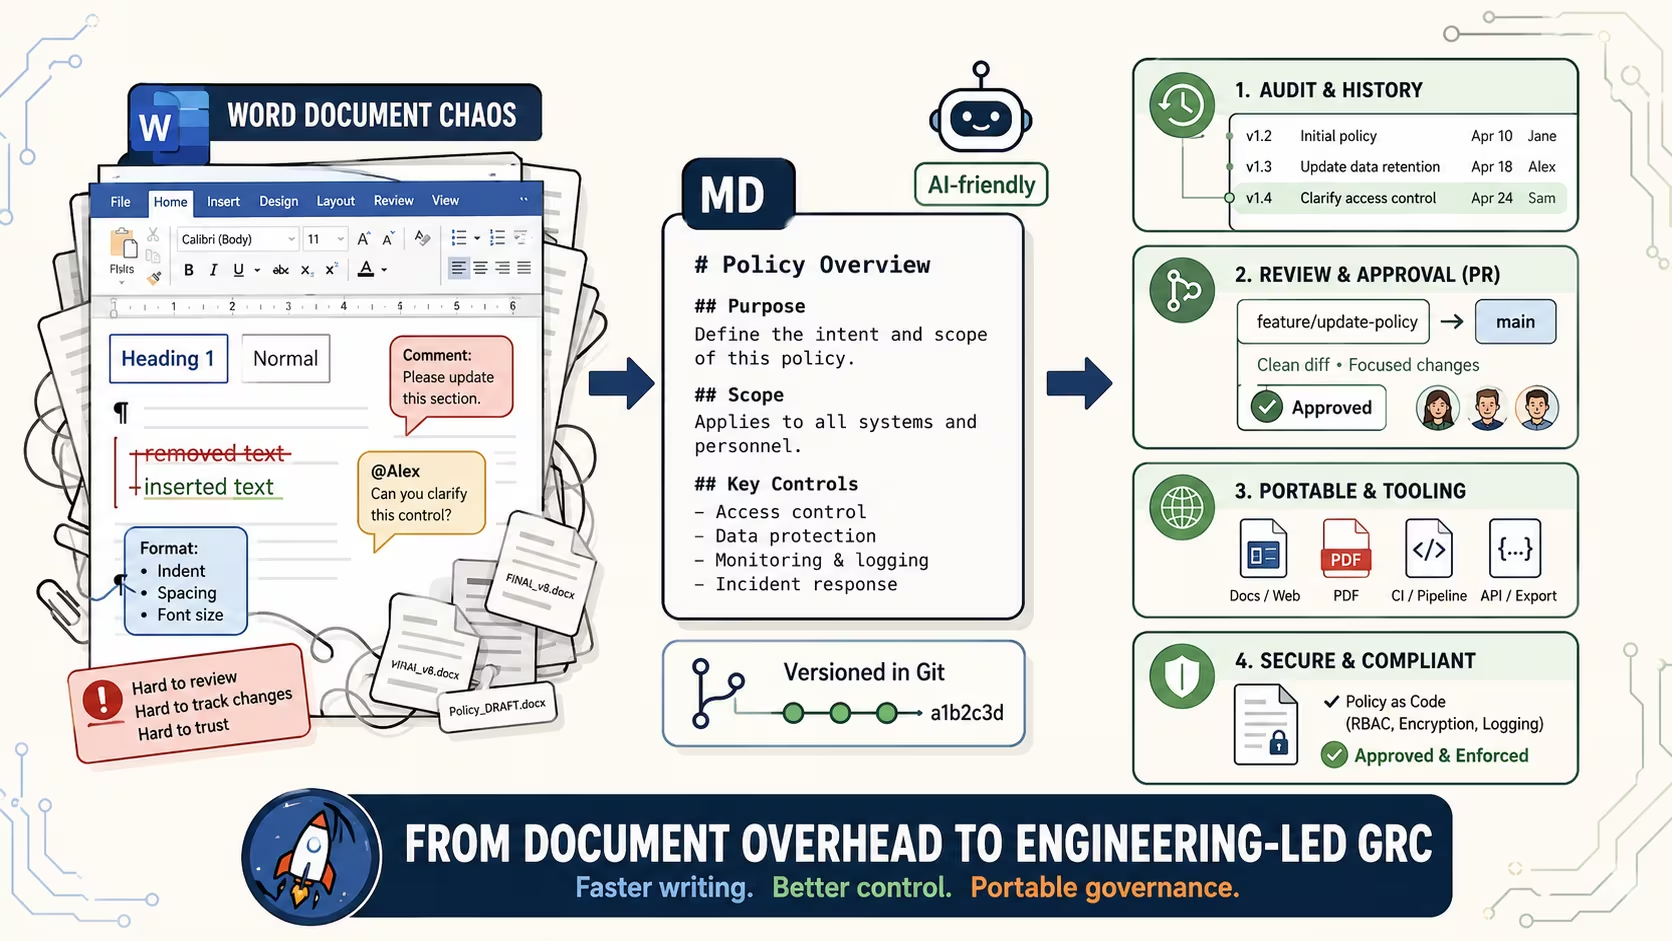
Down With .docx, Long Live .md: Why We Switched to Markdown for Everything
In 2026, documentation needs to be easily readable by humans and AI. Plain text is too plain. You need headings, bold, lists, and tables to make a...
GRC Platform vs GRC Engineering: When You Need Both
We've seen all to often. organizations that have been running a GRC platform for six to twelve months: the dashboard is green, the audit prep feels...
GRC Compliance for On-Prem and Hybrid Environments
GRC platforms automate compliance evidence collection for cloud-native infrastructure. Connect your AWS account, hook in your identity provider, link...
What Vanta and Drata Can't Automate
Companies that implement Vanta or Drata expecting near-complete automation of their SOC 2 compliance work tend to hit the same wall. The integrations...
Your GRC Platform Is Green. Your Compliance is Red.
The GRC platform dashboard is green. Every automated test passes. The readiness score reads somewhere in the nineties. The team spent three months...
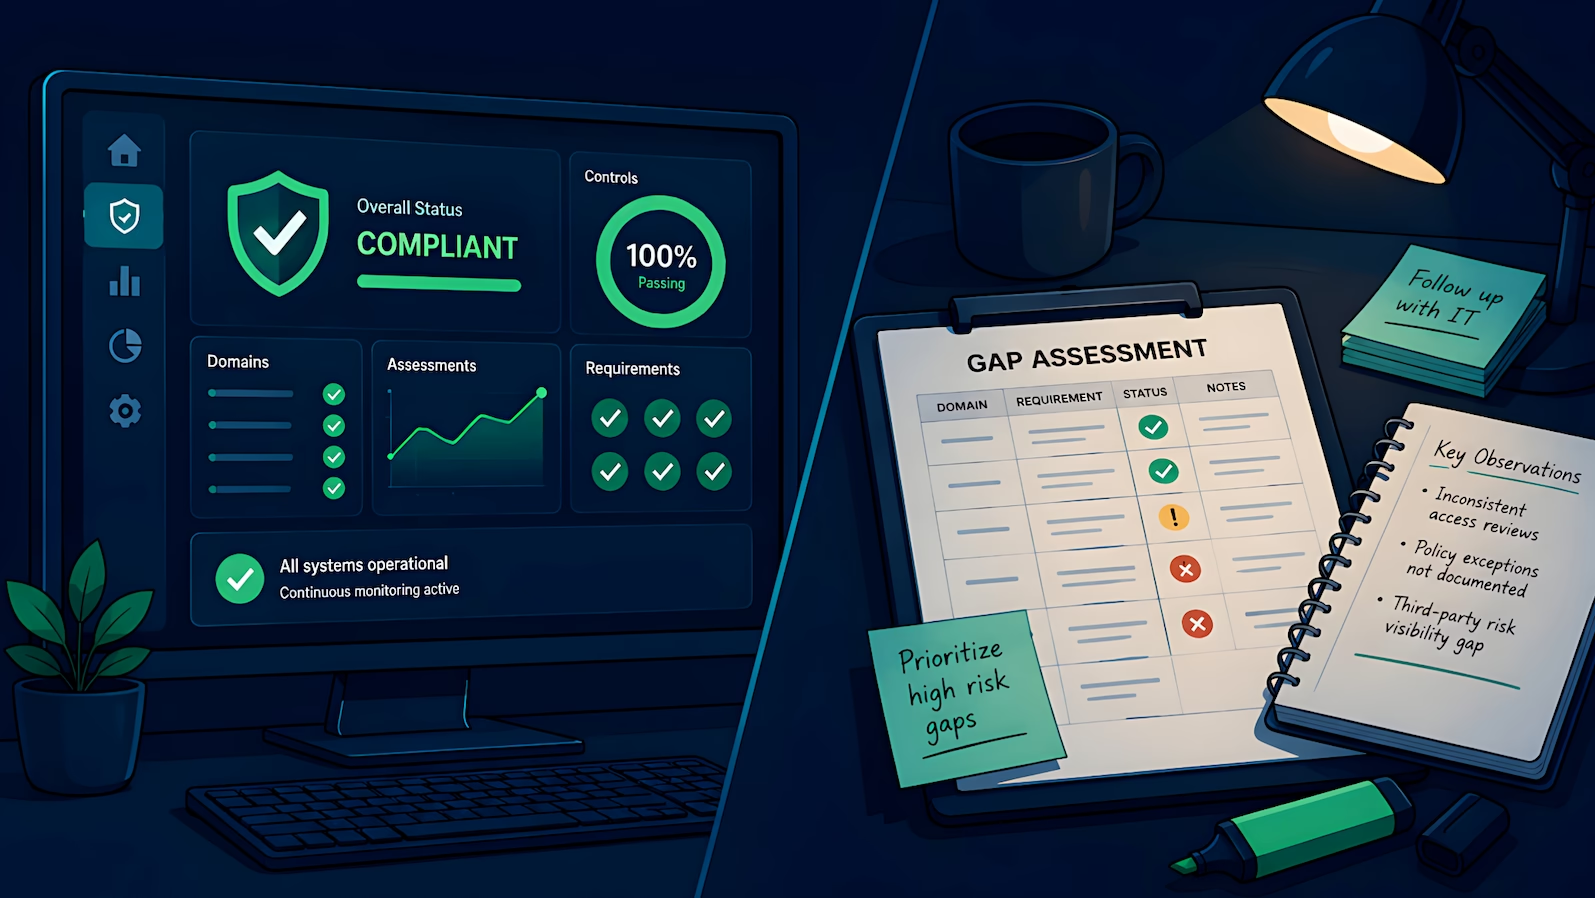
What a SOC 2 Readiness Assessment Includes (With or Without Drata)
A SOC 2 readiness assessment and Drata solve different problems. The assessment tells you whether your control environment is adequate before the...
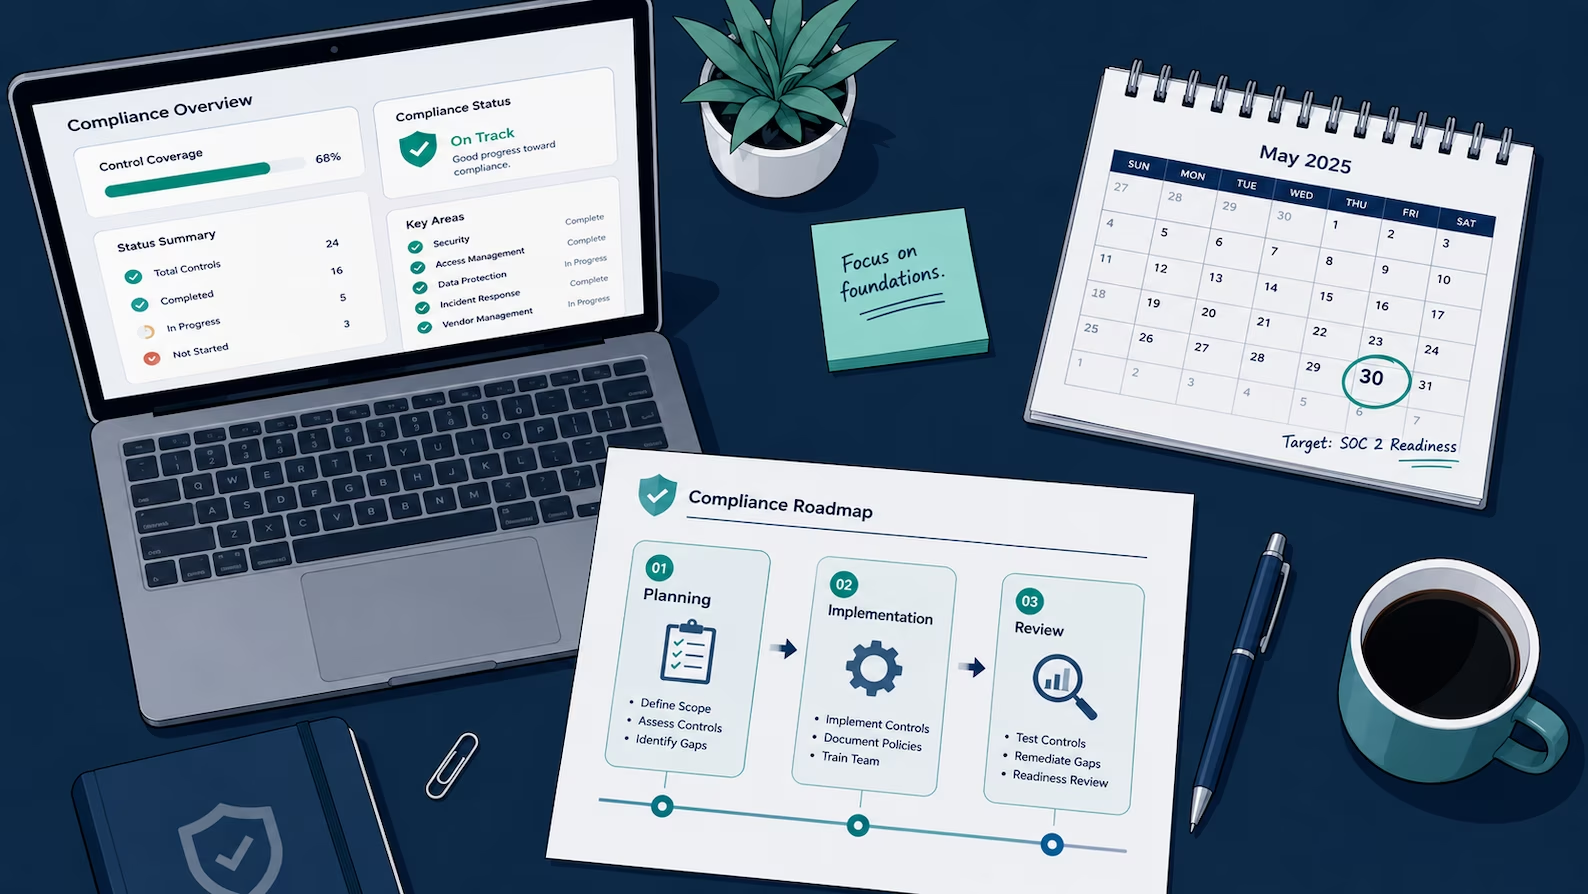
How to Get SOC 2: Timeline, Cost, and First Steps
If you've already read SOC 2 Explained: What It Is and Why Enterprises Require It and you're ready to move, this is the operational post for teams of...
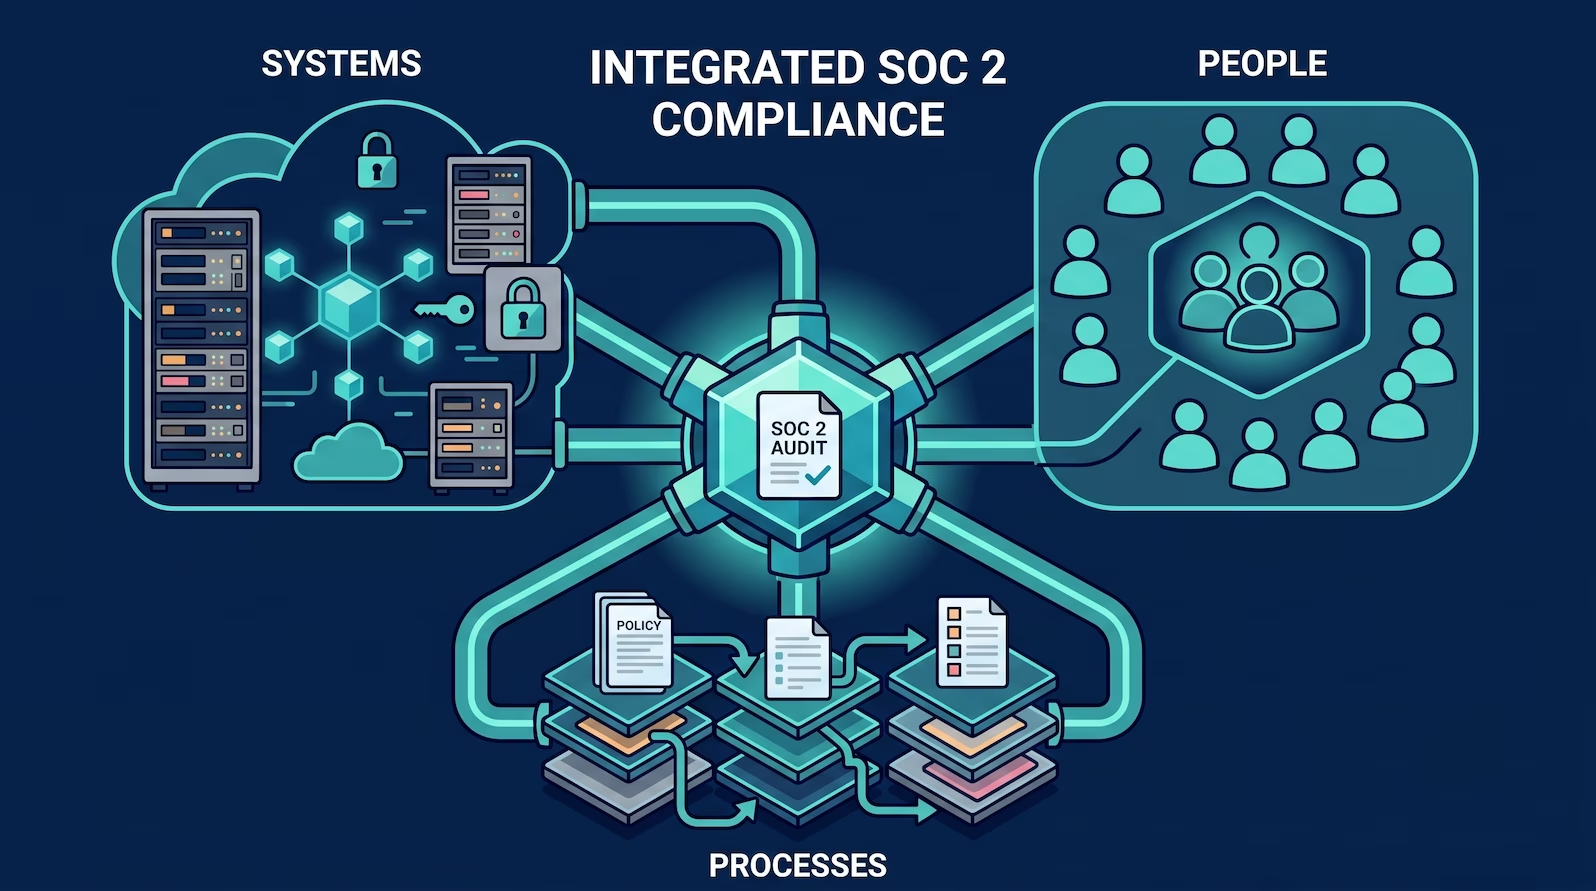
SOC 2 Scope: Systems, People, and Processes. The Complete Guide
Most SOC 2 guides treat scope as a single question: what systems are we certifying? That is one third of the answer.
SOC 2 scope has three...
SOC 2 Explained: What It Is and Why Enterprises Require It
An enterprise prospect sends over a security questionnaire. Or procurement asks whether you have a SOC 2 report. Or a deal stalls because the...
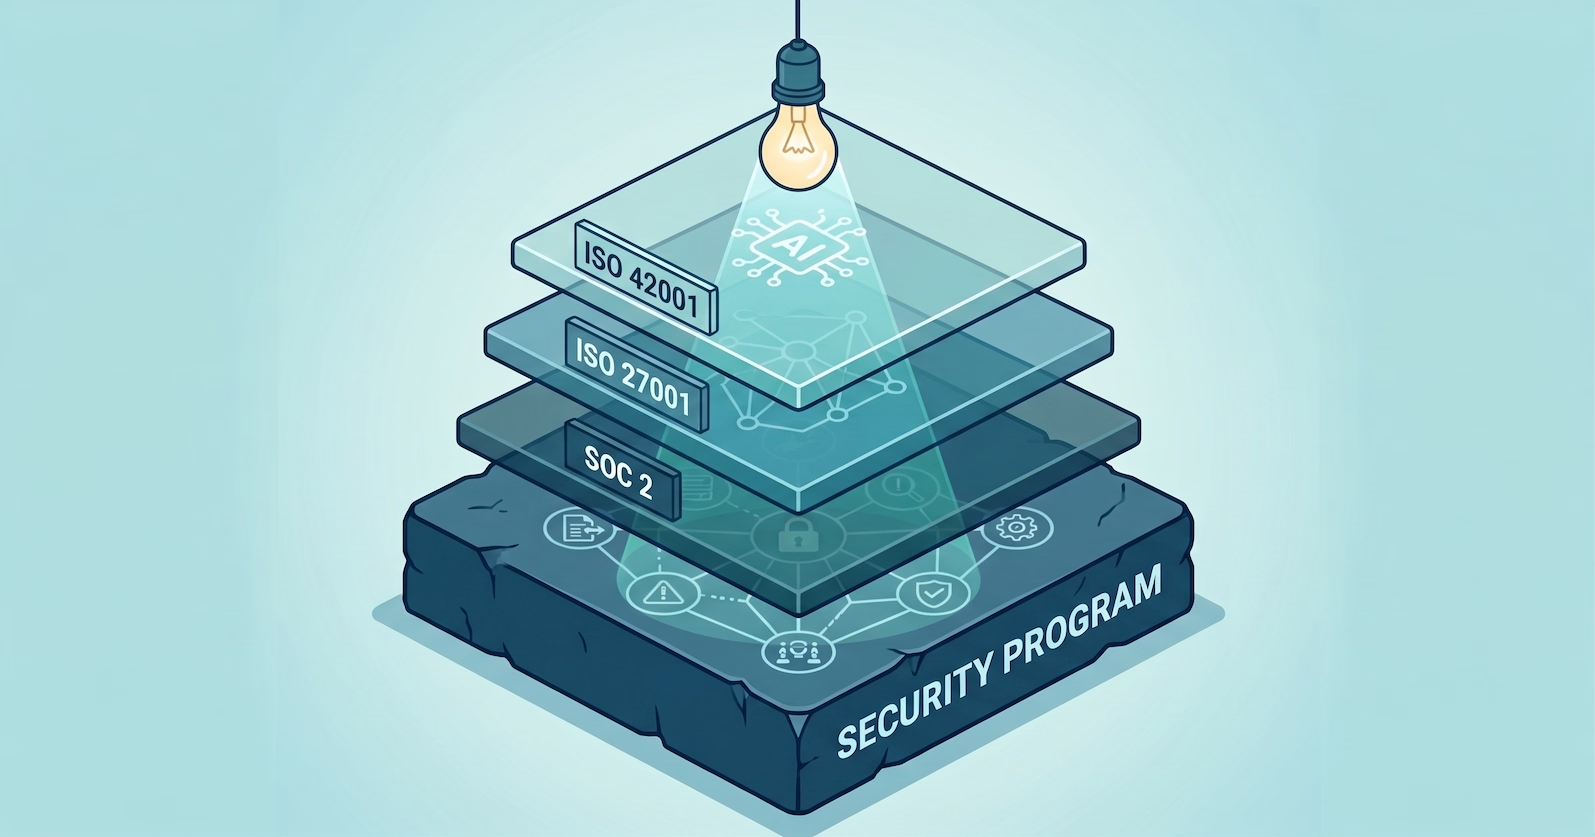
Most of ISO 42001 Is Already Built
How much of an existing SOC 2 or ISO 27001 program carries into ISO 42001, and why the framework tax is mostly imaginary for teams that built a real...
Only Two Auditors in Canada Can Certify ISO 42001. Here's What That Means for Buyers.
In Canada, RFPs landing in 2026 include a clause certification must be issued by an SCC-accredited body. SCC is Canada's national accreditation body,...
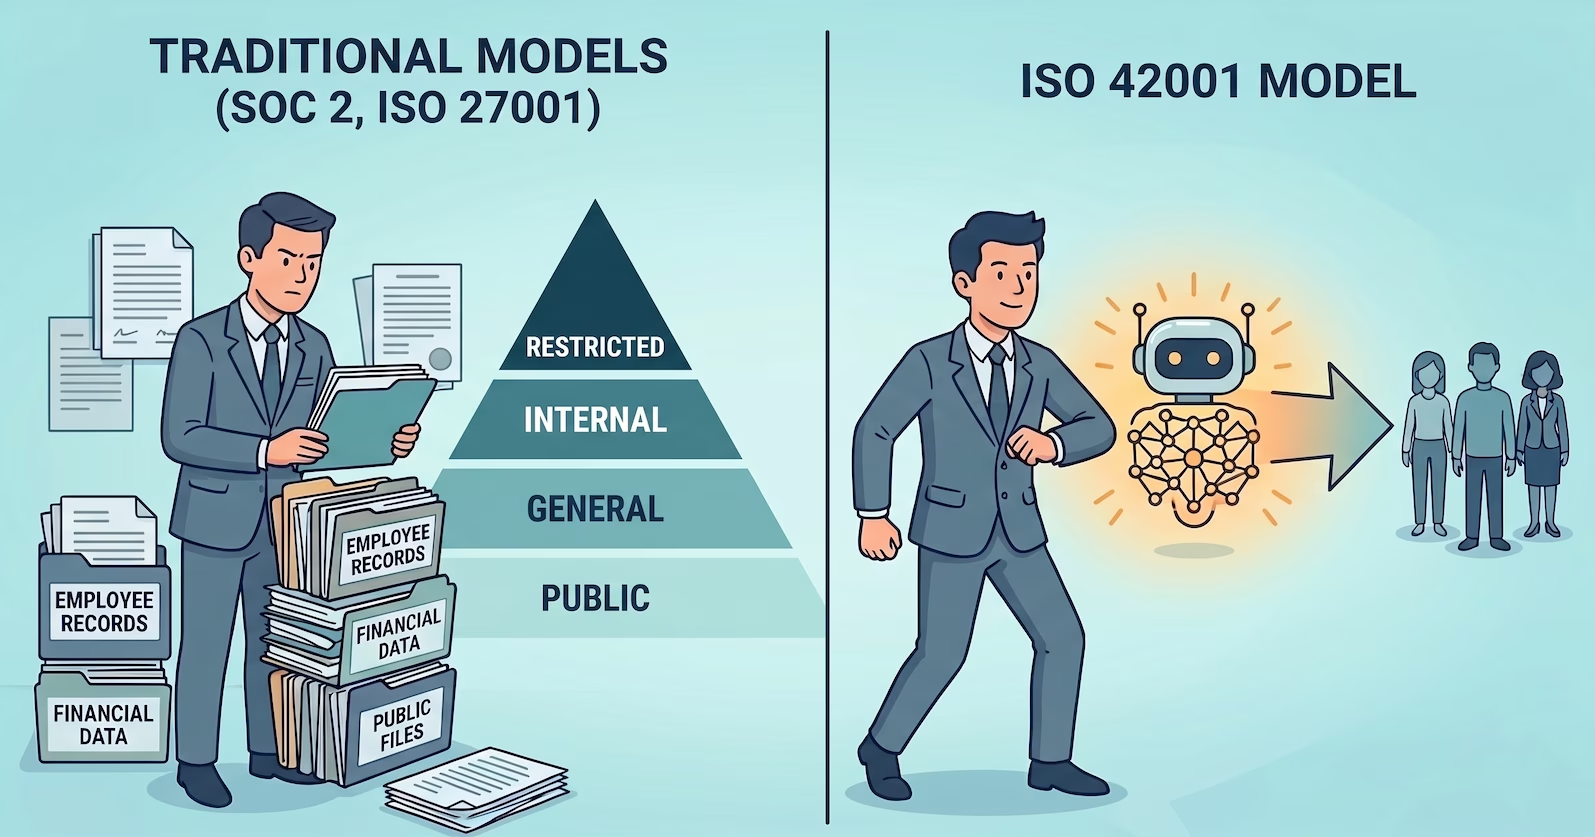
ISO 42001: How AI Governance Differs from Data Protection
Every traditional compliance framework asks the same opening question. How sensitive is the data, and how well is it protected? SOC 2, ISO 27001,...
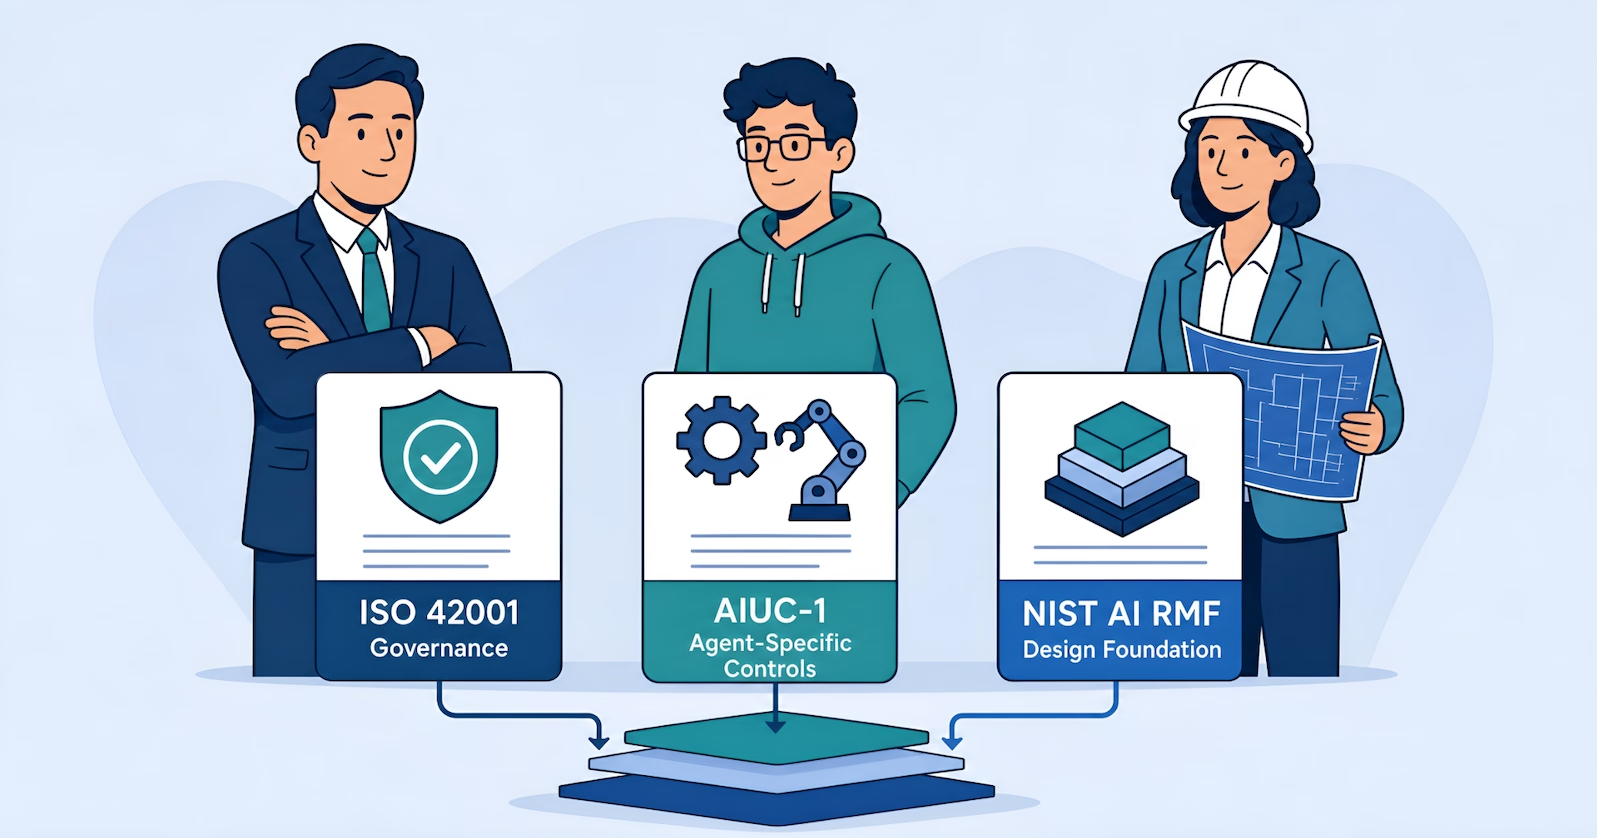
ISO 42001 vs AIUC-1 vs NIST AI RMF: Which Framework Fits
Three AI governance frameworks are fighting for procurement-team attention in 2026, and most of the comparison content treats them as competitors in...
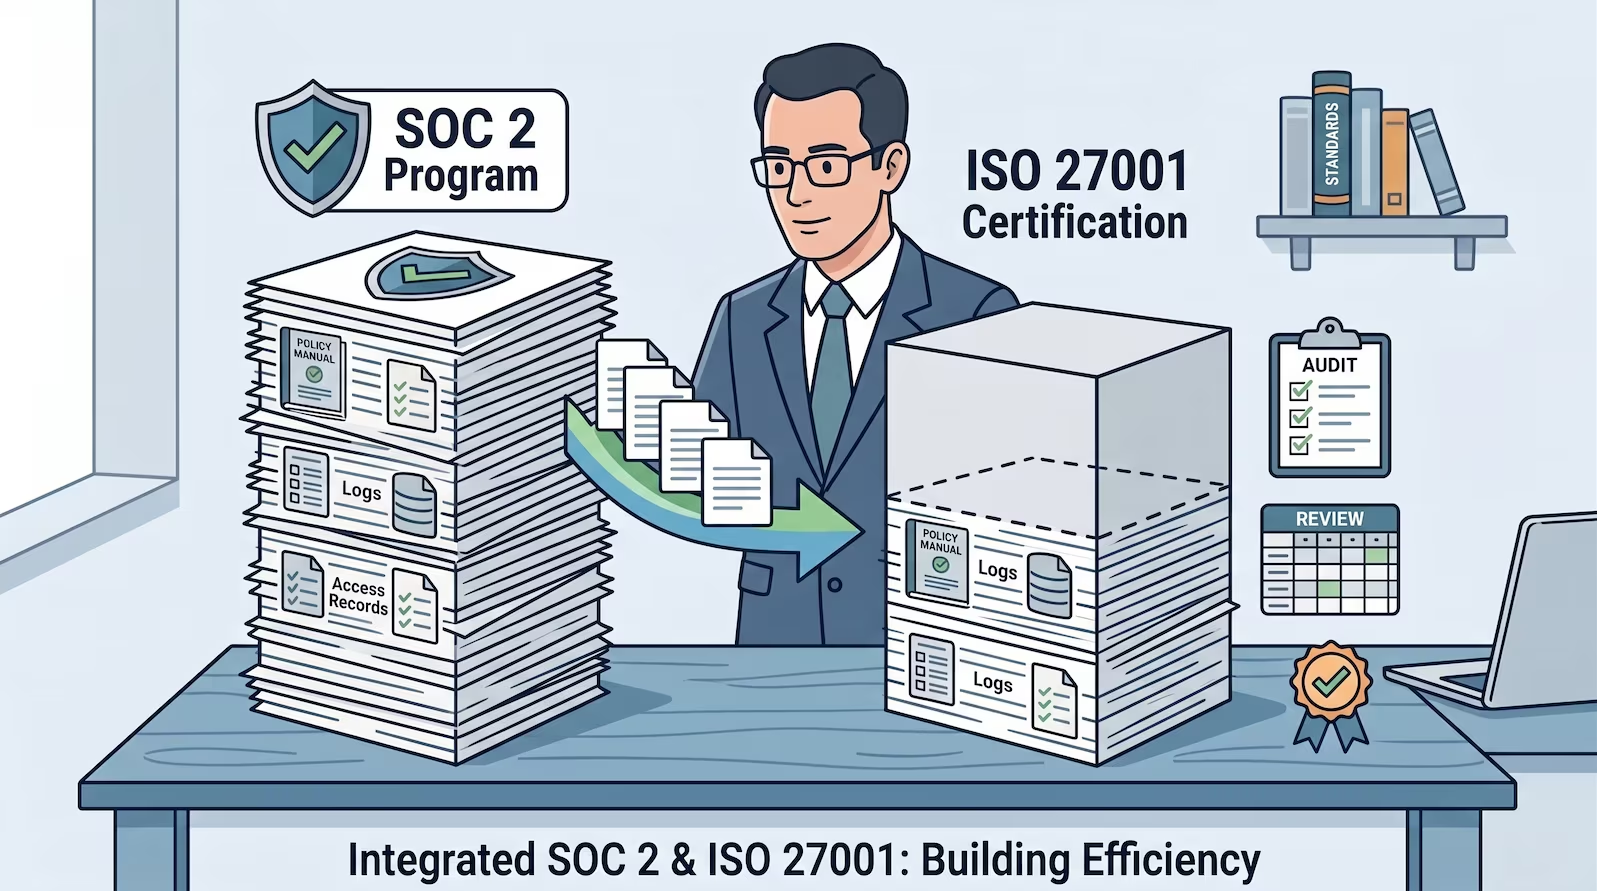
SOC 2 to ISO 27001 Control Mapping: What Transfers and What's Net-New
In our experience, a SOC 2 program covers roughly 70 percent of the work for ISO 27001 certification. The policies carry over, and most controls need...
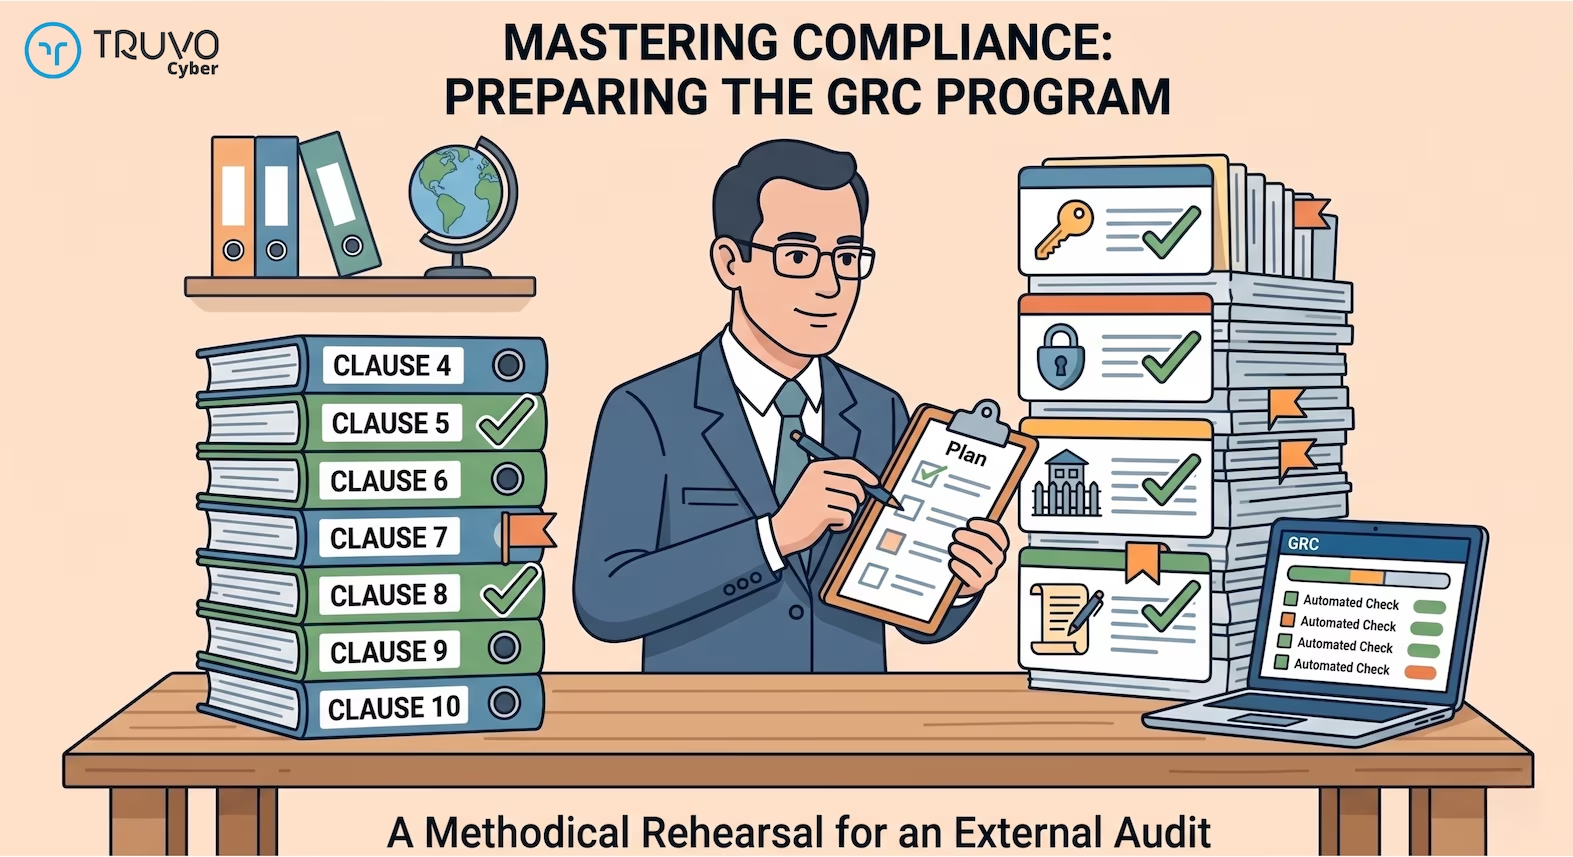
ISO 27001 Internal Audit: What Gets Reviewed
Most organizations pursuing ISO 27001 know they need an internal audit before the external stage 2. What they're less clear on is what that audit...
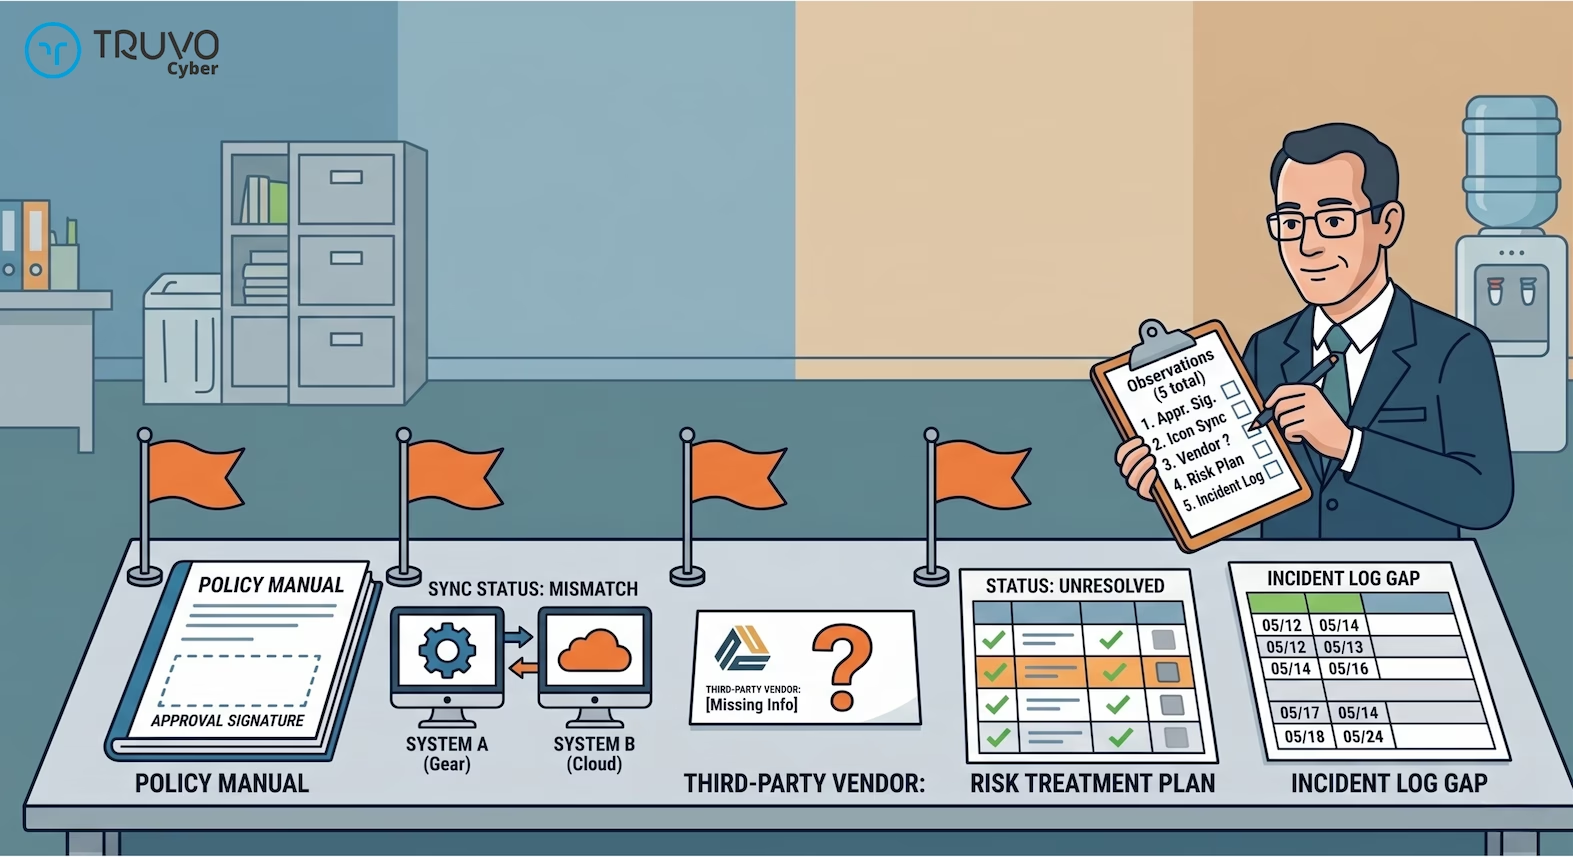
Five ISO 27001 Internal Audit Findings Before Certification
An ISO 27001 internal audit with no major nonconformities is a good result. It means the ISMS is documented, controls are operating, and the evidence...
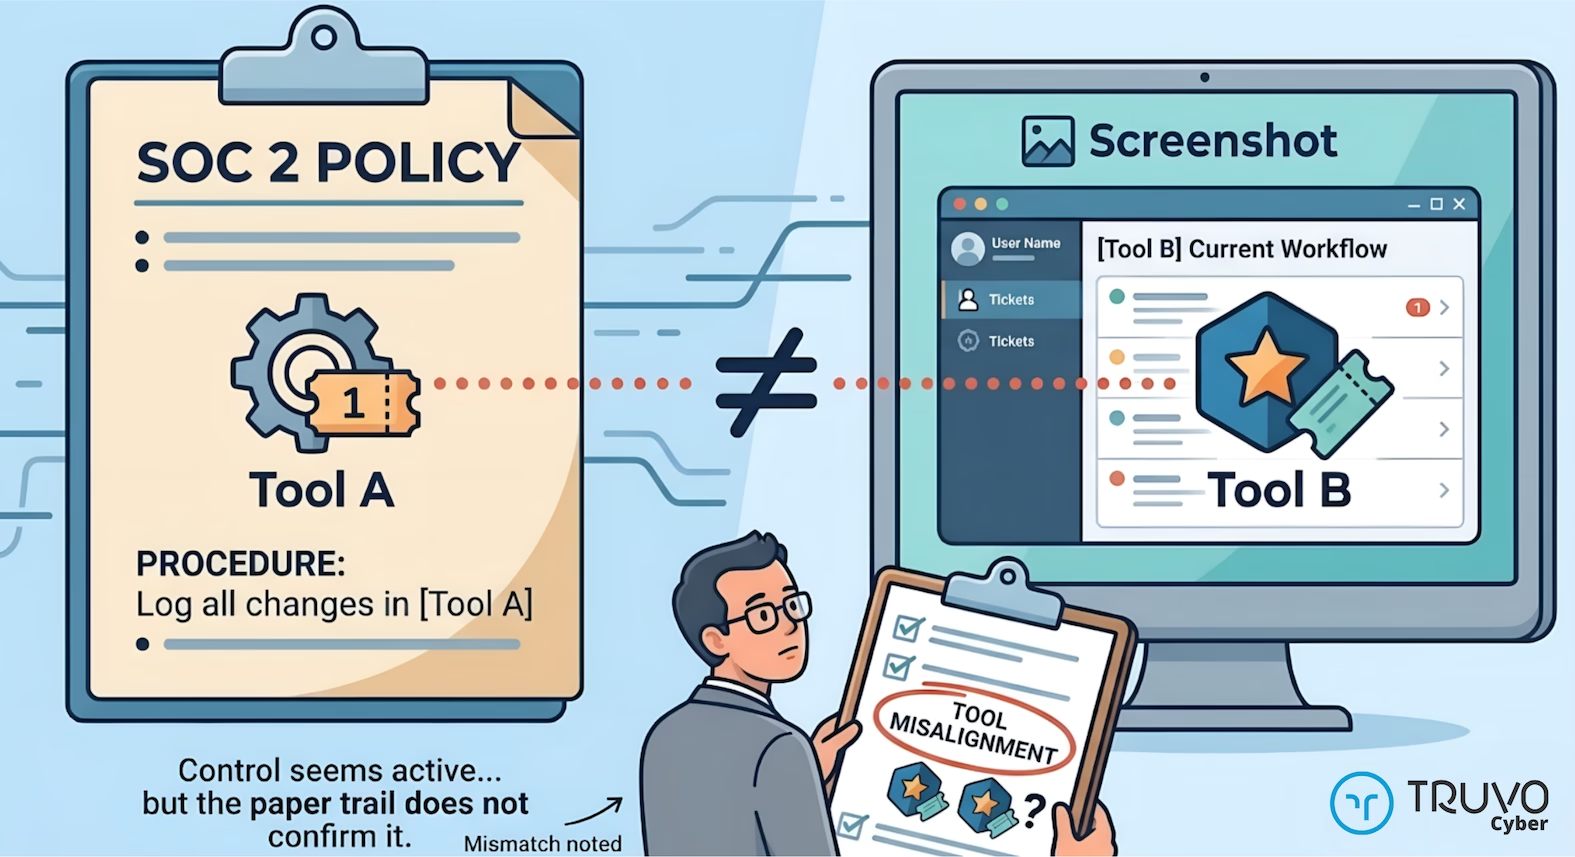
ISO 27001 Evidence Gap: Policy vs Reality
Building an ISO 27001 ISMS is largely an exercise in documentation. You write policies, implement controls, collect evidence, and upload everything...
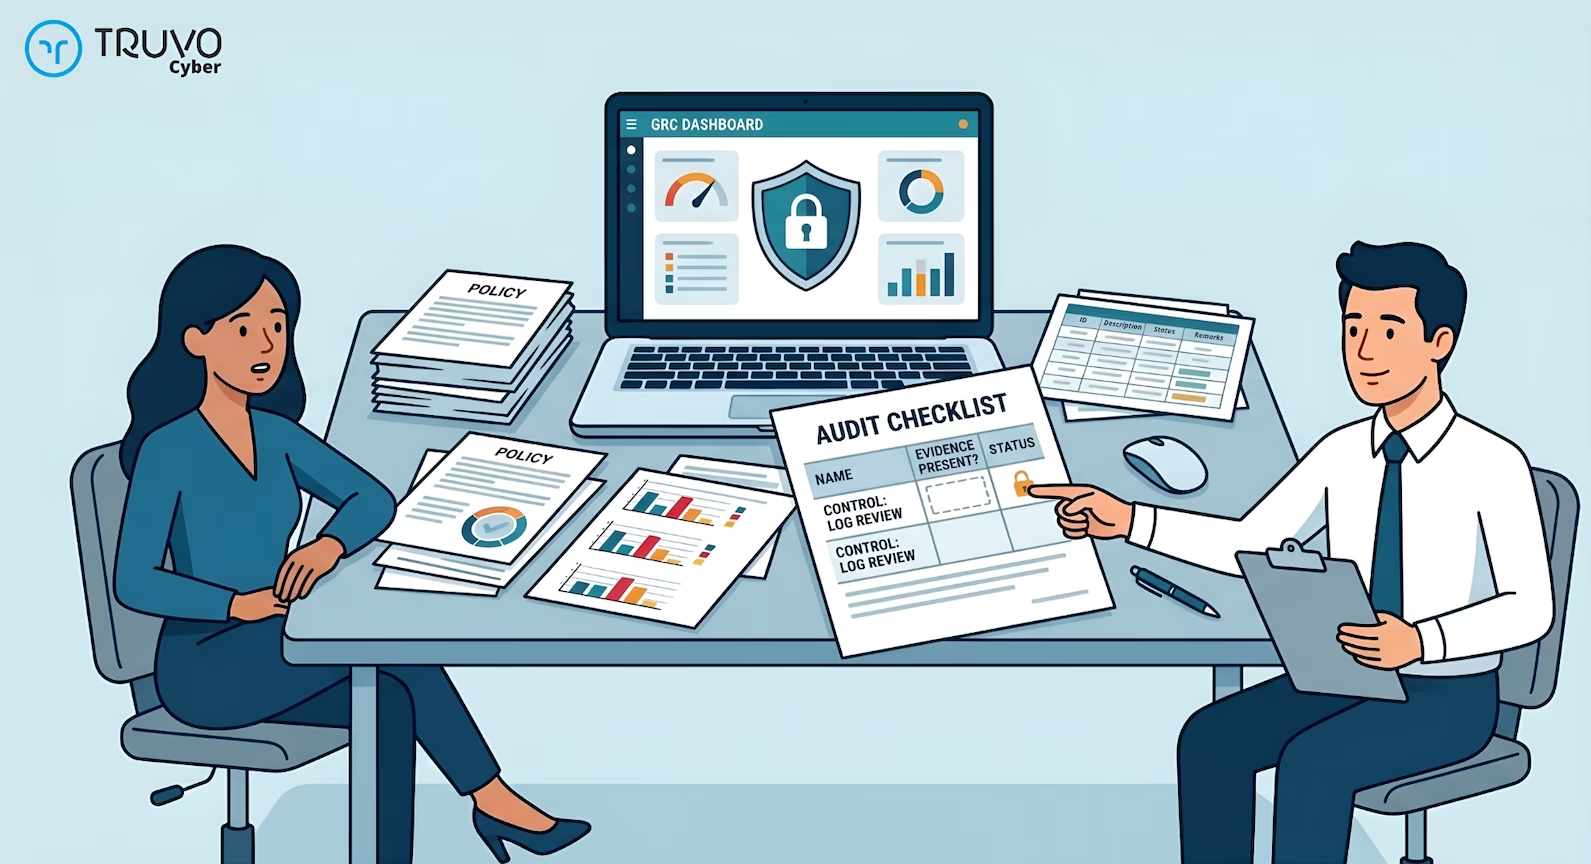
ISO 27001 Internal Audit Consulting in Canada
Most Canadian organizations preparing for ISO 27001 certification have the same question at the internal audit stage: who should run this, and what...
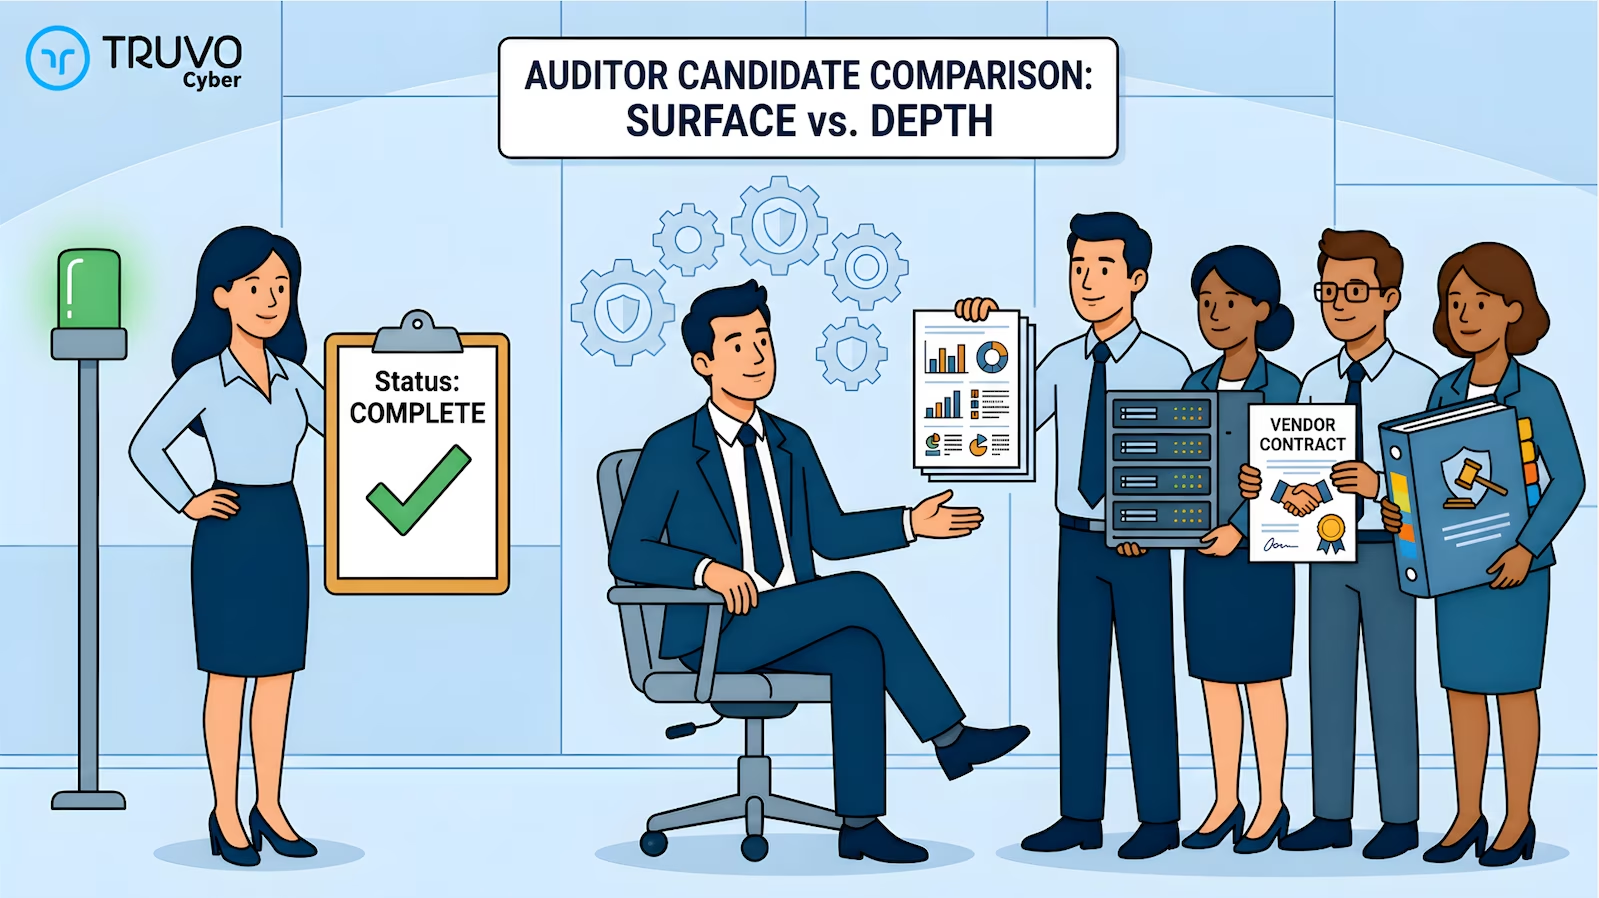
What to Look for in an ISO 27001 Internal Auditor
When you are preparing for ISO 27001 certification, the internal audit is not a formality. It is the last structured opportunity to identify gaps...
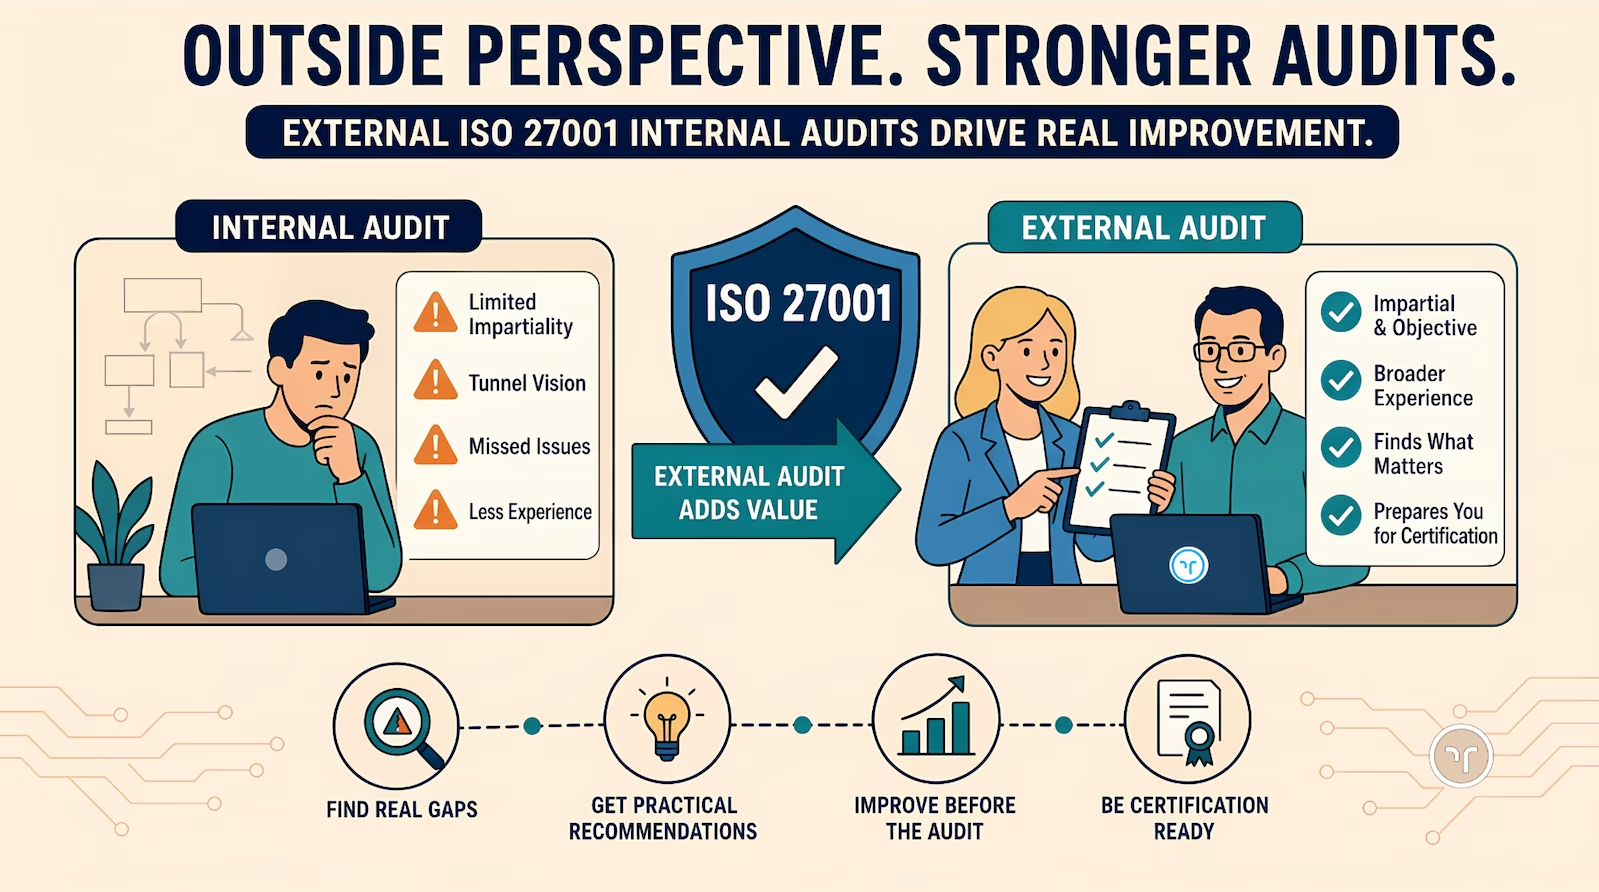
Outsourcing Your ISO 27001 Internal Audit: When It Makes Sense
One of the practical questions that comes up at the internal audit stage is whether to run it internally or bring in outside help. The standard...
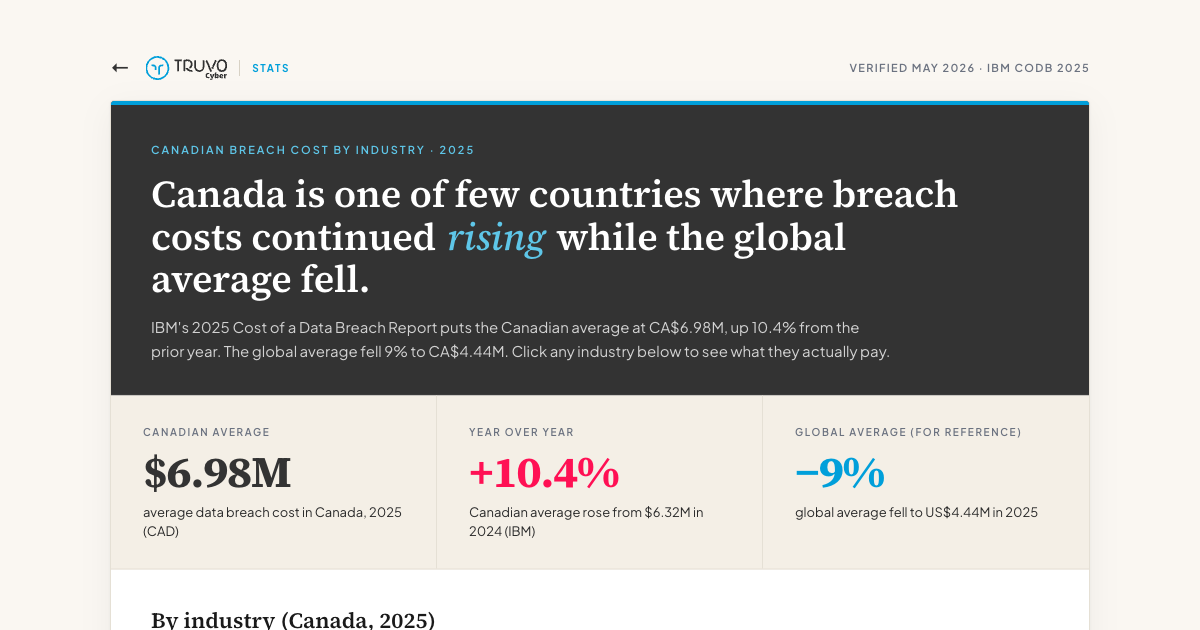
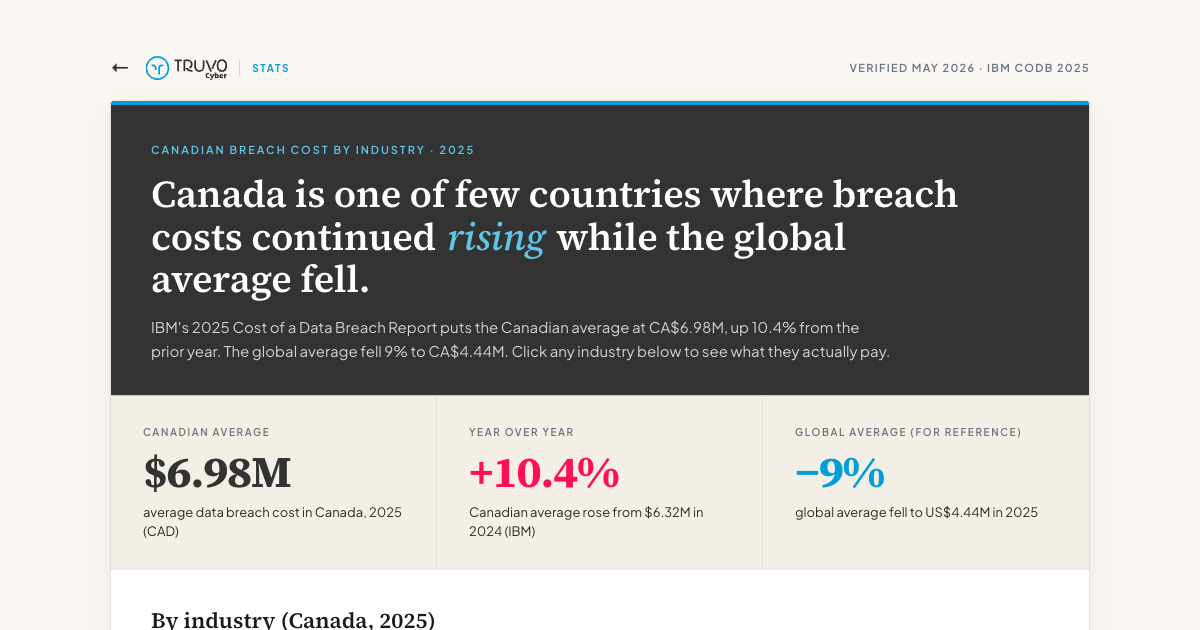
The Real Cost of a Data Breach in Canada (2025)
Canada is moving in the wrong direction on breach economics.
In 2025, the average cost of a data breach for a Canadian organization climbed to...
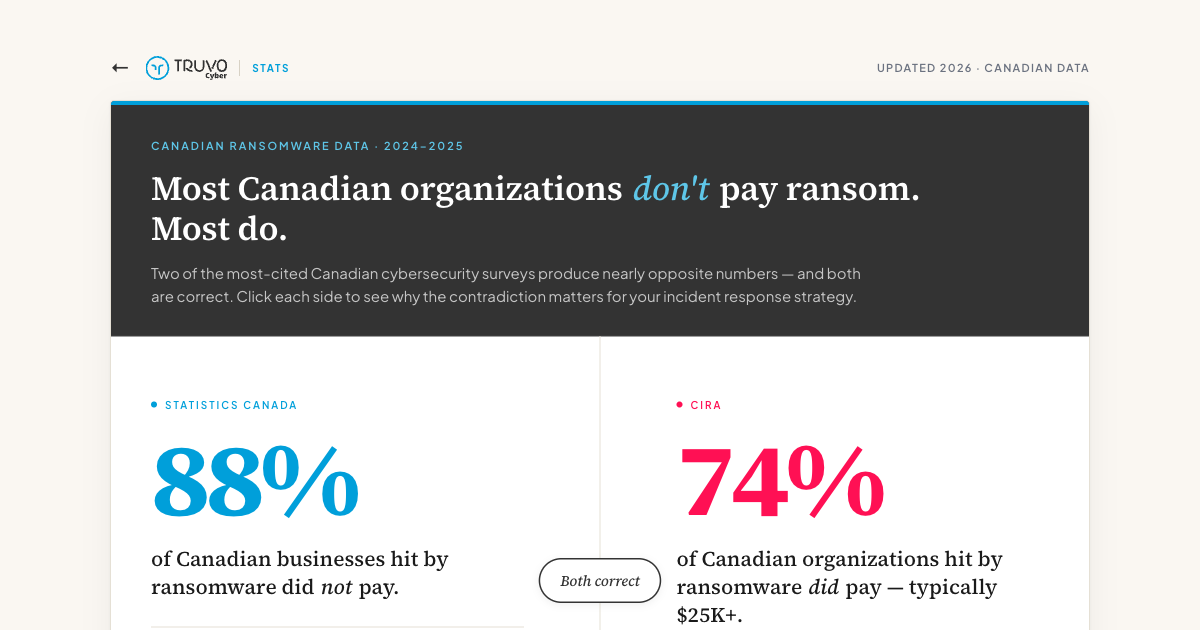
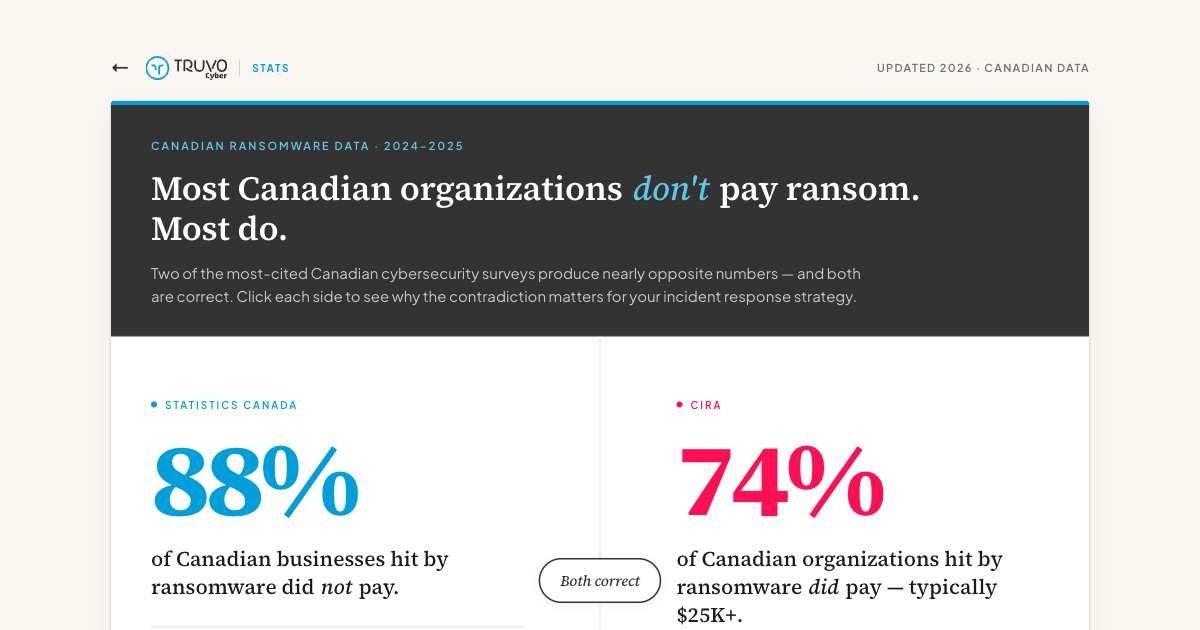
The Canadian Ransomware Paradox: Why Two Surveys Disagree on Payment
Two of the most-cited Canadian ransomware statistics flatly contradict each other.
Statistics Canada, reporting on 2023 data released in October...
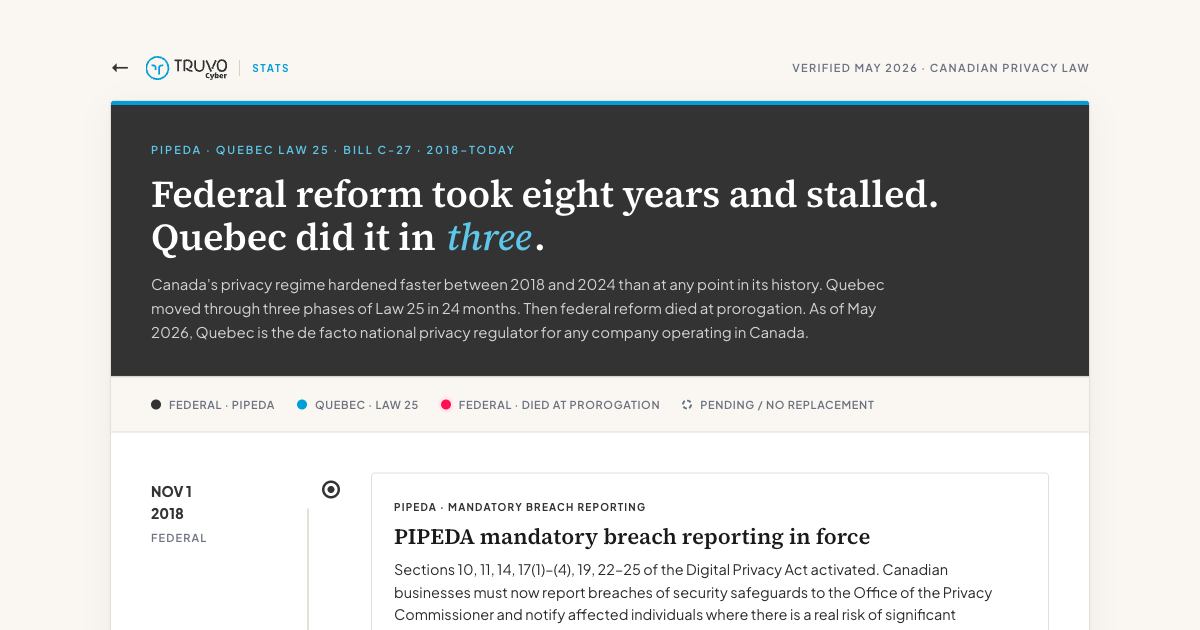
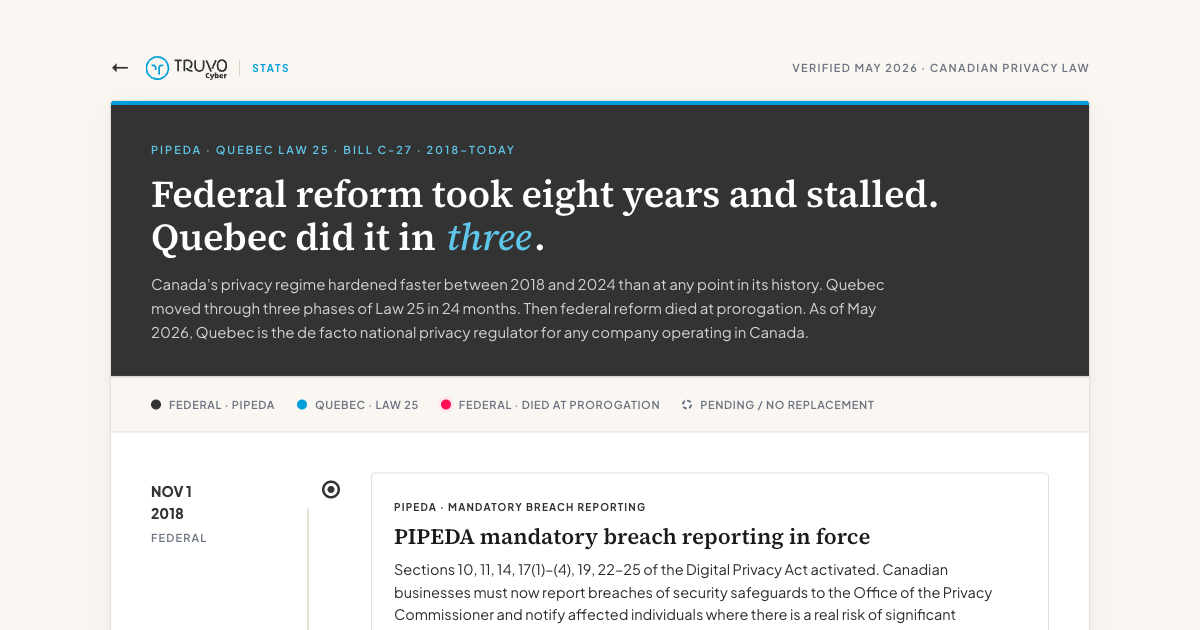
After Bill C-27: Quebec Law 25 and Canadian Privacy Costs
For three years, the dominant story in Canadian privacy law was the federal one. Bill C-27, the Digital Charter Implementation Act, was on track to...
SOC 2 Compliance Services in Canada (2026): Audit Firms, GRC Platforms and Consultants
Bottom line: Every SOC 2 report needs an independent CPA audit firm. Many companies also choose a GRC platform to automate evidence and a consultancy...
SOC 2 for Toronto Fintech and InsurTech
Toronto SaaS has a compliance problem Silicon Valley doesn't: a lot of your customers are Canadian banks, insurers, and licensed payment partners....
Top SOC 2 Consultants in Canada (2026): A Buyer's Guide
The SOC 2 consulting firms active in Canada in 2026 include Truvo Cyber, ISA Cybersecurity, Canadian Cyber, Elastify and the Big 4 (Deloitte, KPMG,...
Why Waiting for the RFP Is the Costliest Compliance Plan
Most companies treat compliance as a procurement problem. Something to handle when a customer or a contract surfaces it. The logic is reasonable on...
Security Vendors With Strong Practices and No Documentation
Here is a contradiction I run into constantly.
A security software vendor calls for a SOC 2 readiness conversation. We start poking at their...
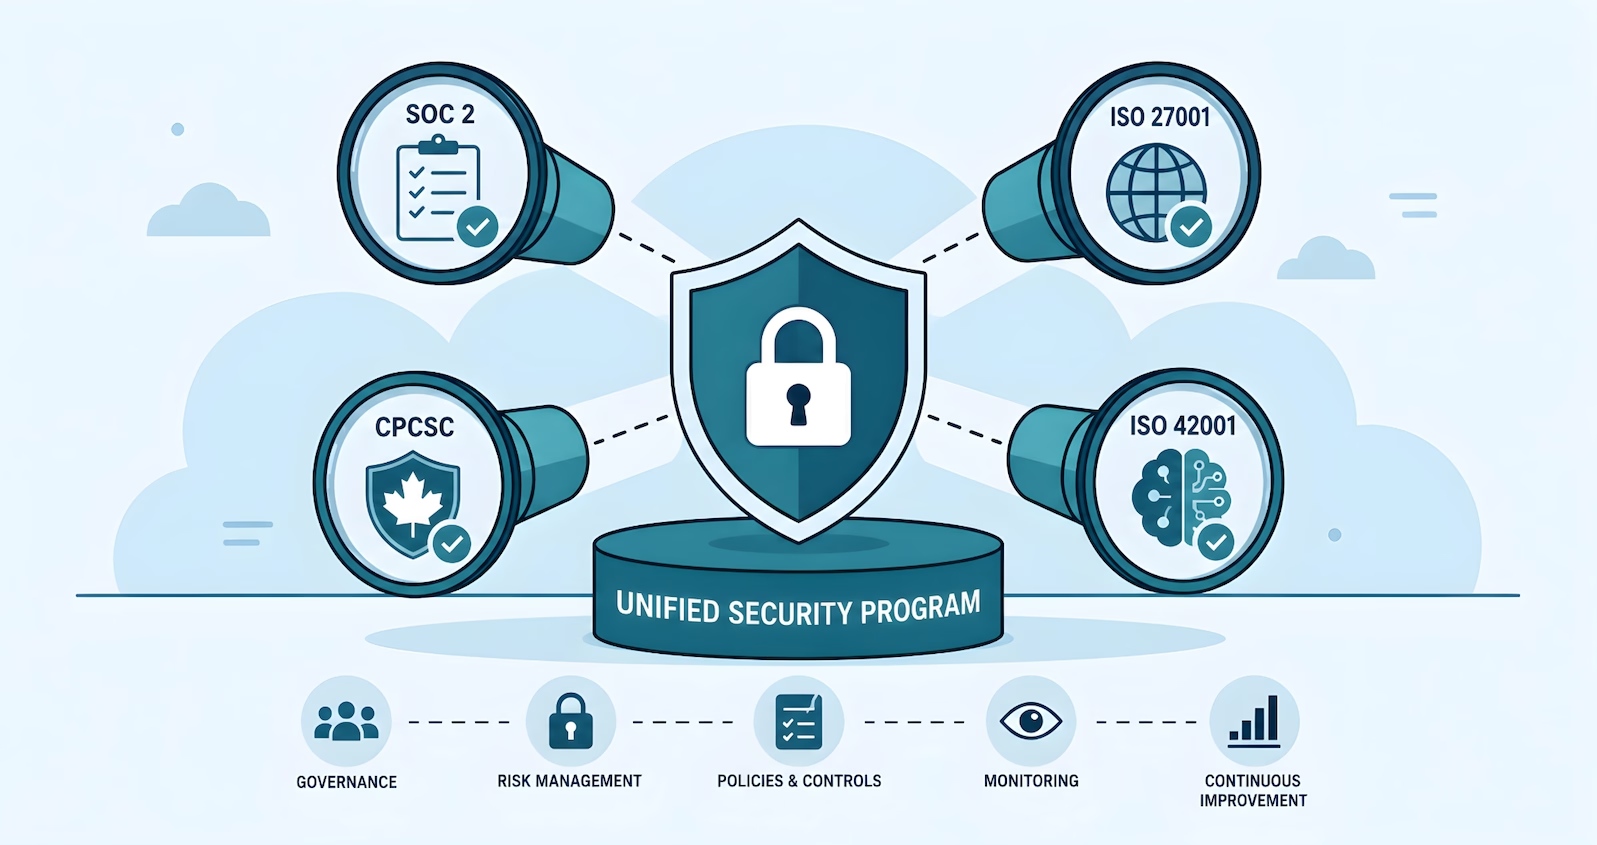
Why Frameworks Are Lenses on a Security Program
When the second framework arrives, most teams make the same mistake.
The first one, usually SOC 2, took nine to twelve months and a large chunk of...