Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

SOC 2 vs ISO 27001: What Carries Over and How to Do Both

SOC 2 vs ISO 27001: What Carries Over and How to Do Both

SOC 2 is an attestation report a licensed CPA firm issues against the AICPA's Trust Services Criteria, describing whether a service organization's...

Automate SOC 2 on AWS with Compliance as Code

Automate SOC 2 on AWS with Compliance as Code

?
SOC 2 Scorecard

Score Your SOC 2 Security Program

16 questions mapped to Common Criteria. See your strengths, find your gaps, get a...

SOC 2 CSOCs: Carve-Out vs Inclusive Method

SOC 2 CSOCs: Carve-Out vs Inclusive Method

SOC 2 CSOCs (Complementary Subservice Organization Controls) are third-party vendor controls your system depends on but does not operate. You address...

What Is ISO 42001? The AI Management Standard Explained

What Is ISO 42001? The AI Management Standard Explained

What Is ISO 42001? The AI Management Standard Explained

ISO/IEC 42001:2023 is the world's first international standard for managing artificial...

ISO 42001 and the EU AI Act: What Maps and What Doesn't

ISO 42001 and the EU AI Act: What Maps and What Doesn't

The Compliance Question Every AI Company Is Asking

The EU AI Act entered into force on August 1, 2024, making it the first comprehensive AI...

ISO 42001 Software Costs: What to Budget for Certification

ISO 42001 Software Costs: What to Budget for Certification

The Cost of AI Governance: Benchmarking Investment in ISO 42001 Compliance Software

Implementing ISO/IEC 42001 is a strategic necessity for AI SaaS...

SOC 2 Automation: What Vanta & Drata Don't Cover

SOC 2 Automation: What Vanta & Drata Don't Cover

Six months after buying Drata, Vanta, Secureframe, or any other compliance automation platform, a company realizes the dashboard is half-populated,...

Security Logging and Monitoring Architecture for SOC 2 and ISO 27001

Security Logging and Monitoring Architecture for SOC 2 and ISO 27001

In cybersecurity, what you don’t know can hurt you. An unmonitored system is a black box where attackers can operate undetected for weeks or months. ...

Web Summit Vancouver: Gary Marcus on AI Limitations and Risks

Web Summit Vancouver: Gary Marcus on AI Limitations and Risks

Key Takeaways from the Web Summit Keynote: A Reality Check on the AI Hype

AI dominated the conversation at this 2025's Web Summit, and for good...

NRC IRAP Funding for SOC 2 Compliance in Canada

NRC IRAP Funding for SOC 2 Compliance in Canada

Yes, NRC IRAP funding can cover a significant portion of SOC 2 and other cybersecurity compliance costs for Canadian companies. The work has to be...

CMMC Level 1 Compliance: Requirements and Implementation Guide

CMMC Level 1 Compliance: Requirements and Implementation Guide

As of November 2025, CMMC is no longer a concept the DoD is considering. It is a contract requirement. Contracting officers are now including CMMC...

SOC 2 Compliance Automation: What Platforms Do and Don't Cover

SOC 2 Compliance Automation: What Platforms Do and Don't Cover

Achieving SOC 2 compliance is a major milestone for SaaS companies and service providers handling sensitive customer data. Yet, for many startups and...

How to Implement ISO 42001: A Practical Guide

How to Implement ISO 42001: A Practical Guide

ISO 42001 is the first international standard for AI management systems. Implementing it means building an Artificial Intelligence Management System...

ISO 42001 vs ISO 27001: What's Different and When You Need Both

ISO 42001 vs ISO 27001: What's Different and When You Need Both

ISO 27001 and ISO 42001 share roughly 60-70% of their controls but govern different risks. ISO 27001 protects information assets through an...

Vector-style illustration for a SOC 2 comparison guide showing Vanta vs. Drata. A purple Vanta llama martial artist and a blue Drata ninja face off on opposing cliffs beneath a bold “SOC 2” title. Clean corporate design with flat colors, strong outlines, and a centered VS symbol.

Vanta vs Drata for SOC 2: Depth vs Integration Breadth

Drata and Vanta are the two most widely adopted SOC 2 compliance automation platforms. Both connect to your cloud, identity, and HR systems to...

AI Governance in GRC: How ISO 42001 Fits Into Your Compliance Program

AI Governance in GRC: How ISO 42001 Fits Into Your Compliance Program

As artificial intelligence (AI) rapidly embeds itself into core business processes, from customer support to code generation, enterprises face a...

ISO 42001 Compliance Software: 2026 Platform Review

ISO 42001 Compliance Software: 2026 Platform Review

The Platforms Compared

Vanta, Drata, Secureframe, and Scrut have all added dedicated ISO 42001 framework support. All four automate evidence...

Vanta vs Drata API Comparison for SOC 2 (2026)

Vanta vs Drata API Comparison for SOC 2 (2026)

?
SOC 2 Scorecard

Score Your SOC 2 Security Program

16 questions mapped to Common Criteria. See your strengths, find your gaps, get a...

Drata vs Vanta for ISO 42001 (2026 Comparison)

Drata vs Vanta for ISO 42001 (2026 Comparison)

How They Compare

Both Drata and Vanta offer dedicated ISO 42001 framework support with automated evidence collection, control cross-mapping to ISO...

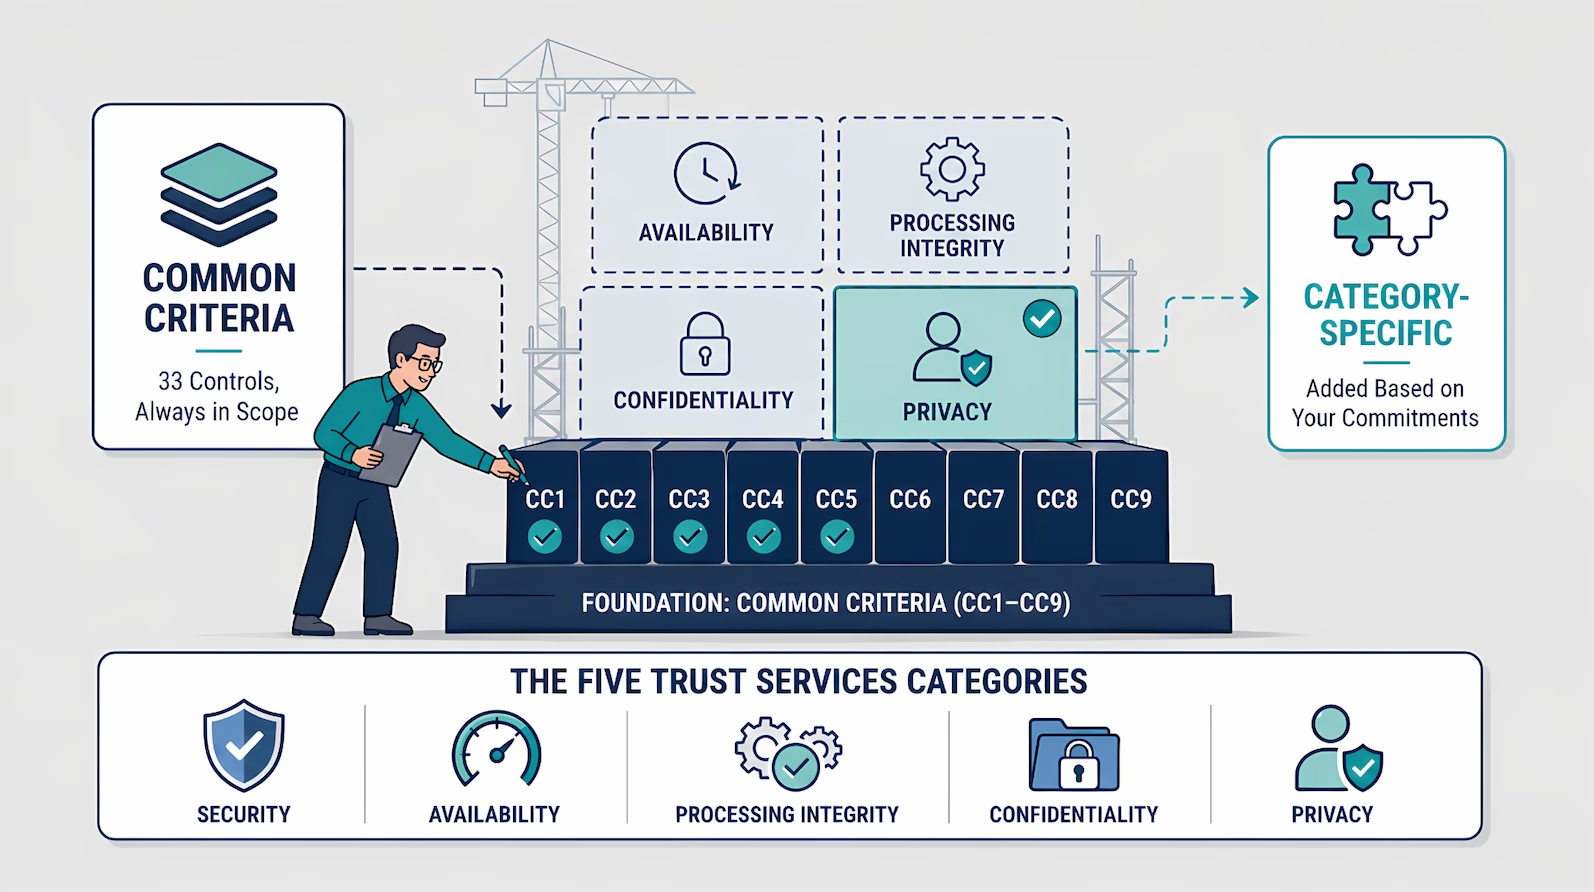
SOC 2 Trust Services Criteria: All 33 Criteria Listed

SOC 2 Trust Services Criteria: All 33 Criteria Listed

The SOC 2 Trust Services Criteria (TSC) are the control requirements the AICPA defines for a SOC 2 audit. They are organized into the Common Criteria...