Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

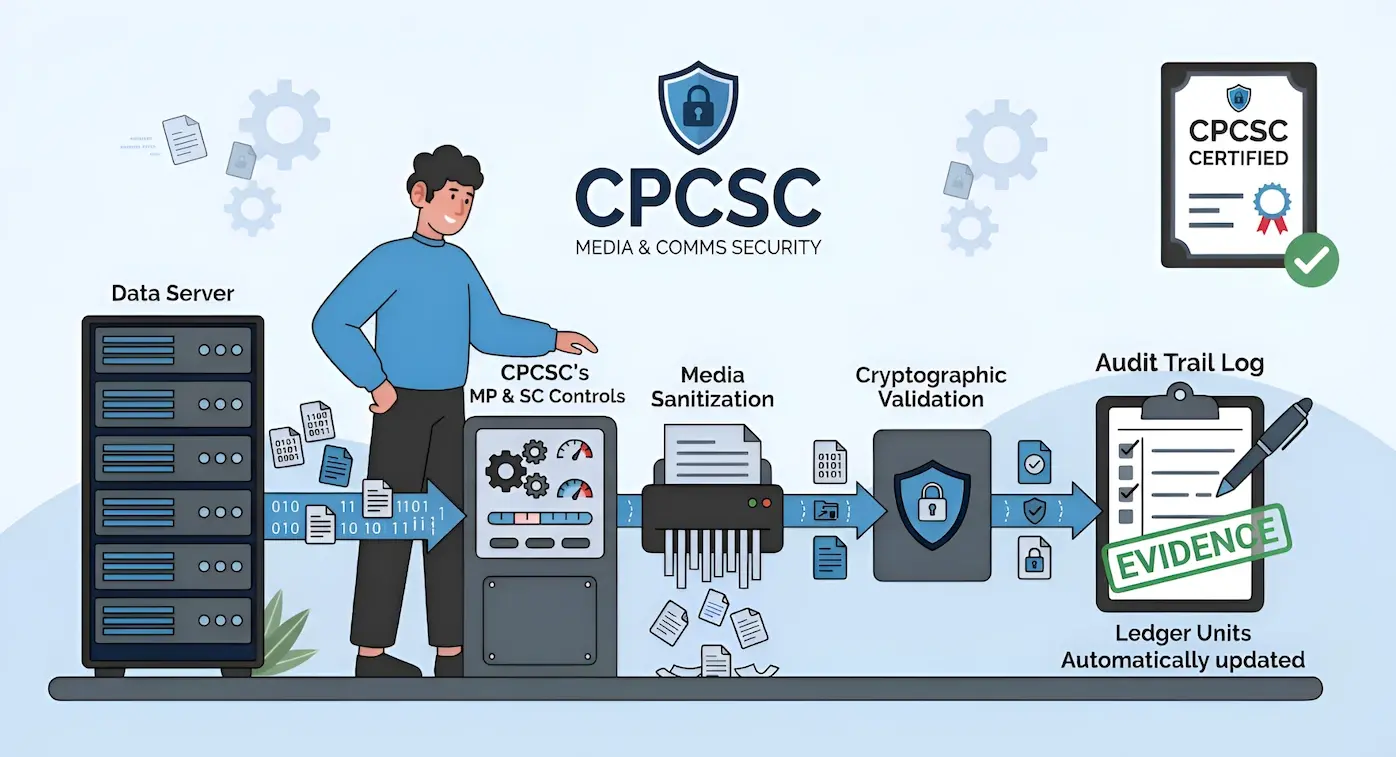
An infographic for CPCSC Media & Comms Security. A person monitors data moving from a server through "MP & SC Controls," "Media Sanitization" (a shredder), and "Cryptographic Validation." It ends at an "Audit Trail Log" marked "EVIDENCE," showing a certified workflow for protecting controlled info.

Protecting Controlled Information: Media and Communications Security (CPCSC)

In a compliance landscape that increasingly assumes cloud-first architecture, media protection controls tend to get deprioritized. The assumption is...
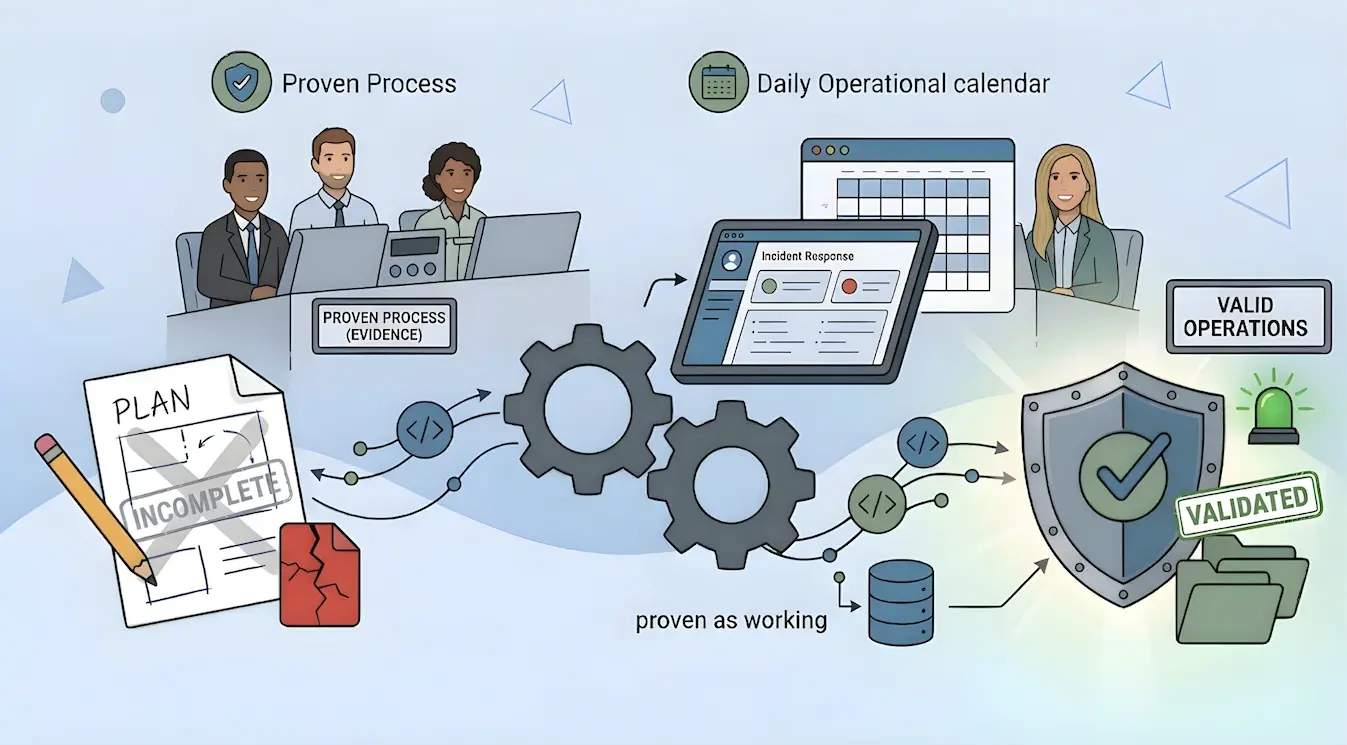
A vector illustration in a clean, flat style showing a cybersecurity team operationalizing their "Proven Process." At center, blue gears turn between a rejected "Incomplete Plan" and a "Validated" shield. The guy from the reference, in a blue sweater and plaid shirt, sits with his team.

Incident Response and System Integrity Under CPCSC

An incident response plan that exists only in a shared drive is not evidence of preparedness. It is evidence of intent, and the Canadian Program for...
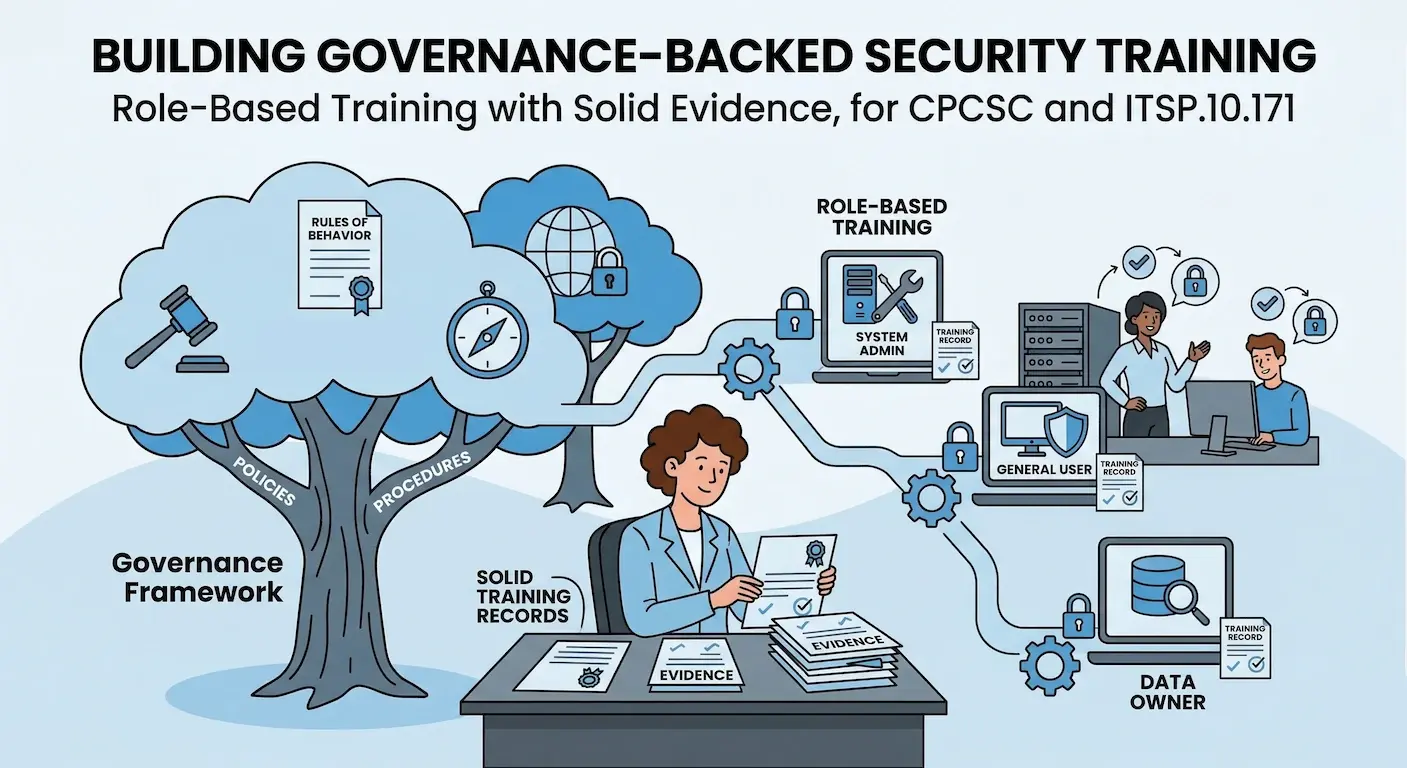
A flat vector illustration showing a "Governance Framework" tree with roots labeled Policies and Procedures. A professional at a desk organizes "Solid Training Records" and evidence. A flow chart connects specific roles—System Admin, General User, Data Owner—to specialized security training.

Security Awareness, Training, and Governance for CPCSC

The previous twelve posts in this series covered the technical and operational control families in ITSP.10.171: access control, incident response,...
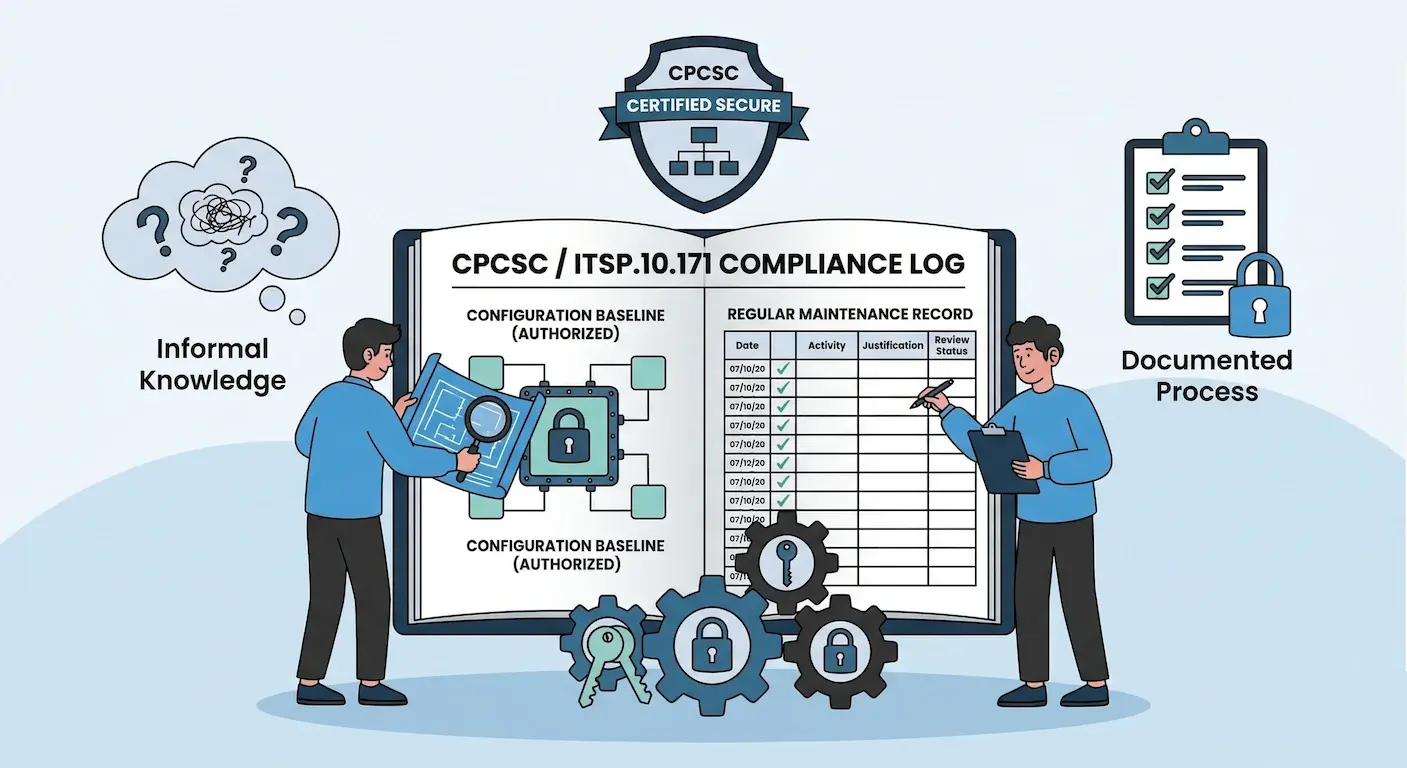
Flat vector illustration showing two professionals moving from "Informal Knowledge" (a messy thought cloud) to a "Documented Process." They are reviewing a CPCSC/ITSP.10.171 compliance log featuring an authorized configuration baseline, maintenance records, and secure system blueprints.

Configuration Management and System Maintenance for Defence Contractors Under CPCSC

There is a specific phrase that comes up in nearly every environment that has never been through a formal configuration review: We know our systems....
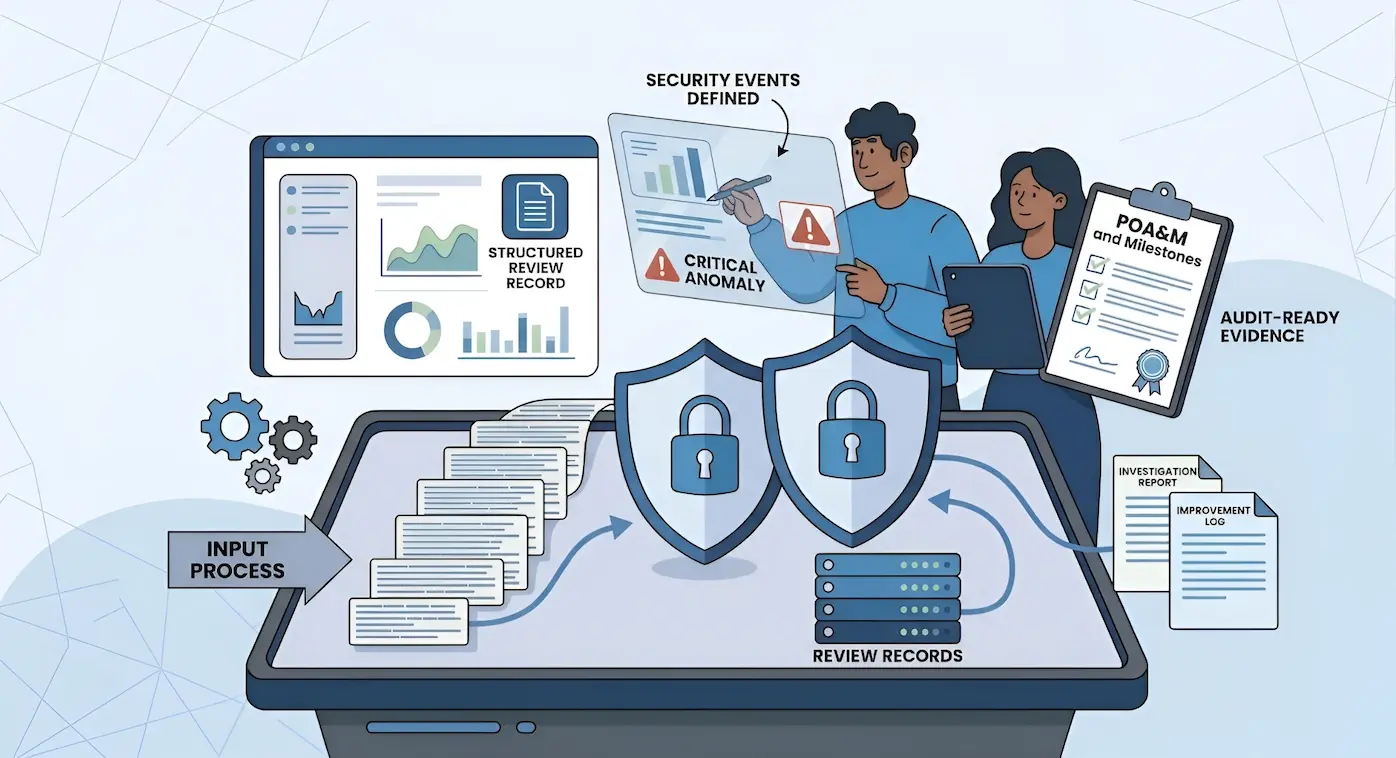
An illustration of a cybersecurity audit process. Two professionals analyze data on a digital screen featuring "Security Events Defined" and "Critical Anomaly." Elements include an "Input Process" feeding into "Review Records," a "Structured Review Record" dashboard, and "POA&M and Milestones."

Audit Logging, Monitoring, and Accountability for CPCSC

Most organizations produce logs. Application servers generate them, firewalls record them, identity providers track them. The volume is rarely the...
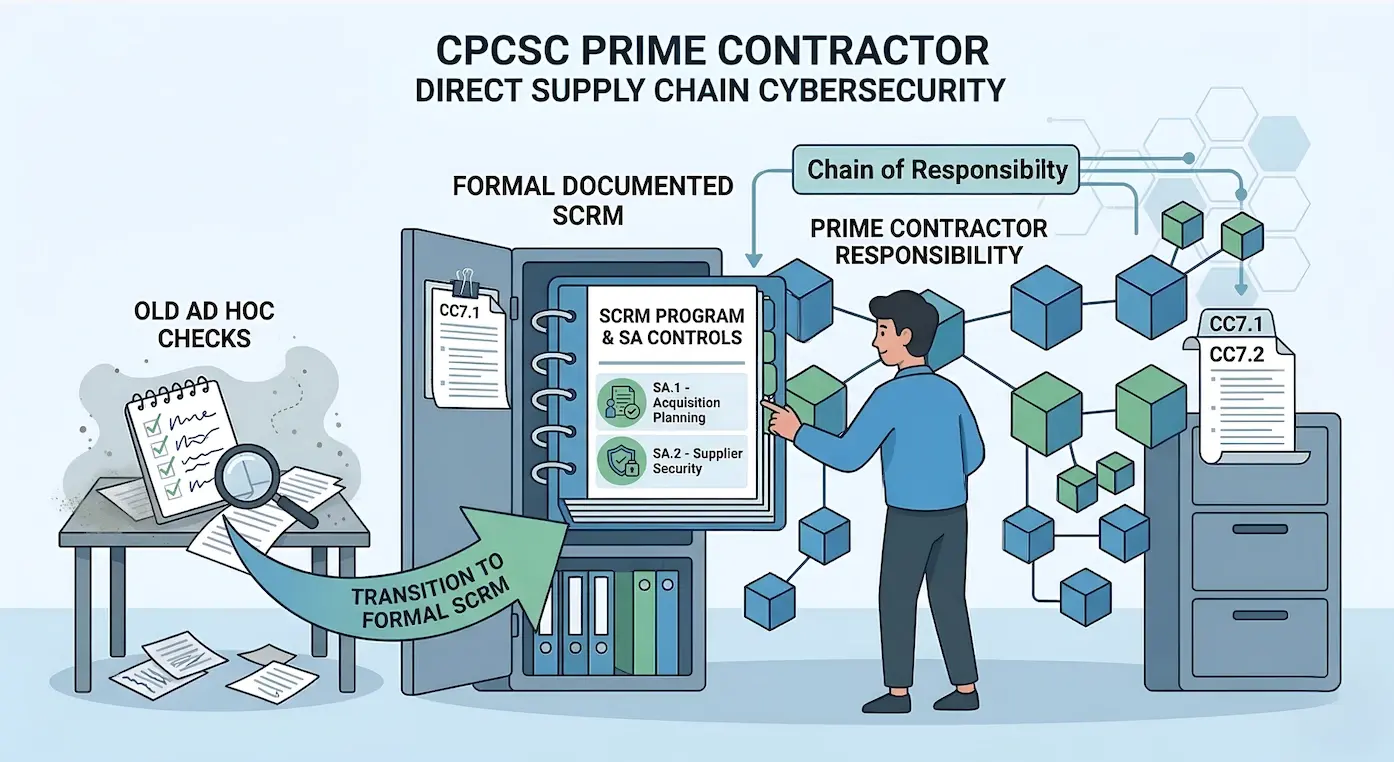
An illustration titled "CPCSC Prime Contractor Direct Supply Chain Cybersecurity" showing a transition from "Old Ad Hoc Checks" (messy papers) to "Formal Documented SCRM." A person manages a structured supply chain network linked to a formal SCRM program with SA.1 and SA.2 security controls.

Supply Chain Risk Management Under CPCSC

For most of the history of Canadian defence procurement, cybersecurity obligations ended at the prime contractor's perimeter. A prime could hold a...
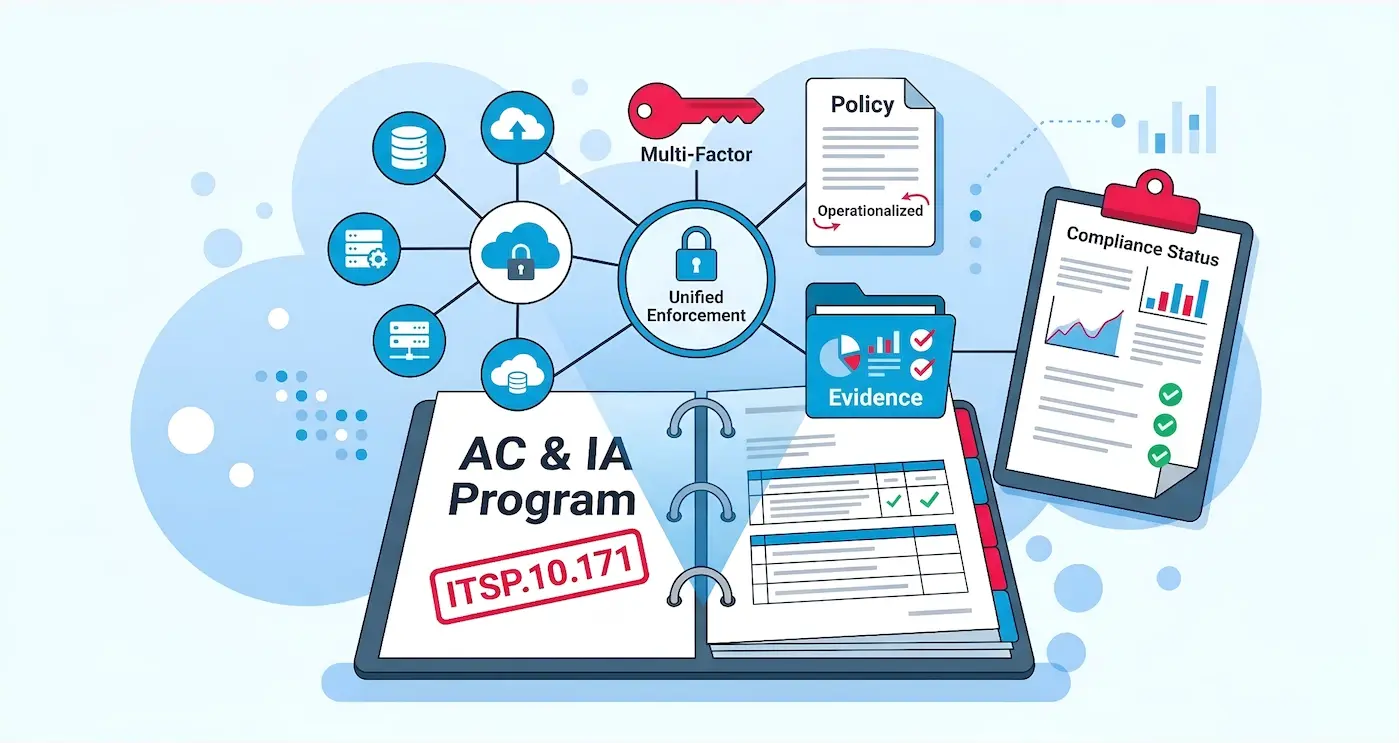
Flat vector illustration on a blue bubbly background showing a formal "AC & IA Program" binder for ITSP.10.171. Icons for MFA, policy, and evidence are connected to a central "Unified Enforcement" hub, with a compliance clipboard showing data charts, signifying an operationalized security program.

Access Control and Identity Management Under ITSP.10.171

Every security program has access controls of some kind. Password policies exist, MFA is probably enabled somewhere, and someone has a spreadsheet...
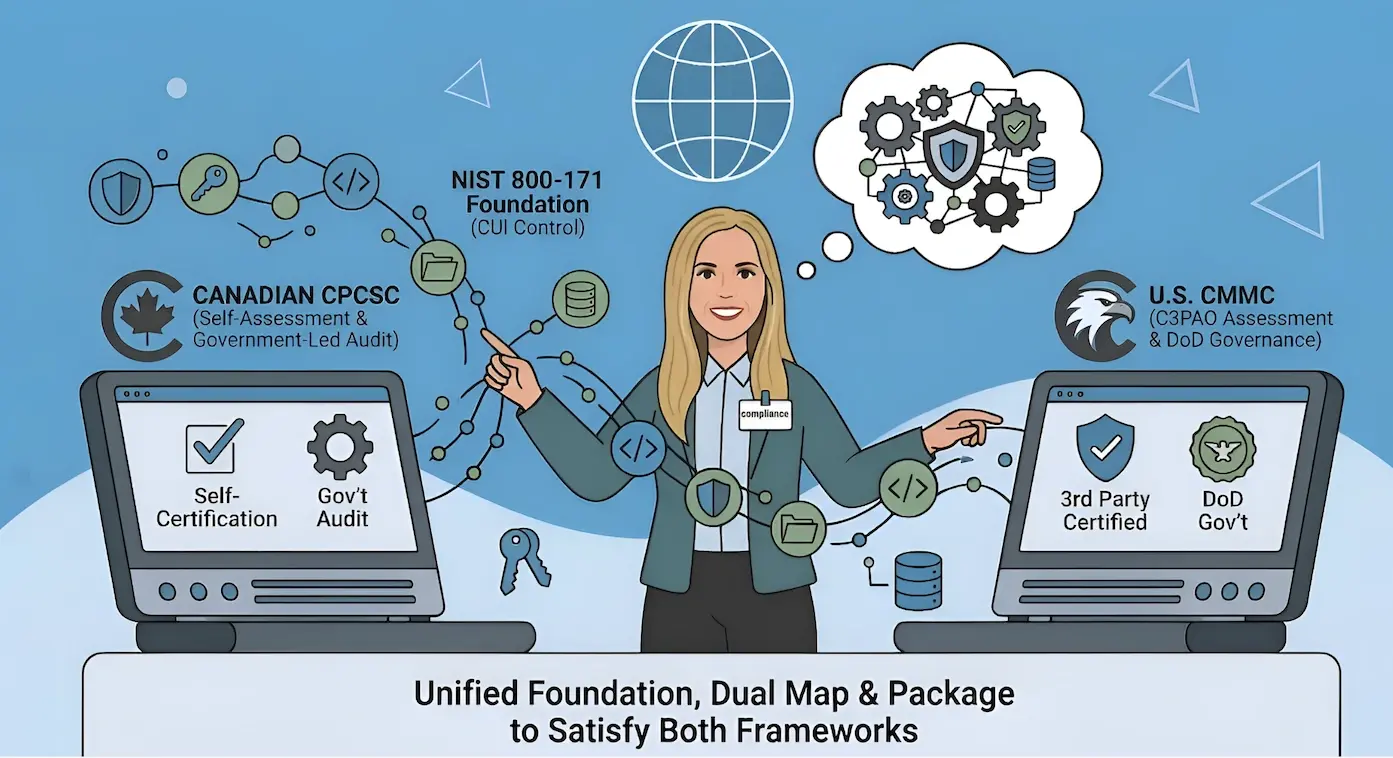
An infographic comparing Canadian CPCSC (Self-Assessment & Gov-Led Audit) and U.S. CMMC (C3PAO Assessment & DoD Governance). A central professional woman links both frameworks to a shared NIST 800-171 Foundation, emphasizing a unified strategy to satisfy both dual-jurisdiction requirements.

CPCSC vs CMMC: What Dual-Jurisdiction Contractors Need to Know

CPCSC (Canada) and CMMC (United States) both derive from NIST SP 800-171, so their control sets largely overlap. They differ in how each program...
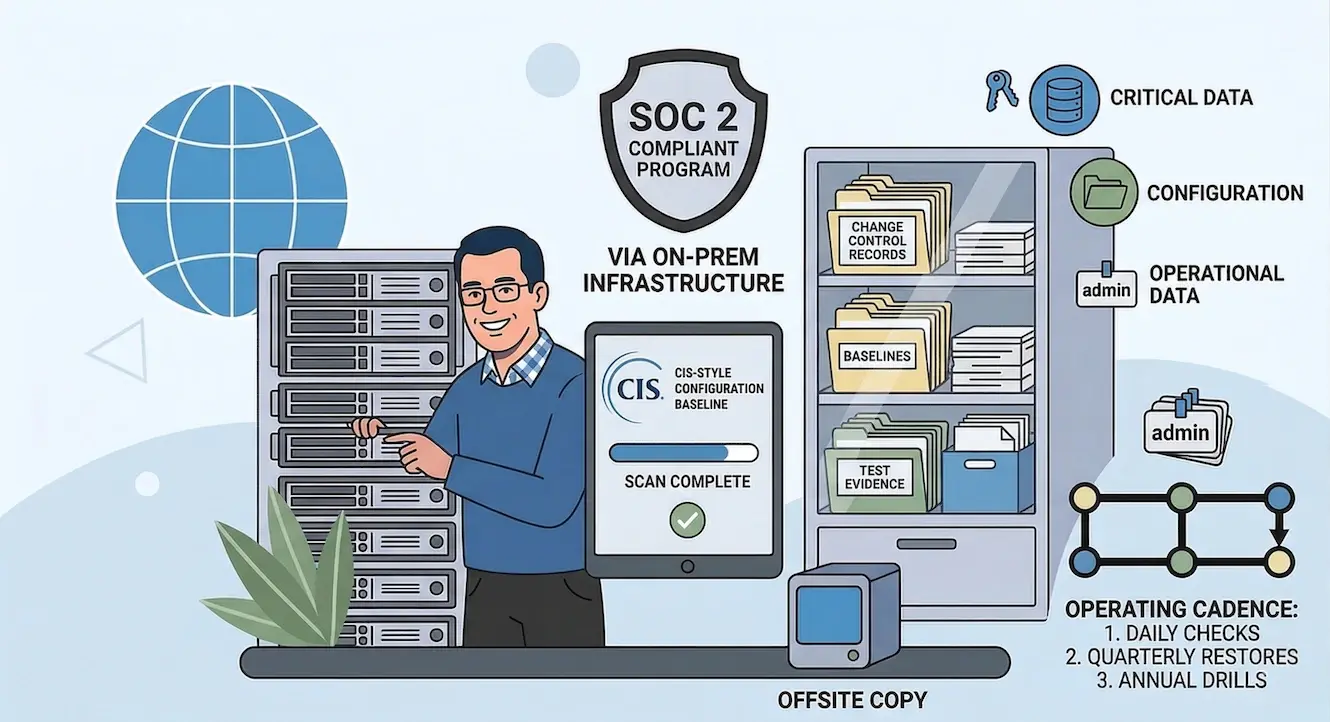
Illustration showing a SOC 2 compliant program via on-prem infrastructure. A man stands by a server rack and a tablet showing a completed CIS configuration scan. To the right, a filing cabinet stores baselines and test evidence. An "Operating Cadence" list details daily, quarterly, and annual tasks.

SOC 2 Configuration Baselines for Bare Metal: CIS Benchmarks & Beyond

In cloud environments, configuration compliance is a toggle. Enable AWS Config, deploy a conformance pack, and the platform continuously evaluates...
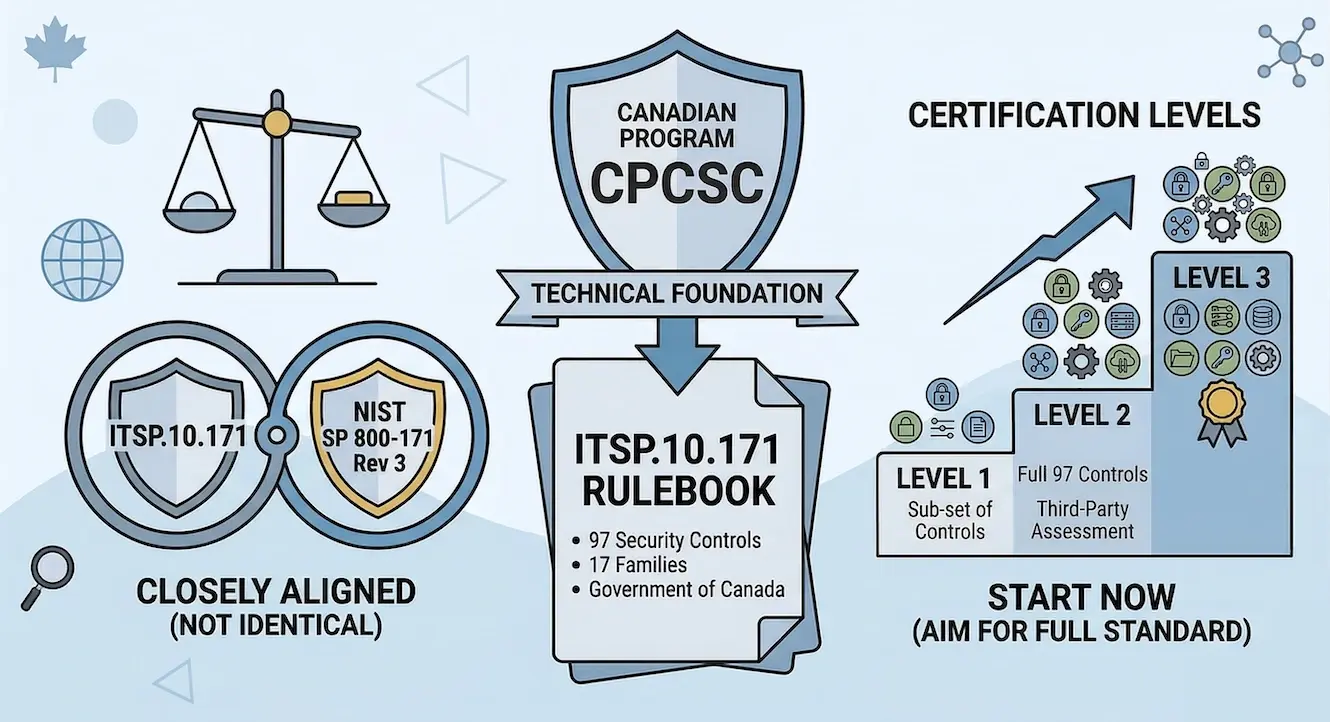
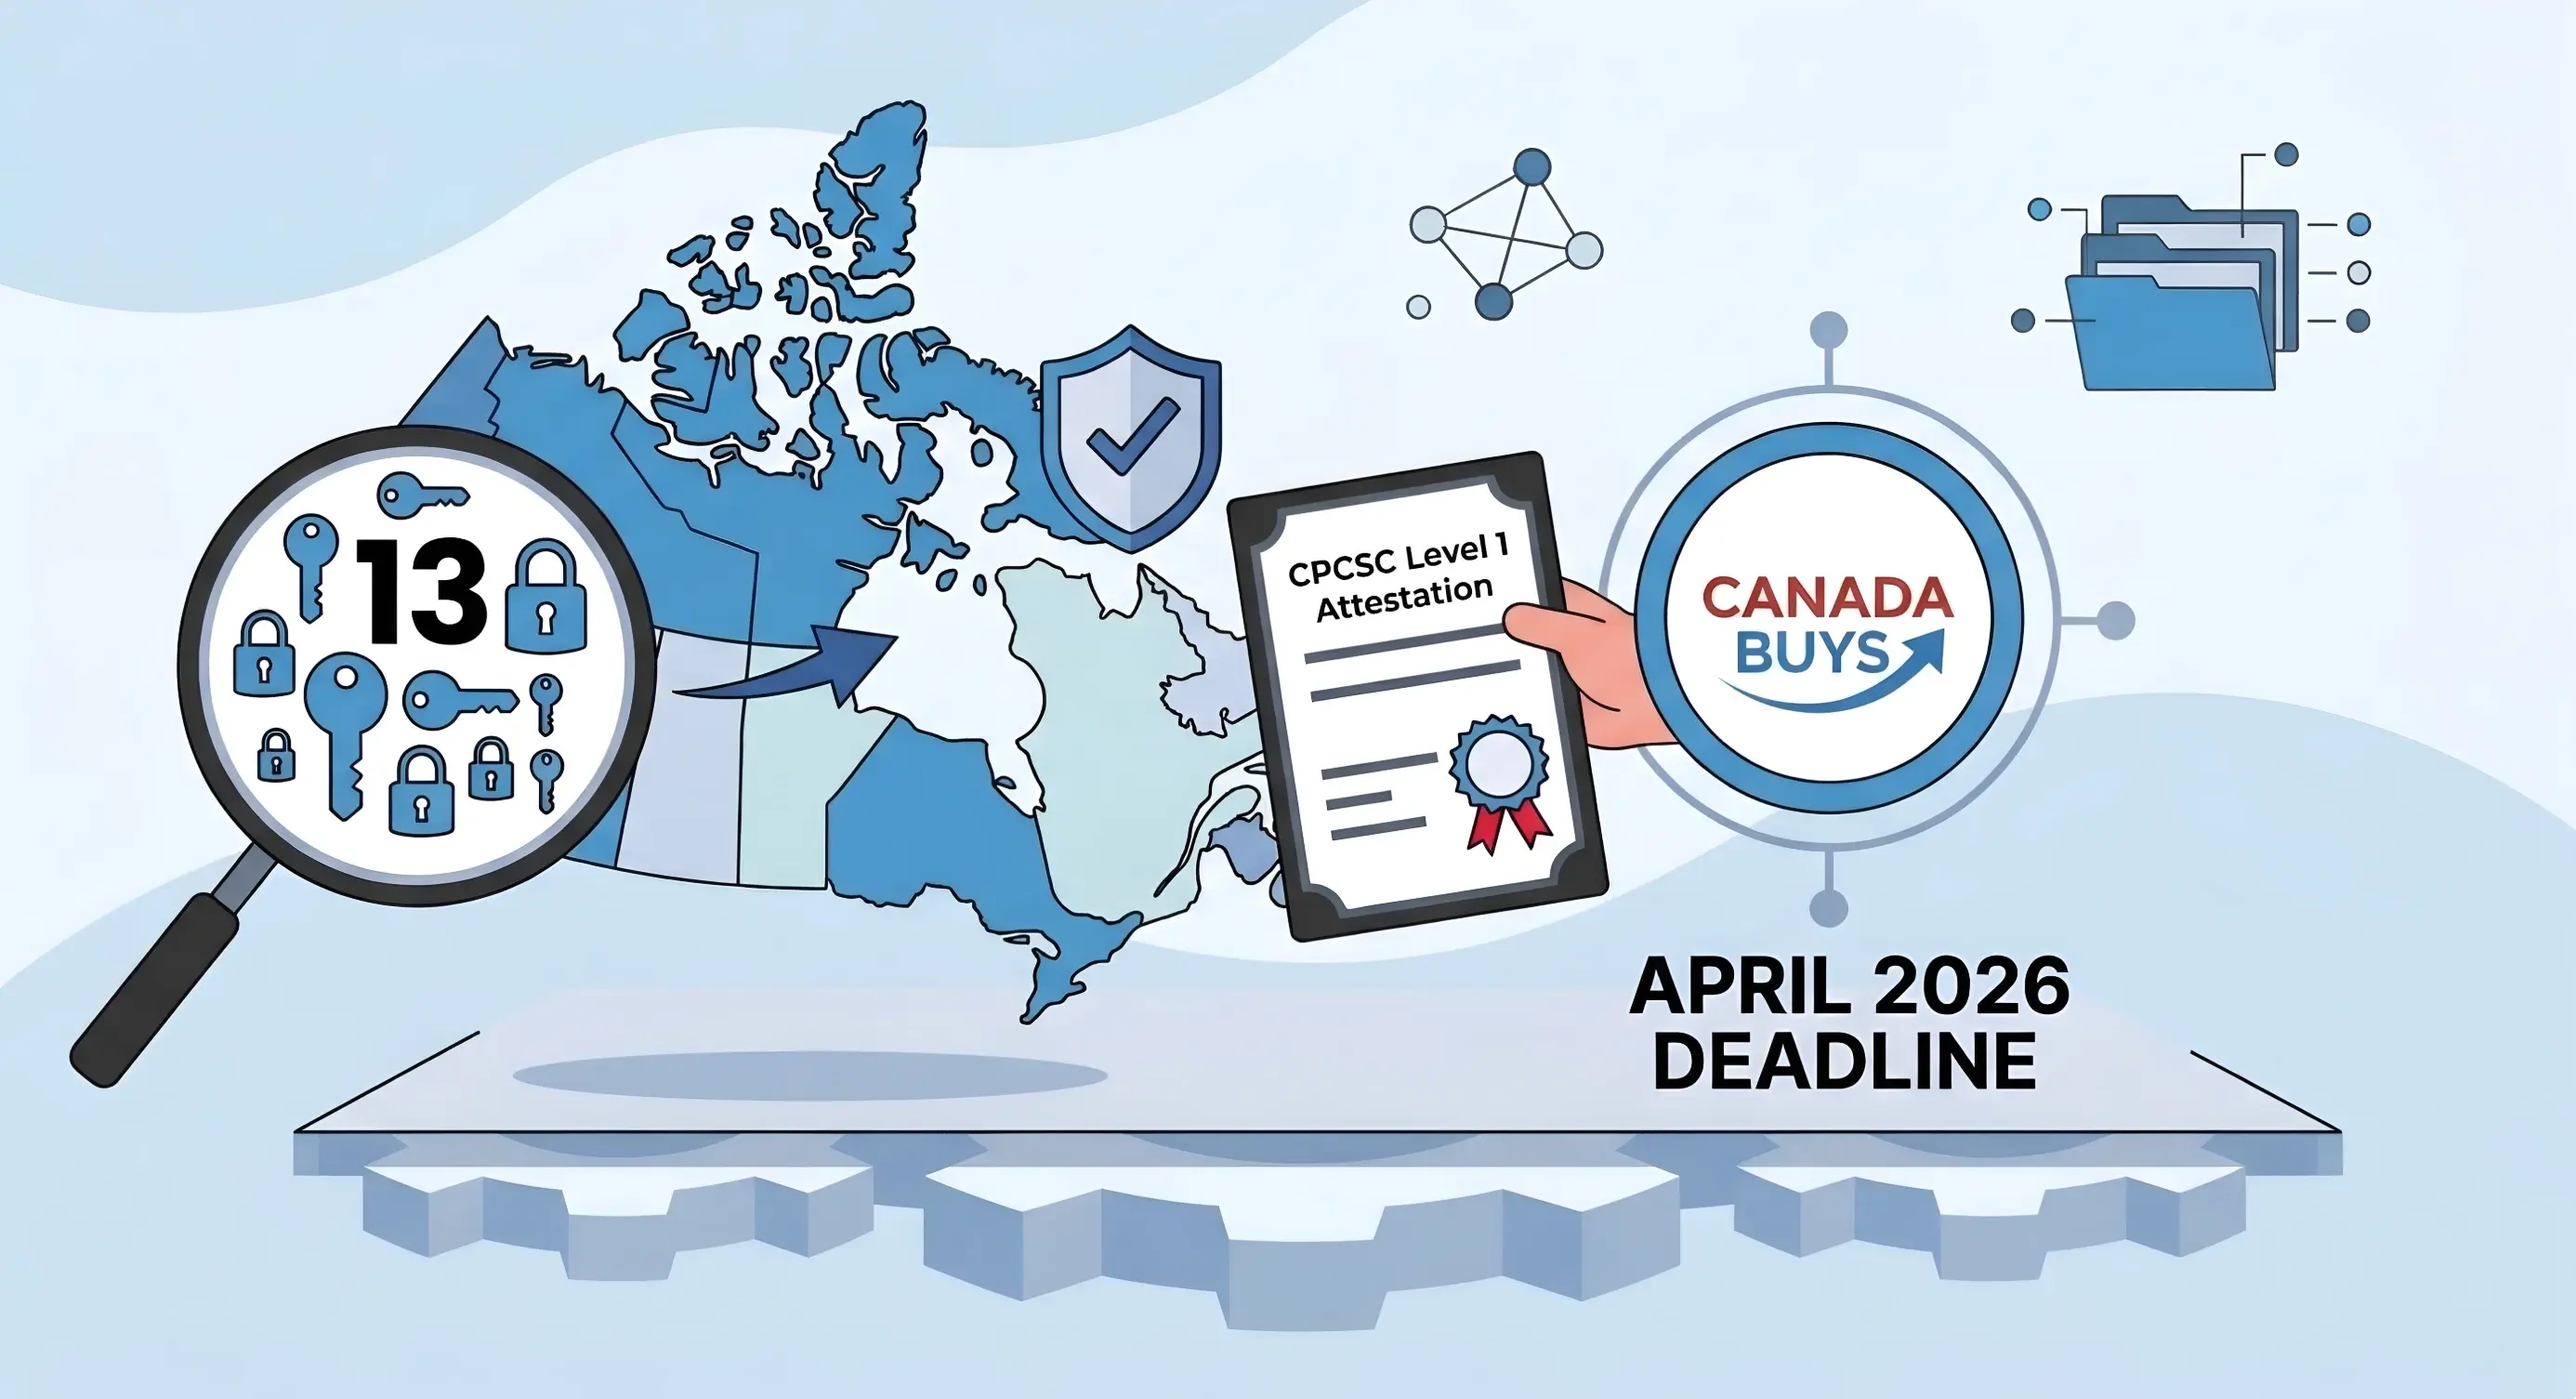
An infographic for the CPCSC Level 1 Attestation featuring a map of Canada and a magnifying glass highlighting "13" keys. A hand holds a certificate next to the CanadaBuys logo. Text warns of an "April 2026 Deadline," all set against a blue background with gears and file folder icons.

CPCSC Level 1 Self-Assessment: A Practical Guide

CPCSC Level 1 is an annual self-assessment of your organization against the security requirements of the Canadian Program for Cyber Security...
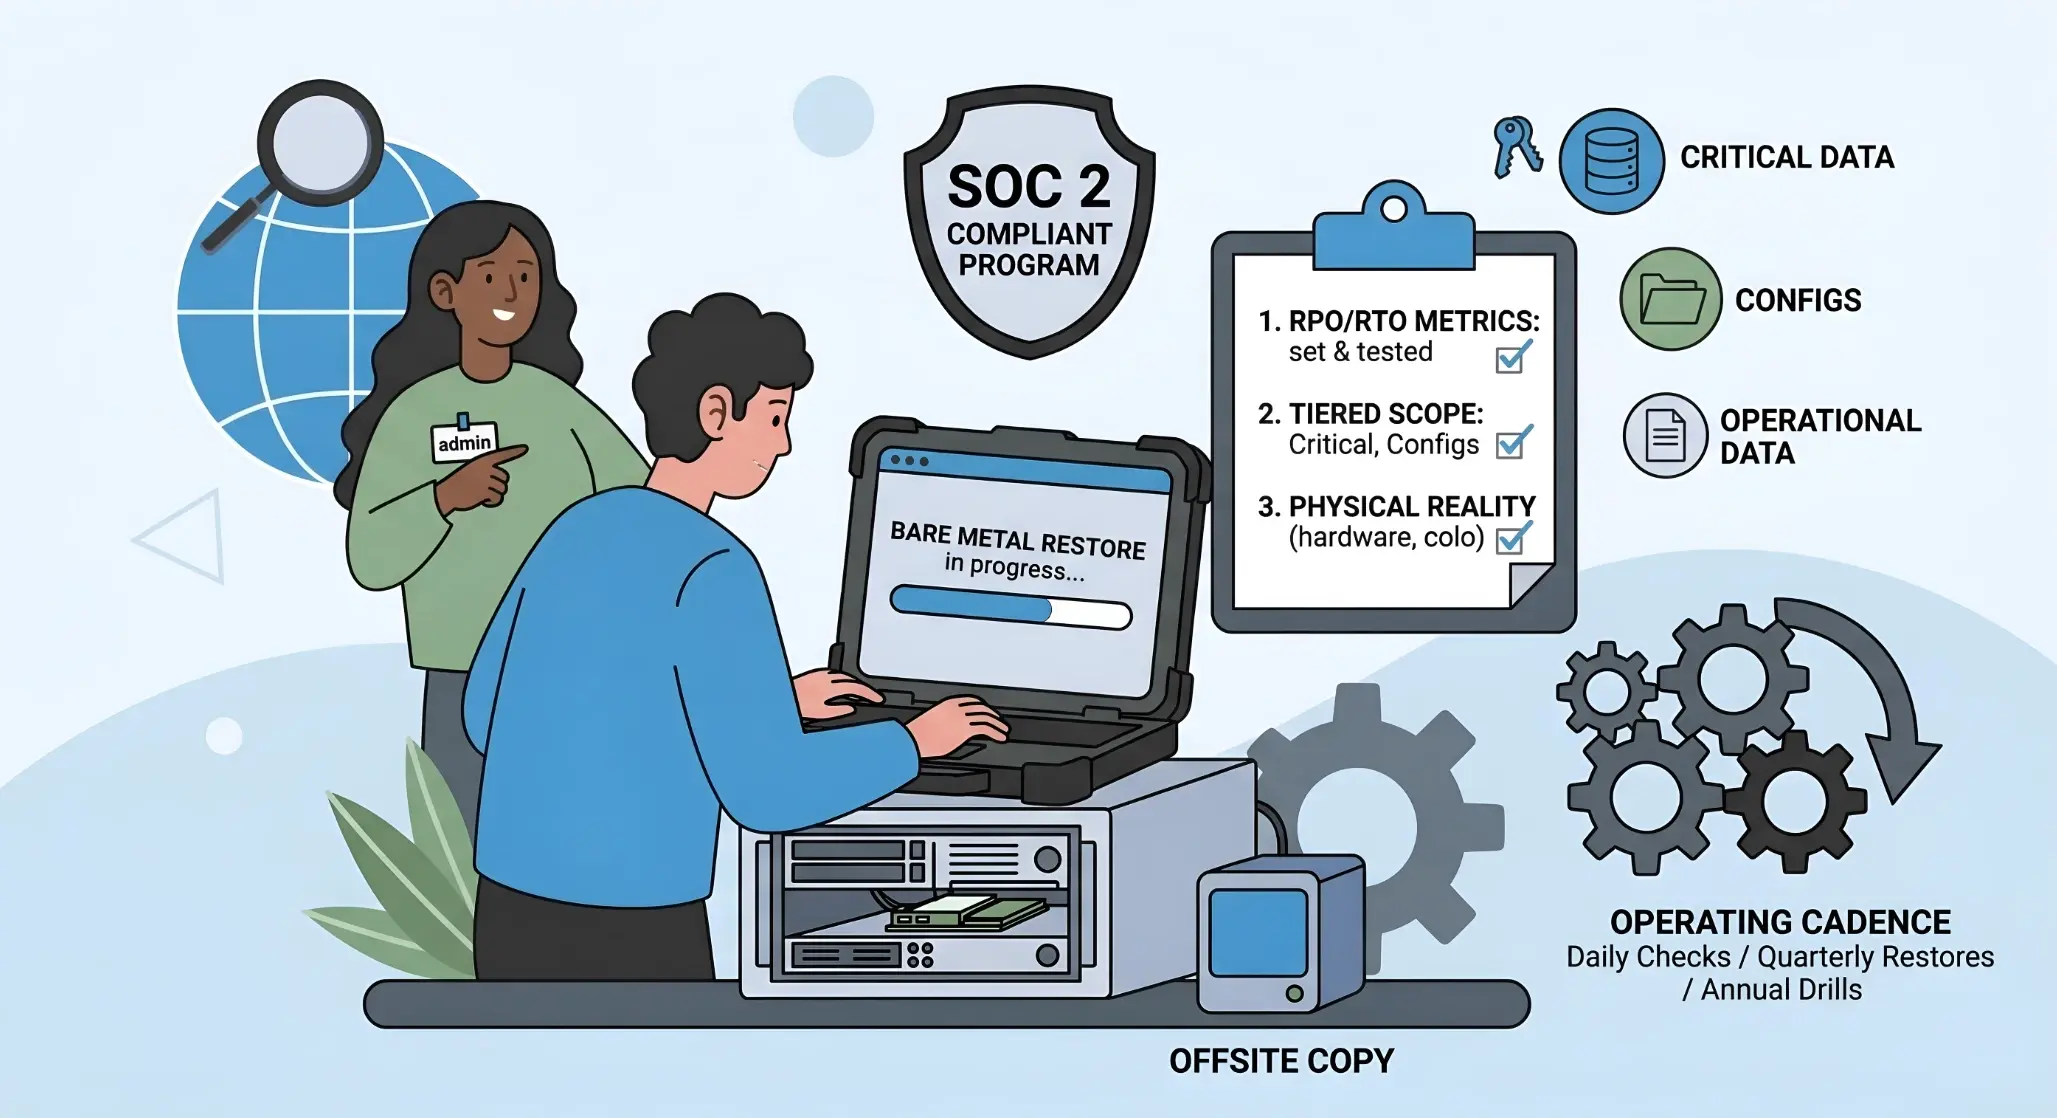
Infographic for SOC 2 Backup and Disaster Recovery. An admin watches a tech perform a "Bare Metal Restore." A checklist highlights RPO/RTO metrics, tiered scope (Critical Data, Configs, Operational Data), and physical hardware. Icons show offsite copies and an operating cadence for drills.

SOC 2 Backup and Disaster Recovery for On-Premise Infrastructure

SOC 2 backup and disaster recovery for on-prem systems comes down to four things auditors check: backups that run and alert on failure, a copy stored...
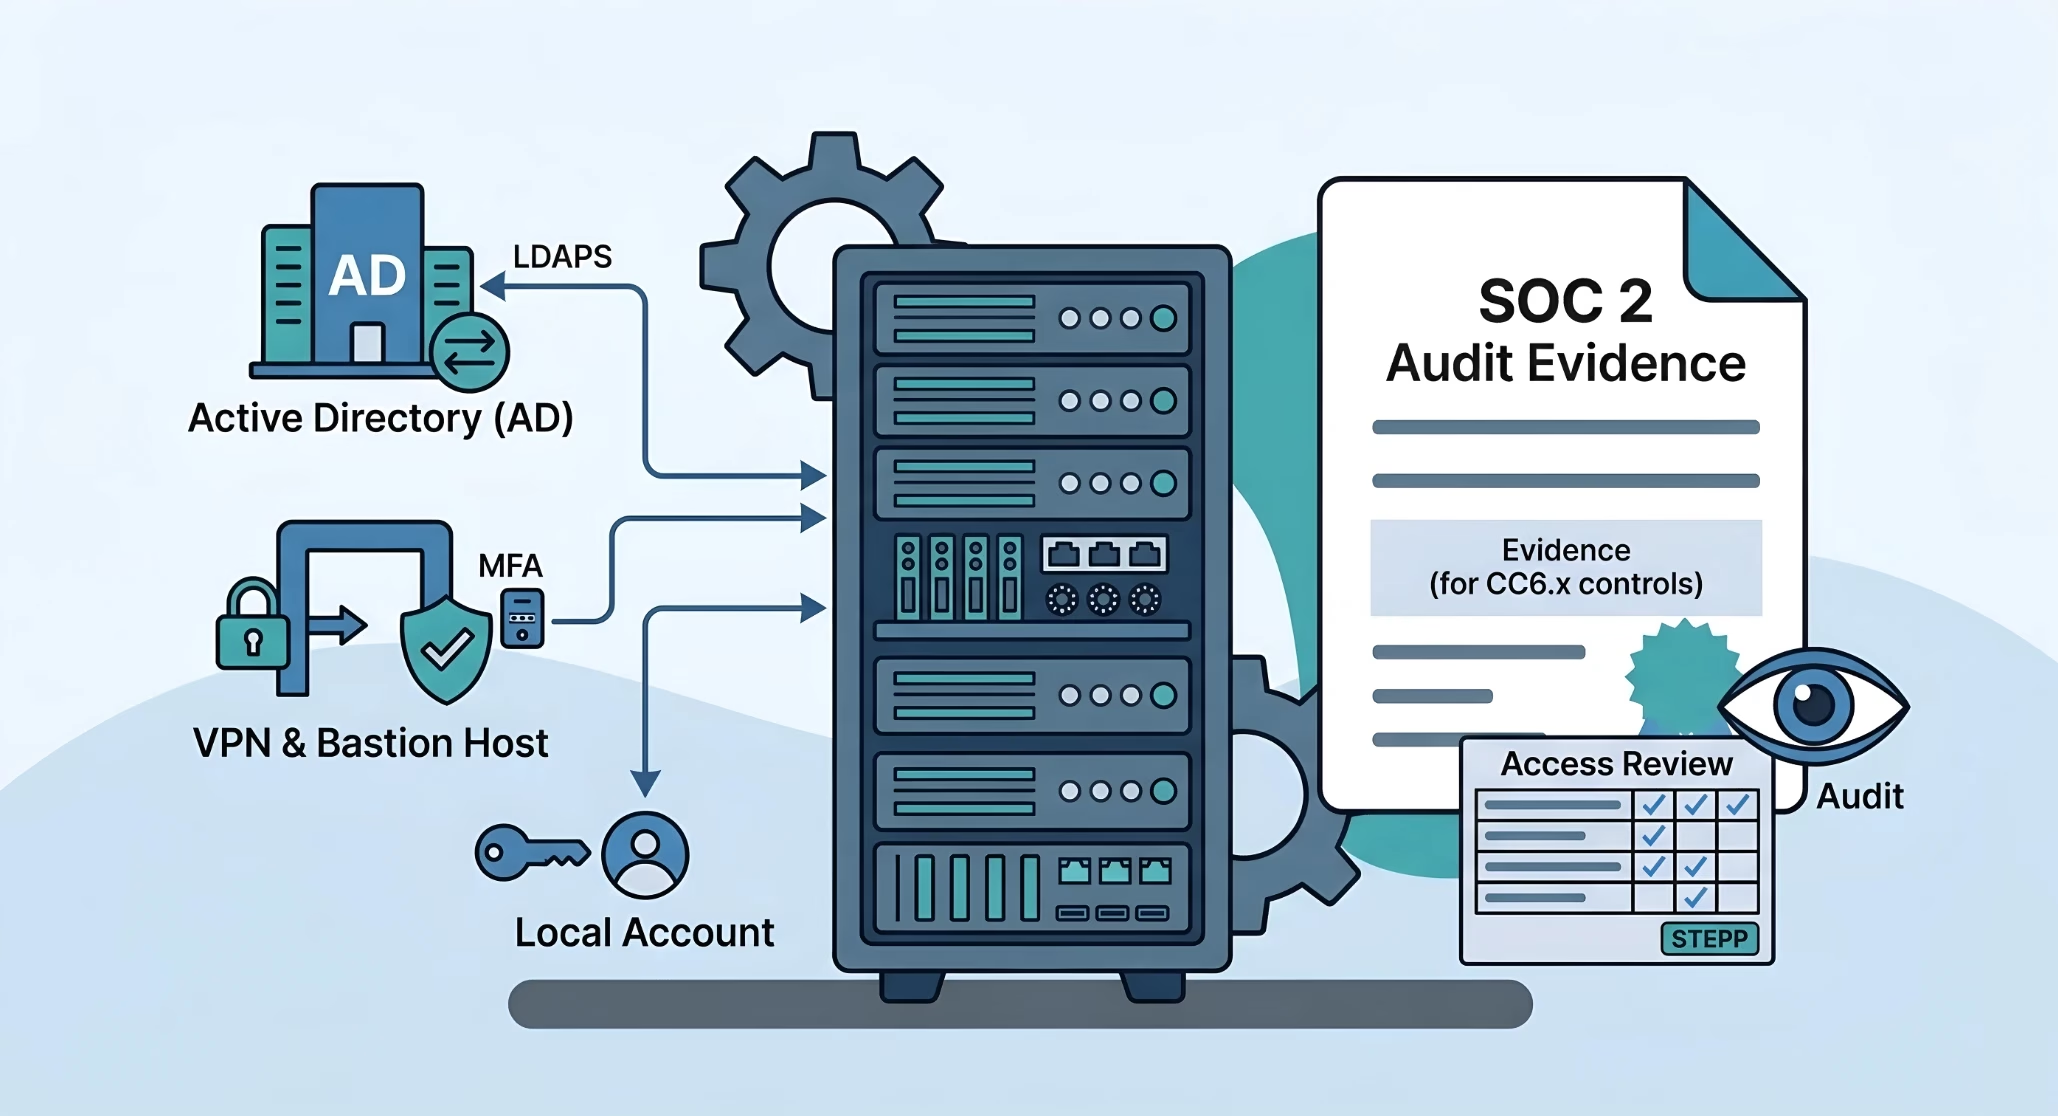
An illustration showing SOC 2 access control for on-premise servers. It depicts Active Directory via LDAPS, VPN and Bastion hosts with MFA, and local accounts connecting to a server rack. A "SOC 2 Audit Evidence" document for CC6.x controls and an access review checklist are shown on the right.

SOC 2 Access Control for On-Premise and Bare Metal Environments

In cloud environments, access control is a managed service. AWS IAM provides centralized identity, Okta handles SSO across every SaaS tool, and the...
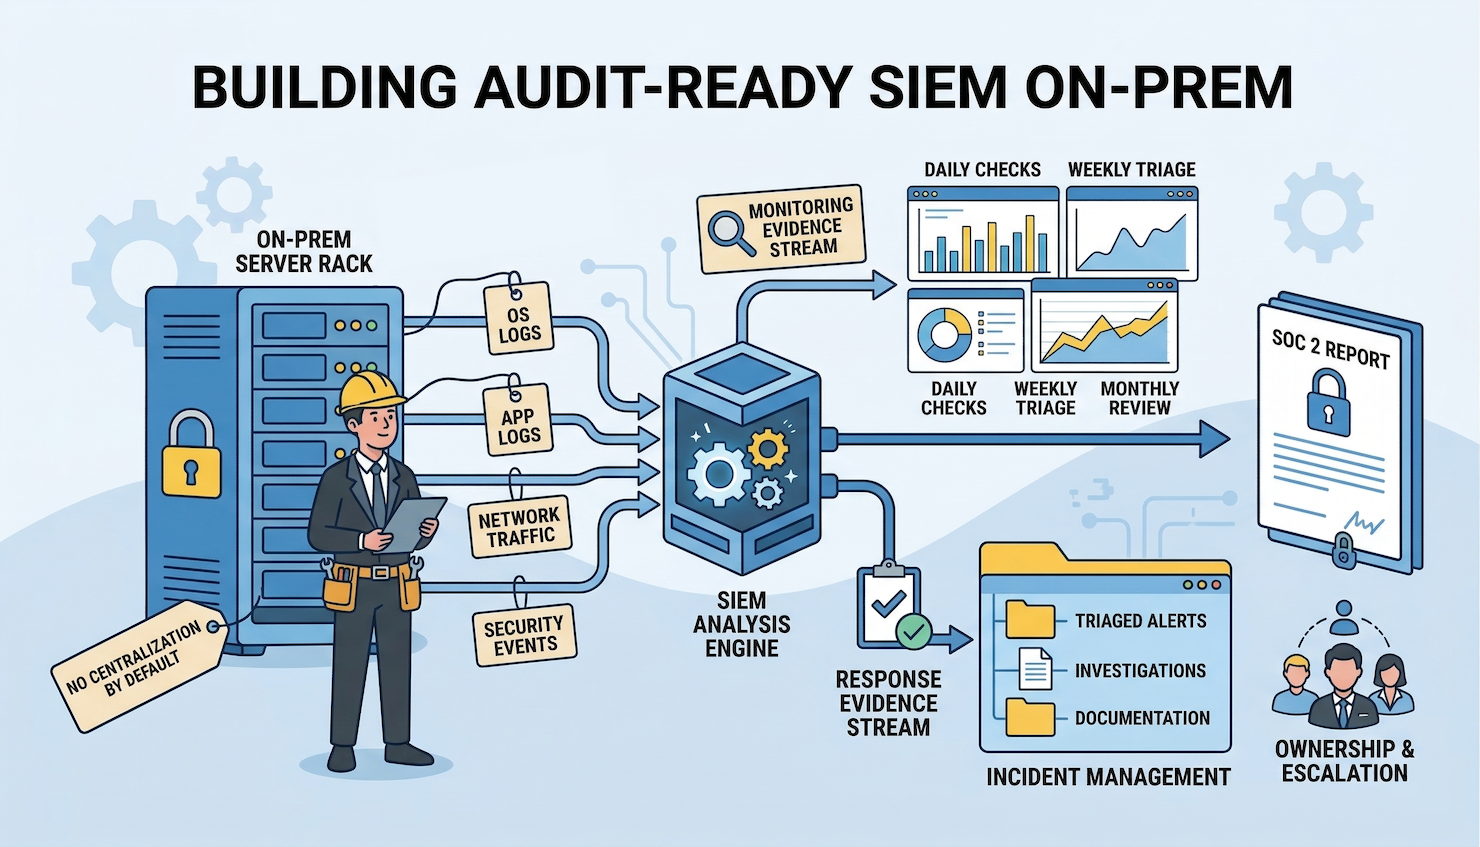
Infographic titled "Building Audit-Ready SIEM On-Prem." It shows logs (OS, App, Network, Security) flowing from a server rack into a SIEM Analysis Engine. This feeds into monitoring streams, incident management (triaged alerts, investigations), and ownership escalation to produce a SOC 2 Report.

SOC 2 Logging and SIEM for Bare Metal Servers

In a cloud environment, centralized logging is a toggle. Enable CloudTrail, turn on VPC Flow Logs, configure GuardDuty, and the compliance platform...
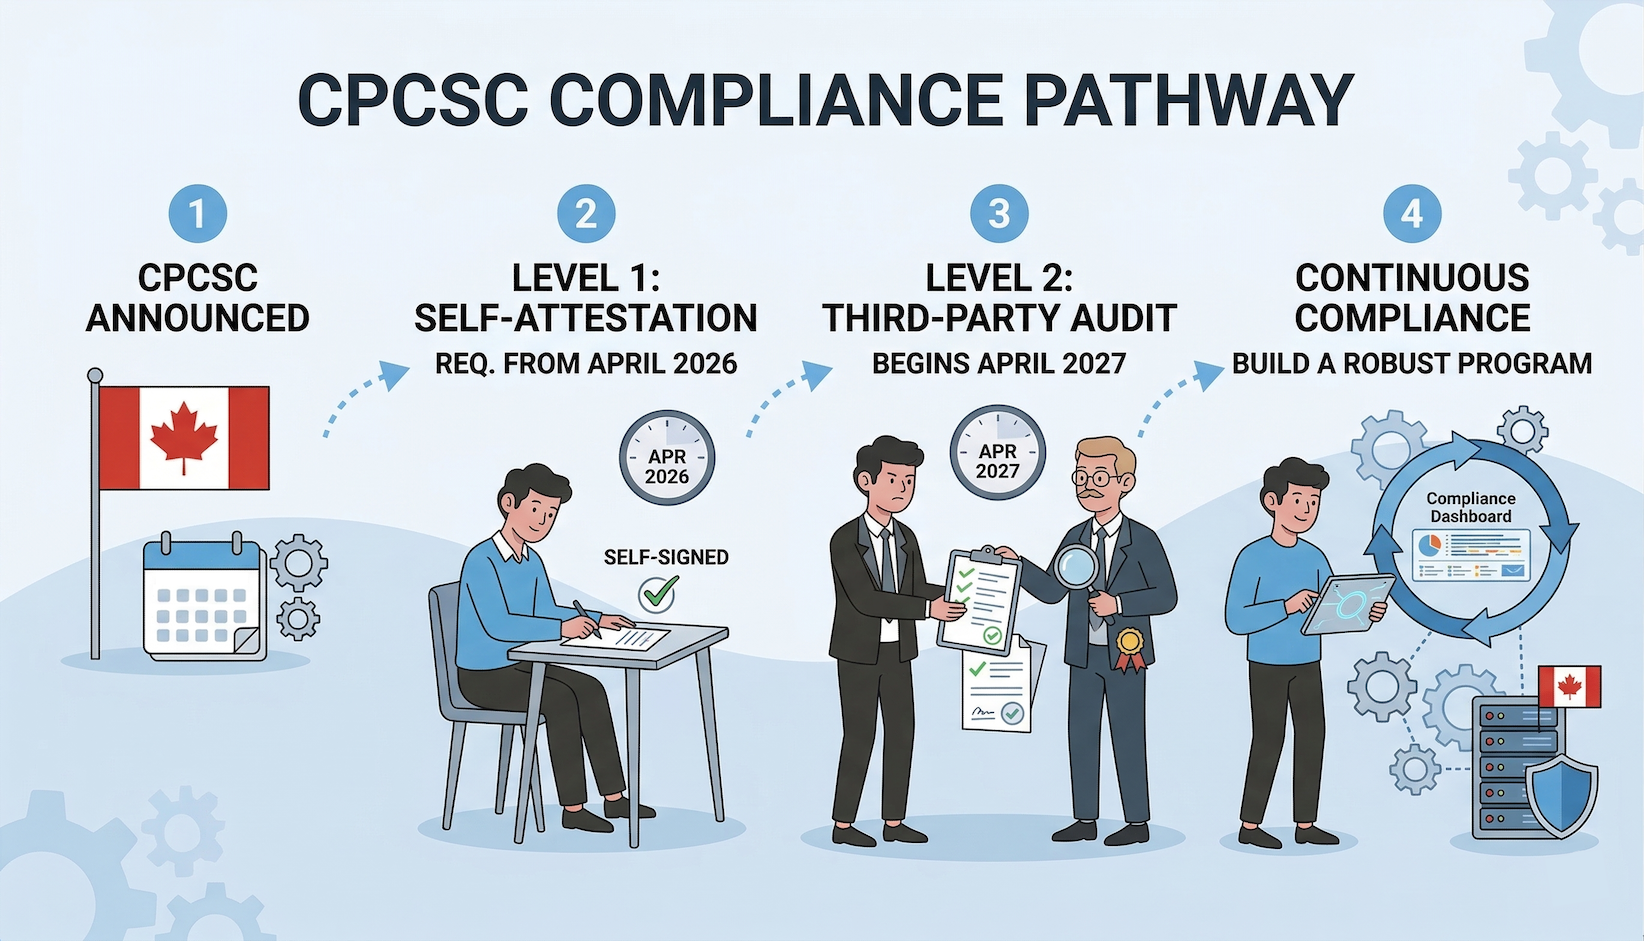
Infographic titled "CPCSC Compliance Pathway" outlining four stages for Canadian defence contractors: 1. CPCSC Announced, 2. Level 1 Self-Attestation (April 2026), 3. Level 2 Third-Party Audit (April 2027), and 4. Continuous Compliance via a robust program and digital dashboard.

CPCSC: What Defence Contractors Need Before April 2026

The Canadian Program for Cyber Security Certification (CPCSC) is Canada's mandatory cybersecurity certification for companies bidding on Department...
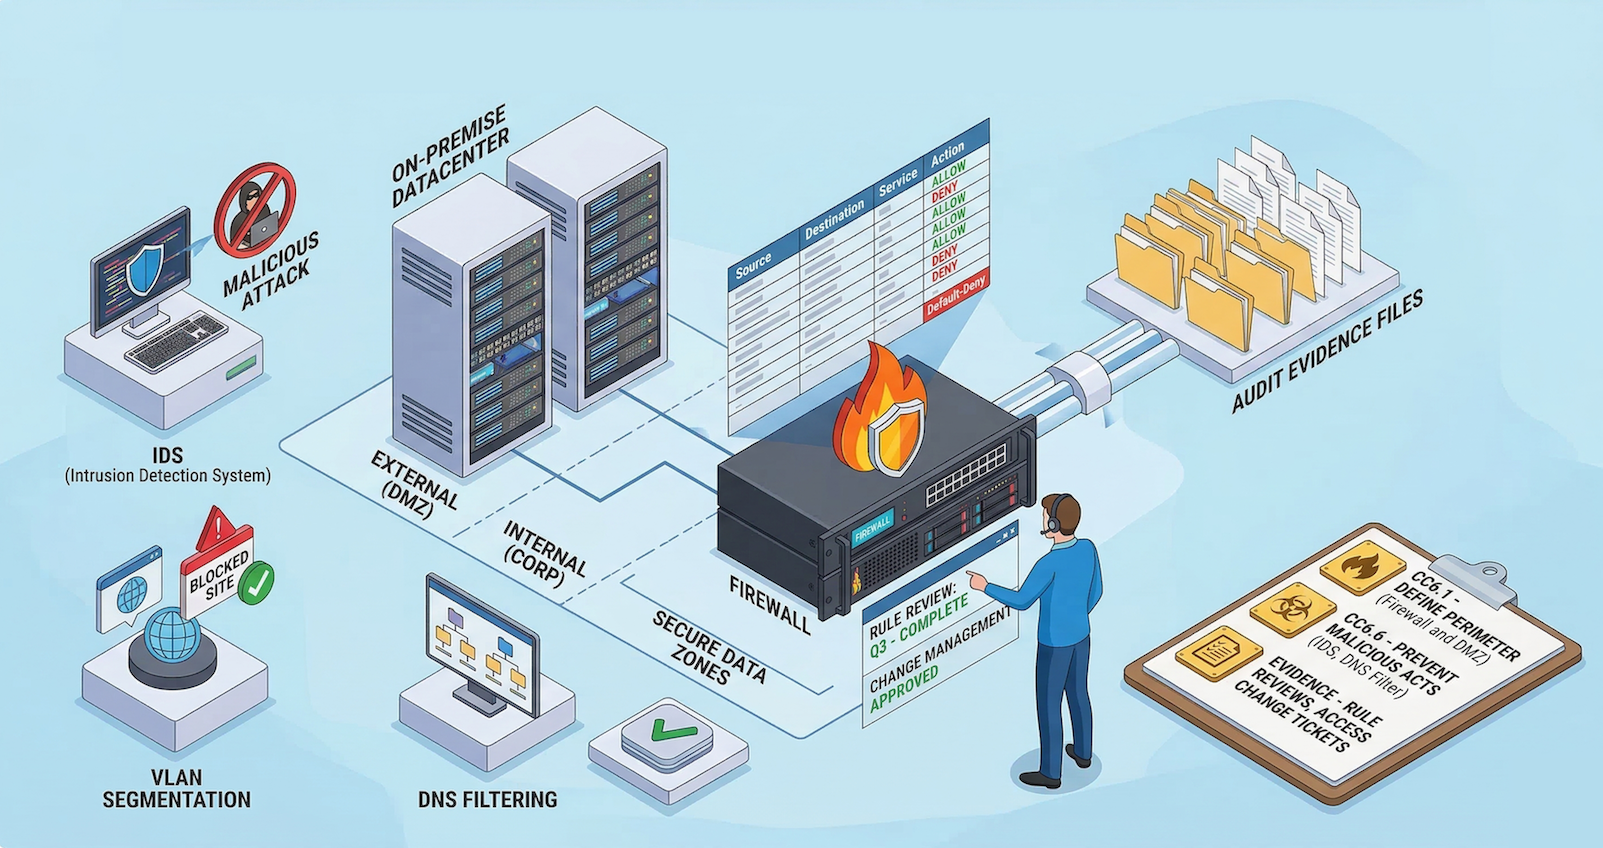
An isometric infographic titled "SOC 2 Compliance: Strengthening On-Premise Infrastructure." It shows a technician managing a firewall, IDS, and VLAN segmentation to protect data zones from malicious attacks. A clipboard lists CC6.1 and CC6.6 controls, leading to organized audit evidence files.

SOC 2 Network Security Controls for On-Premise Environments

Every SOC 2 guide on network security assumes the infrastructure lives in AWS. The advice is always the same: configure security groups, enable VPC...
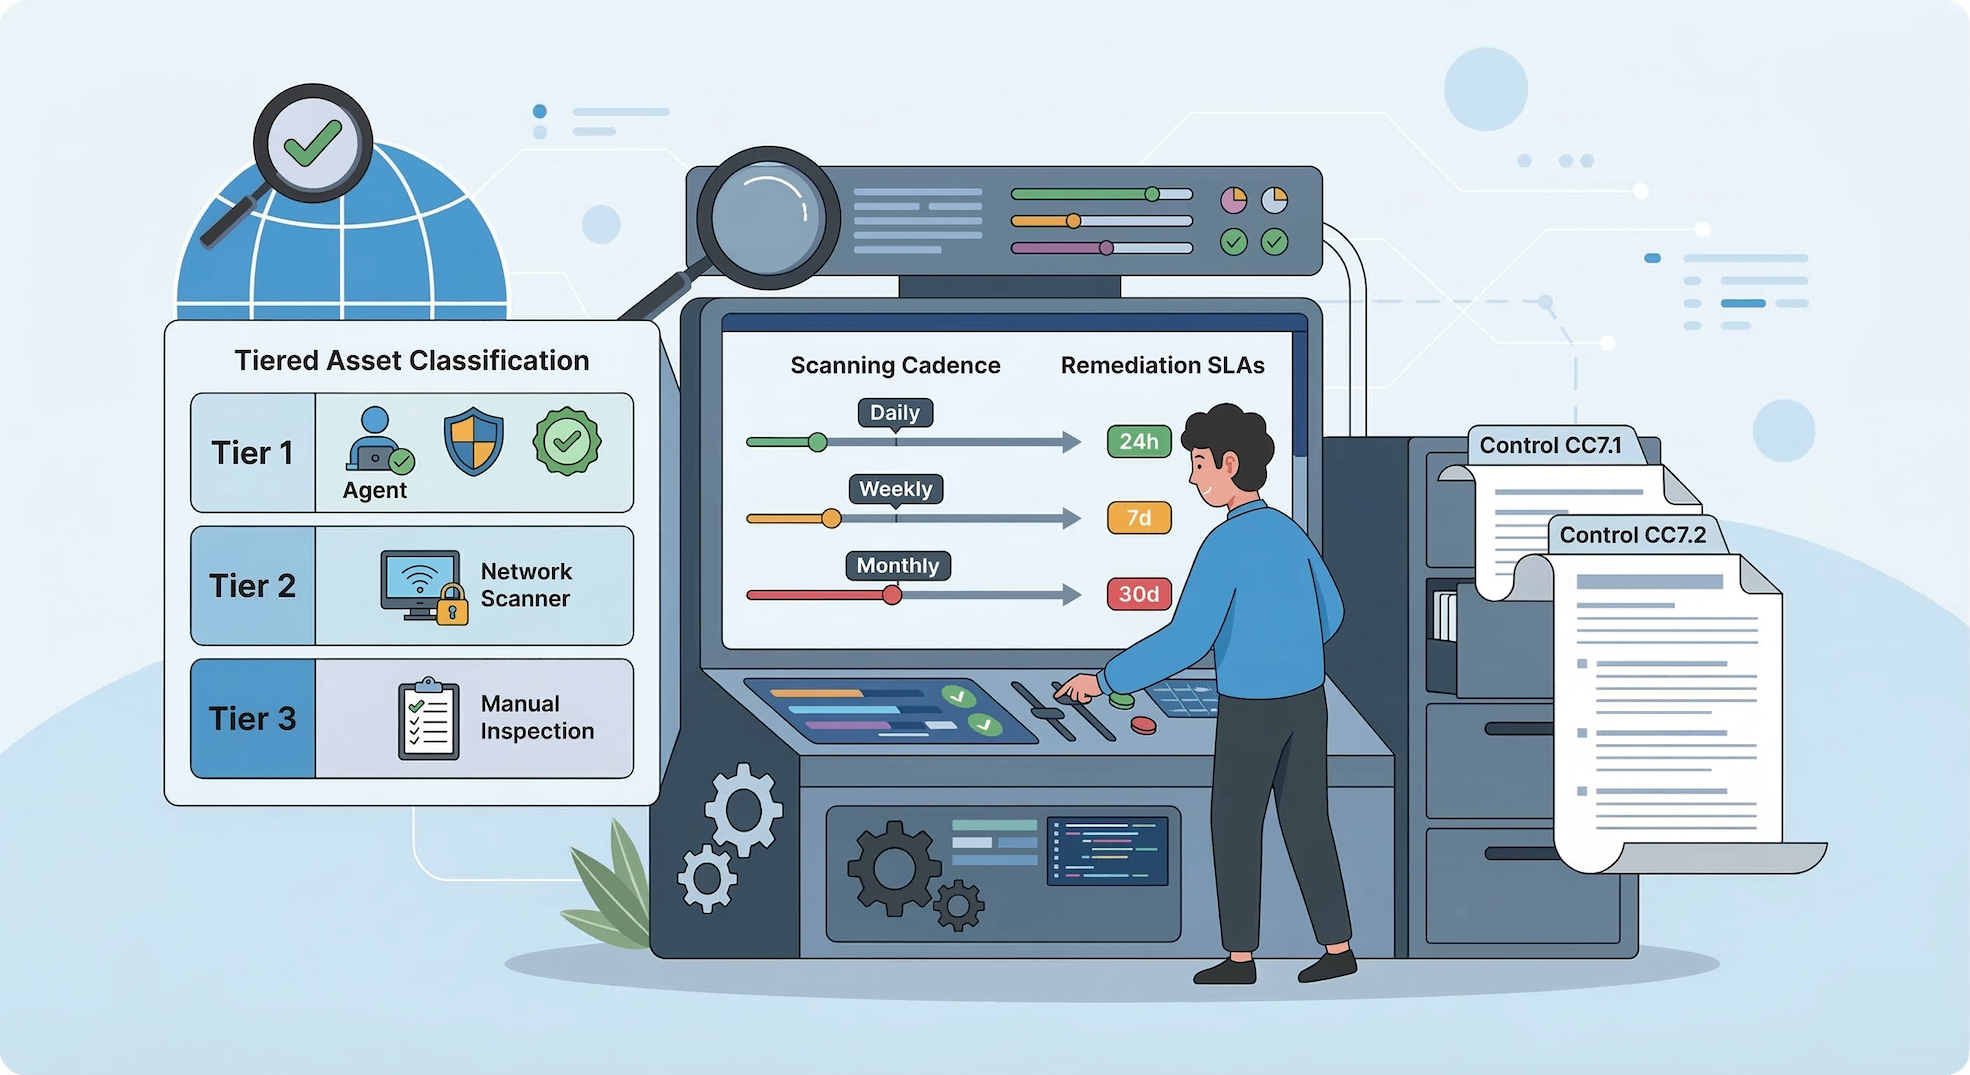
An illustration of a technician managing a security operations center for SOC 2 compliance. It features a tiered asset classification chart (Agent, Network Scanner, Manual Inspection), a dashboard showing scanning cadences and remediation SLAs, and filing cabinets with audit control documents.

SOC 2 Vulnerability Scanning for On-Prem Servers

Every SOC 2 vulnerability scanning guide assumes the same starting point: connect a cloud-native scanner, enable automated assessments, and let the...
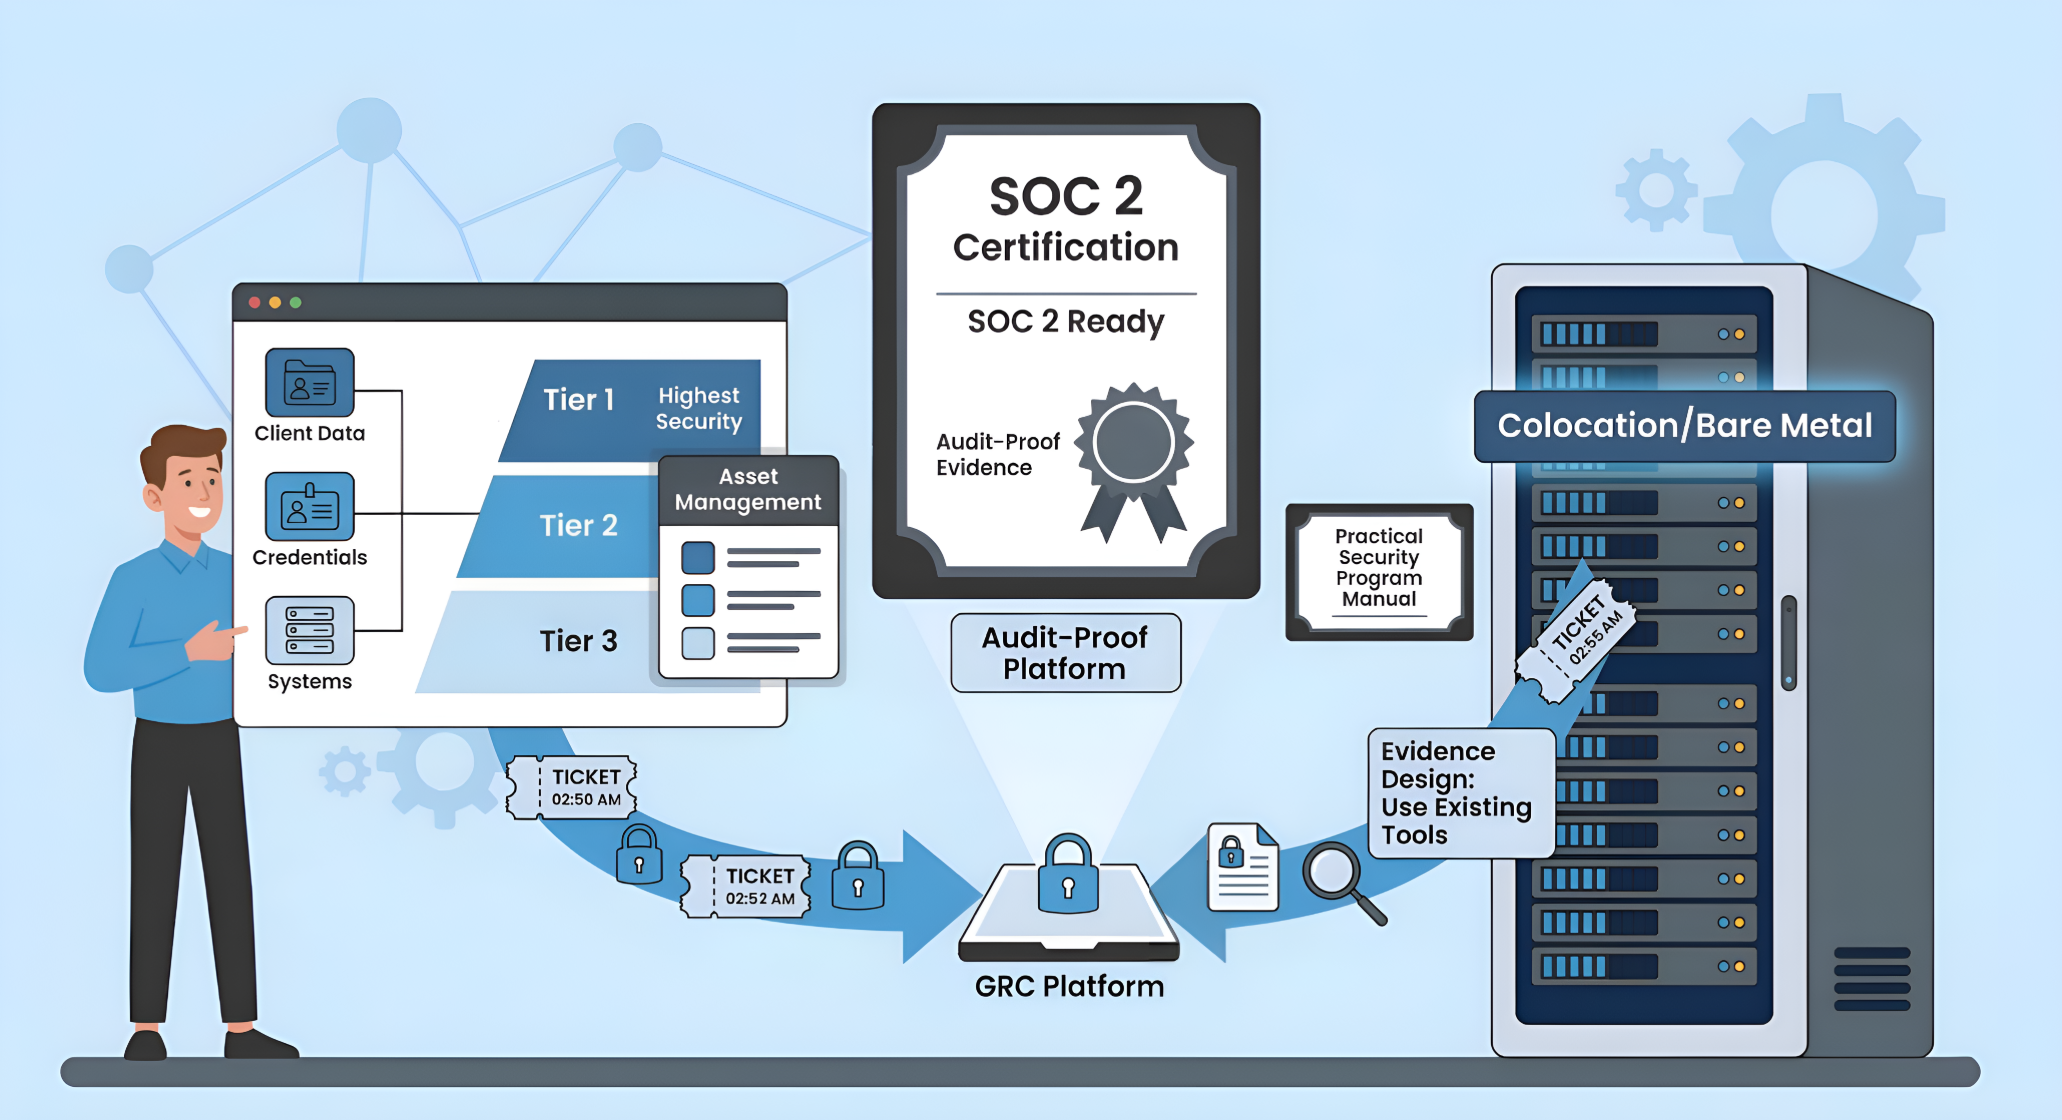
Infographic showing SOC 2 certification for Colocation/Bare Metal environments. It depicts an Audit-Proof Platform (GRC) collecting evidence like tickets and asset management data to achieve "SOC 2 Ready" status outside of standard AWS-style clouds.

SOC 2 Readiness for Bare Metal SaaS: What to Expect

A pattern keeps showing up. A SaaS company that has been running successfully for years, sometimes a decade or more, gets a call from a major...
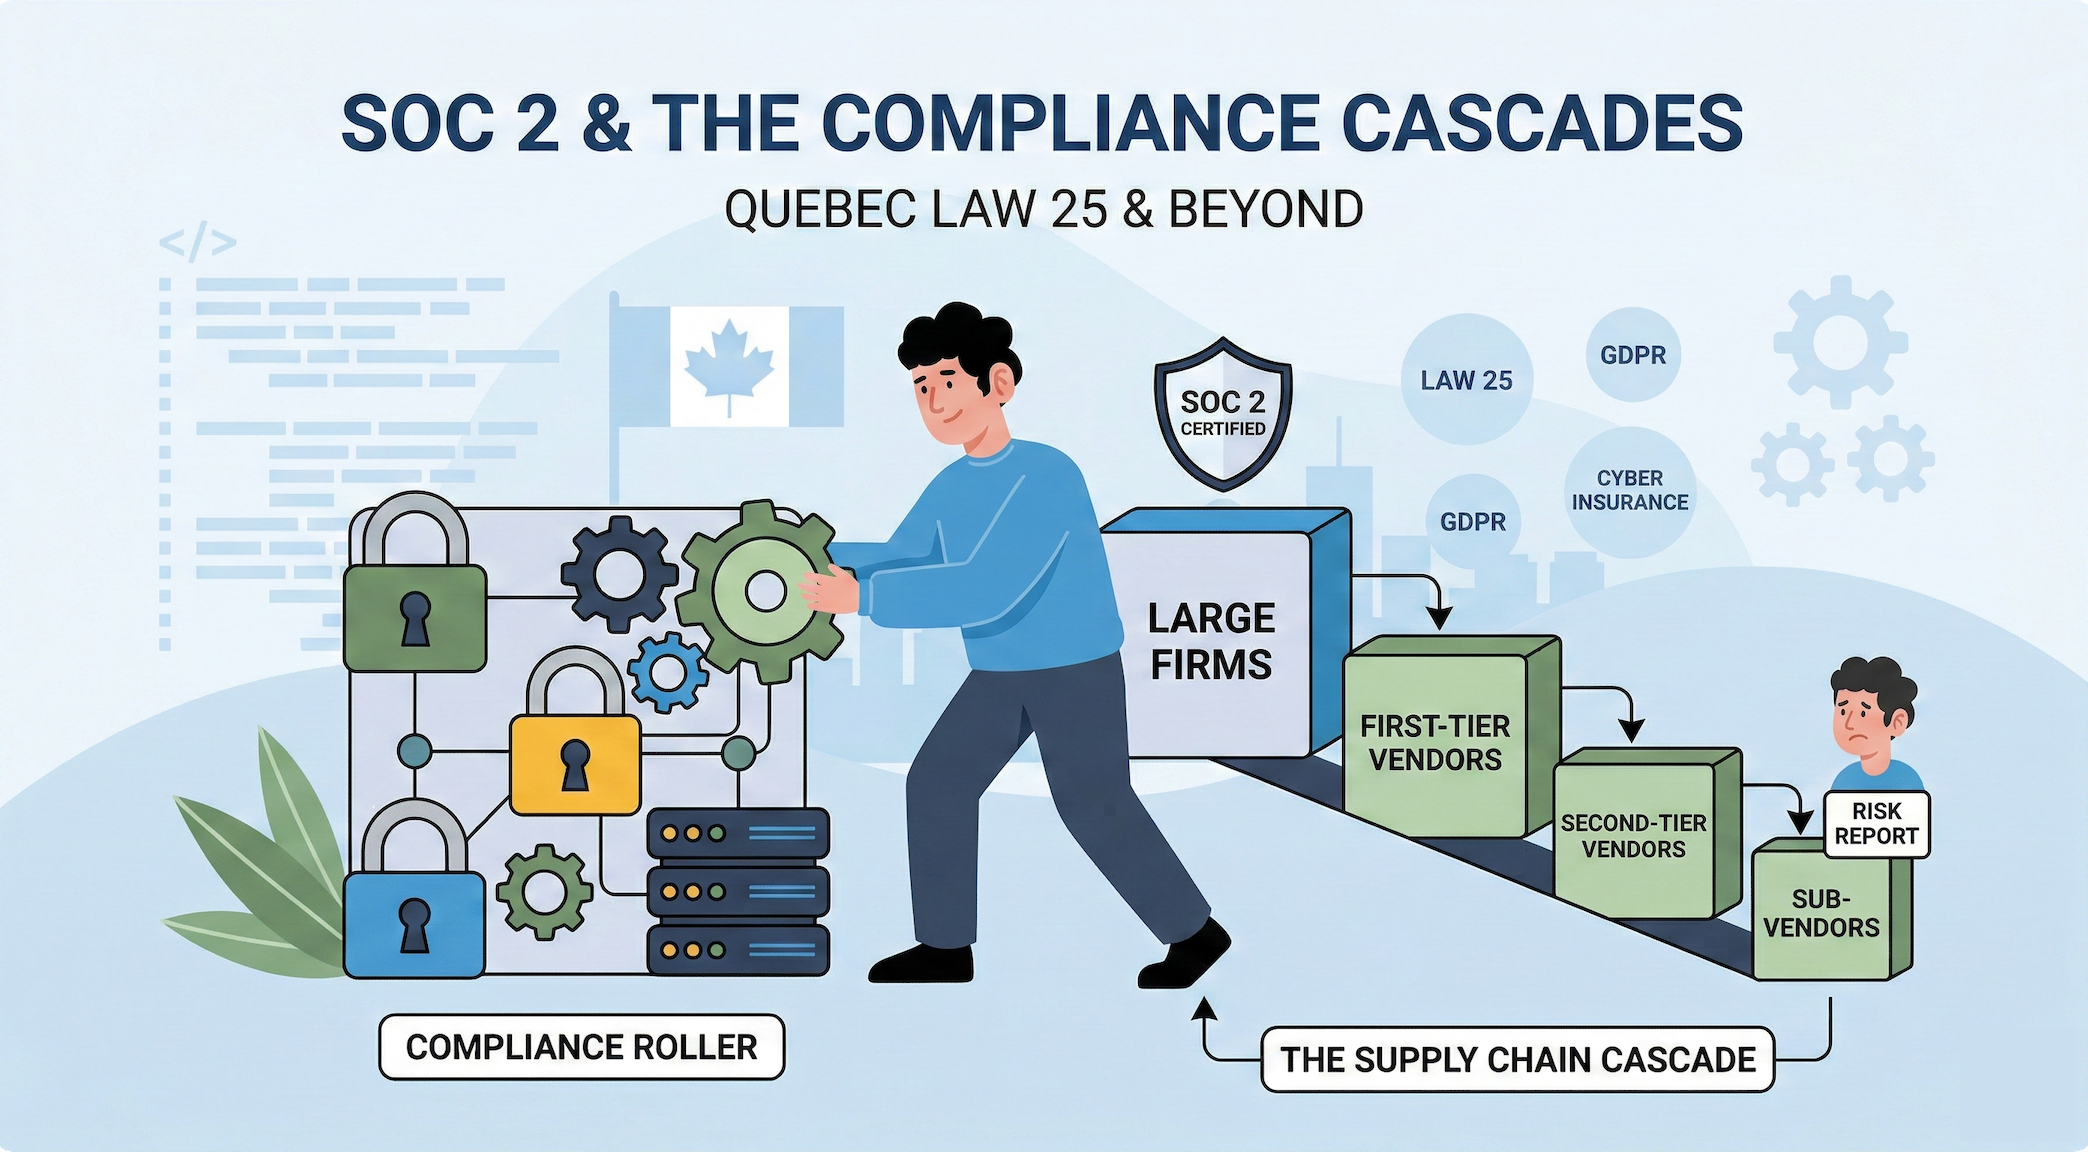
An infographic titled "SOC 2 & THE COMPLIANCE CASCADES" depicts a "Compliance Roller" pushing a "Supply Chain Cascade" of blocks from Large Firms down to Sub-Vendors. This illustrates how Law 25 and GDPR requirements create a chain reaction of SOC 2 necessity for small vendors.

The SOC 2 Snowball: How Law 25 Pushes Compliance Down Supply Chains

SOC 2, and compliance in general, is self-perpetuating. Once a company achieves certification, one of the first things the framework requires is...
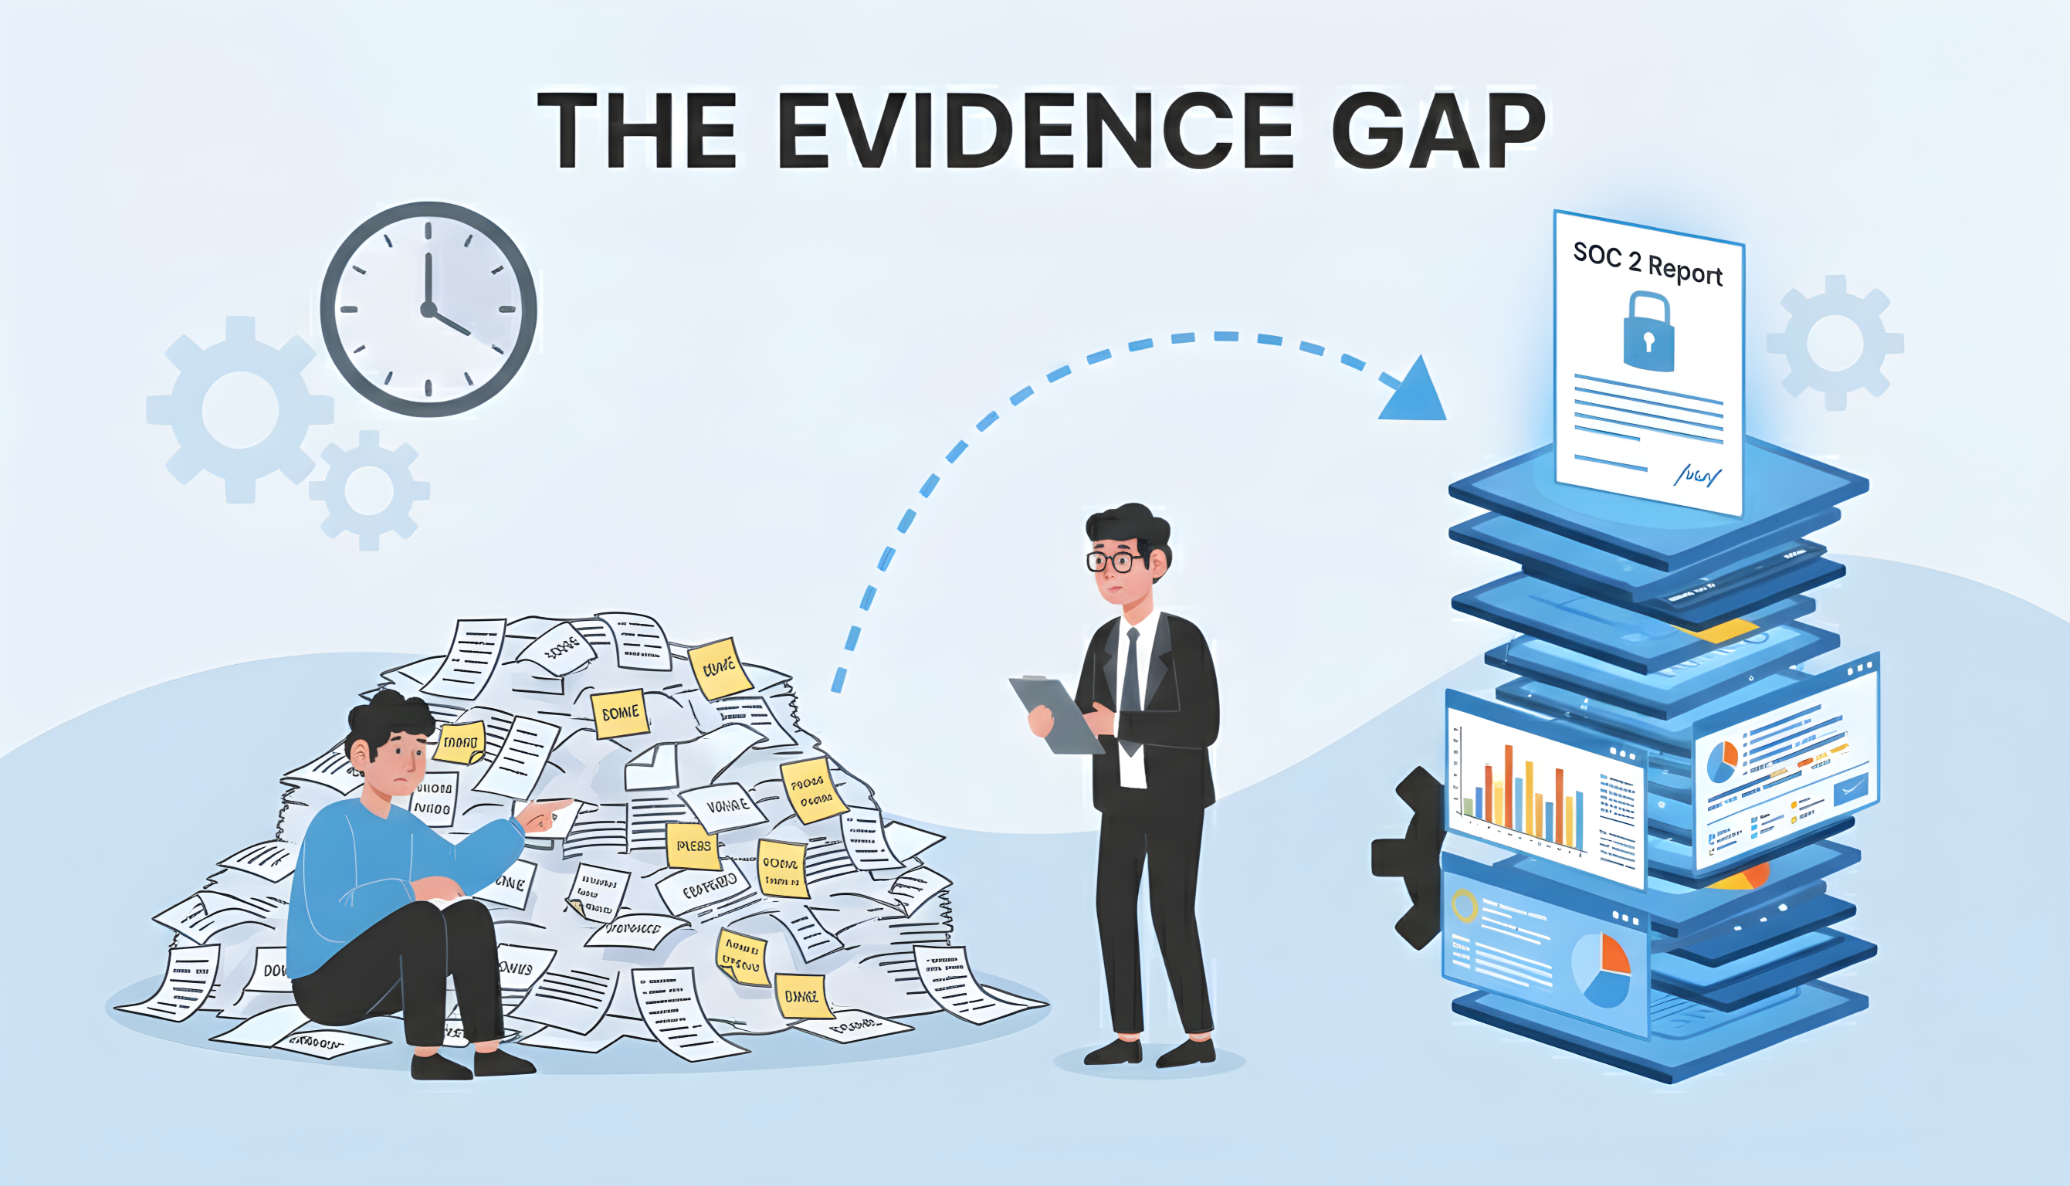
An illustration titled "THE EVIDENCE GAP." On the left, a person sits by a messy pile of papers, representing manual chaos. On the right, a neat stack of digital dashboards leads to a "SOC 2 Report." A blue arrow points from the clutter toward the streamlined, automated digital solution.

Bridging the Evidence Gap: How to Turn Solid Security into SOC 2 Compliance

The most common compliance gap has nothing to do with missing controls. It's missing evidence.

What we see often is that technically competent teams...
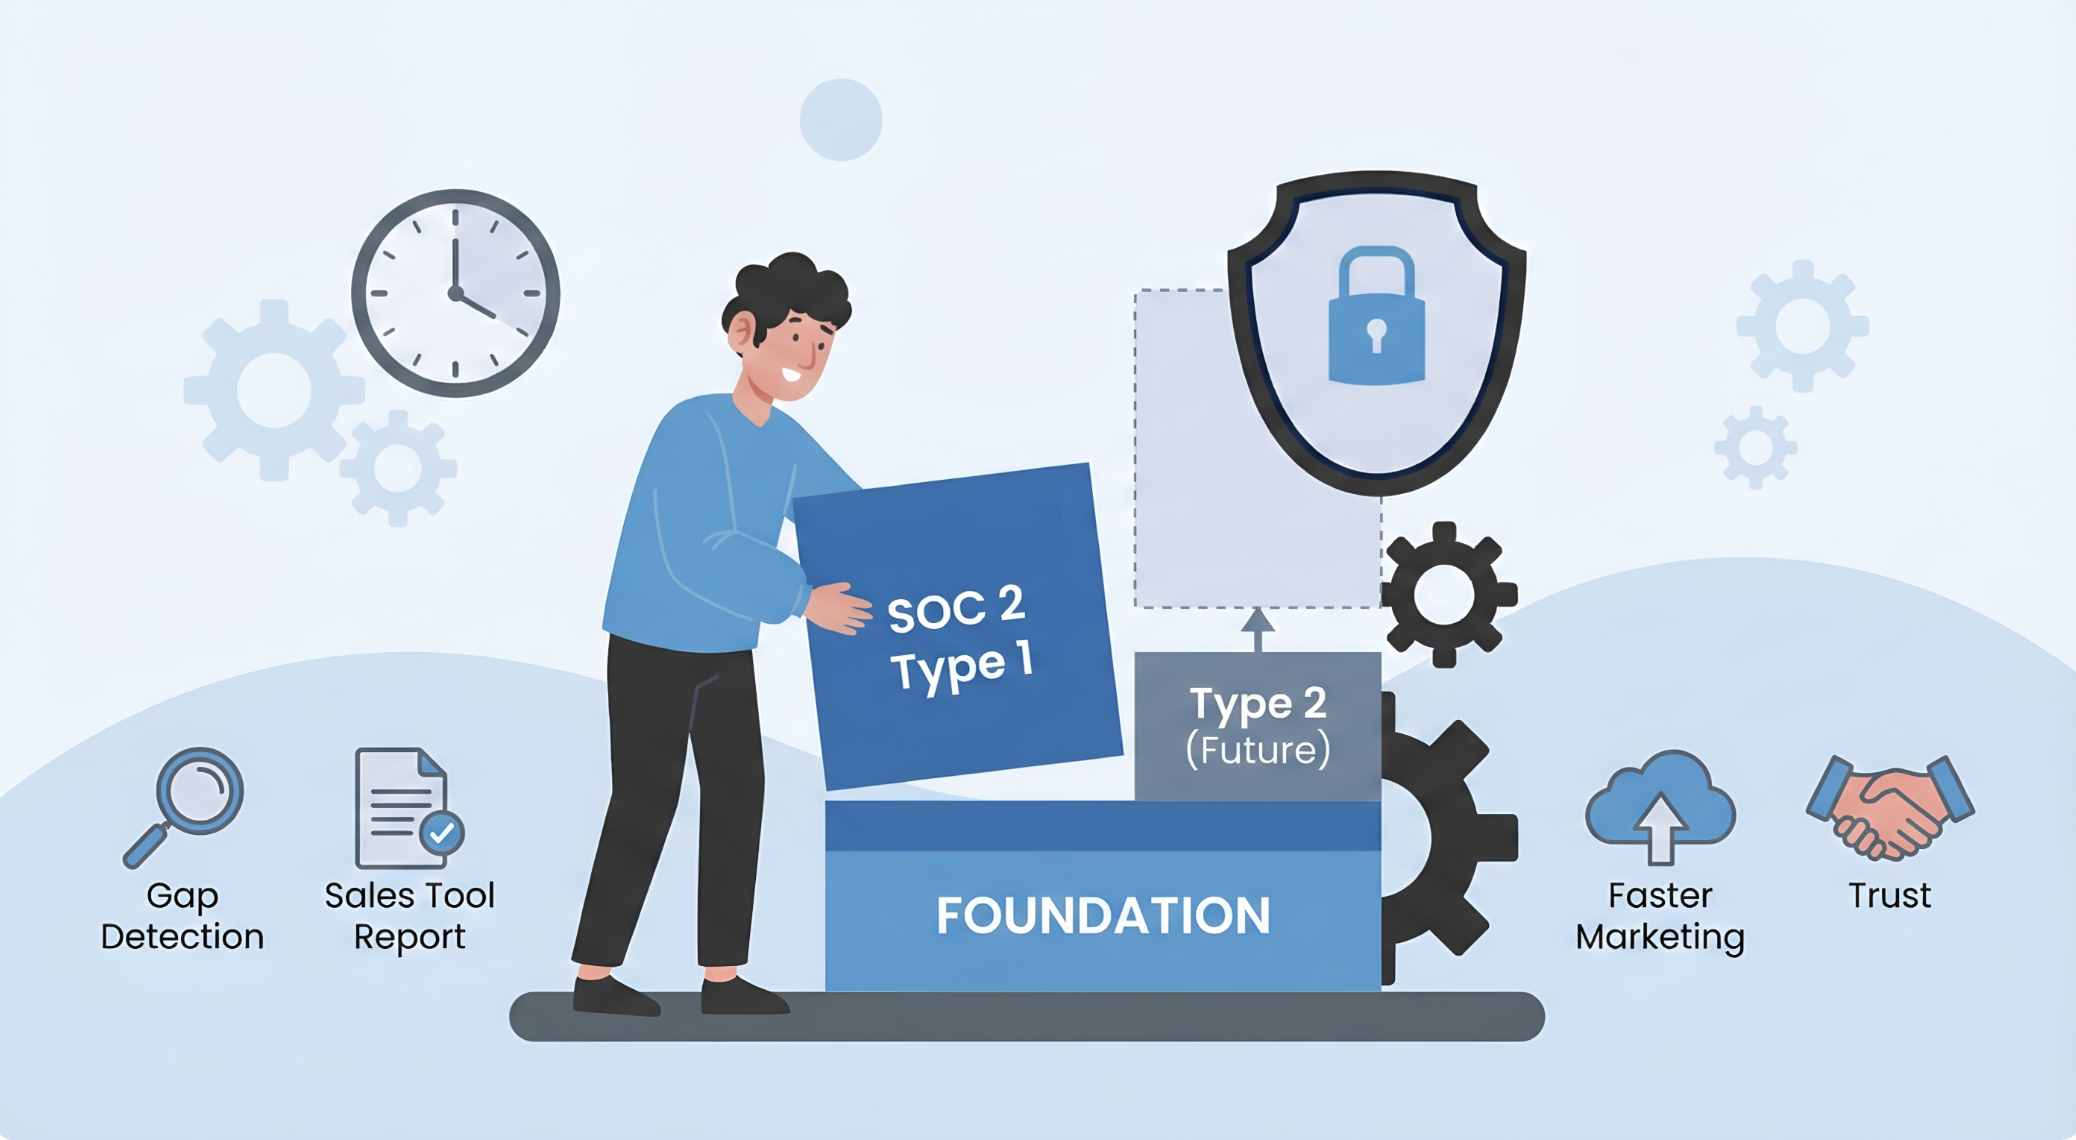
Illustration of the SOC 2 compliance journey progressing from a Type 1 audit to a Type 2 audit.

Why We Recommend SOC 2 Type 1 (Even Though You Don't Need It)

Most companies skip straight to Type 2. It's the *real* SOC 2, right? Type 1 is just not worth it. We used to think that way too. We've changed our...
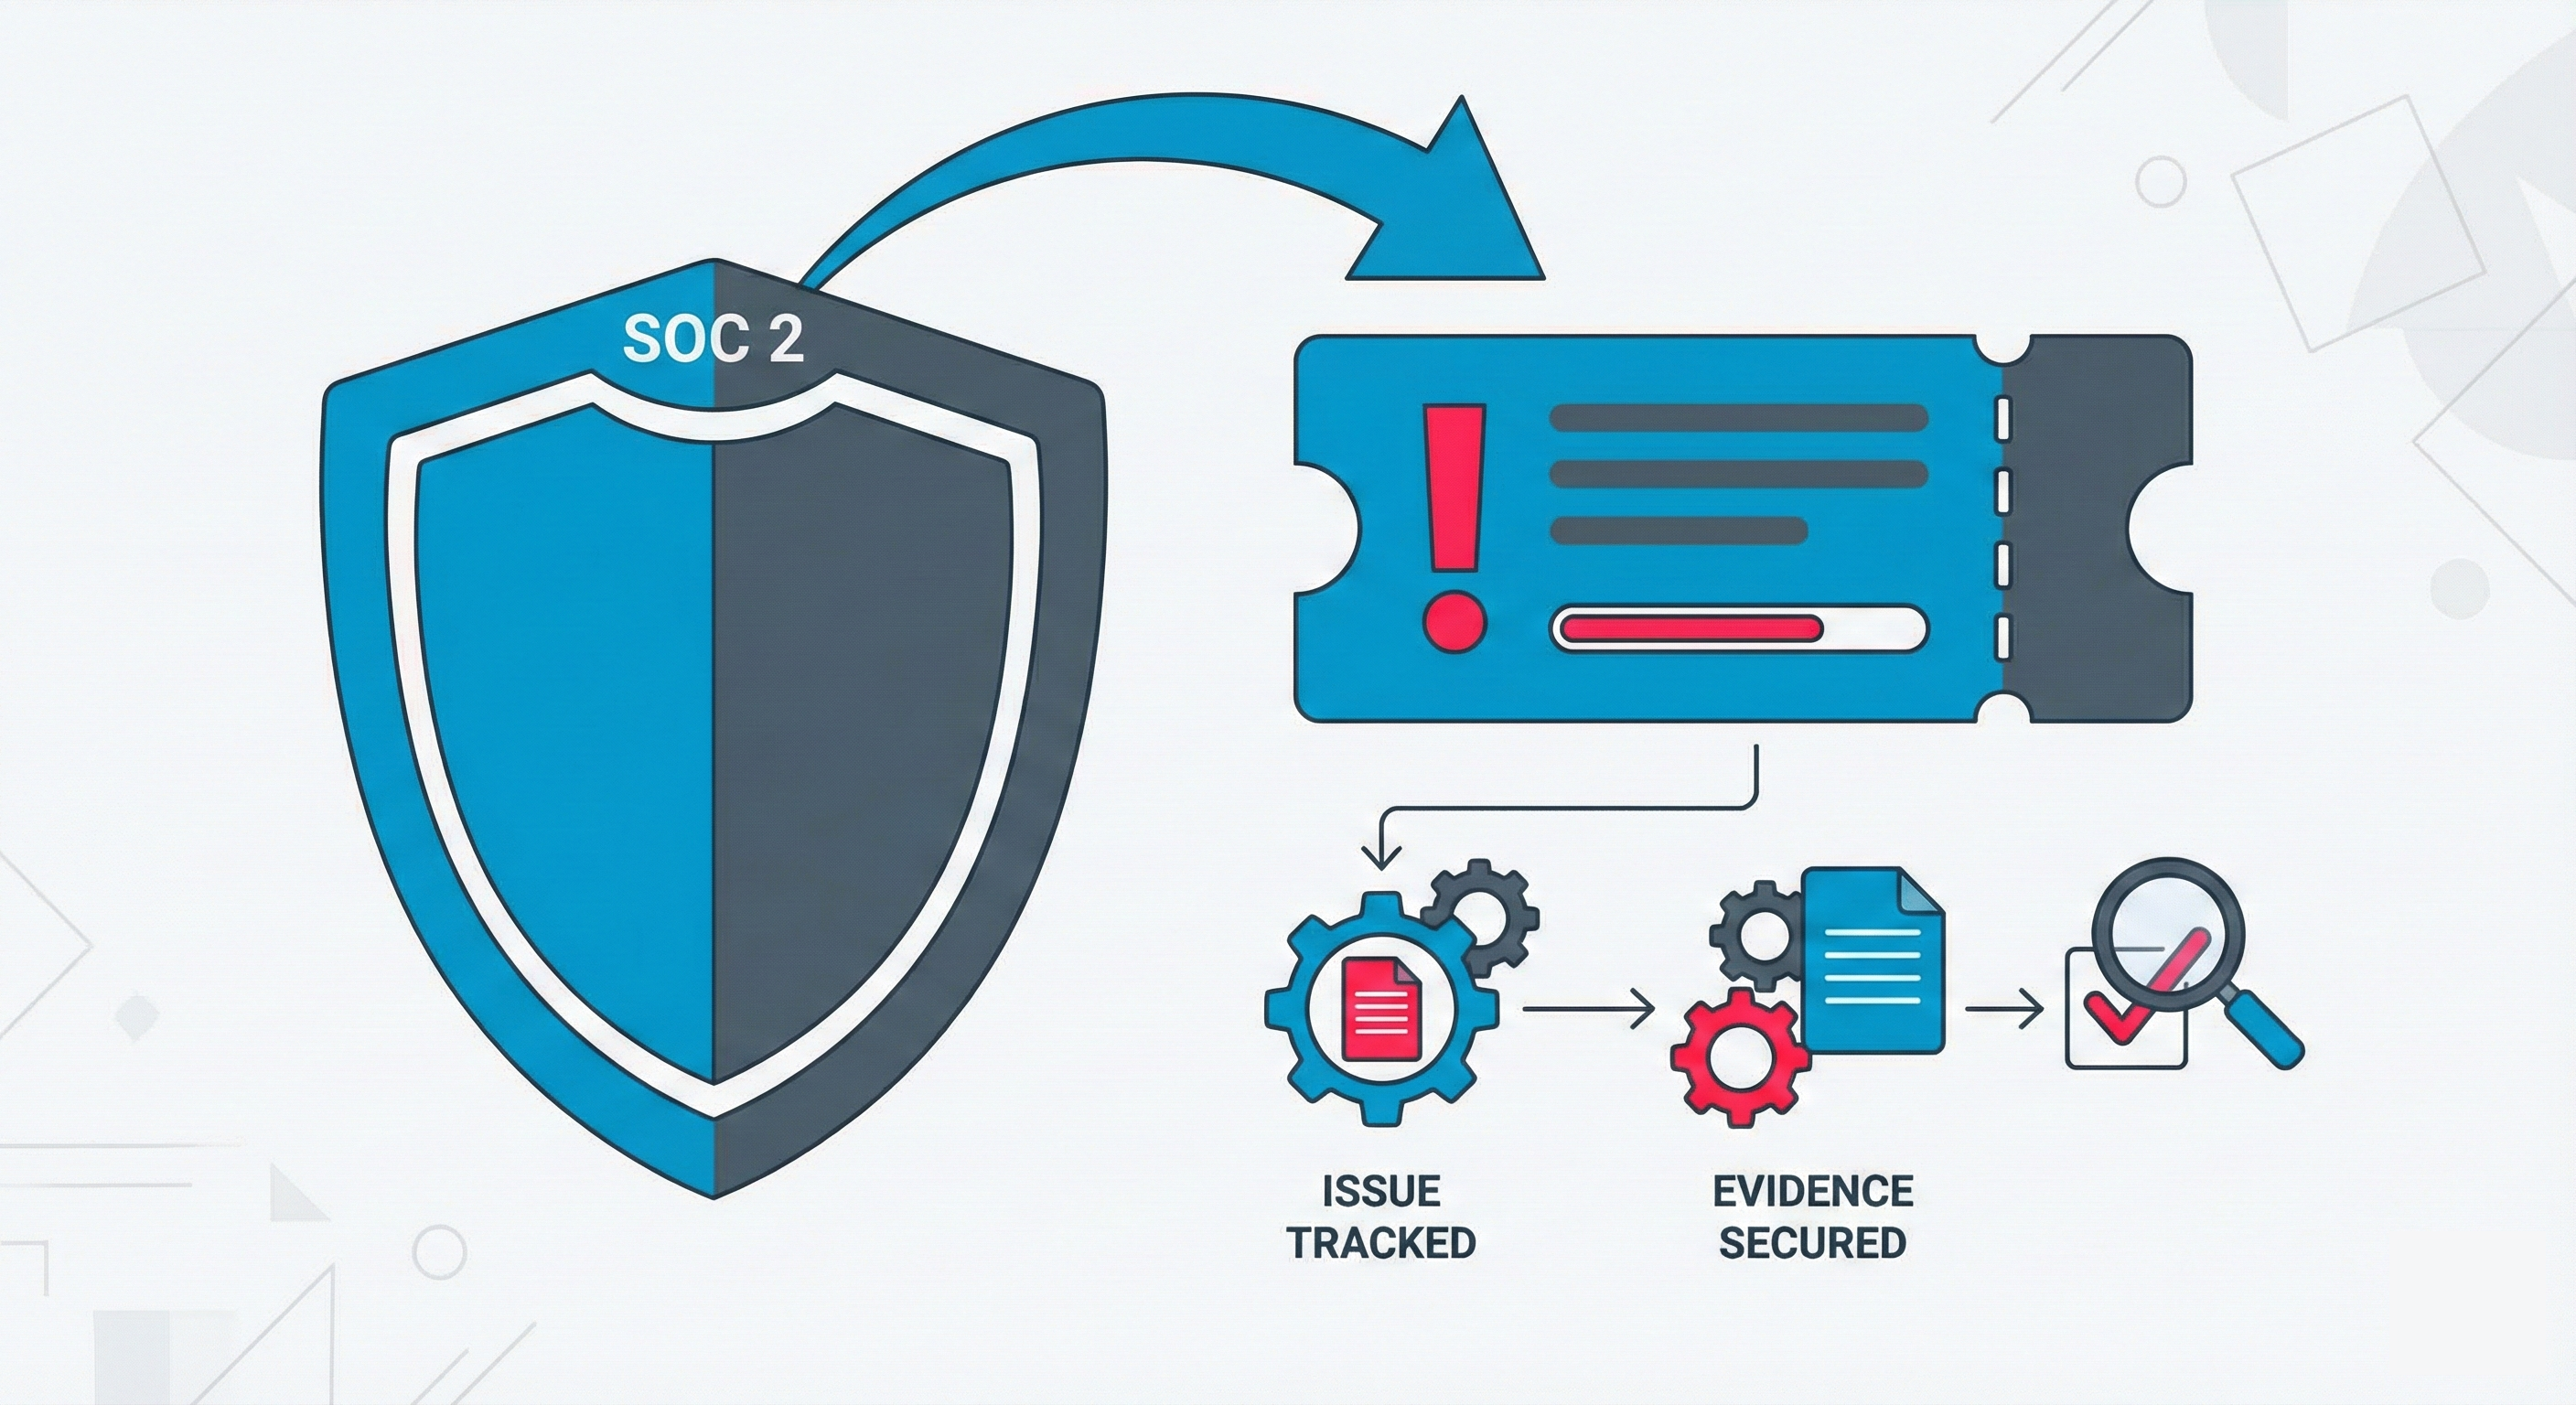
Featured image for SOC 2 SLA for vulnerability patching

SOC 2 Ticketing & SLAs: Vulnerability Patching & Incident Response

TL;DR: SOC 2 compliance requires a formal, trackable process for all security-relevant activities. Under the Trust Services Criteria, this means...
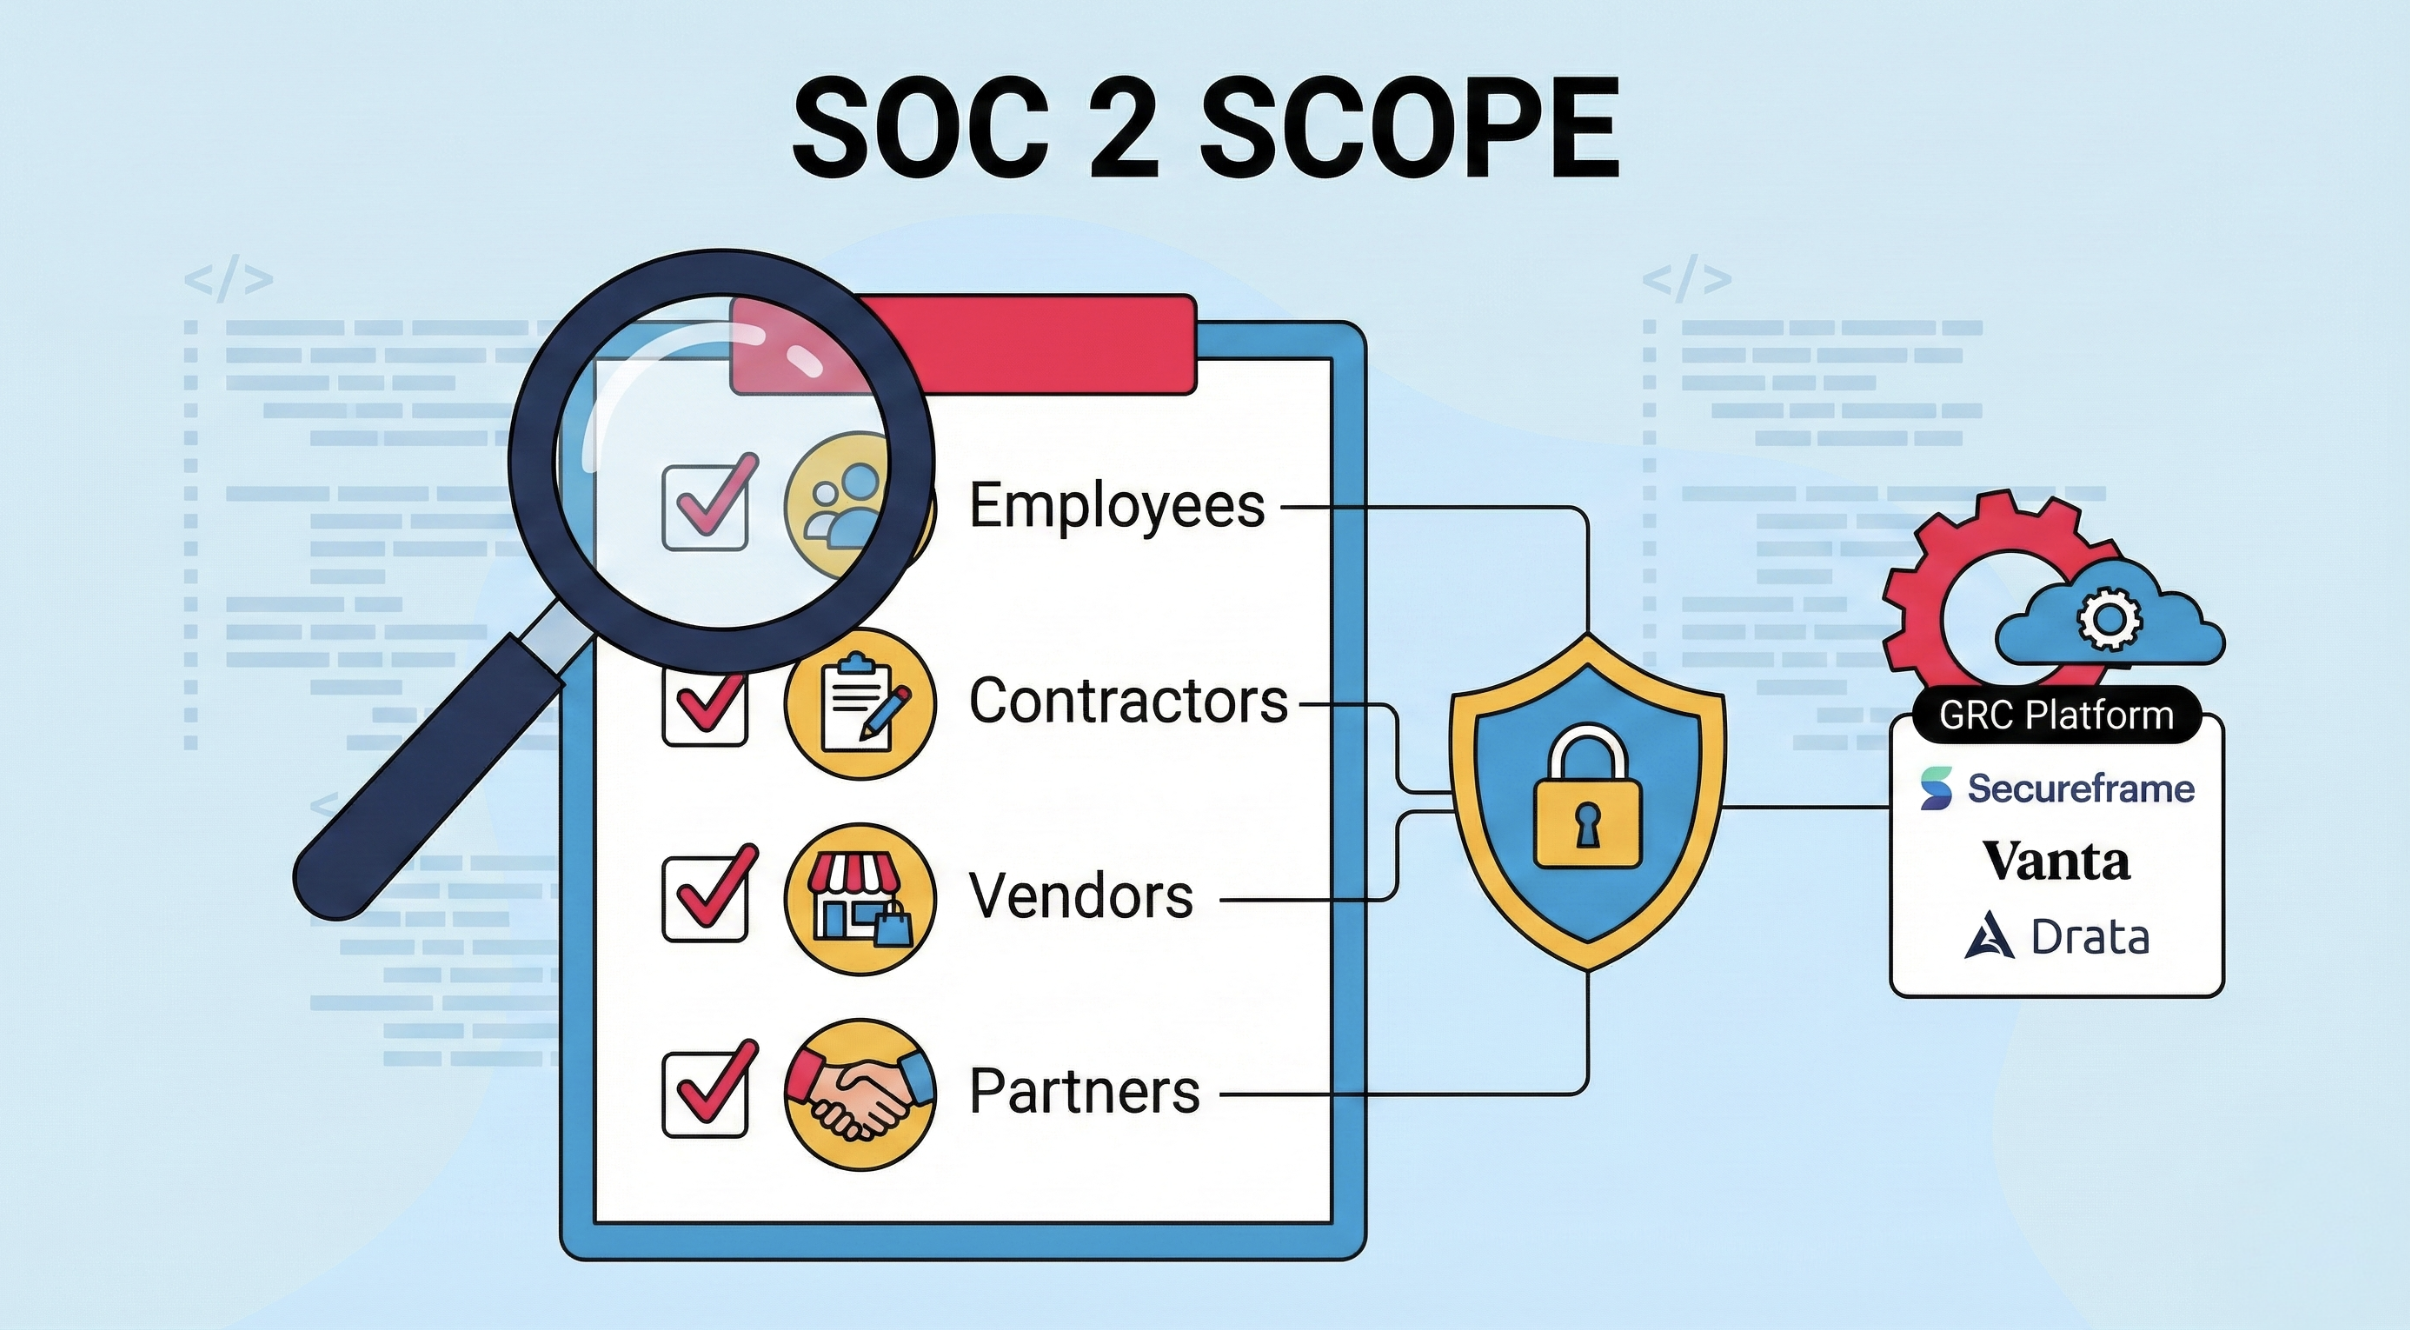
Audit scope (magnifying glass) for SOC 2 includes Employees, Contractors, and Vendors, linking them to security controls (shield/lock). This process integrates with a GRC Platform featuring Secureframe, Vanta, and Drata logos. Light blue background with coding elements.

SOC 2 People Scoping: Which Employees, Contractors, and Vendors

Short answer: a person is in SOC 2 scope when their role or access affects the system's ability to meet the Trust Services Criteria commitments.
  • ...
Automate CI/CD Security for SOC 2: SAST, SCA, DAST Integration Guide

Automate CI/CD Security for SOC 2: SAST, SCA, DAST Integration Guide

To automate CI/CD security for SOC 2, run five types of security scans in the pipeline, fail the build on critical findings, and send the results to...

Supply Chain Cyber Risk: Why Your Vendors' Security Is Your Problem

Supply Chain Cyber Risk: Why Your Vendors' Security Is Your Problem

Supply chain cyber risk has become one of the most pressing cybersecurity challenges for businesses of all sizes. A single compromise in a supplier’s...

Why Invest in Compliance Automation If You Only Need SOC 2?

Why Invest in Compliance Automation If You Only Need SOC 2?

TL;DR: Even when SOC 2 is the only compliance requirement on the table, a compliance automation platform (Vanta, Drata, Secureframe, Scrut) pays for...

Security Questionnaire Automation: From Fire Drill to System

Security Questionnaire Automation: From Fire Drill to System

Security Questionnaire Automation: From Fire Drill to System

A 200-question security questionnaire lands in the sales team's inbox on a Thursday...

Is SOC 2 a Waste of Money? Evaluating Its Security Value

Is SOC 2 a Waste of Money? Evaluating Its Security Value

?
SOC 2 Scorecard

Score Your SOC 2 Security Program

16 questions mapped to Common Criteria. See your strengths, find your gaps, get a...

CMMC Explained: Cybersecurity Maturity Model Certification

CMMC Explained: Cybersecurity Maturity Model Certification

Most companies first hear about CMMC when a solicitation arrives with a clause they have never seen before, or when a prime contractor asks a...

What Is Cyber Security Posture? Definition and Importance

What Is Cyber Security Posture? Definition and Importance

Like in any industry, cyber security and cybercrime is constantly evolving. To keep up, you need to remain familiar with upcoming trends and the...