SOC 2SOC 2 ImplementationSOC 2 On-PremSOC 2 Bare-MetalRisk Management


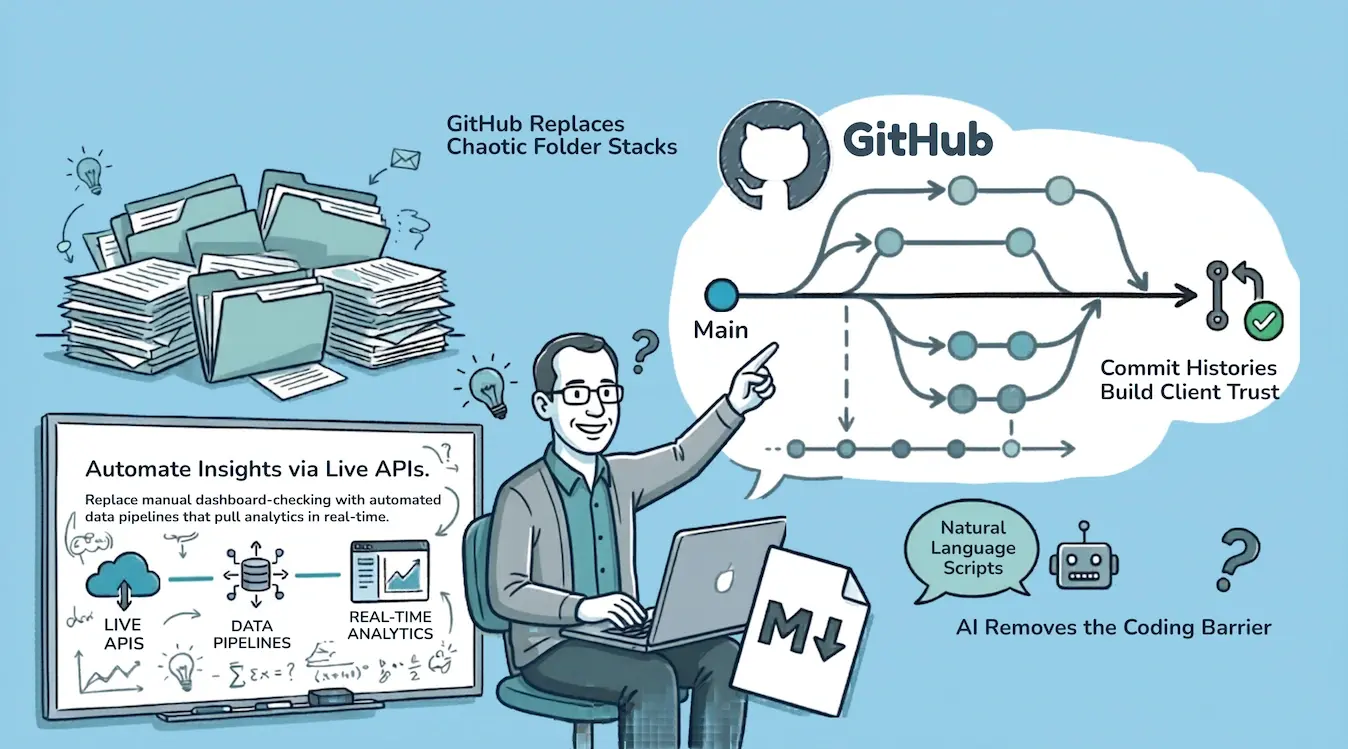
For years, programmers had an unfair advantage over the rest of us.
Not because they could build software. Because they could access data. Rich,...
On paper, DIY compliance looks straightforward. Subscribe to a GRC platform, follow the control library, collect evidence, engage an auditor. The...
Most SOC 2 consultants know AWS. Some know Azure and GCP. Very few know what to do when your stack includes a colocation facility, a bare-metal fleet...
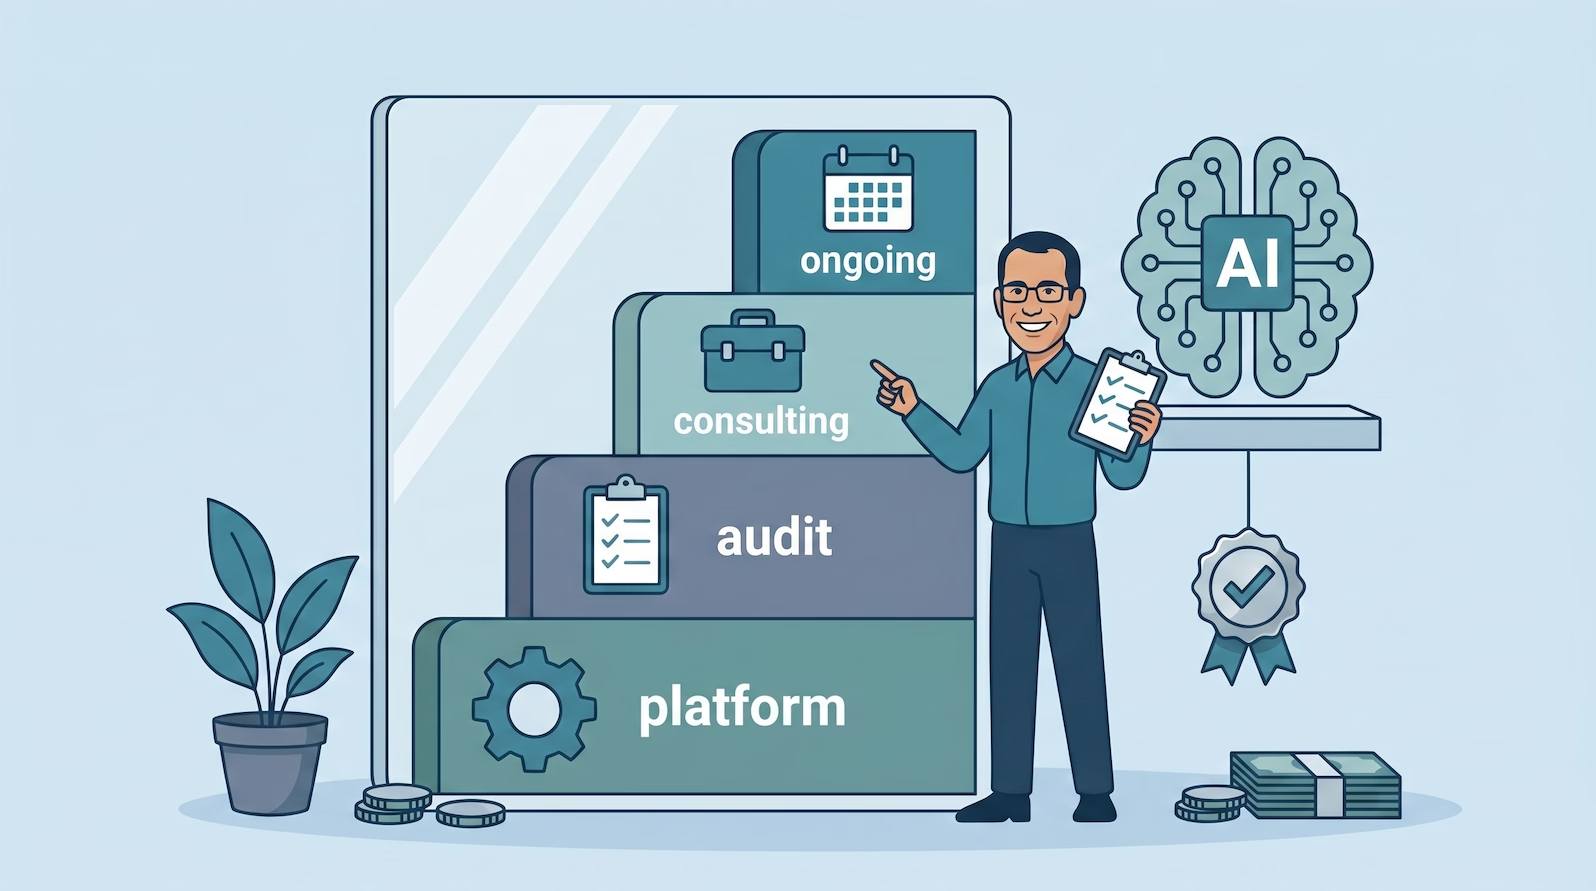
If you are an AI SaaS company looking at ISO 42001, the first question is not what does the standard say. It is what is this going to cost us in...
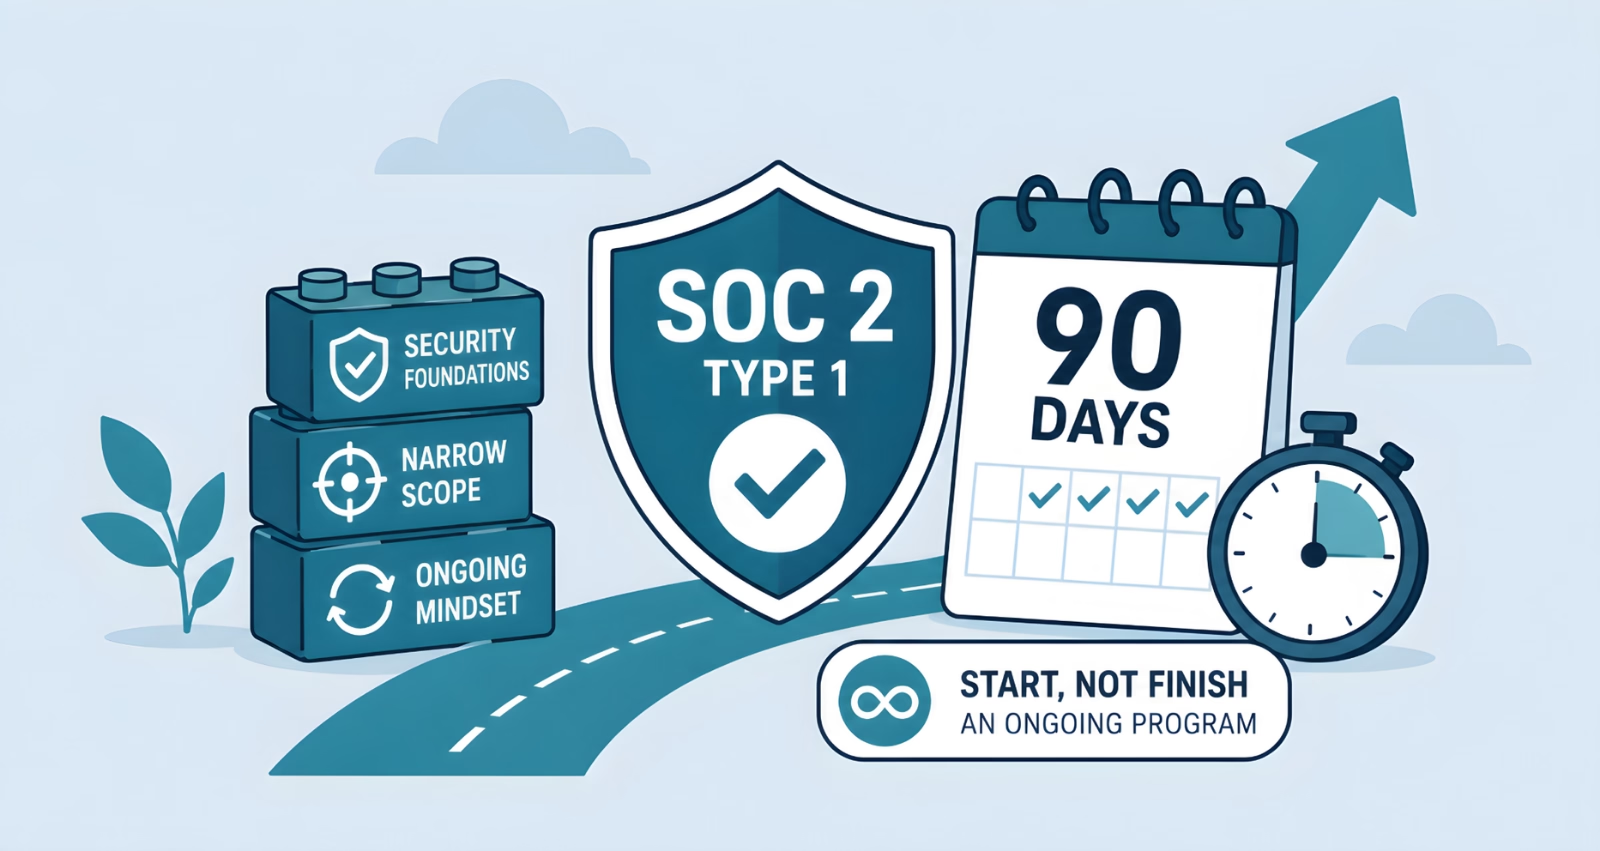
Ninety days from kickoff to a SOC 2 readiness is achievable. It is not achievable for every company, and the companies that hit it make deliberate...
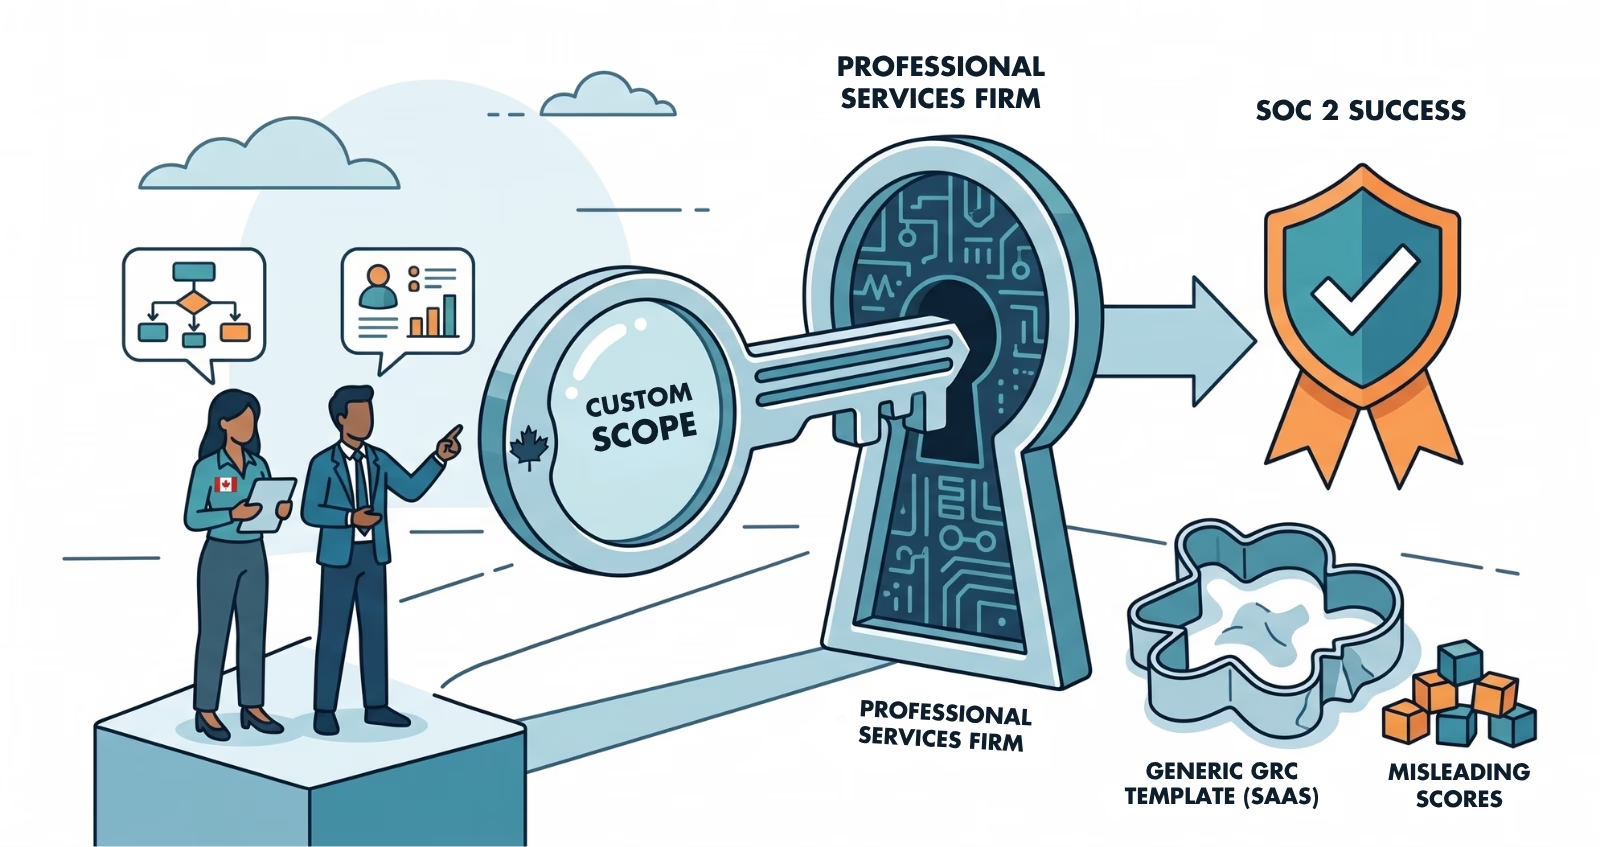
A professional services firm starts its SOC 2 process the same way most companies do. An enterprise client puts it in an RFP. The team subscribes to...
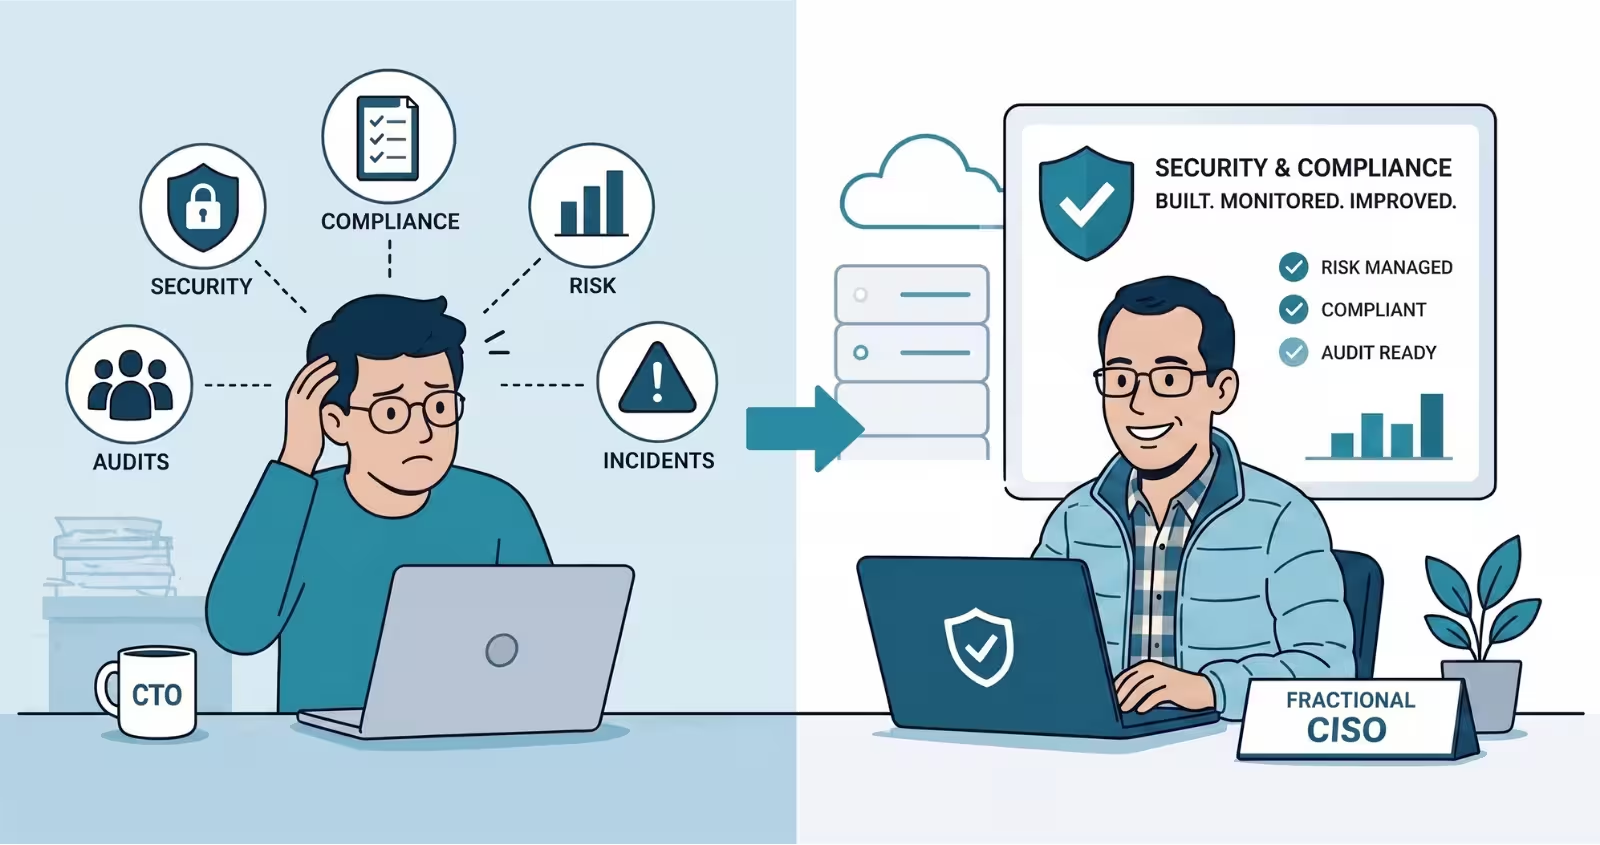
Security leadership at most SaaS companies follows a predictable pattern. The CTO handles it. Not because they volunteered, but because nobody else...
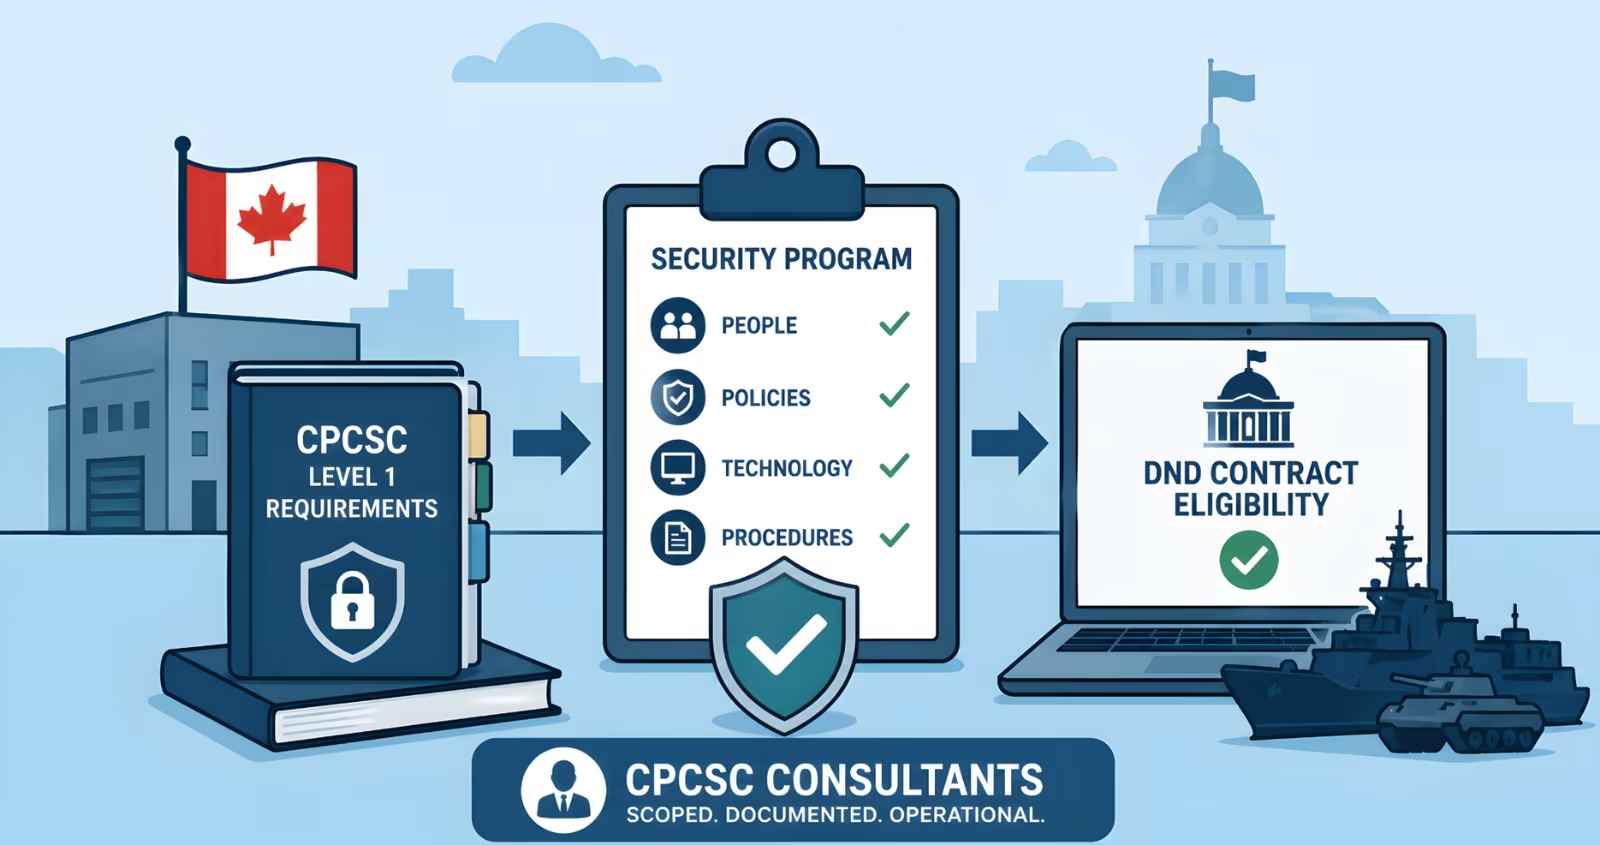
CPCSC Level 1 attestation becomes a procurement requirement for Department of National Defence contracts in April 2026. Companies that can't attest...
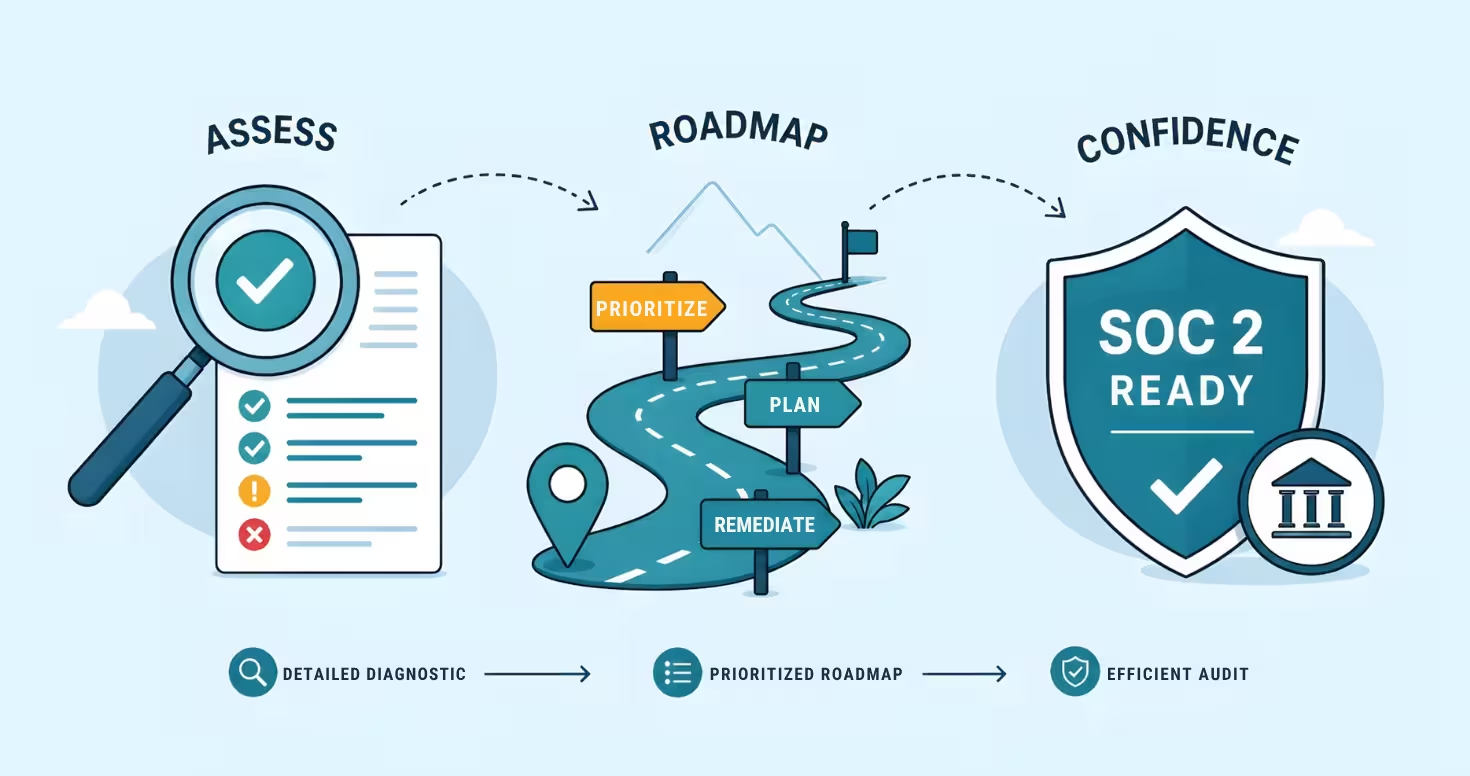
A SOC 2 readiness assessment is not the audit. It is the diagnostic step that tells a company exactly where it stands before committing budget and...
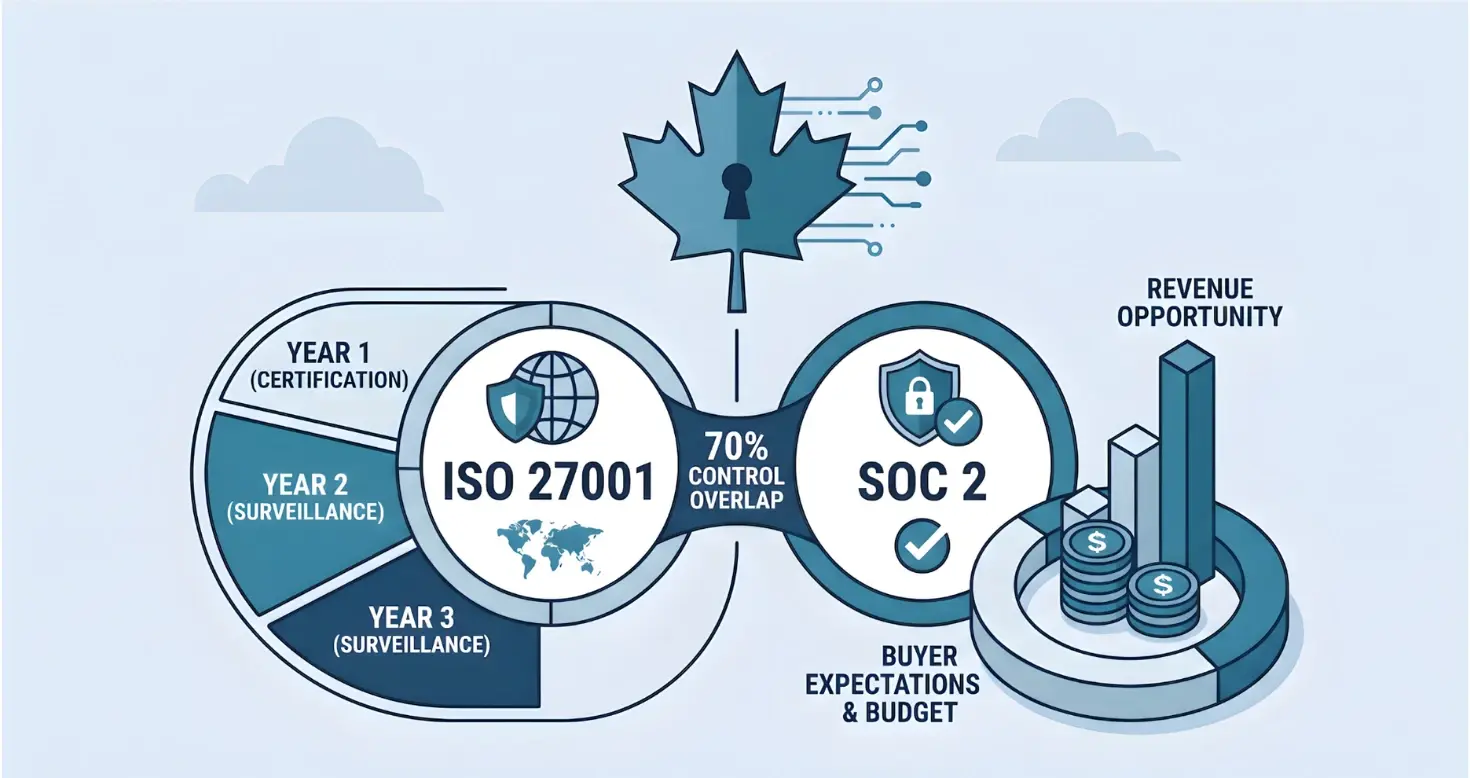
ISO 27001 certification gives you a one-to-two-page certificate. SOC 2 gives you a 40-to-50-page report describing every control, how it was tested,...
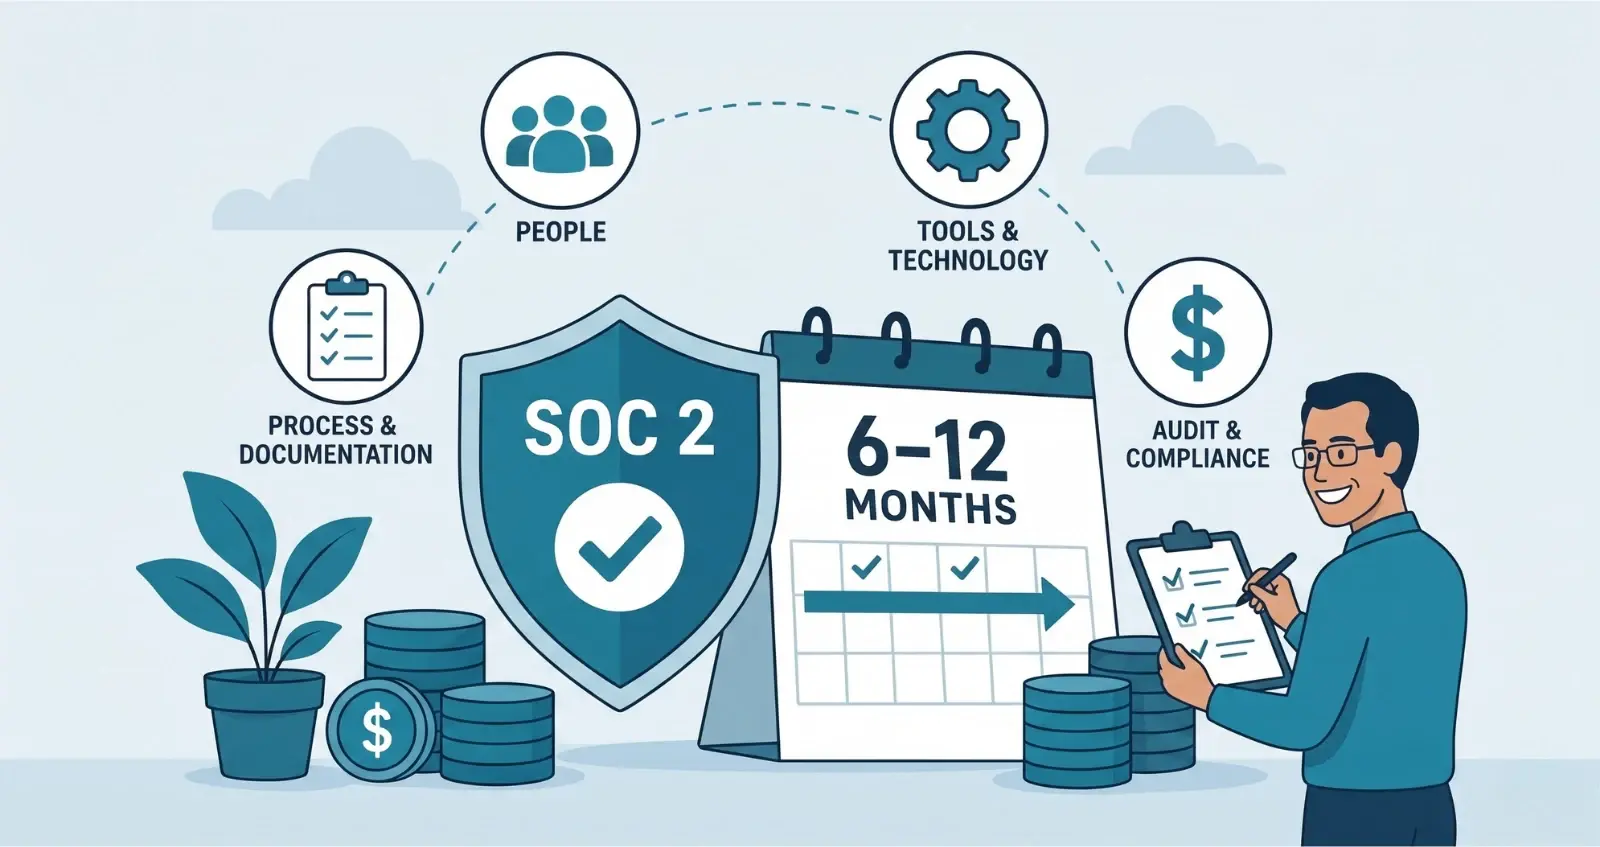
SOC 2 has four cost components. Most companies only budget for two of them, then get surprised by the rest halfway through the engagement.
Here is...
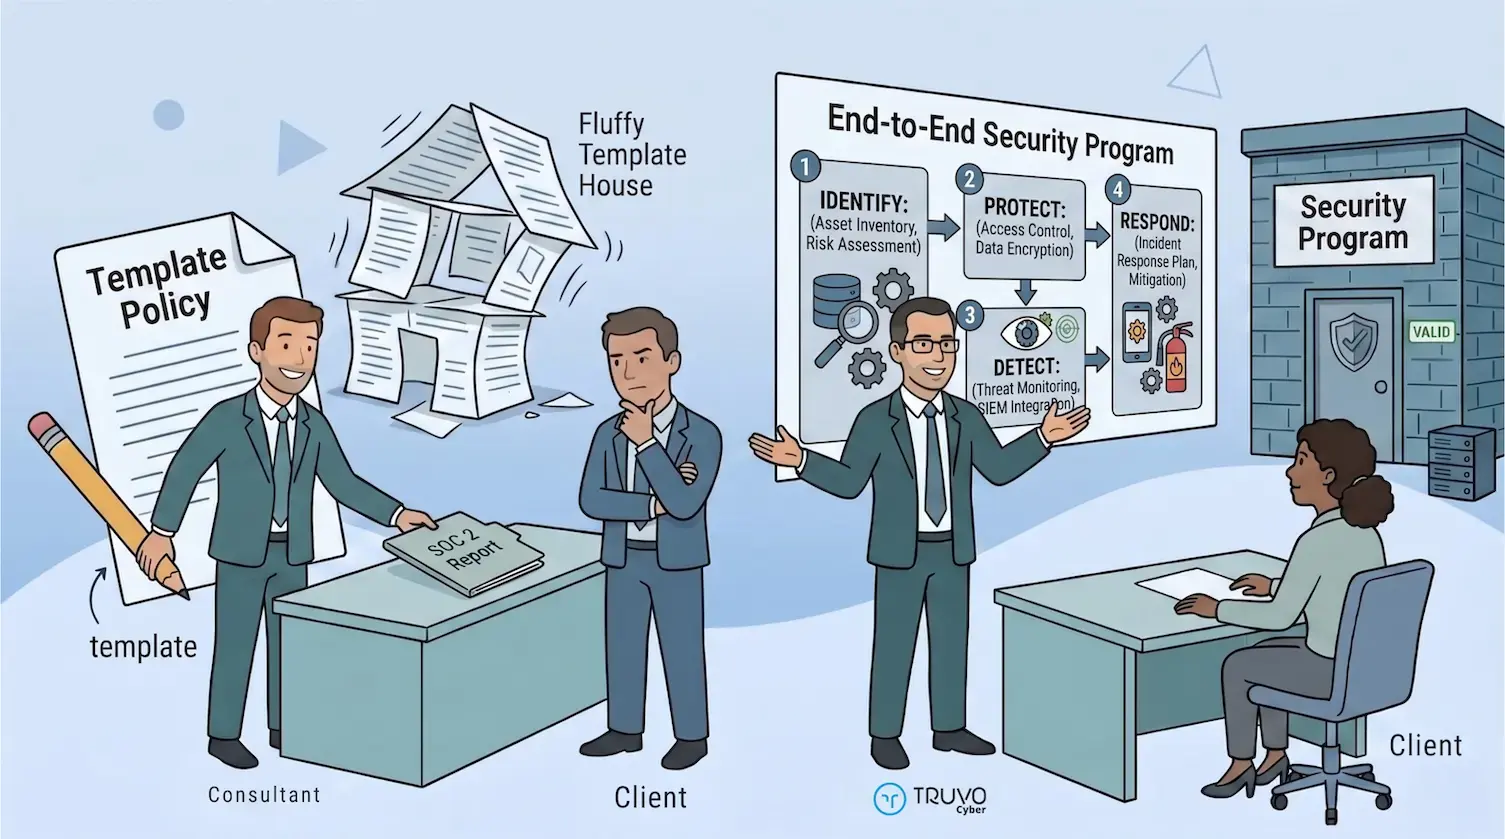
Platform-first firms compress the engagement into days or a few weeks. They take a policy template library, swap...
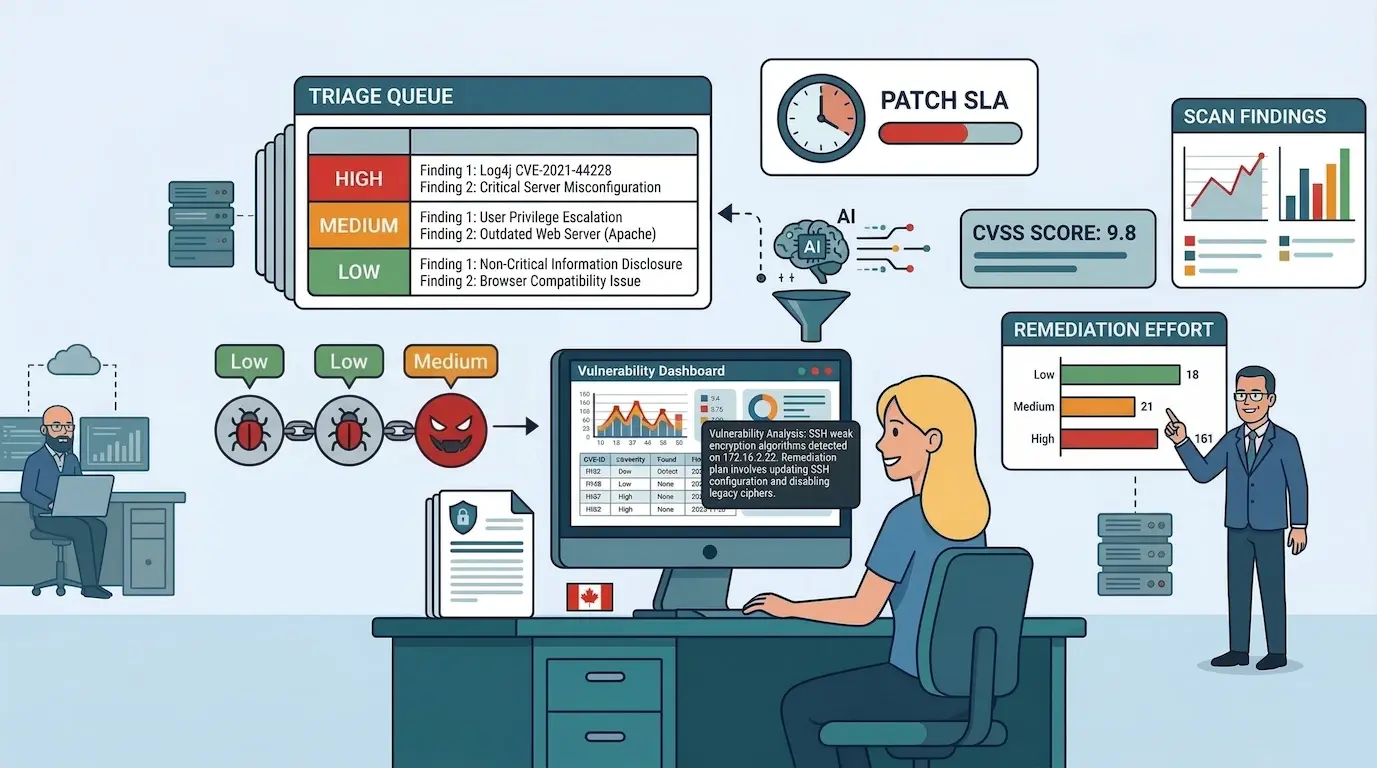
I have been thinking about what Anthropic's Project Glasswing announcement actually means for the clients we advise. The honest answer is that it...
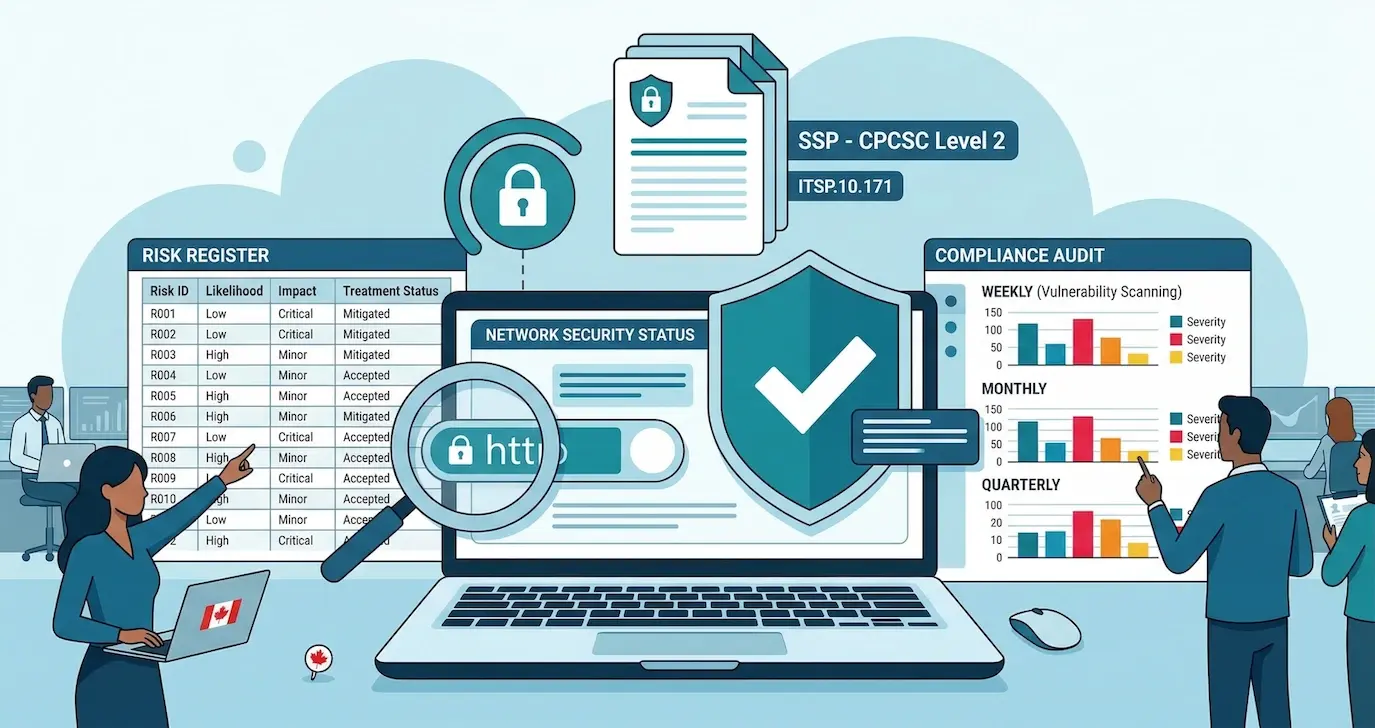
The majority of ITSP.10.171 control families deal with operational security: how you configure systems, manage access, protect data. The Risk...
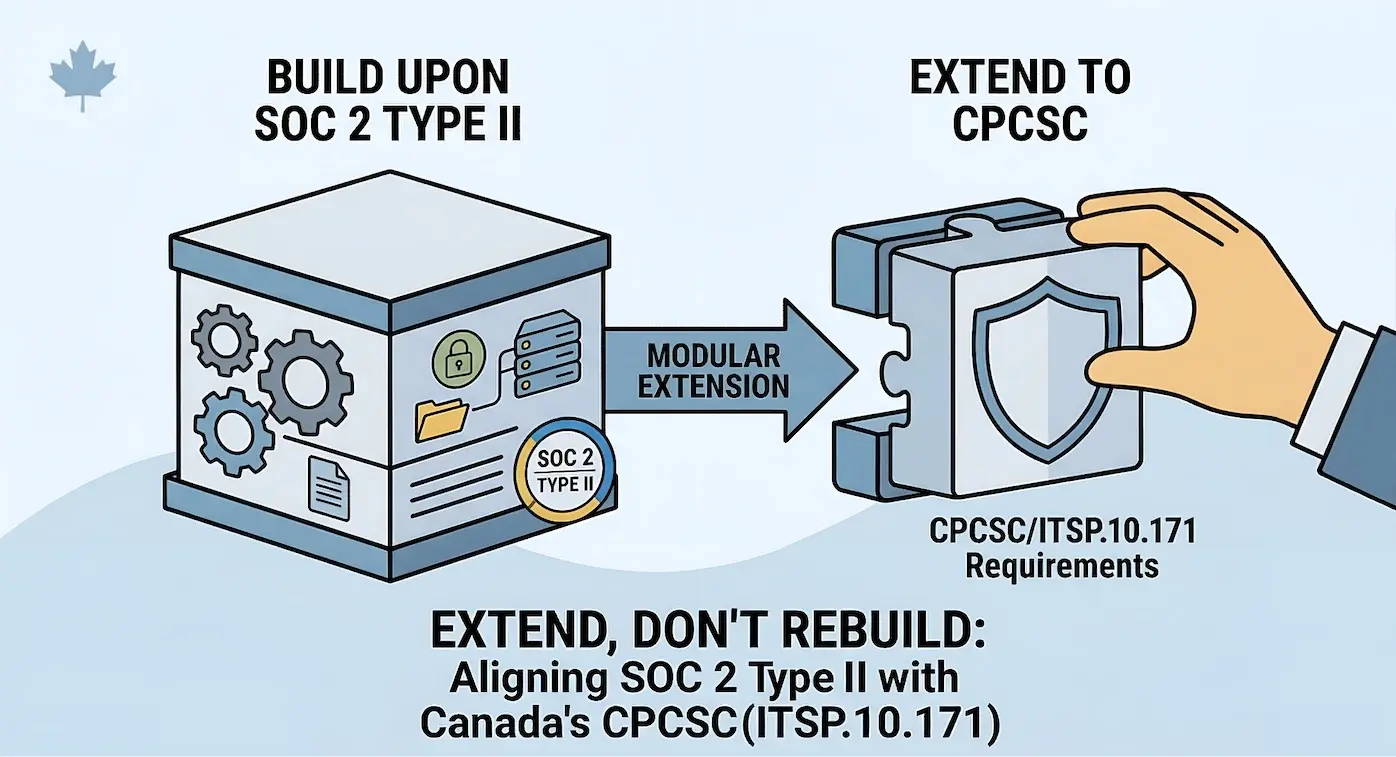
The question comes up consistently when companies with established security programs look at entering the Canadian defence supply chain: Do we need...
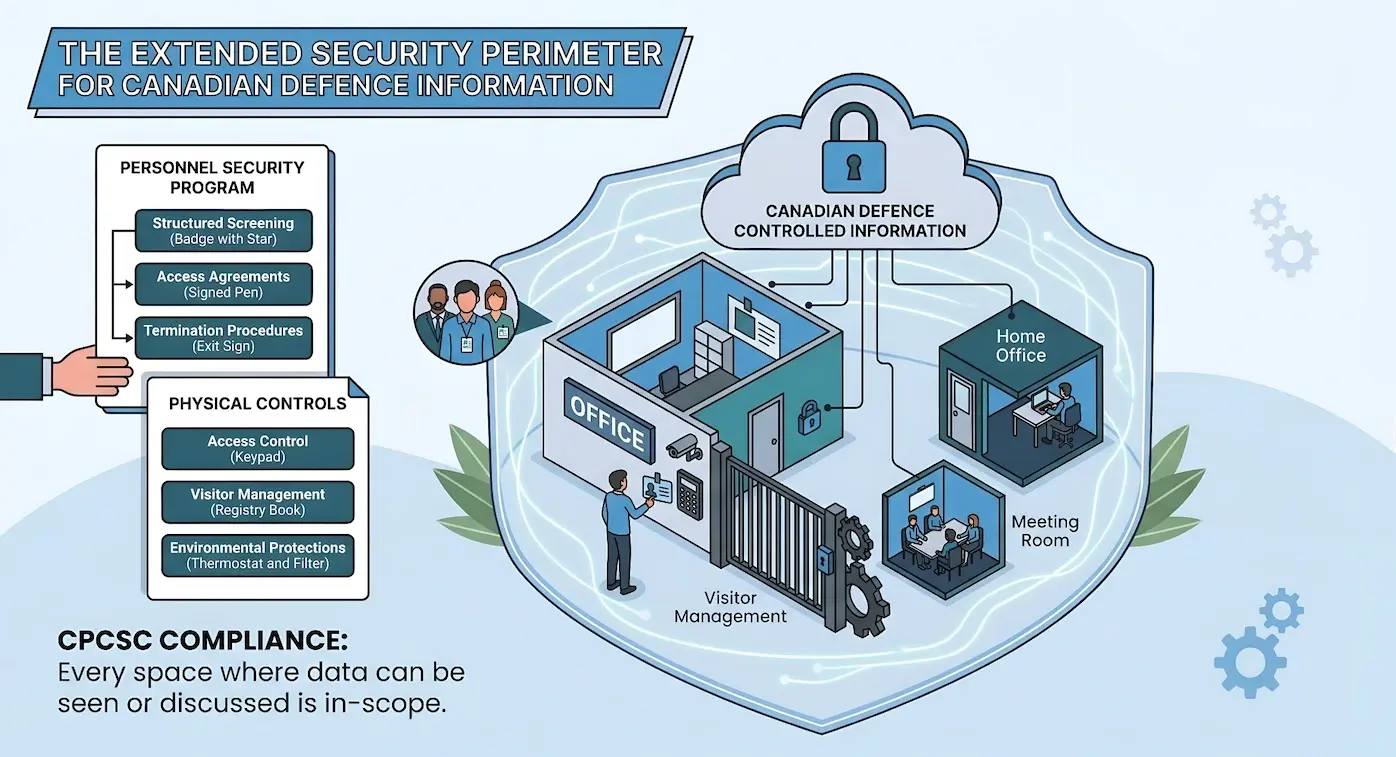
Every other control family in ITSP.10.171 has a reasonable analogue in the commercial compliance world. Access control maps to SOC 2 CC6. Incident...
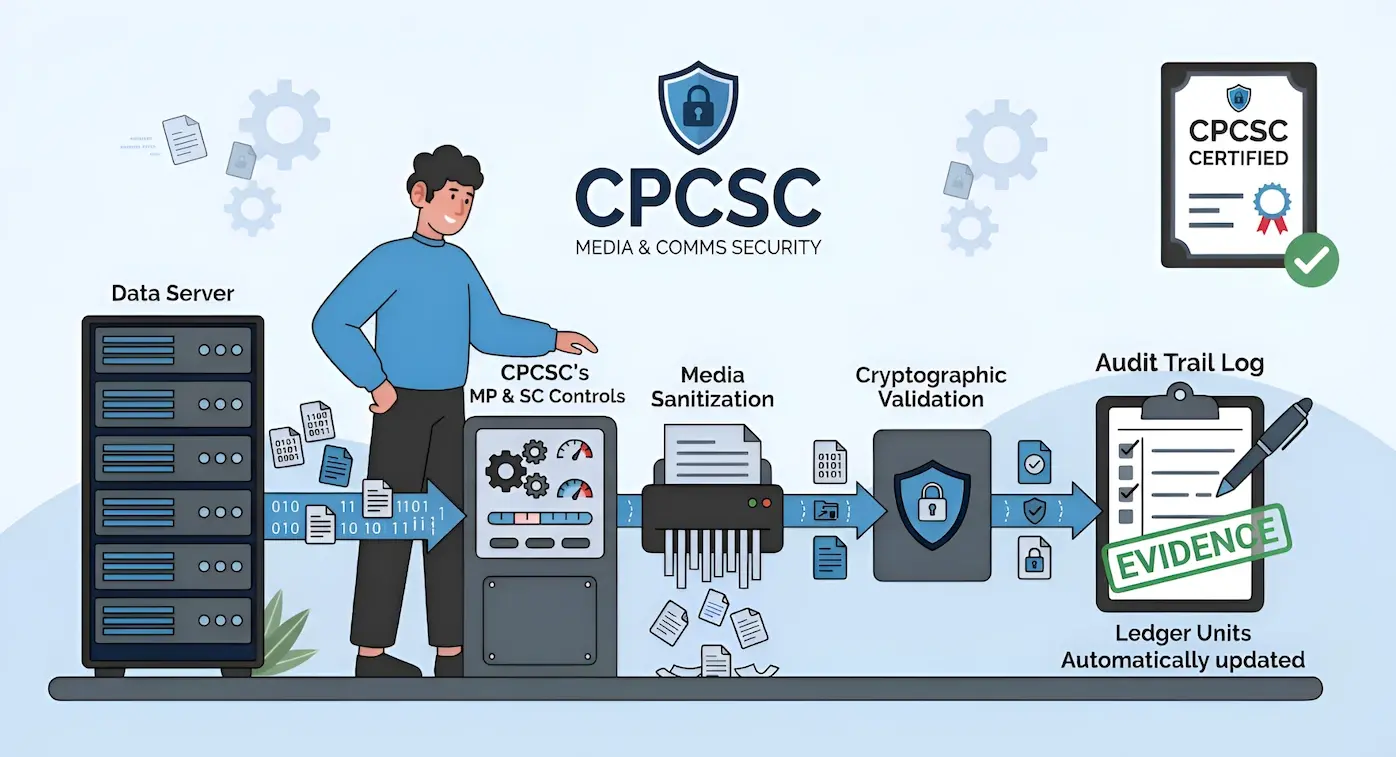
In a compliance landscape that increasingly assumes cloud-first architecture, media protection controls tend to get deprioritized. The assumption is...
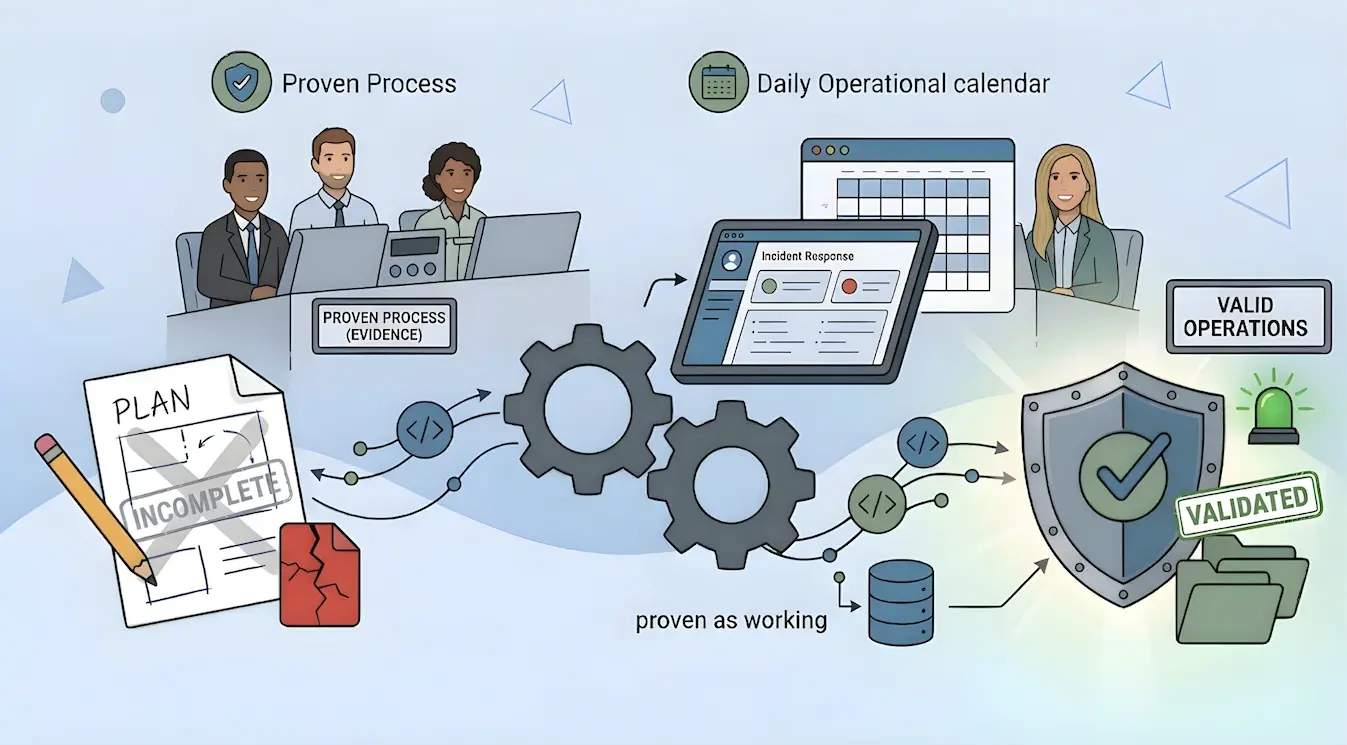
An incident response plan that exists only in a shared drive is not evidence of preparedness. It is evidence of intent, and the Canadian Program for...
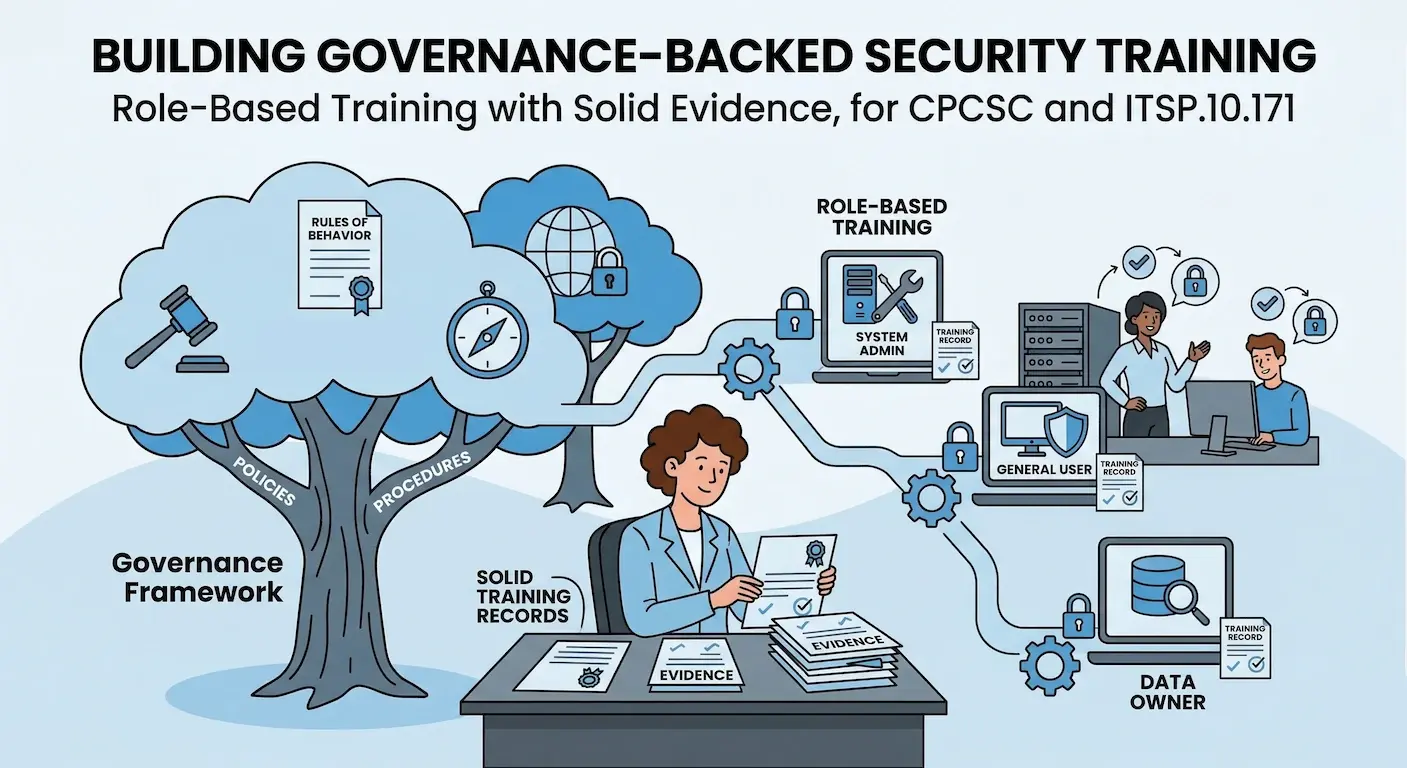
The previous twelve posts in this series covered the technical and operational control families in ITSP.10.171: access control, incident response,...
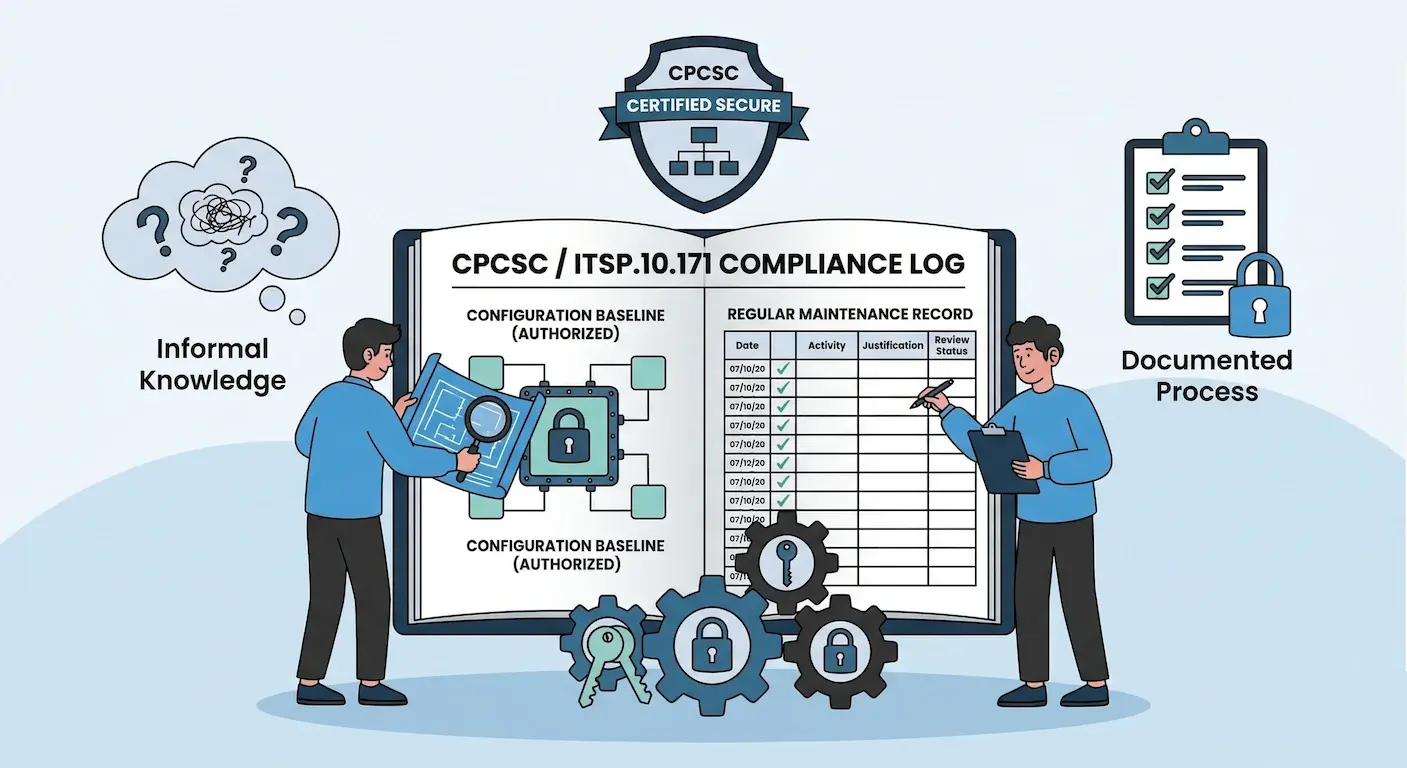
There is a specific phrase that comes up in nearly every environment that has never been through a formal configuration review: We know our systems....
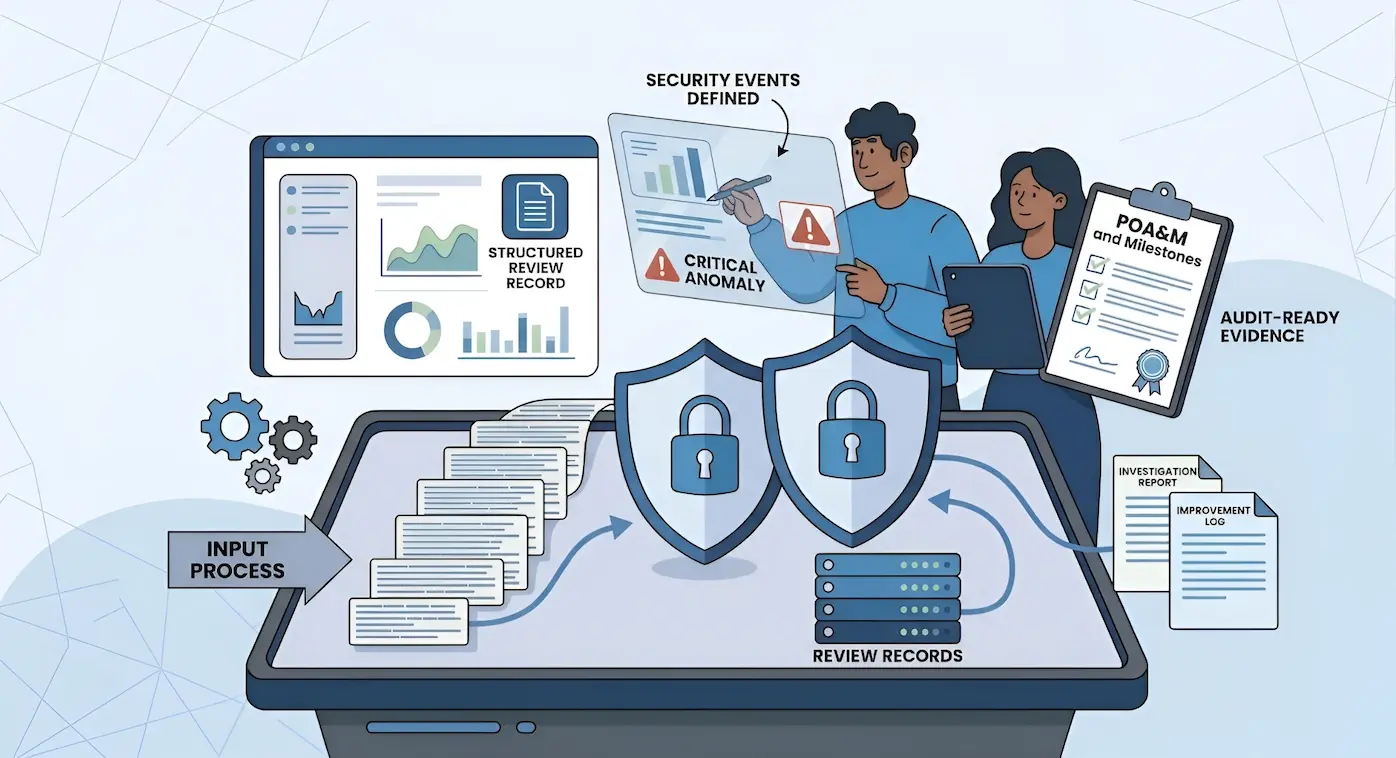
Most organizations produce logs. Application servers generate them, firewalls record them, identity providers track them. The volume is rarely the...
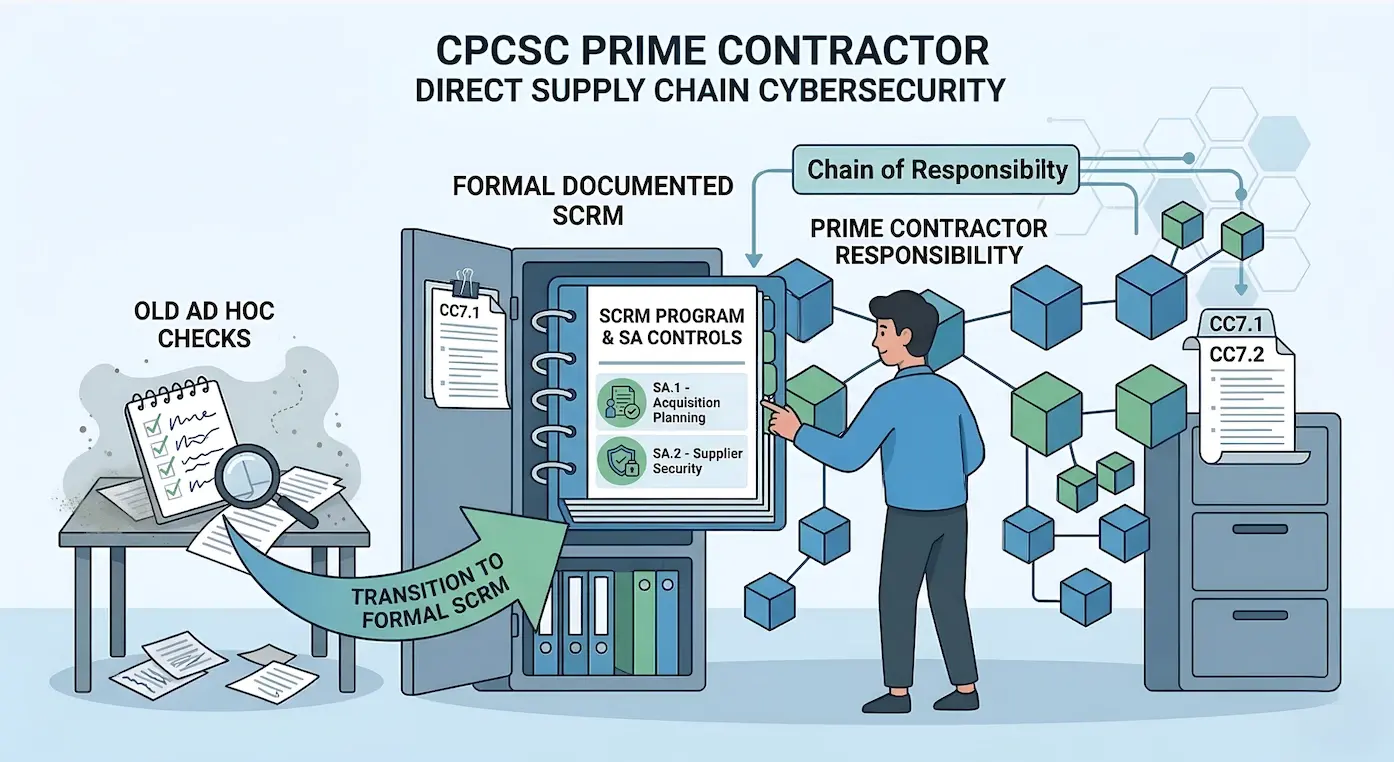
For most of the history of Canadian defence procurement, cybersecurity obligations ended at the prime contractor's perimeter. A prime could hold a...
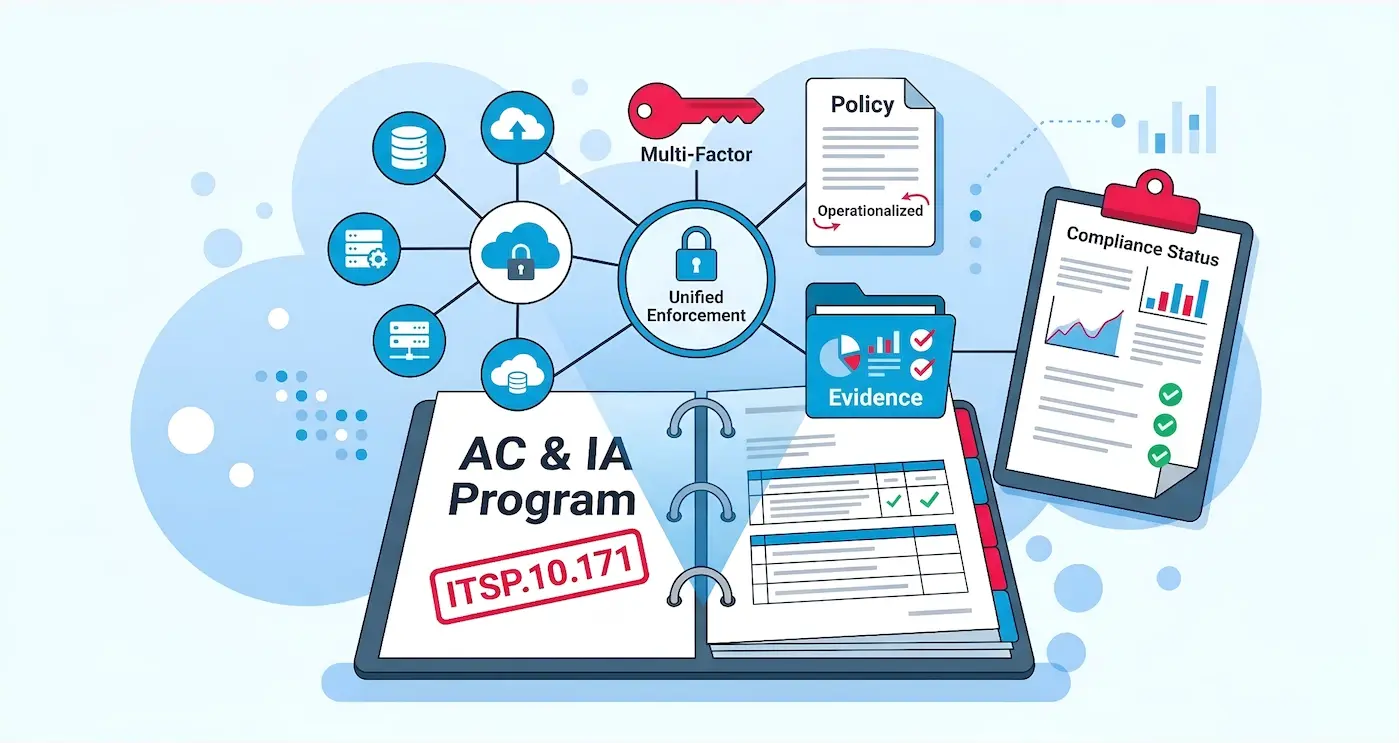
Every security program has access controls of some kind. Password policies exist, MFA is probably enabled somewhere, and someone has a spreadsheet...