Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

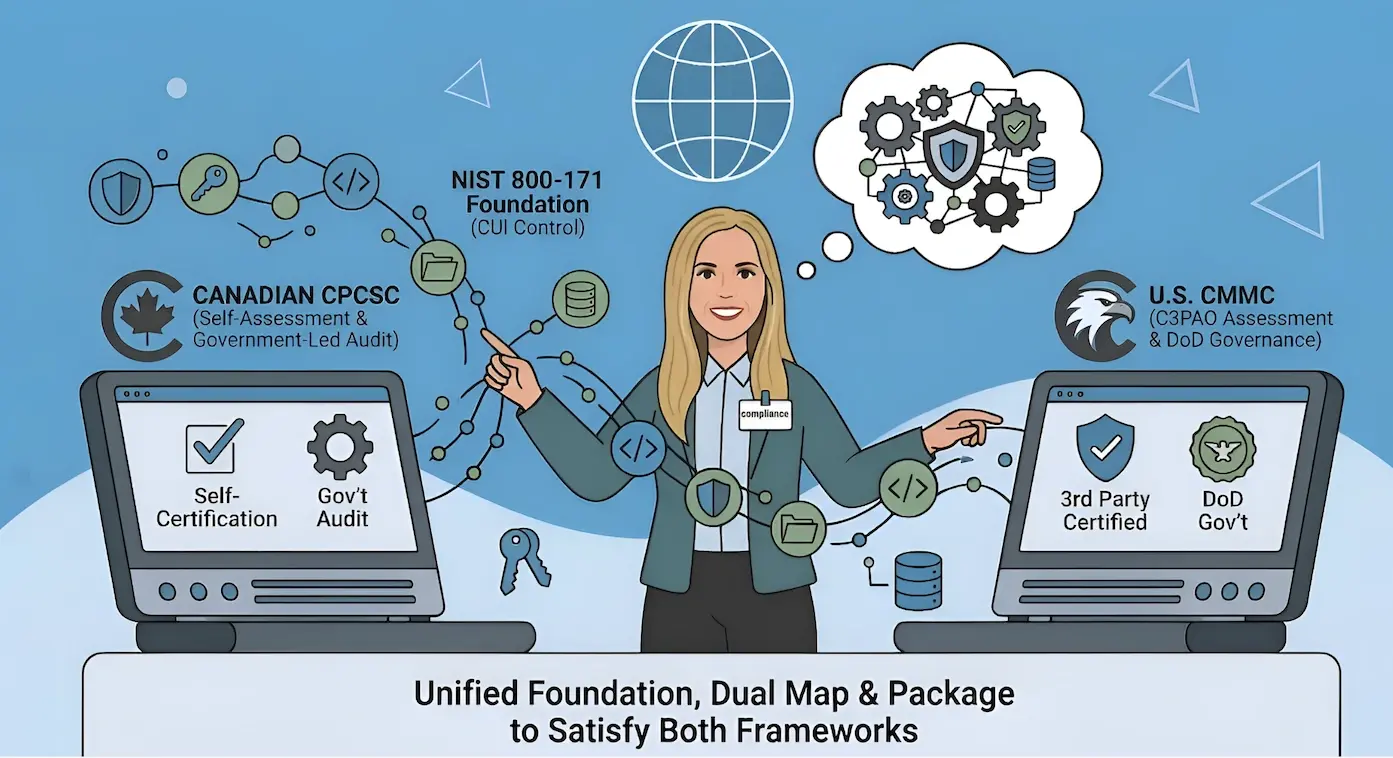
An infographic comparing Canadian CPCSC (Self-Assessment & Gov-Led Audit) and U.S. CMMC (C3PAO Assessment & DoD Governance). A central professional woman links both frameworks to a shared NIST 800-171 Foundation, emphasizing a unified strategy to satisfy both dual-jurisdiction requirements.

CPCSC vs CMMC: What Dual-Jurisdiction Contractors Need to Know

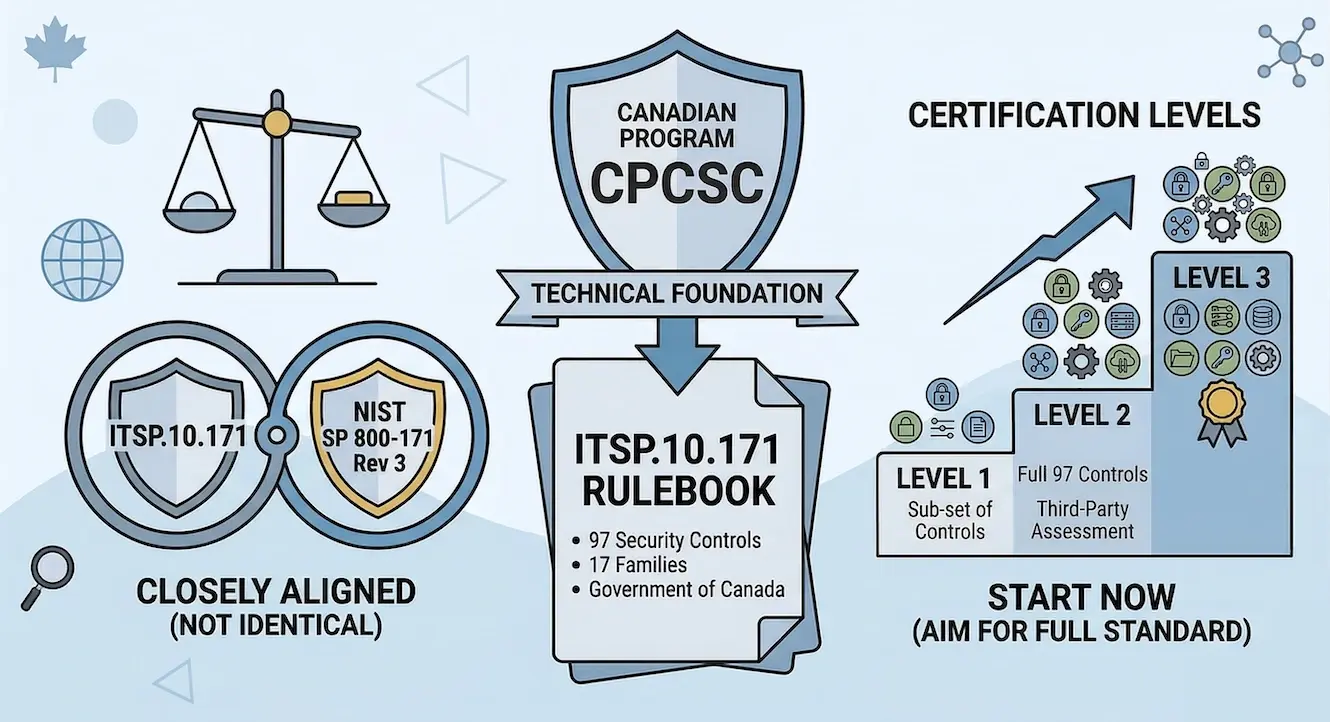
CPCSC (Canada) and CMMC (United States) both derive from NIST SP 800-171, so their control sets largely overlap. They differ in how each program...
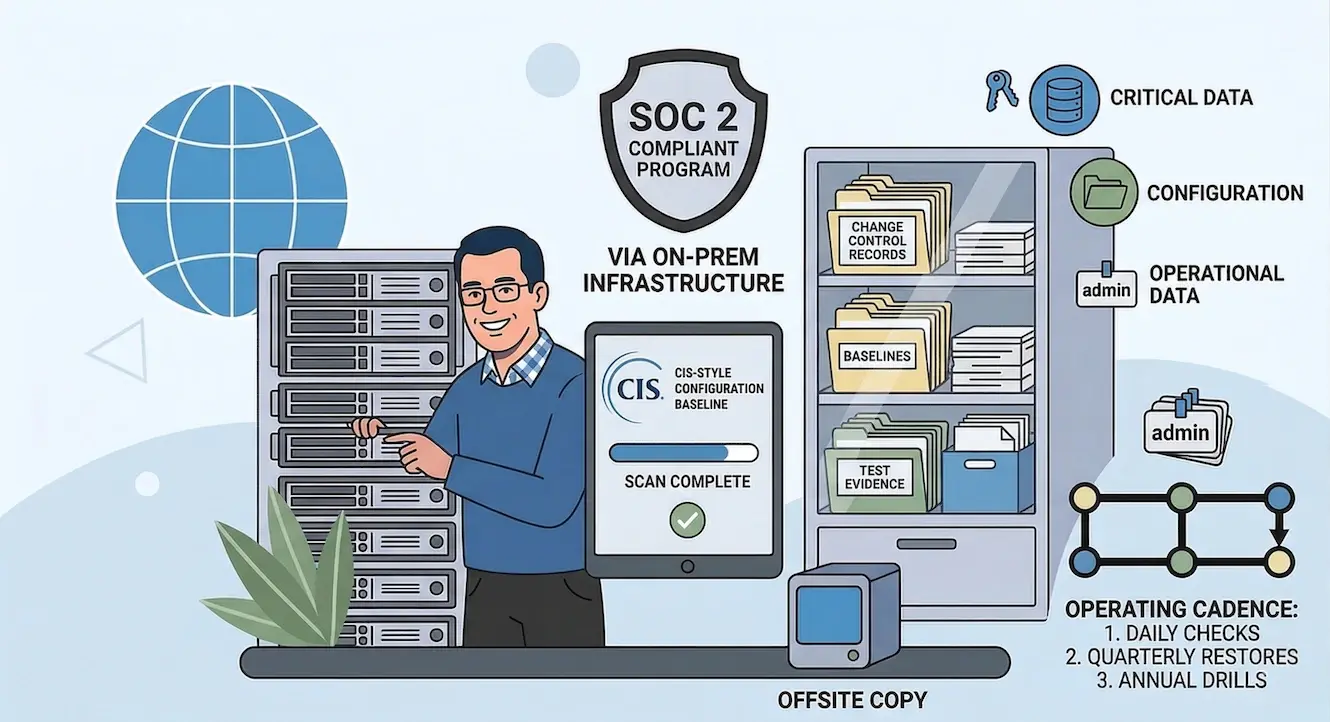
Illustration showing a SOC 2 compliant program via on-prem infrastructure. A man stands by a server rack and a tablet showing a completed CIS configuration scan. To the right, a filing cabinet stores baselines and test evidence. An "Operating Cadence" list details daily, quarterly, and annual tasks.

SOC 2 Configuration Baselines for Bare Metal: CIS Benchmarks & Beyond

In cloud environments, configuration compliance is a toggle. Enable AWS Config, deploy a conformance pack, and the platform continuously evaluates...
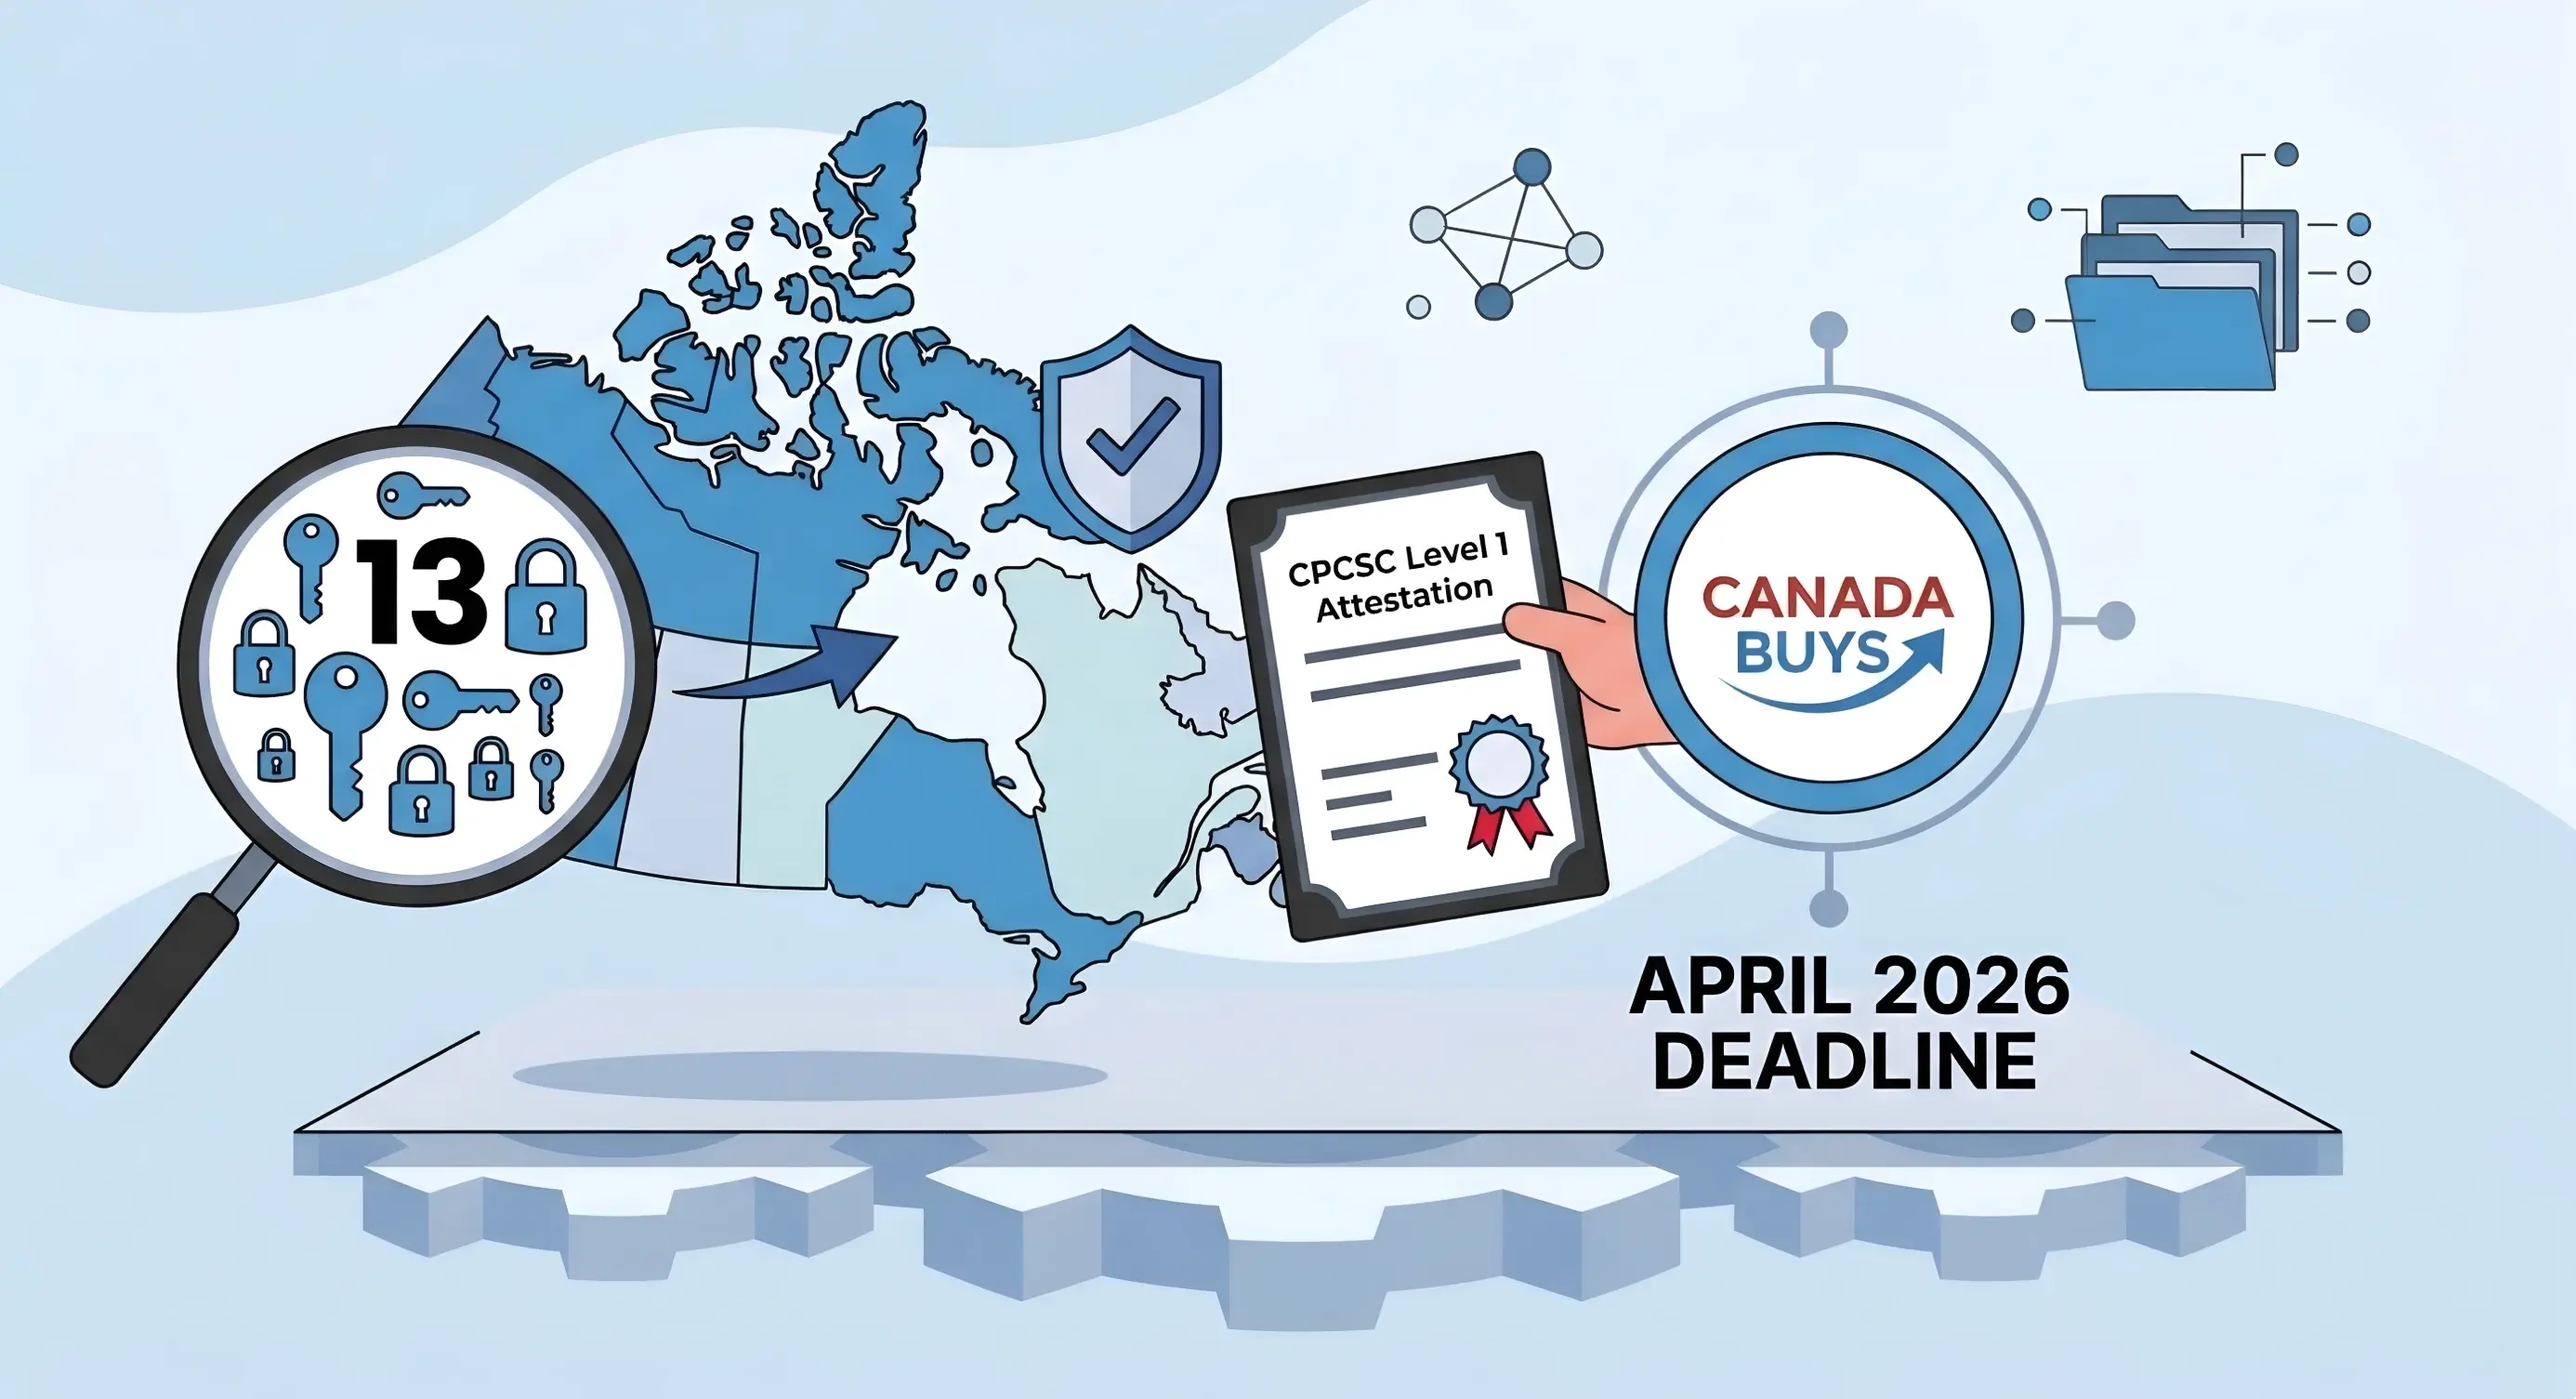
An infographic for the CPCSC Level 1 Attestation featuring a map of Canada and a magnifying glass highlighting "13" keys. A hand holds a certificate next to the CanadaBuys logo. Text warns of an "April 2026 Deadline," all set against a blue background with gears and file folder icons.

CPCSC Level 1 Self-Assessment: A Practical Guide

CPCSC Level 1 is an annual self-assessment of your organization against the security requirements of the Canadian Program for Cyber Security...
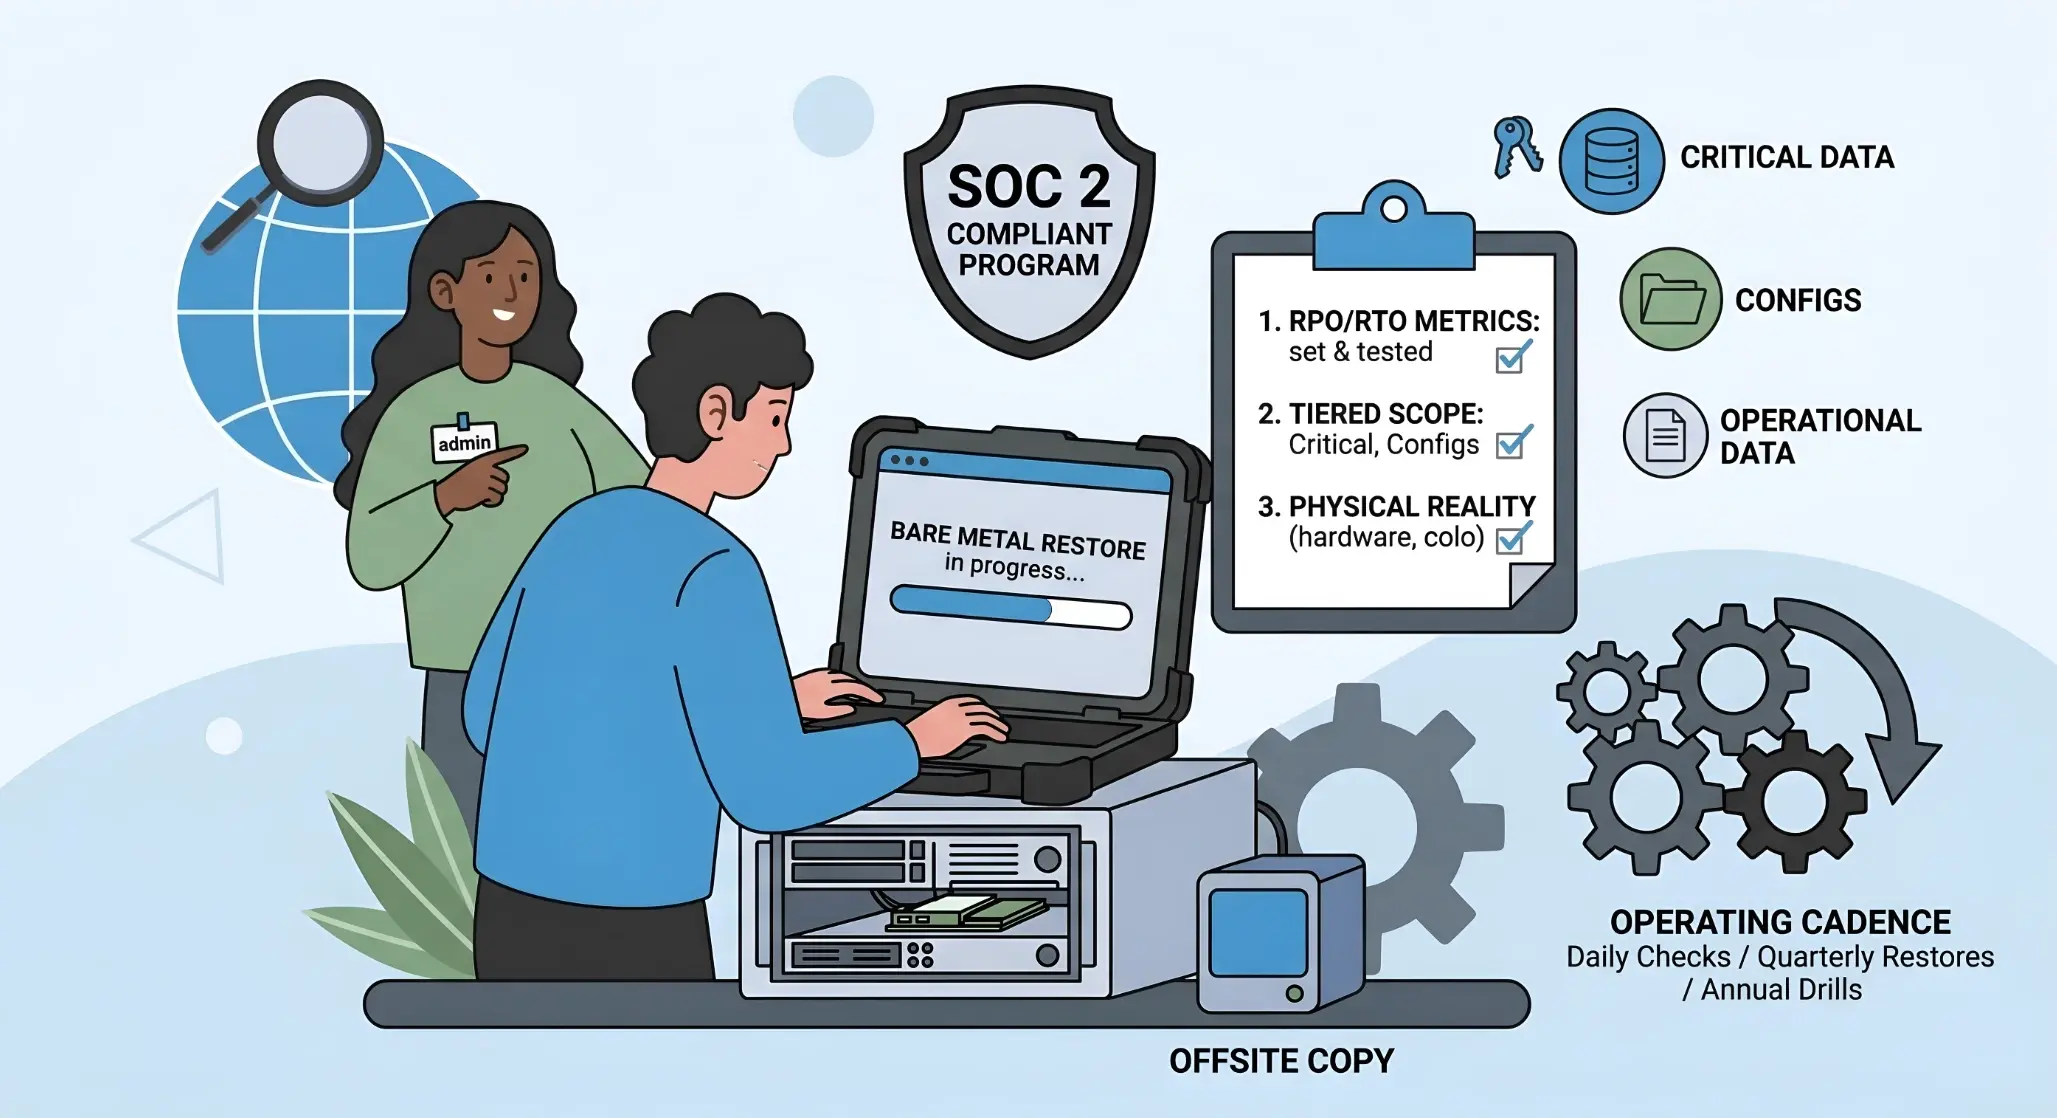
Infographic for SOC 2 Backup and Disaster Recovery. An admin watches a tech perform a "Bare Metal Restore." A checklist highlights RPO/RTO metrics, tiered scope (Critical Data, Configs, Operational Data), and physical hardware. Icons show offsite copies and an operating cadence for drills.

SOC 2 Backup and Disaster Recovery for On-Premise Infrastructure

Cloud disaster recovery is a region failover. Click a button, spin up infrastructure in another availability zone, and the platform handles...
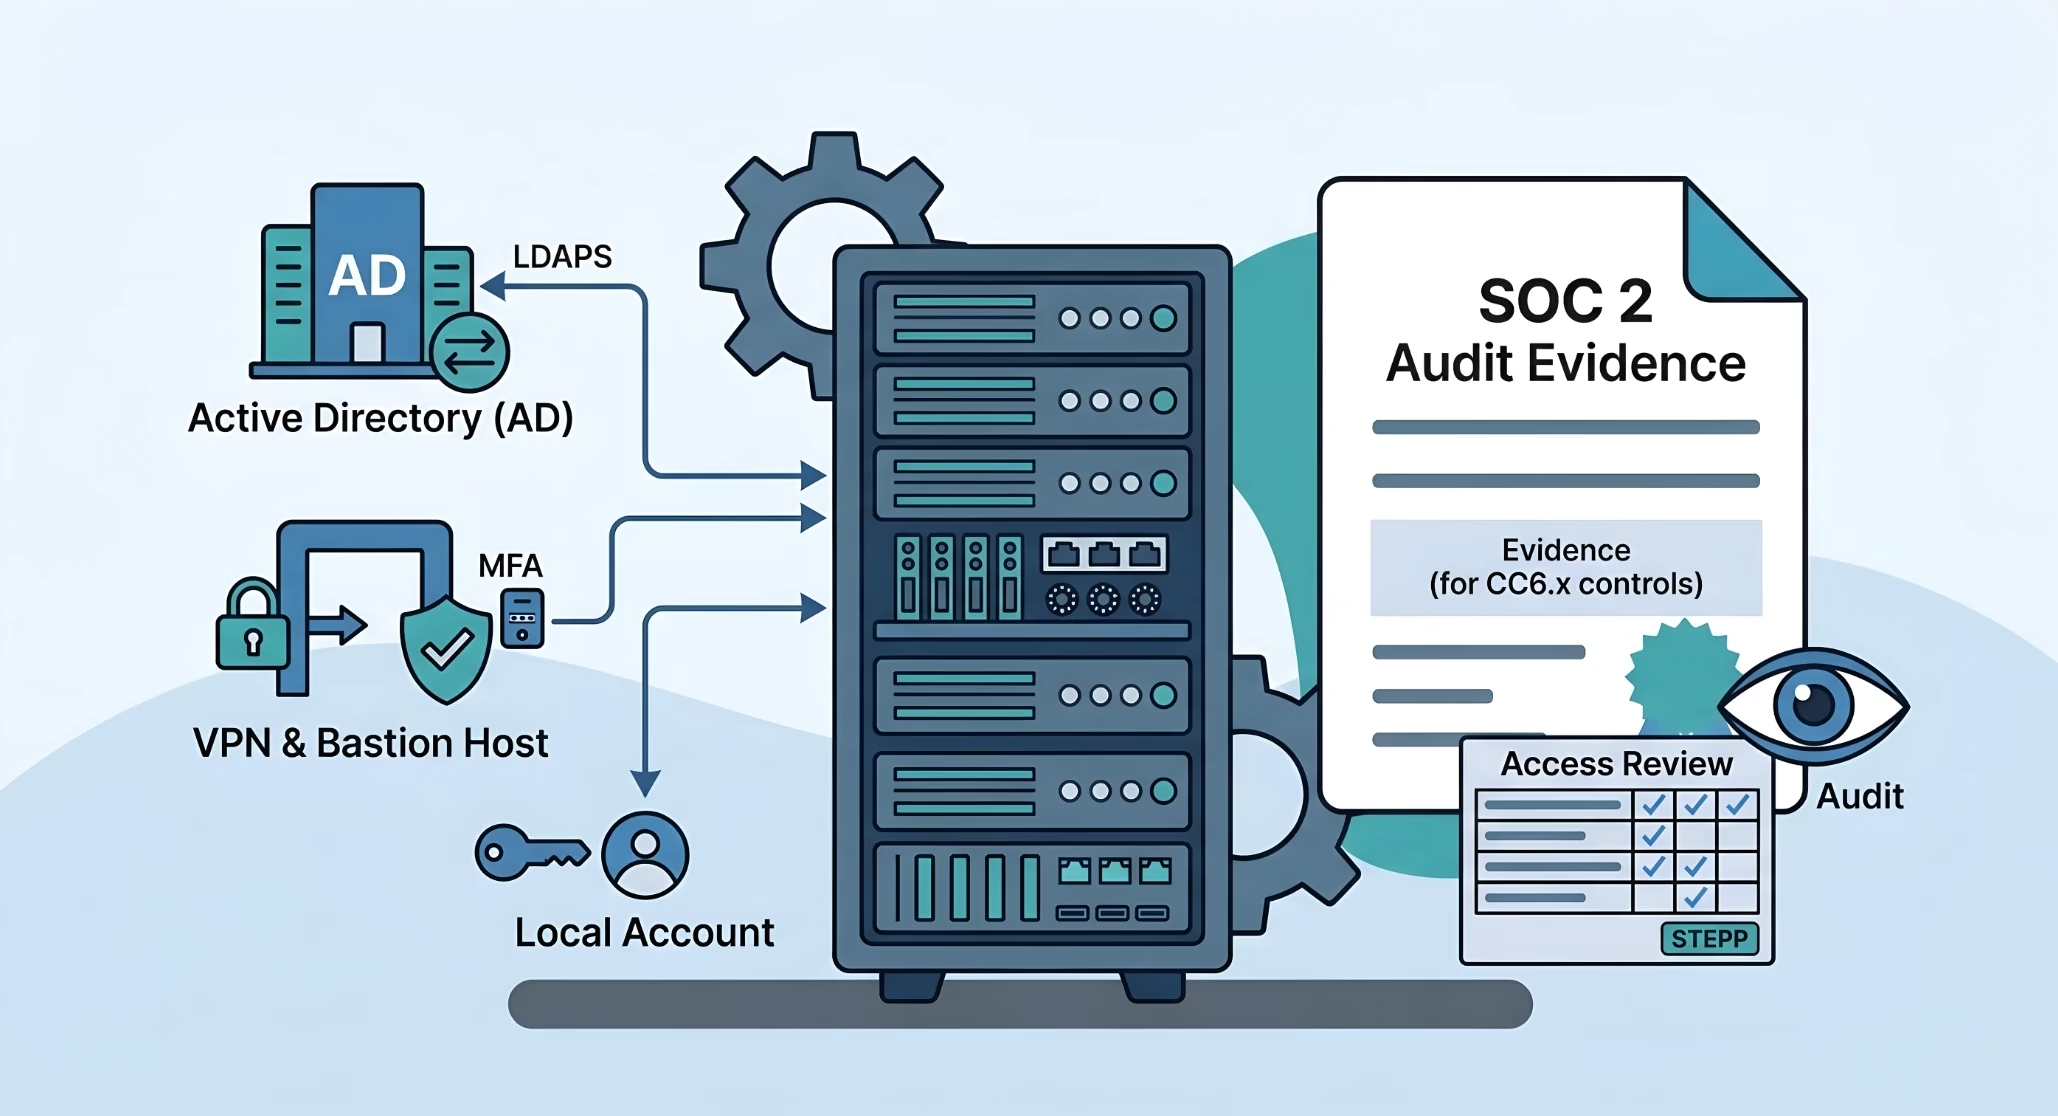
An illustration showing SOC 2 access control for on-premise servers. It depicts Active Directory via LDAPS, VPN and Bastion hosts with MFA, and local accounts connecting to a server rack. A "SOC 2 Audit Evidence" document for CC6.x controls and an access review checklist are shown on the right.

SOC 2 Access Control for On-Premise and Bare Metal Environments

In cloud environments, access control is a managed service. AWS IAM provides centralized identity, Okta handles SSO across every SaaS tool, and the...
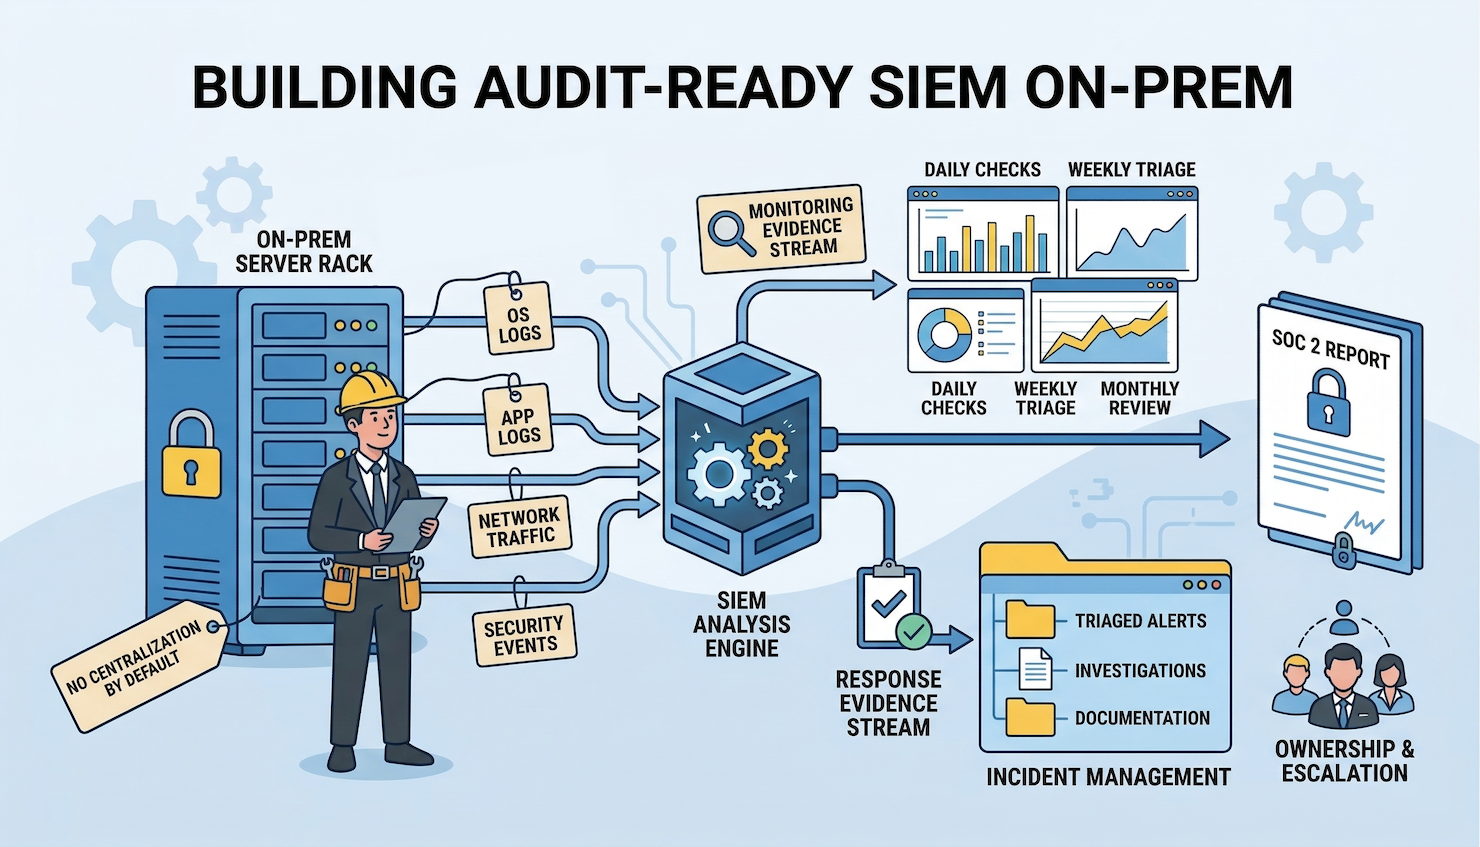
Infographic titled "Building Audit-Ready SIEM On-Prem." It shows logs (OS, App, Network, Security) flowing from a server rack into a SIEM Analysis Engine. This feeds into monitoring streams, incident management (triaged alerts, investigations), and ownership escalation to produce a SOC 2 Report.

SOC 2 Logging and SIEM for Bare Metal Servers

In a cloud environment, centralized logging is a toggle. Enable CloudTrail, turn on VPC Flow Logs, configure GuardDuty, and the compliance platform...
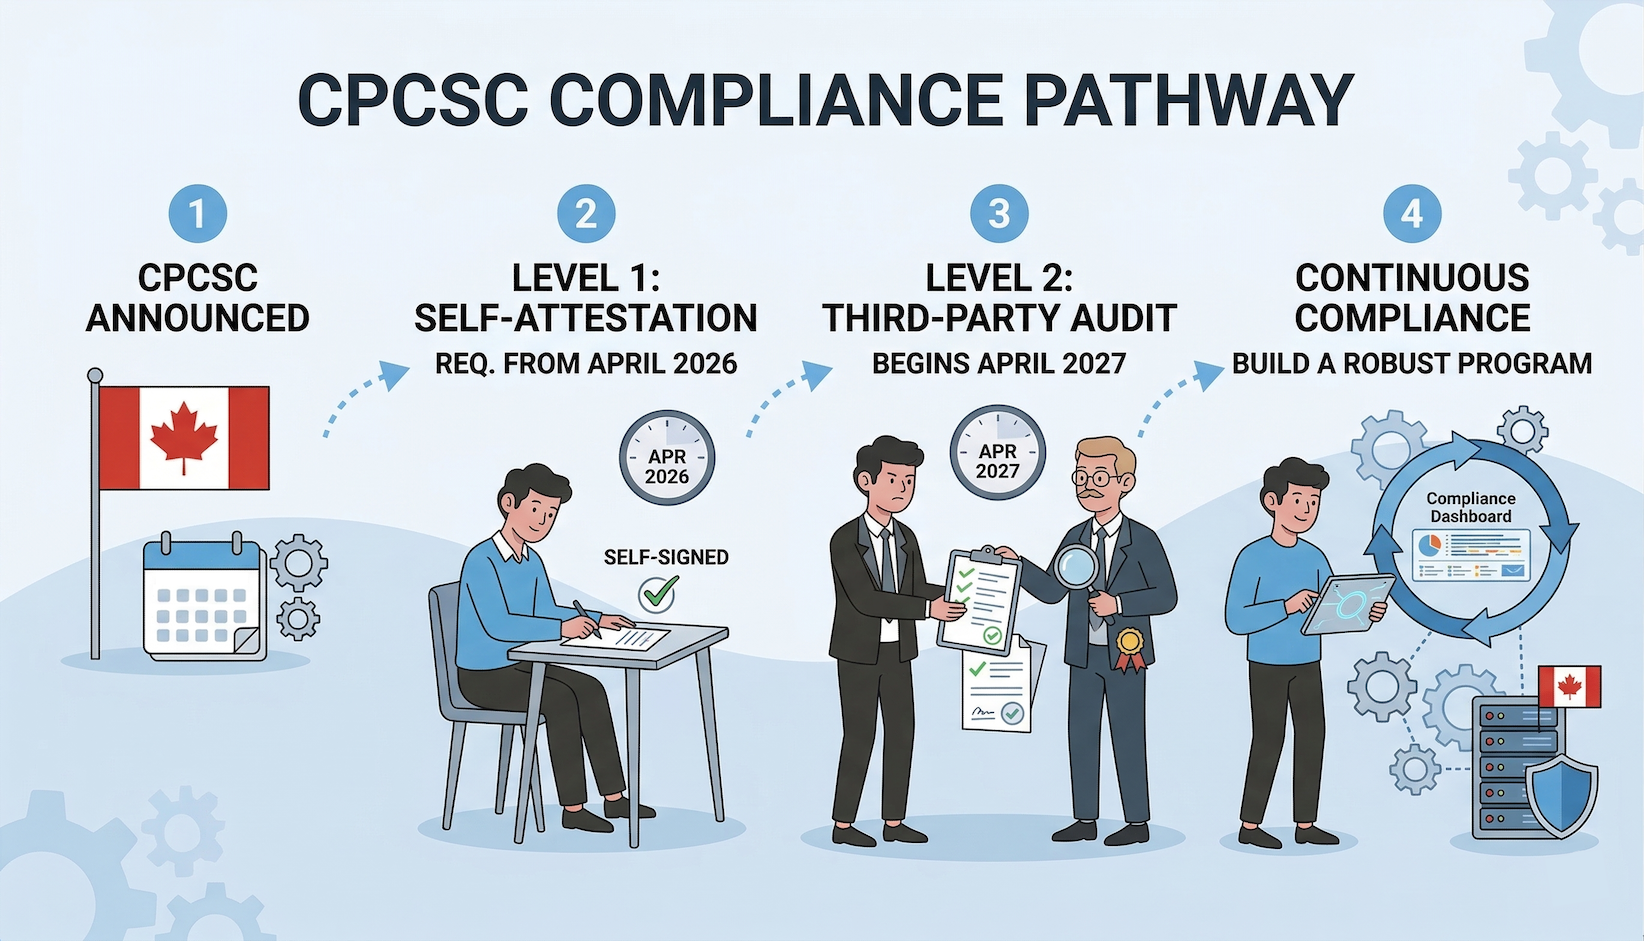
Infographic titled "CPCSC Compliance Pathway" outlining four stages for Canadian defence contractors: 1. CPCSC Announced, 2. Level 1 Self-Attestation (April 2026), 3. Level 2 Third-Party Audit (April 2027), and 4. Continuous Compliance via a robust program and digital dashboard.

CPCSC: What Defence Contractors Need Before April 2026

The Canadian Program for Cyber Security Certification (CPCSC) is Canada's mandatory cybersecurity certification for companies bidding on Department...
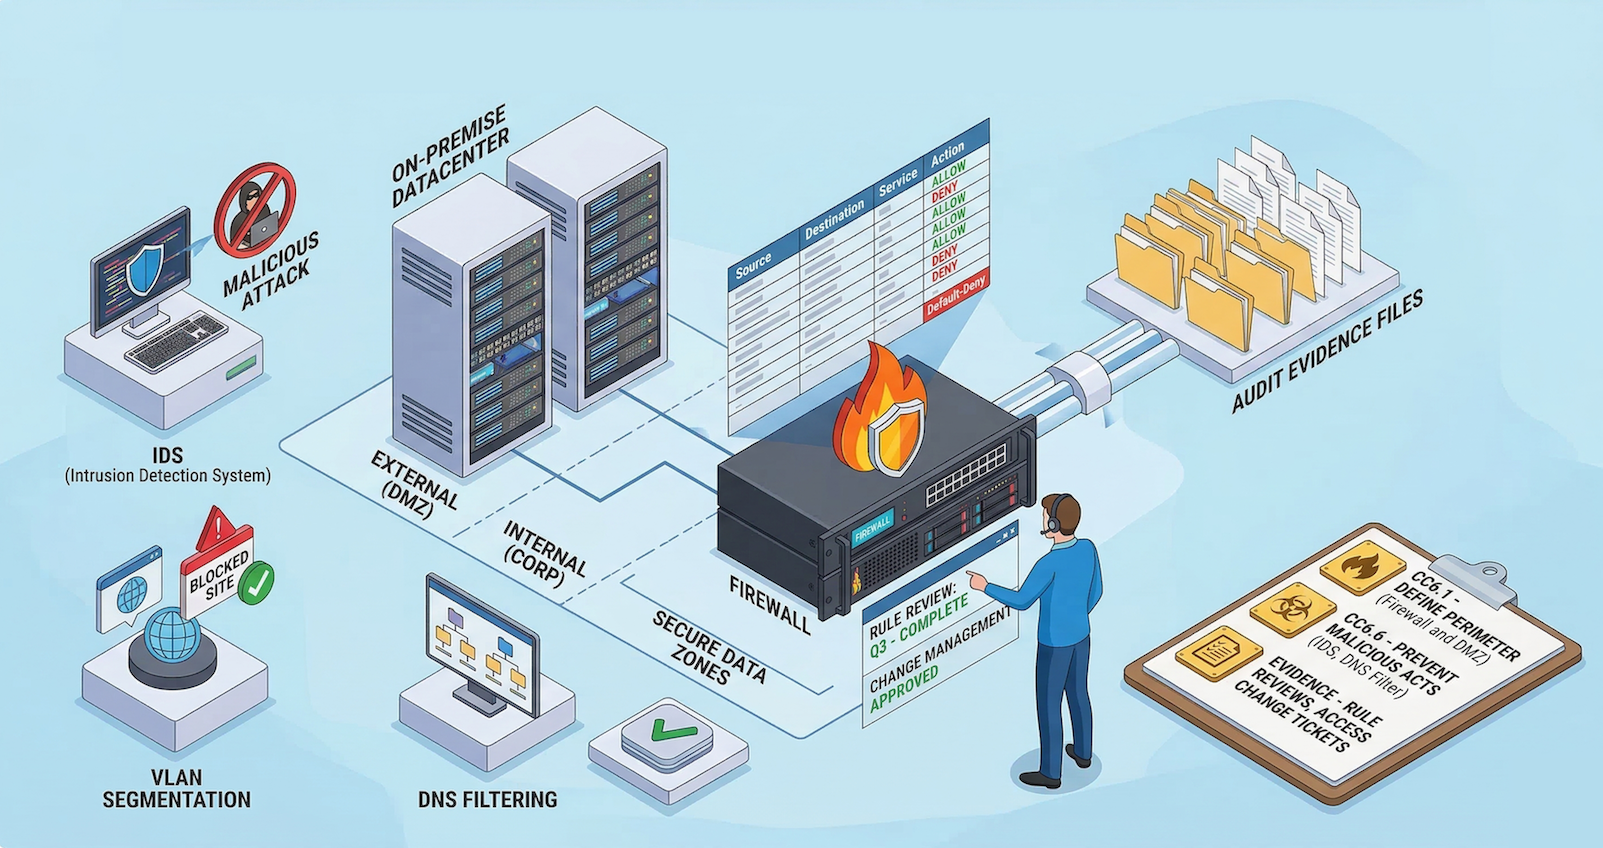
An isometric infographic titled "SOC 2 Compliance: Strengthening On-Premise Infrastructure." It shows a technician managing a firewall, IDS, and VLAN segmentation to protect data zones from malicious attacks. A clipboard lists CC6.1 and CC6.6 controls, leading to organized audit evidence files.

SOC 2 Network Security Controls for On-Premise Environments

Every SOC 2 guide on network security assumes the infrastructure lives in AWS. The advice is always the same: configure security groups, enable VPC...
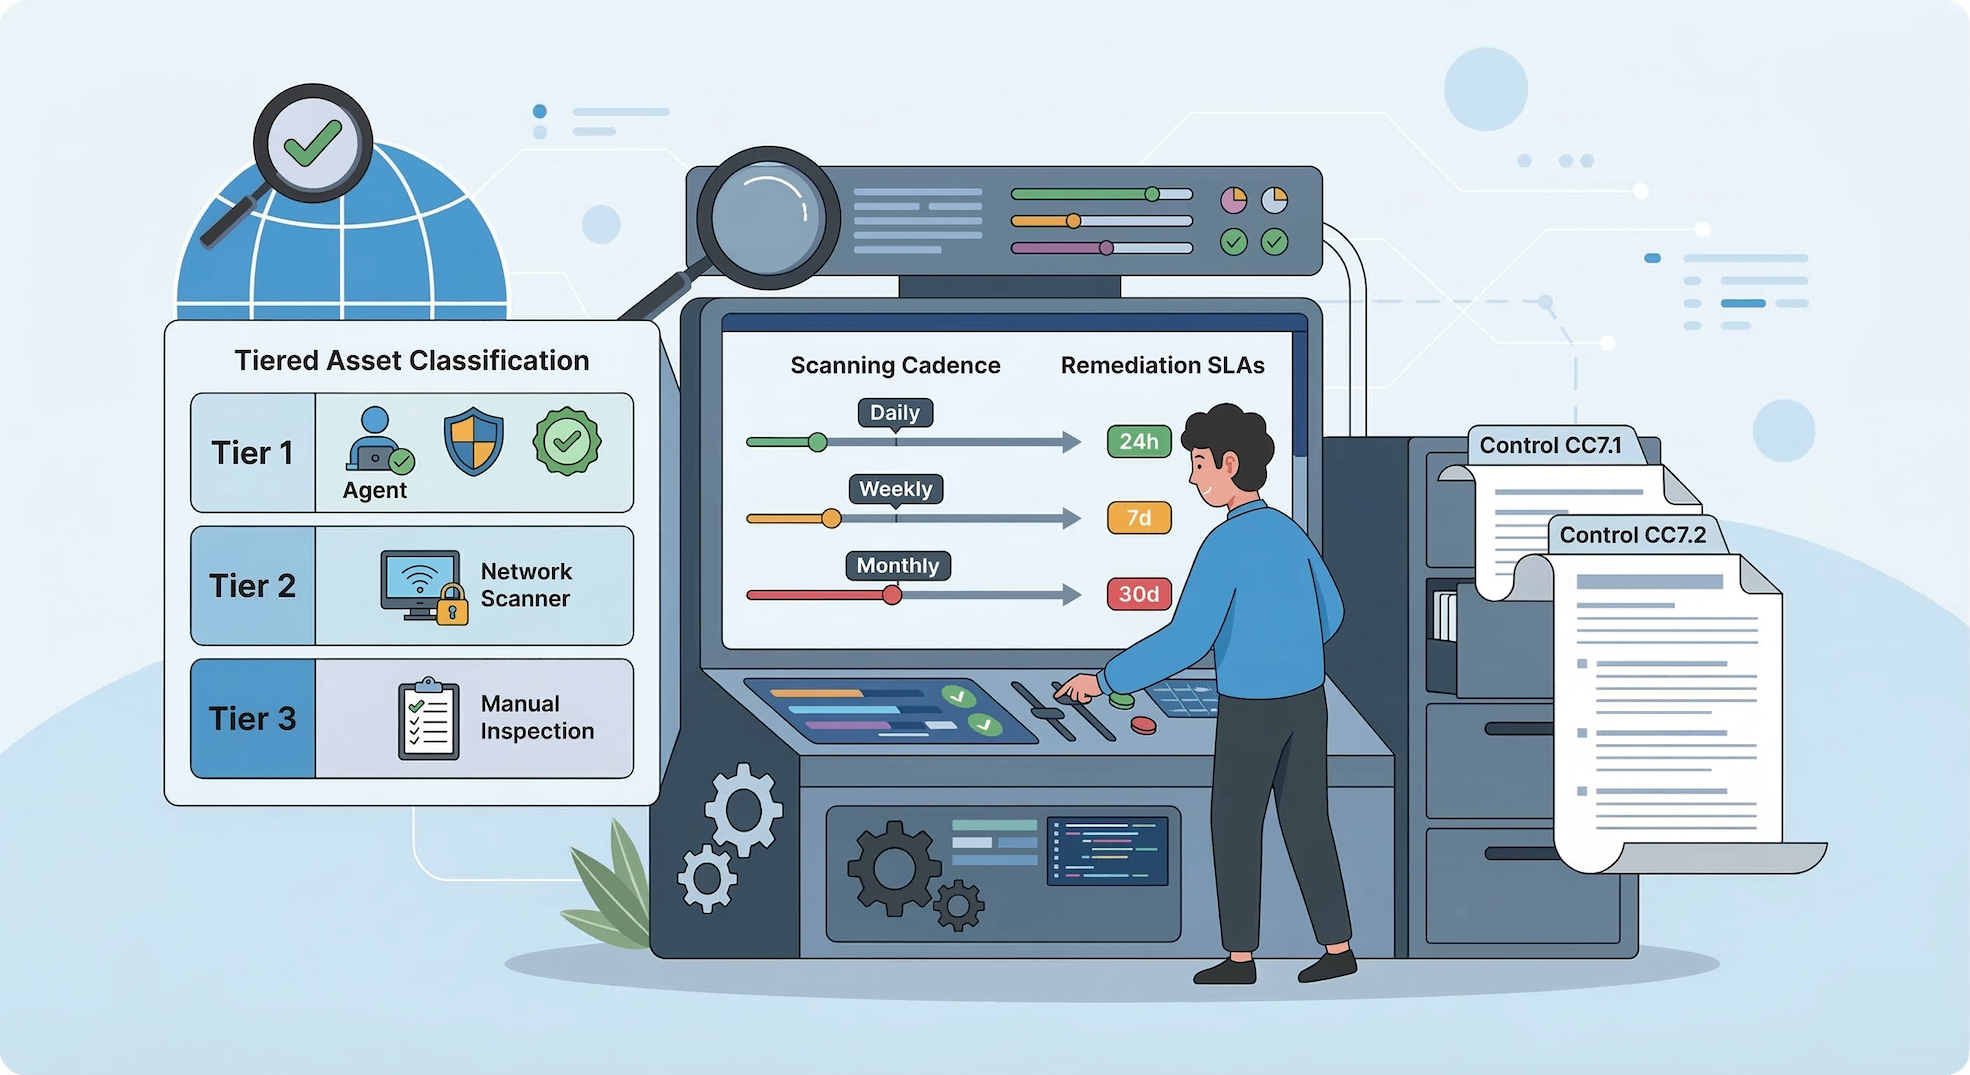
An illustration of a technician managing a security operations center for SOC 2 compliance. It features a tiered asset classification chart (Agent, Network Scanner, Manual Inspection), a dashboard showing scanning cadences and remediation SLAs, and filing cabinets with audit control documents.

SOC 2 Vulnerability Scanning for On-Prem Servers

Every SOC 2 vulnerability scanning guide assumes the same starting point: connect a cloud-native scanner, enable automated assessments, and let the...
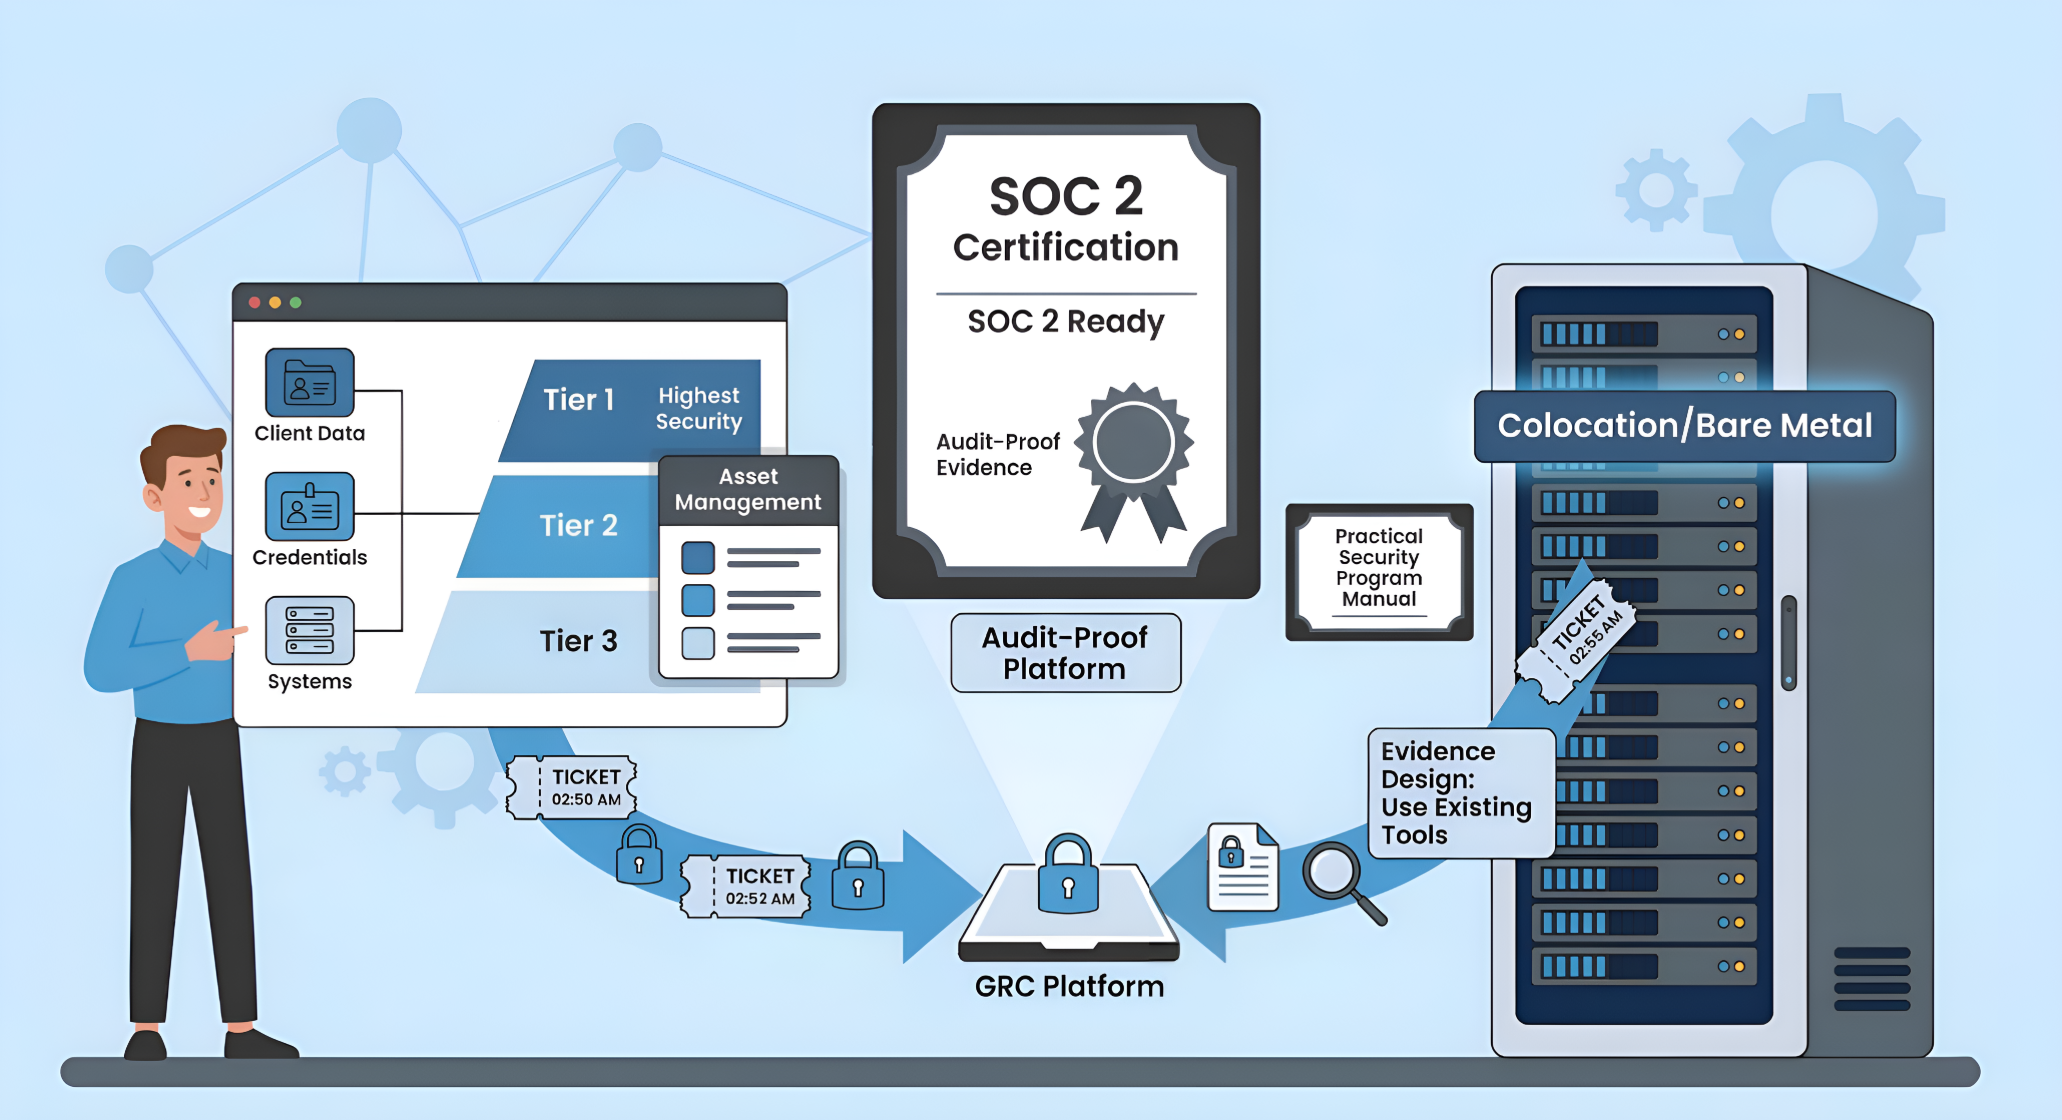
Infographic showing SOC 2 certification for Colocation/Bare Metal environments. It depicts an Audit-Proof Platform (GRC) collecting evidence like tickets and asset management data to achieve "SOC 2 Ready" status outside of standard AWS-style clouds.

SOC 2 Readiness for Bare Metal SaaS: What to Expect

A pattern keeps showing up. A SaaS company that has been running successfully for years, sometimes a decade or more, gets a call from a major...
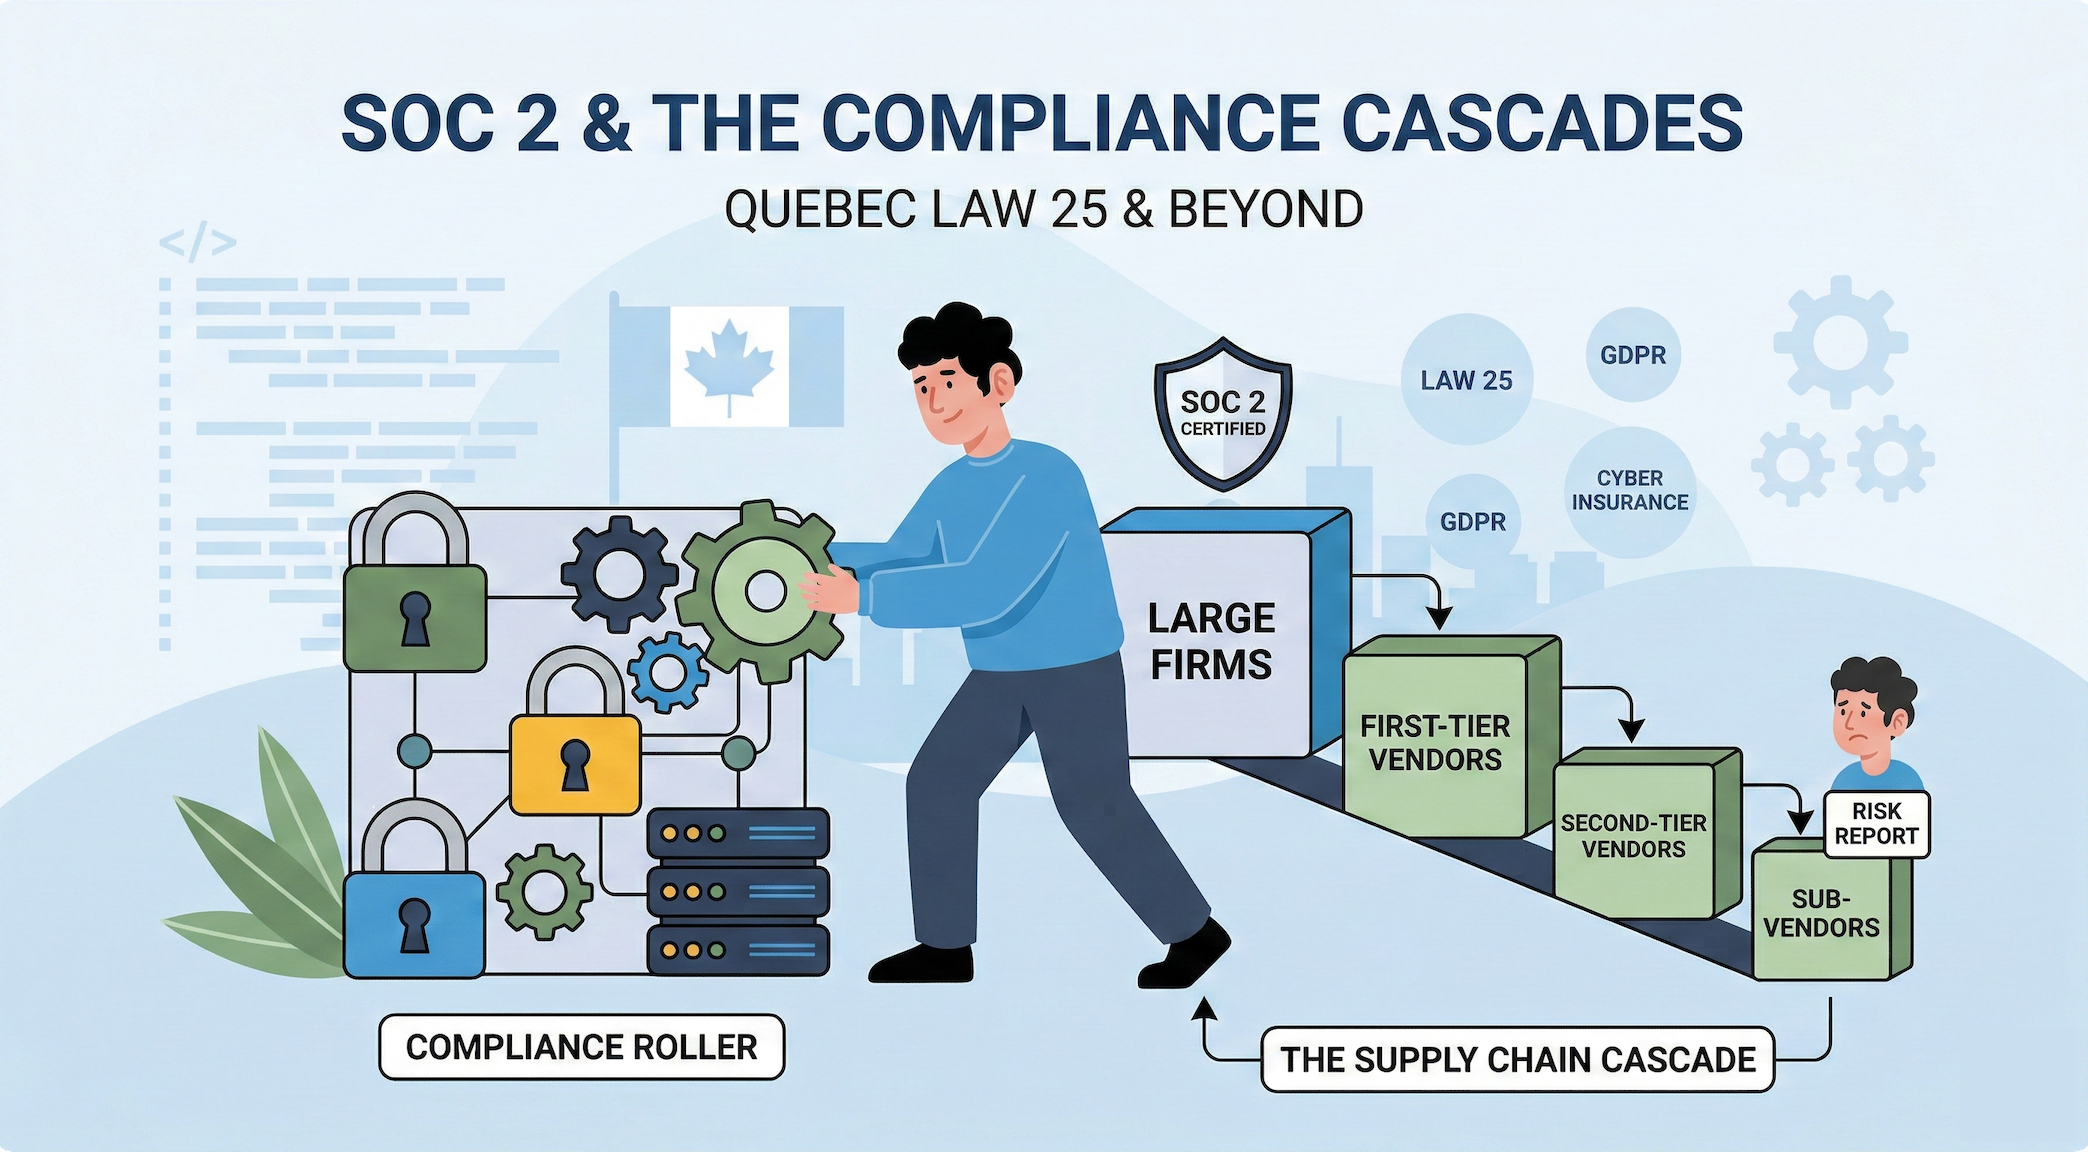
An infographic titled "SOC 2 & THE COMPLIANCE CASCADES" depicts a "Compliance Roller" pushing a "Supply Chain Cascade" of blocks from Large Firms down to Sub-Vendors. This illustrates how Law 25 and GDPR requirements create a chain reaction of SOC 2 necessity for small vendors.

The SOC 2 Snowball: How Law 25 Pushes Compliance Down Supply Chains

SOC 2, and compliance in general, is self-perpetuating. Once a company achieves certification, one of the first things the framework requires is...
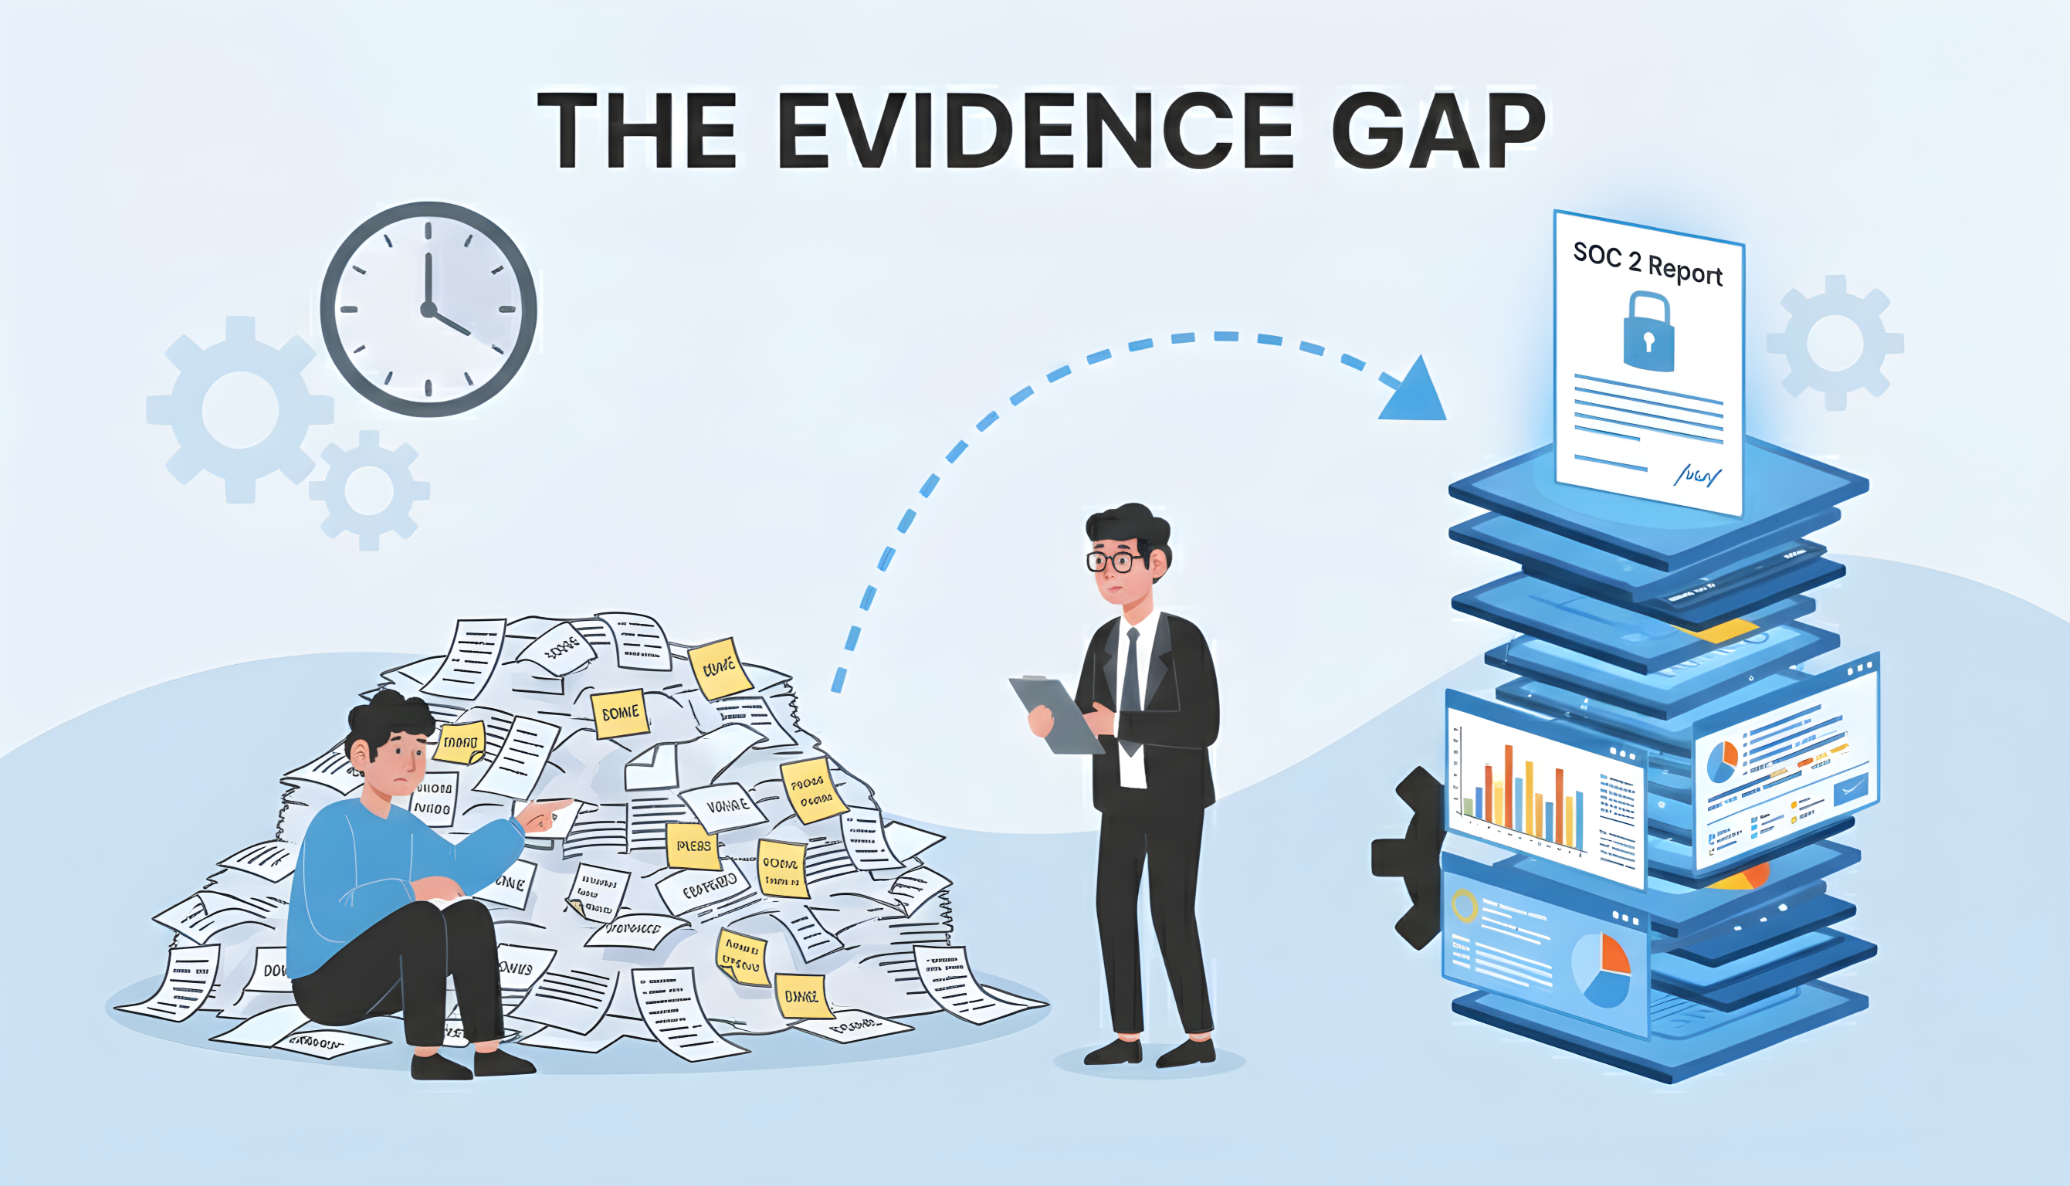
An illustration titled "THE EVIDENCE GAP." On the left, a person sits by a messy pile of papers, representing manual chaos. On the right, a neat stack of digital dashboards leads to a "SOC 2 Report." A blue arrow points from the clutter toward the streamlined, automated digital solution.

Bridging the Evidence Gap: How to Turn Solid Security into SOC 2 Compliance

The most common compliance gap has nothing to do with missing controls. It's missing evidence.

What we see often is that technically competent teams...
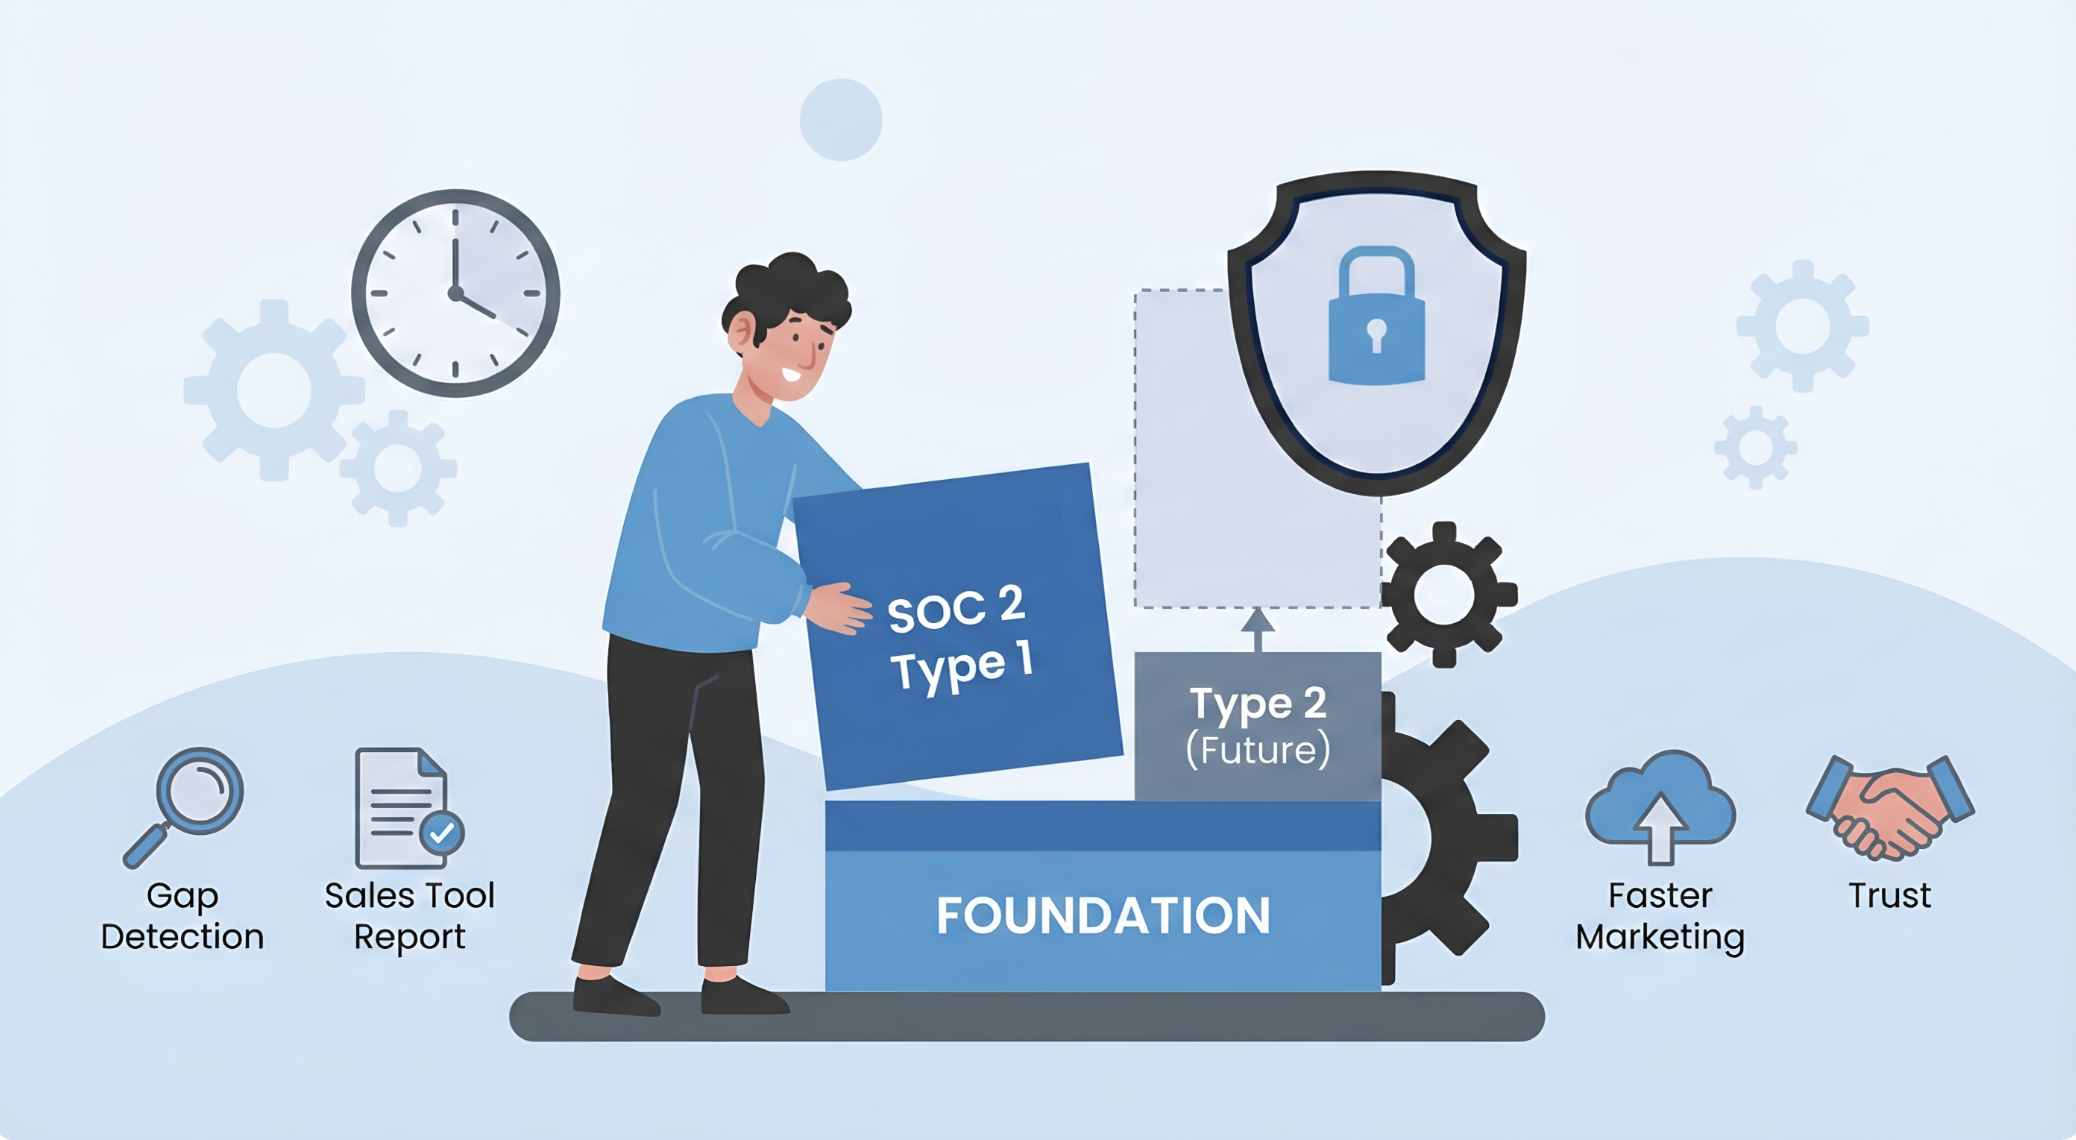
Illustration of the SOC 2 compliance journey progressing from a Type 1 audit to a Type 2 audit.

Why We Recommend SOC 2 Type 1 (Even Though You Don't Need It)

Most companies skip straight to Type 2. It's the *real* SOC 2, right? Type 1 is just not worth it. We used to think that way too. We've changed our...
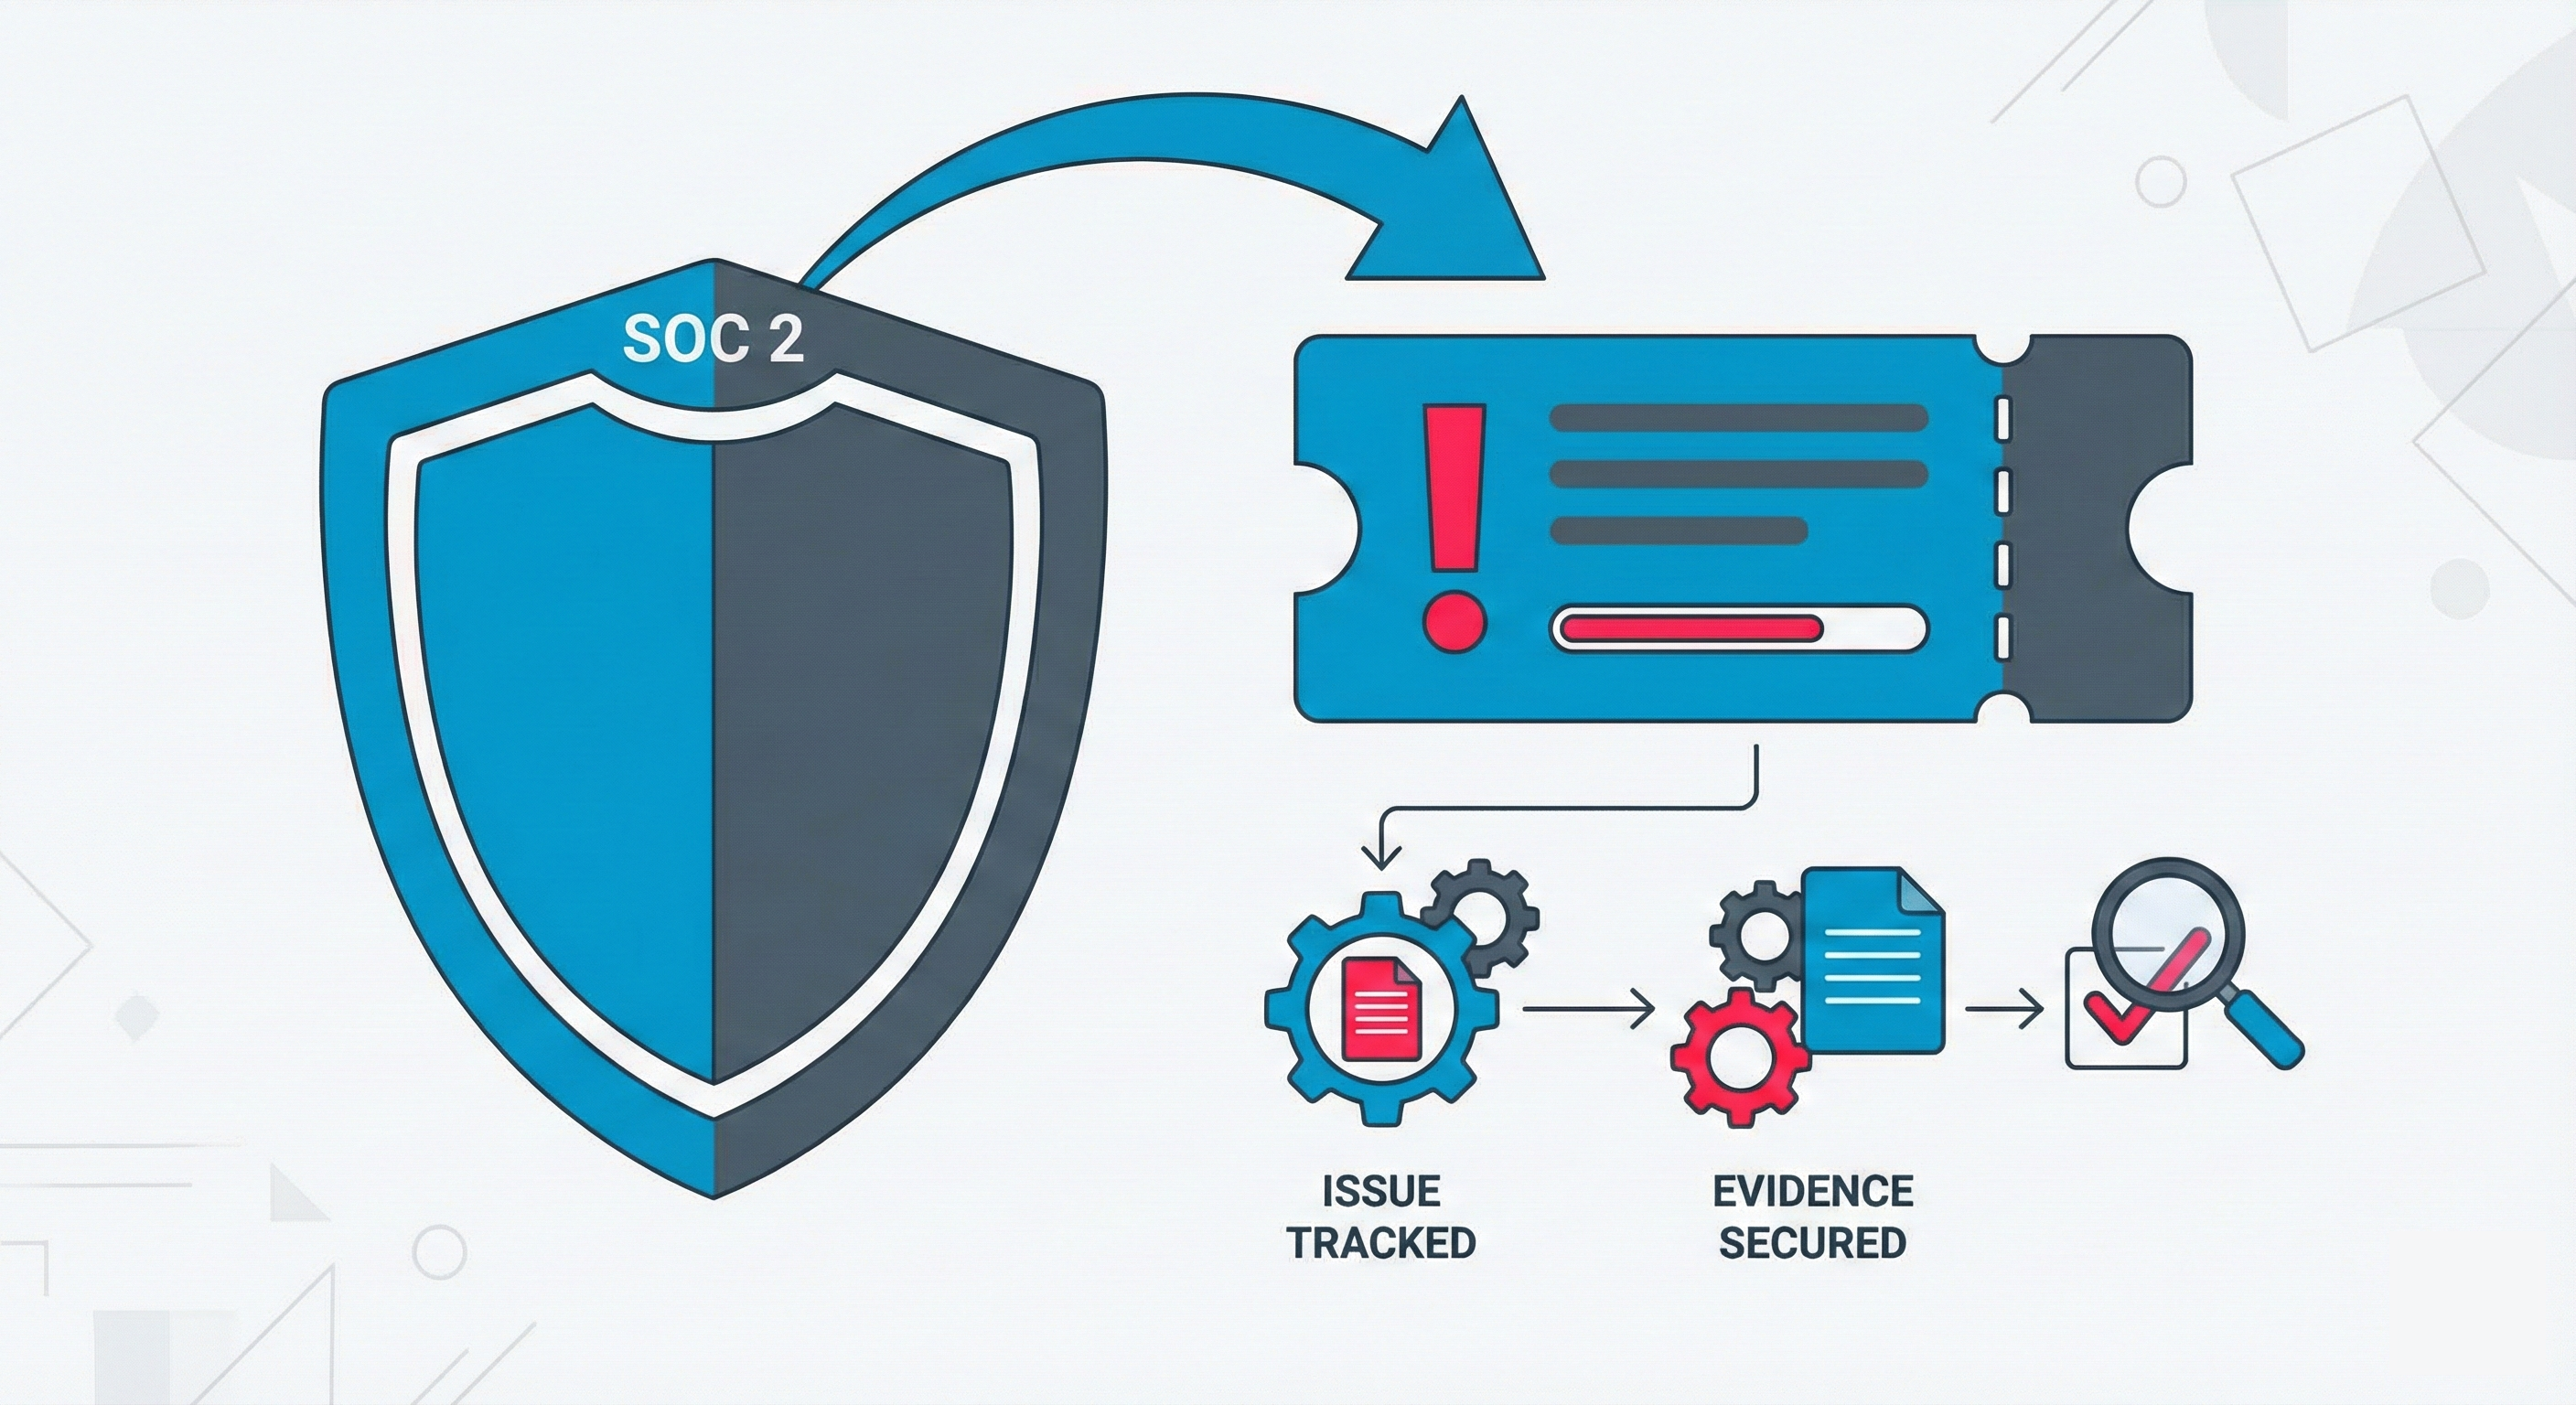
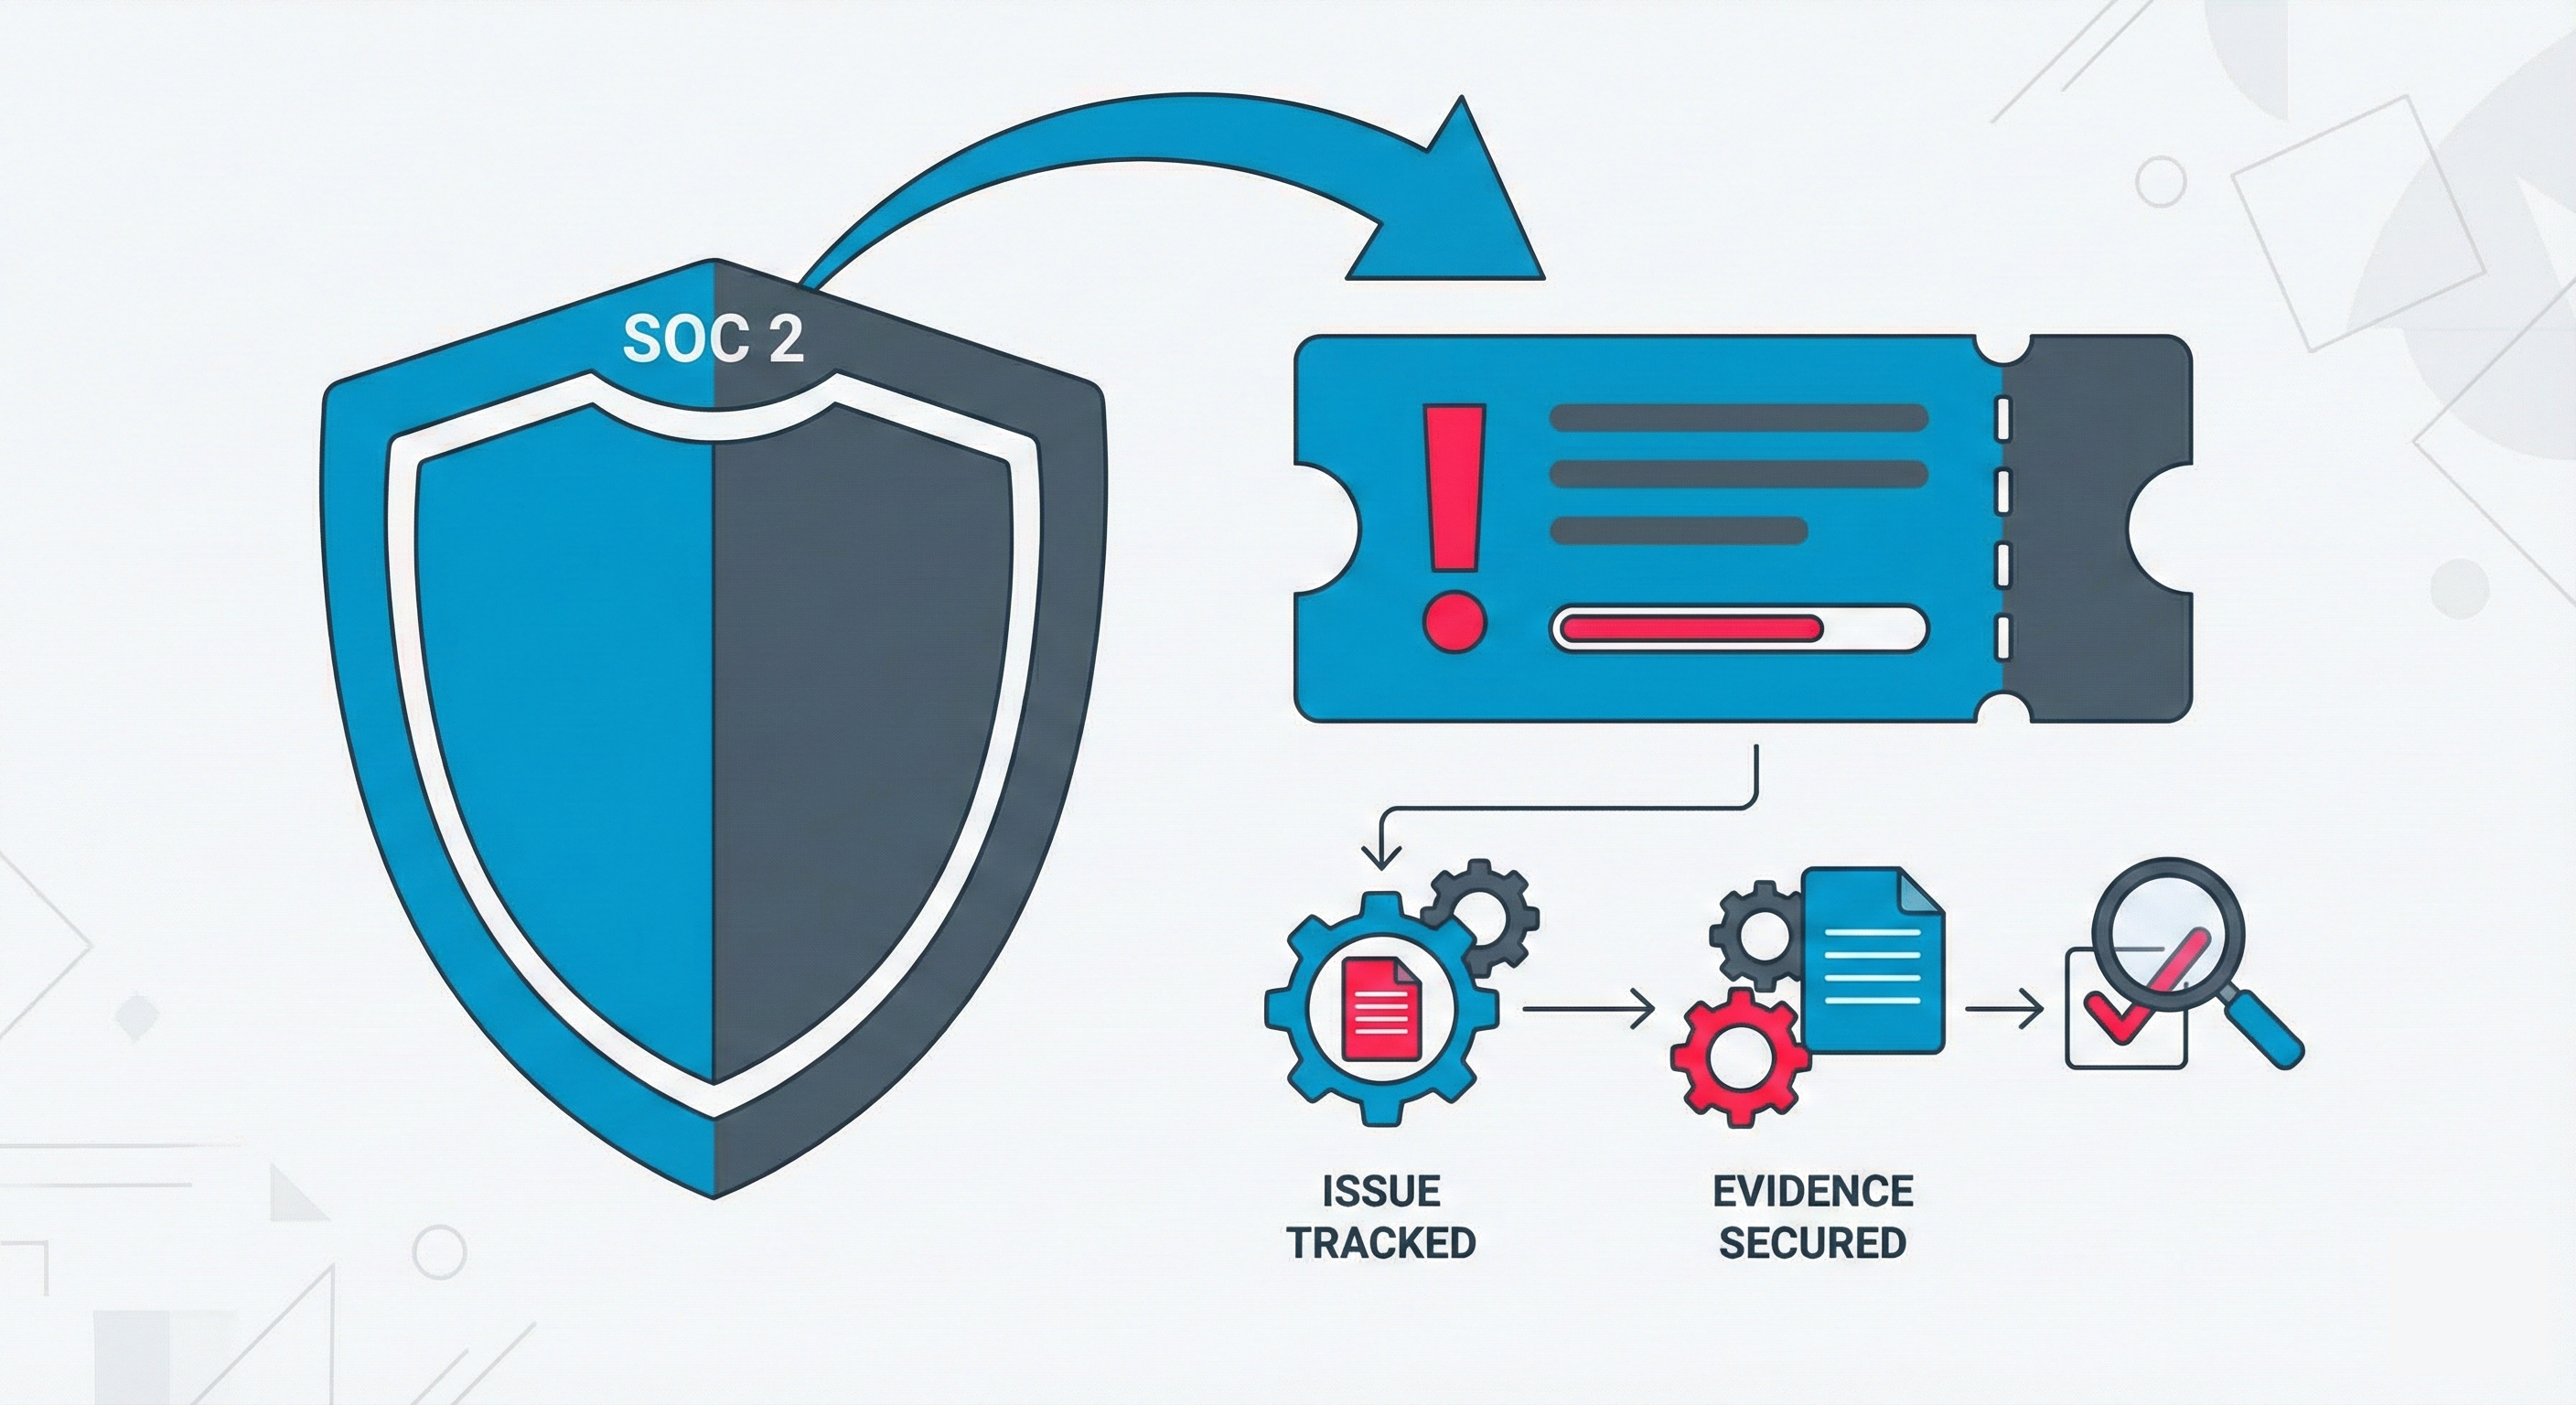
Featured image for SOC 2 SLA for vulnerability patching

SOC 2 Ticketing & SLAs: Vulnerability Patching & Incident Response

TL;DR: SOC 2 compliance requires a formal, trackable process for all security-relevant activities. Under the Trust Services Criteria, this means...
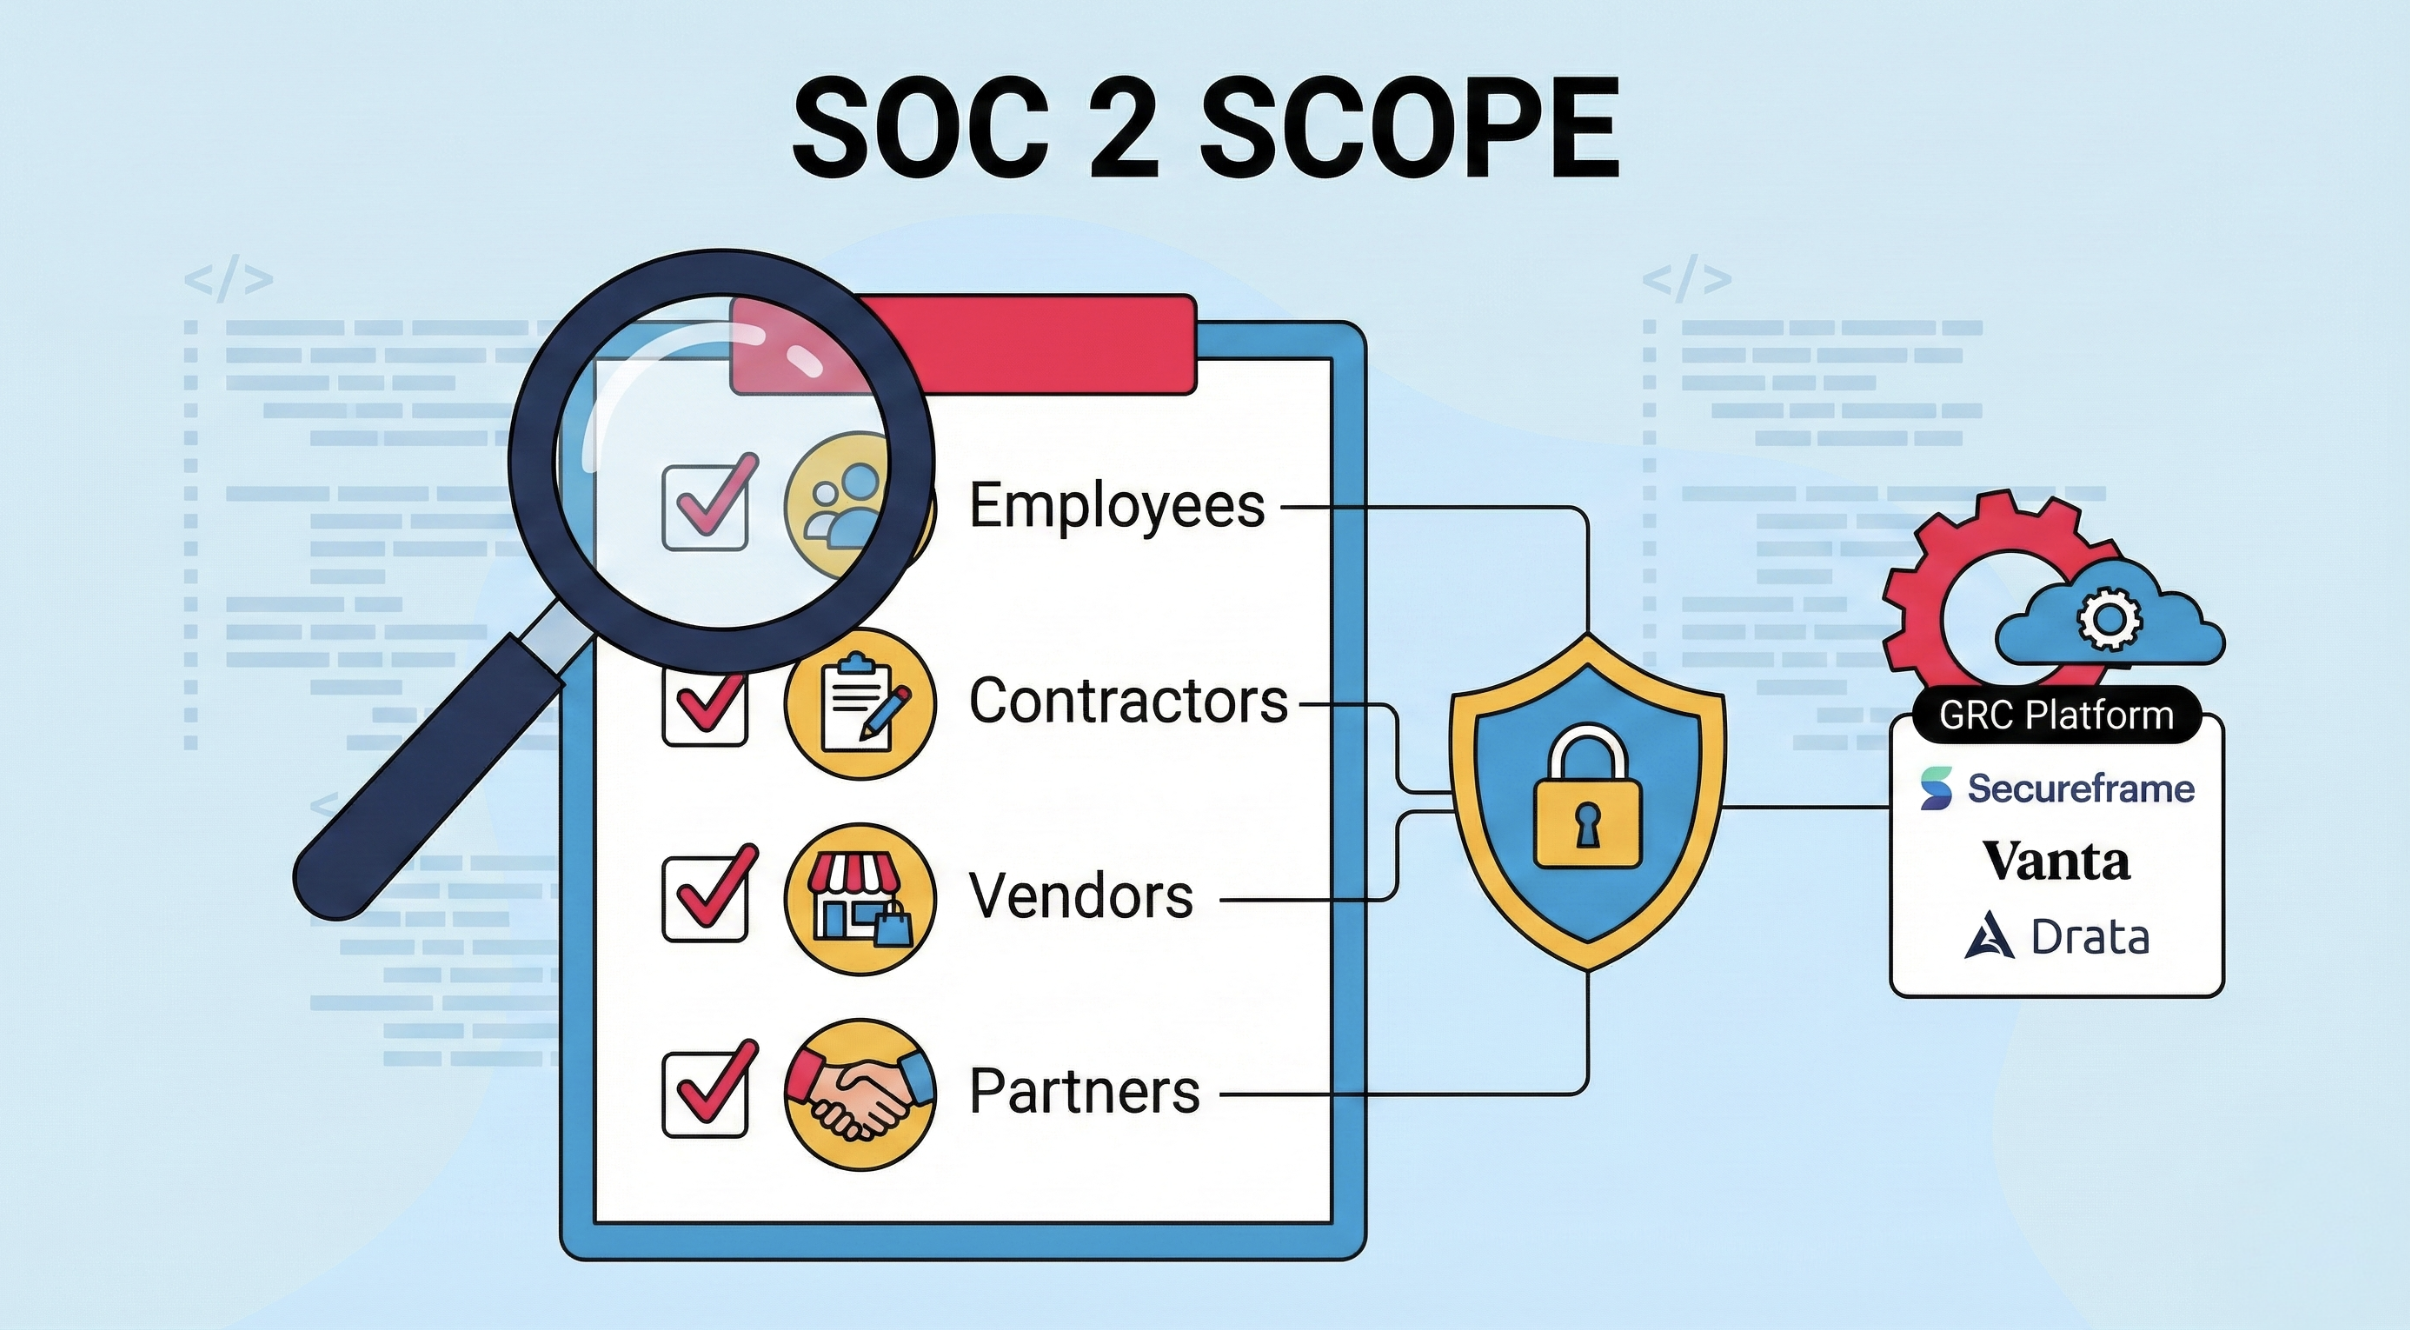
Audit scope (magnifying glass) for SOC 2 includes Employees, Contractors, and Vendors, linking them to security controls (shield/lock). This process integrates with a GRC Platform featuring Secureframe, Vanta, and Drata logos. Light blue background with coding elements.

SOC 2 People Scoping: Which Employees, Contractors, and Vendors

TL;DR: The core question for SOC 2 people scoping: does their role or access affect your system's ability to meet its Trust Services Criteria...
Automate CI/CD Security for SOC 2: SAST, SCA, DAST Integration Guide

Automate CI/CD Security for SOC 2: SAST, SCA, DAST Integration Guide

As a CTO, securing your CI/CD pipeline is critical for SOC 2 compliance. This guide shows you how to automate essential security scans, Container...

Supply Chain Cyber Risk: Why Your Vendors' Security Is Your Problem

Supply Chain Cyber Risk: Why Your Vendors' Security Is Your Problem

Supply chain cyber risk has become one of the most pressing cybersecurity challenges for businesses of all sizes. A single compromise in a supplier’s...

Why Invest in Compliance Automation If You Only Need SOC 2?

Why Invest in Compliance Automation If You Only Need SOC 2?

TL;DR: Even when SOC 2 is the only compliance requirement on the table, a compliance automation platform (Vanta, Drata, Secureframe, Scrut) pays for...

Security Questionnaire Automation: From Fire Drill to System

Security Questionnaire Automation: From Fire Drill to System

Security Questionnaire Automation: From Fire Drill to System

A 200-question security questionnaire lands in the sales team's inbox on a Thursday...

Is SOC 2 a Waste of Money? Evaluating Its Security Value

Is SOC 2 a Waste of Money? Evaluating Its Security Value

?
SOC 2 Scorecard

Score Your SOC 2 Security Program

16 questions mapped to Common Criteria. See your strengths, find your gaps, get a...

CMMC Explained: Cybersecurity Maturity Model Certification

CMMC Explained: Cybersecurity Maturity Model Certification

Most companies first hear about CMMC when a solicitation arrives with a clause they have never seen before, or when a prime contractor asks a...

What Is Cyber Security Posture? Definition and Importance

What Is Cyber Security Posture? Definition and Importance

Like in any industry, cyber security and cybercrime is constantly evolving. To keep up, you need to remain familiar with upcoming trends and the...

SOC 2 Trust Services Categories: Security, Availability, and Beyond

SOC 2 Trust Services Categories: Security, Availability, and Beyond

As a startup navigating the complexities of data security, understanding SOC 2 compliance is essential. SOC 2 (System and Organization Controls 2) is...

Shift-Left Cybersecurity Compliance: Benefits & Challenges

Shift-Left Cybersecurity Compliance: Benefits & Challenges

New business reality is that companies must prioritize cybersecurity compliance to protect customer data and demonstrate their security posture. The...

SOC 2 Renewal: What Changes the Second Time Around

SOC 2 Renewal: What Changes the Second Time Around

For many SaaS companies, achieving SOC 2 compliance is a major milestone, a sign that they take security and customer trust seriously. But the real...

What Is a SOC 2 Type 2 Report and Why Does It Matter?

What Is a SOC 2 Type 2 Report and Why Does It Matter?

TL;DR: A SOC 2 Type 2 report is an independent audit that evaluates whether an organization's security controls are operating effectively over a...

How to Build a Security Program That Maps to Any Framework

How to Build a Security Program That Maps to Any Framework

Every compliance framework, SOC 2, ISO 27001, CMMC, HIPAA, asks the same fundamental question: does this organization have an effective security...

A Practical Guide for Ransomware Response

A Practical Guide for Ransomware Response

Ransomware attacks are among the most disruptive forms of cybercrime, locking businesses out of their own data and demanding ransom for its release....

SOC 2 Compliance Roadmap: From Gap Assessment to Audit-Ready

SOC 2 Compliance Roadmap: From Gap Assessment to Audit-Ready

Every SOC 2 roadmap on the internet reads the same way: pick a platform, connect your integrations, run the gap analysis, remediate, audit. Five...