
Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

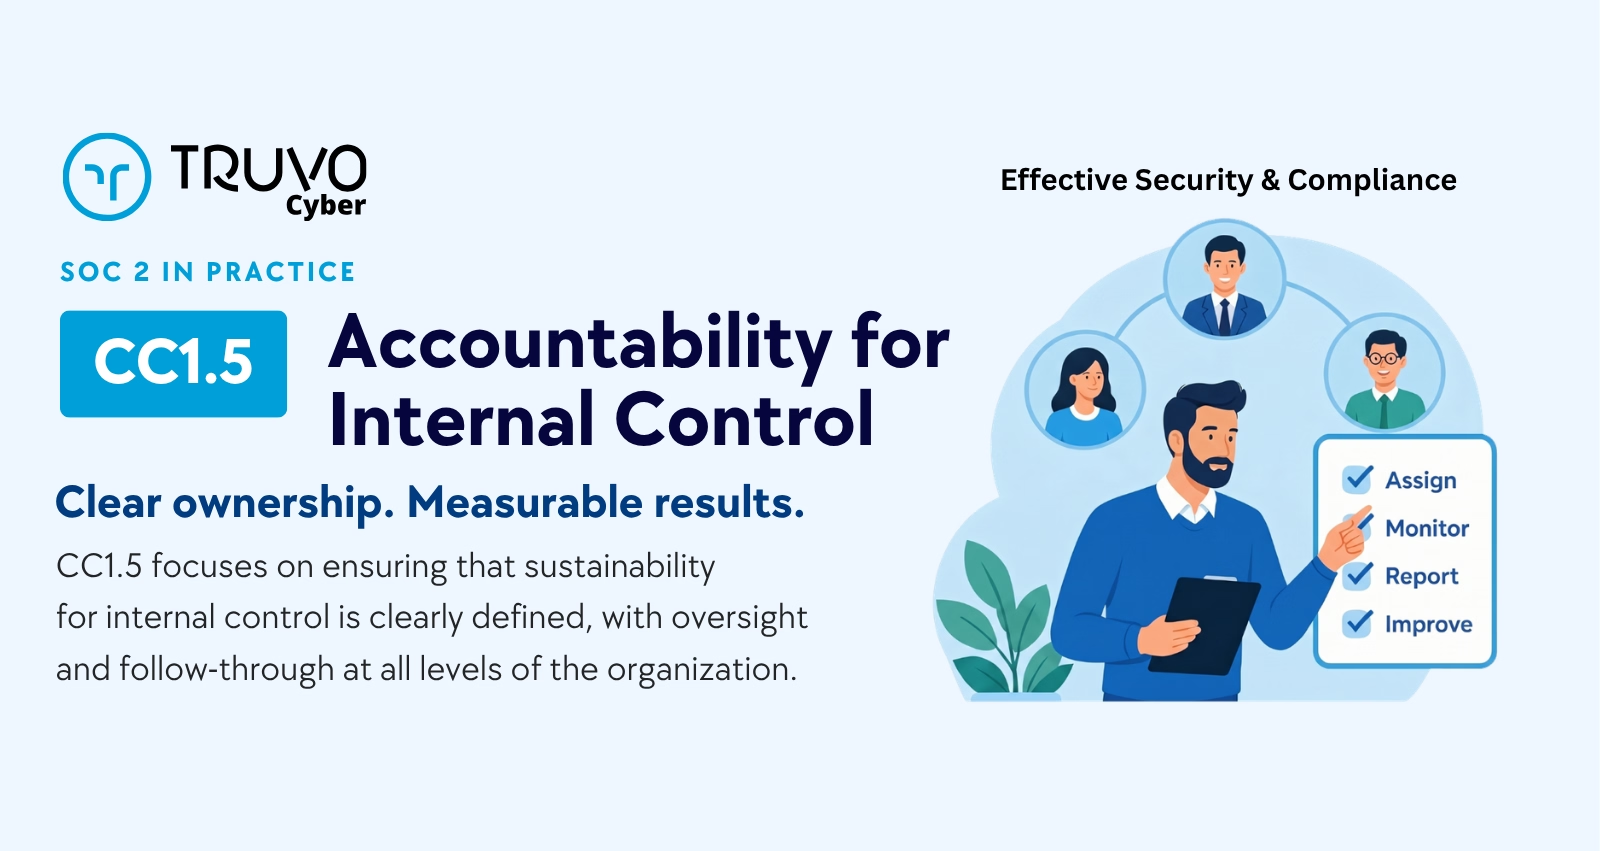
SOC2 CC1.5 - accountability for internal control

SOC 2 CC1.5: Accountability for Internal Control

SOC 2 CC1.5 requires an organization to hold individuals accountable for the internal control responsibilities assigned to them. It closes the CC1...
Stock photo by Ann H via Pexels, illustrating cybersecurity threat protection (temporary placeholder pending custom hero design).

SOC 2 CC6.8: Preventing and Detecting Unauthorized or Malicious Software

SOC 2 CC6.8 requires controls that prevent, or detect and act on, the introduction of unauthorized or malicious software. It sits in the CC6 series...
Stock photo by Markus Winkler via Pexels, illustrating data encryption network (temporary placeholder pending custom hero design).

SOC 2 CC6.7: Restricting the Transmission, Movement, and Removal of Information

SOC 2 CC6.7 requires that information is protected when it is transmitted, moved, or removed, and that only authorized users and processes can do so....
Stock photo by panumas nikhomkhai via Pexels, illustrating network security firewall (temporary placeholder pending custom hero design).

SOC 2 CC6.6: Protecting Against Threats From Outside System Boundaries

SOC 2 CC6.6 requires logical access security measures that protect the system against threats originating outside its boundaries. It sits in the CC6...
Stock photo by Andrey Matveev via Pexels, illustrating hardware data destruction (temporary placeholder pending custom hero design).

SOC 2 CC6.5: Discontinuing Protections Over Disposed Assets

SOC 2 CC6.5 requires that data and software are rendered unrecoverable before an asset loses its protections or leaves the company's control. It sits...
Stock photo by Gustavo Fring via Pexels, illustrating fraud prevention finance (temporary placeholder pending custom hero design).

SOC 2 CC3.3: Considering the Potential for Fraud in Risk Assessment

SOC 2 CC3.3 requires an entity to consider the potential for fraud when it assesses risks to its objectives. It sits in the CC3 series (Risk...
Stock photo by Nataliya Vaitkevich via Pexels, illustrating business change management (temporary placeholder pending custom hero design).

SOC 2 CC3.4: Identifying and Assessing Significant Changes

SOC 2 CC3.4 requires an entity to identify and assess changes that could significantly affect its system of internal control. It closes the CC3...
Stock photo by Mikhail Nilov via Pexels, illustrating policy documents compliance (temporary placeholder pending custom hero design).

SOC 2 CC5.3: Policies and Procedures

SOC 2 CC5.3 requires an organization to deploy its control activities through policies that state what is expected and procedures that put those...
Stock photo by Markus Winkler via Pexels, illustrating security controls audit (temporary placeholder pending custom hero design).

SOC 2 CC5.1: Selecting and Developing Control Activities

SOC 2 CC5.1 requires an organization to select and develop control activities that reduce its risks to an acceptable level, choosing each control...
Stock photo by Ketut Subiyanto via Pexels, illustrating business partnership meeting (temporary placeholder pending custom hero design).

SOC 2 CC2.3: External Communication

SOC 2 CC2.3 requires an organization to communicate with external parties about matters that affect how its internal control operates, and to give...
Stock photo by Yan Krukau via Pexels, illustrating business strategy planning (temporary placeholder pending custom hero design).

SOC 2 CC3.1: Specifying Objectives With Enough Clarity to Assess Risk

SOC 2 CC3.1 requires an entity to state its objectives clearly enough that the risks to those objectives can be identified and assessed. It opens the...
Stock photo by Monstera Production via Pexels, illustrating risk management analysis (temporary placeholder pending custom hero design).

SOC 2 CC3.2: Identifying and Analyzing Risk to Your Objectives

SOC 2 CC3.2 requires an entity to identify risks to its objectives across the whole organization and to analyze them well enough to decide how each...
SOC2 CC1.4 Commitment to Competence

SOC 2 CC1.4: Commitment to Competence

SOC 2 CC1.4 requires an organization to attract, develop, and retain people who are competent to carry out their responsibilities, and to hold...
Stock photo by Negative Space via Pexels, illustrating data analytics dashboard (temporary placeholder pending custom hero design).

SOC 2 CC2.1: Quality Information Supporting Controls

SOC 2 CC2.1 requires an organization to obtain or generate and use relevant, quality information so that its internal controls can function. It opens...
SOC 2 CC1.3 - Structures, Reporting Lines & Authorities

SOC 2 CC1.3: Structures, Reporting Lines, and Authorities

SOC 2 CC1.3 requires management, with board oversight, to set up the organizational structures, reporting lines, and authorities the business needs...
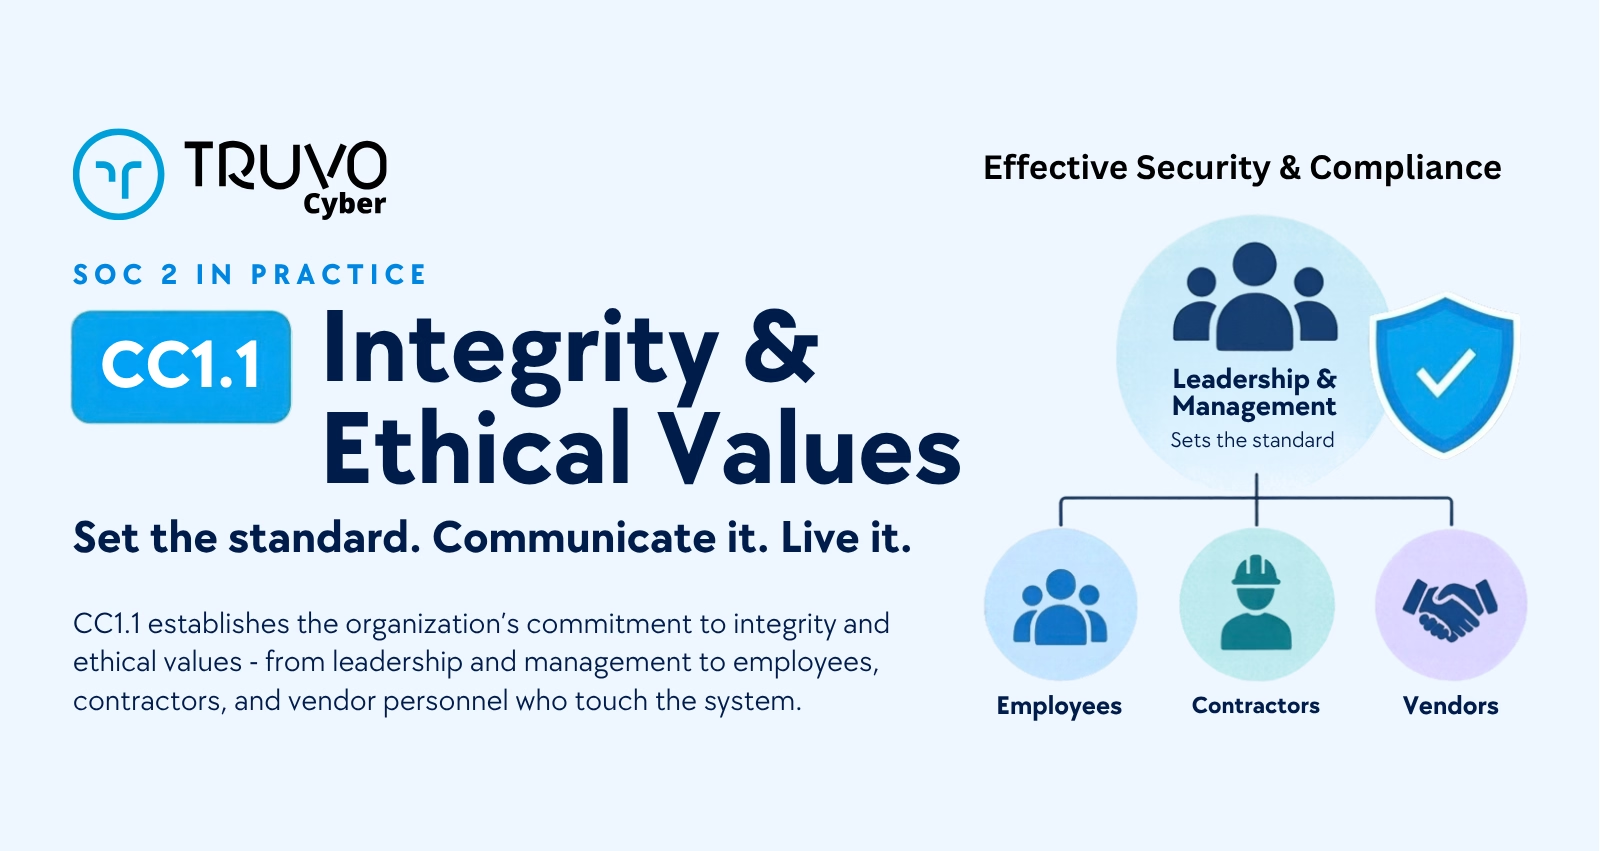
SOC 2 CC1.1 Integrity & Ethical Values

SOC 2 CC1.1: Integrity and Ethical Values

SOC 2 CC1.1 requires an organization to demonstrate a commitment to integrity and ethical values, starting with how the board and management behave...
Stock photo by Markus Winkler via Pexels, illustrating compliance deficiency tracking remediation (temporary placeholder pending custom hero design).

SOC 2 CC4.2: Evaluating and Communicating Deficiencies

SOC 2 CC4.2 requires an organization to evaluate the deficiencies its monitoring turns up and communicate them, in a timely way, to the people who...
Stock photo by Towfiqu barbhuiya via Pexels, illustrating internal audit security assessment (temporary placeholder pending custom hero design).

SOC 2 CC4.1: Ongoing and Separate Evaluations

SOC 2 CC4.1 requires an organization to select, develop, and run a mix of ongoing and separate evaluations to confirm its internal controls are...
Stock photo by Felicity Tai via Pexels, illustrating two business professionals comparing documents meeting (temporary placeholder pending custom hero design).

SOC 2 CC6.4: Restricting Physical Access to Facilities and Assets

SOC 2 CC6.4 requires that physical access to facilities and protected information assets is restricted to authorized personnel. It sits in the CC6...
Stock photo by Erik Mclean via Pexels, illustrating vendor risk third party management (temporary placeholder pending custom hero design).

SOC 2 CC9.2: Vendor and Business Partner Risk Management

SOC 2 CC9.2 is the vendor and business partner risk criterion: it requires an organization to assess and manage the risks that come from the third...
Stock photo by K via Pexels, illustrating business continuity disaster recovery (temporary placeholder pending custom hero design).

SOC 2 CC9.1: Risk Mitigation for Business Disruptions

SOC 2 CC9.1 is the risk mitigation criterion for business disruptions: it requires an organization to identify, select, and develop activities that...
Stock photo by Tima Miroshnichenko via Pexels, illustrating security operations monitoring dashboard (temporary placeholder pending custom hero design).

SOC 2 CC7.2: Monitoring System Components for Anomalies

SOC 2 CC7.2 is the security monitoring criterion in the Trust Services Criteria: it requires an organization to monitor its systems for anomalies and...
Stock photo by Ann H via Pexels, illustrating vulnerability management security scanning (temporary placeholder pending custom hero design).

SOC 2 CC7.1: Detecting Configuration Changes and New Vulnerabilities

SOC 2 CC7.1 is where the vulnerability management program lives inside the Trust Services Criteria: it requires an organization to detect...
Physical access-control keypad and card reader, illustrating role-based access and least privilege for SOC 2 CC6.3.

SOC 2 CC6.3: Role-Based Access, Least Privilege, and Segregation of Duties

SOC 2 CC6.3 is where role design meets audit evidence: it requires that access to protected information assets is authorized, modified, or removed...
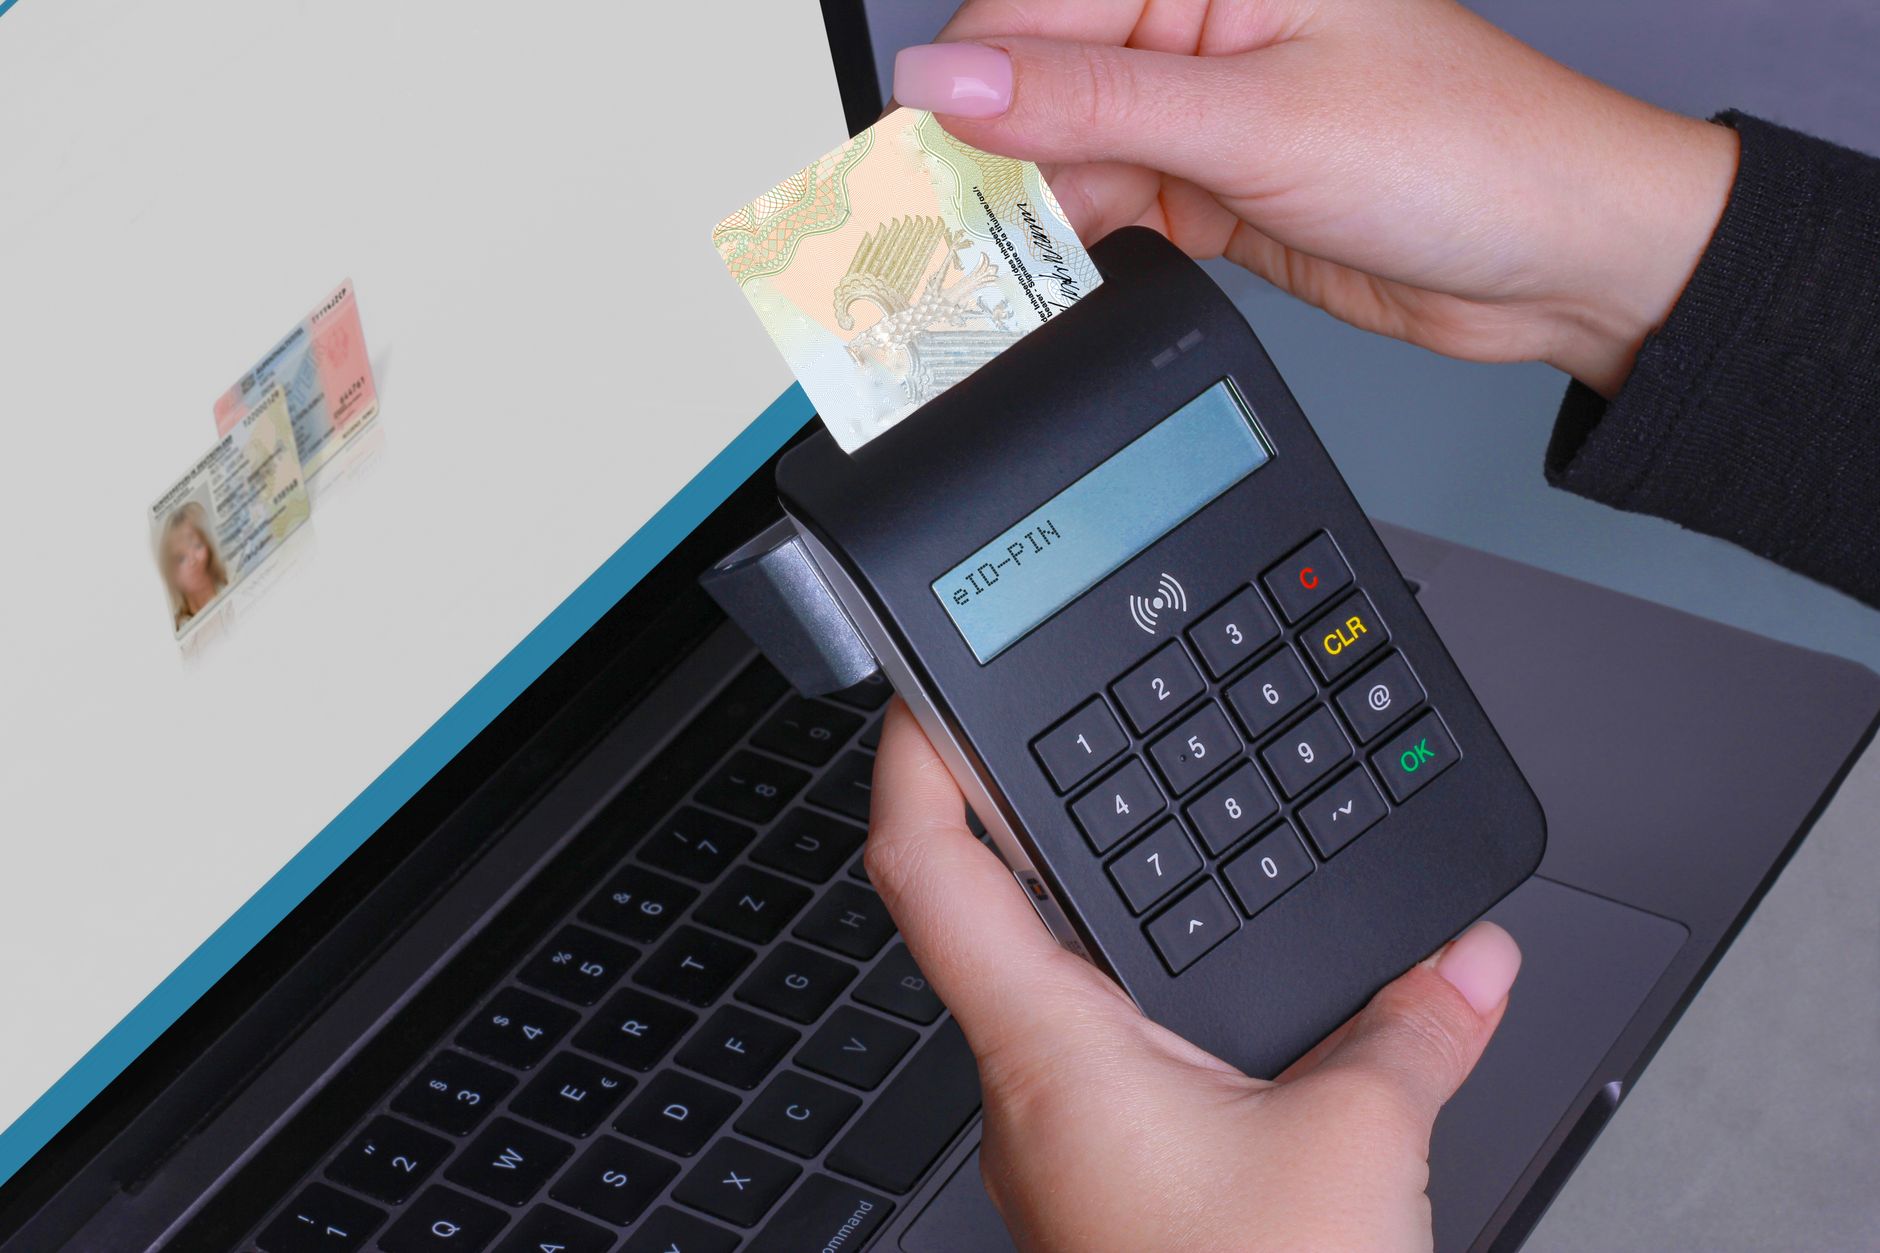
Stock photo by REINER SCT via Pexels, illustrating user access provisioning identity (temporary placeholder pending custom hero design).

SOC 2 CC6.2: Registers, Authorizes, and Administers User Access

SOC 2 CC6.2 is the credential lifecycle criterion in the Trust Services Criteria: it requires an organization to register and authorize new users...
Stock photo by Christina Morillo via Pexels, illustrating software change management devops (temporary placeholder pending custom hero design).

SOC 2 CC8.1: Authorizes, Designs, Tests, Approves, and Implements Changes

SOC 2 CC8.1 is the change management criterion: the single criterion in the CC8 series, covering how changes to infrastructure, data, software, and...
Stock photo by Tima Miroshnichenko via Pexels, illustrating team strategy meeting whiteboard planning office (temporary placeholder pending custom hero design).

What Is GRC in Cyber Security? Governance, Risk, and Compliance Explained

GRC in cyber security stands for governance, risk, and compliance: the discipline of directing a security program (governance), identifying and...
Stock photo by cottonbro studio via Pexels, illustrating reviewing contract documents office desk pen (temporary placeholder pending custom hero design).

Vendor Risk Assessment: How to Assess Vendors Without Drowning in Questionnaires

A vendor risk assessment is the structured evaluation of a vendor's security and compliance posture, scaled to the access and data that vendor holds....
Stock photo by panumas nikhomkhai via Pexels, illustrating data center network servers blue (temporary placeholder pending custom hero design).

What Is Security Architecture? A Practitioner's Guide

Security architecture is the practice of understanding a system component by component and connection by connection. In practice it comes down to two...
Stock photo by ThisIsEngineering via Pexels, illustrating drawing technical diagram computer screen (temporary placeholder pending custom hero design).

How to Create a Security Architecture Diagram (With a Worked Example)

A security architecture diagram is a boxes-and-arrows drawing of a system: boxes for the key components, arrows for the data flows or network flows...