Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

Filter by Tag

Canadian cybersecurity and compliance statistics 2026

Canadian Cybersecurity & Compliance Statistics 2026

The bottom line for 2026: Canadian data breach costs rose 10.4% to CA$6.98 million even as the global average fell. Canada is the outlier, and the...
ISO 42001 Cost in 2026: The 4 Factors

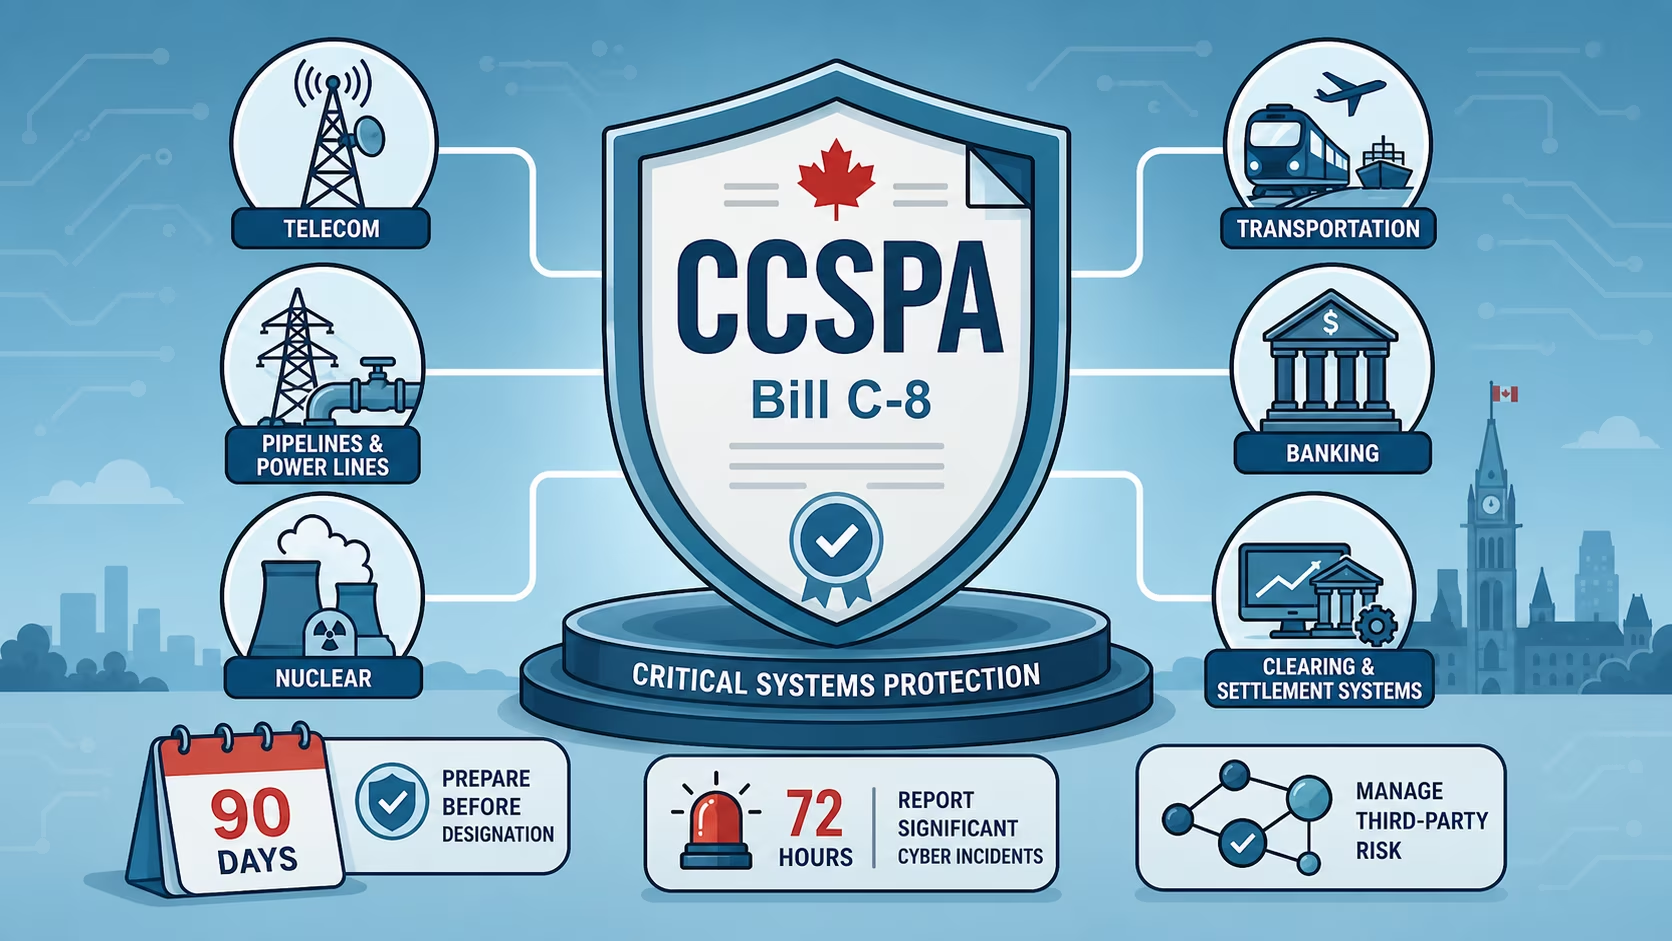
Bill C-8 Is Law: What Canada's Critical Cyber Systems Protection Act Requires, and Who It Reaches

Bill C-8 is now law. Its centrepiece, the Critical Cyber Systems Protection Act (CCSPA), places mandatory security obligations on operators in six...
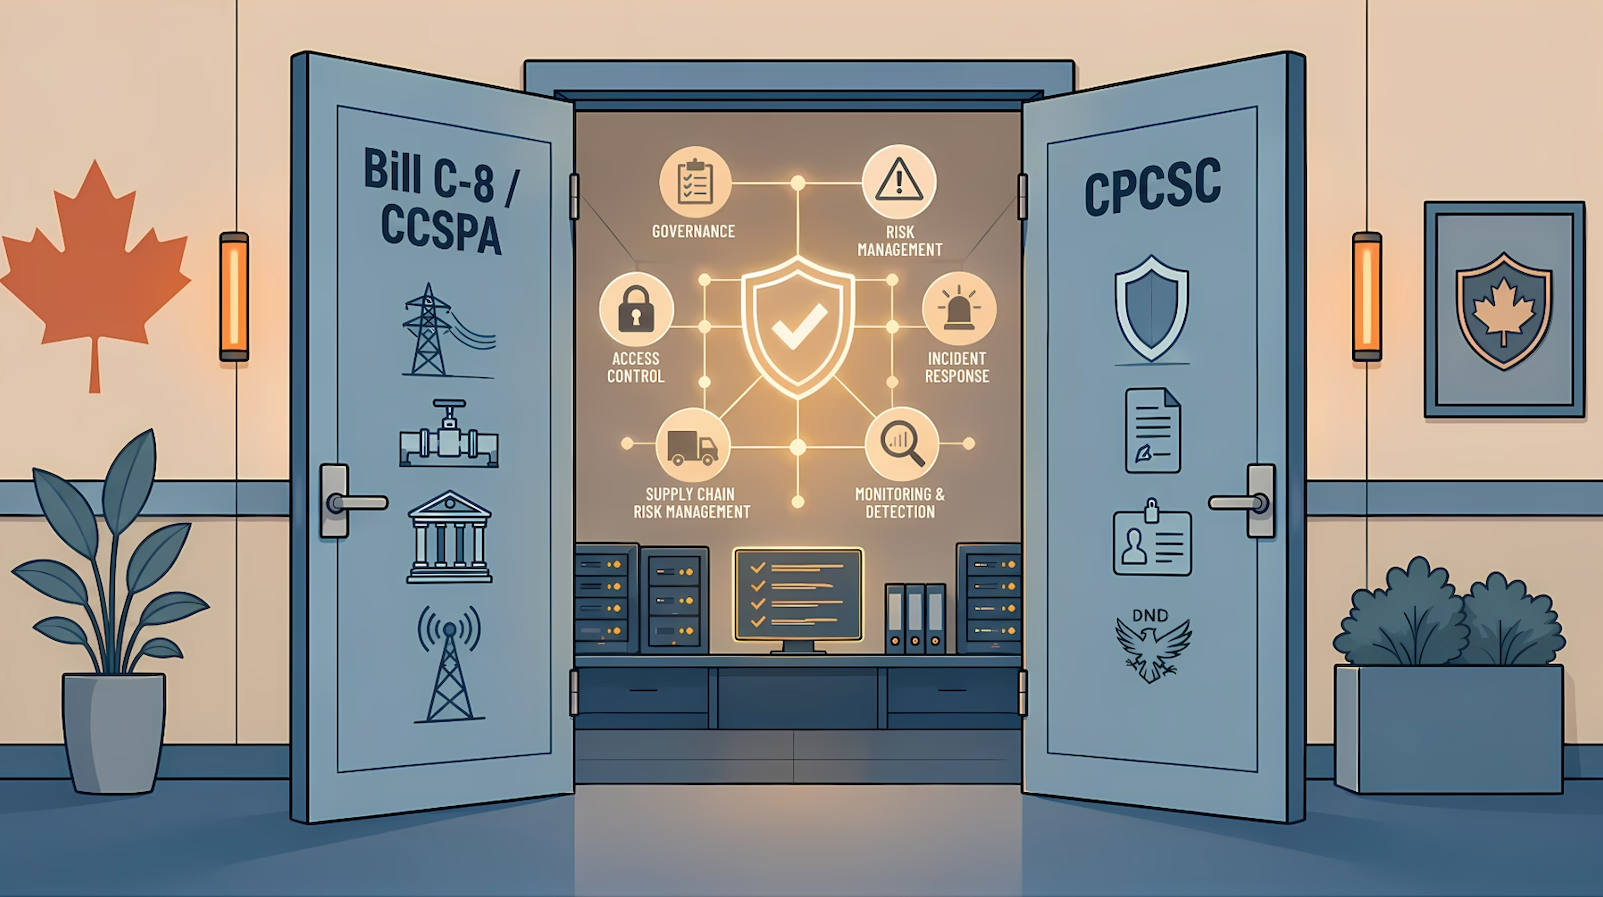
Two open doors labeled “Bill C-8 / CCSPA” and “CPCSC” lead into the same glowing cybersecurity control room, illustrating how Canada’s regulatory and procurement mandates both require a documented security program.

Bill C-8 vs CPCSC: Canada Now Has Two Cyber Mandates. Which One Reaches You?

Canada now runs two federal cybersecurity mandates that reach companies through entirely different doors. Bill C-8's Critical Cyber Systems...
Flat vector illustration showing Bill C-8 supplier requirements, with a secured laptop and servers connected to banks, telecom towers, energy infrastructure, rail, and aviation, alongside legal documents, a gavel, a 90-day program window, and a deadline clock.

Bill C-8 Supplier Requirements: Selling to Banks, Telecoms, and Energy After the CCSPA

Bill C-8 is law, and its centrepiece, the Critical Cyber Systems Protection Act (CCSPA), places no direct obligations on the software and technology...
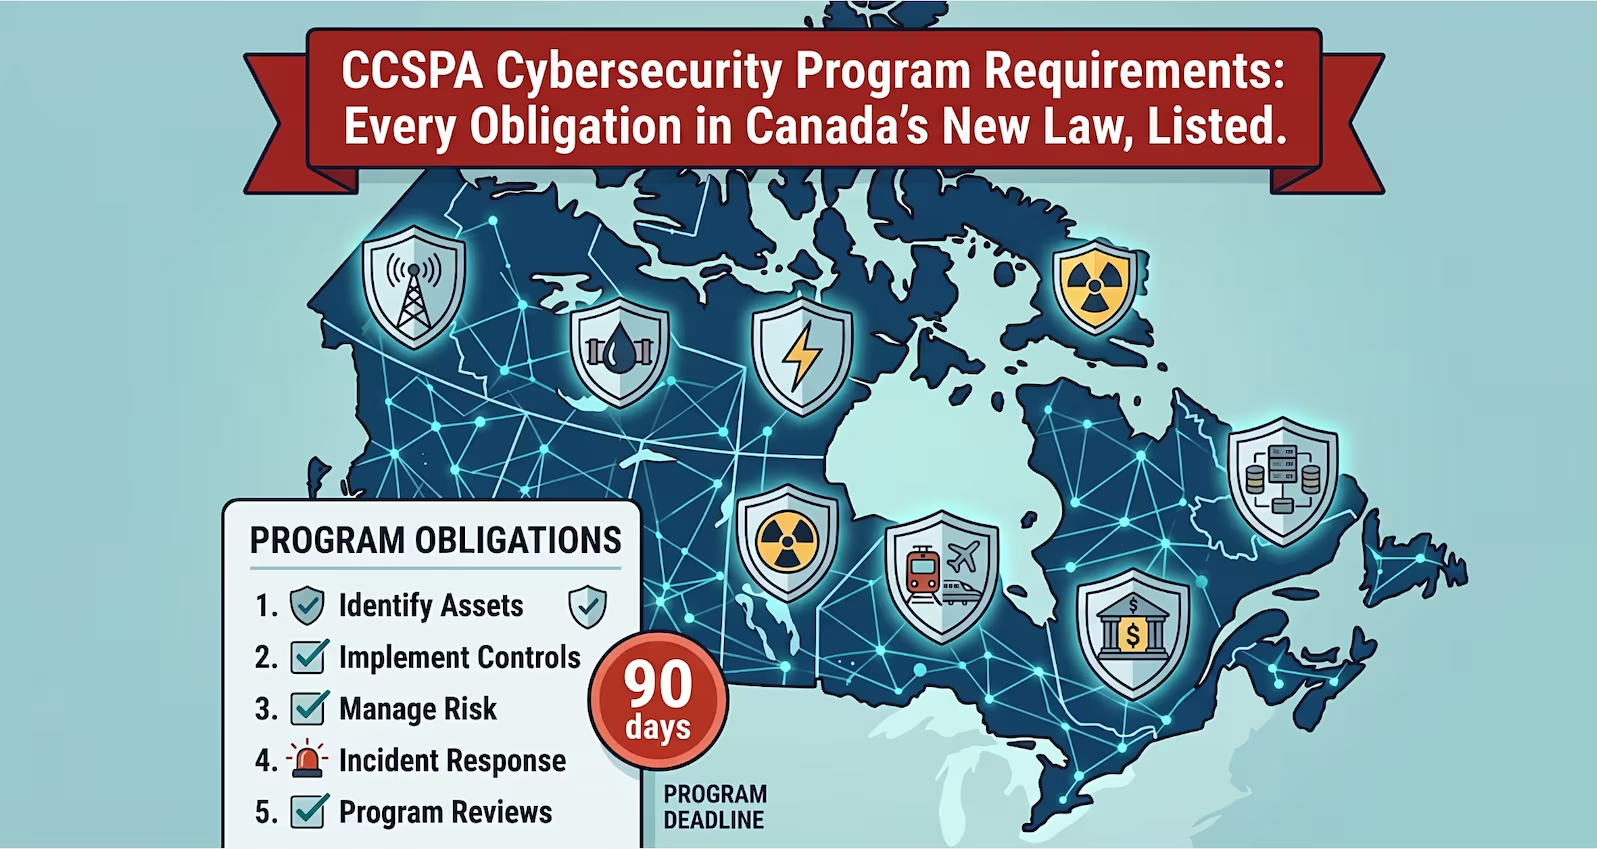
Infographic titled “CCSPA Cybersecurity Program Requirements.” A map of Canada shows networked shields over critical sectors. Features a 5-step checklist of obligations (Identify Assets to Program Reviews) and a red “90 days” program deadline badge.

CCSPA Cybersecurity Program Requirements: Every Obligation in Canada's New Law, Listed

A CCSPA cyber security program is a documented set of reasonable steps to identify and manage cyber security risk, protect critical cyber systems,...
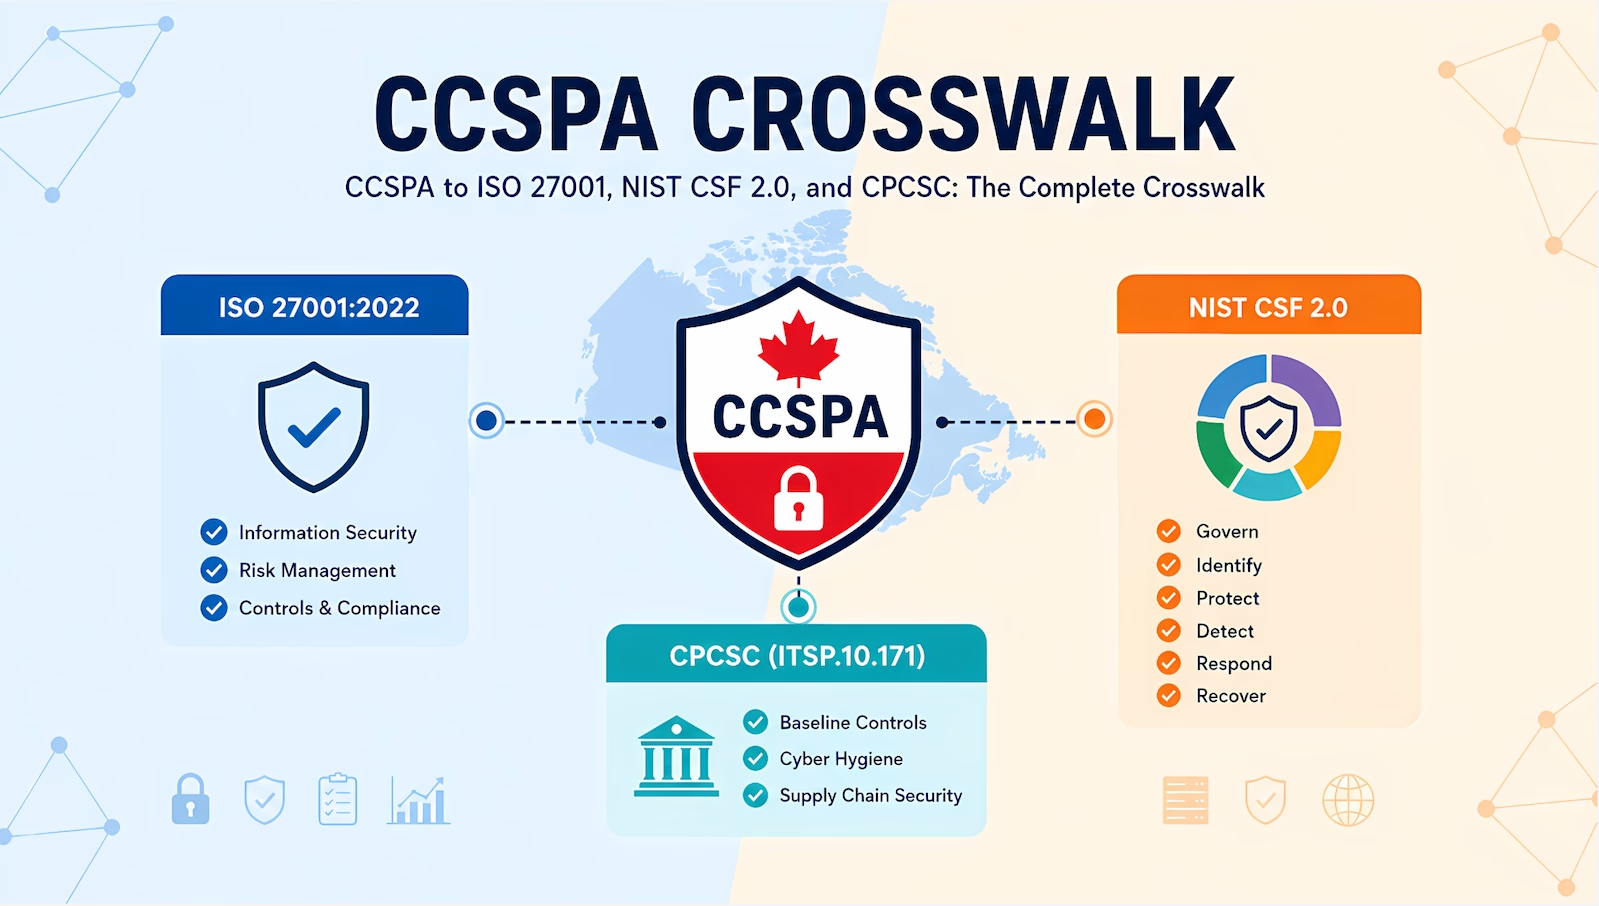
CCSPA crosswalk infographic showing a central Canadian shield connected to ISO 27001:2022, NIST CSF 2.0, and CPCSC ITSP.10.171, with compliance controls, cybersecurity icons, and a map of Canada in a clean blue, teal, orange, and red design.

Mapping the CCSPA to ISO 27001, NIST CSF 2.0, and CPCSC: The Complete Crosswalk

This crosswalk maps the seven obligation areas of the Critical Cyber Systems Protection Act (CCSPA), enacted June 16, 2026 as Part 2 of Bill C-8,...
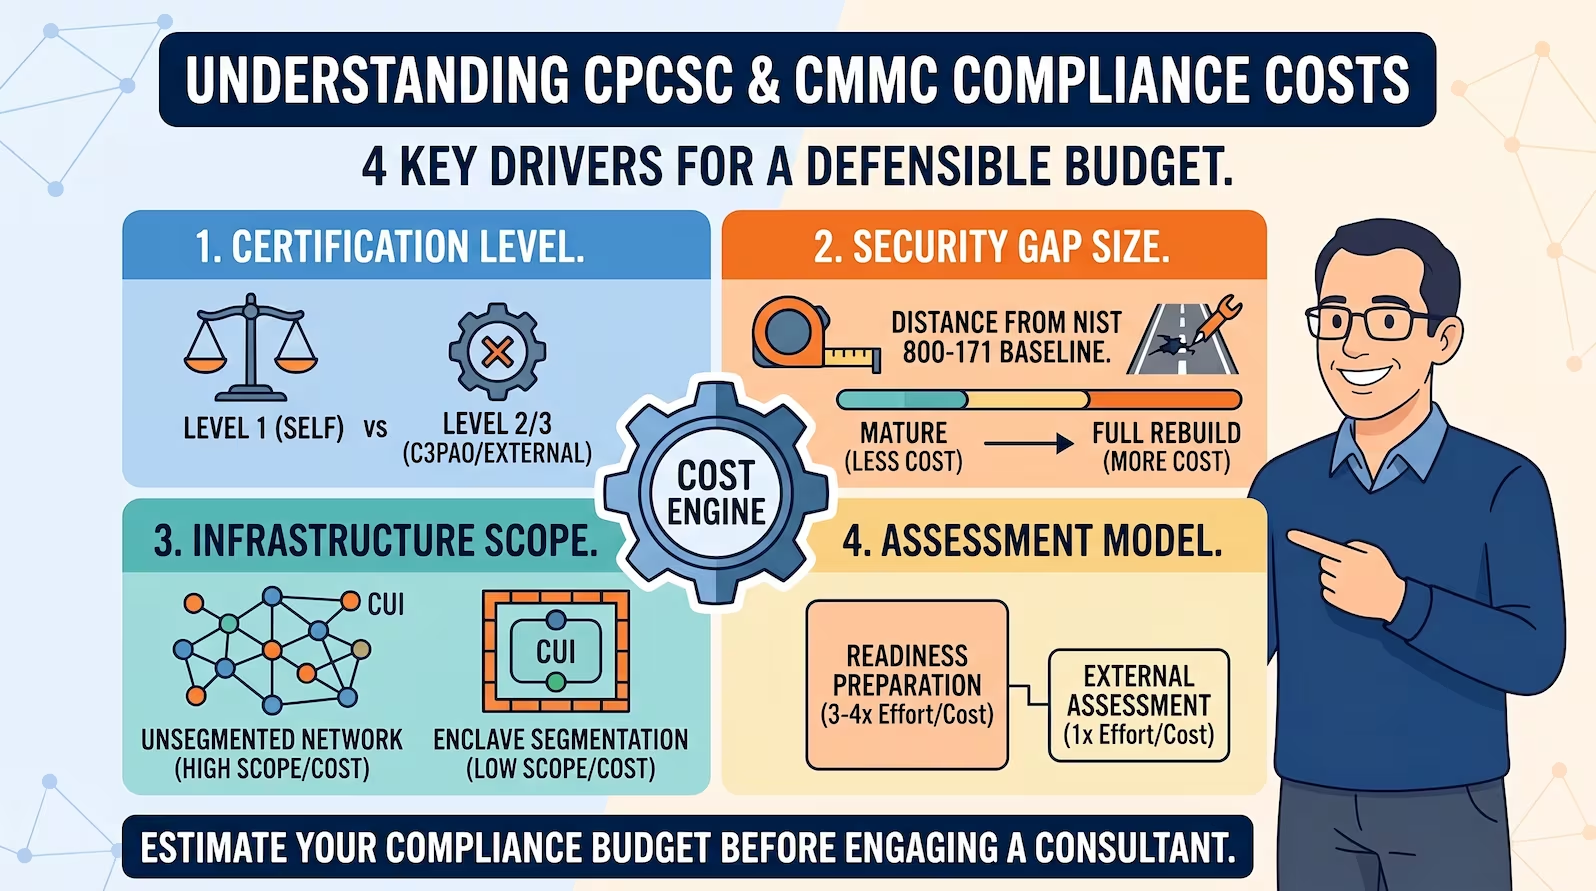
Infographic outlining 4 key drivers for CPCSC & CMMC compliance budgets: 1. Certification Level (Level 1 vs Level 2/3); 2. Security Gap Size (NIST 800-171 gap); 3. Infrastructure Scope (enclave vs unsegmented); 4. Assessment Model (prep vs assessment). Features a 'Cost Engine' gear.

CPCSC & CMMC Cost in 2026: The 4 Factors

There is no single price tag for CPCSC or CMMC compliance, and any consultancy that quotes one before scoping your environment is guessing. The real...
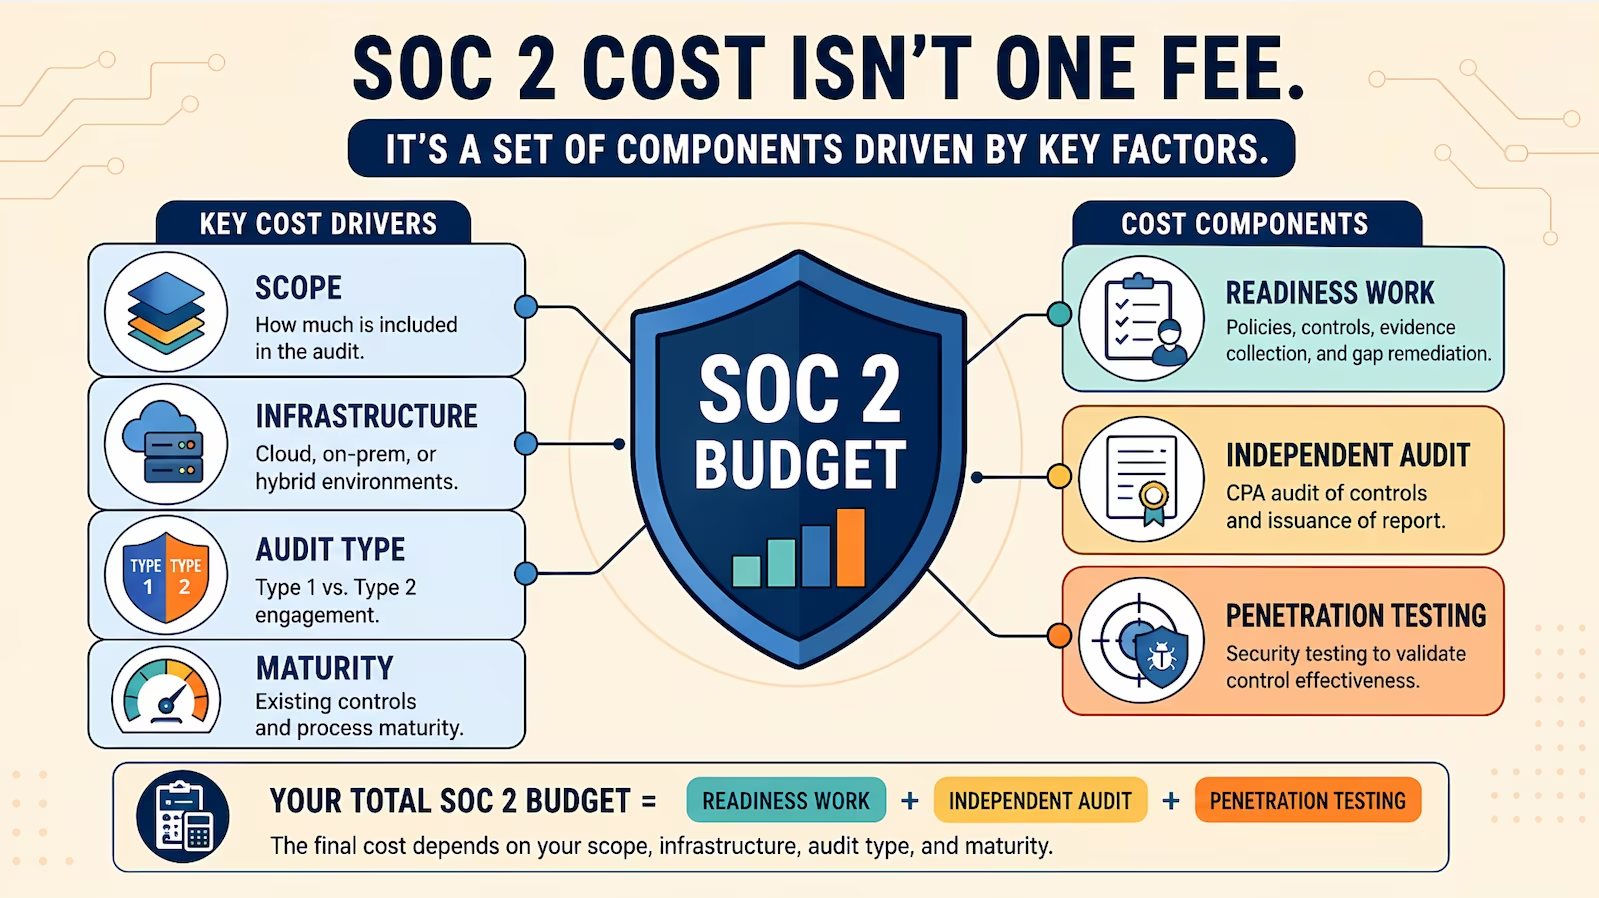
Flat vector infographic showing a SOC 2 budget split into readiness work, an independent audit, and penetration testing, with total cost driven by scope, infrastructure, Type 1 or Type 2 audit, and organizational maturity.

What SOC 2 Costs in 2026: The 4 Factors

TL;DR: All-in SOC 2 cost for a growth-stage SaaS company typically runs between US$20,000 and US$100,000 in the first year, with most SMBs in the...
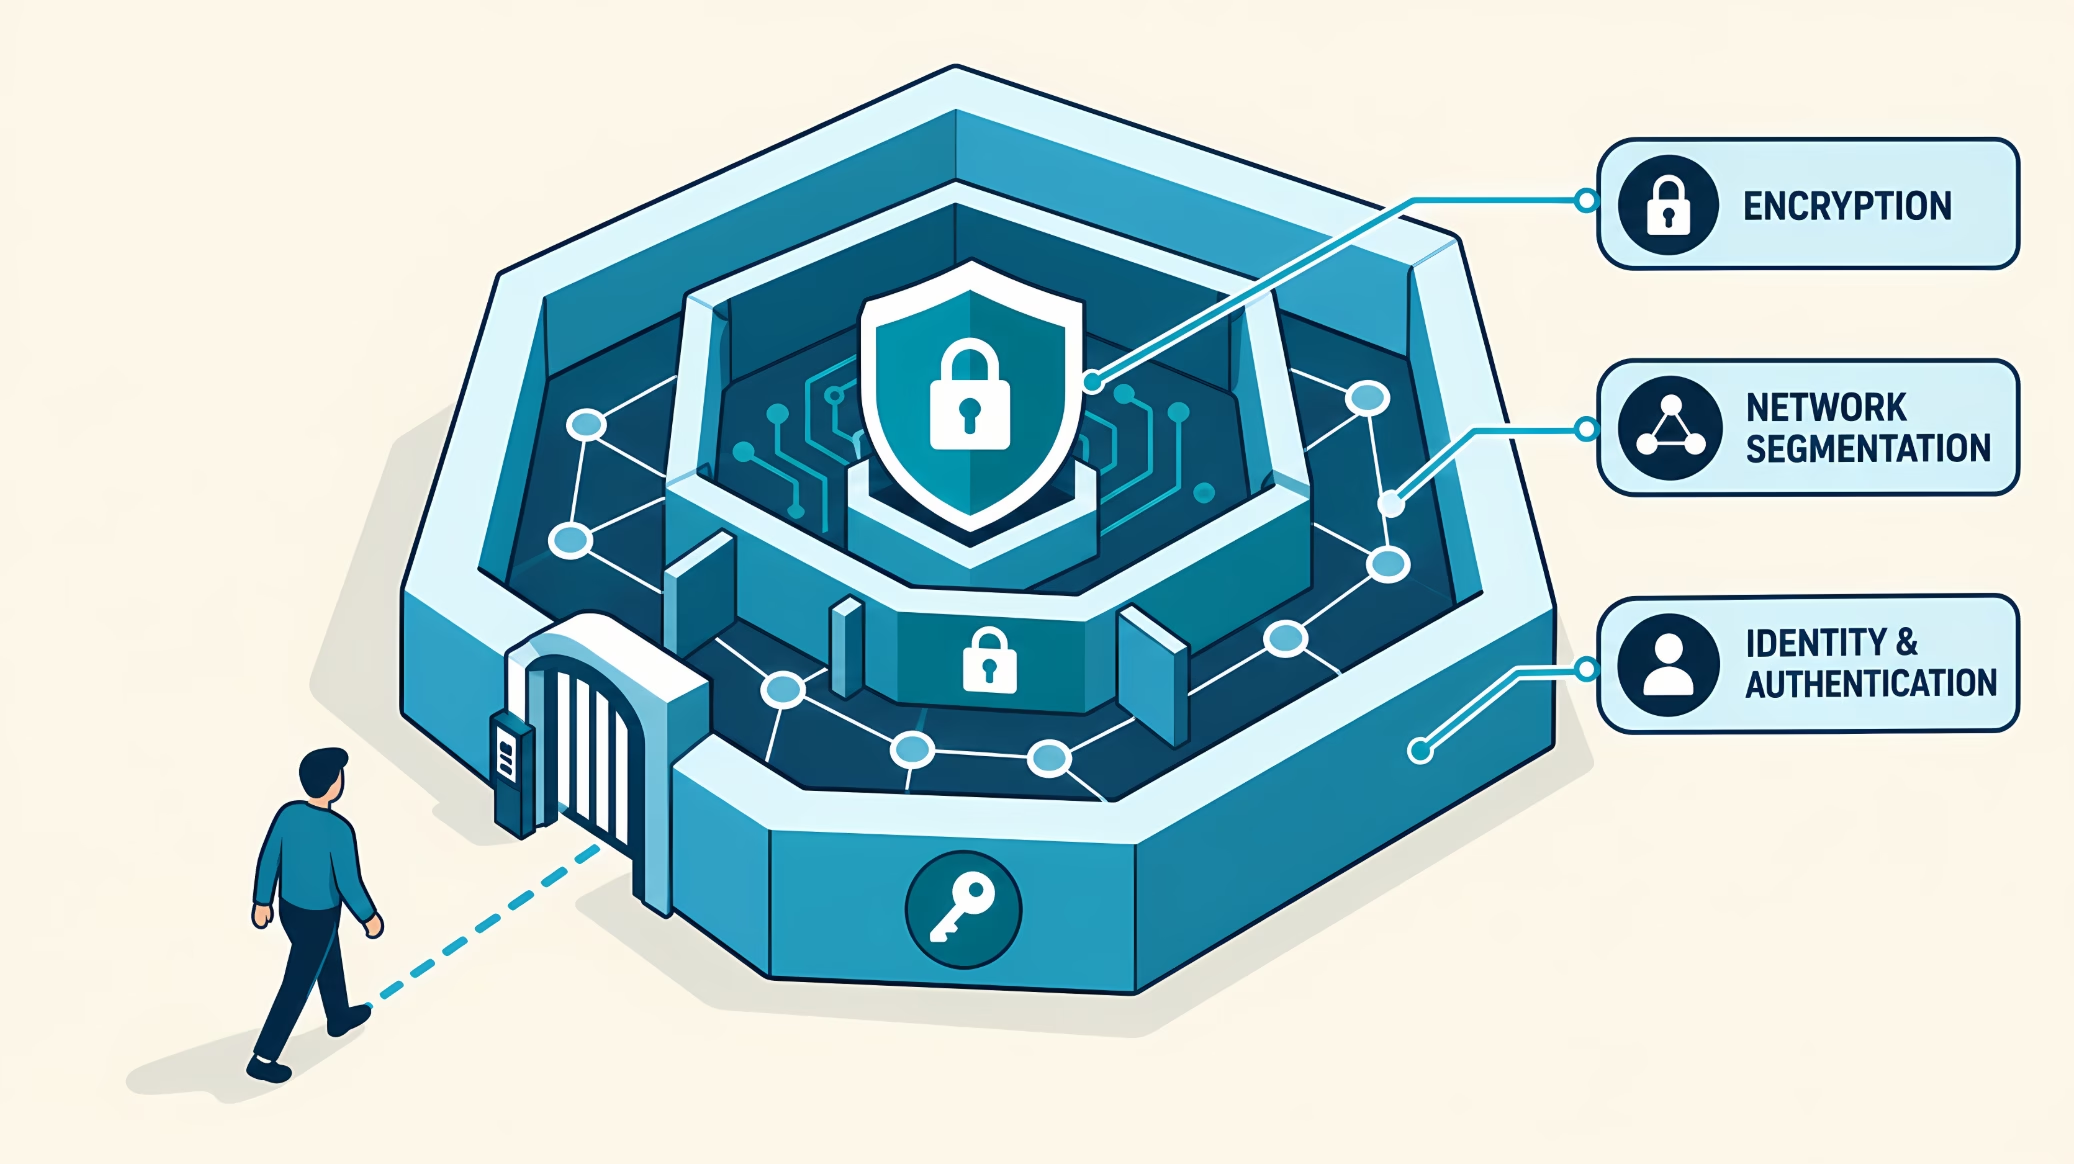
Isometric vector illustration of layered cybersecurity defenses around a central shield, showing encryption, network segmentation, identity and authentication, and a user approaching a controlled access gate.

SOC 2 CC6.1: Logical Access Security Software, Infrastructure, and Architectures

SOC 2 CC6.1 is the foundational access control criterion in the Trust Services Criteria: it requires an organization to implement logical access...
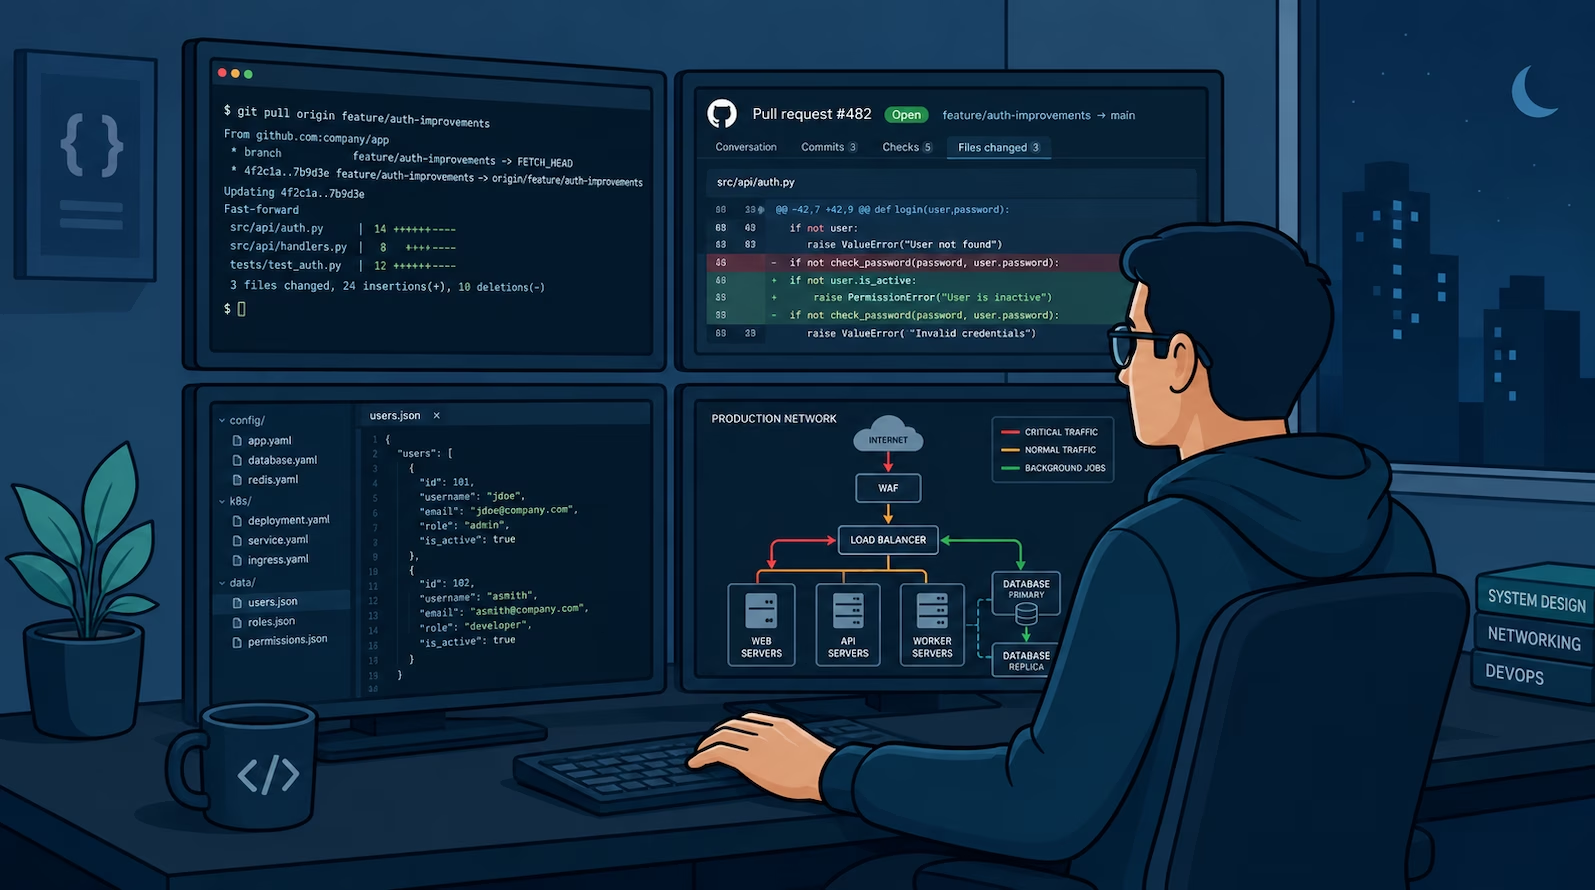
An illustration of a software engineer working at night with a four-monitor setup. The screens display a Git terminal, a GitHub pull request code diff, a JSON configuration file, and a production network architecture diagram.

GRC Engineering: Building Compliance Into Infrastructure

At Truvo, GRC engineering is how we run compliance: we treat governance, risk, and compliance as an engineering discipline rather than an...
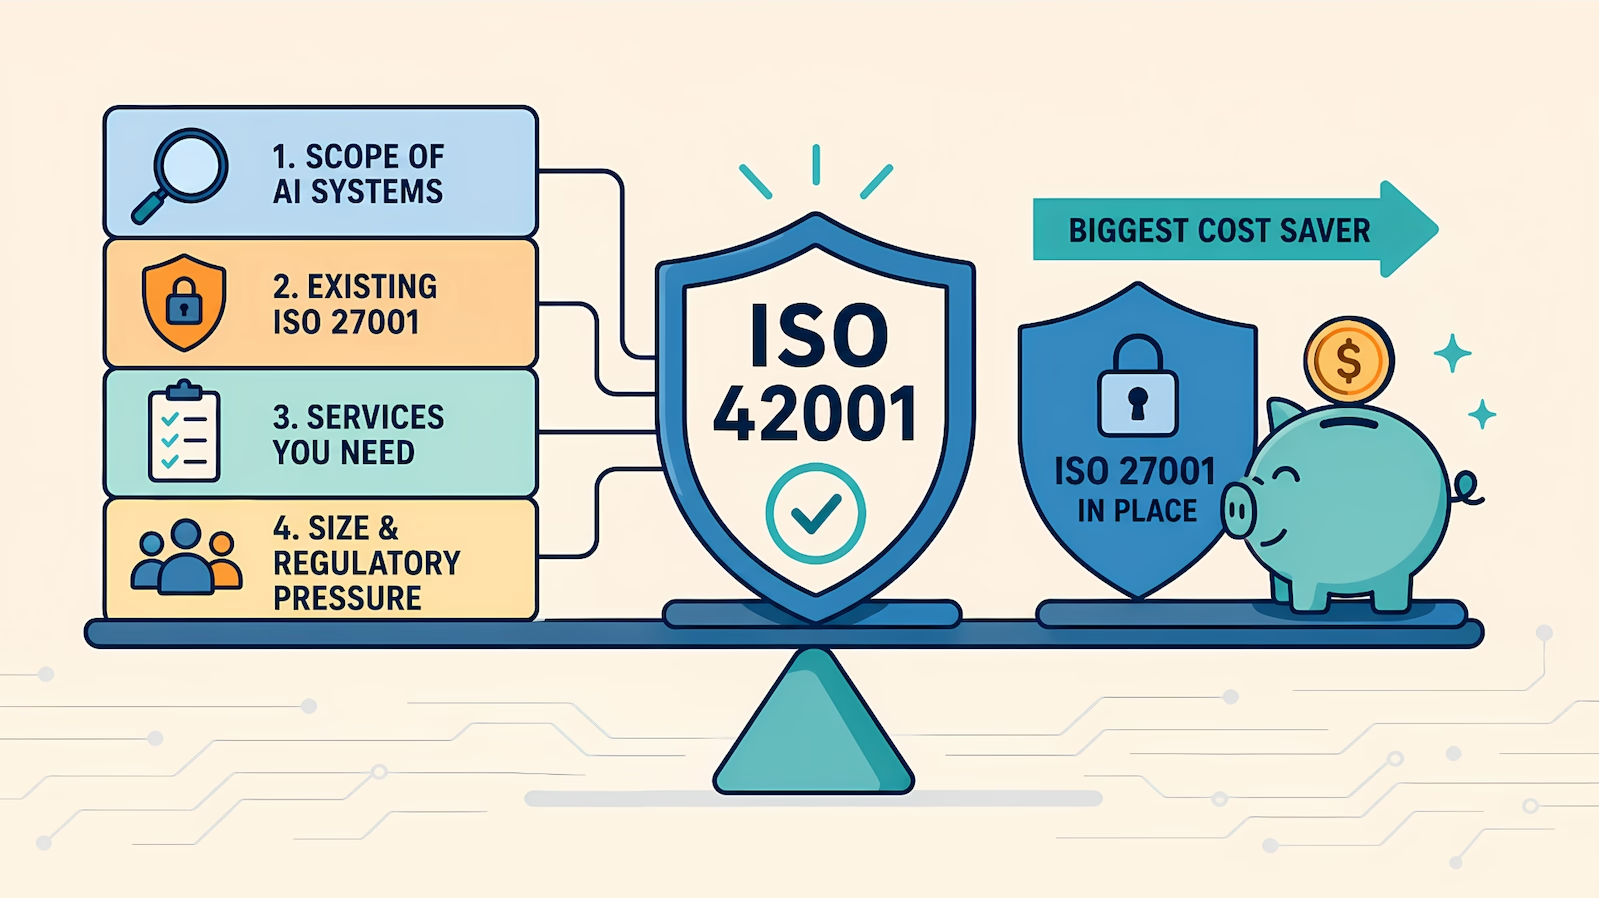
ISO 42001 Cost in 2026: The 4 Factors

ISO 42001 Cost in 2026: The 4 Factors

ISO 42001 implementation and certification for small organization can land anywhere between roughly US$20,000 and US$55,000 for a first...
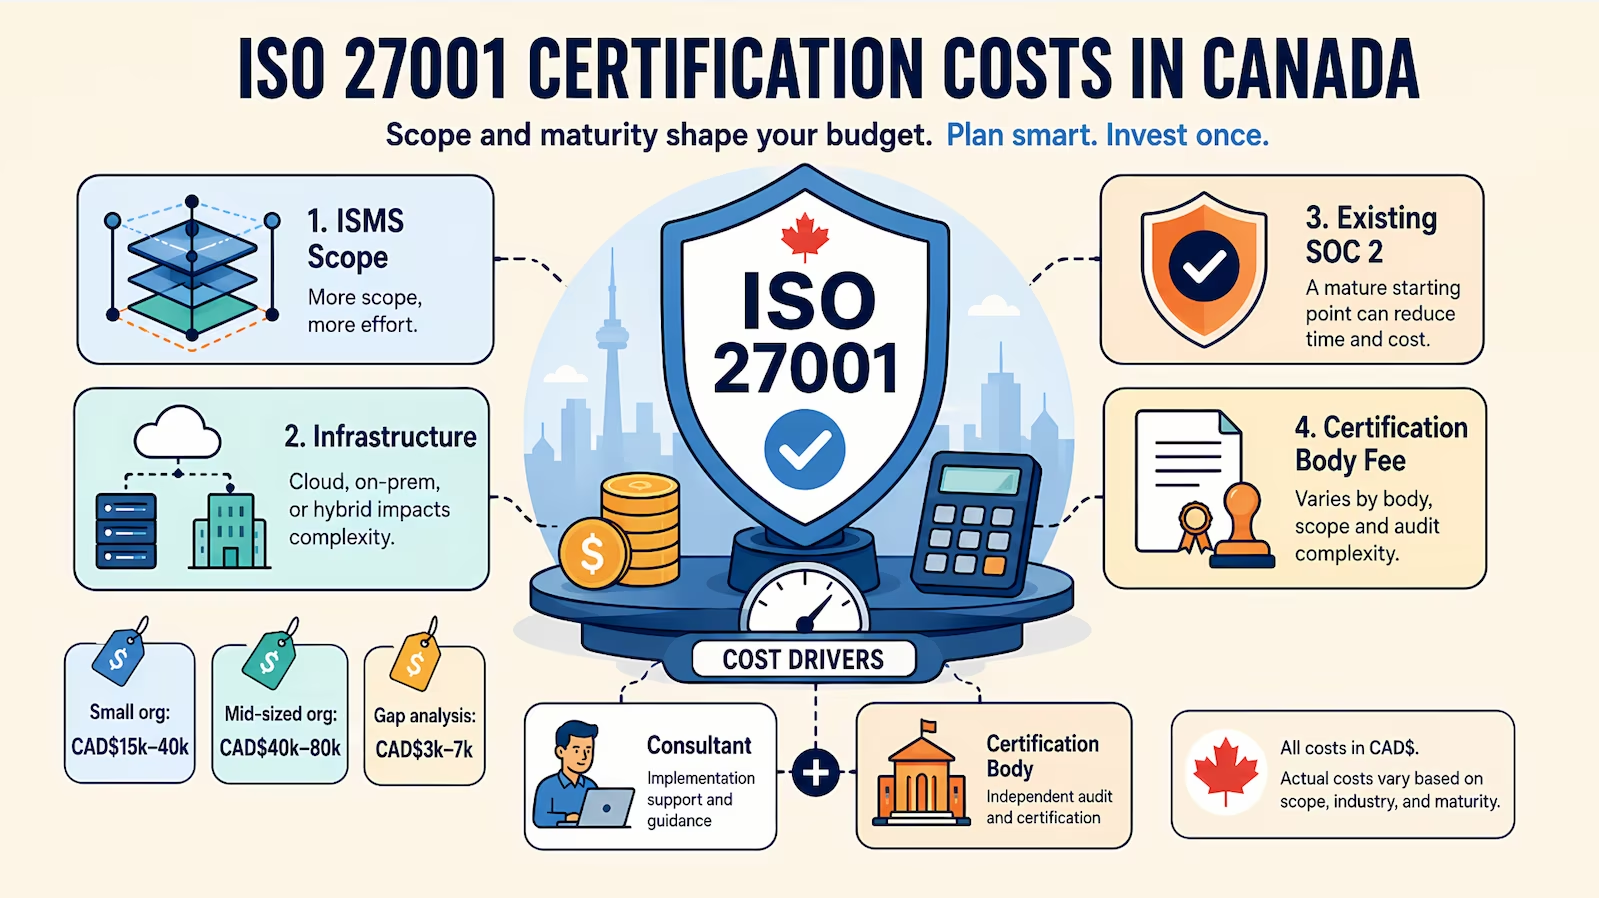
ISO 27001 cost in 2026 for Canadian companies

ISO 27001 Cost in 2026: The 4 Factors That Set It

TL;DR

For a Canadian company, ISO 27001 typically costs between CAD$15,000 and $40,000 for a small organization (under 50 employees) and CAD$40,000...
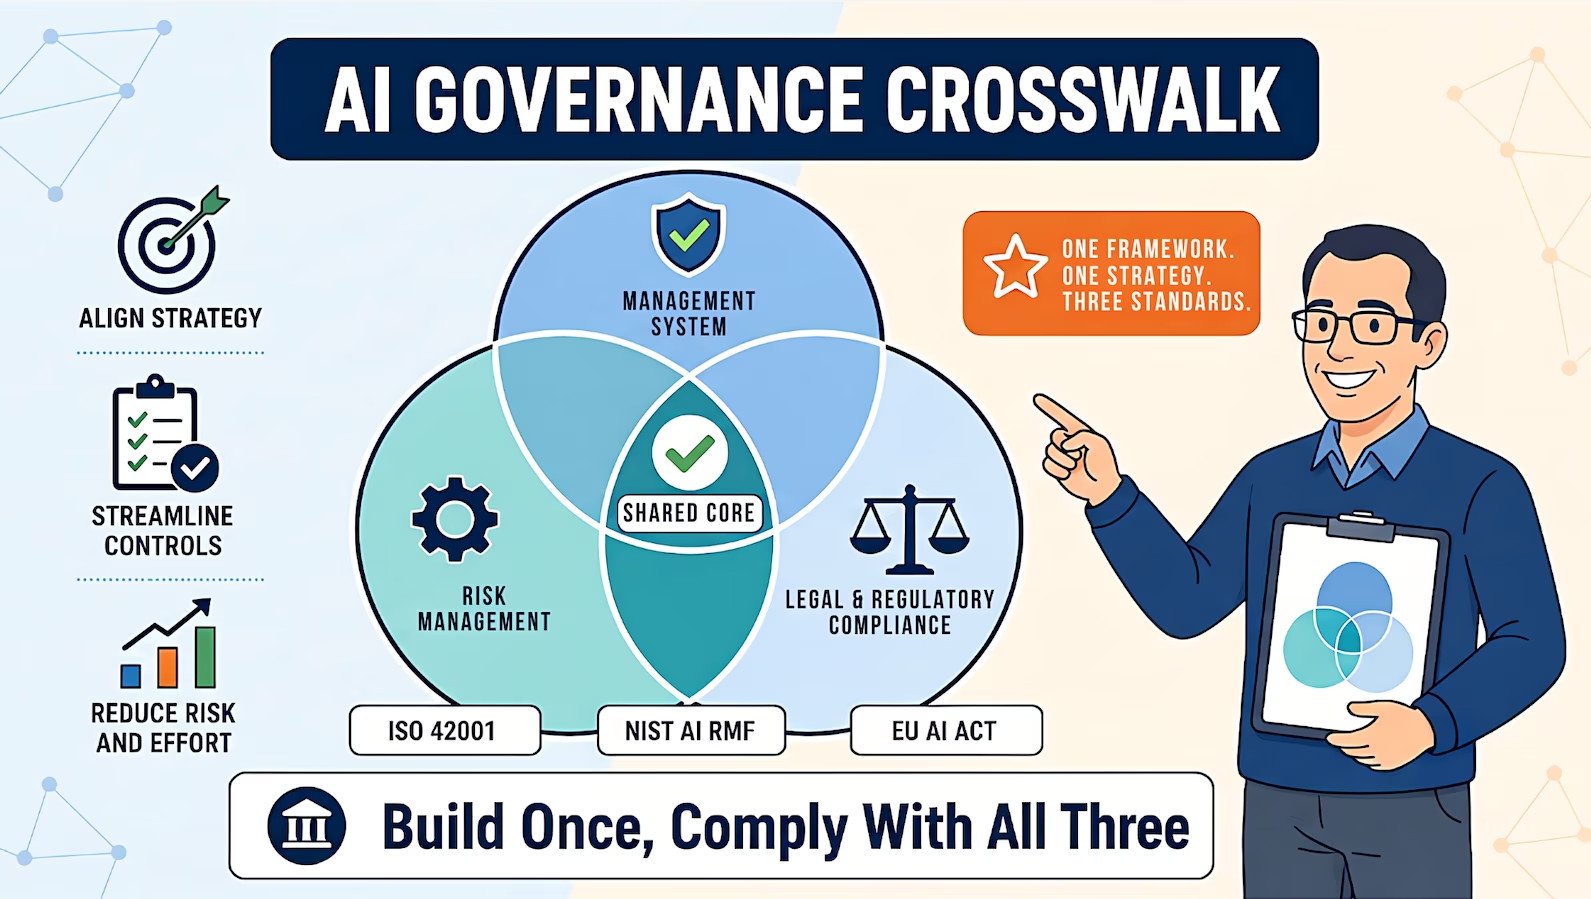
An animated infographic titled "AI Governance Crosswalk." A Venn diagram connects Risk Management (ISO 42001), Management System (NIST AI RMF), and Legal Compliance (EU AI ACT) to a central "Shared Core." A man points, and text at the bottom reads "Build Once, Comply With All Three."

ISO 42001, NIST AI RMF, and the EU AI Act: The Complete Control Crosswalk

ISO 42001, the NIST AI RMF, and the EU AI Act overlap on roughly two-thirds of their controls. Design one control set against that shared core and...
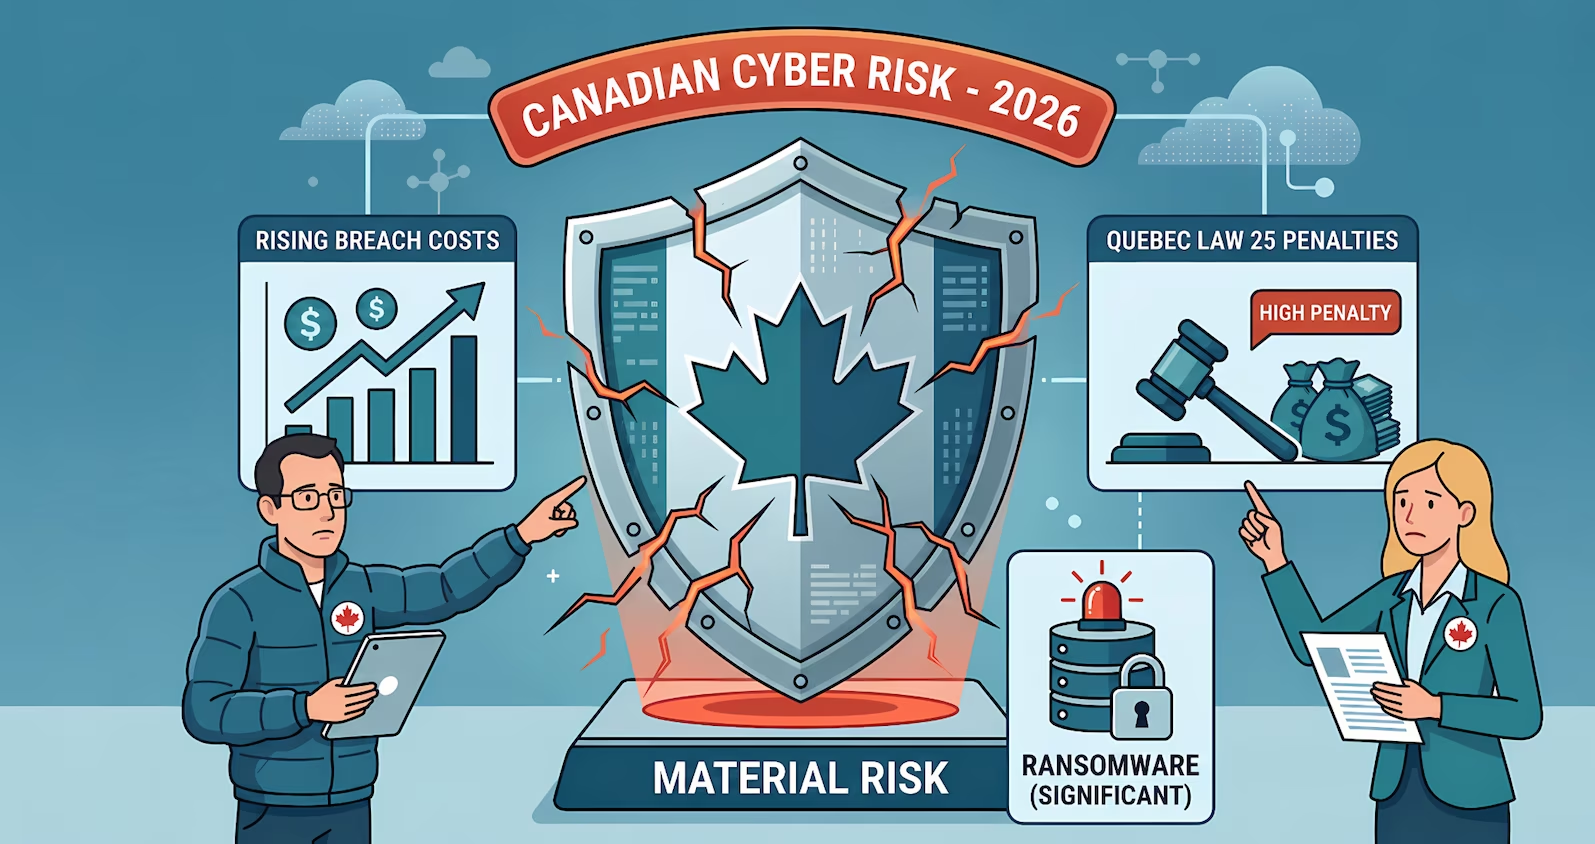
Infographic "Canadian Cyber Risk - 2026" with a central fractured maple leaf shield representing "Material Risk". Surrounding data panels cover "Rising Breach Costs", "Quebec Law 25 Penalties", and "Ransomware (Significant)". Analysts point to key threats.

Canadian Cybersecurity & Compliance Statistics 2026

The bottom line for 2026: Canadian data breach costs rose 10.4% to CA$6.98 million even as the global average fell. Canada is the outlier, and the...
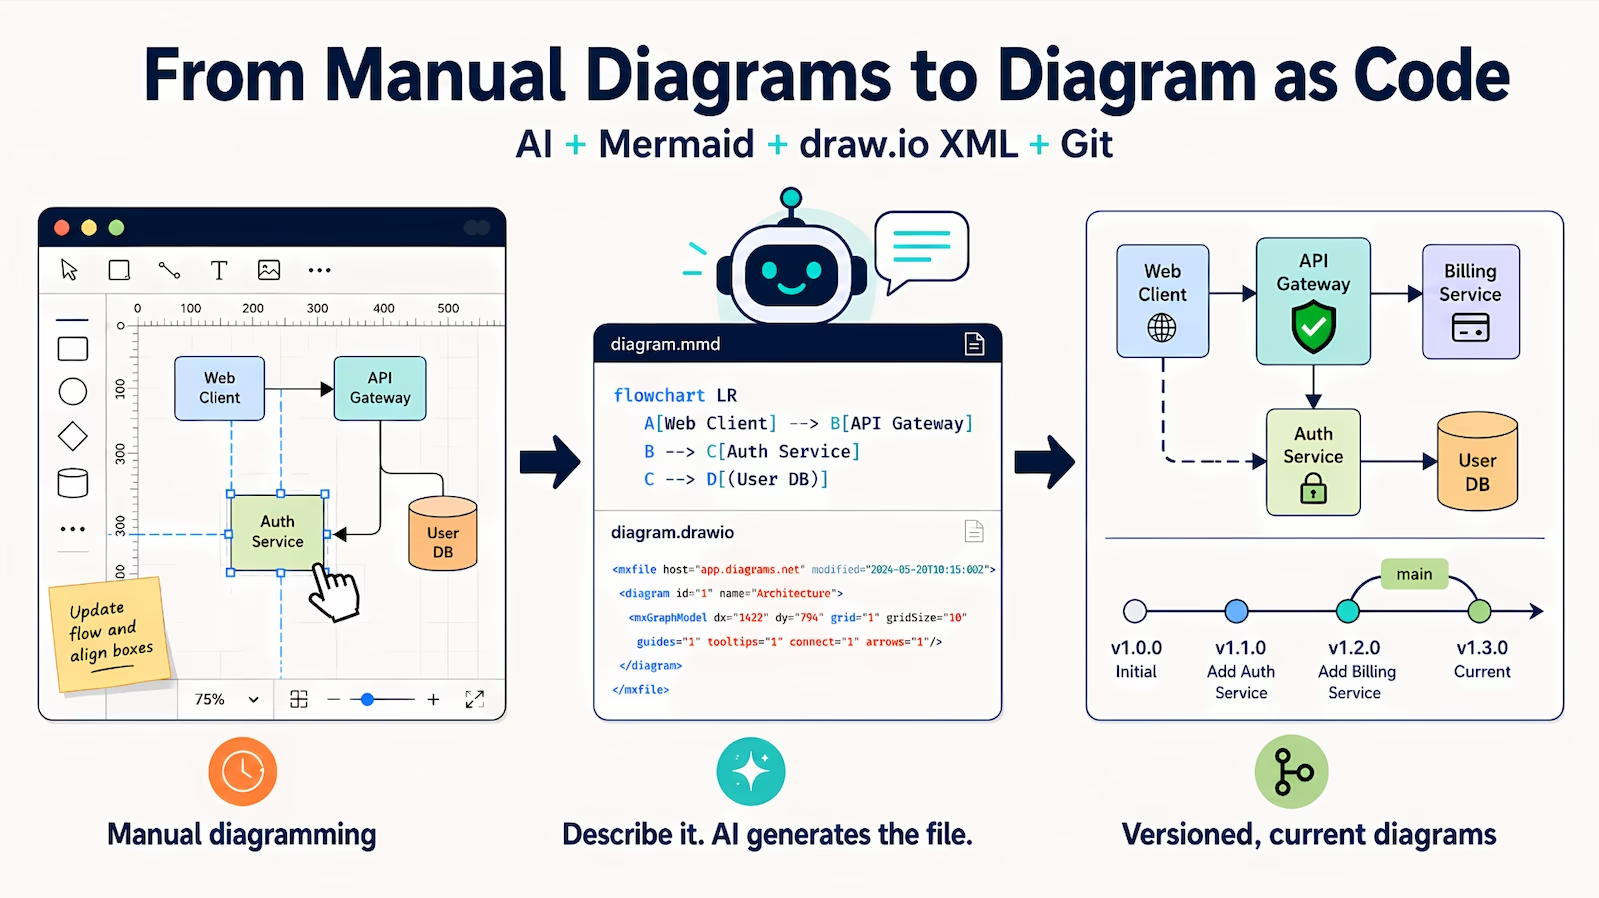
Diagram as Code With AI — Truvo blog hero

Diagram as Code: How To Replace Lucidchart With AI and Draw.io

As a cybersecurity consulting firm, one of the first things we do with any client is understand their architecture. That means drawing network...
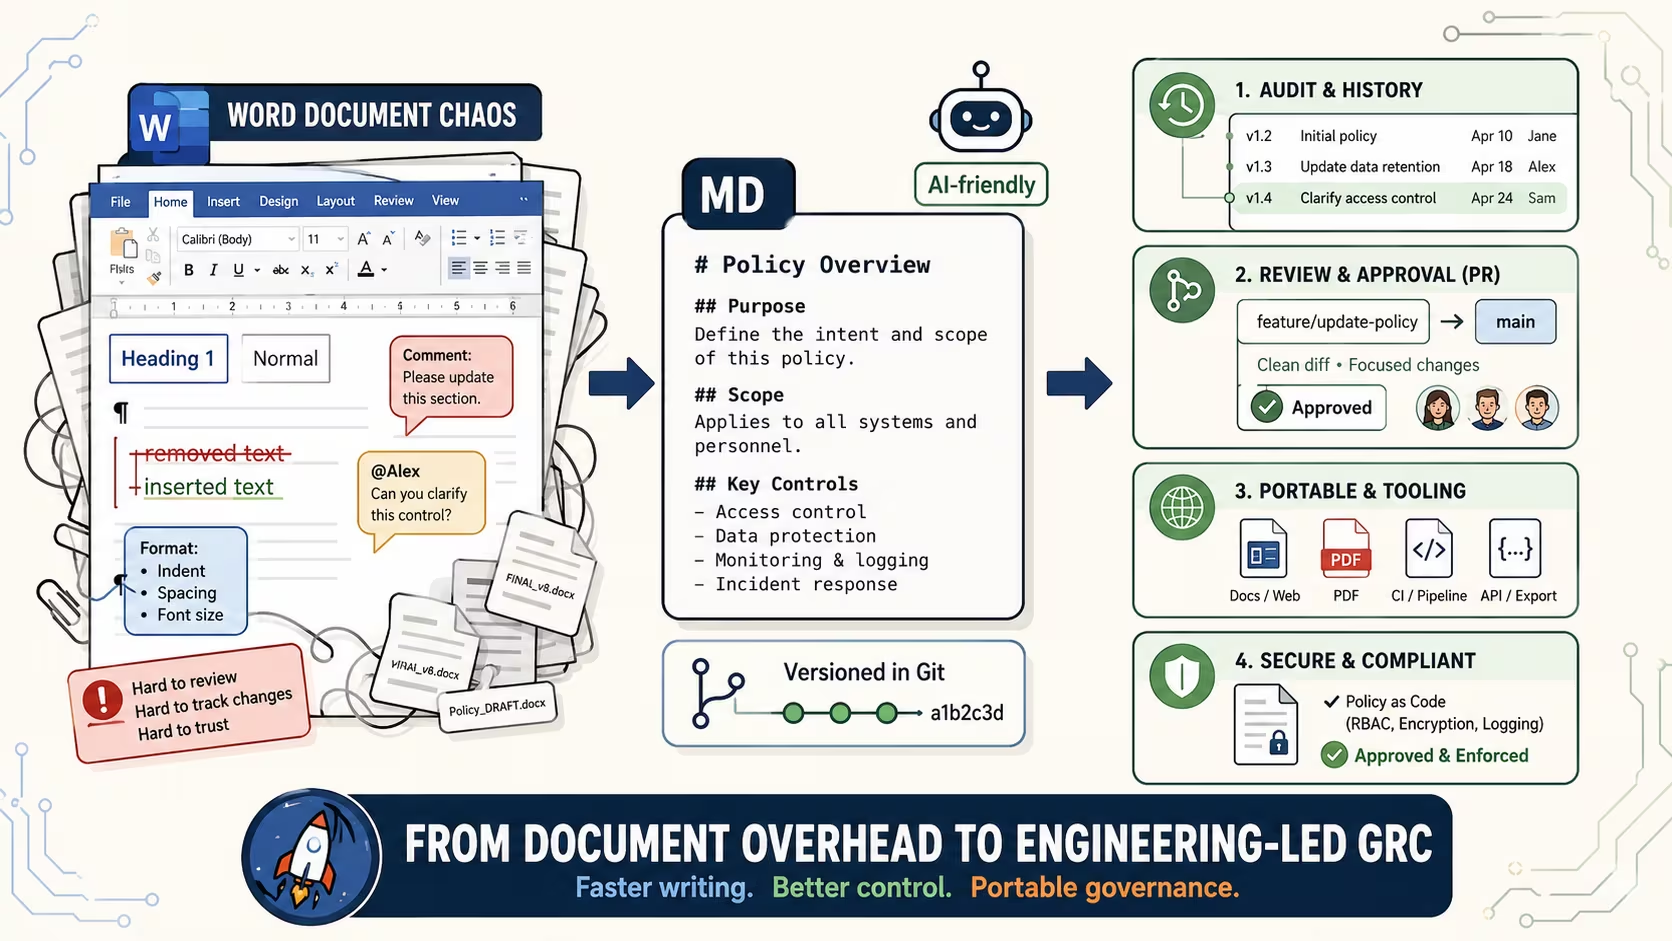
Down With .docx, Long Live .md — Truvo blog hero

Down With .docx, Long Live .md: Why We Switched to Markdown for Everything

In 2026, documentation needs to be easily readable by humans and AI. Plain text is too plain. You need headings, bold, lists, and tables to make a...
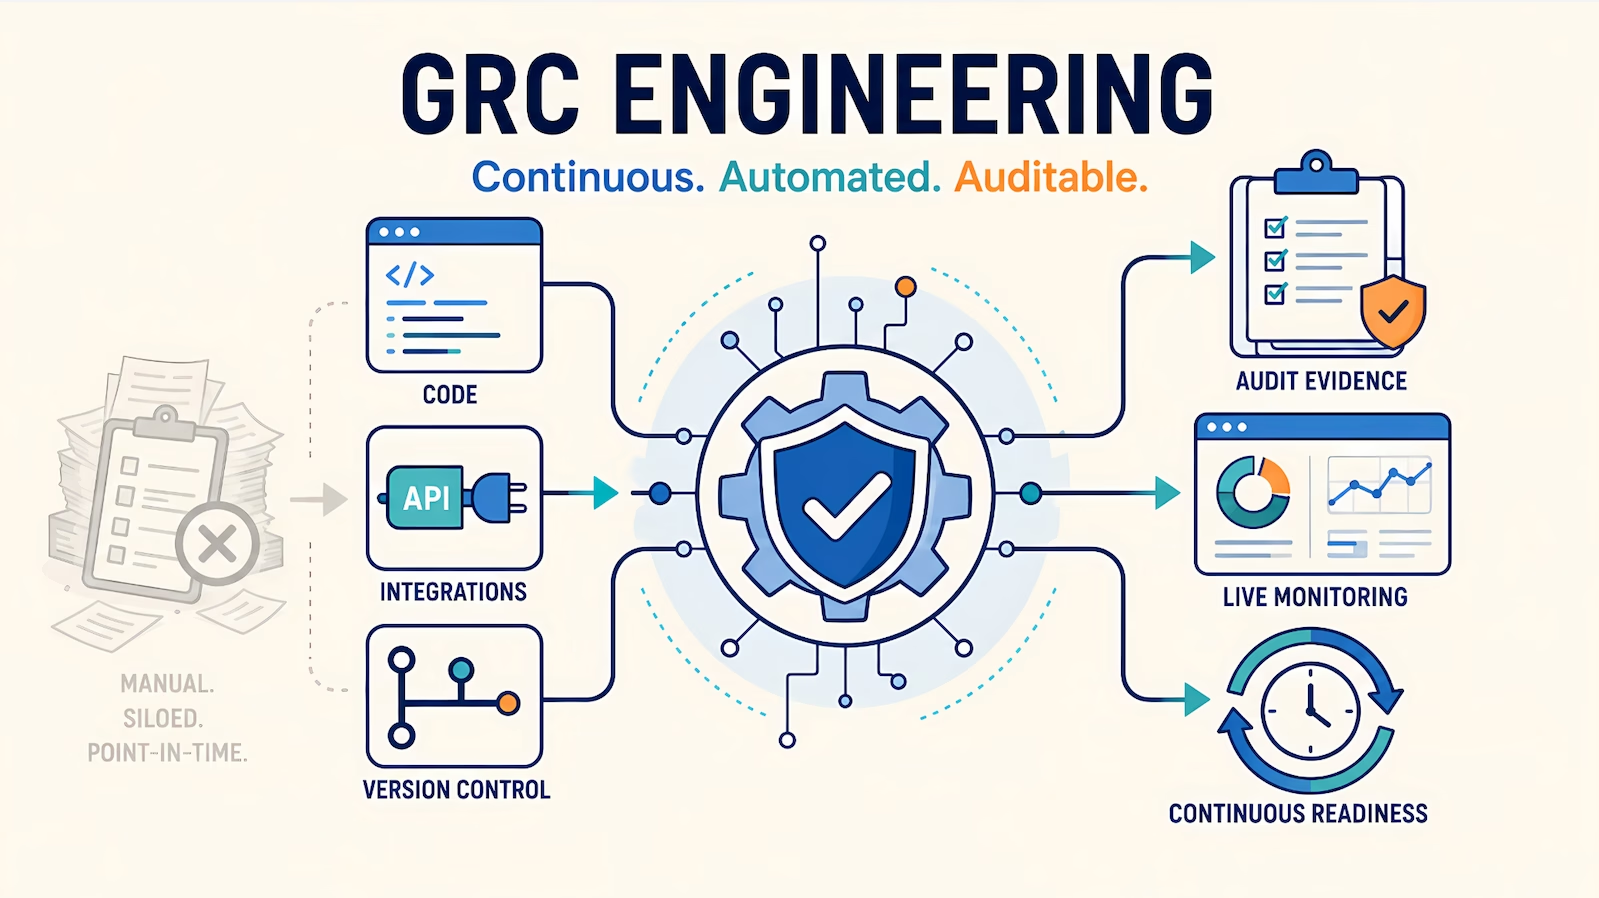
Flat vector infographic showing GRC engineering transforming manual compliance into code-driven workflows using APIs and version control, producing automated monitoring, audit evidence, and continuous audit readiness.

What is GRC Engineering? A Plain-Language Definition

GRC engineering has been picking up momentum in the security community. It is in job postings, conference agendas, and strategy conversations at...
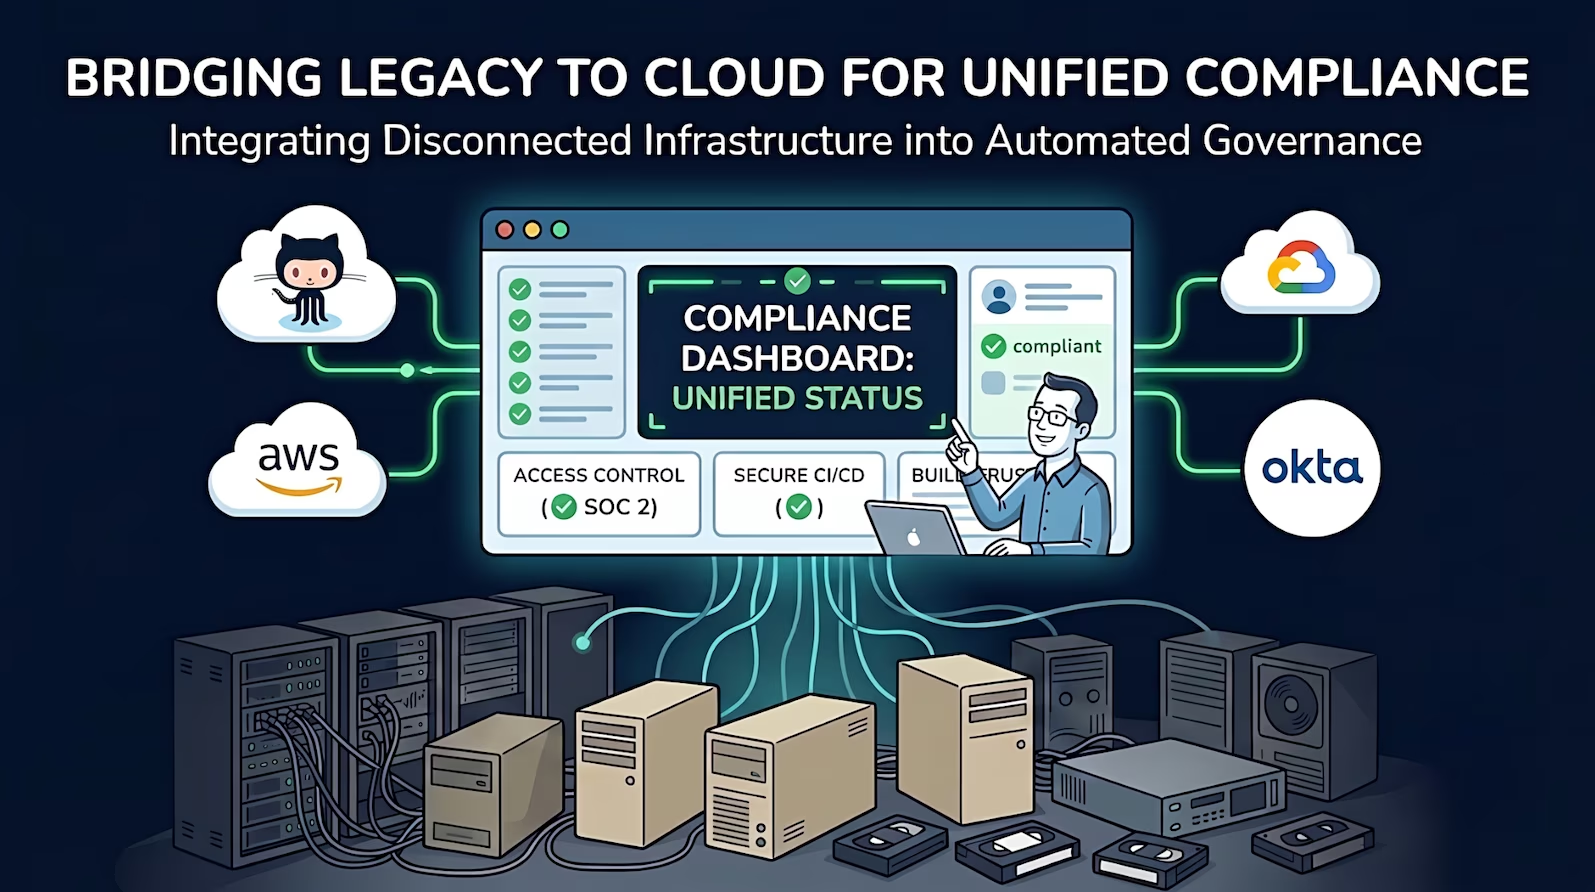
An infographic visualizing "BRIDGING LEGACY TO CLOUD FOR UNIFIED COMPLIANCE." Old server racks and a jumble of desktop computers are linked by wires to a glowing central screen labeled "COMPLIANCE DASHBOARD," which also connects to cloud service icons for GitHub, AWS, and Okta.

GRC Platform vs GRC Engineering: When You Need Both

We've seen all to often. organizations that have been running a GRC platform for six to twelve months: the dashboard is green, the audit prep feels...
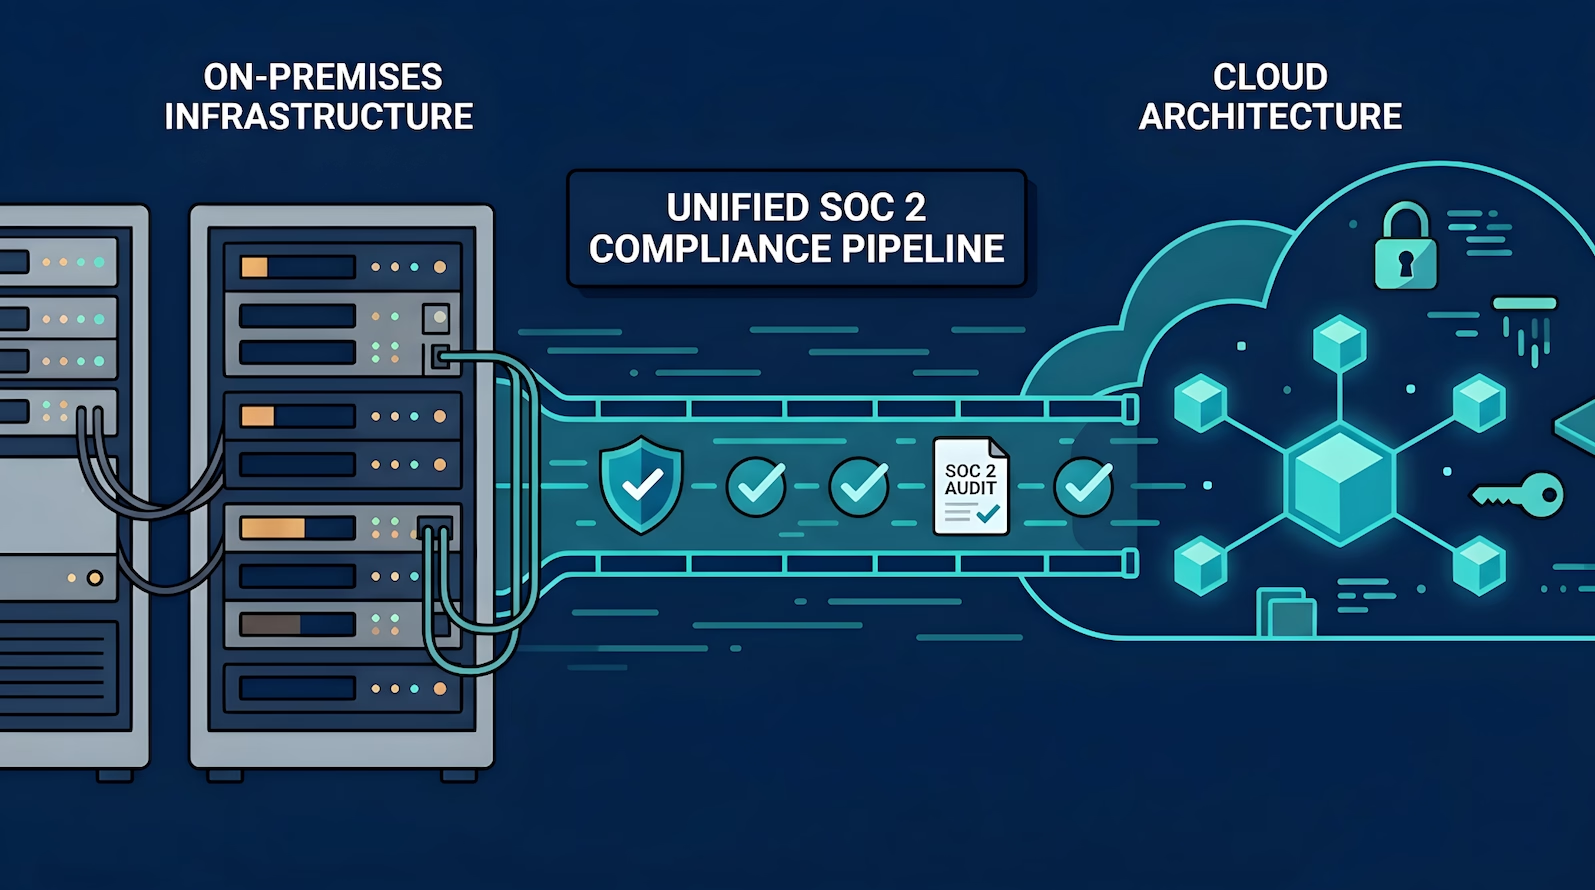
A diagram titled "Unified SOC 2 Compliance Pipeline" shows a blue arrow flowing from a two-cabinet "ON-PREMISES INFRASTRUCTURE" server to a "CLOUD ARCHITECTURE" cloud icon containing a teal cube network, a padlock, and a key. Within the arrow, a "SOC 2 AUDIT" icon is flanked by three shield checkmarks.

GRC Compliance for On-Prem and Hybrid Environments

GRC platforms automate compliance evidence collection for cloud-native infrastructure. Connect your AWS account, hook in your identity provider, link...
What Vanta and Drata Can't Automate

What Vanta and Drata Can't Automate

Companies that implement Vanta or Drata expecting near-complete automation of their SOC 2 compliance work tend to hit the same wall. The integrations...
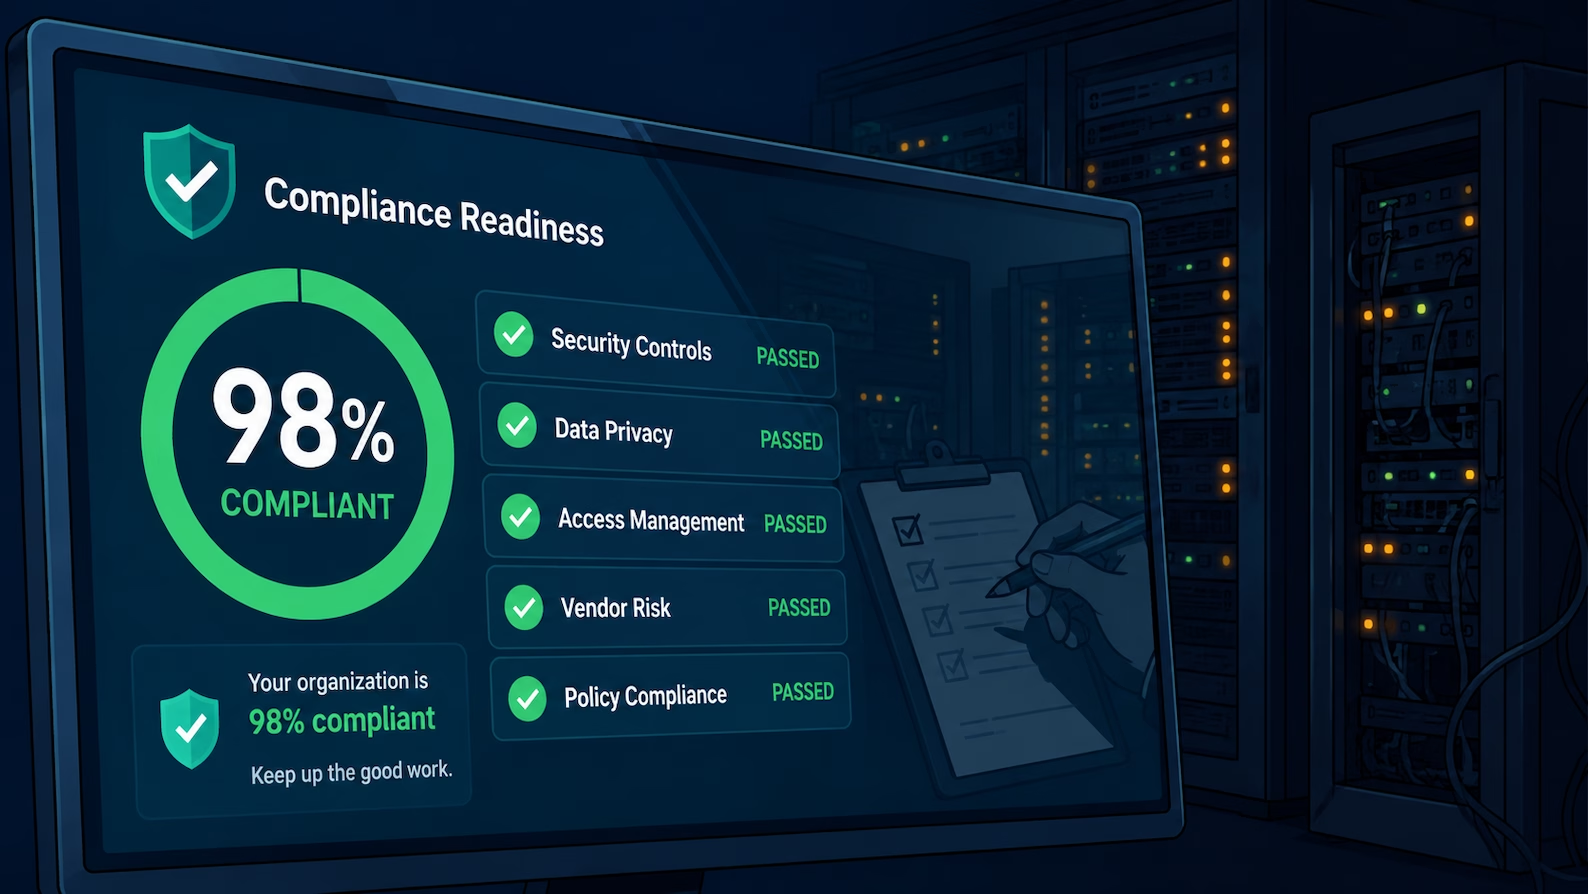
Compliance dashboard showing 98% readiness glows green on a monitor in a dark server room. A subtle reflection of an auditor’s clipboard and pen appears on the screen alongside shadowed server racks, highlighting the gap between automated compliance metrics and real-world audit visibility.

Your GRC Platform Is Green. Your Compliance is Red.

The GRC platform dashboard is green. Every automated test passes. The readiness score reads somewhere in the nineties. The team spent three months...
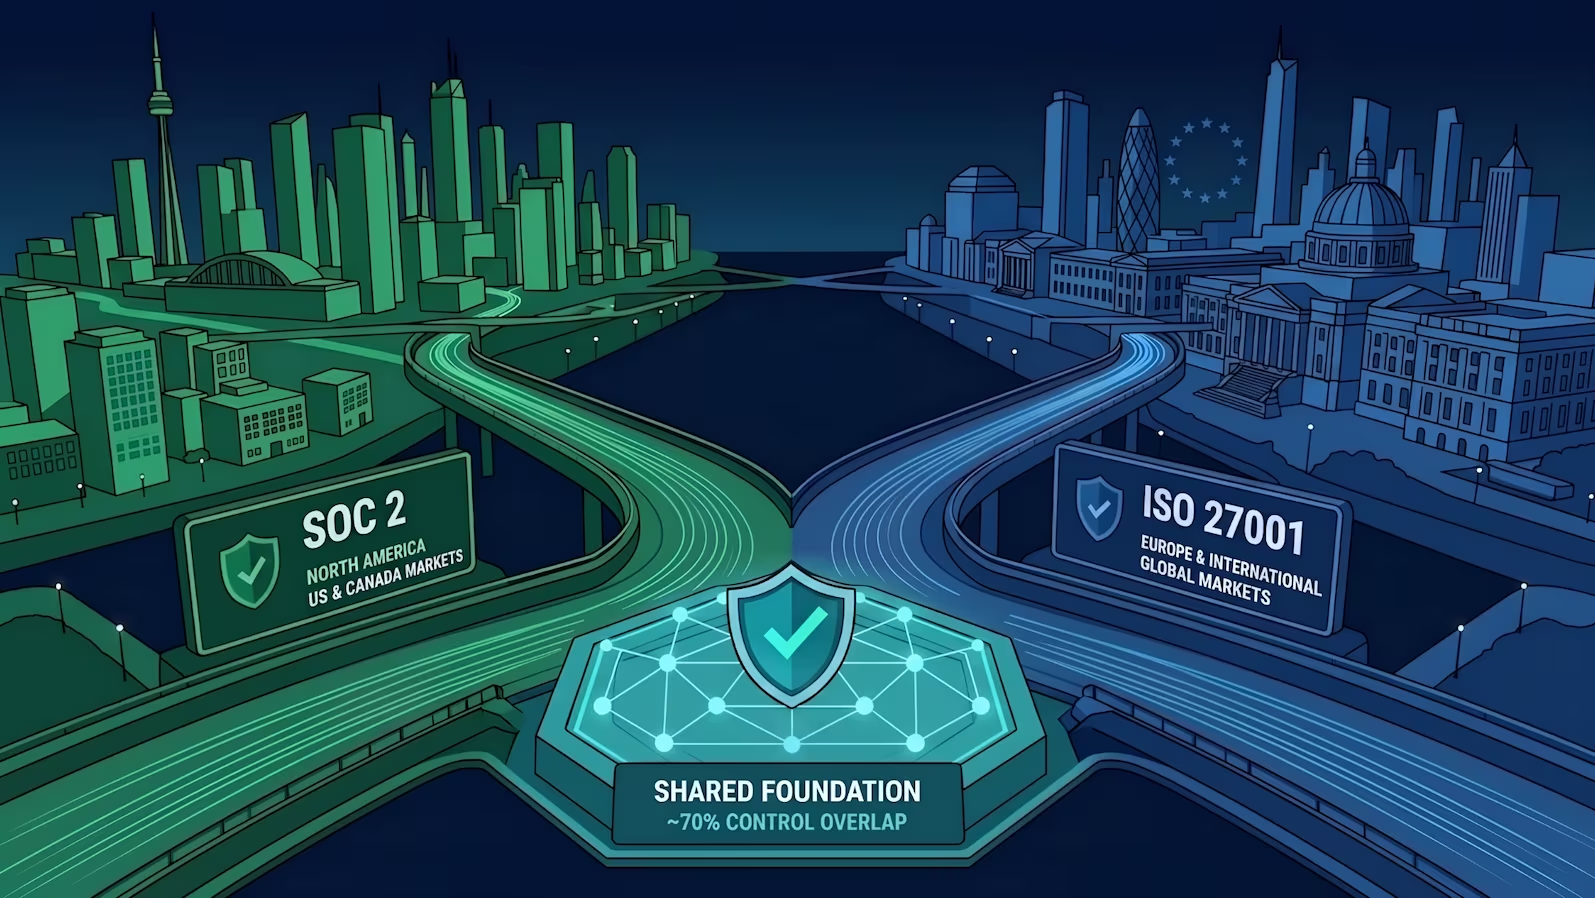
A schematic map illustration showing green and blue paths converging from different cityscapes. On the green left, a North American skyline and sign labeled "SOC 2". On the blue right, a European/Global skyline and sign labeled "ISO 27001". The paths meet at a central glowing hexagonal data hub with network nodes. Text below the central hub reads "SHARED FOUNDATION, ~70% CONTROL OVERLAP", illustrating standard convergence.

ISO 27001 vs. SOC 2: Which Should Come First?

The answer is almost always determined by one thing: who is buying from you and where they are located. US enterprise buyers want SOC 2. EU and...
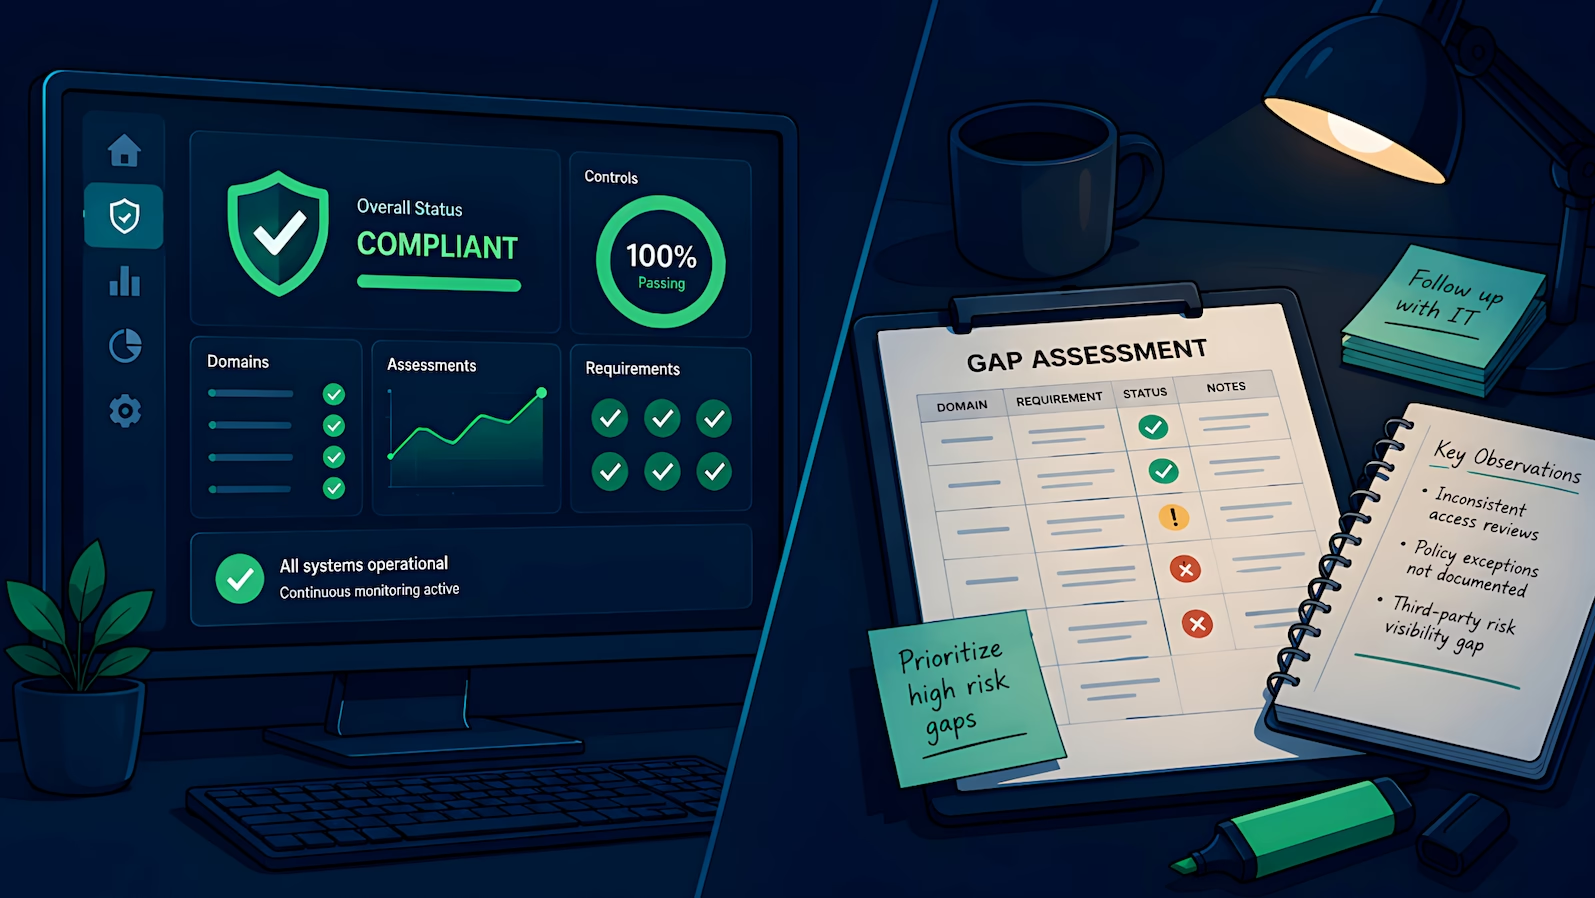
Split illustration showing an automated compliance dashboard with green checkmarks beside a consultant’s desk with a gap assessment, notes, and highlighted risks, contrasting platform monitoring with human review.

What a SOC 2 Readiness Assessment Includes (With or Without Drata)

A SOC 2 readiness assessment and Drata solve different problems. The assessment tells you whether your control environment is adequate before the...
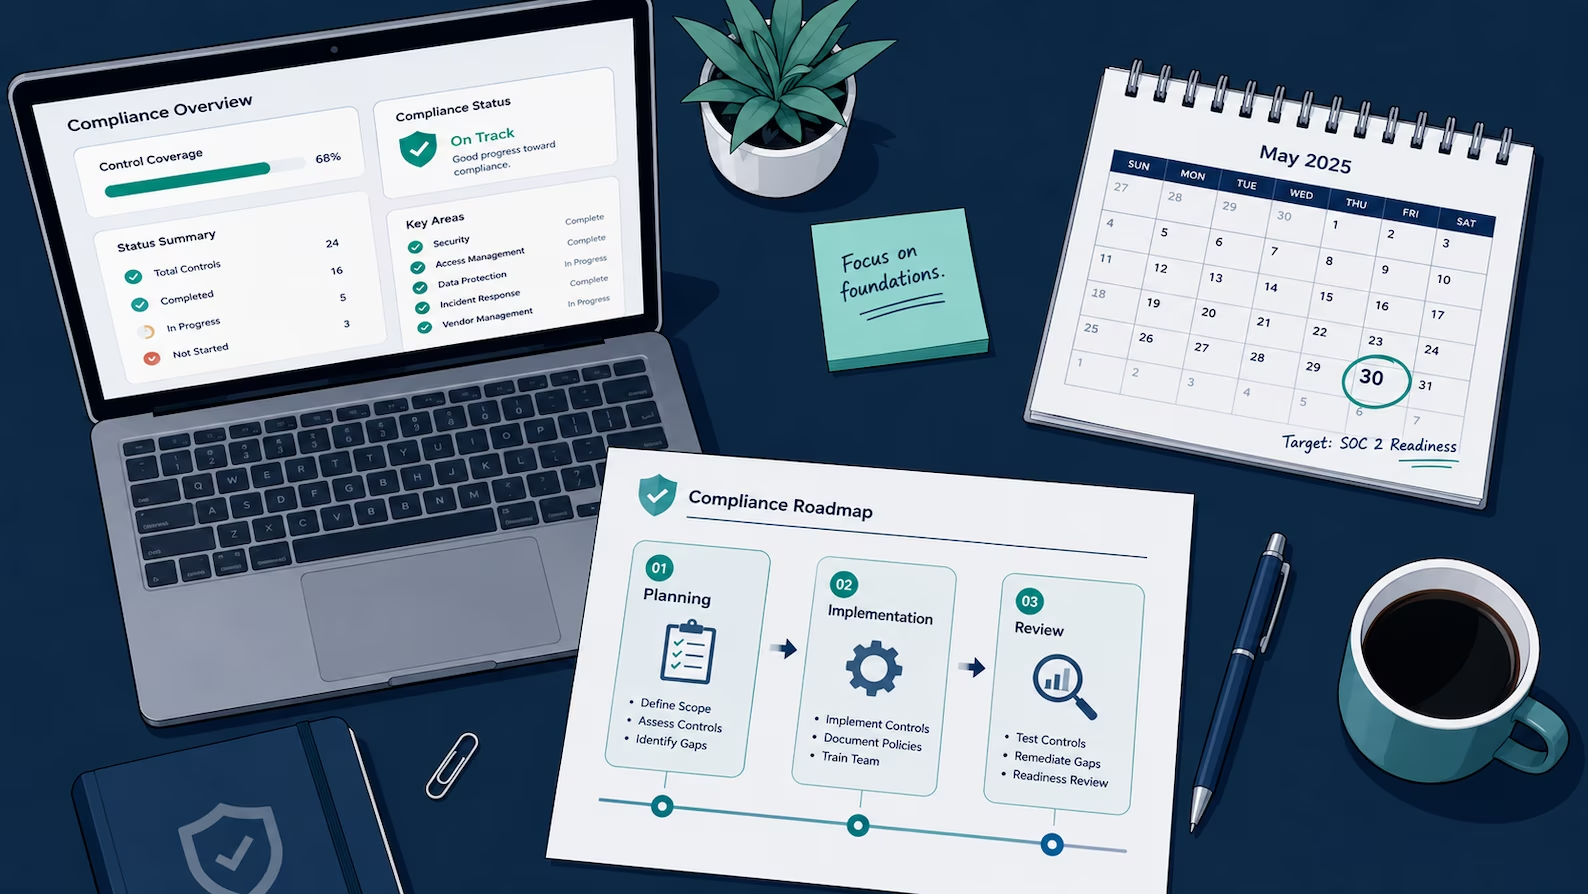
Overhead illustration of a startup workspace on a dark navy desk, featuring a laptop with a compliance dashboard, a three-phase roadmap document, and a calendar with a readiness target date circled, showing a clear, manageable compliance plan in progress.

How to Get SOC 2: Timeline, Cost, and First Steps

If you've already read SOC 2 Explained: What It Is and Why Enterprises Require It and you're ready to move, this is the operational post for teams of...
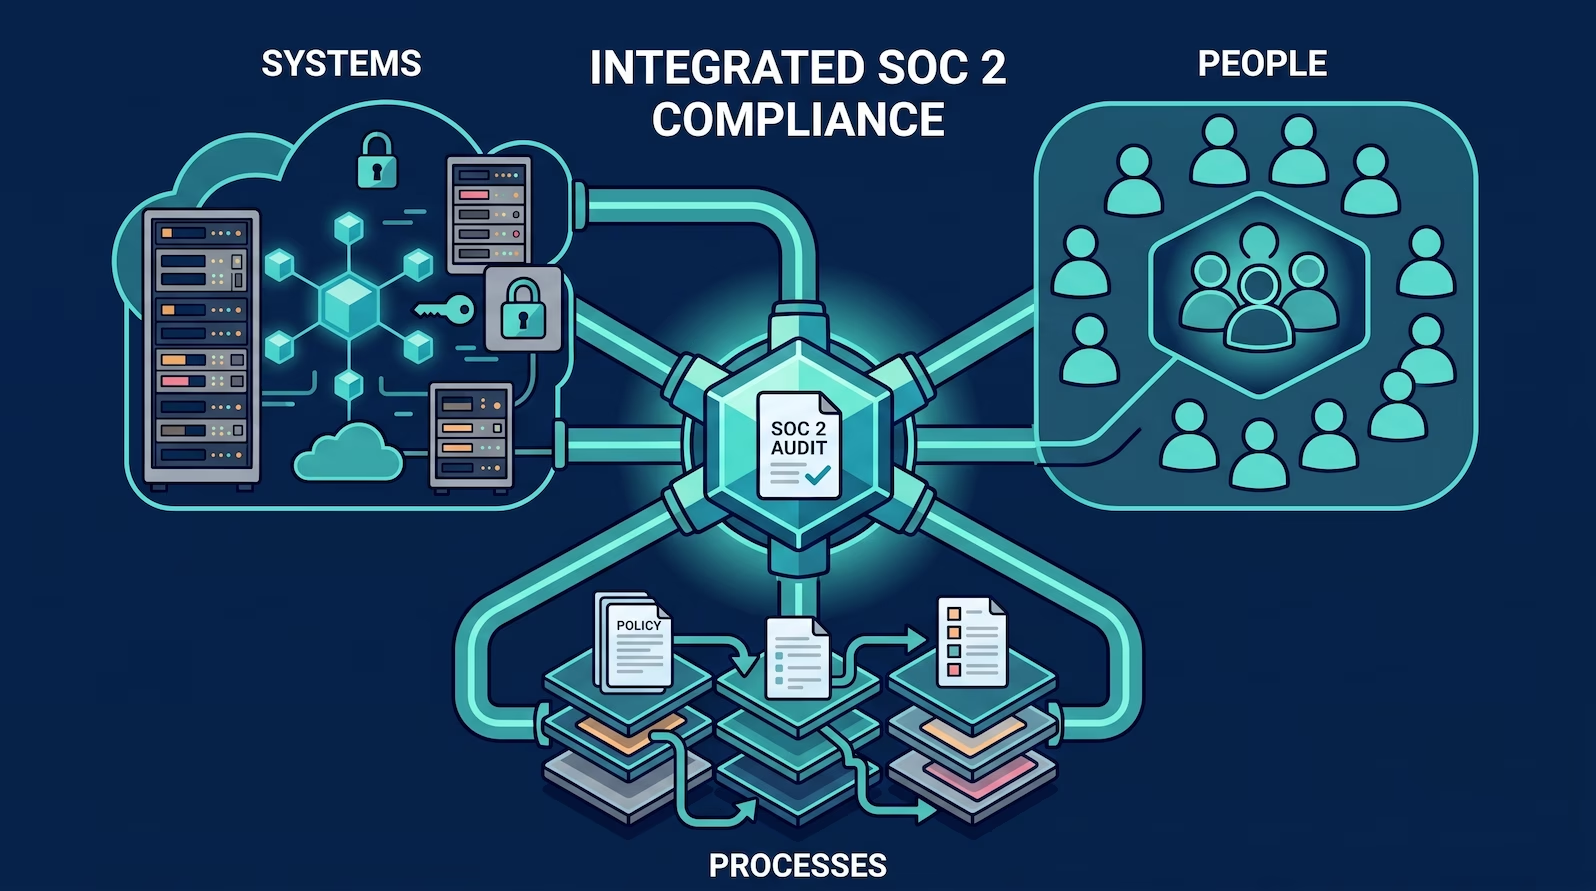
An architectural diagram titled "INTEGRATED SOC 2 COMPLIANCE" shows three components—Systems (servers/clouds), People (icon groups), and Processes (document stacks)—all converging on a central "SOC 2 AUDIT" hub with glowing connections.

SOC 2 Scope: Systems, People, and Processes. The Complete Guide

Most SOC 2 guides treat scope as a single question: what systems are we certifying? That is one third of the answer.

SOC 2 scope has three...
A stylized vector desk illustration on dark blue-green. Left: open laptop showing 'PRODUCT DASHBOARD' charts. Center: a bound 'SOC 2 TYPE II AUDIT REPORT' with seal. Right: 'SECURITY QUESTIONNAIRE' papers with checks and pencil. Glowing circuits connect them with floating icons: $, €, 👍, 🔒.

SOC 2 Explained: What It Is and Why Enterprises Require It

An enterprise prospect sends over a security questionnaire. Or procurement asks whether you have a SOC 2 report. Or a deal stalls because the...
An illustrative office scene featuring a laptop displaying a "Compliant" SOC 2 dashboard with green checkmarks, alongside a physical "SOC 2 Report" notebook on a glass conference table. In the background, a large window shows a cityscape, and a branded sign reads "Canadian Tech, Trusted."

SOC 2 Consultants in Canada: Audit-Ready Programs

SaaS companies come to us when SOC 2 starts blocking deals.

Truvo is a Canadian cybersecurity consultancy. We run SOC 2 readiness and audit support...
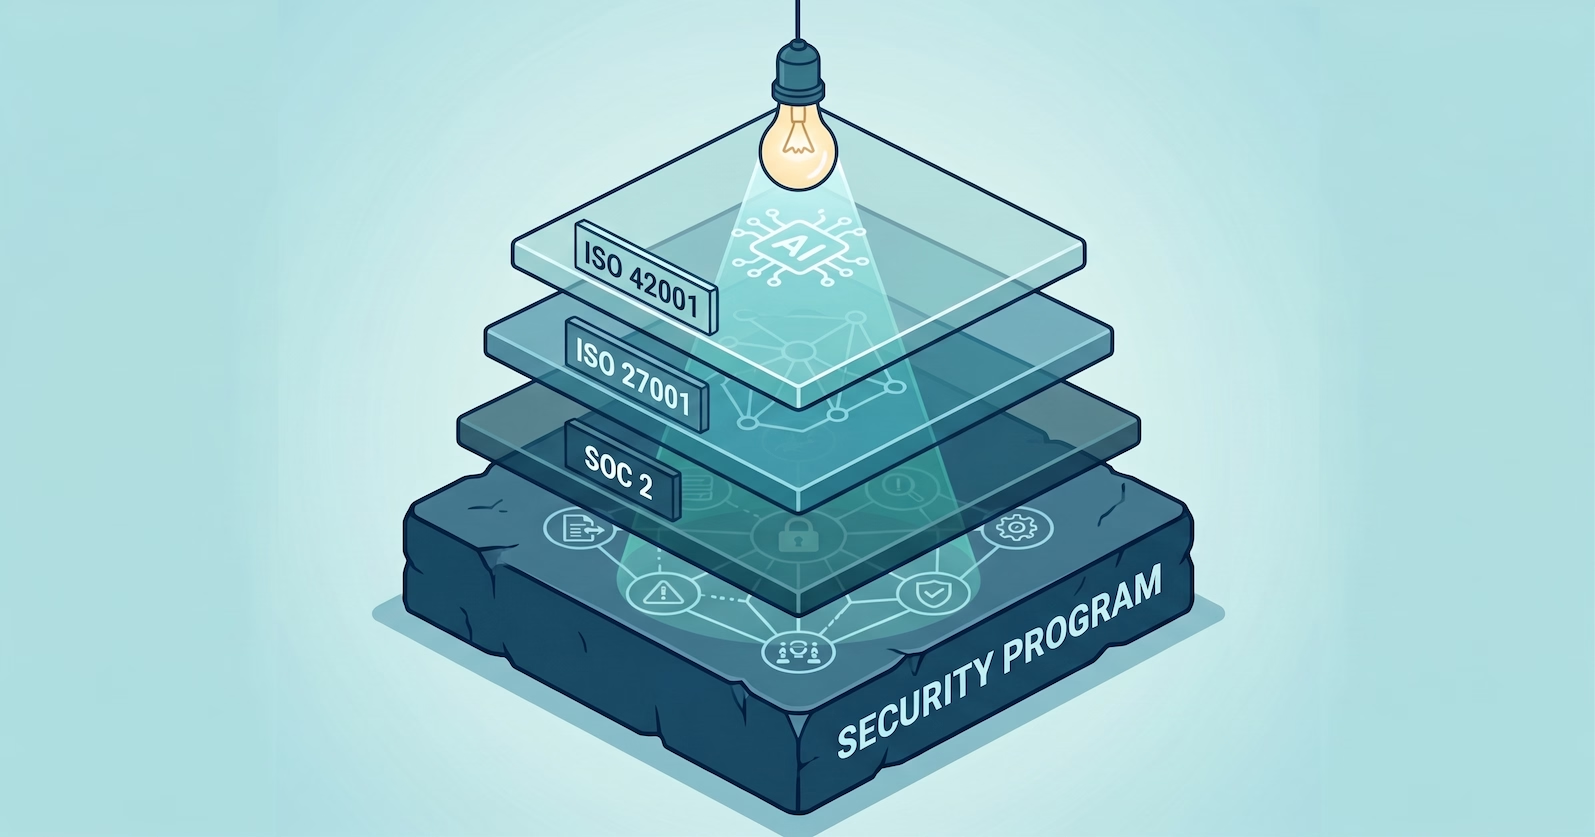
Most of ISO 42001 Is Already Built

Most of ISO 42001 Is Already Built

How much of an existing SOC 2 or ISO 27001 program carries into ISO 42001, and why the framework tax is mostly imaginary for teams that built a real...

Truvo Cyber blog hero — Only Two Auditors in Canada Can Certify ISO 42001: what that bottleneck means for cost, timeline, and 2026 certification planning.

Only Two Auditors in Canada Can Certify ISO 42001. Here's What That Means for Buyers.

In Canada, RFPs landing in 2026 include a clause certification must be issued by an SCC-accredited body. SCC is Canada's national accreditation body,...
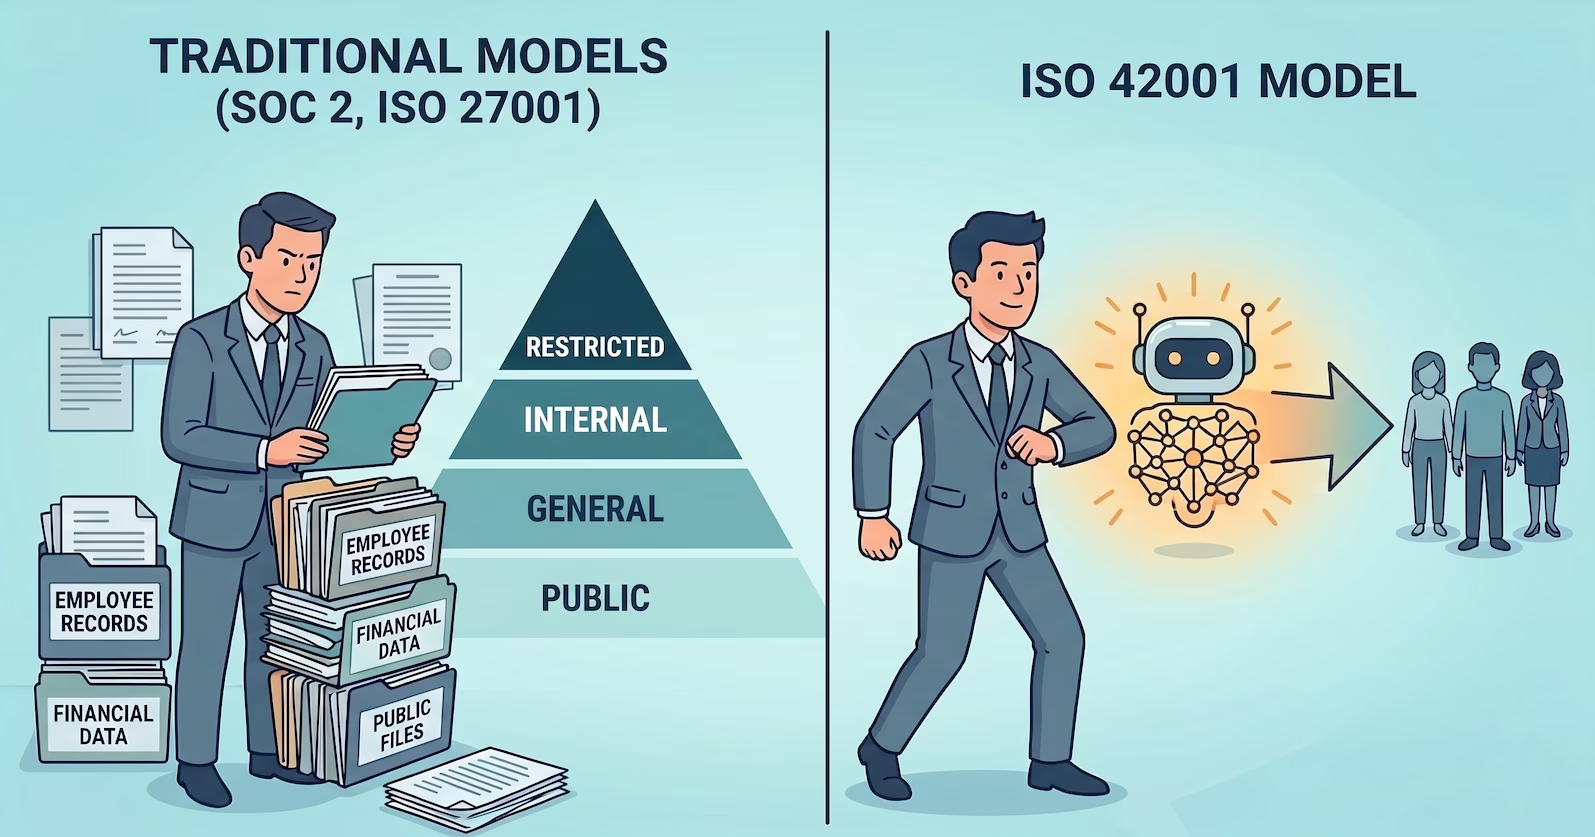
Truvo Cyber blog hero — ISO 42001 explained: why AI governance governs usage, not data classification, and how that reframes the ISMS mental model.

ISO 42001: How AI Governance Differs from Data Protection

Every traditional compliance framework asks the same opening question. How sensitive is the data, and how well is it protected? SOC 2, ISO 27001,...