

Build

AIUC-1 certification readiness for AI agent companies

Enterprise buyers want proof that your AI agents behave as designed, in the cloud, on-prem, in colocation or on neocloud GPUs. AIUC-1 is the standard built for that question. We prepare your company for AIUC-1 certification:

  • Gap assessment against all six AIUC-1 domains, scoped to your agents and the infrastructure they run on
  • Policies, controls and evidence written for how your agents operate
  • AI penetration testing and red teaming of your agents for prompt injection, jailbreaks, data leakage, hallucinations and unsafe tool calls
  • Evidence organized for the accredited auditor
  • Support through quarterly retests and annual renewal

Talk to an AIUC-1 consultant

Tell us which agents you plan to certify and a consultant will follow up to book a call.

What AIUC-1 readiness includes

One senior lead and a specialist team, from scoping through the accredited audit.

icon-5

AIUC-1 scoping and gap assessment

We define the agents, deployment context and applicable requirements, then rate your current controls across Data and Privacy, Security, Safety, Reliability, Accountability and Society, with a prioritized remediation roadmap. We cover cloud, on-prem, colocation and neocloud deployments, including model hosting and data isolation.

icon-7

Policies and Security Program Manual

AI-specific policies, acceptable use, incident handling and human escalation procedures, written for your operations and mapped to AIUC-1 requirements.

icon-8

Agent controls and guardrails

Your engineers implement the technical controls with clear instructions: input and output filtering, tool-call permissions, data access limits and exception escalation.

icon-6

Logging and traceability

Records of what each agent did and why, kept in a form an auditor can review, to support the Accountability domain.

icon-2

AI penetration testing and red teaming

Adversarial testing of your agents for prompt injection, jailbreaks, data leakage, hallucinations and unsafe tool calls, plus a penetration test of your AI endpoints. The reports serve as evidence for the AIUC-1 third-party testing requirements, which call for testing at least every quarter.

icon-4

Audit coordination

Evidence organized by requirement, your team prepared for auditor interviews, and the accredited audit scheduled with a firm such as Schellman or Coalfire.

How AIUC-1 readiness works: Assess, Build, Operate

A defined scope and a fixed price, agreed before kickoff. Your team knows what happens each week and what is expected of them.

01

Assess

Scope the agents and deployment context, run the AIUC-1 gap assessment across all six domains and agree on a remediation roadmap with owners.

02

Build

Policies, Security Program Manual, agent guardrails, logging and evidence, then a technical evaluation of your agents. Gaps close before AIUC's own evaluations and the accredited audit.

03

Operate

Certification holds for one year. AIUC-1 calls for third-party testing every quarter and AIUC updates the standard quarterly. Your team maintains the program in-house, or our managed service keeps it current through renewal.

What you hold at the end

An AI agent program ready for the AIUC evaluations and the accredited audit.

  • AIUC-1 gap assessment report

  • Remediation roadmap with owners

  • AI policy suite

  • Security Program Manual

  • Technical evaluation report for your agents

  • Evidence organized by requirement

  • Evaluation readiness review

  • Accredited audit scheduled

Why companies choose Truvo for AIUC-1

Agent-level assurance built on a real security program.

Who AIUC-1 readiness is for

AIUC-1 certifies specific AI agents. Companies whose product is an agent, or who deploy agents that take real actions for customers, get the most from it. It gives buyers a recognized answer on agentic AI security.

Frequently asked questions about AIUC-1 certification

AIUC-1 is a security, safety and reliability standard for AI agents, maintained by the Artificial Intelligence Underwriting Company (AIUC). It covers six domains: Data and Privacy, Security, Safety, Reliability, Accountability and Society.

Certification has four steps. Scoping defines the agents and deployment context. AIUC conducts adversarial evaluations, including red-teaming against prompt injection, jailbreaks, data leakage, hallucinations and unsafe tool calls. An accredited auditor, such as Schellman or Coalfire, reviews the policy, operational and technical controls and the evidence. AIUC then issues a certificate and audit report.

One year. Certified agents are retested quarterly against the standard version locked in at certification, and AIUC updates the standard every quarter.

Two kinds of testing apply. AIUC conducts the certification evaluations itself. The standard also requires quarterly testing by qualified, independent third parties across security, safety, reliability, data and privacy, and accountability risks. We perform that AI penetration testing and red teaming, including the penetration test of your AI endpoints, and the reports serve as evidence for the audit.

Your consultant scopes the certification, leads the gap assessment, writes the policies and Security Program Manual, guides your engineers on agent controls and logging, prepares your team for the evaluations and coordinates the accredited audit. AIUC and the auditor issue the certification independently.

ISO 42001 certifies an organization's AI management system: ownership, risk assessment and impact assessment across its use of AI. AIUC-1 certifies specific AI agents and tests how they behave. Many companies pursue ISO 42001 for governance and AIUC-1 for agent-level assurance, and the evidence overlaps.

Yes. AIUC-1 asks you to document the deployment decision (cloud or on-prem), protect the model hosting environment, record processing locations and isolate customer data. On your own hardware or a neocloud, more of that evidence is collected by hand, and we collect it.

Start with the AIUC-1 gap assessment. Your SOC 2 controls cover much of the Data and Privacy and Security domains. The new work typically concentrates on agent guardrails, reliability testing and traceability of agent actions.

Get your AIUC-1 readiness roadmap

Book a 30-minute strategy call. We look at the agents you plan to certify and give you a clear scope, timeline and price.

From the blog: AI governance

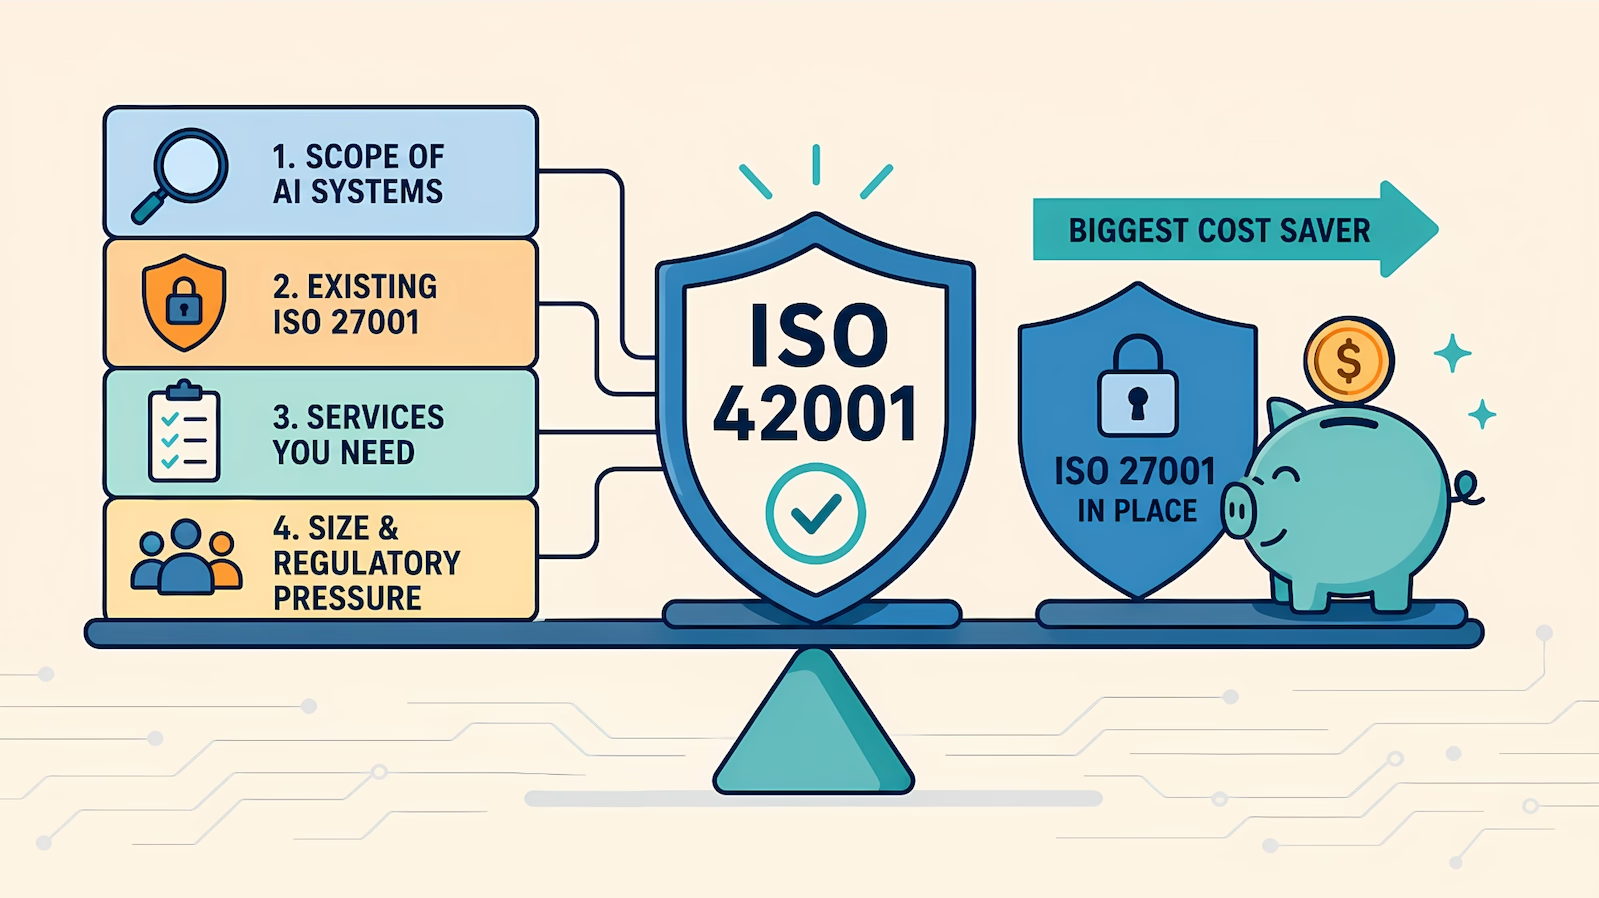
ISO 42001 Cost in 2026: The 4 Factors

ISO 42001 implementation and certification for small organization can land anywhere between roughly US$20,000 and US$55,000 for a first ...
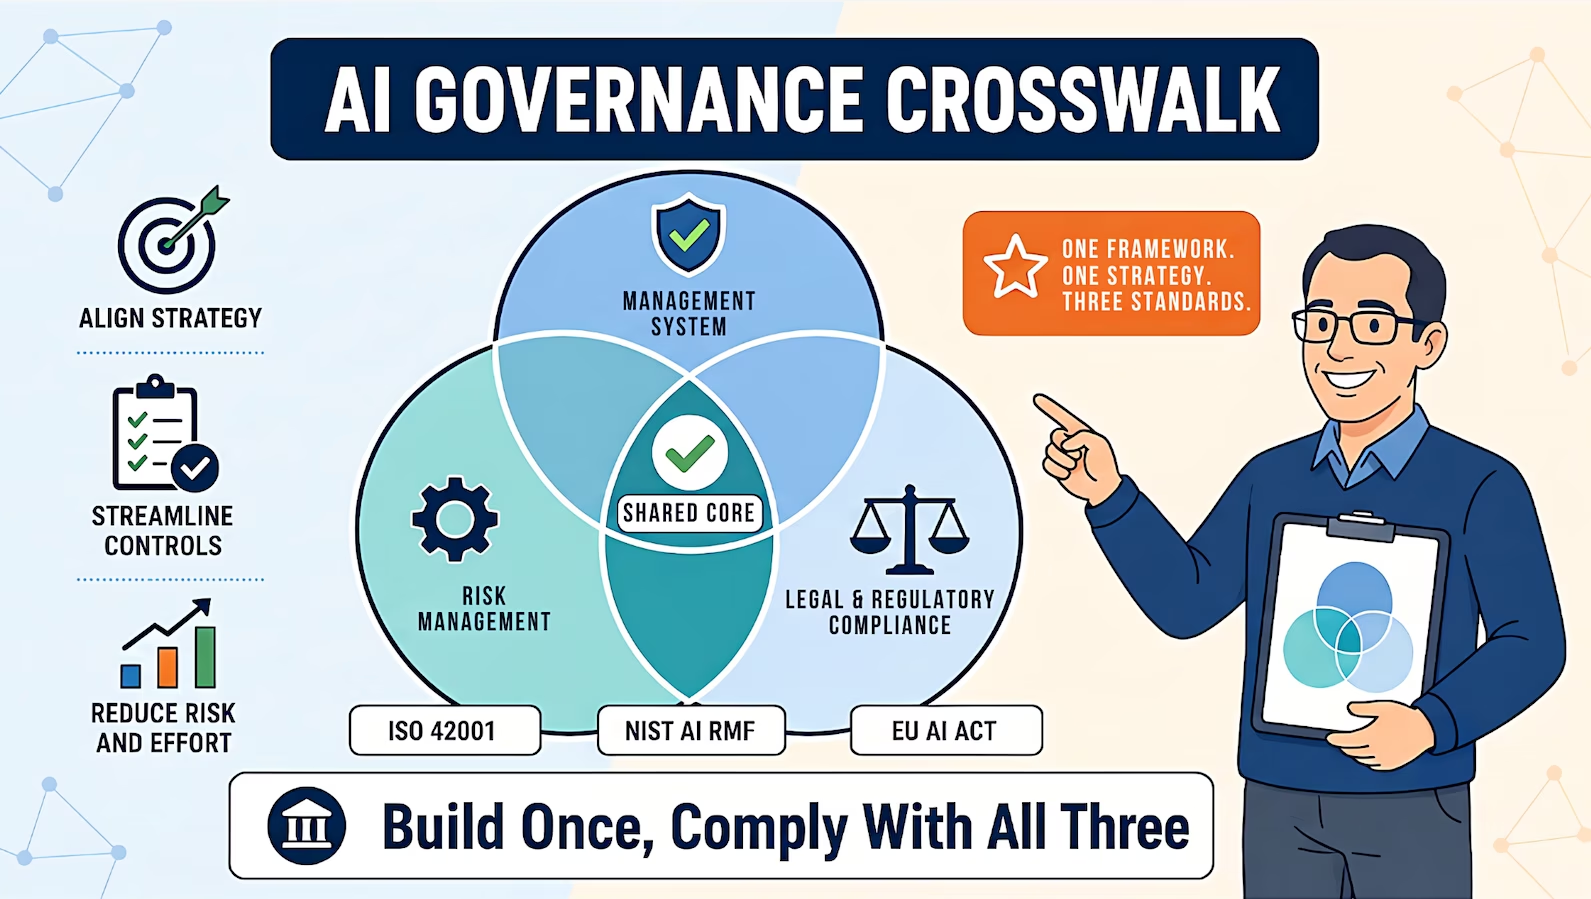
ISO 42001, NIST AI RMF, and the EU AI Act: The Complete Control Crosswalk

ISO 42001, the NIST AI RMF, and the EU AI Act overlap on roughly two-thirds of their controls. Design one control set against that shared core and ...
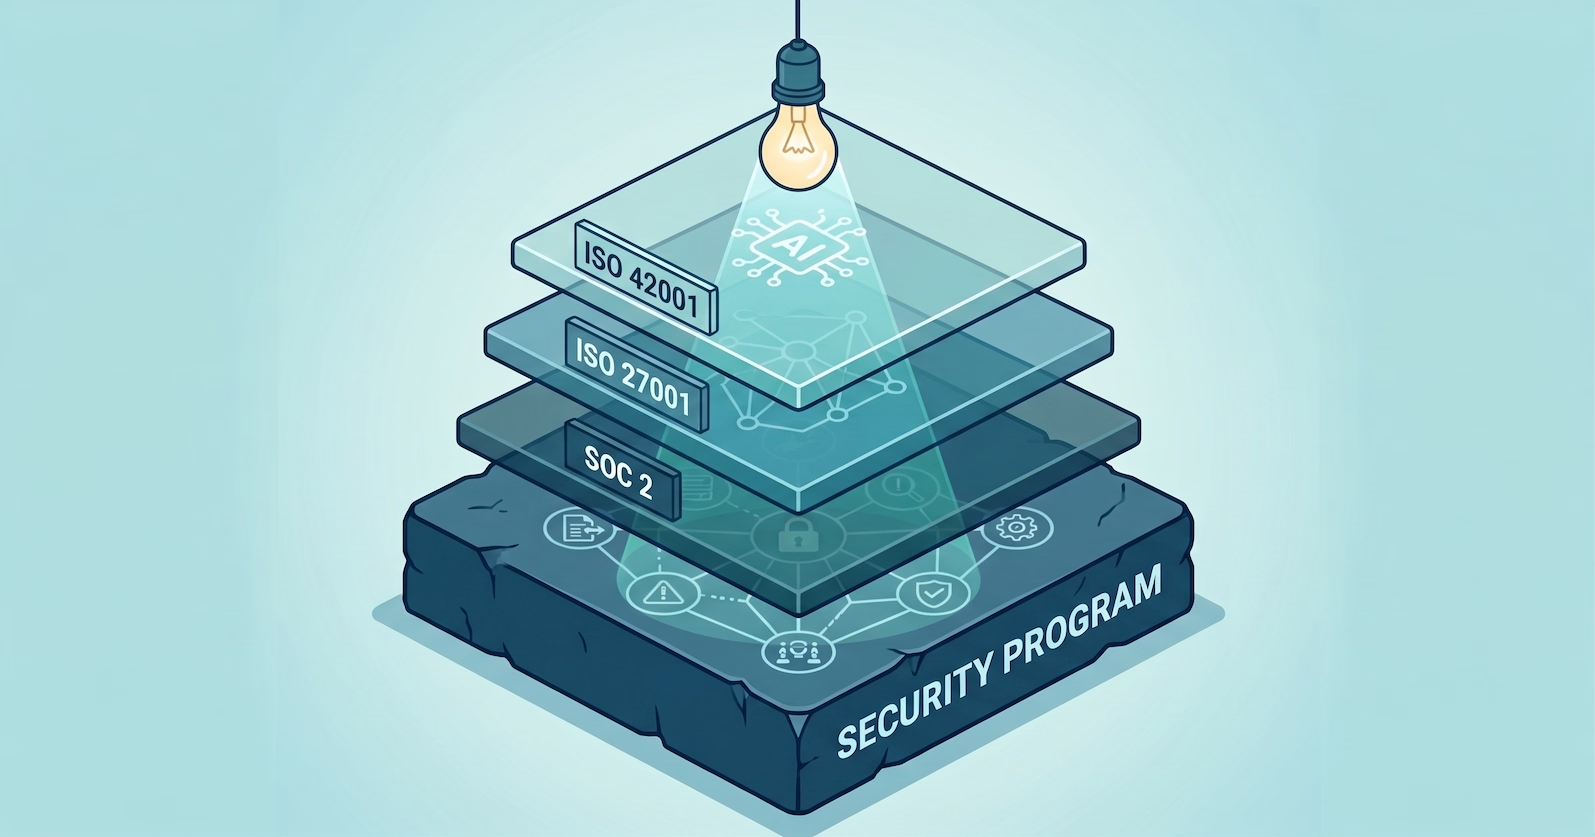
Most of ISO 42001 Is Already Built

How much of an existing SOC 2 or ISO 27001 program carries into ISO 42001, and why the framework tax is mostly imaginary for teams that built a real ...