AI Security

ISO 27090 AI Security Consulting

Truvo puts the AI security guidance of ISO/IEC 27090:2026 to work inside your ISO 27001 ISMS or ISO 42001 AI management system. A senior lead helps your team protect training data, models and AI features against threats such as data poisoning, prompt injection and model theft.

  • Covers the AI systems you build and the AI services you buy
  • Built into your ISO 27001 ISMS or ISO 42001 AIMS
  • Led by a senior CISSP in the US or Canada

For most SMBs, ISO 27090 consulting costs USD $2,500 to $5,000 a month to build and operate the program.

Talk to an AI security consultant

Share the AI systems in scope and your timeline, and a consultant will follow up to book a call.

What does ISO 27090 implementation involve?

Truvo follows the Assess, Build, Operate model, with ISO 27090 guidance built into the management system you already have.

What do you get from an ISO 27090 engagement?

Four things you hold at the end, ready for customer security reviews.

When is Truvo the right call?

For many companies, the trigger is an enterprise customer security review that asks how AI features, models and training data are protected.

What do clients say about Truvo's ISO work?

"Truvo Cyber conducted our ISO 27001 and ISO 27701 internal audit. They were easy to work with, communicated clearly throughout the project, and delivered a thorough, professional report on time. I would recommend them to any organization working through similar compliance requirements."

Ellipse (1) (1)
Aimee Halbert

UserTesting

"Truvo is an instrumental and integrated part of our team...
They don’t just provide recommendations; they ensure we meet our stringent ISO 27001 and SWIFT compliance goals. We trust them with projects of national importance, and they deliver."

Mask Group-1
Matt Charette

CISO, Payments Canada

Ready to plan your ISO 27090 AI security program?

Book a strategy call. We review your AI systems, your ISO 27001 or ISO 42001 status and your timeline, and give you a clear picture of the scope and investment.

Book Your Free ISO Strategy Session

What do companies ask about ISO 27090?

For most SMBs, ISO 27090 consulting costs USD $2,500 to $5,000 a month to build and operate the program. The monthly fee depends on the number of AI systems in scope, whether you build models or use third-party AI services, and whether an ISO 27001 ISMS or ISO 42001 AIMS is already in place.

ISO/IEC 27090:2026 is an international standard from ISO/IEC JTC 1/SC 27, published in October 2026. It gives guidance on understanding, detecting and mitigating security threats specific to AI systems throughout their life cycle, from training data to models, including threats such as data poisoning and model theft.

ISO describes ISO 27090 as security guidance with no requirements for a management system, so organizations apply it within a certifiable management system such as ISO 27001 or ISO 42001. An independent assessment against ISO 27090 gives customers an outside view of your AI security.

ISO/IEC 42001 sets requirements for an AI management system, covering how an organization manages its responsibilities, risks and opportunities relating to AI. ISO 27090 focuses on security threats to AI systems and ways to address them. Many companies use ISO 42001 for AI governance and ISO 27090 to guide the security safeguards inside it.

ISO 27090 complements ISO/IEC 27001 and ISO/IEC 27002 by addressing threats specific to AI systems. ISO 27001 sets the requirements for the information security management system, and ISO 27090 adds detail on the AI data, models and workflows that need extra protection. Truvo builds the ISO 27090 safeguards into your ISO 27001 risk treatment plan.

ISO's guide to the standard lists data poisoning, model exfiltration, evasion attacks, membership inference, model inversion, direct model poisoning, prompt injection, sensitive model output and outputs that contain injection attacks. It also covers threat modelling, red teaming, supply chain security and the security of model updates and retraining.

Yes. ISO describes the standard as intended for organizations of all sizes that develop or use AI, and its suggested first steps include identifying AI systems supplied by third parties. For companies that buy AI, the work typically centers on supplier selection, the data shared with each service, access to the service and monitoring of its use.

Yes, as a separate engagement with a different team, so the assessors stay independent of the program. See our ISO 27090 AI security assessment page.

Client data, documentation and sensitive materials are stored in secure North American cloud environments. Every engagement is led by a senior CISSP in the US or Canada with 10+ years in security, and every consultant on the engagement is an experienced, vetted professional.

How is Truvo different?

Our consultants build and operate management systems, so AI security fits how your team builds and operates AI.

Ready to secure your AI systems?

ISO 27090 AI security consulting led by practitioners who build and operate management systems.

From the blog: AI security and governance

Top ISO 42001 Consultants in Canada (2026): A Buyer's Guide

Truvo Cyber is a Canadian cybersecurity firm that implements ISO/IEC 42001, the AI management system standard, for SaaS and technology companies ...
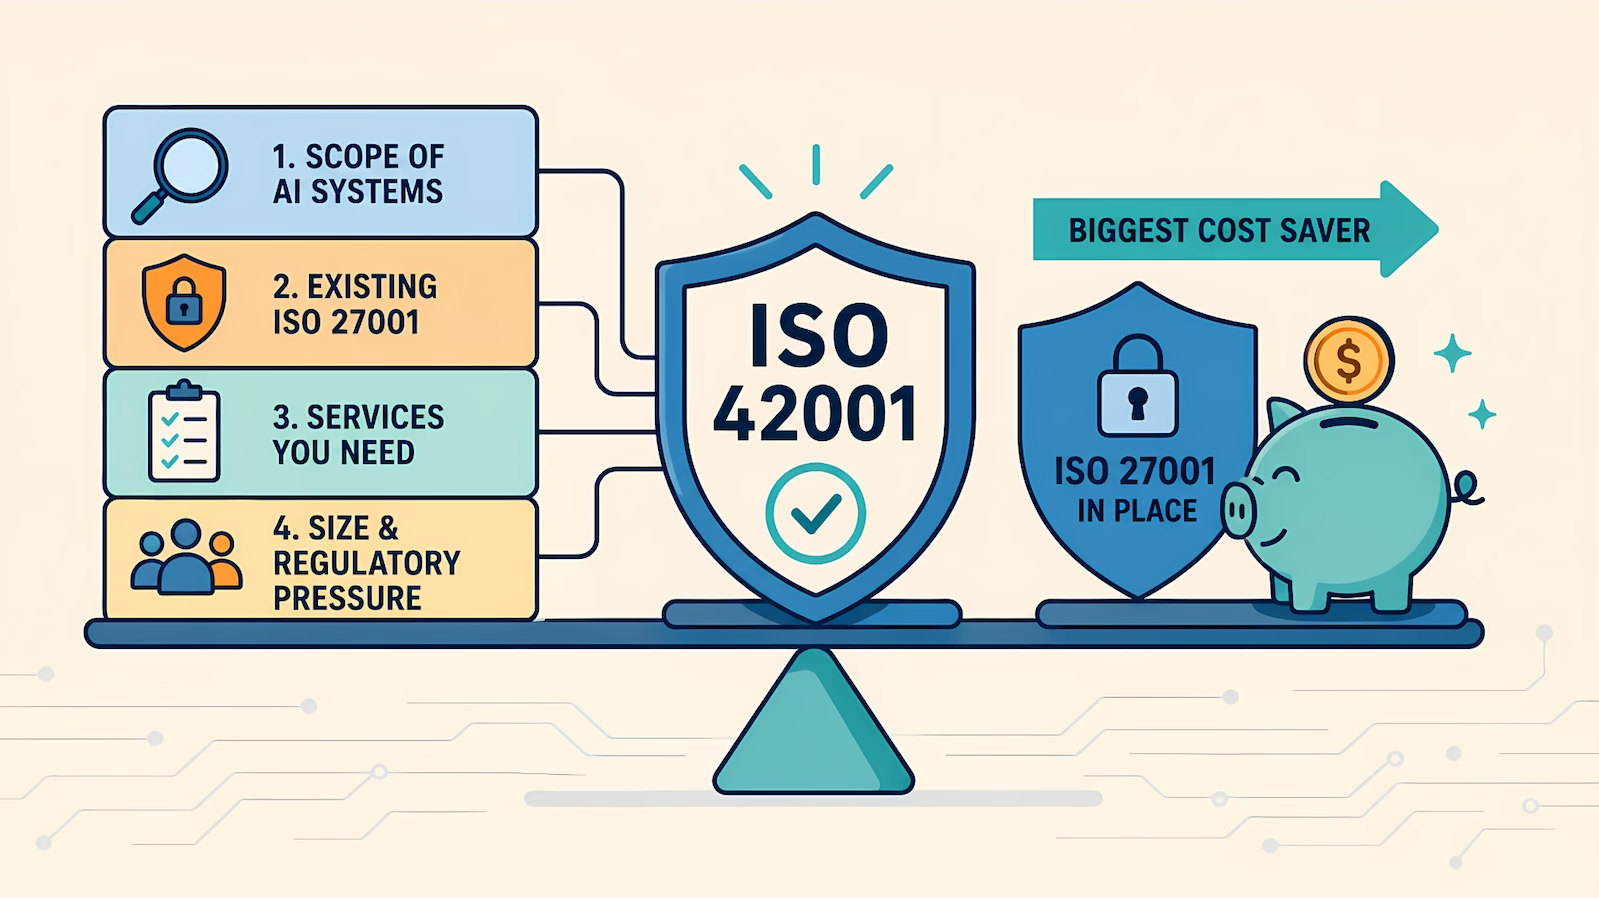
ISO 42001 Cost in 2026: The 4 Factors

ISO 42001 implementation and certification for small organization can land anywhere between roughly US$20,000 and US$55,000 for a first ...
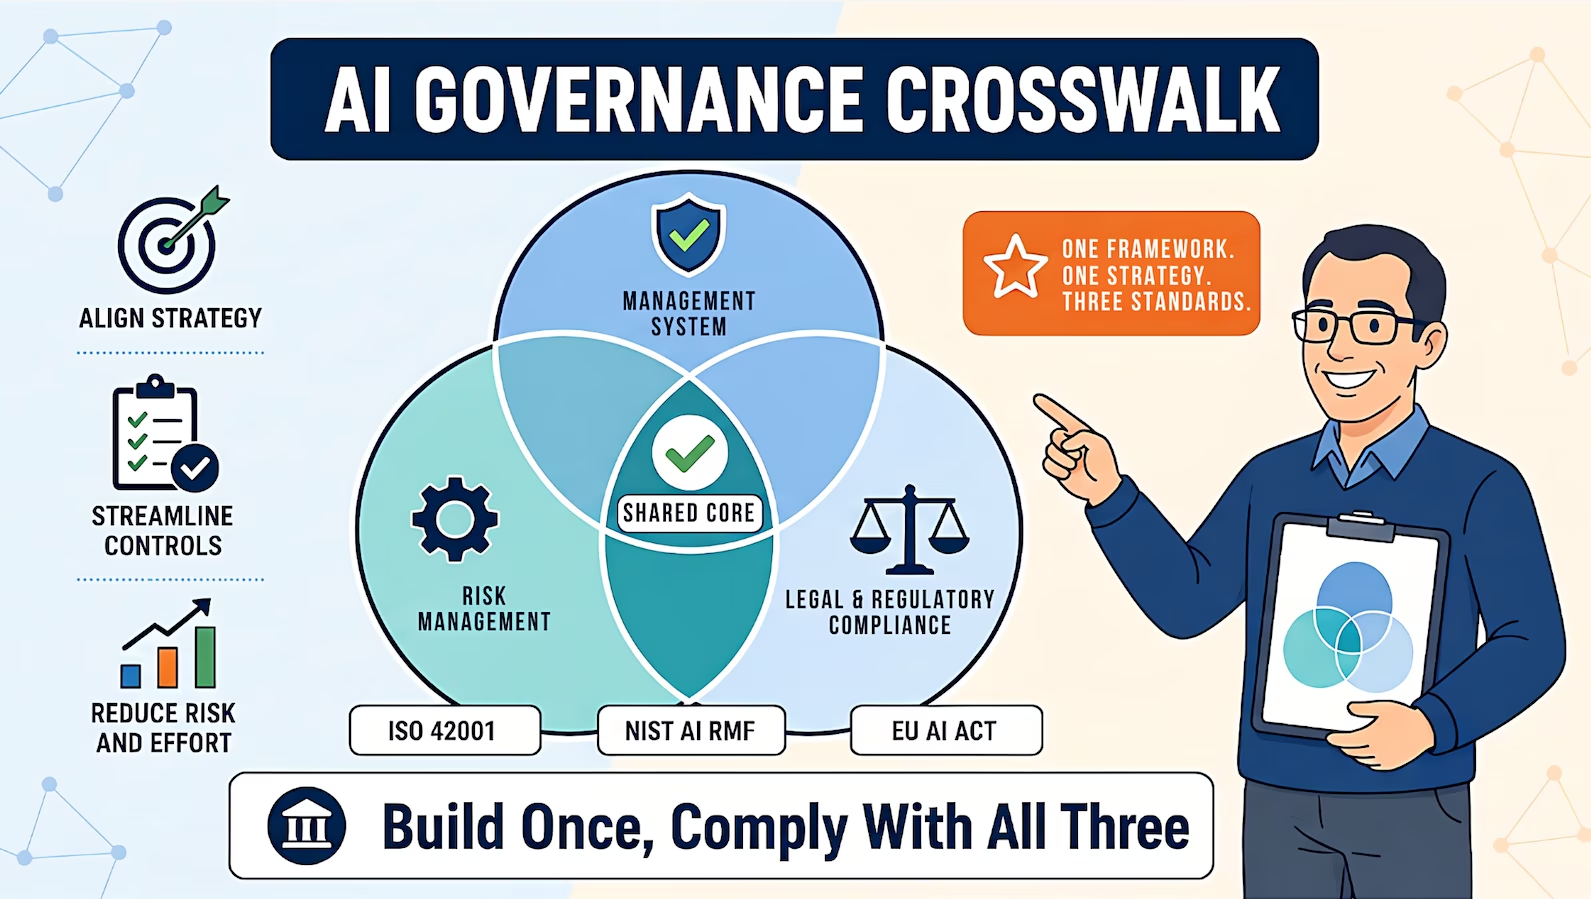
ISO 42001, NIST AI RMF, and the EU AI Act: The Complete Control Crosswalk

ISO 42001, the NIST AI RMF, and the EU AI Act overlap on roughly two-thirds of their controls. Design one control set against that shared core and ...