SOC 2ISO 27001


In our experience, a SOC 2 program covers roughly 70 percent of the work for ISO 27001 certification. The policies carry over, and most controls need ...
Complementary user entity controls (CUECs) are the controls a vendor's SOC 2 report assumes its customers operate. A typical cloud arrangement: the...
SOC 2 evidence collection on-prem works without APIs: auditors accept evidence collected by hand, by script, or by screenshot, provided it is...
A service that runs partly in a public cloud and partly on company-owned hardware is one system for SOC 2 whenever customer data or commands cross...
A SOC 2 report survives a move from a hyperscaler to a neocloud, but its system description, boundary, vendor list and a set of controls change. The...
A Jobber account holds client names, addresses, job history, and, for businesses using Jobber Payments, saved payment details. It is also the system...
A Google Workspace account is not secured by default just because Google operates the infrastructure behind it. Google secures the servers; the...
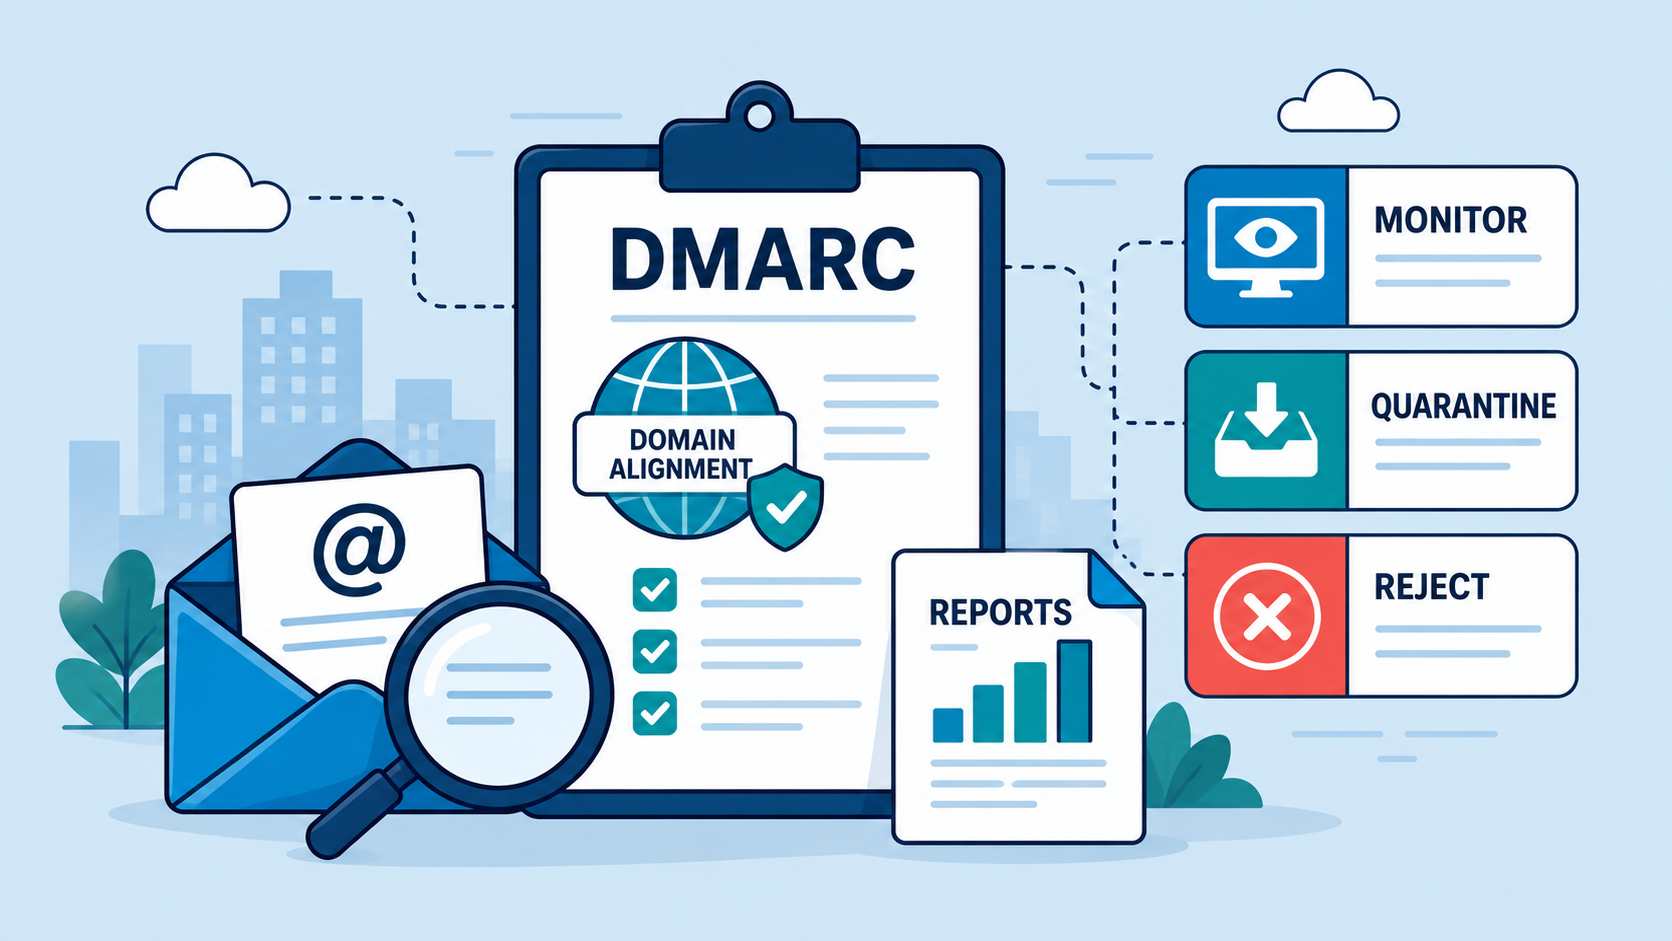
A DMARC check looks at a message that has already gone through SPF and DKIM, and asks one more question: does the domain that passed either of those...
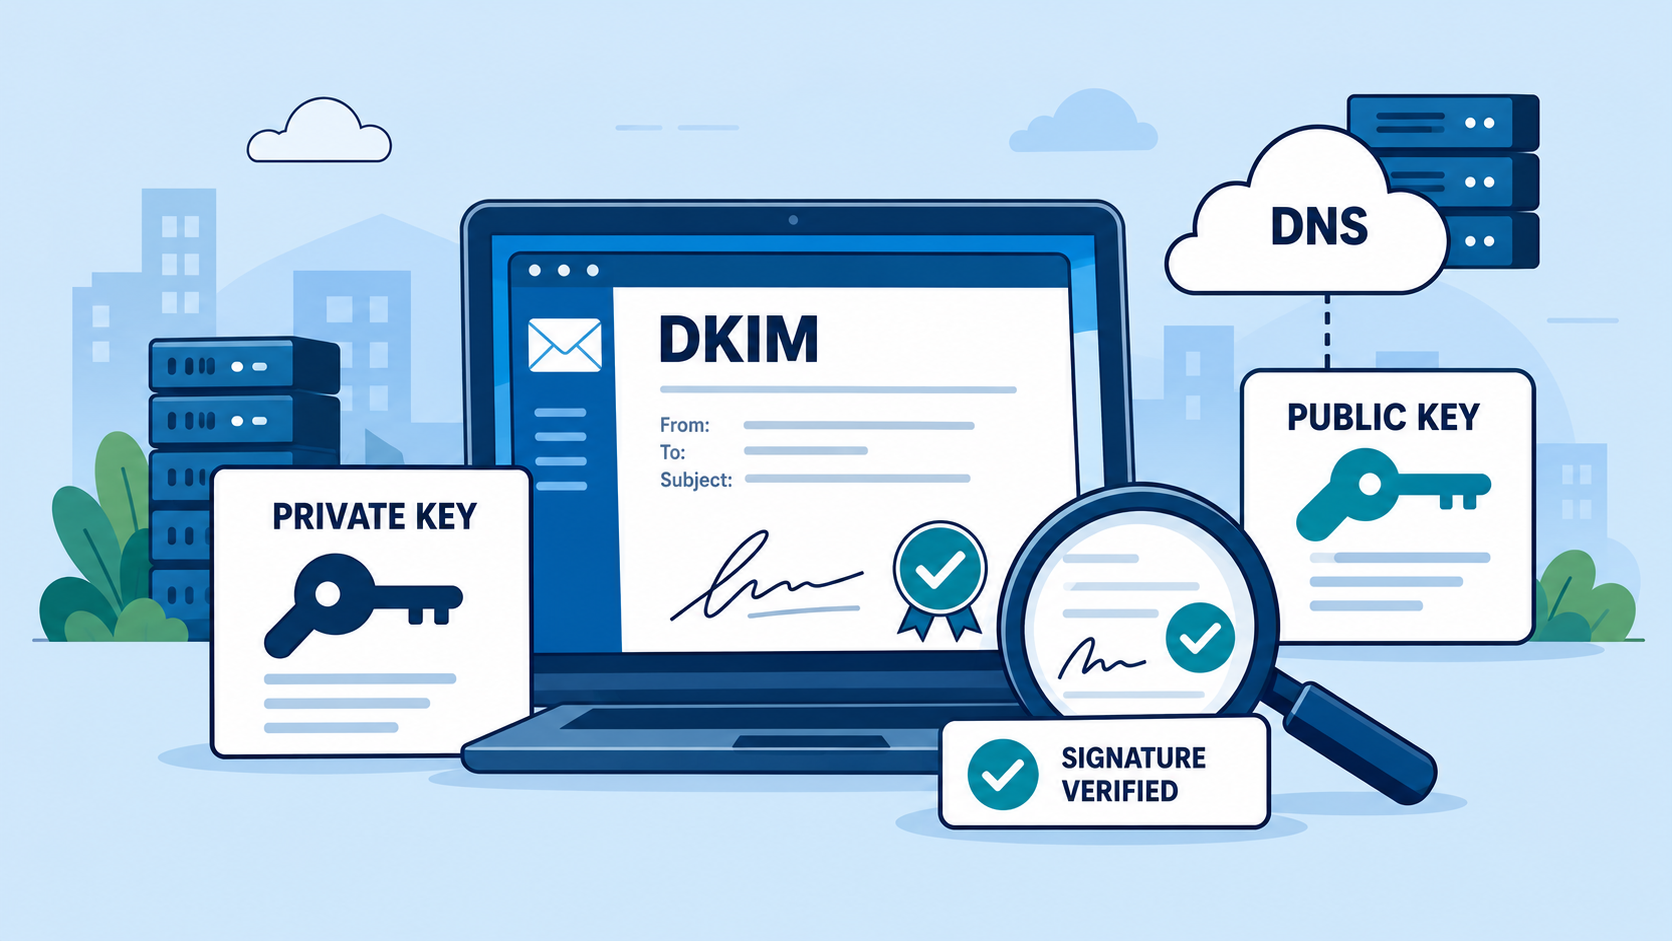
A DKIM check confirms two things about a message: 1) that a system holding the sending domain's private key signed it, and 2) that the signed parts...
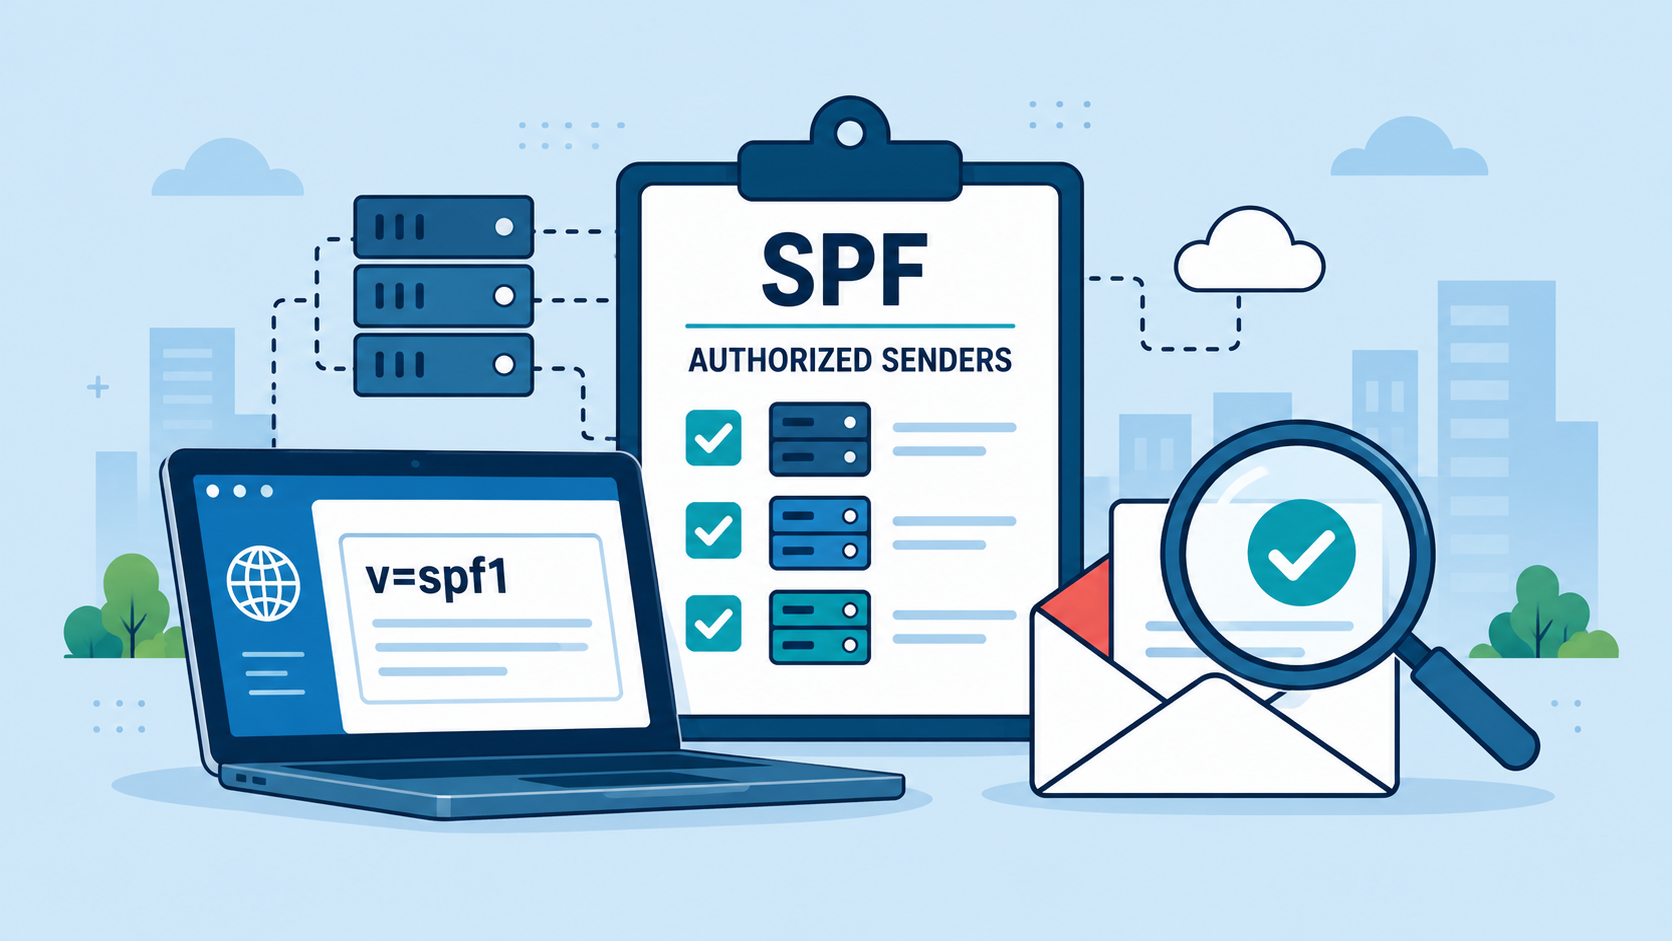
When a message arrives, the receiving mail server checks the sending domain's SPF record before it does almost anything else with the message. It...
Truvo Cyber is a Canadian cybersecurity firm that performs independent ISO 27001 internal audits for companies preparing for a certification audit or...
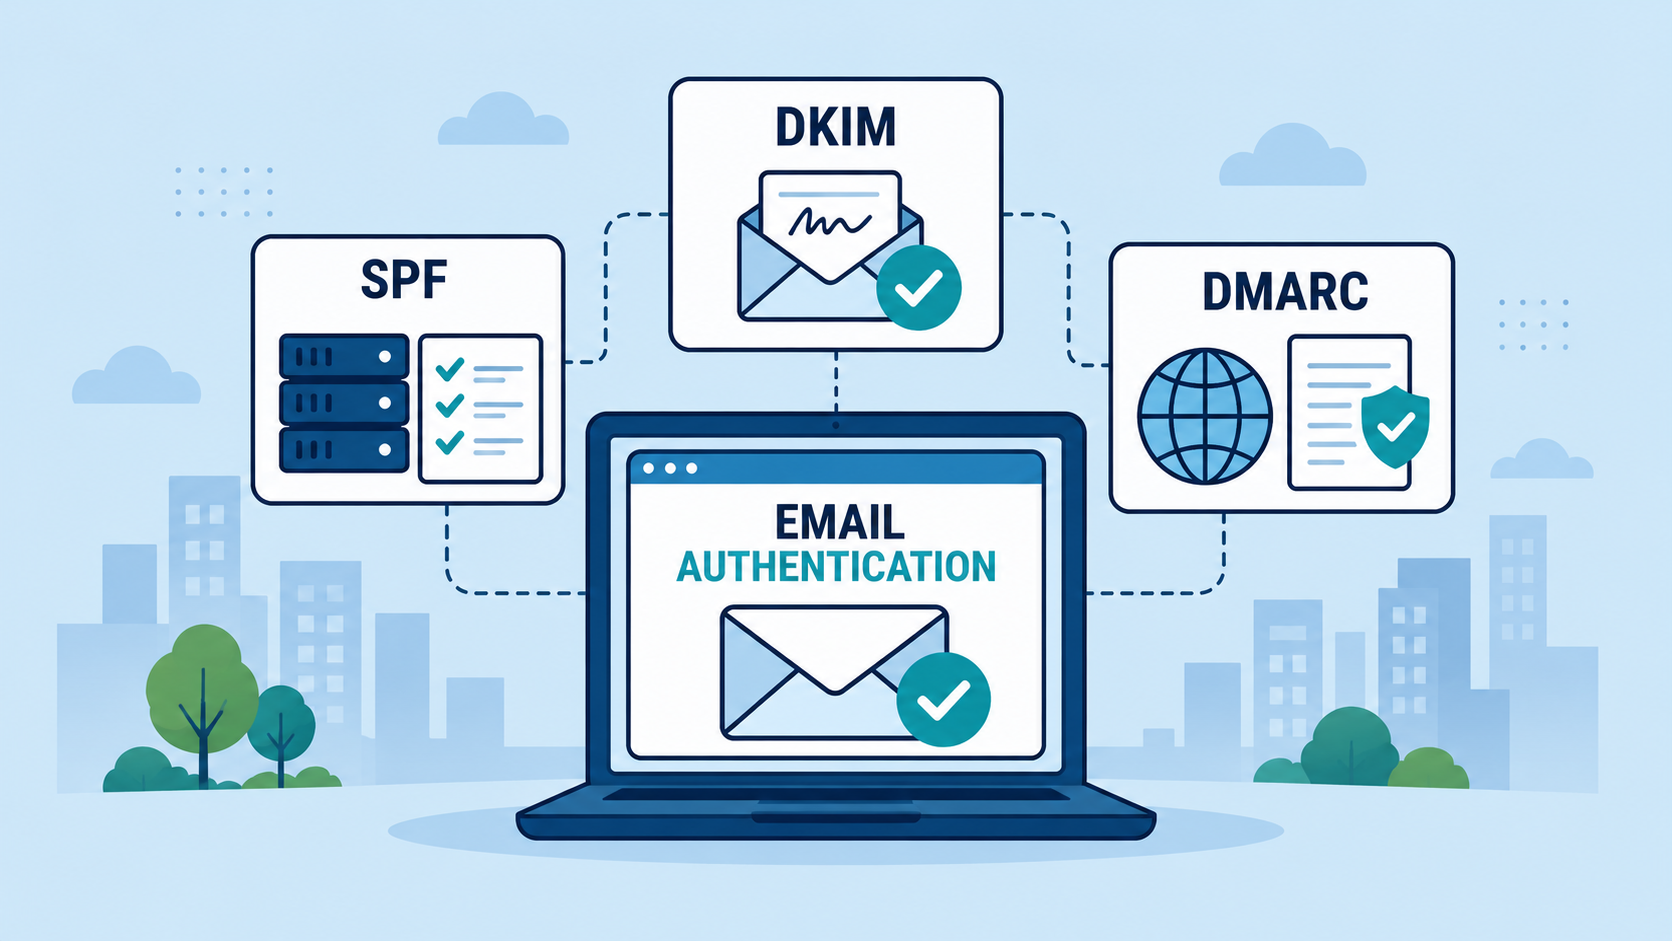
SPF, DKIM and DMARC work as a team to stop attackers from sending email that looks like it comes from a domain they do not control. SPF checks...
DNSSEC (the DNS Security Extensions) signs DNS records so a validating resolver can prove an answer came from the zone owner and was not altered; it...
DKIM (DomainKeys Identified Mail) lets a domain sign its outgoing mail with a private key and publish the matching public key in DNS, so a receiving...
BIMI (Brand Indicators for Message Identification) is a DNS TXT record, published at default._bimi.yourdomain.com, that lets participating mailbox...
An SPF record is a DNS TXT record, published at a domain and starting with v=spf1, that lists the IP addresses and services allowed to send email...
DMARC (Domain-based Message Authentication, Reporting and Conformance) is a DNS TXT record, published at _dmarc.yourdomain.com, that tells receiving...
ISO 27001 A.5.7 requires an organization to collect and analyze information about information security threats, turn it into threat intelligence, and...
ISO 27001 A.5.18 requires that access rights to information and systems are provisioned, reviewed, modified, and removed across the whole lifecycle,...
ISO 27001 A.5.17 requires that authentication information, the passwords, keys, tokens, and secrets people and systems use to prove identity, is...
ISO 27001 A.5.16 requires an organization to manage the full life cycle of identities, for both people and non-human accounts, from creation through...
ISO 27001 A.8.3 requires that access to information and application functions is restricted in line with the access control policy, enforced at the...
ISO 27001 A.8.12 requires data leakage prevention measures on the systems, networks, and devices that handle sensitive information, so that data...
ISO 27001 A.8.1 requires that information stored on, processed by, or accessible through user endpoint devices, meaning laptops, desktops, phones,...
ISO 27001 A.8.4 requires that read and write access to source code, development tools, and software libraries is restricted to what a person needs...
To satisfy ISO 27001 A.8.28, apply secure coding principles to how your team writes software: adopt language-specific coding standards, plan security...
To satisfy ISO 27001 A.8.25, write down the rules that govern how your team builds software, then apply them consistently across the whole life...
ISO 27001 A.8.24 requires a policy on the use of cryptography, including key management, applied according to risk rather than encrypting everything...
ISO 27001 A.8.13 requires that backup copies of information, software, and systems are maintained and tested against an agreed backup policy. It is a...
ISO 27001 A.8.7 requires that protection against malware is implemented and backed by appropriate user awareness across every system that runs code....