SOC 2CI/CDChange Management


On paper, DIY compliance looks straightforward. Subscribe to a GRC platform, follow the control library, collect evidence, engage an auditor. The...
Most SOC 2 consultants know AWS. Some know Azure and GCP. Very few know what to do when your stack includes a colocation facility, a bare-metal fleet...
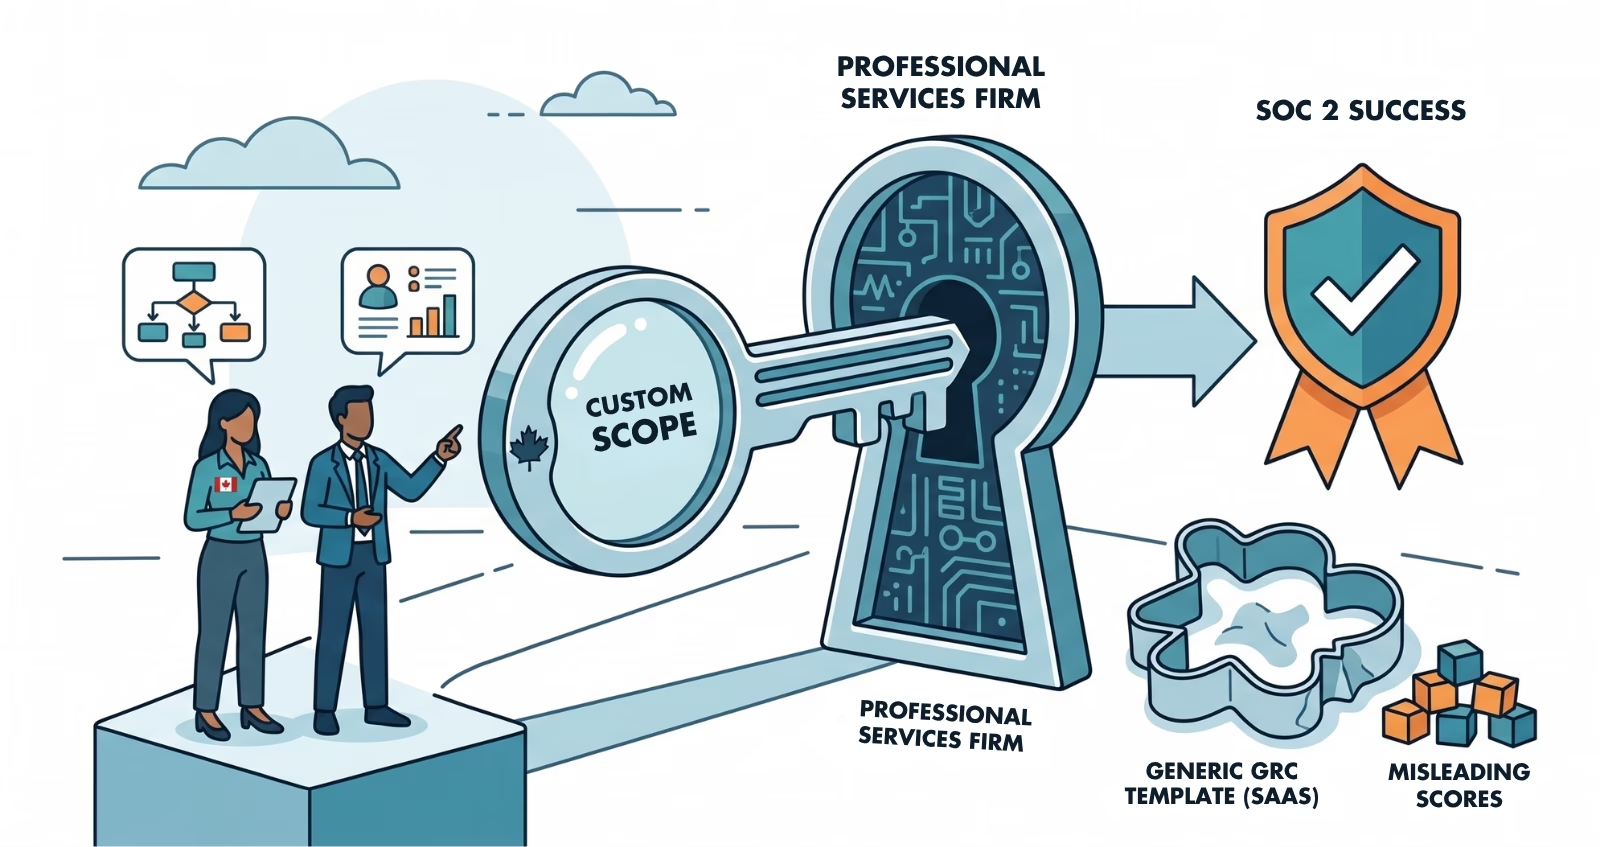
A professional services firm starts its SOC 2 process the same way most companies do. An enterprise client puts it in an RFP. The team subscribes to...
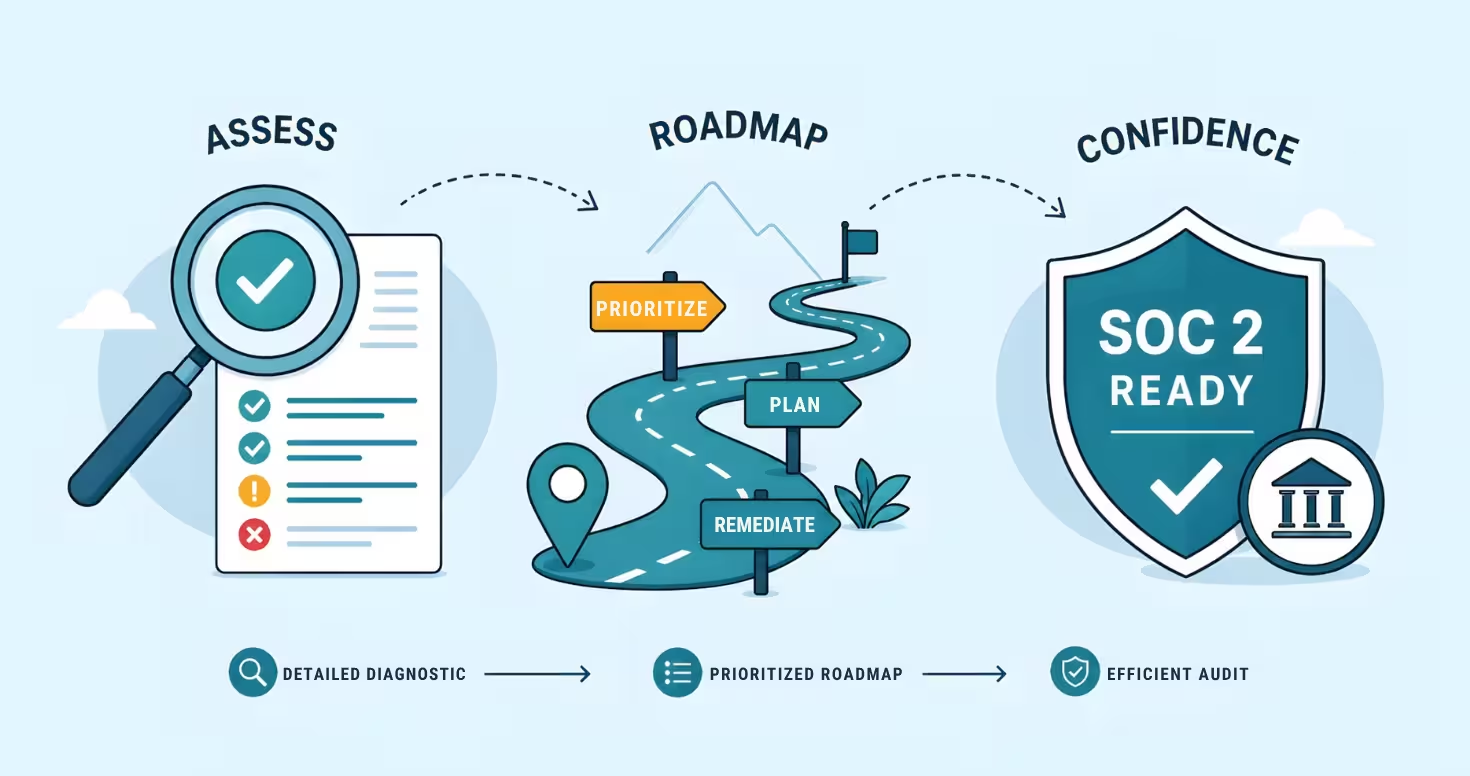
A SOC 2 readiness assessment is not the audit. It is the diagnostic step that tells a company exactly where it stands before committing budget and...
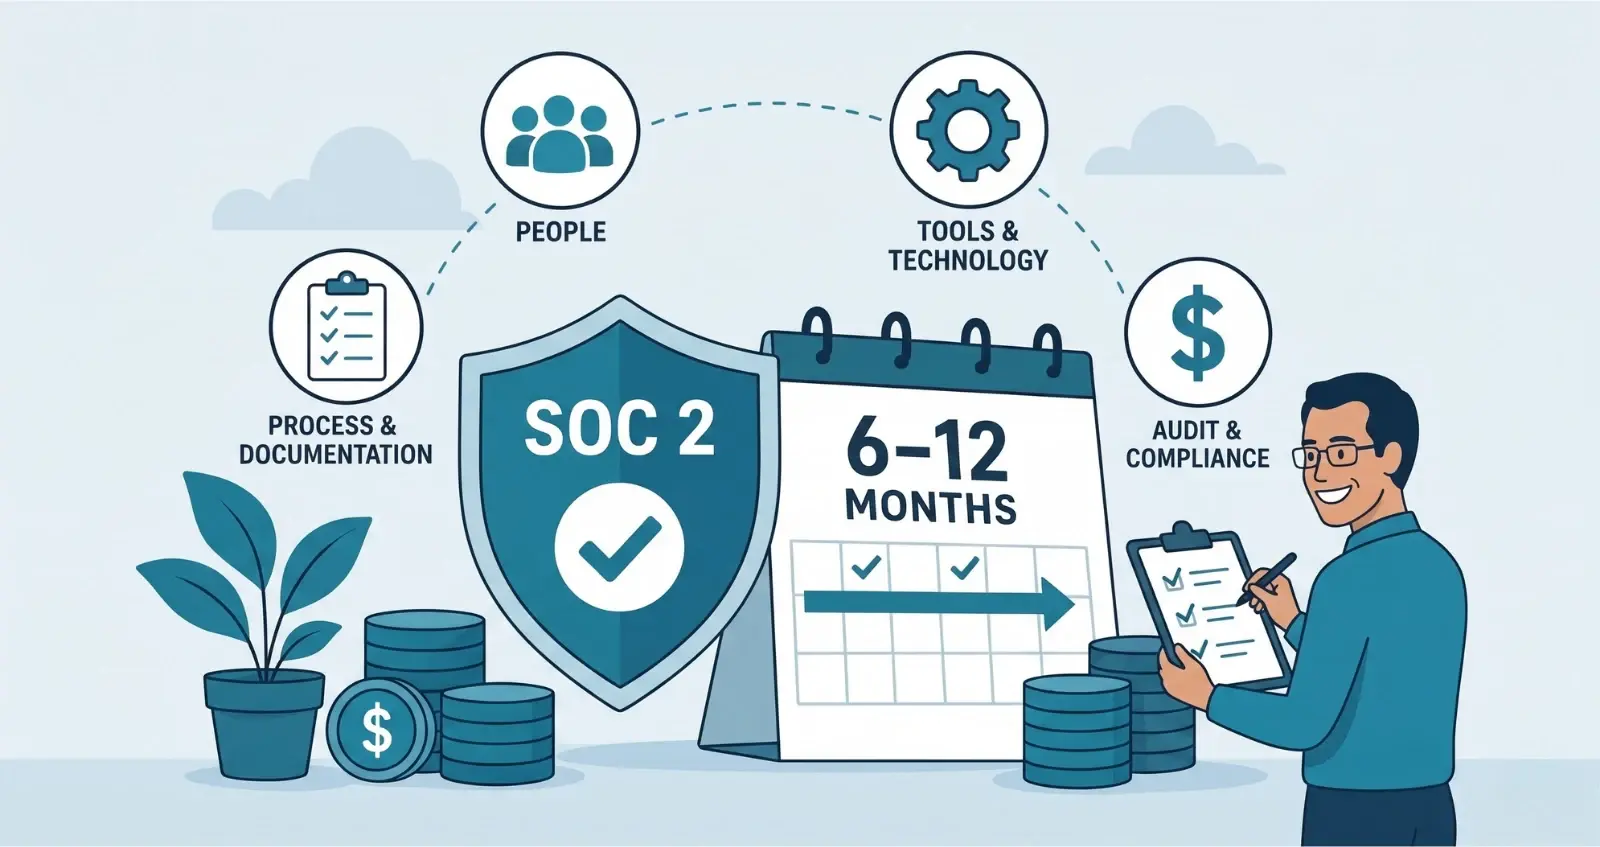
SOC 2 has four cost components. Most companies only budget for two of them, then get surprised by the rest halfway through the engagement.
Published...
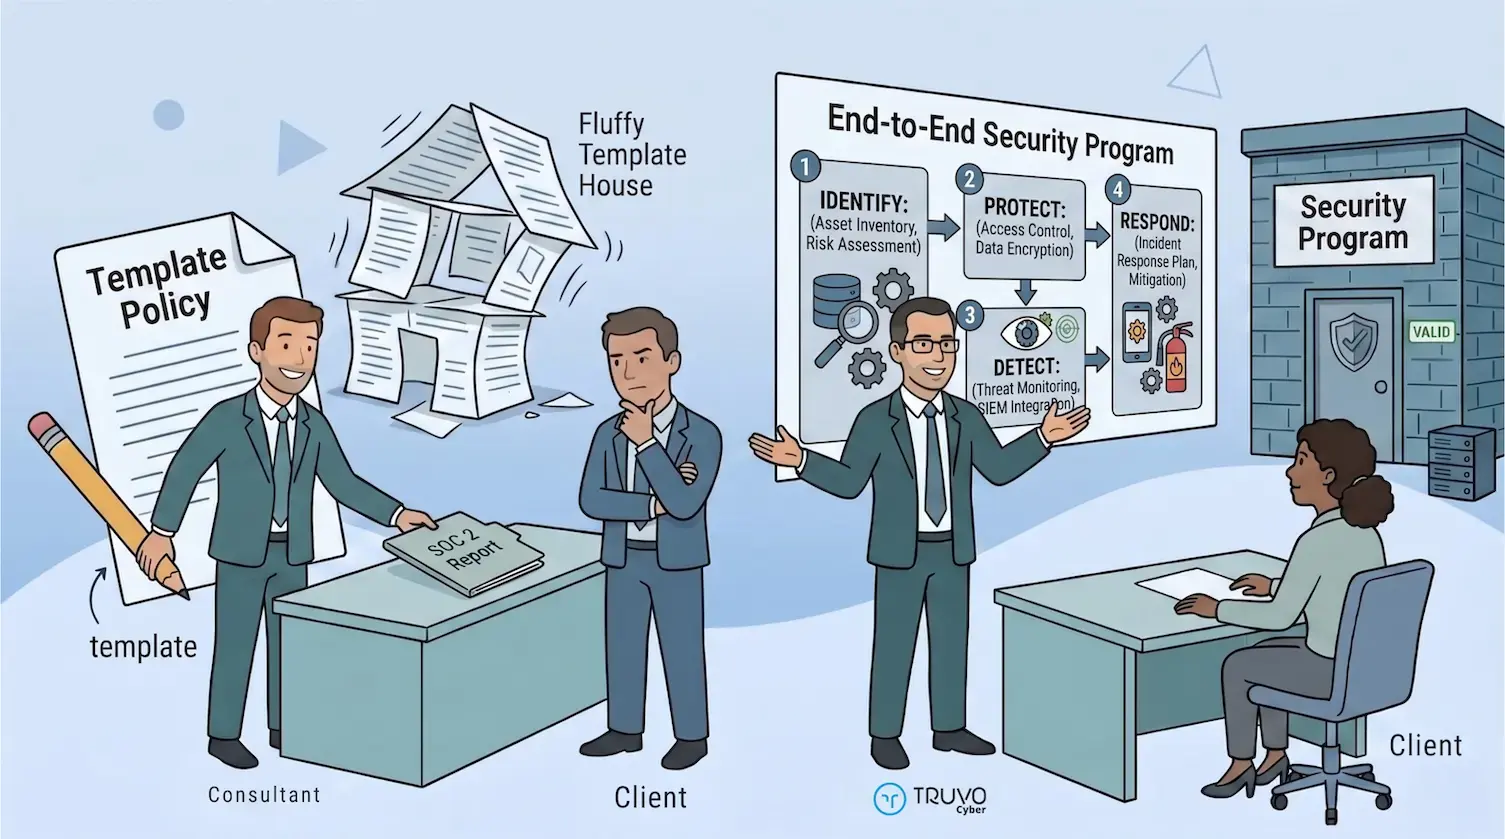
Platform-first firms compress the engagement into days or a few weeks. They take a policy template library, swap...
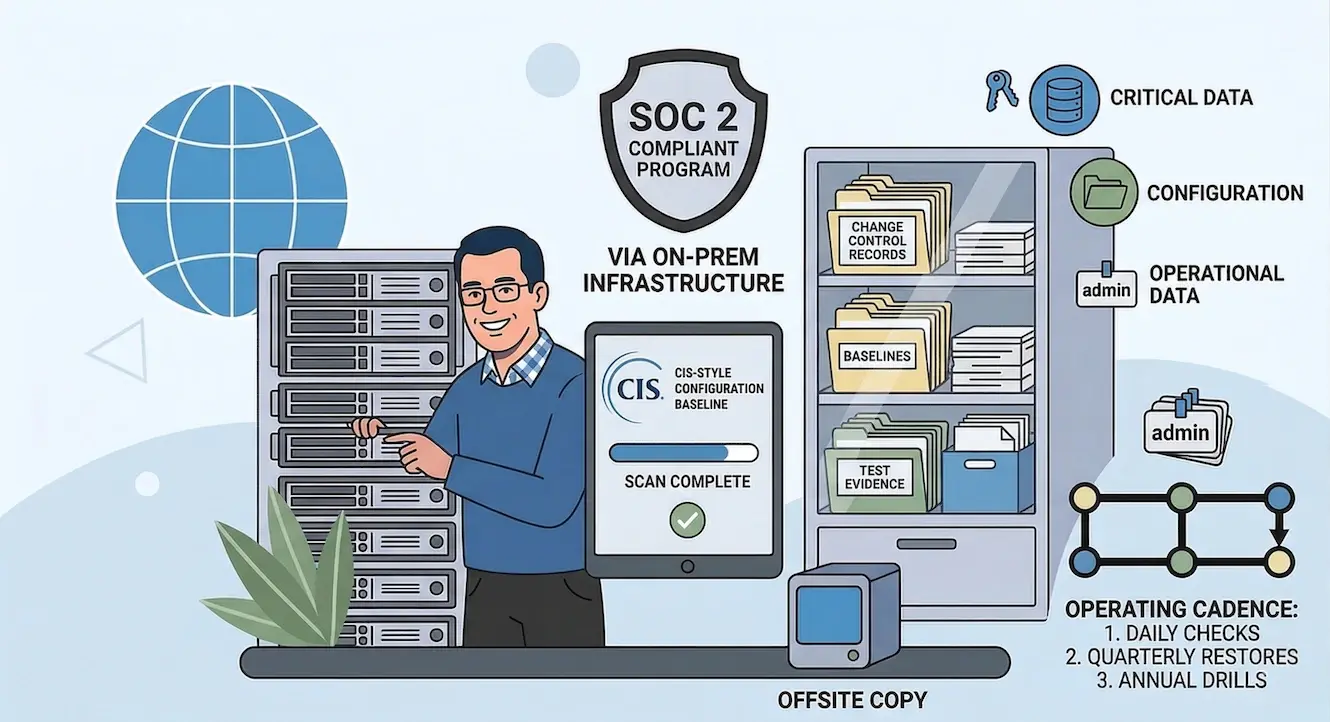
In cloud environments, configuration compliance is a toggle. Enable AWS Config, deploy a conformance pack, and the platform continuously evaluates...
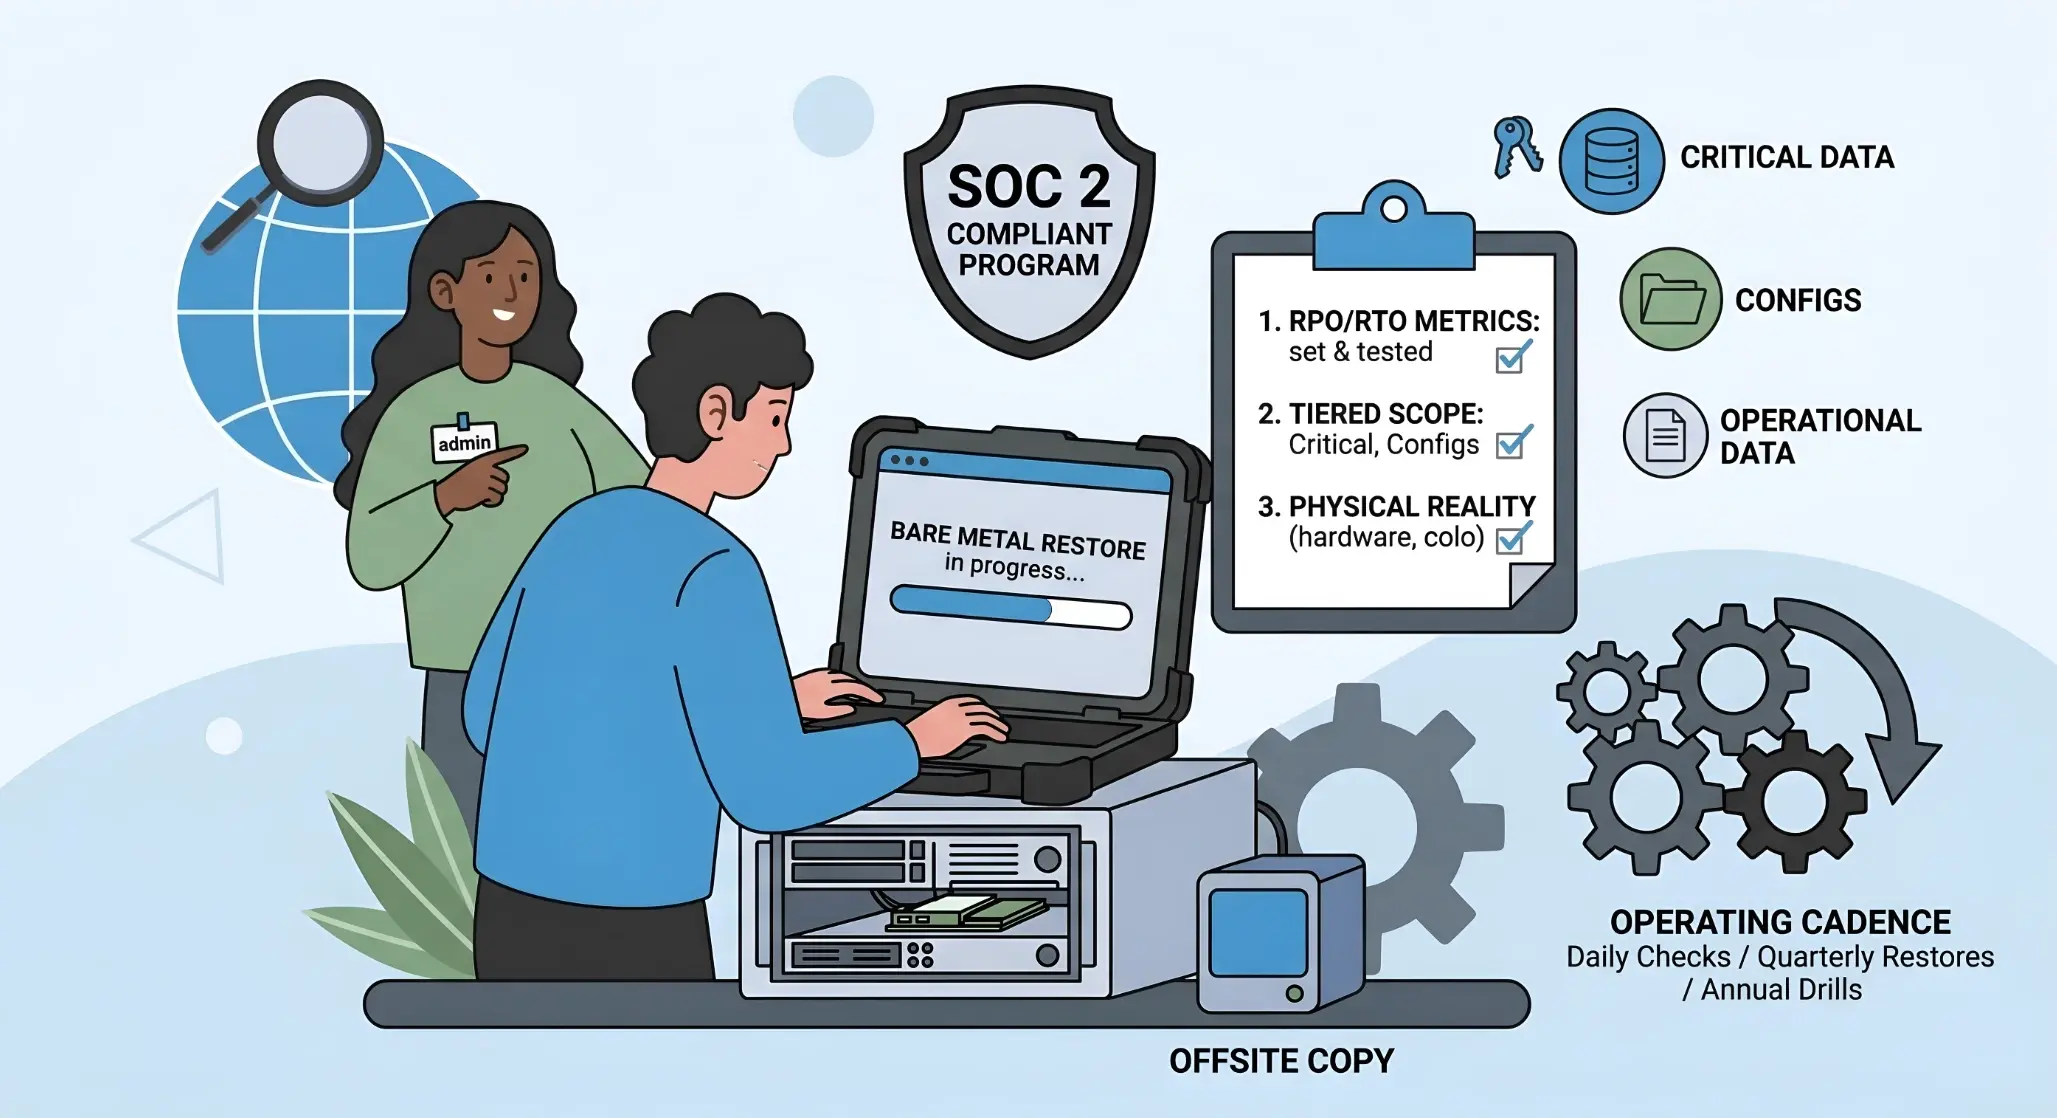
SOC 2 backup and disaster recovery for on-prem systems comes down to four things auditors check: backups that run and alert on failure, a copy stored...
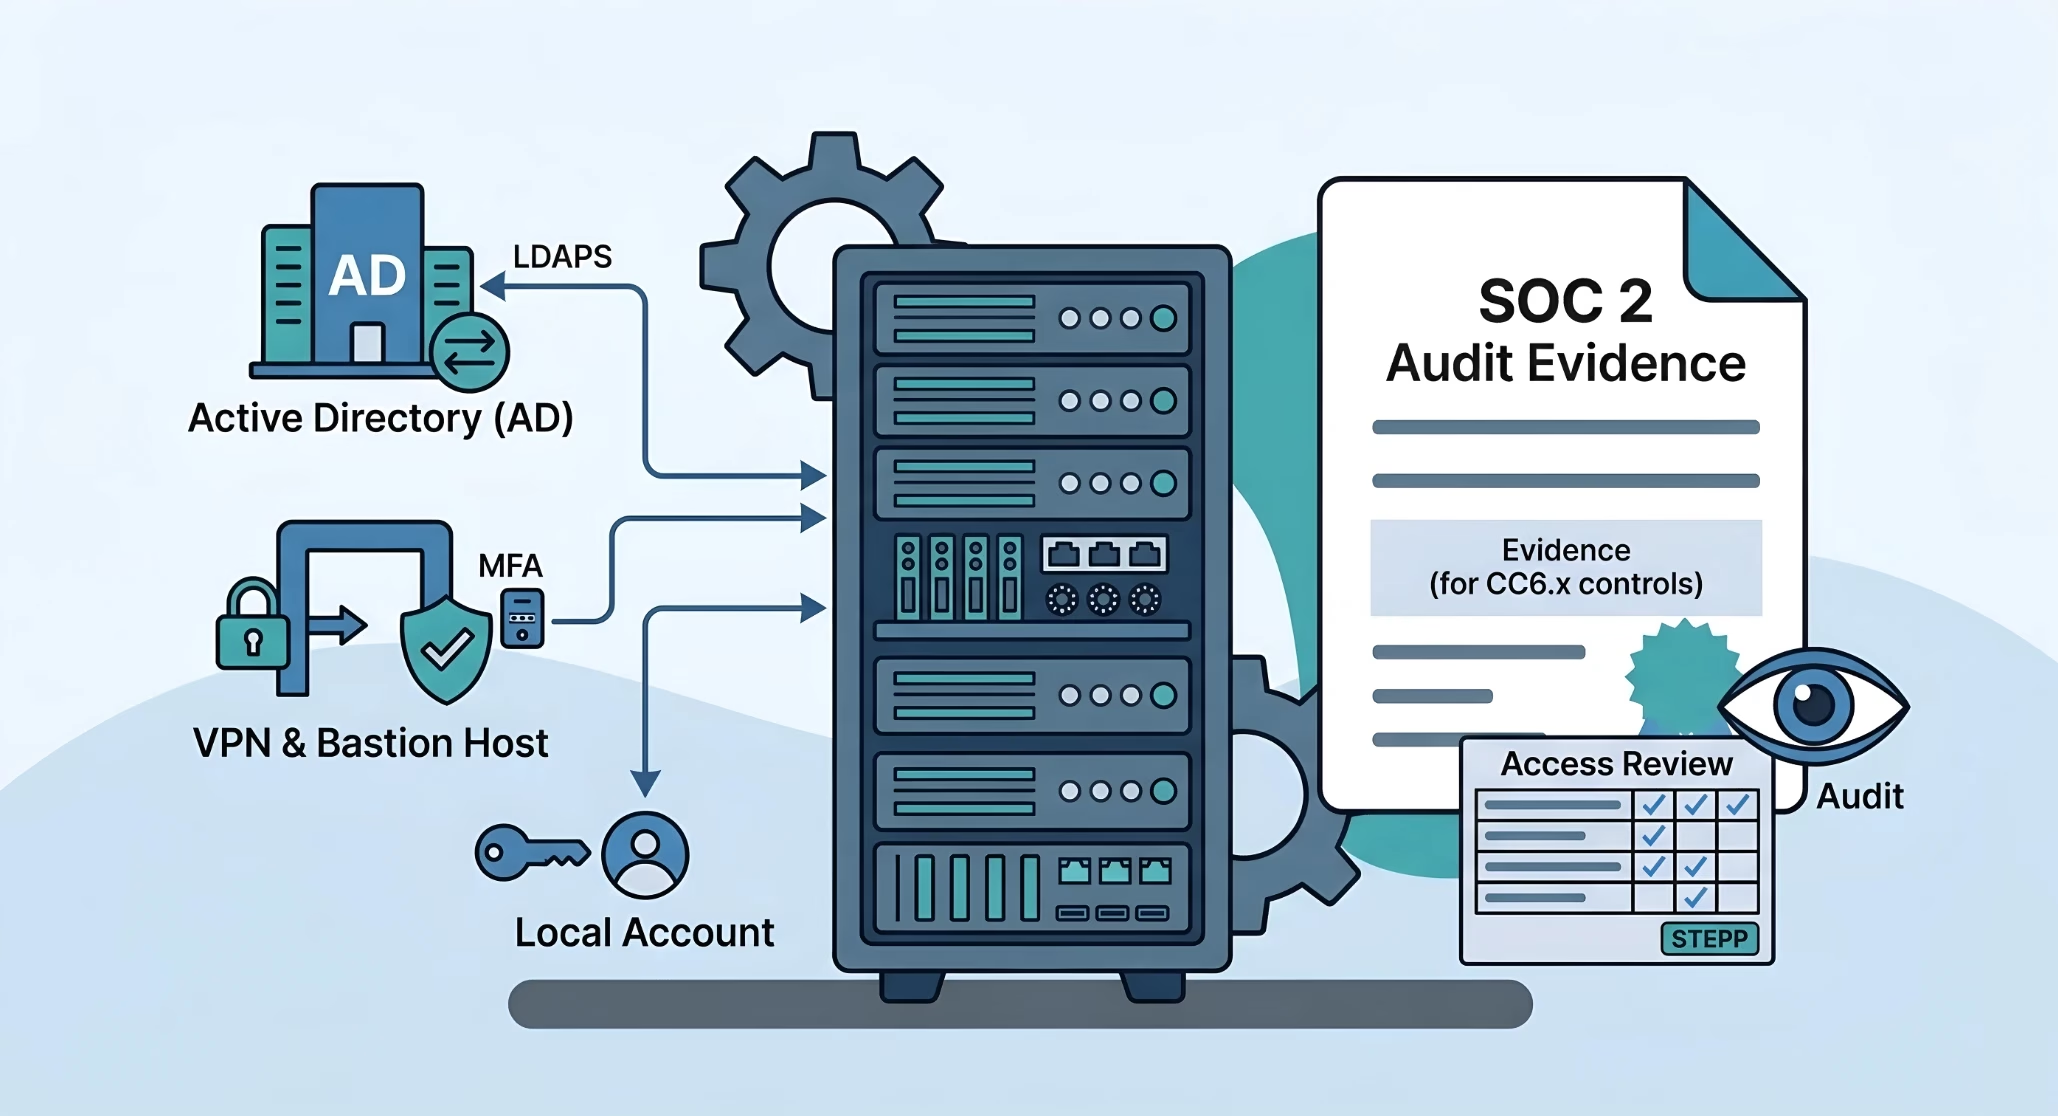
In cloud environments, access control is a managed service. AWS IAM provides centralized identity, Okta handles SSO across every SaaS tool, and the...
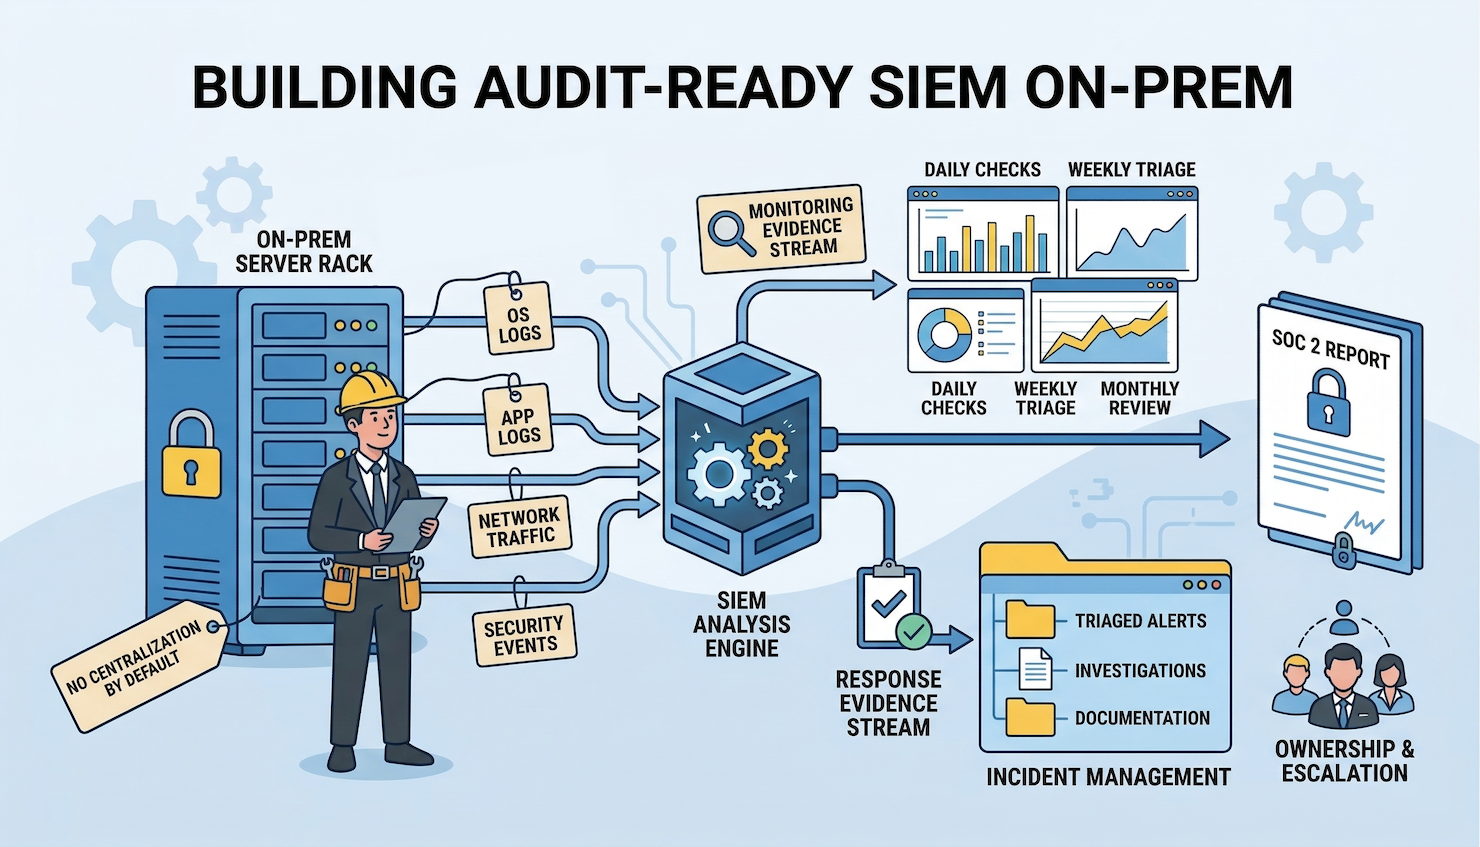
In a cloud environment, centralized logging is a toggle. Enable CloudTrail, turn on VPC Flow Logs, configure GuardDuty, and the compliance platform...
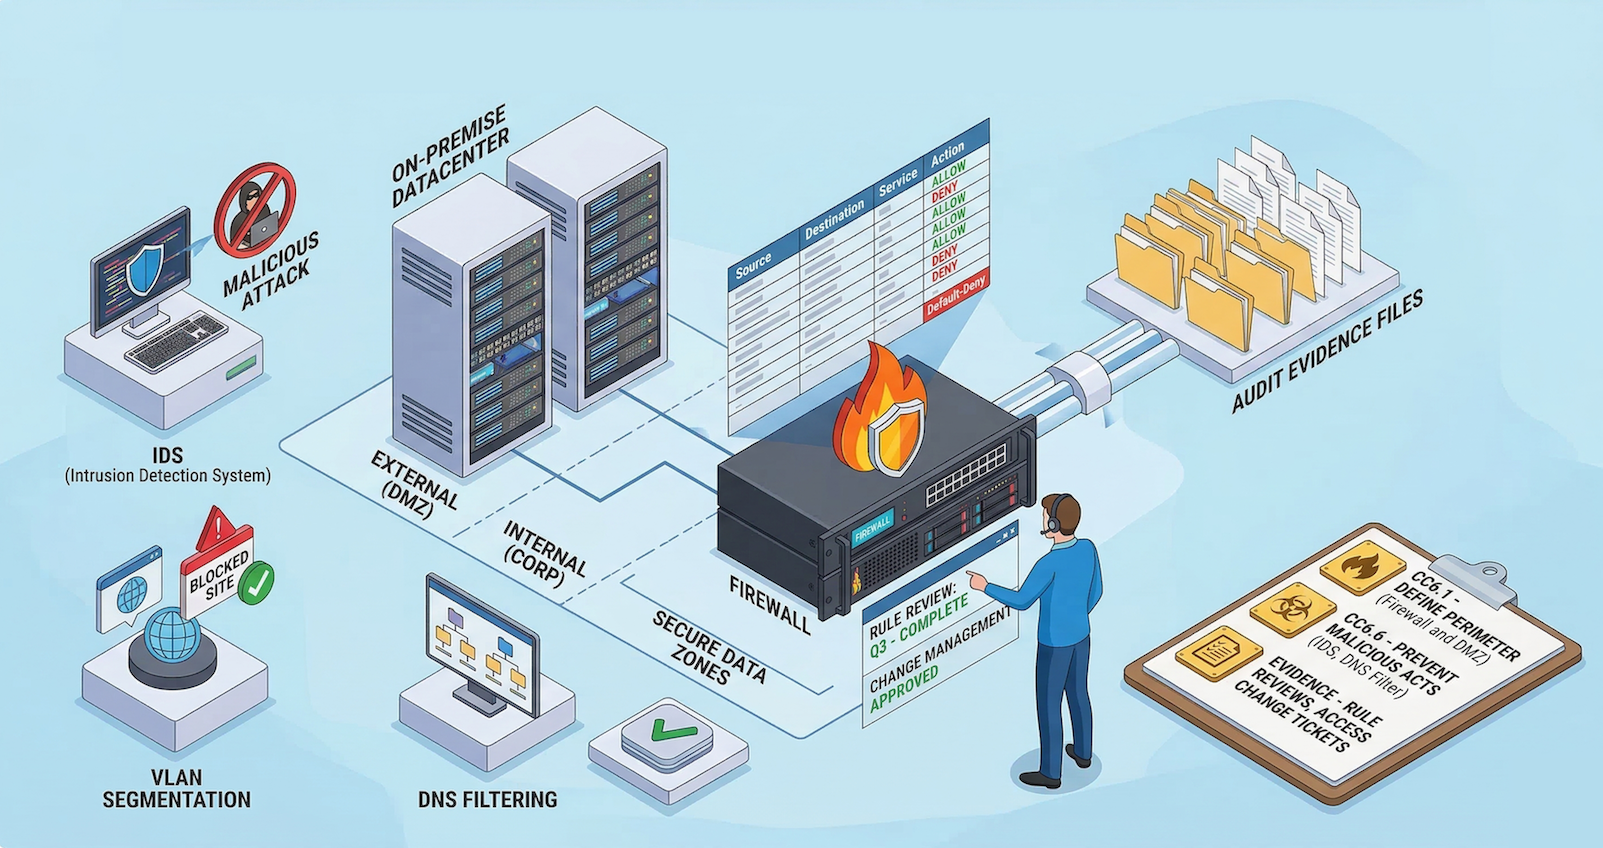
Every SOC 2 guide on network security assumes the infrastructure lives in AWS. The advice is always the same: configure security groups, enable VPC...
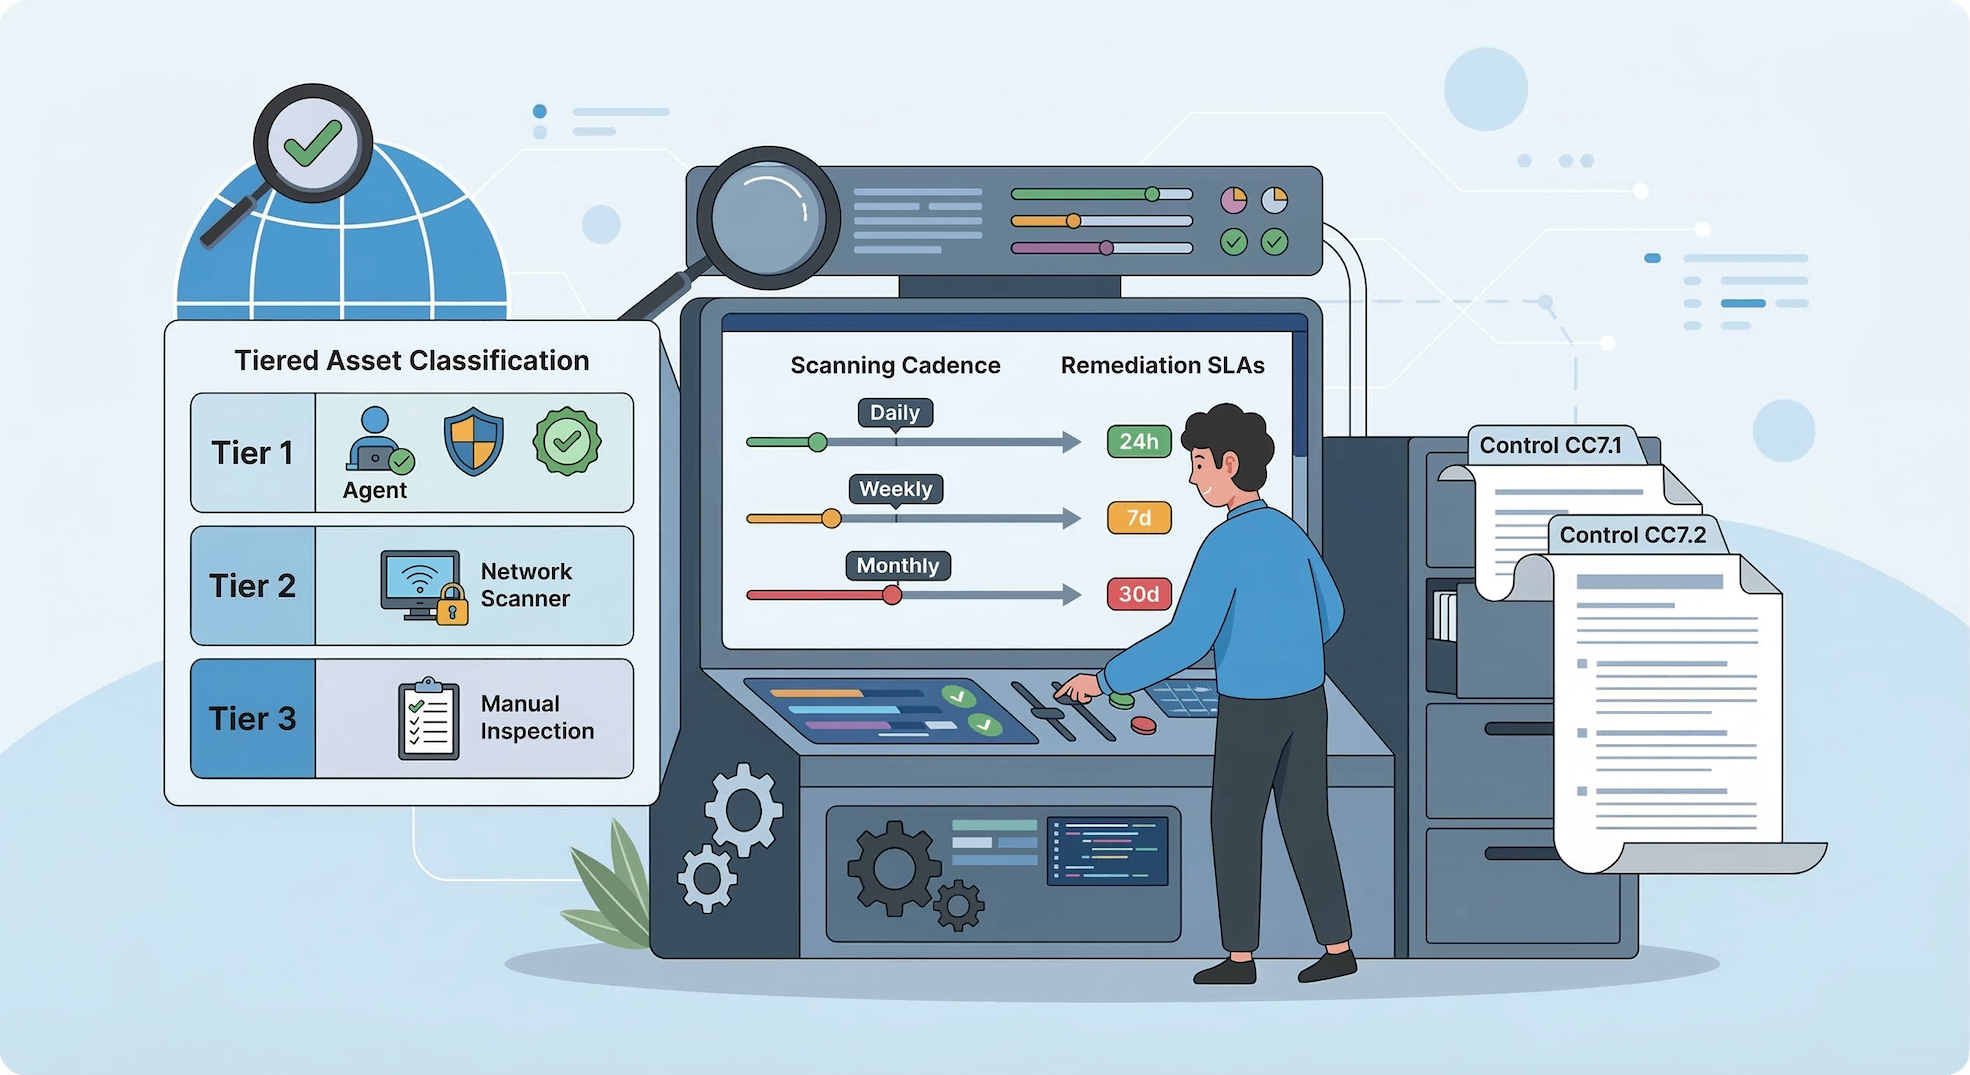
Every SOC 2 vulnerability scanning guide assumes the same starting point: connect a cloud-native scanner, enable automated assessments, and let the...
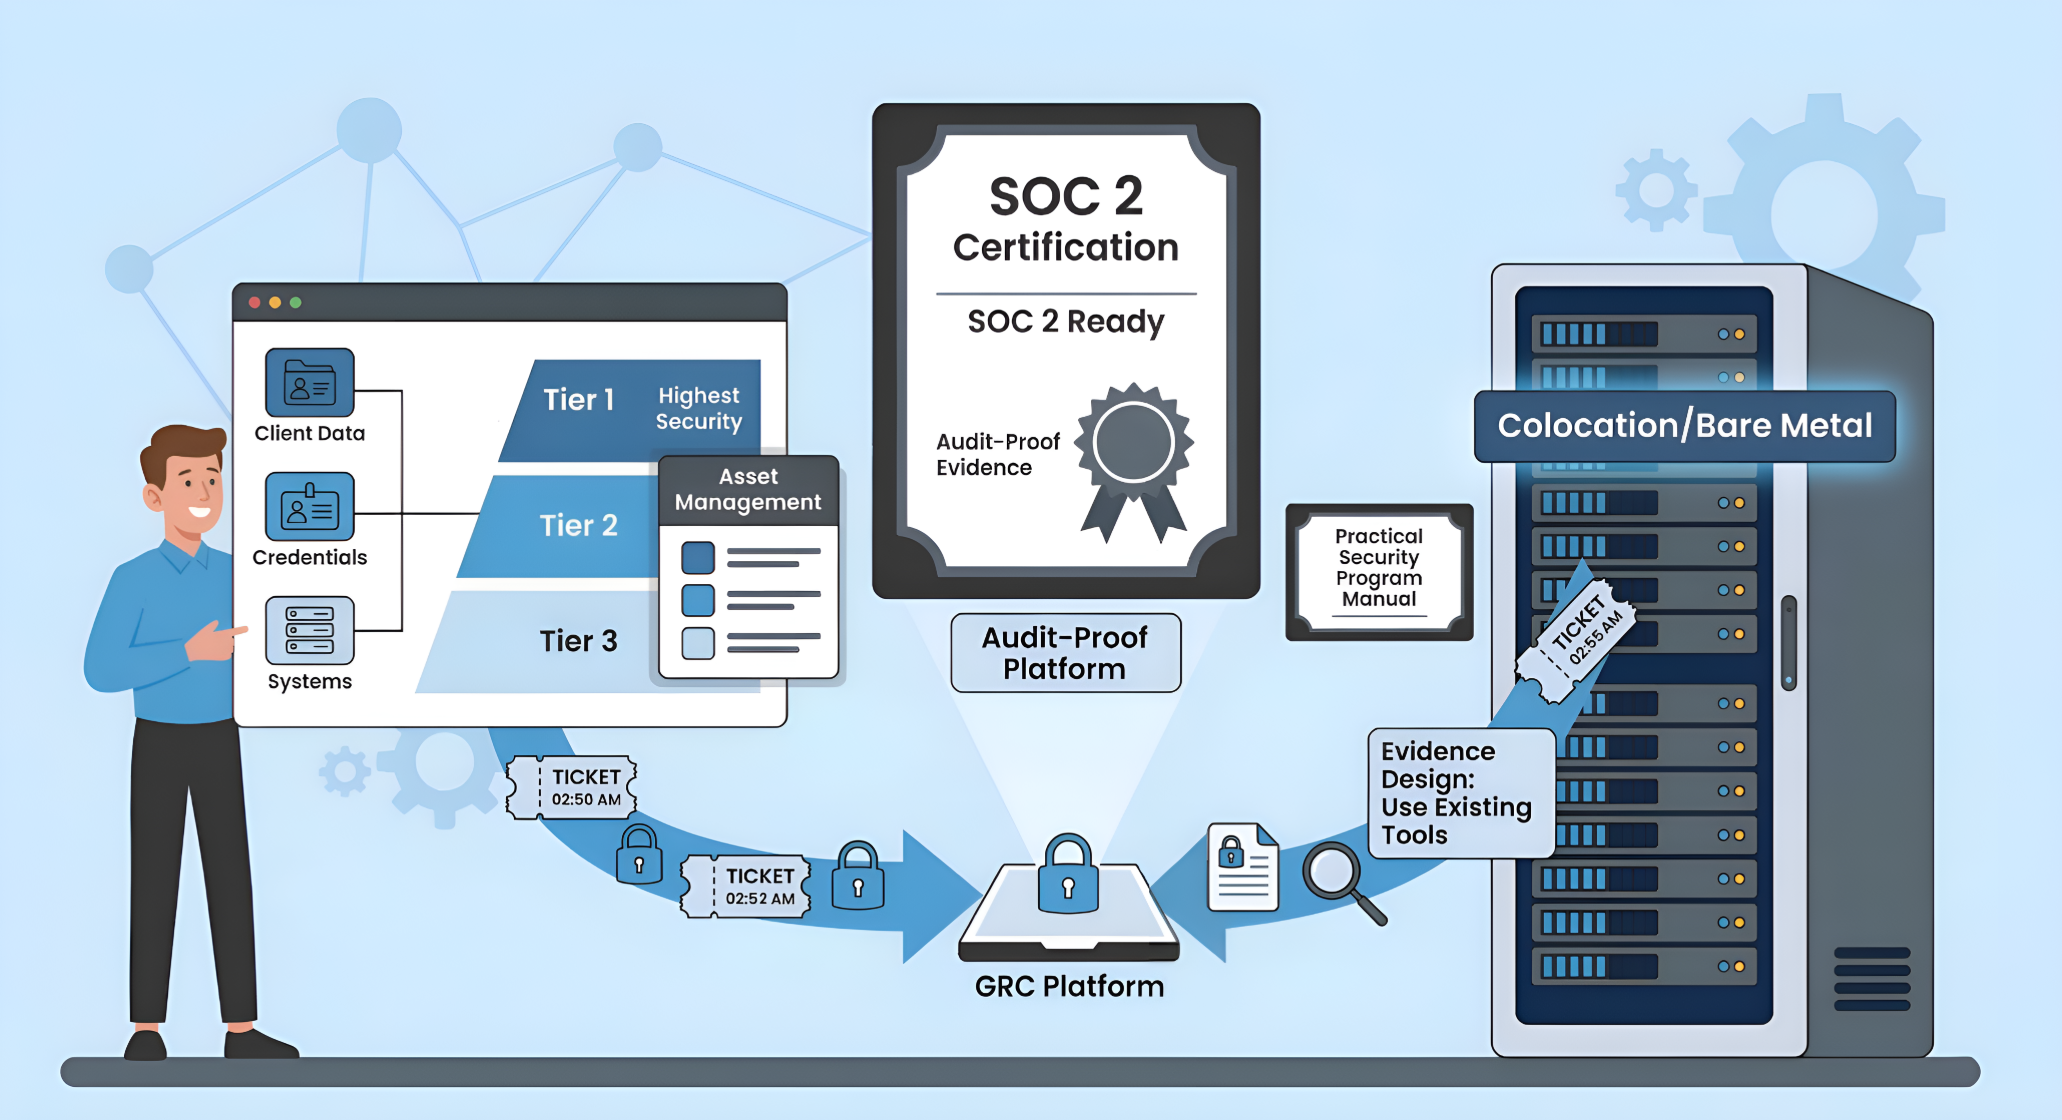
A pattern keeps showing up. A SaaS company that has been running successfully for years, sometimes a decade or more, gets a call from a major...
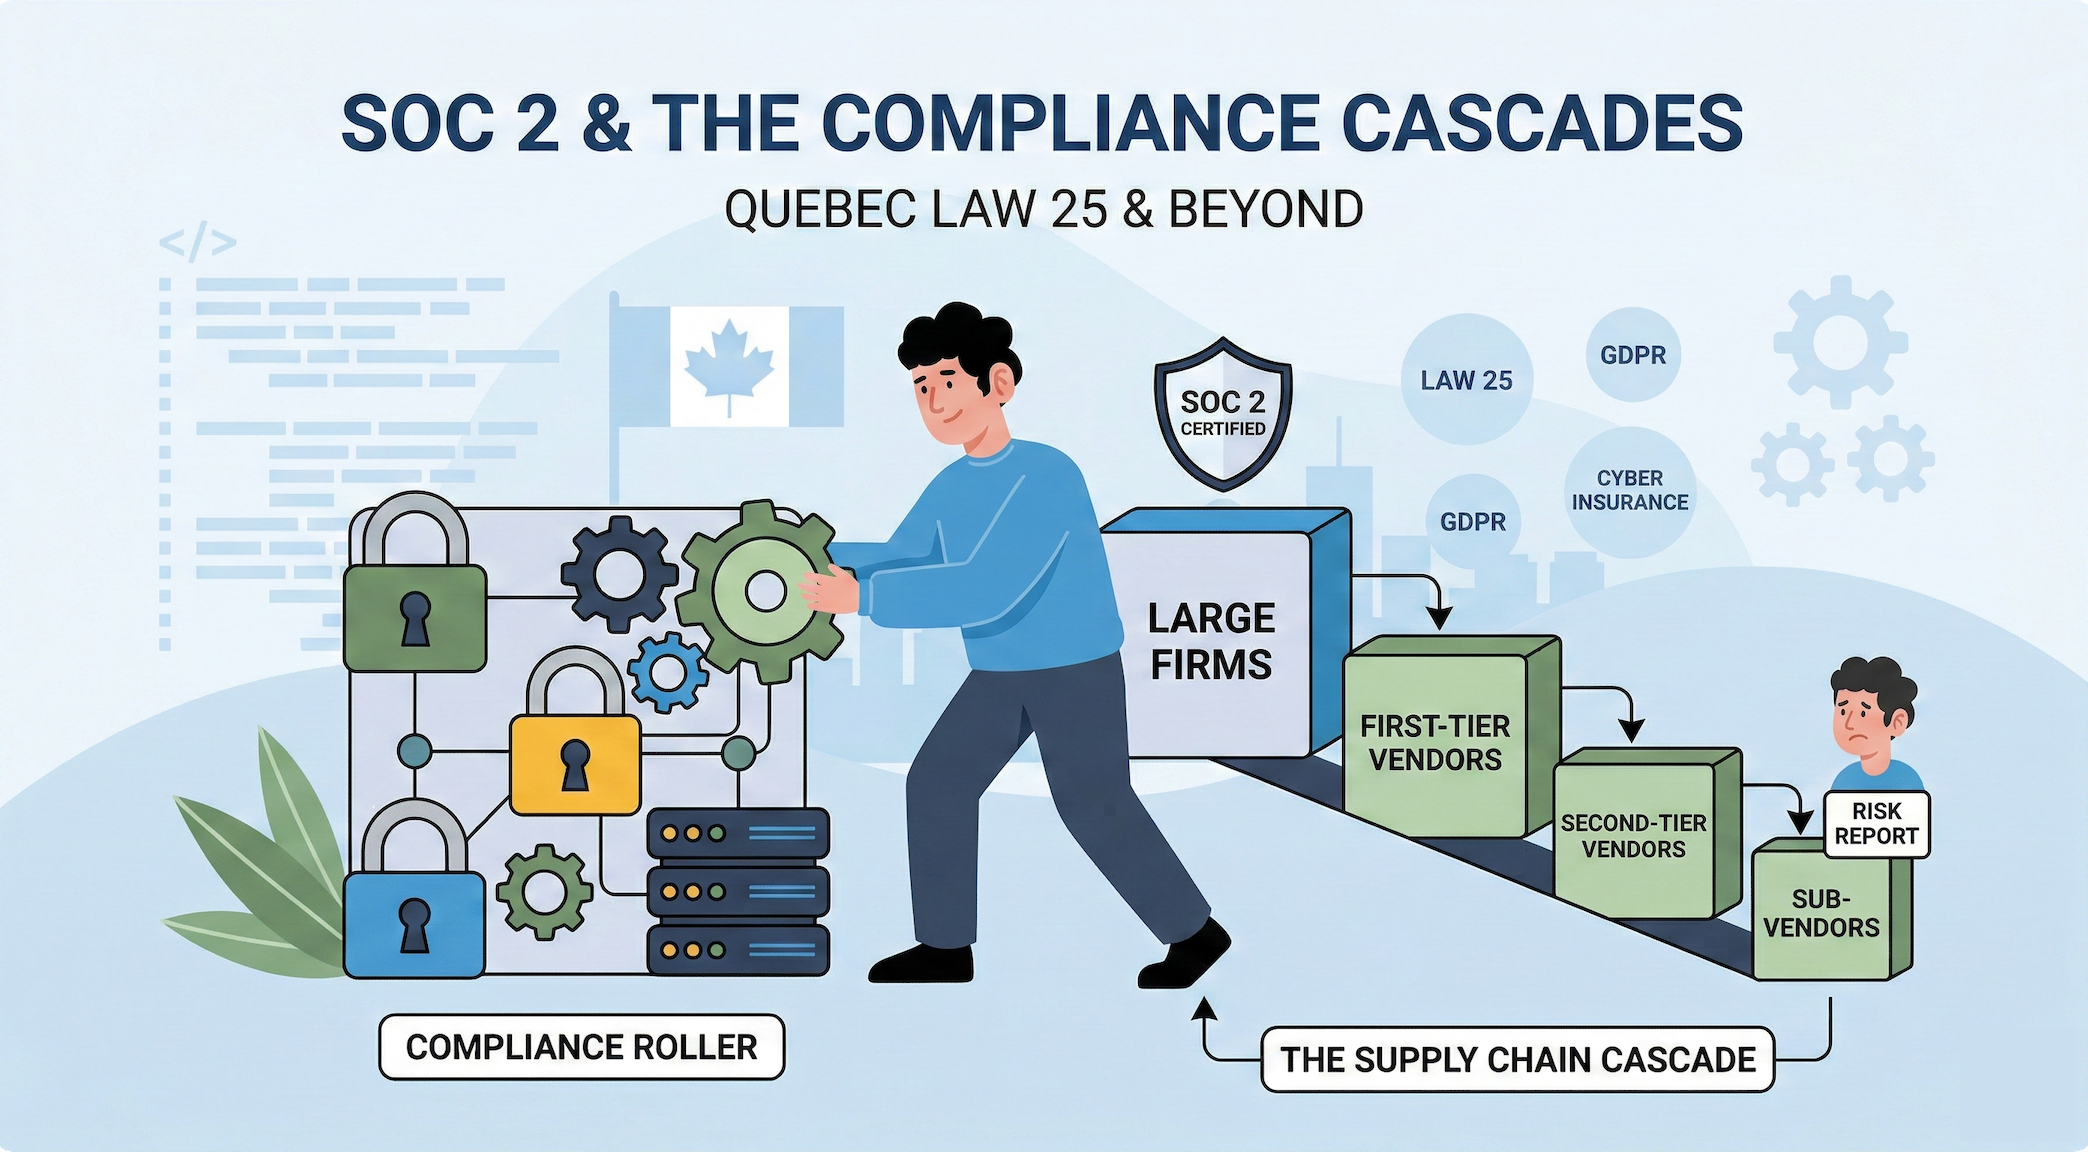
SOC 2, and compliance in general, is self-perpetuating. Once a company achieves certification, one of the first things the framework requires is...
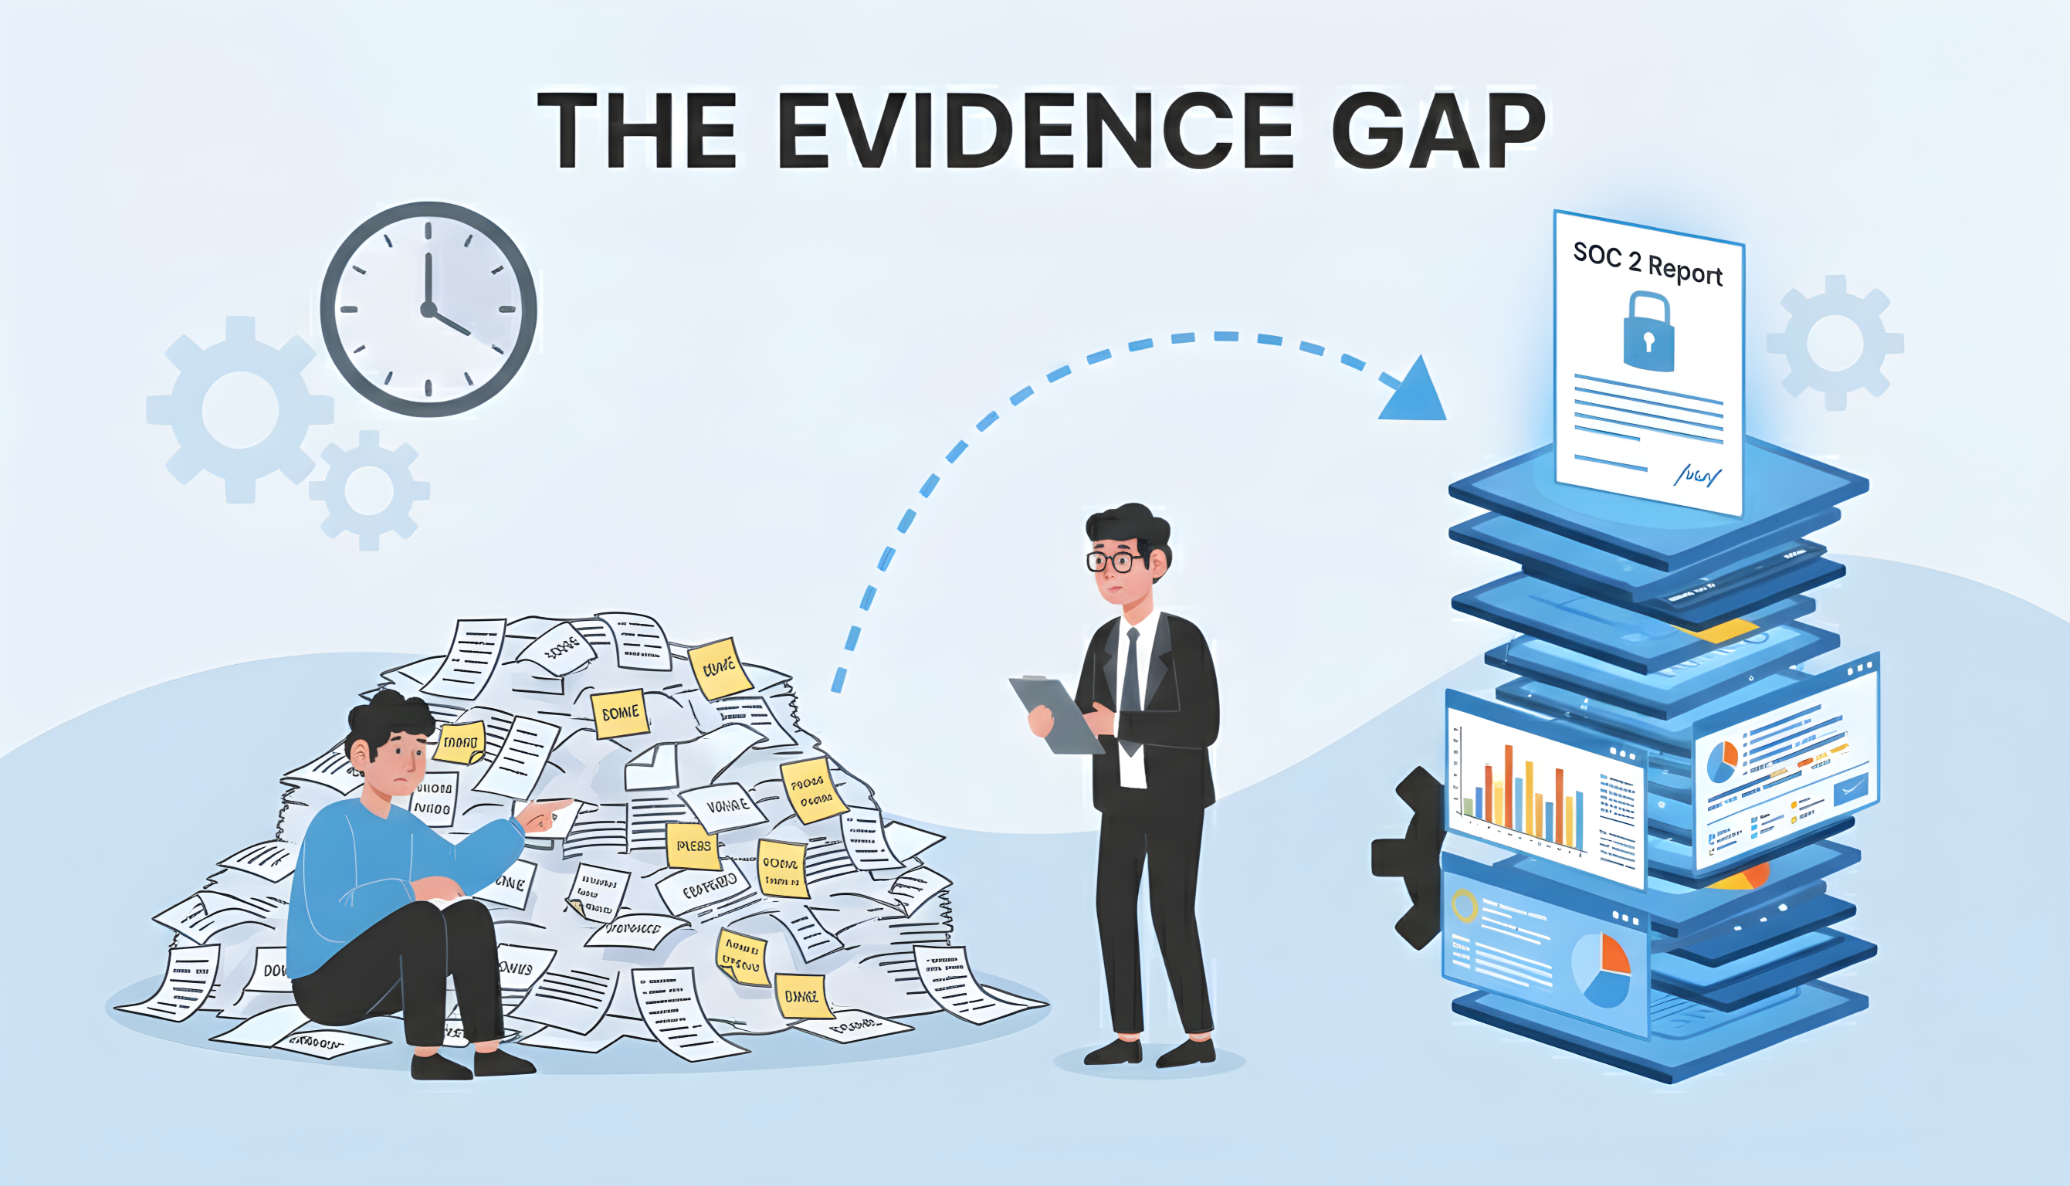
The most common compliance gap has nothing to do with missing controls. It's missing evidence.
What we see often is that technically competent teams...
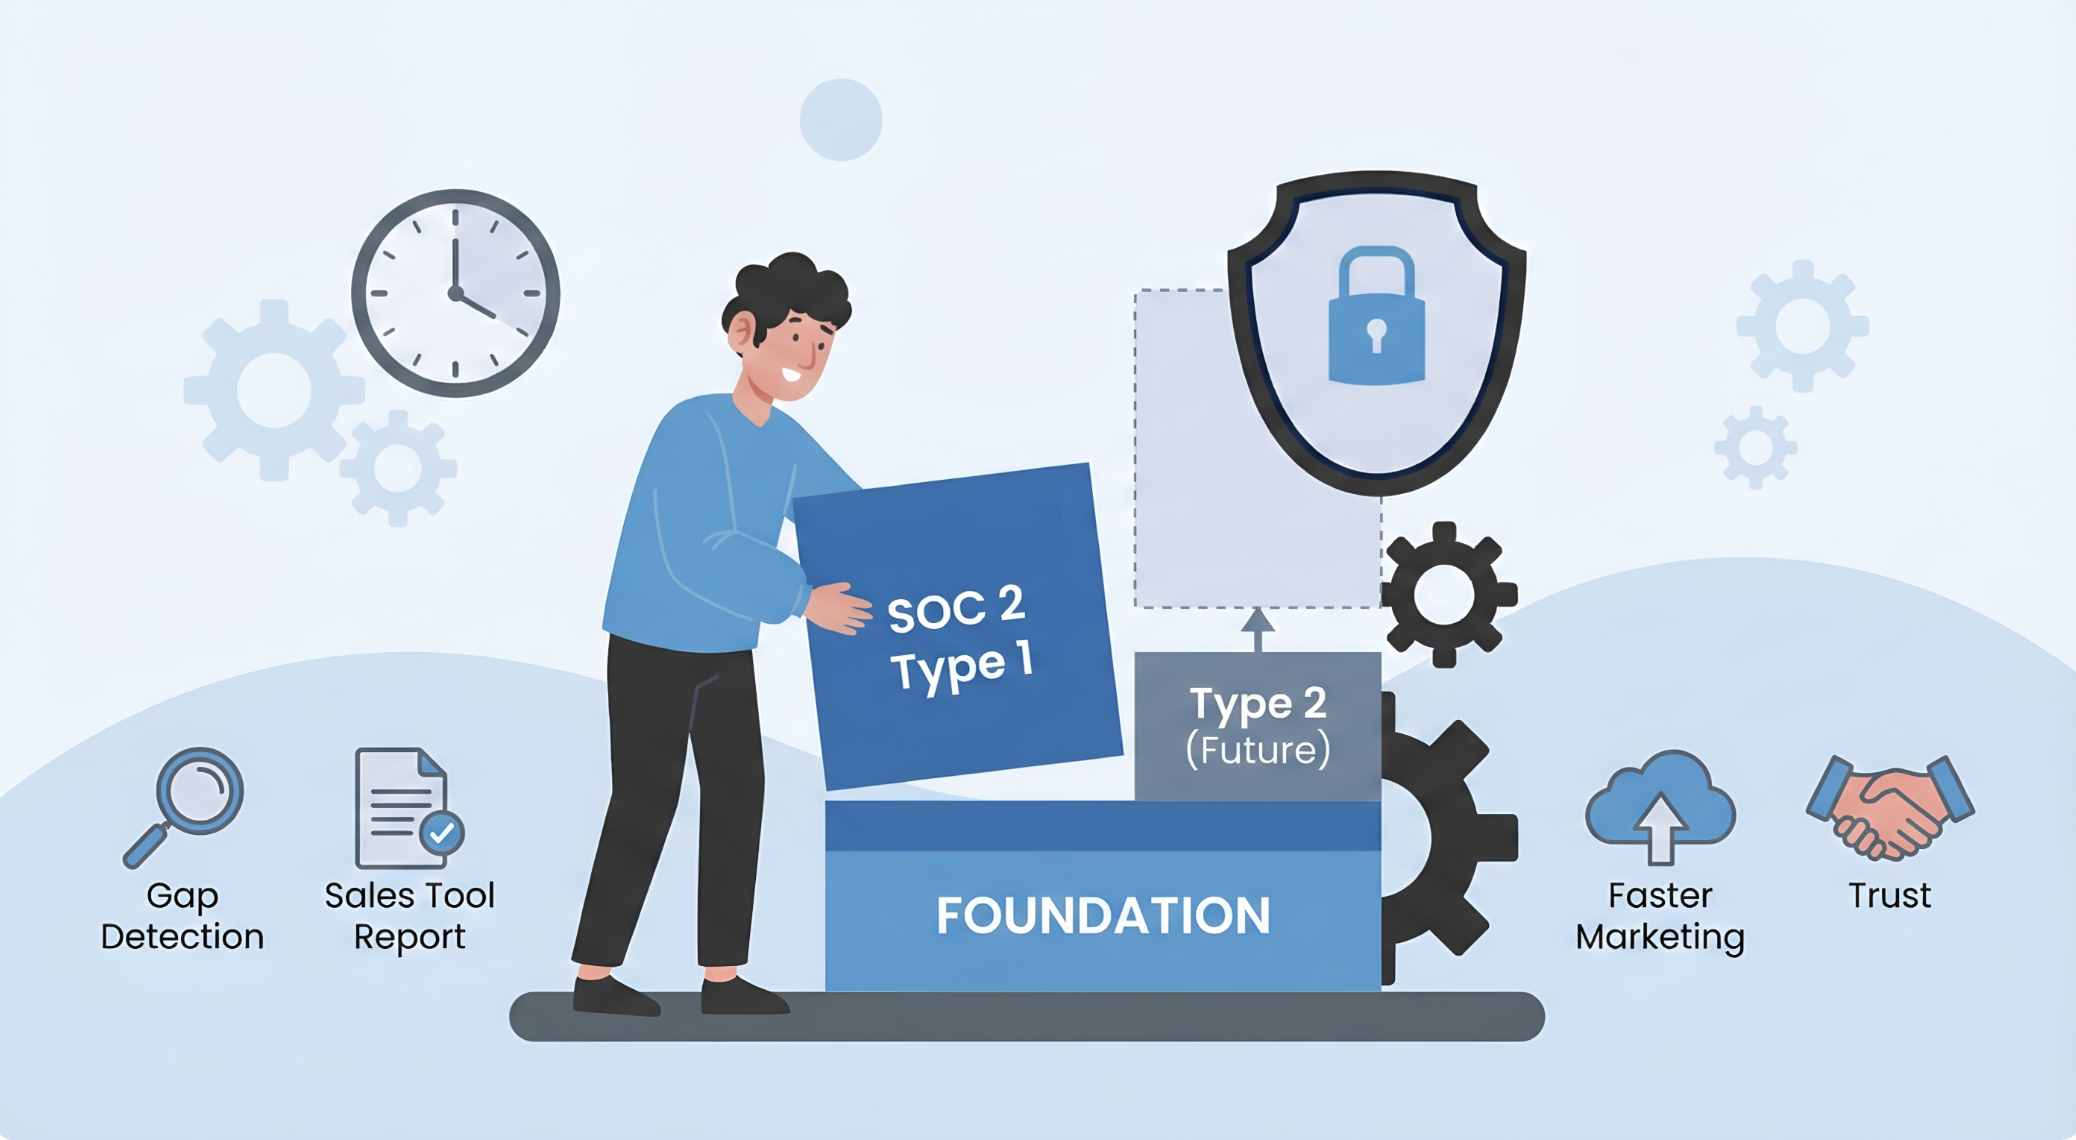
Most companies skip straight to Type 2. It's the *real* SOC 2, right? Type 1 is just not worth it. We used to think that way too. We've changed our...
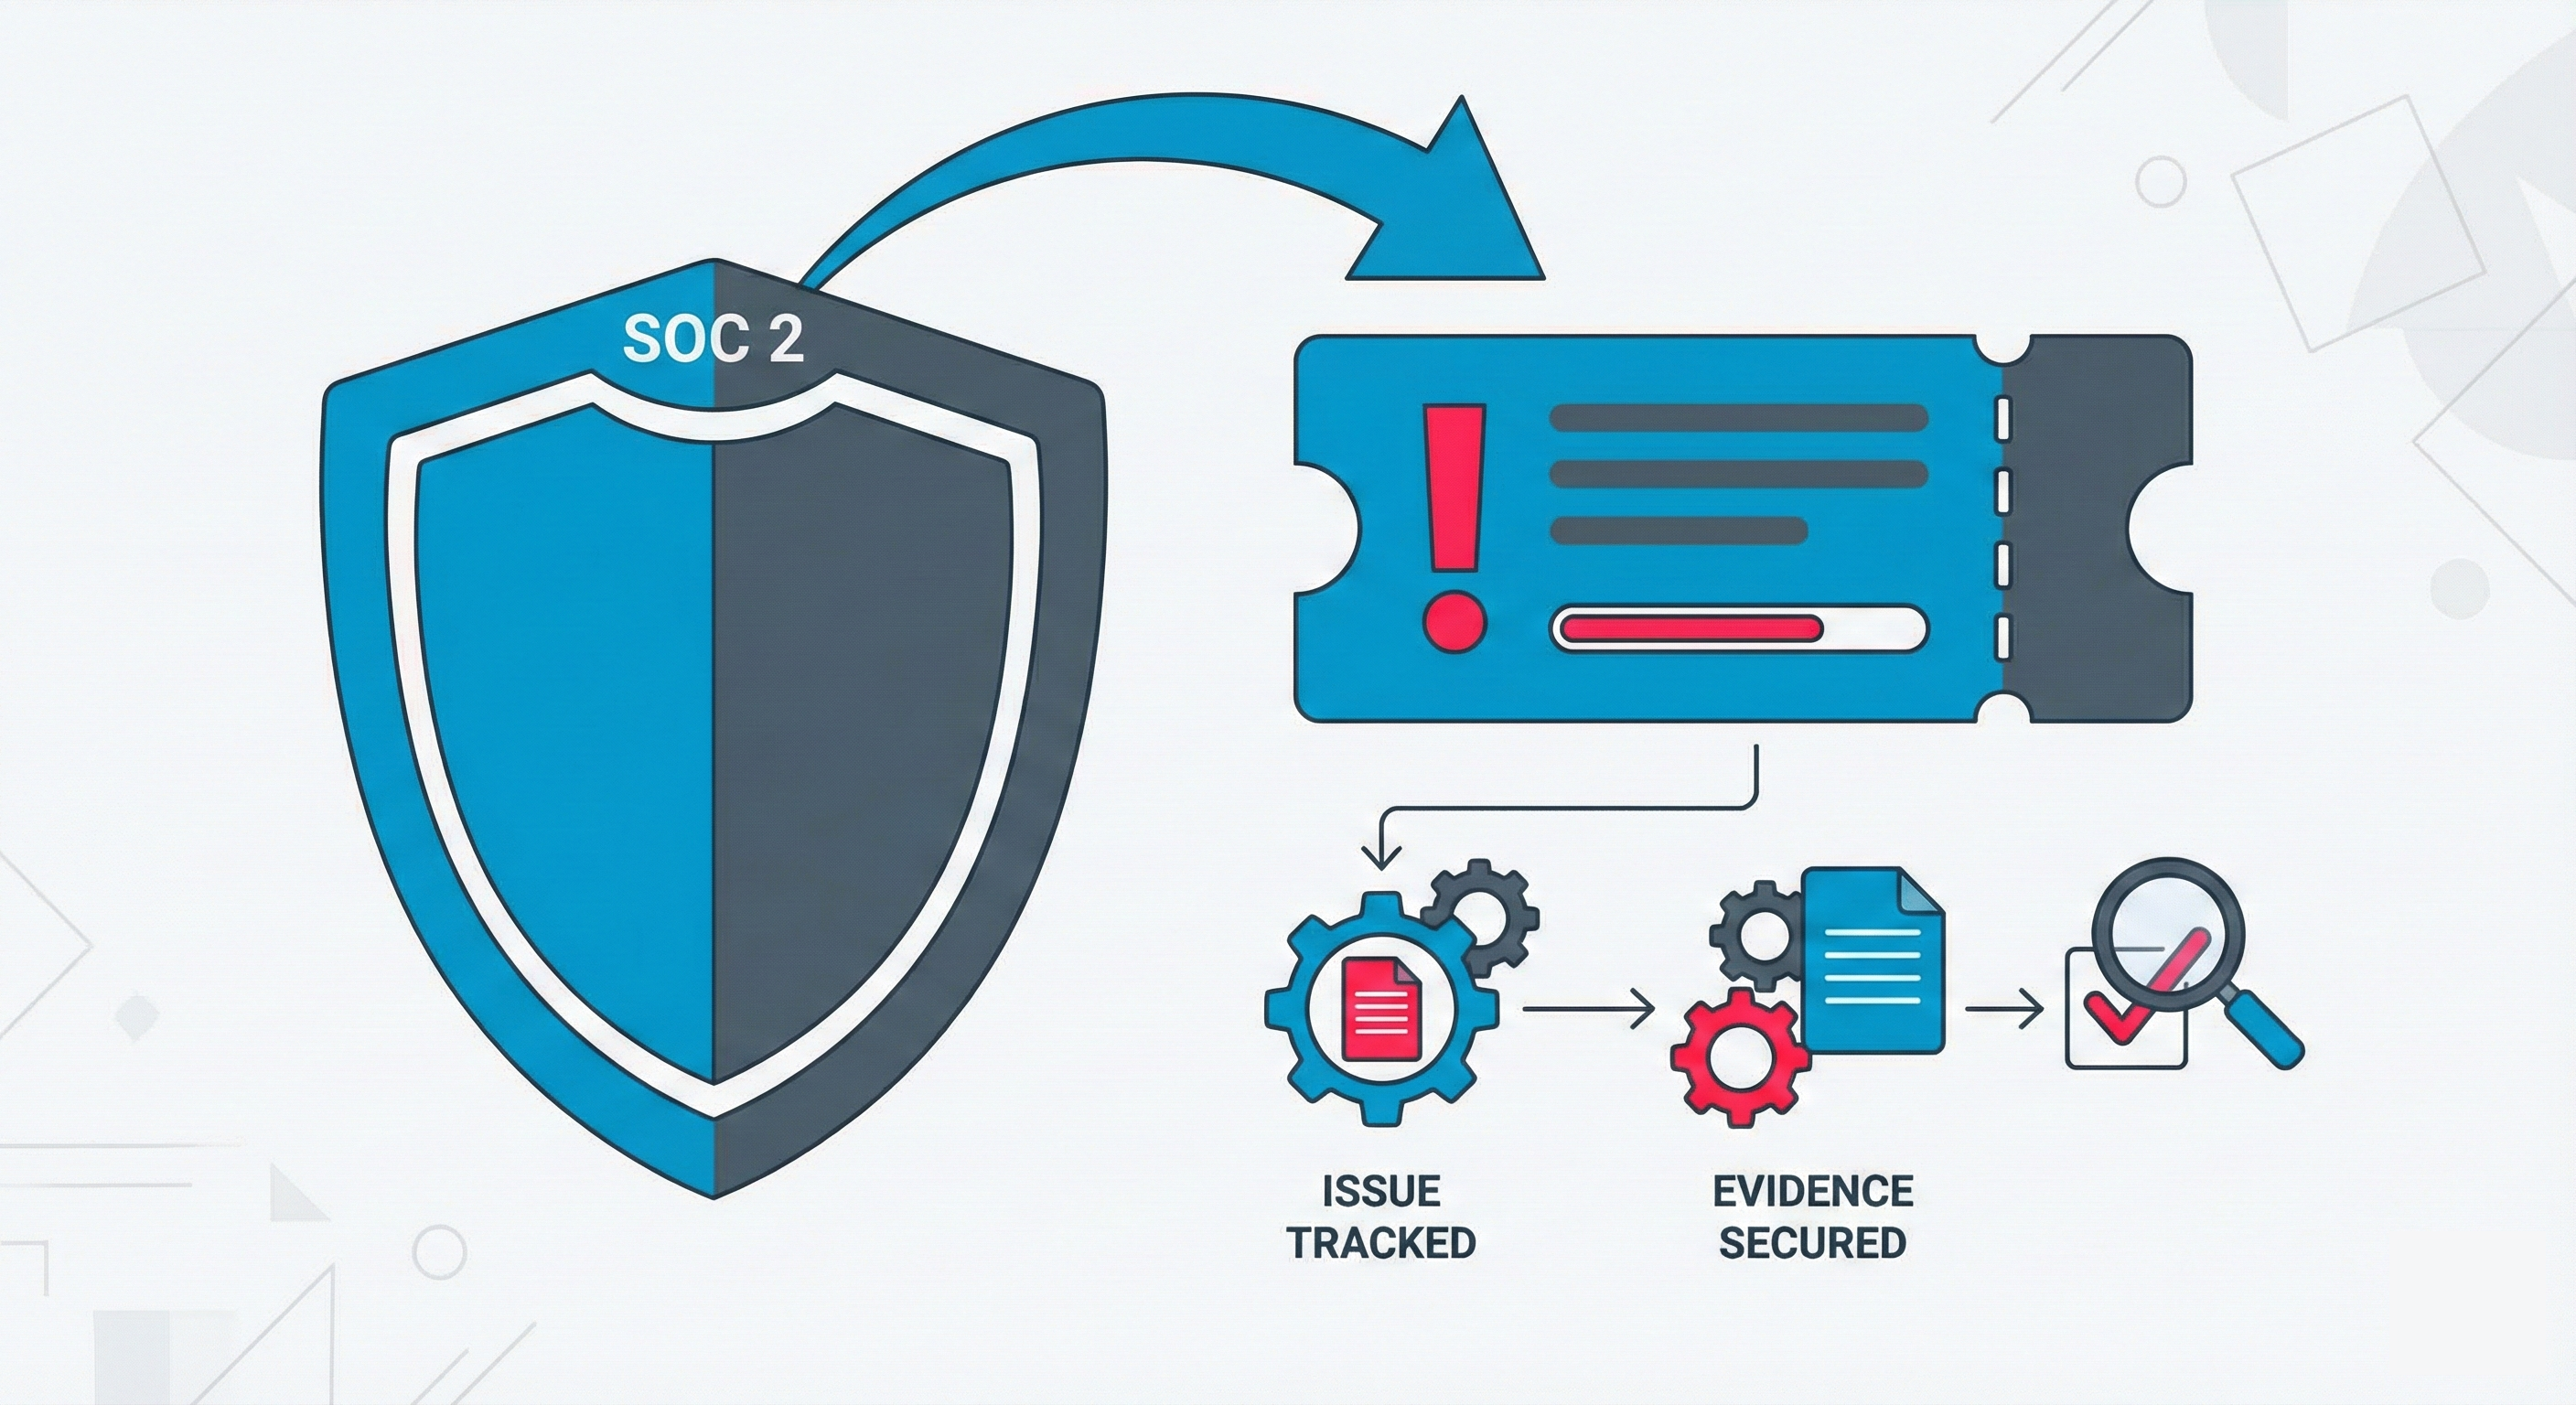
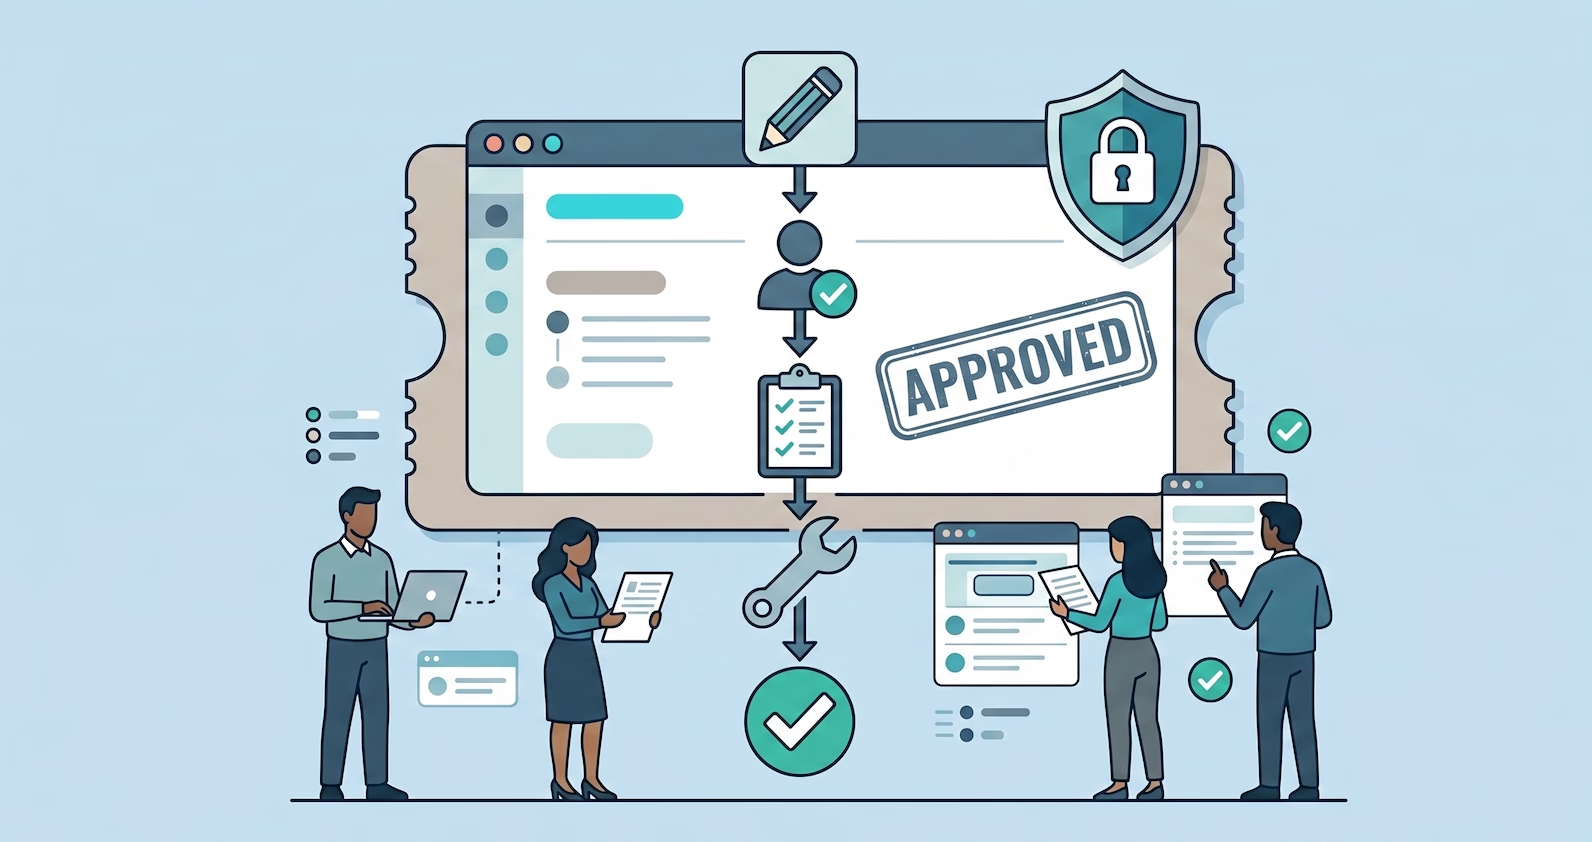
TL;DR: SOC 2 compliance requires a formal, trackable process for all security-relevant activities. Under the Trust Services Criteria, this means...
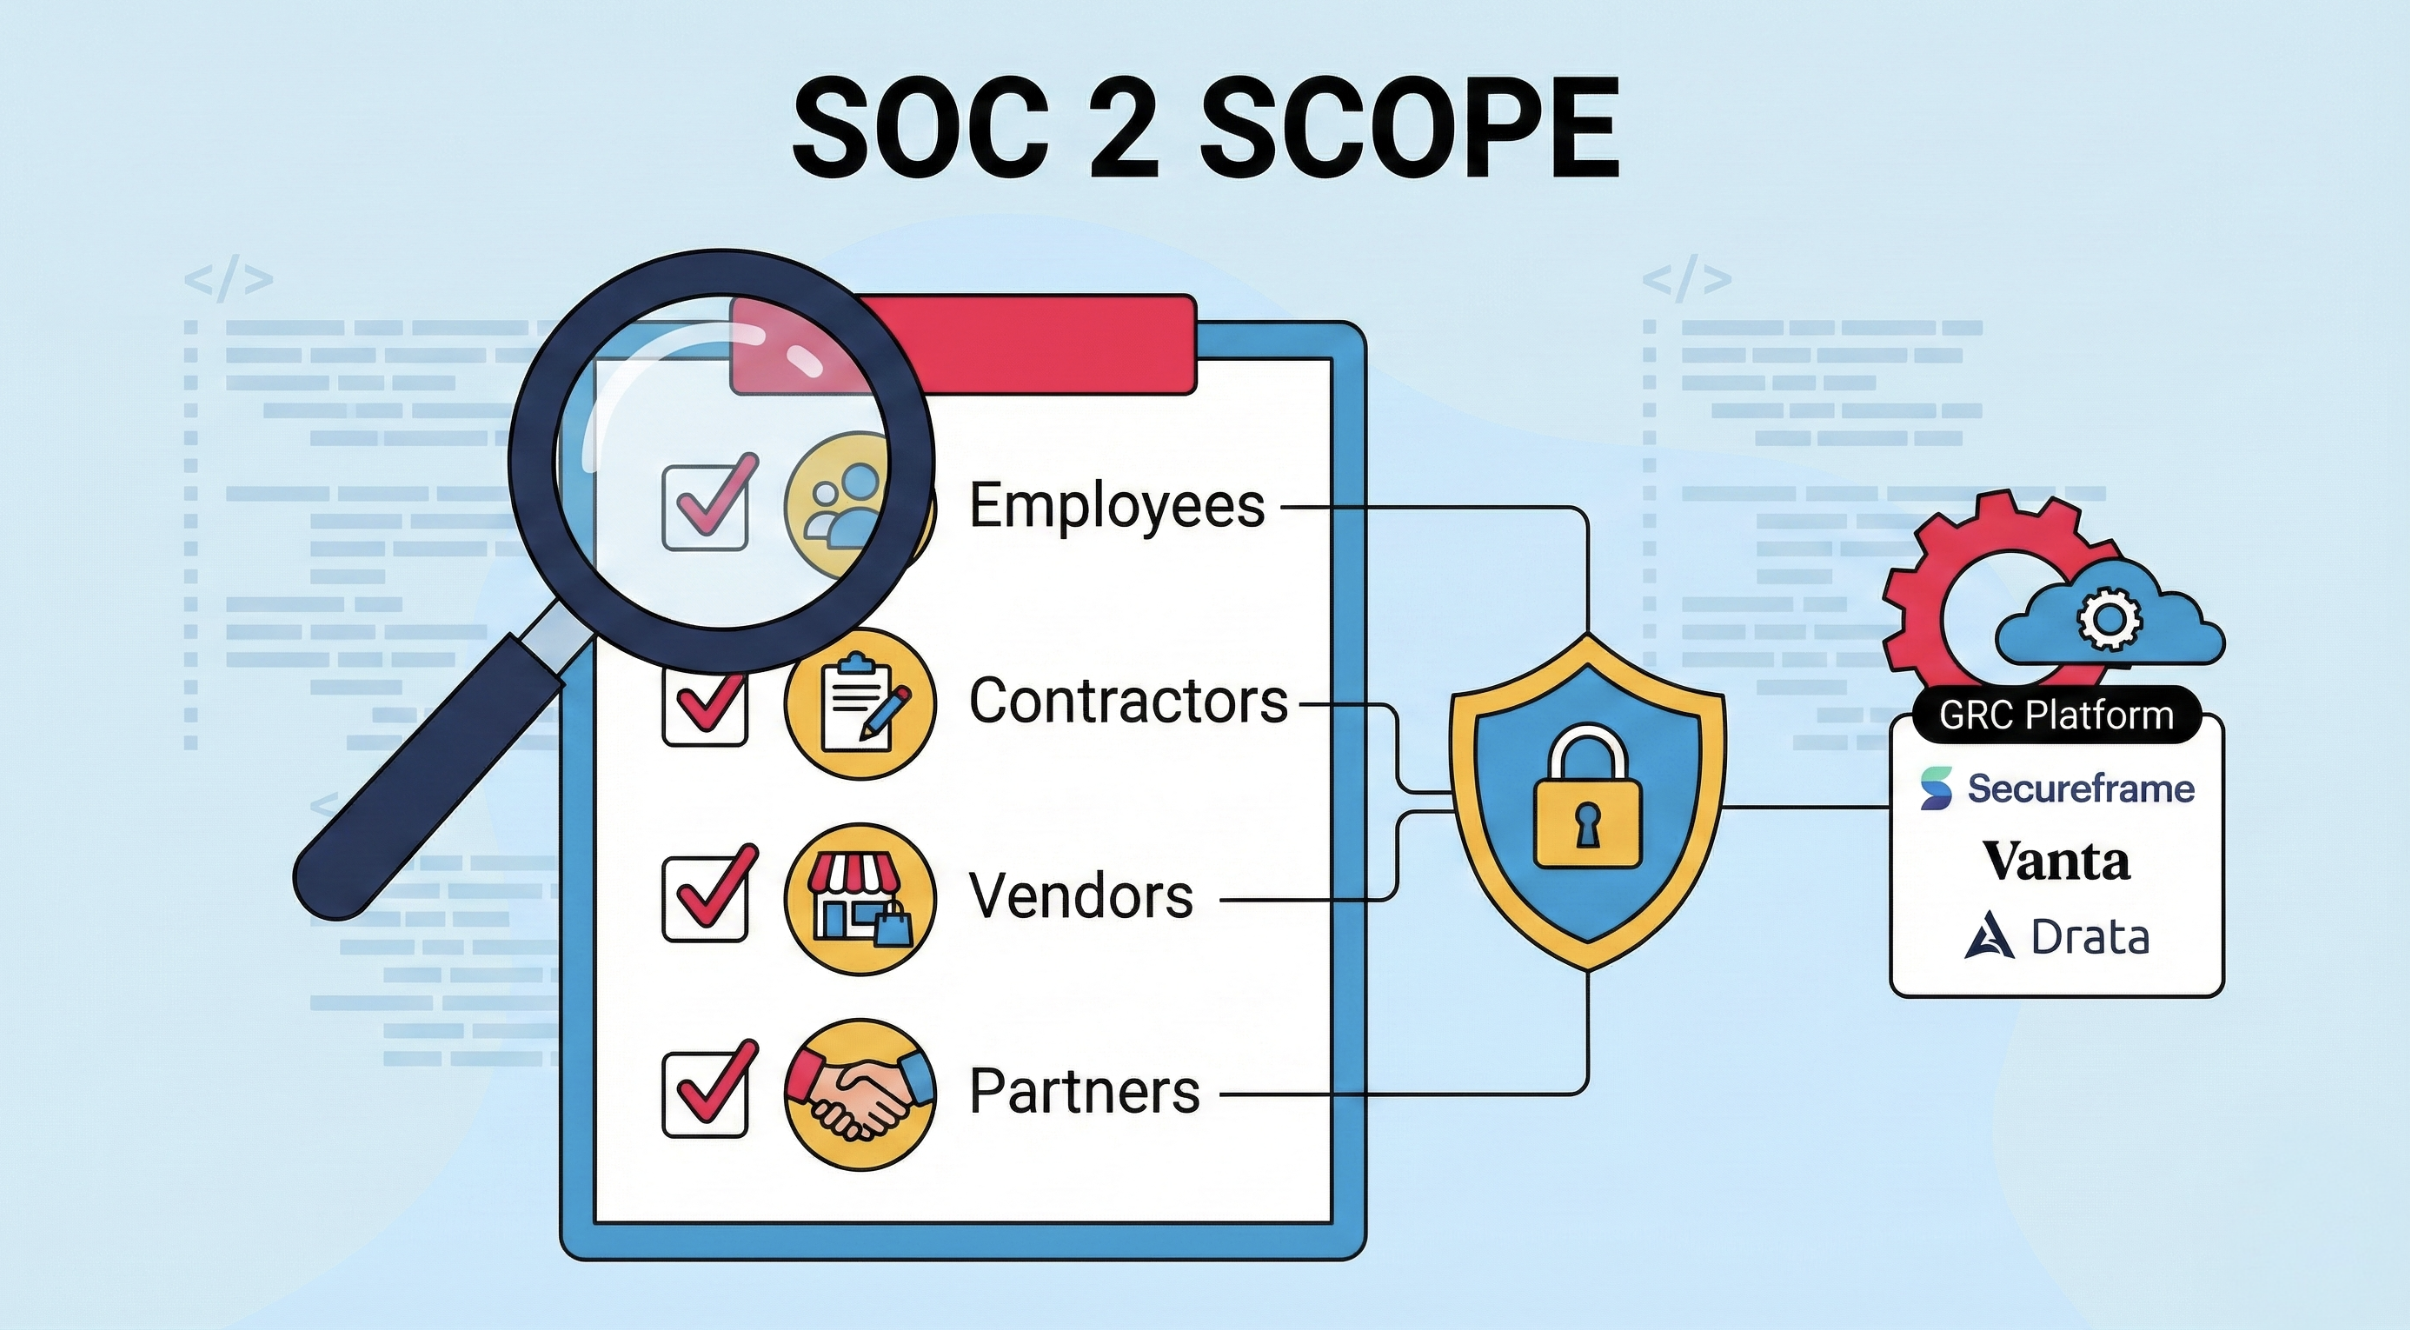
Short answer: a person is in SOC 2 scope when their role or access affects the system's ability to meet the Trust Services Criteria commitments.
To automate CI/CD security for SOC 2, run five types of security scans in the pipeline, fail the build on critical findings, and send the results to...

TL;DR: Even when SOC 2 is the only compliance requirement on the table, a compliance automation platform (Vanta, Drata, Secureframe, Scrut) pays for...

As a startup navigating the complexities of data security, understanding SOC 2 compliance is essential. SOC 2 (System and Organization Controls 2) is...

For many SaaS companies, achieving SOC 2 compliance is a major milestone, a sign that they take security and customer trust seriously. But the real...

A SOC 2 Type 2 report is a CPA firm's opinion on whether a service organization's security controls were designed well and operated effectively over...

Every SOC 2 roadmap on the internet reads the same way: pick a platform, connect your integrations, run the gap analysis, remediate, audit. Five...

SOC 2 is an attestation report a licensed CPA firm issues against the AICPA's Trust Services Criteria. The report describes whether a service...

SOC 2 CSOCs (Complementary Subservice Organization Controls) are vendor controls your system depends on but does not operate. A SOC 2 report handles...

Six months after buying Drata, Vanta, Secureframe, or any other compliance automation platform, a company realizes the dashboard is half-populated,...