SOC 2


SOC 2 CC9.1 is the risk mitigation criterion for business disruptions: it requires an organization to identify, select, and develop activities that...
SOC 2 CC7.2 is the security monitoring criterion in the Trust Services Criteria: it requires an organization to monitor its systems for anomalies and...
SOC 2 CC7.1 is where the vulnerability management program lives inside the Trust Services Criteria: it requires an organization to detect...
SOC 2 CC6.3 is where role design meets audit evidence: it requires that access to protected information assets is authorized, modified, or removed...
SOC 2 CC6.2 is the credential lifecycle criterion in the Trust Services Criteria: it requires an organization to register and authorize new users...
SOC 2 CC8.1 is the change management criterion: the single criterion in the CC8 series, covering how changes to infrastructure, data, software, and...
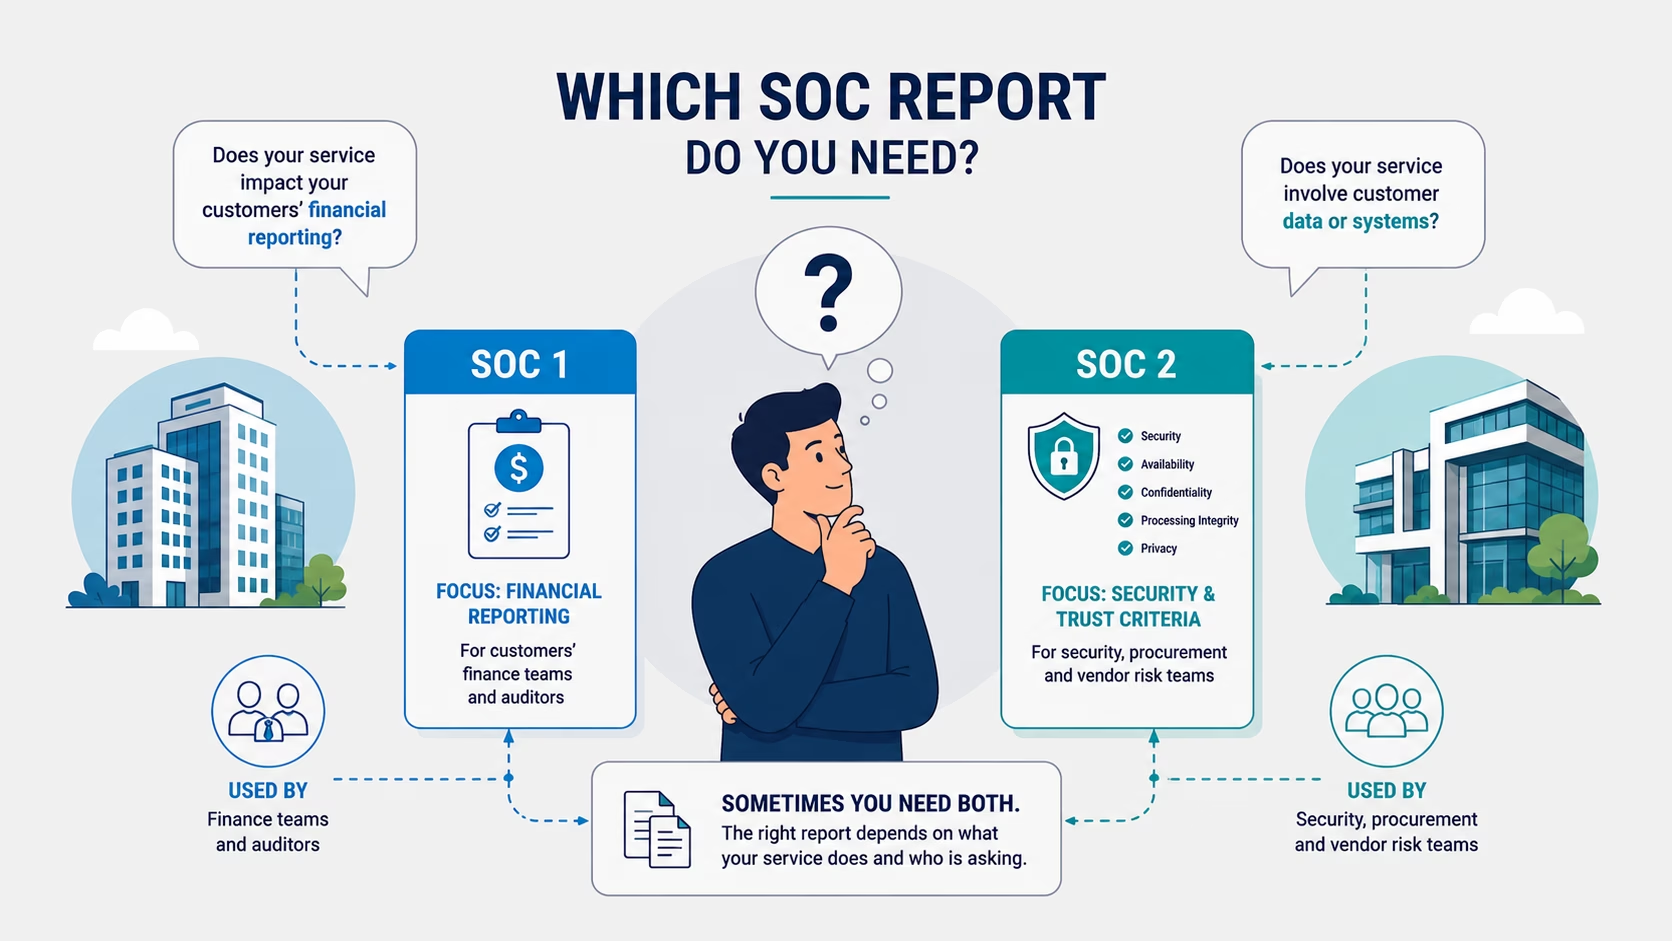
A SOC 1 report covers the controls at a service organization that are relevant to its customers' financial reporting, known as internal control over...
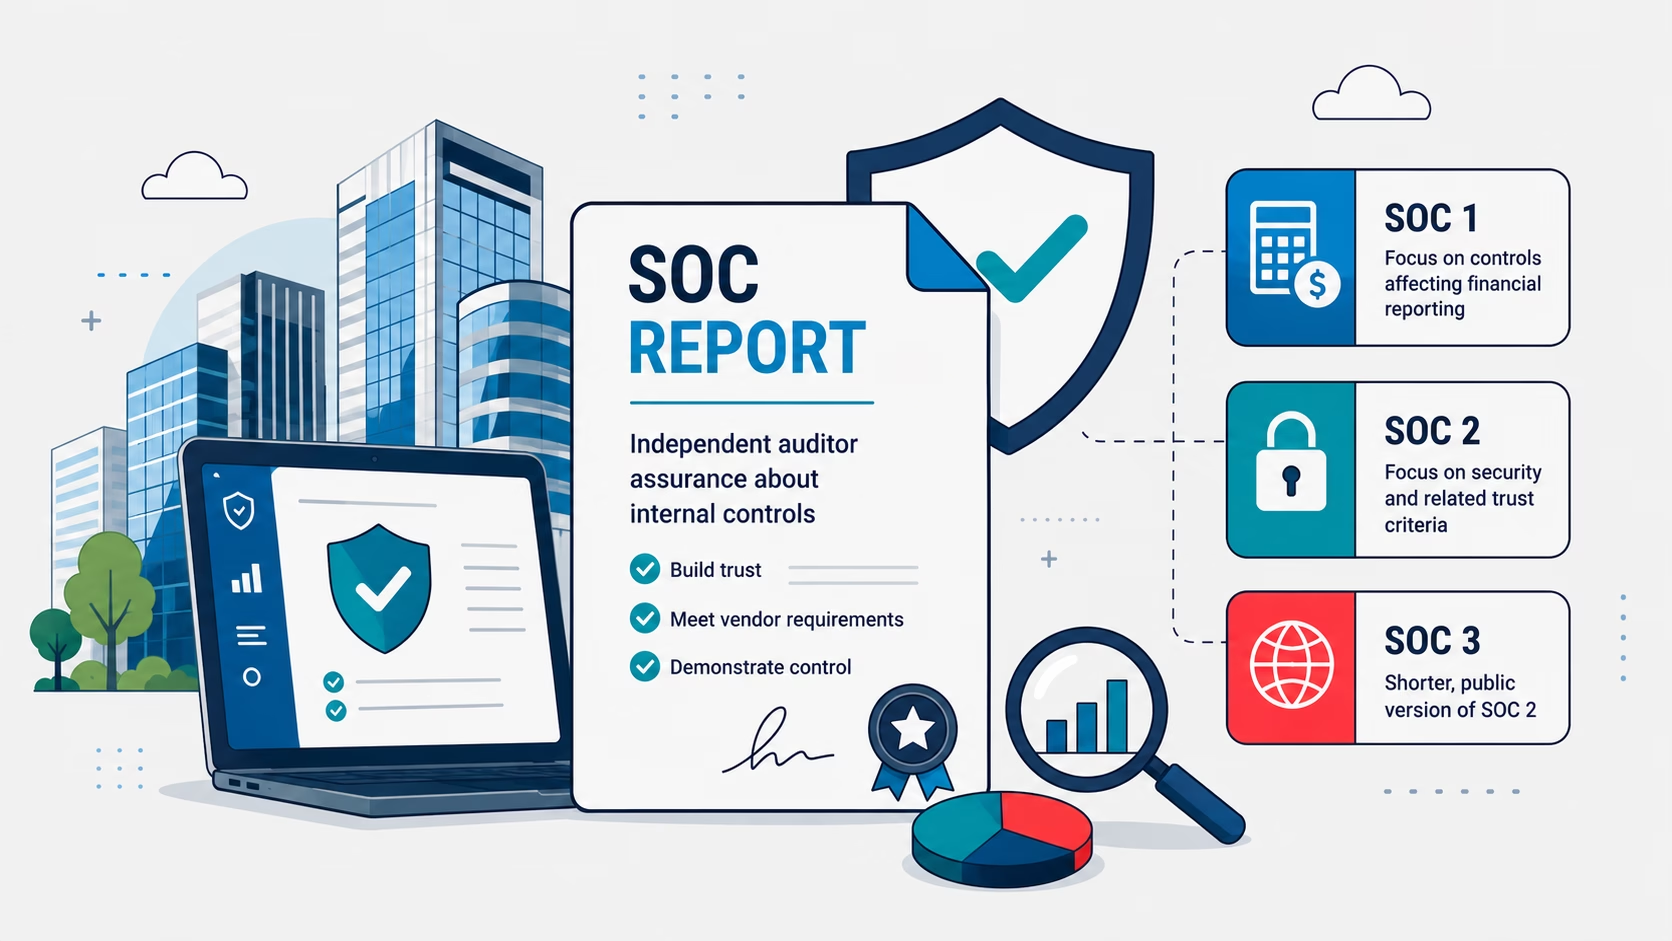
A SOC report (System and Organization Controls report) is an independent auditor's attestation report on a service organization's controls, issued by...
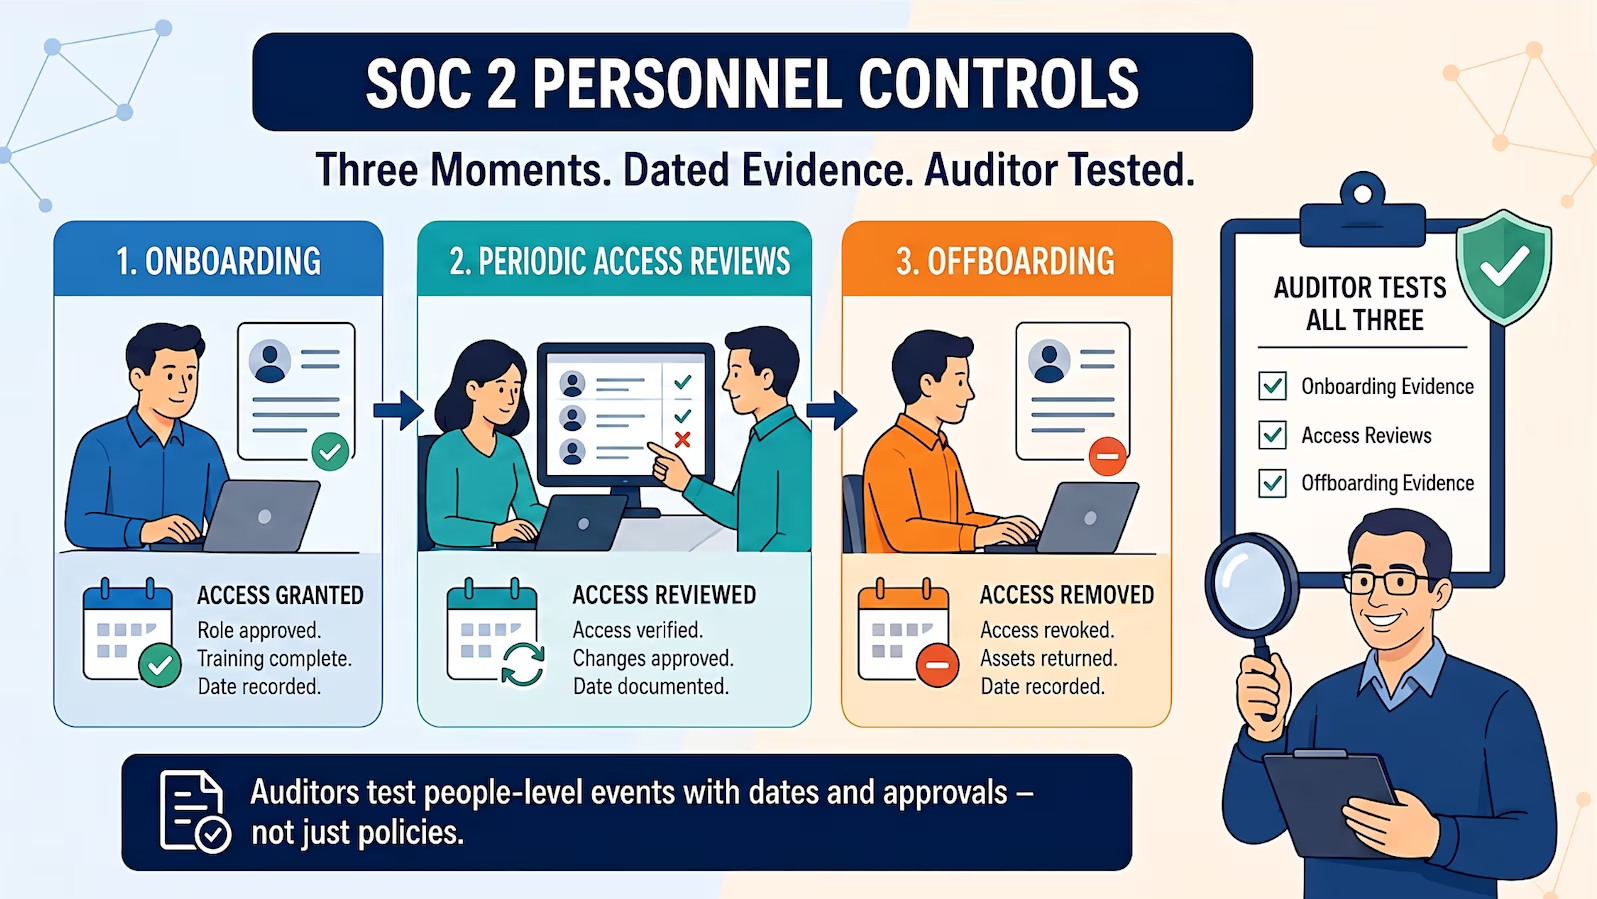
SOC 2 personnel controls come down to three moments: onboarding on day one, the periodic user access review that confirms access still matches the...
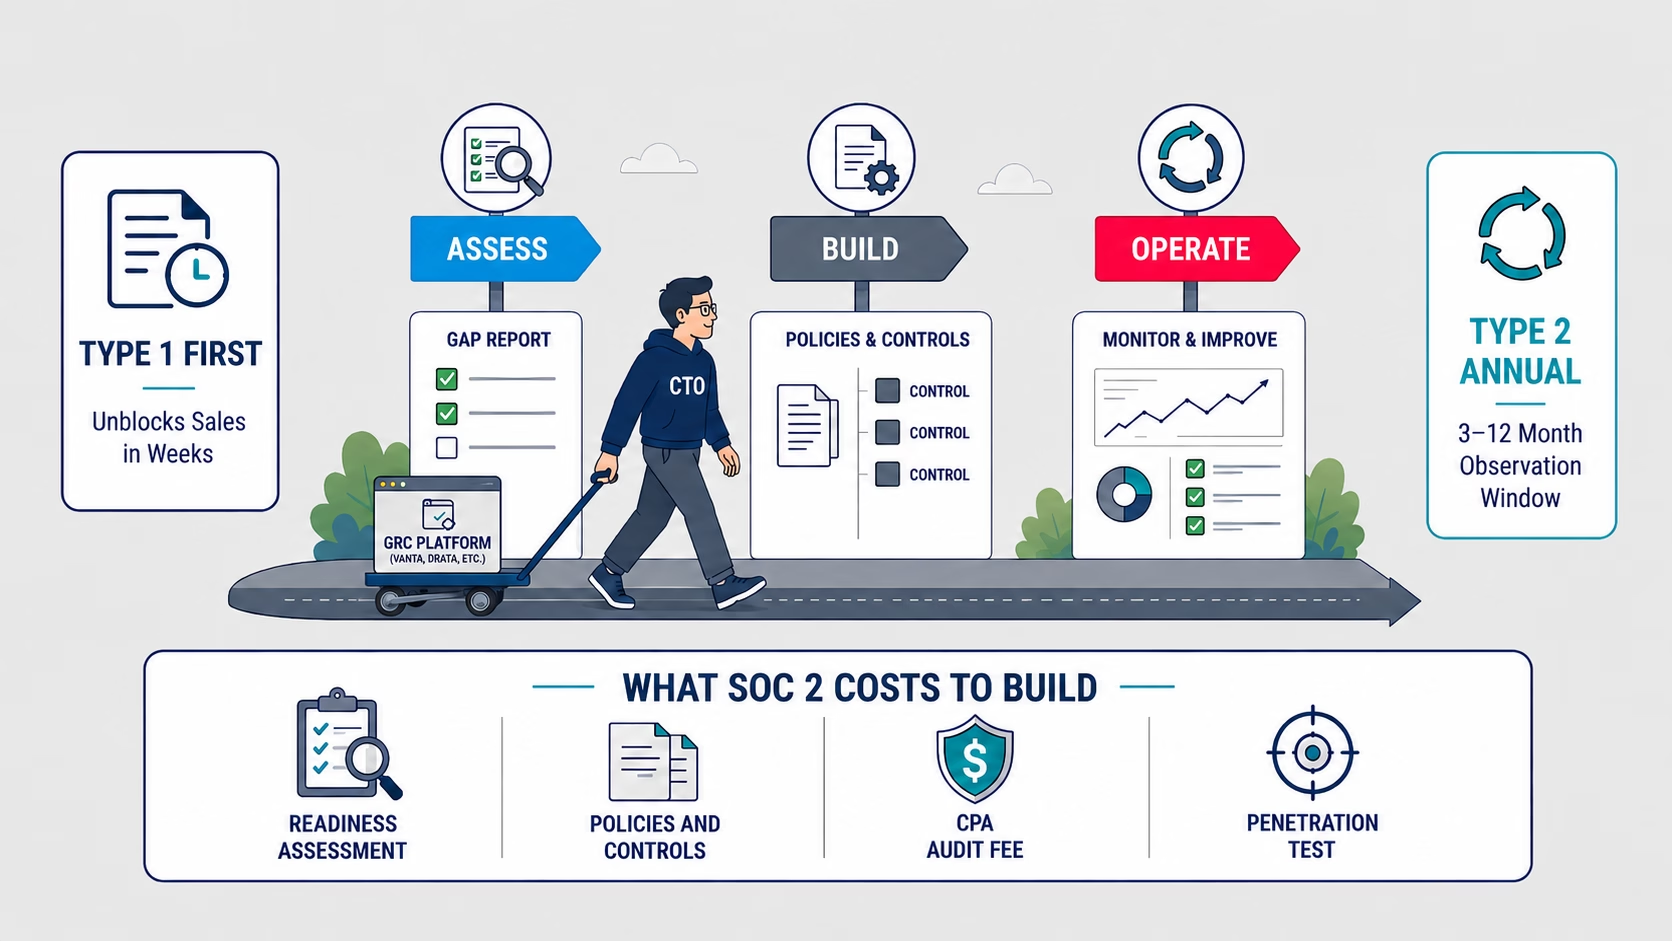
TL;DR: SOC 2 compliance for a B2B SaaS company is a sales requirement before it is a security exercise: enterprise buyers use the report to clear...
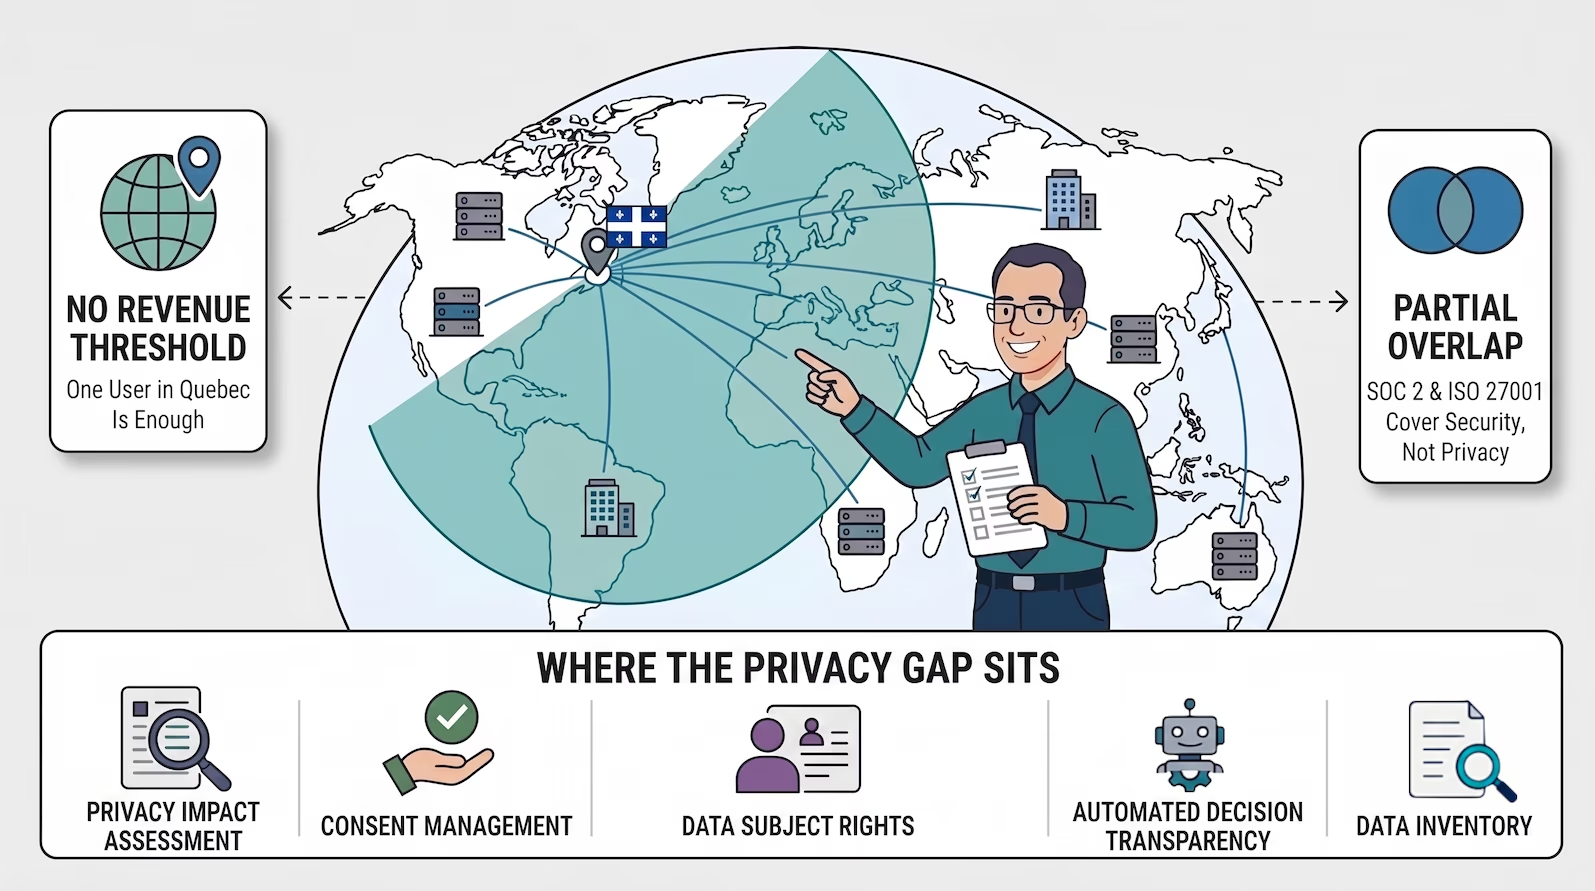
Quebec Law 25 is the province's modernized private-sector privacy law: a set of amendments (adopted in 2021 as Bill 64) to the Act respecting the...
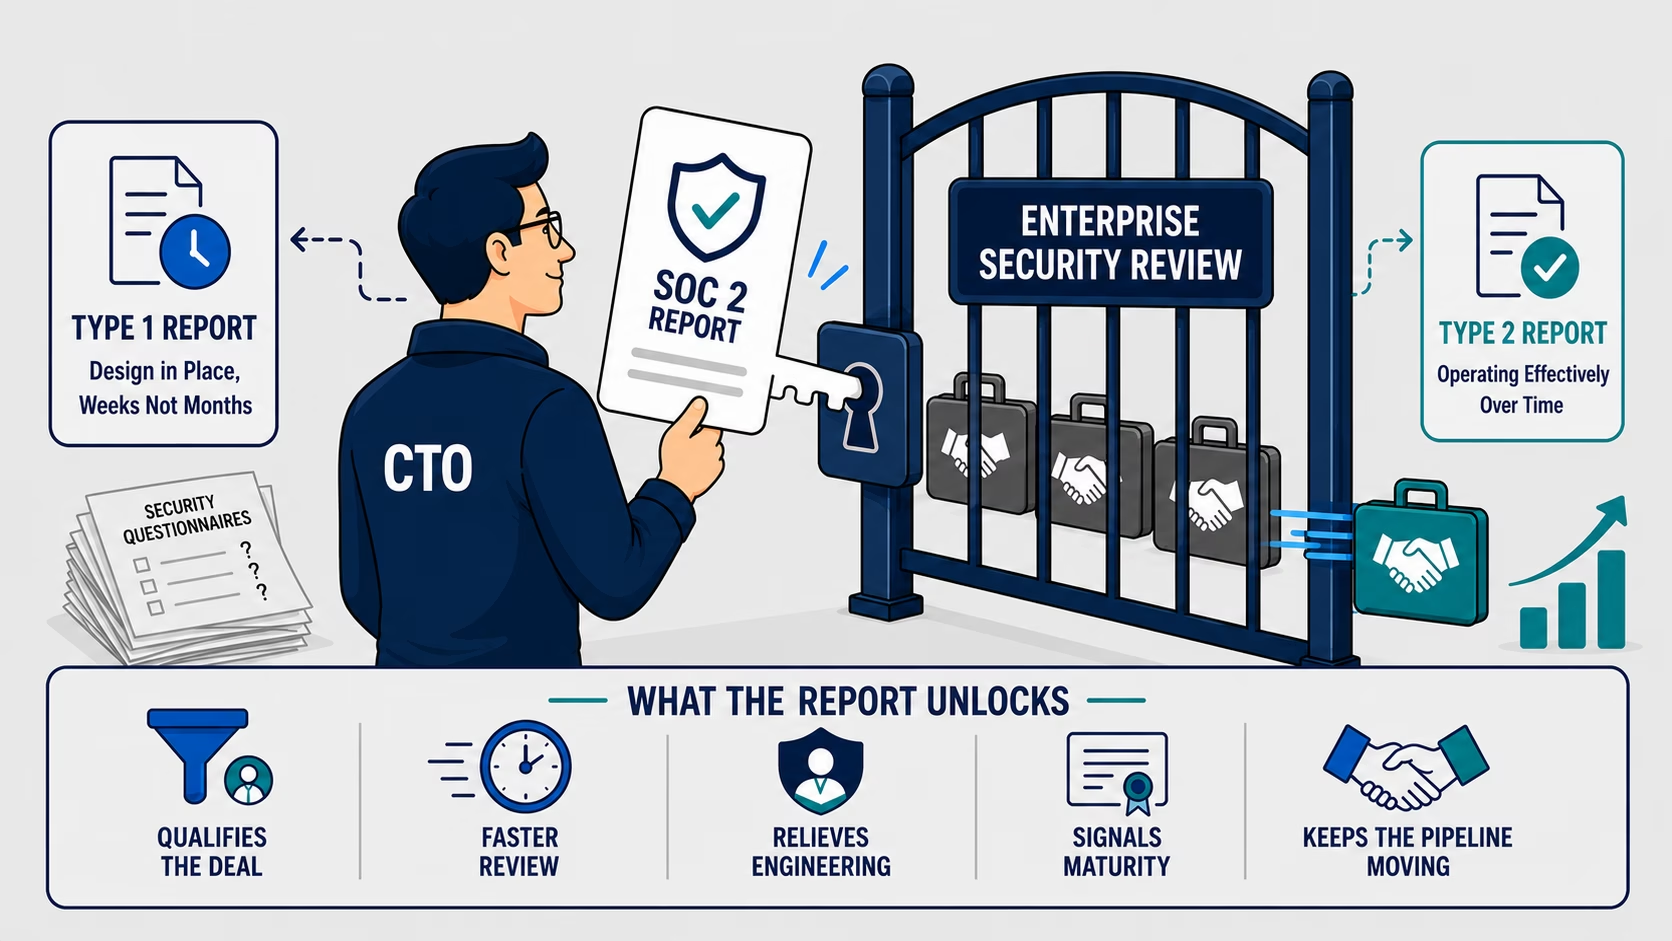
Enterprise buyers treat a SOC 2 report as the price of admission for SaaS vendors that touch their data or systems. For a CTO, that turns SOC 2 from...
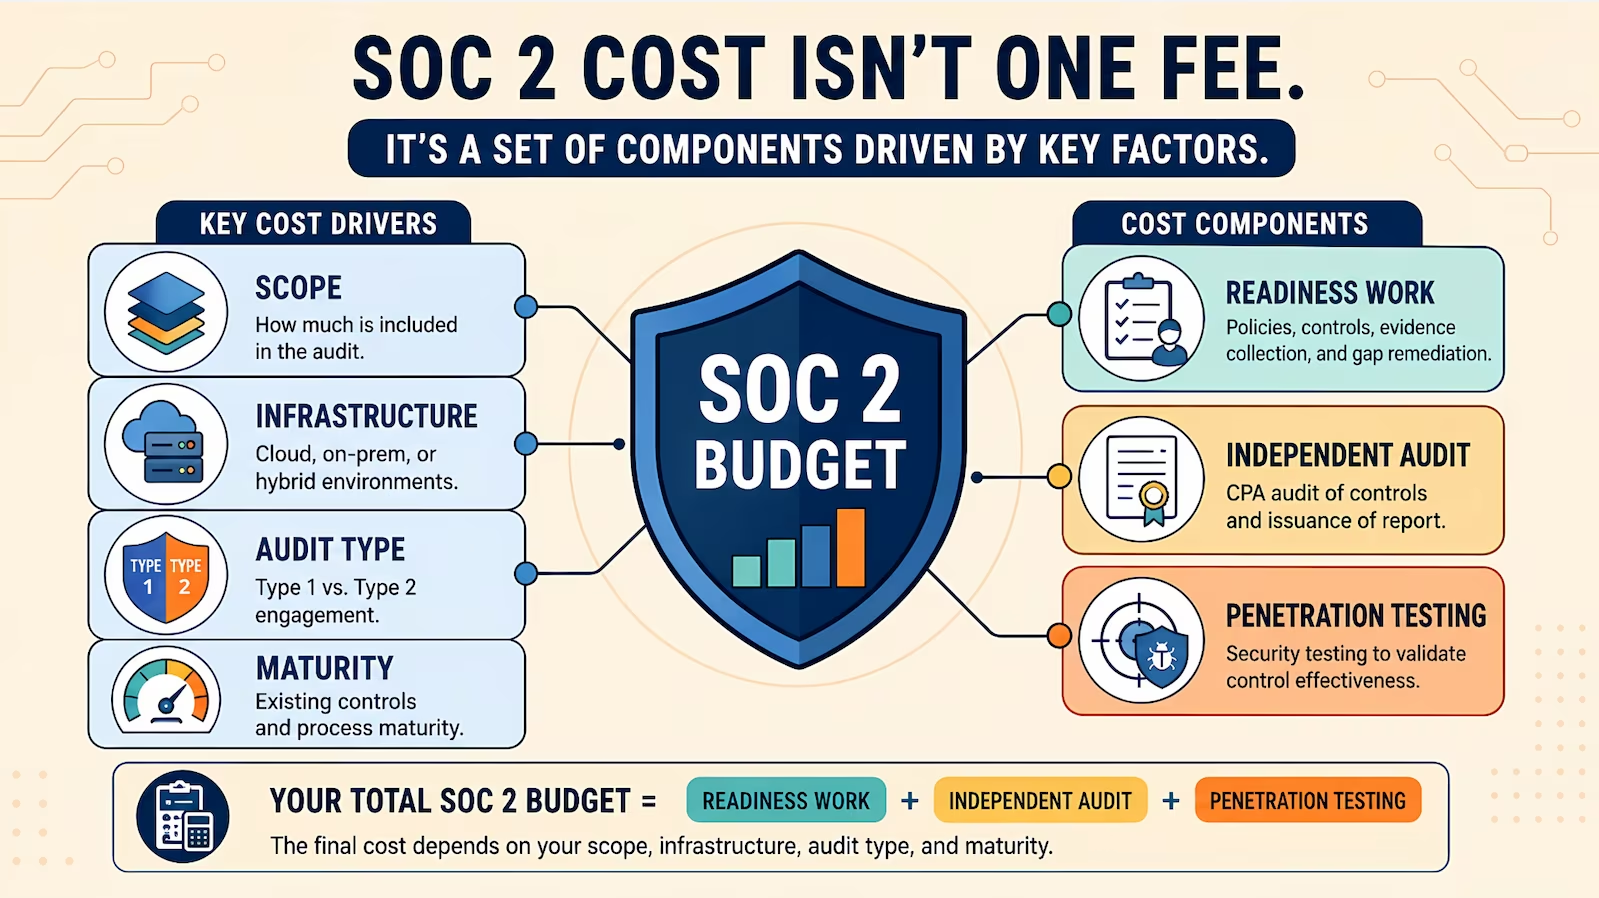
A SOC 2 audit fee alone costs roughly $7,500 to $100,000 or more in 2026, depending on report type, company size and the audit firm, with published...
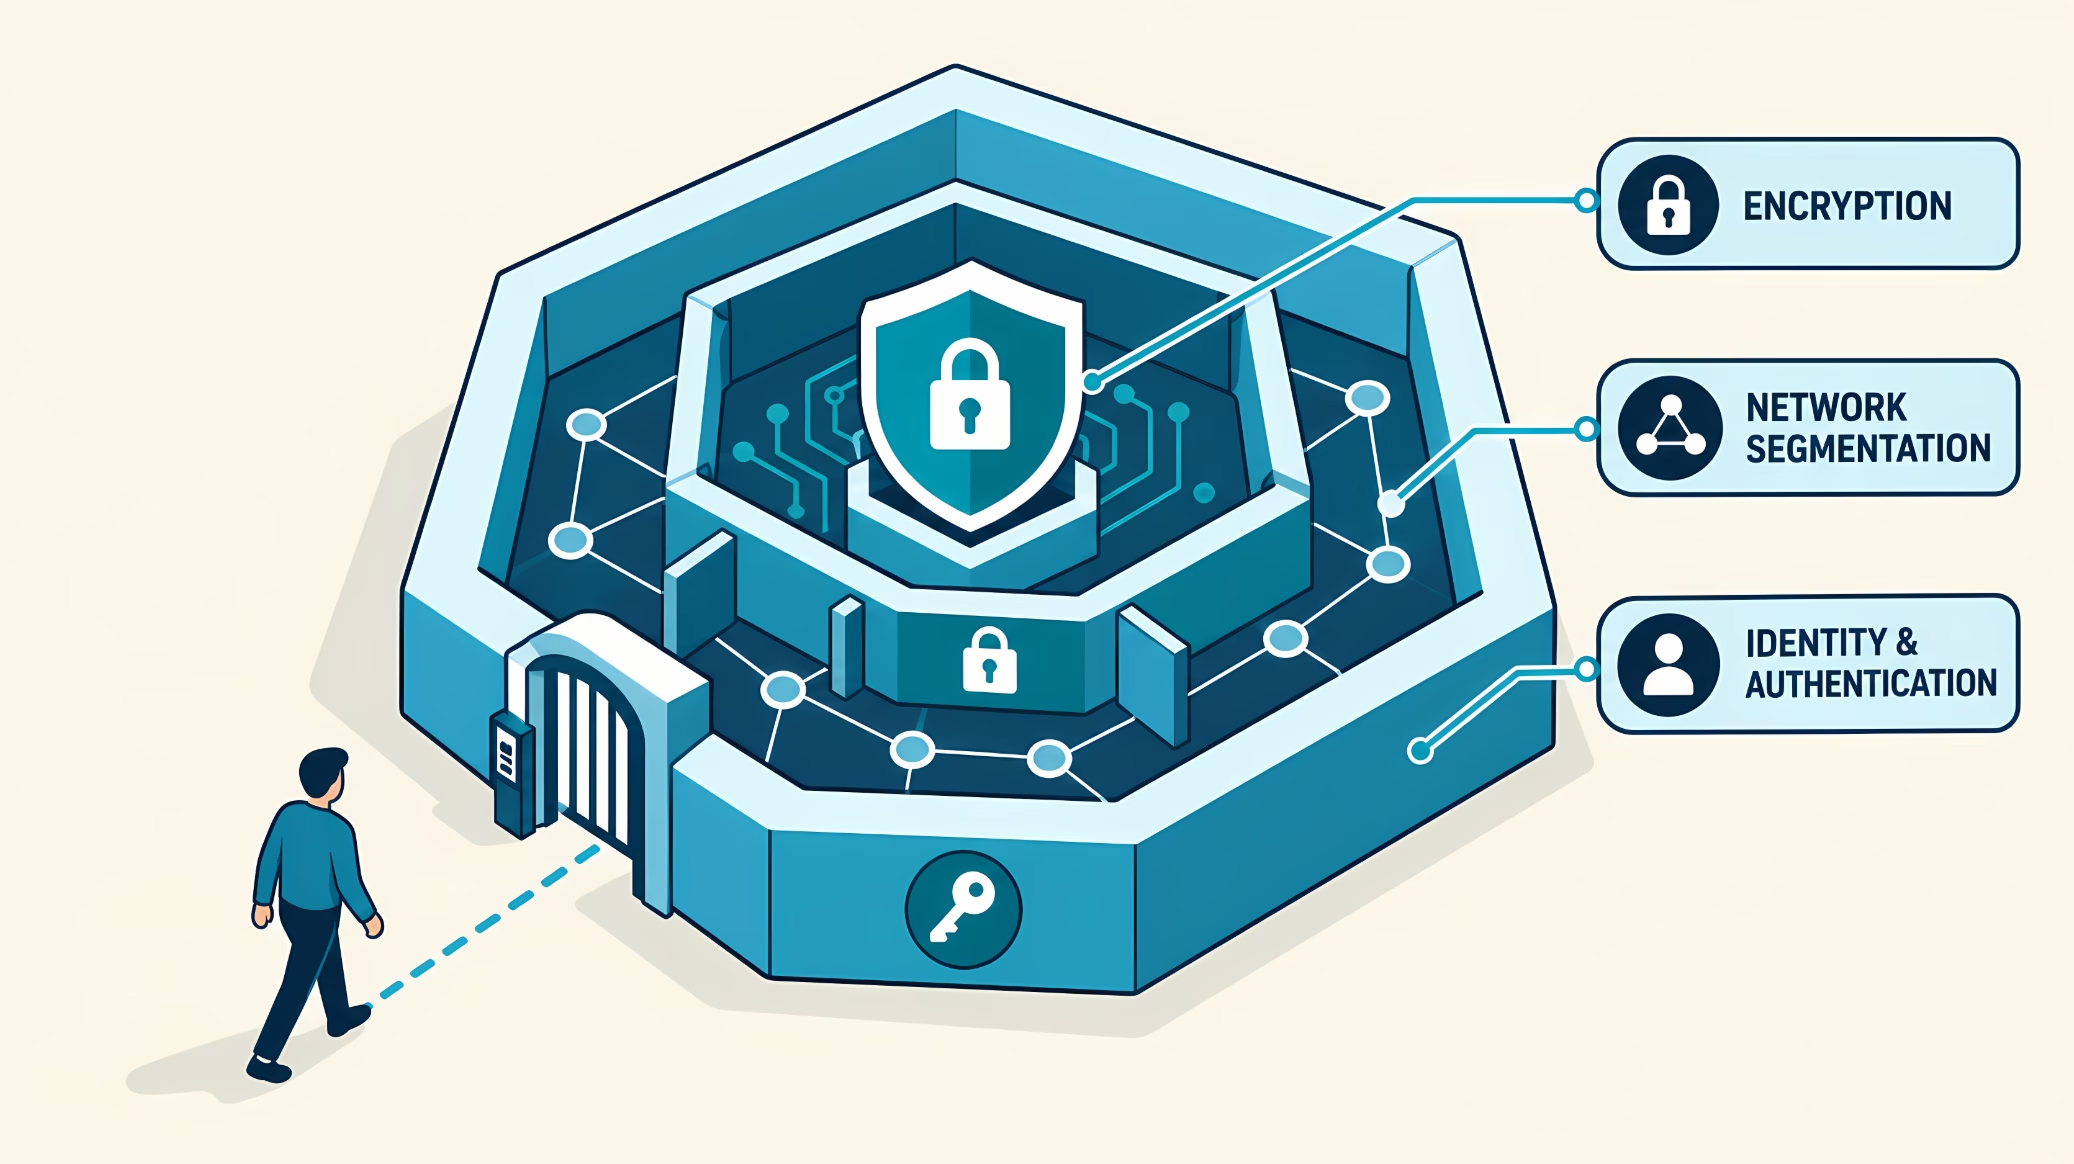
SOC 2 CC6.1 is the foundational access control criterion in the Trust Services Criteria: it requires an organization to implement logical access...
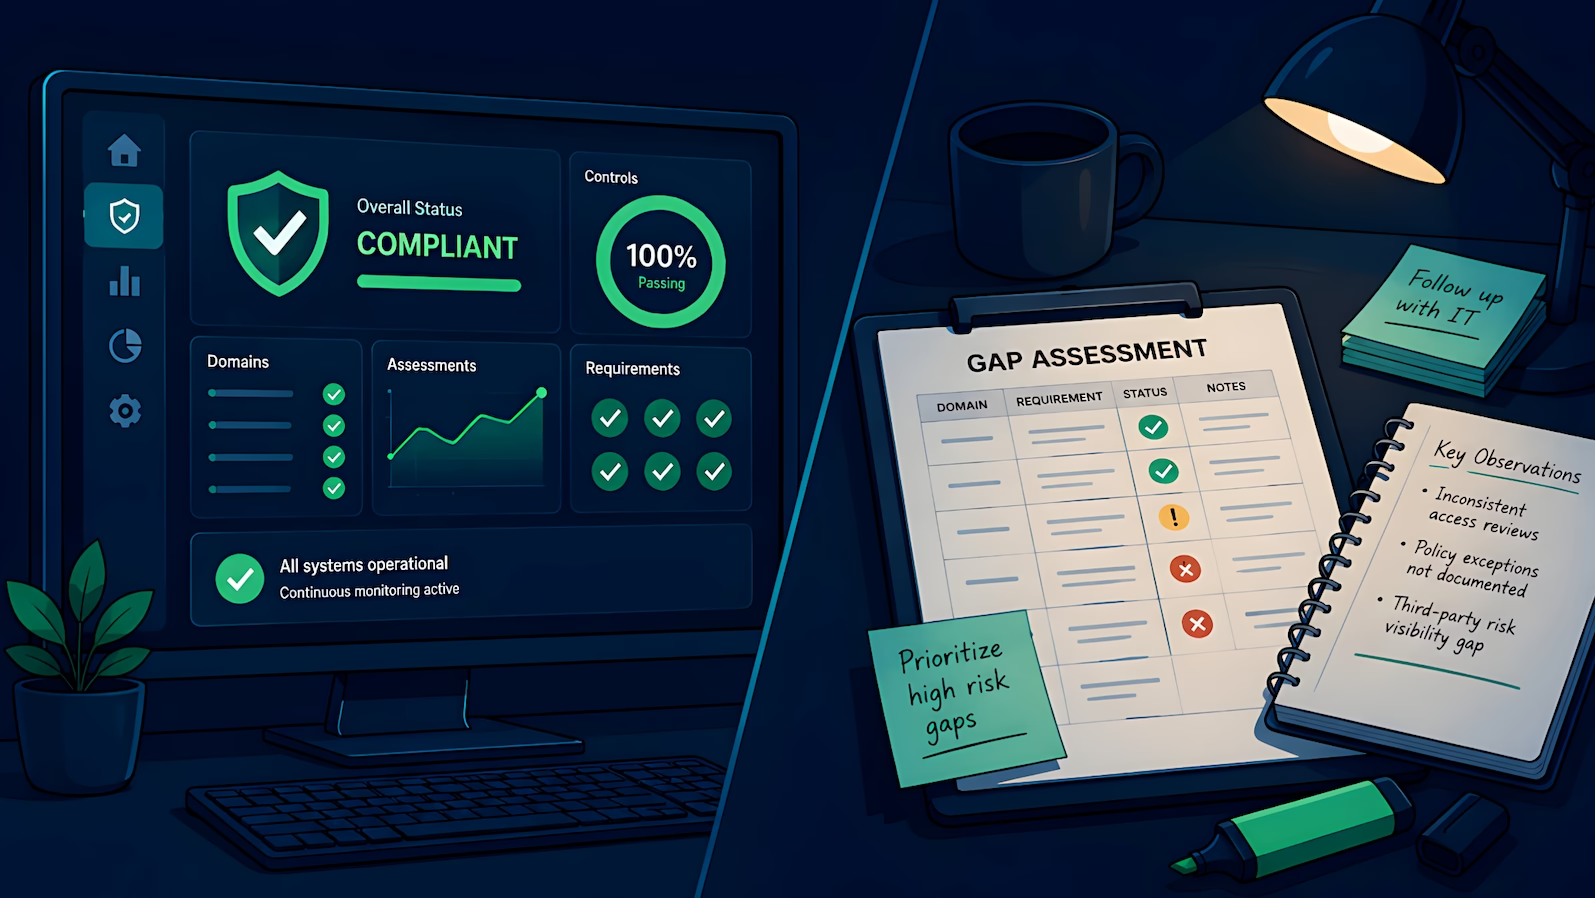
A SOC 2 readiness assessment and Drata solve different problems. The assessment tells you whether your control environment is adequate before the...
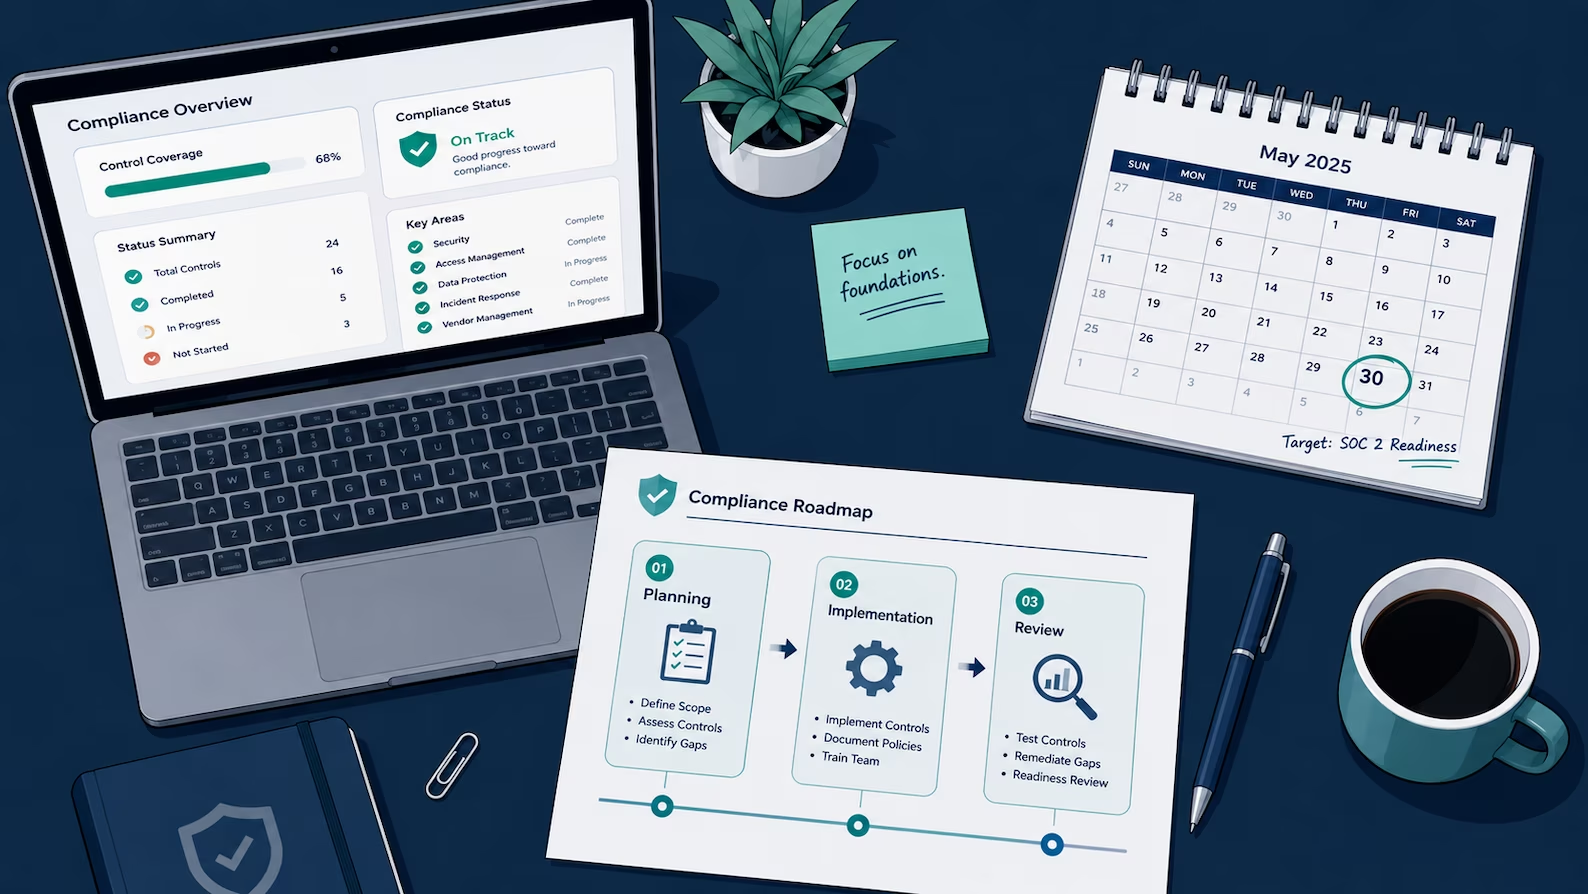
If you've already read SOC 2 Explained: What It Is and Why Enterprises Require It and you're ready to move, this is the operational post for teams of...
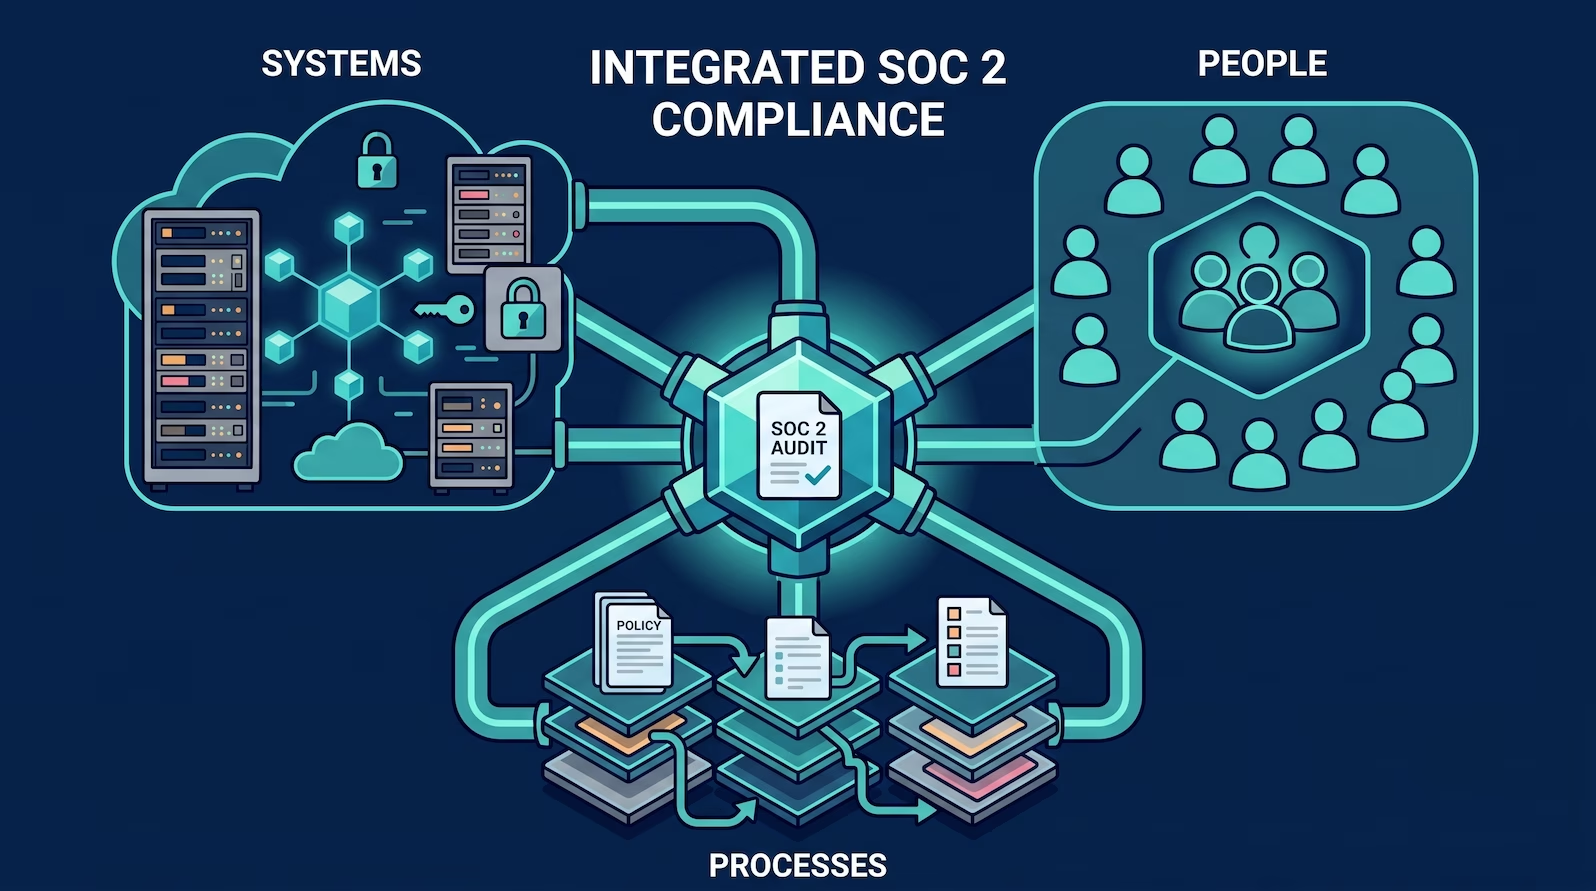
SOC 2 scope answers three questions: which systems the audit covers, which people, and which processes. Systems are one third of the answer.
SOC 2...
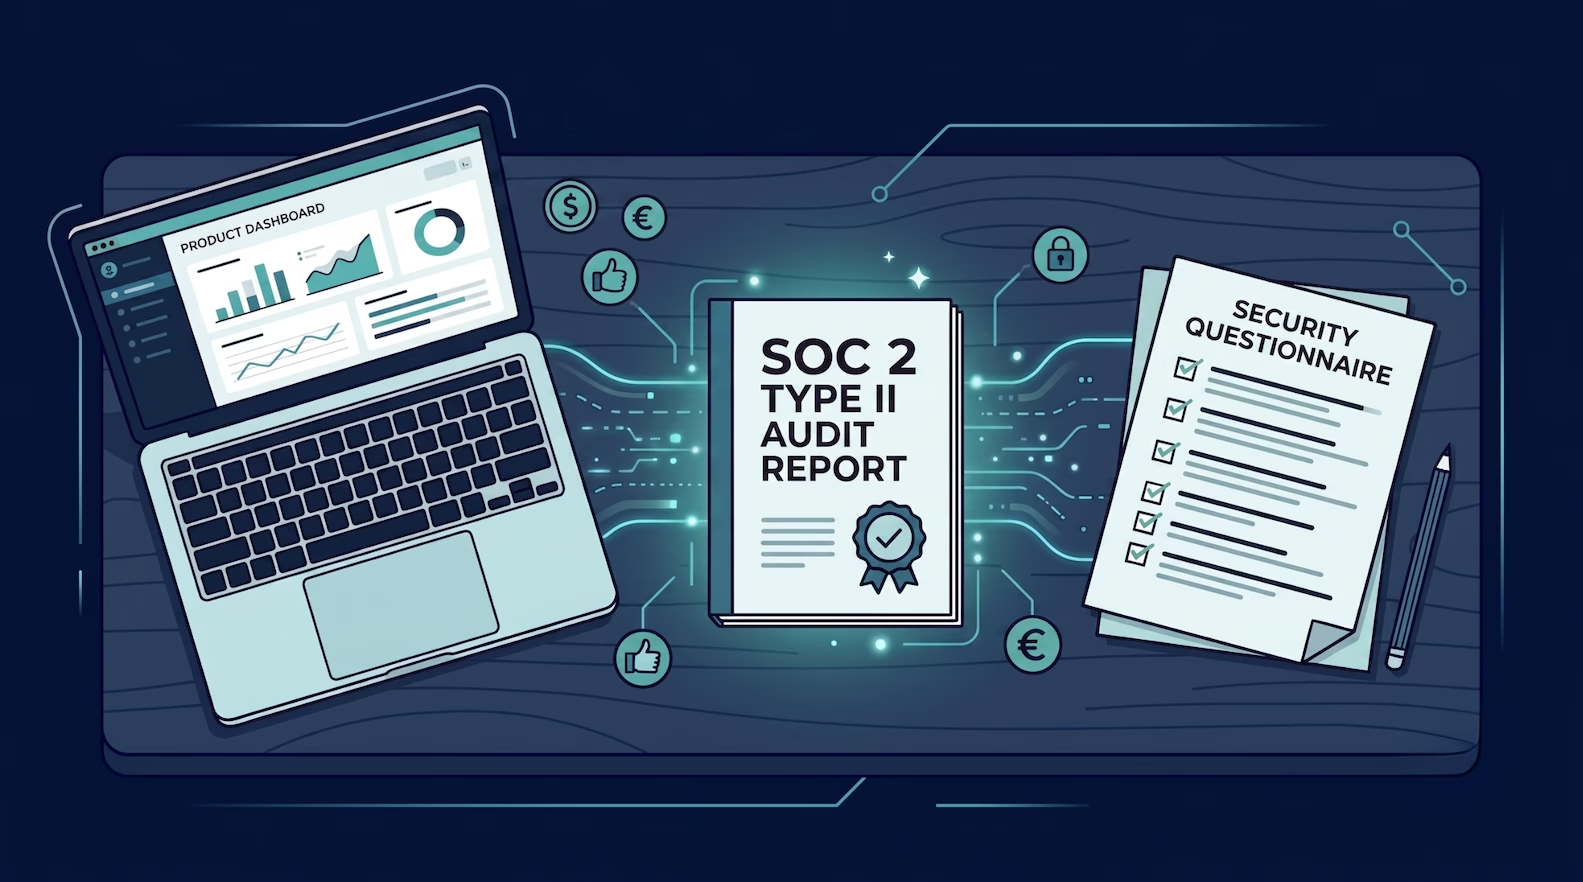
An enterprise prospect sends over a security questionnaire. Or procurement asks whether you have a SOC 2 report. Or a deal stalls because the...
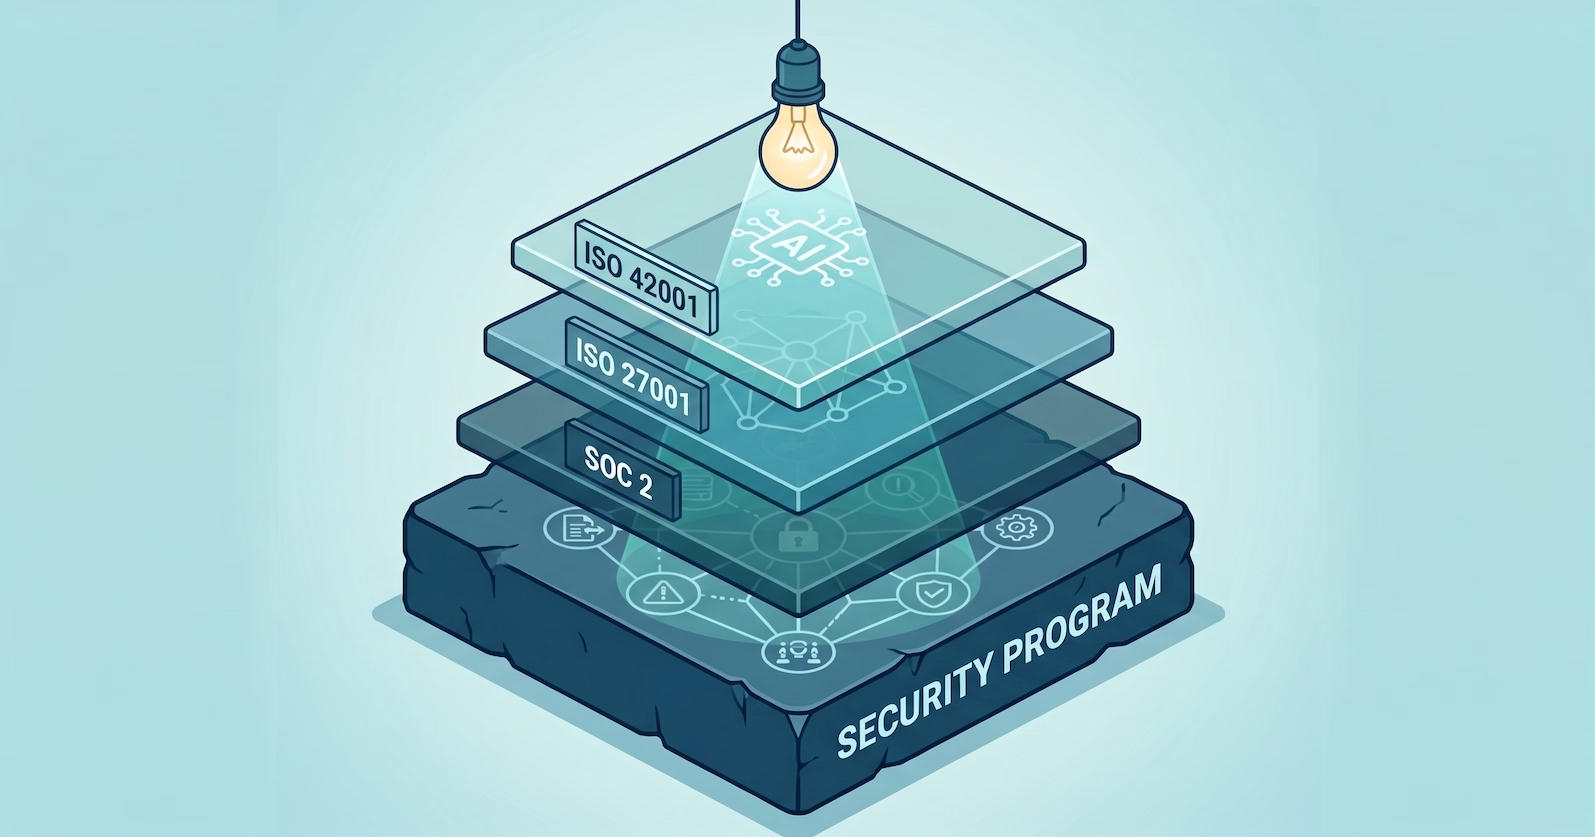
How much of an existing SOC 2 or ISO 27001 program carries into ISO 42001, and why the framework tax is mostly imaginary for teams that built a real...
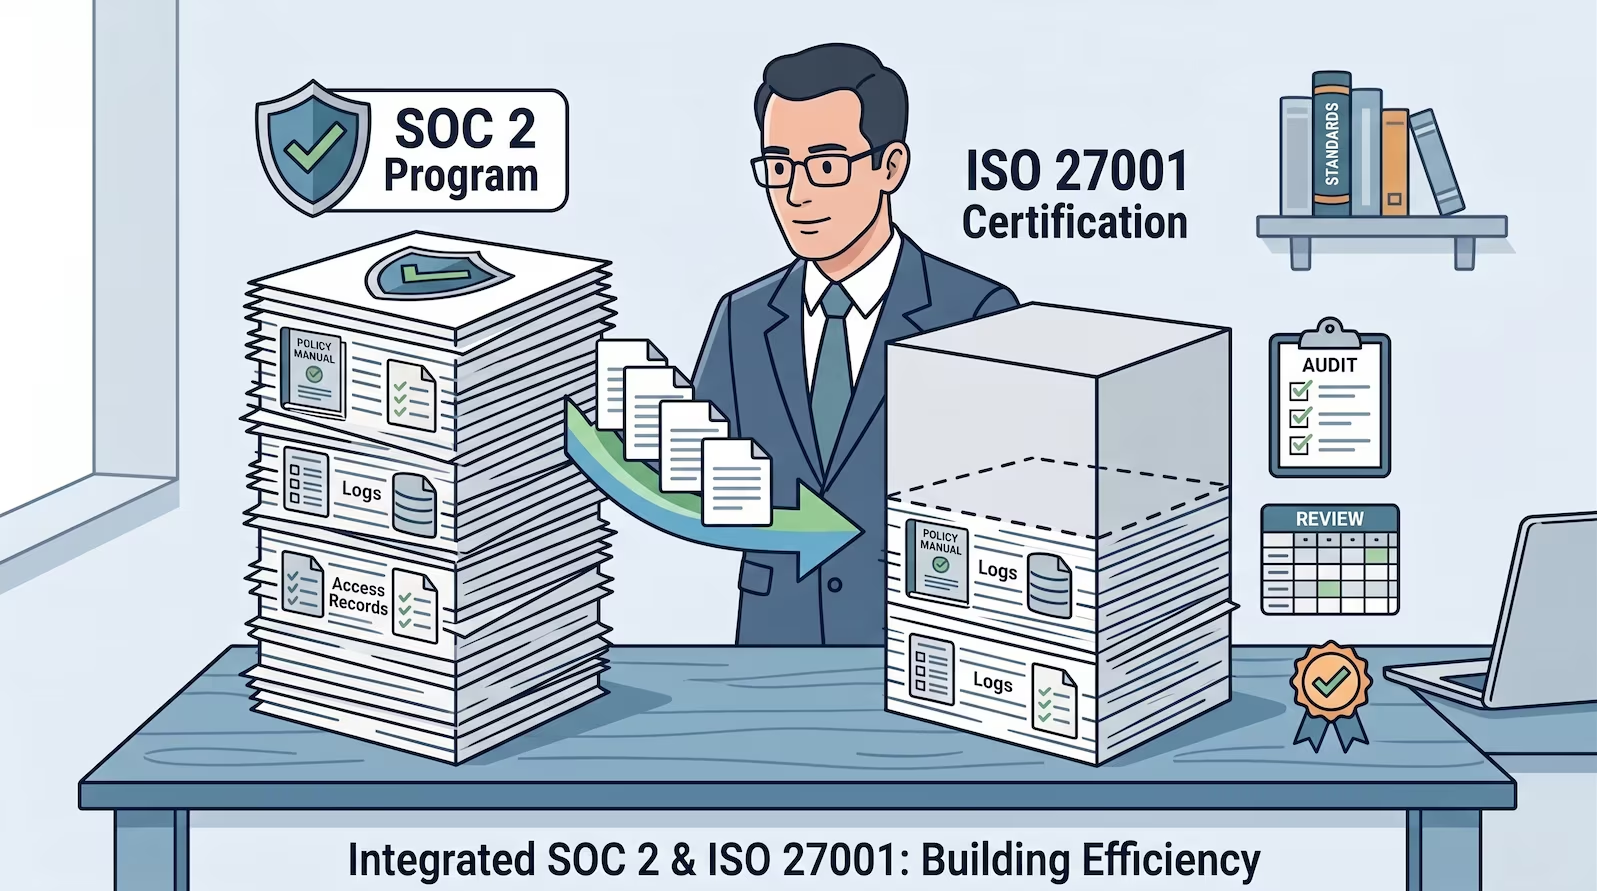
In our experience, a SOC 2 program covers roughly 70 percent of the work for ISO 27001 certification. The policies carry over, and most controls need...
Bottom line: Every SOC 2 report needs an independent CPA audit firm. Many companies also choose a GRC platform to automate evidence and a consultancy...
Toronto SaaS has a compliance problem Silicon Valley doesn't: a lot of your customers are Canadian banks, insurers, and licensed payment partners....
The SOC 2 consulting firms active in Canada in 2026 include Truvo Cyber, Canadian Cyber, Elastify, and the Big 4 (Deloitte, KPMG, PwC, EY). ISA...
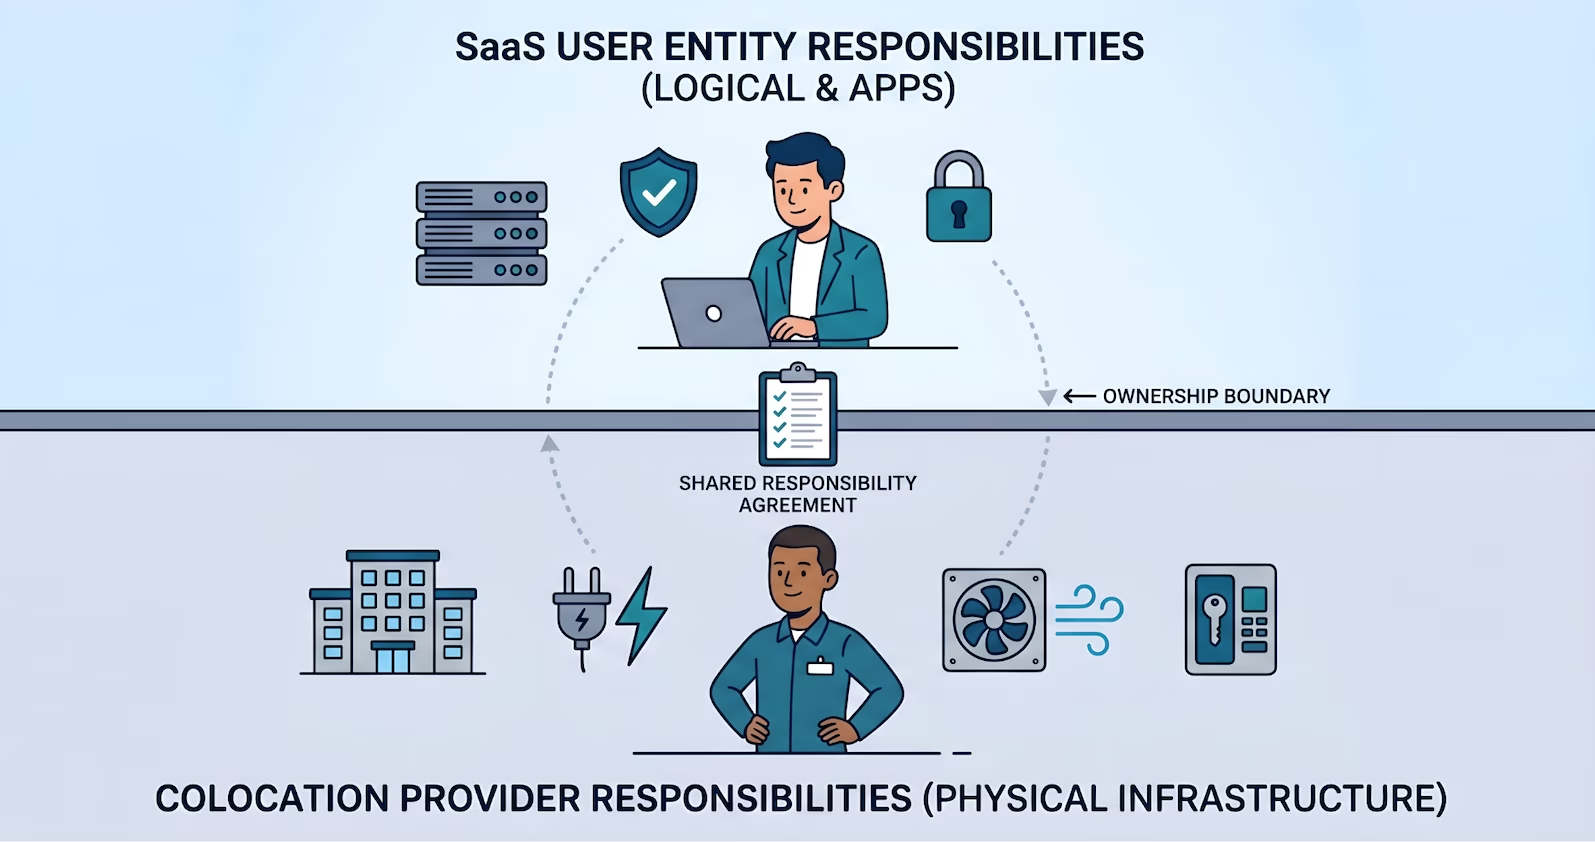
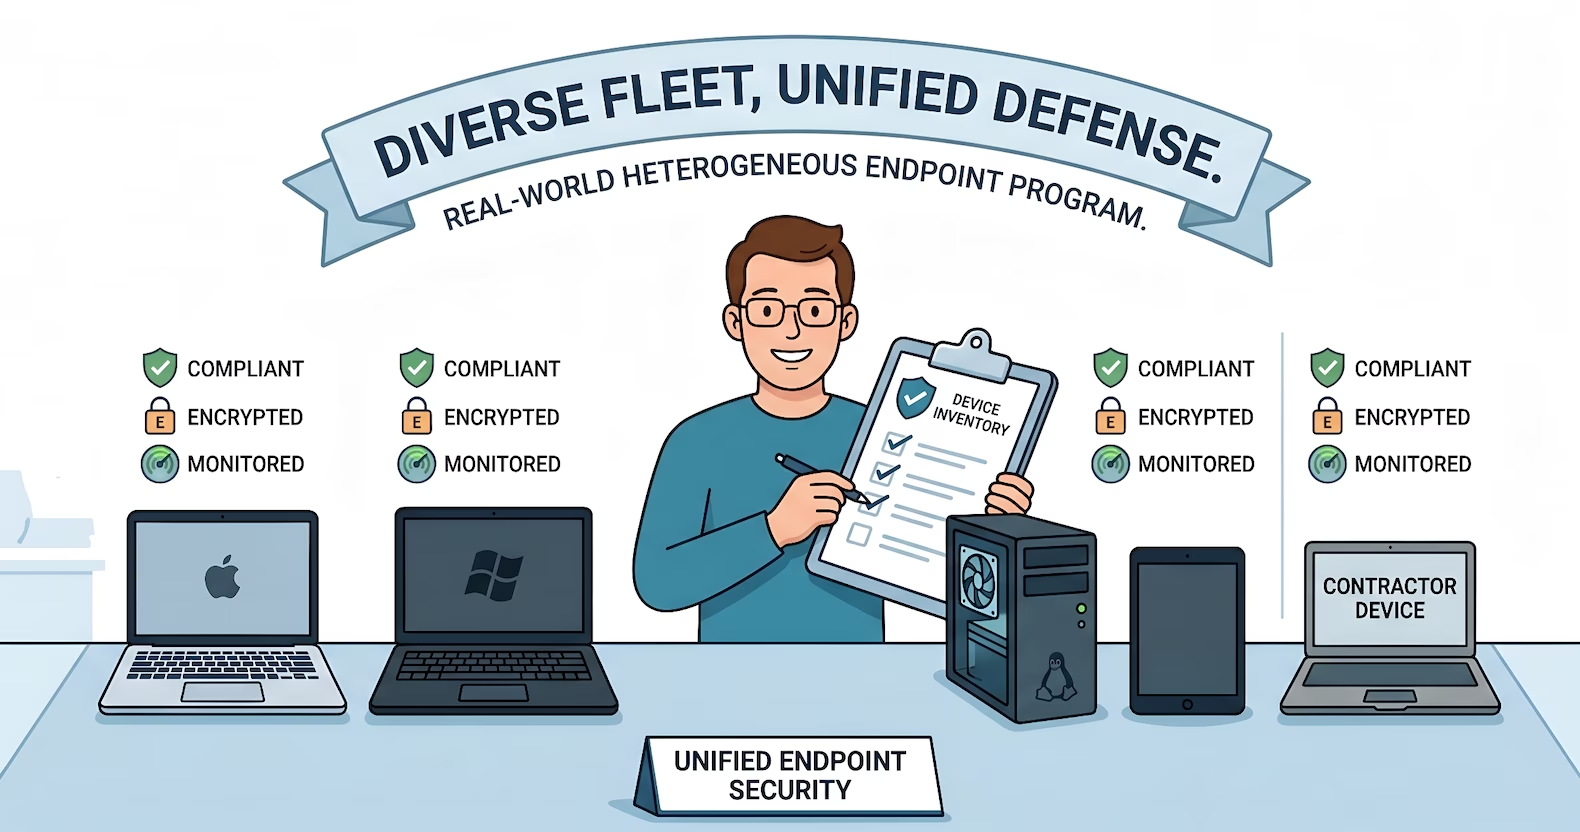
SOC 2 endpoint security rests mainly on CC6.1 (logical access, including endpoint devices) and CC6.8 (anti-malware and software control), with CC6.7...