CybersecurityIncidentIncident ResponseAI



Co-Founder & Principal Consultant, CISSP, CCSP
Former security architect for Bank of Canada and Payments Canada. 20+ years building compliance programs for critical infrastructure. Ali leads Truvo's SOC 2, ISO 27001, and CMMC engagements, bringing enterprise-grade security architecture to growing companies.
Follow on LinkedIn →
We recently used frontier AI throughout an incident response engagement, from the first log query to the final incident report. This is how it went,...
Truvo Cyber is a Canadian cybersecurity firm that implements ISO/IEC 42001, the AI management system standard, for SaaS and technology companies...
A SOC 2 report must be issued by a licensed CPA firm, and Canadian companies can choose either a Canadian firm reporting under CSAE 3000 or a US firm...
Truvo Cyber is a Canadian cybersecurity firm that prepares defence suppliers for the Canadian Program for Cyber Security Certification (CPCSC):...
Truvo Cyber is a Canadian cybersecurity firm that implements ISO 27001 for SaaS, technology and infrastructure companies: gap assessment, ISMS build,...
SOC 2 and HIPAA test most of the same security controls, so a company that handles health data for healthcare customers can run one security program...
Phishing-resistant MFA in Microsoft Entra ID means signing in with a passkey, Windows Hello for Business or certificate-based authentication, methods...
Microsoft Identity Manager (MIM) 2016 SP2 reaches end of support on January 9, 2029. Microsoft extended the date from January 13, 2026, and its...
An Active Directory to Entra ID migration moves the source of authority for users, groups, devices and applications from on-premises domain...
HR-driven provisioning makes the HR system the source of truth for identity: a hire in the HR platform creates the account, a change of role updates...
The fastest way to check a site for PHP2Shell is to run the free PHP2Shell checker, which reads the PHP version the site advertises and compares it...
On October 21, 2026, Railway disclosed that an unauthorized third party may have accessed the encrypted environment variables of its customers and,...
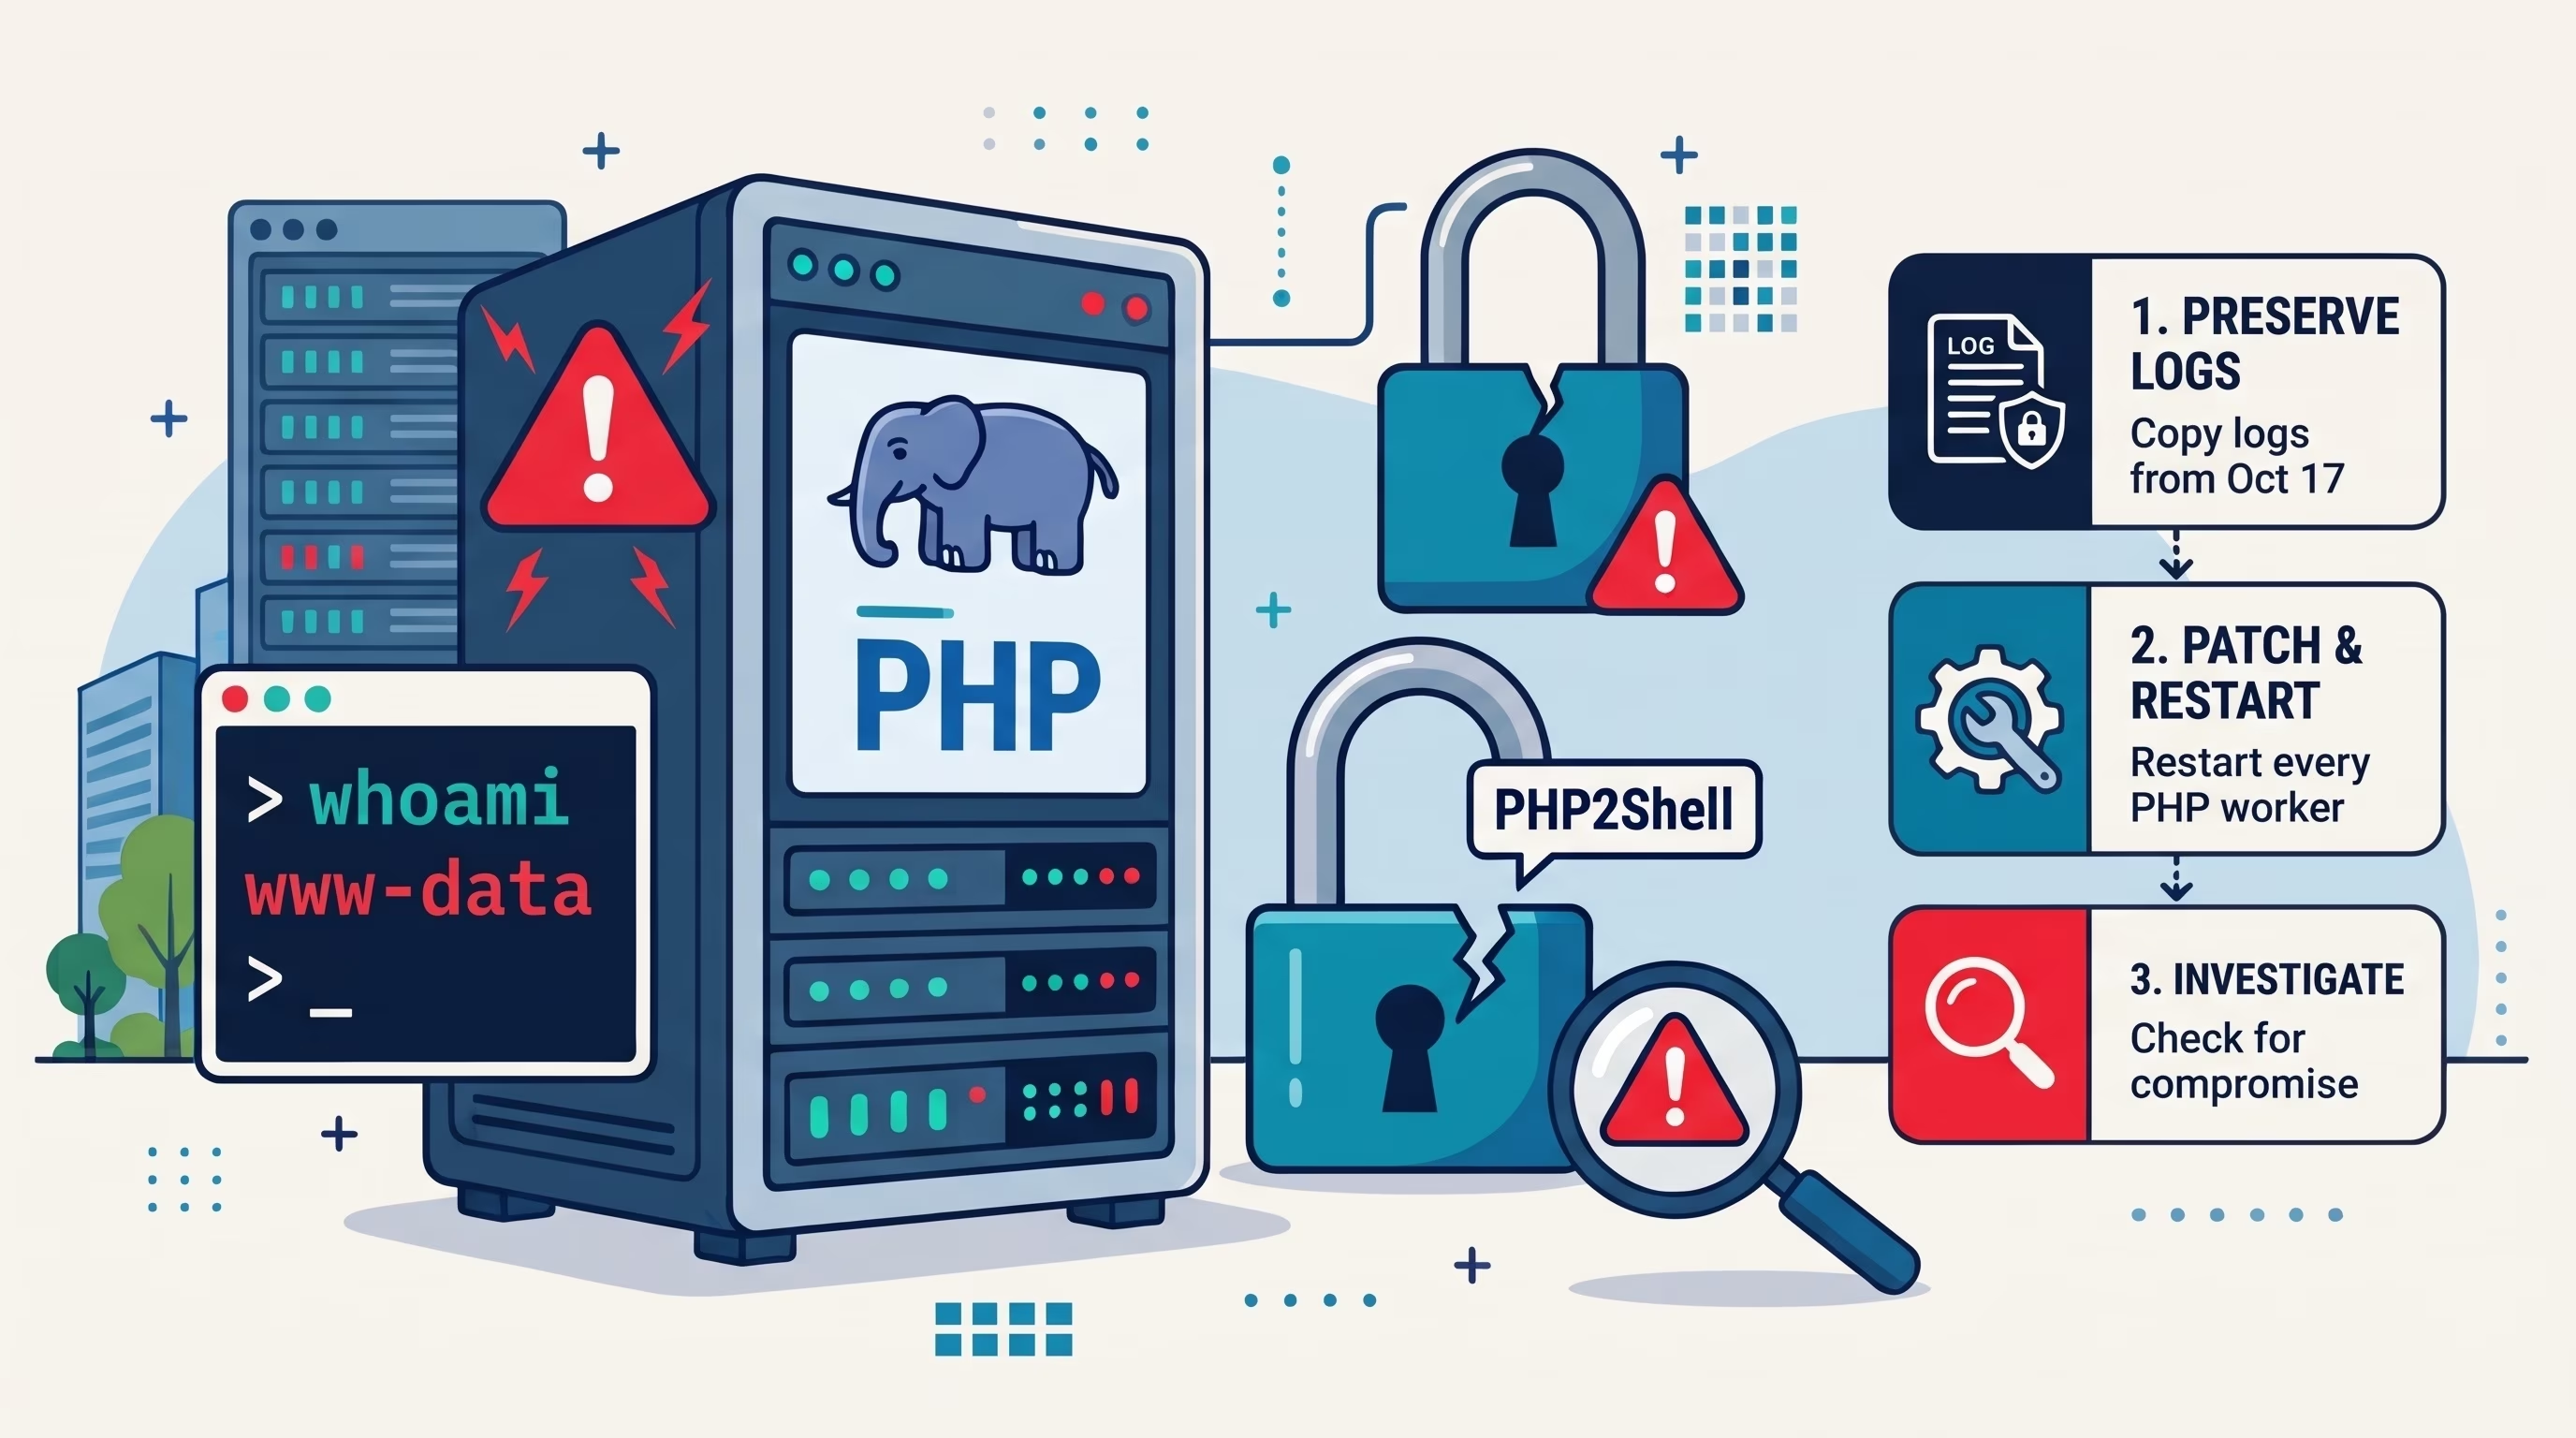
PHP2Shell is two critical flaws in the PHP engine, CVE-2026-109618 and CVE-2026-109619, that allow remote code execution without a login on PHP web...
Agentic AI security architecture starts with a map of the components of an AI agent system and the connections between them, which sets the scope,...
Self-hosted automation platforms meet SOC 2 the same way any other in-scope system does: the platform goes into scope, and the company shows access...
A security questionnaire process is the repeatable way a company receives, answers, packages and follows up on the security reviews its customers...
SOC 2 processing integrity is the optional Trust Services Category (criteria PI1.1 to PI1.5) that tests whether a system processes data completely,...
SOC 2 availability asks a company to meet the availability commitments it makes to customers, and the criteria (A1.1, A1.2 and A1.3) name no second...
SOC 2 scope can leave out development and test servers, but it includes the source code repository, the CI/CD pipeline and any internal team whose...
SOC 2 audit preparation on on-prem infrastructure slows down in five places: infrastructure scanning and logging, application and container scanning,...
Vanta and Drata work for an on-prem SOC 2 program, and they automate the corporate half of it: identity, HR records, code review, endpoints,...
Datadog can supply SOC 2 evidence for vulnerability identification (CC7.1), security monitoring (CC7.2), alert evaluation (CC7.3), unauthorized or...
Hybrid cloud security monitoring applies the same detection, vulnerability scanning, and configuration checks to on-premises servers as to cloud...
Yes. Datadog Cloud SIEM is Datadog's security information and event management (SIEM) product. It applies threat detection rules to the logs already...
Datadog Cloud Security Management checks hosts, containers, and cloud accounts for software vulnerabilities and insecure settings. It uses the same...
IEC 62443 is a series of international standards, developed by the IEC and ISA, for securing industrial automation and control systems (IACS). A...
The EU Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, is an EU law that sets mandatory cybersecurity requirements for hardware and software...
An infrastructure provider can meet SOC 2, ISO 27001 and HIPAA with one security program, because all three test the same capabilities: risk...
On-prem SOC 2 costs more than a cloud SOC 2 mainly in readiness: in Truvo Cyber engagements, a readiness assessment for a cloud SMB of up to 100...
SOC 2 for a semiconductor company covers the service customers buy, such as hosted compute, an API, SDK delivery and the customer data behind them,...