Cybersecurity


45 posts
The fastest way to check a site for PHP2Shell is to run the free PHP2Shell checker, which reads the PHP version the site advertises and compares it ...
On October 21, 2026, Railway disclosed that an unauthorized third party may have accessed the encrypted environment variables of its customers and,...
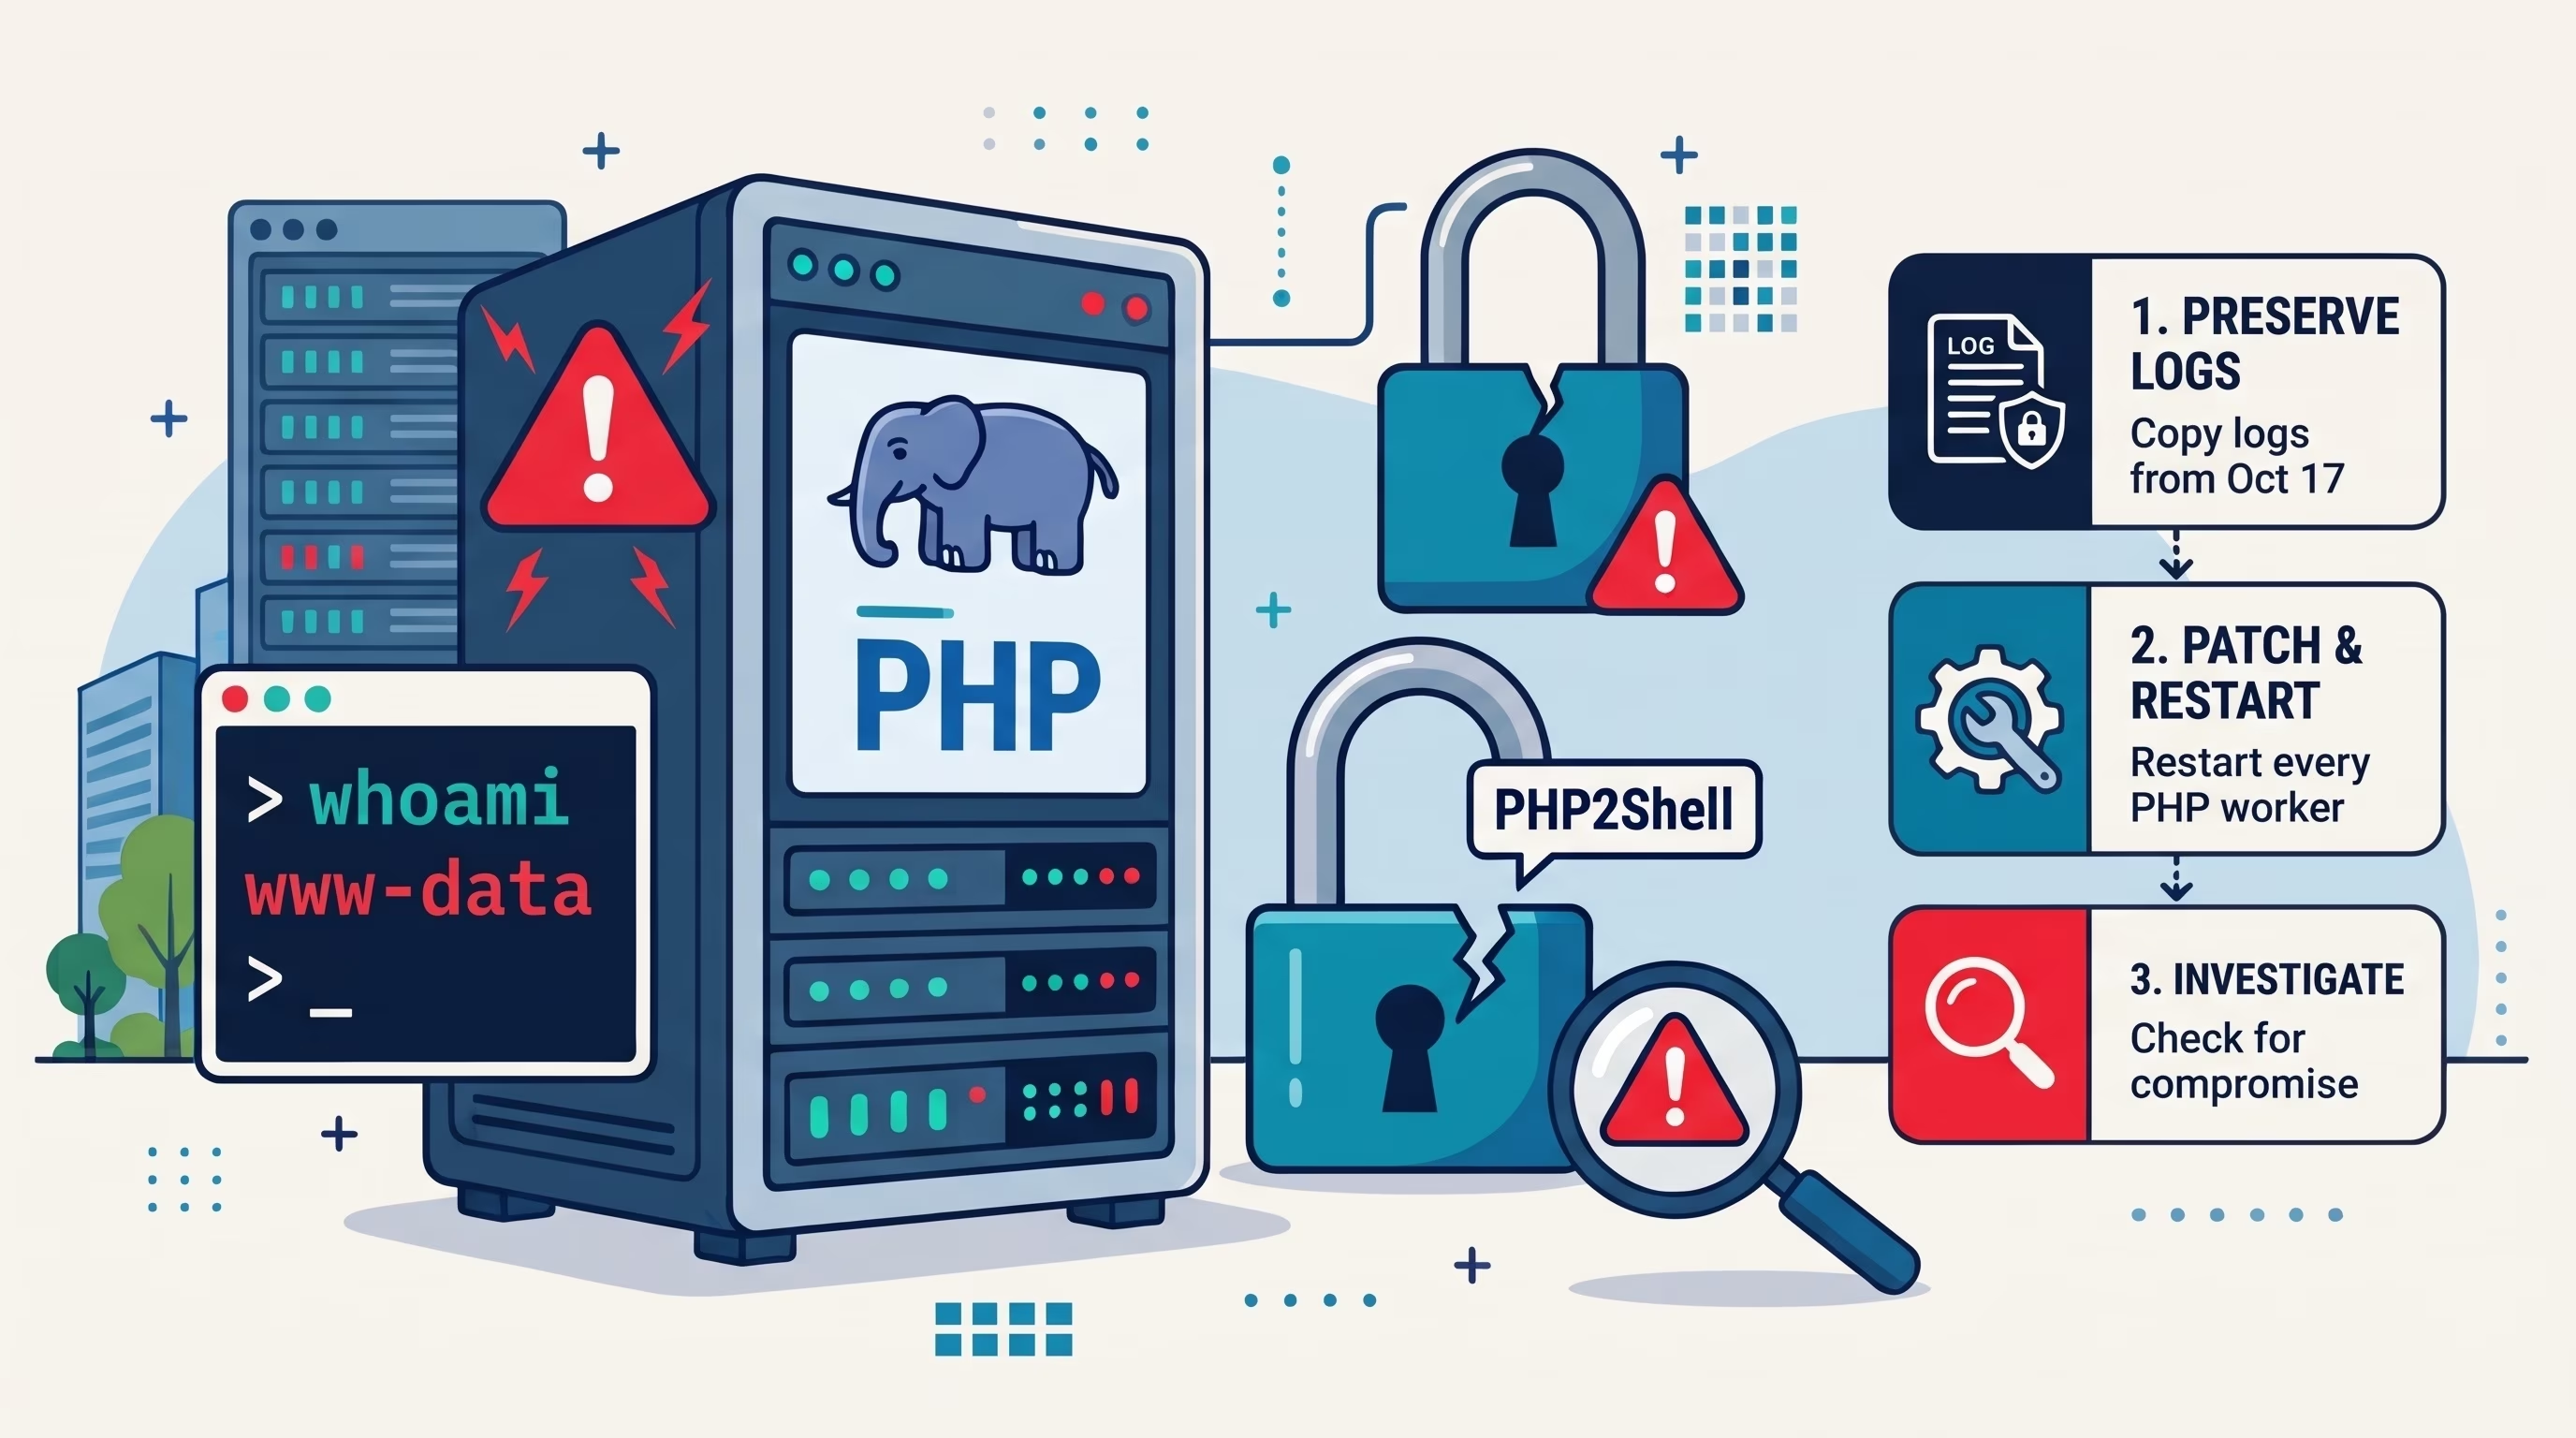
PHP2Shell is two critical flaws in the PHP engine, CVE-2026-109618 and CVE-2026-109619, that allow remote code execution without a login on PHP web...
Agentic AI security architecture starts with a map of the components of an AI agent system and the connections between them, which sets the scope,...
Datadog can supply SOC 2 evidence for vulnerability identification (CC7.1), security monitoring (CC7.2), alert evaluation (CC7.3), unauthorized or...
Hybrid cloud security monitoring applies the same detection, vulnerability scanning, and configuration checks to on-premises servers as to cloud...
Yes. Datadog Cloud SIEM is Datadog's security information and event management (SIEM) product. It applies threat detection rules to the logs already...
Datadog Cloud Security Management checks hosts, containers, and cloud accounts for software vulnerabilities and insecure settings. It uses the same...
The EU Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, is an EU law that sets mandatory cybersecurity requirements for hardware and software...
A neocloud is a cloud provider built around renting GPU compute for AI training and inference, often on bare metal servers, with far fewer managed...
A Jobber account holds client names, addresses, job history, and, for businesses using Jobber Payments, saved payment details. It is also the system...
A Google Workspace account is not secured by default just because Google operates the infrastructure behind it. Google secures the servers; the...
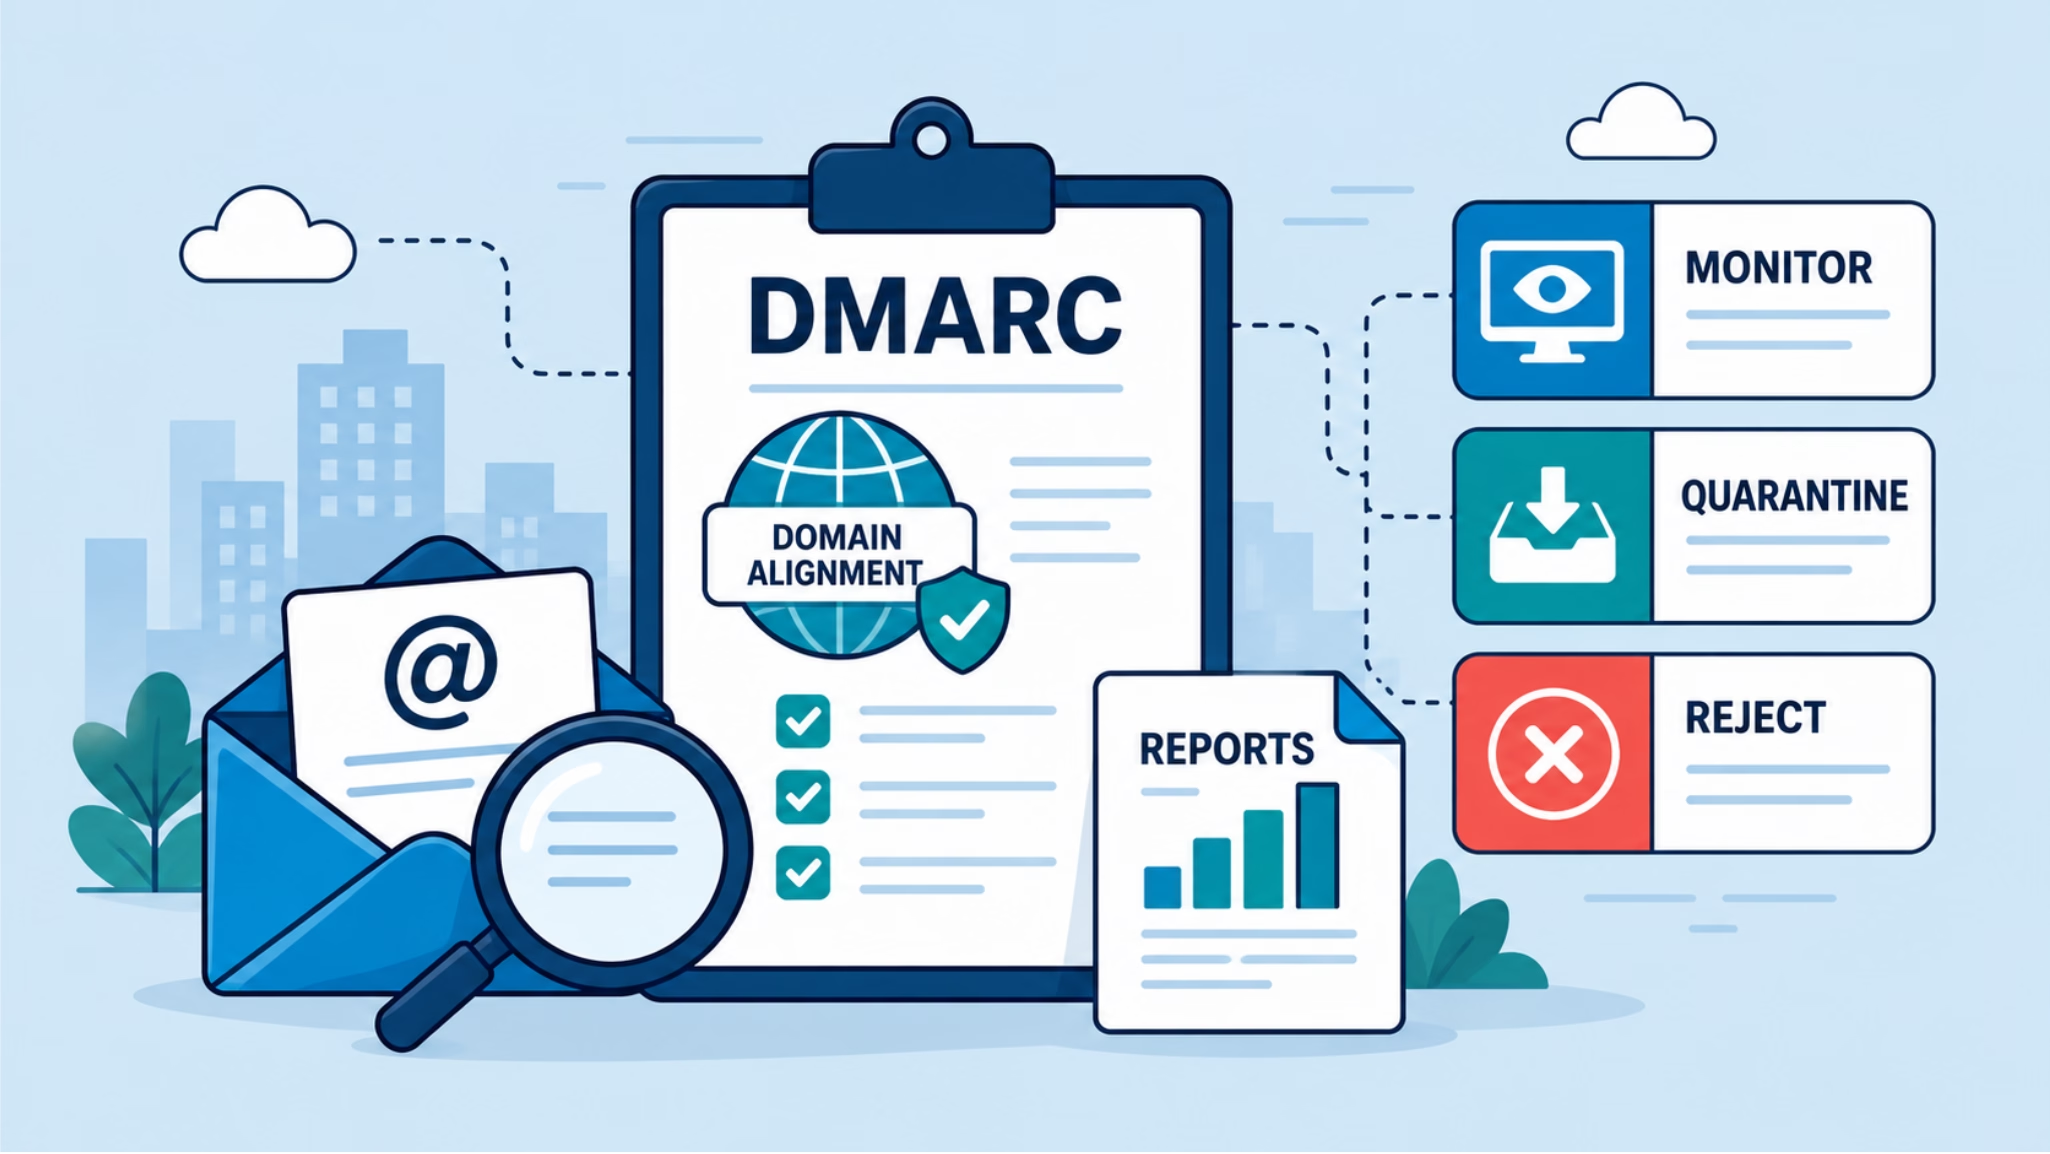
A DMARC check looks at a message that has already gone through SPF and DKIM, and asks one more question: does the domain that passed either of those...
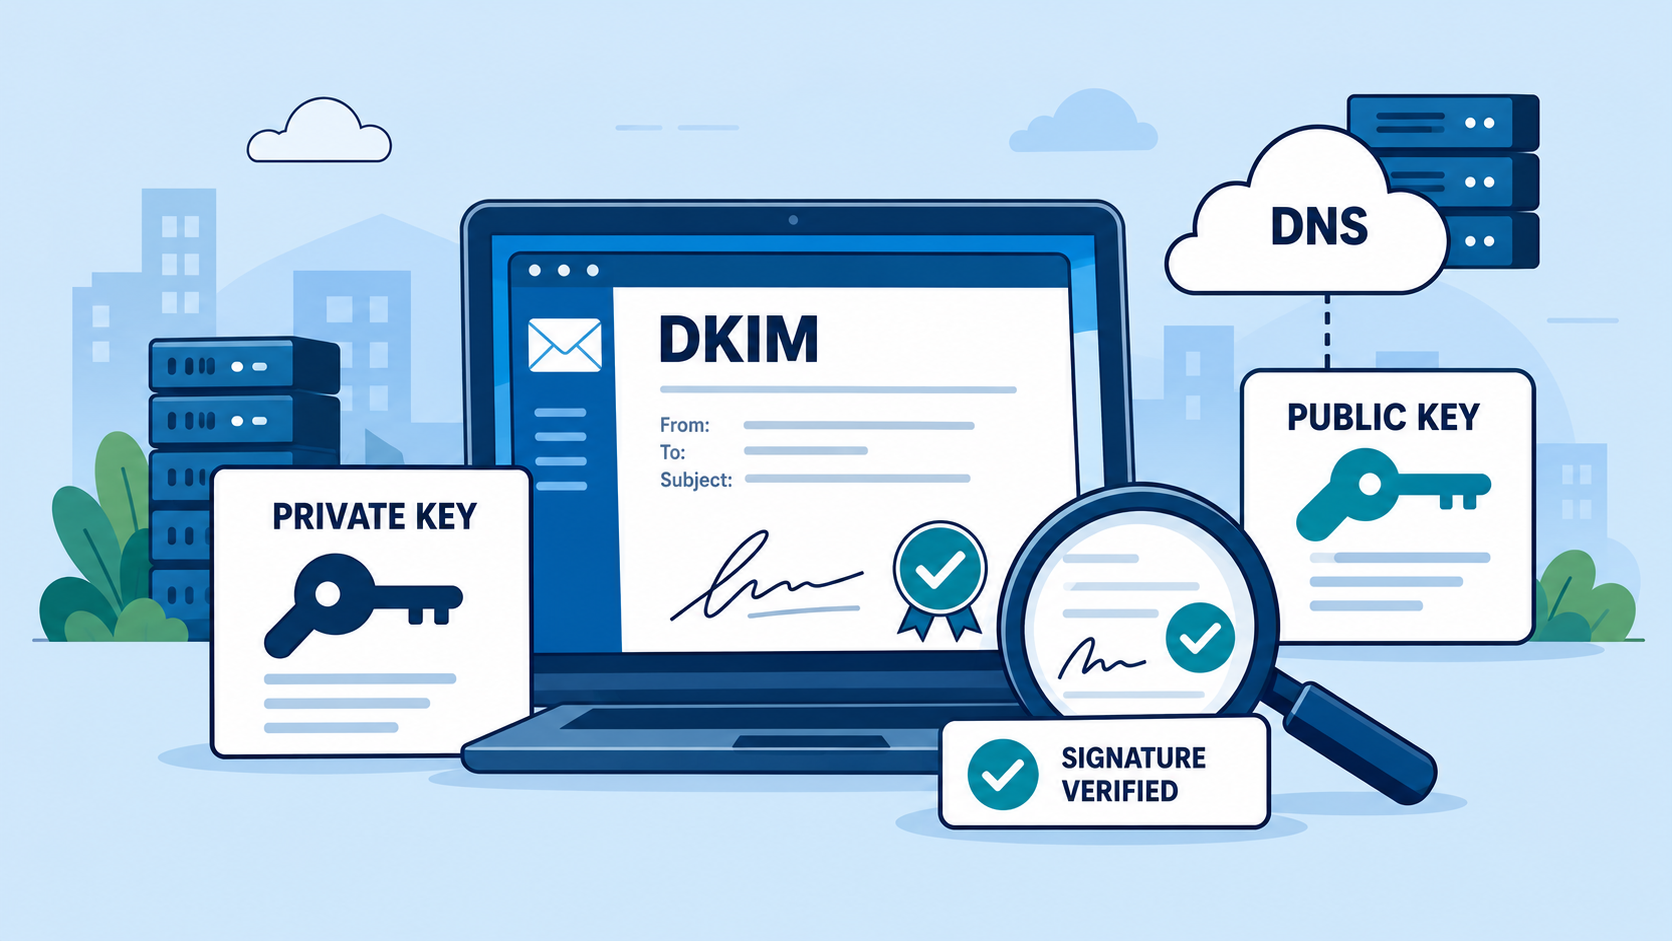
A DKIM check confirms two things about a message: 1) that a system holding the sending domain's private key signed it, and 2) that the signed parts...
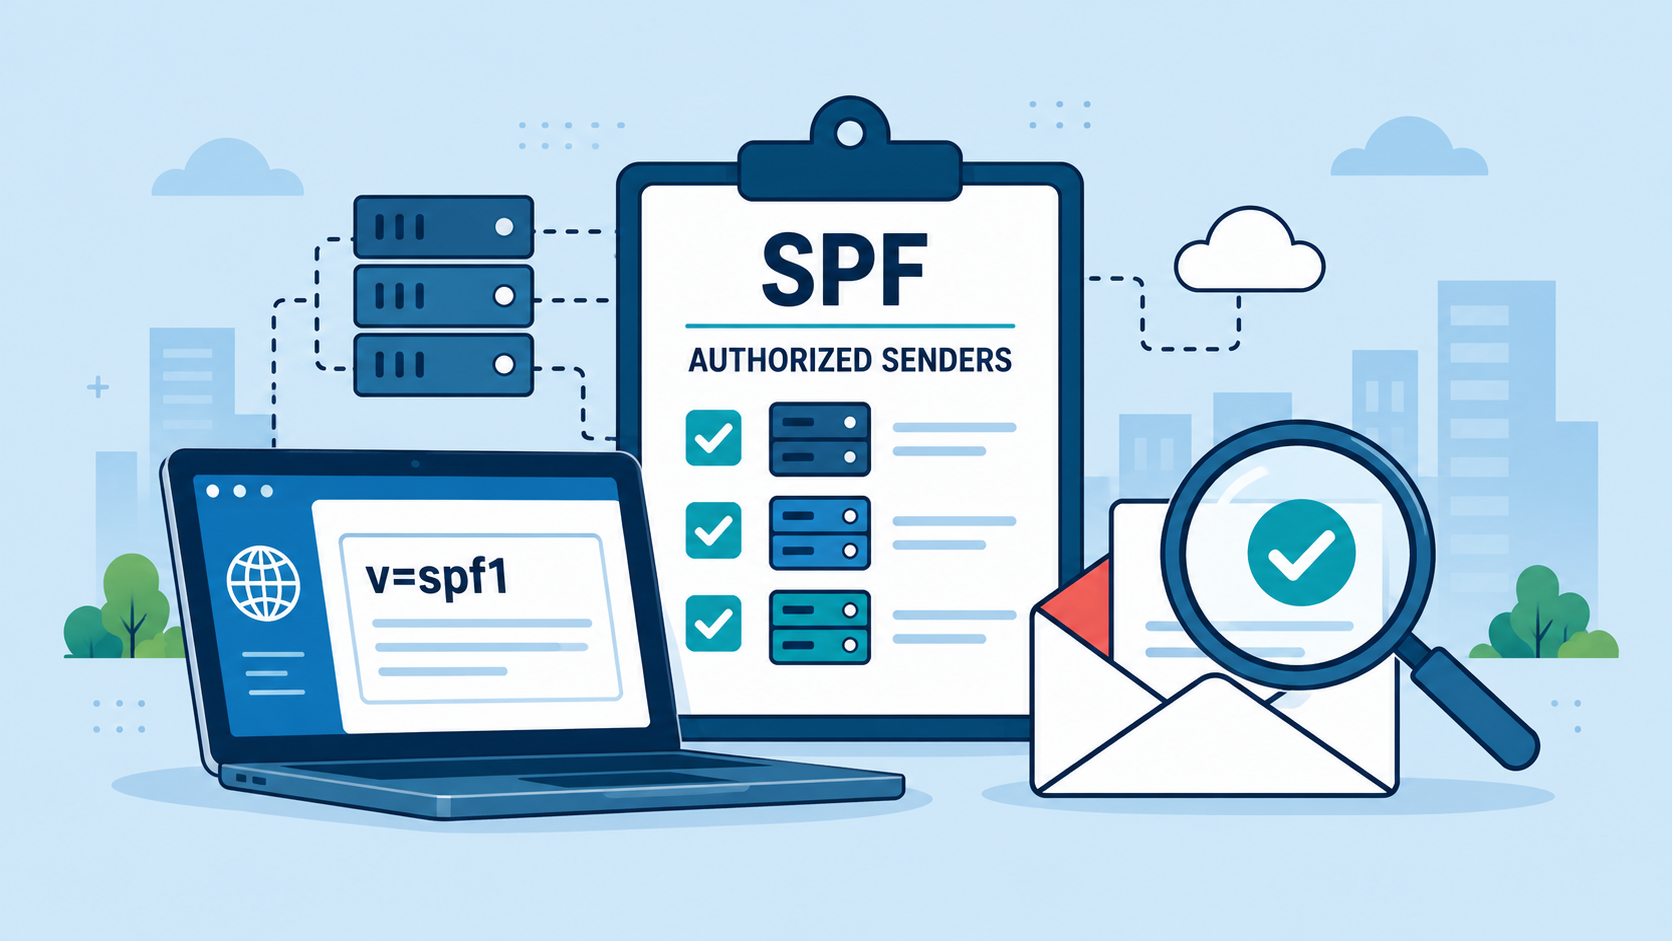
When a message arrives, the receiving mail server checks the sending domain's SPF record before it does almost anything else with the message. It...
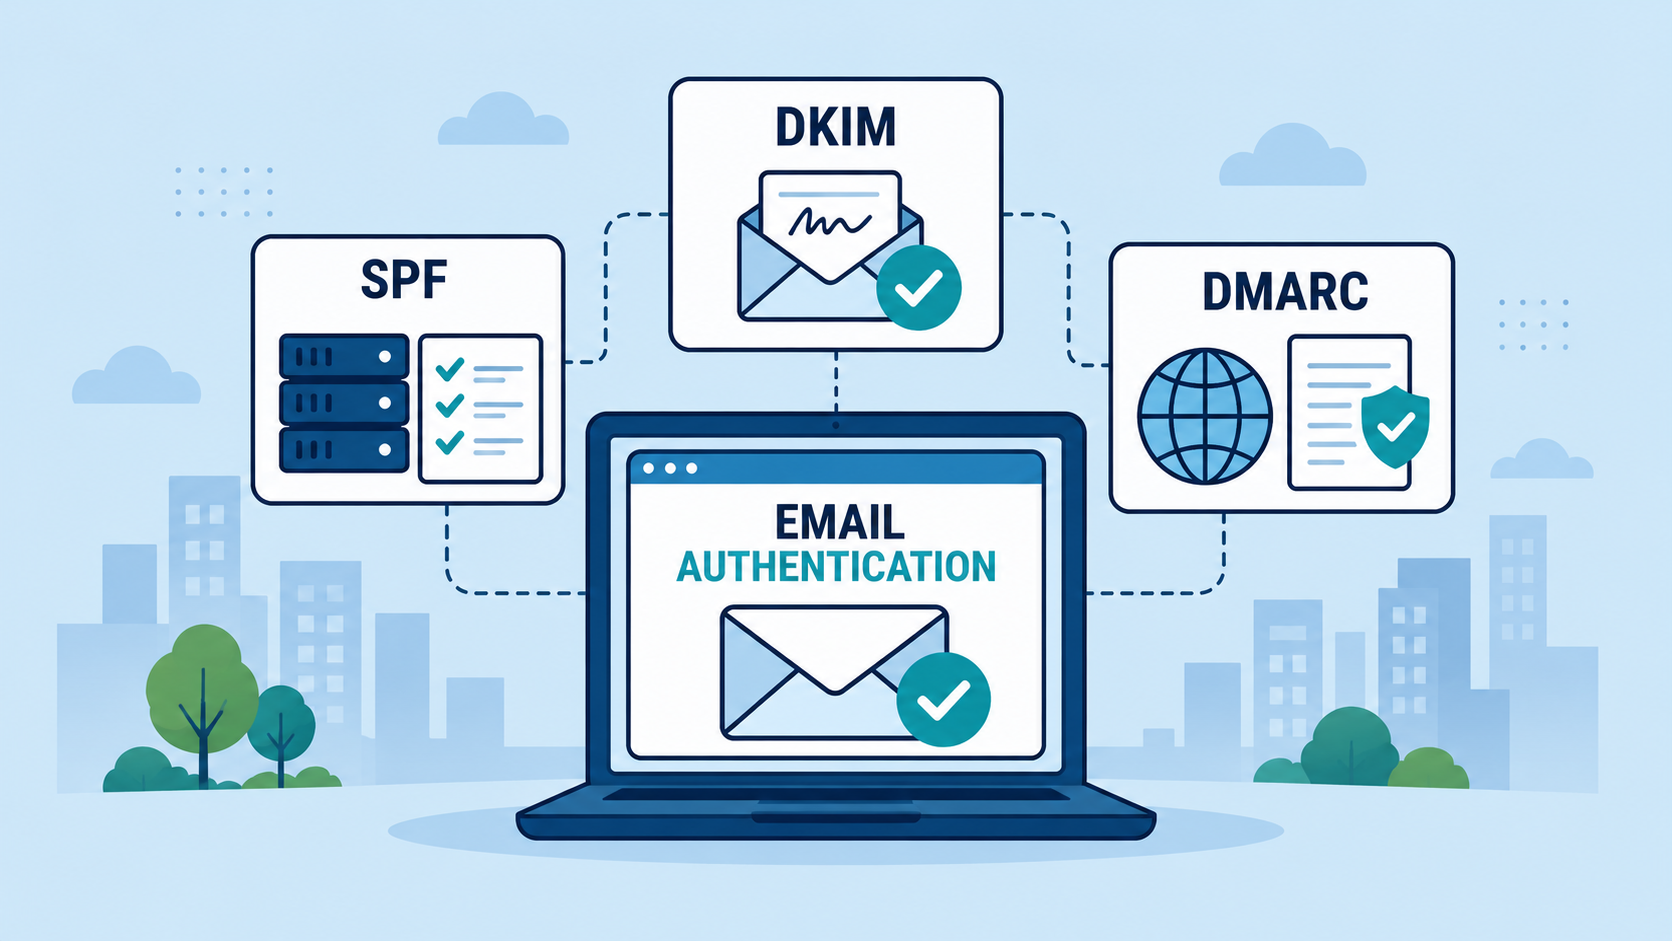
SPF, DKIM and DMARC work as a team to stop attackers from sending email that looks like it comes from a domain they do not control. SPF checks...
The right vCISO service for a mid-market SaaS company is the one that owns and runs the security program end to end, on a fractional basis, the way a...
A security architect does three jobs: sets security requirements for systems other people design, assesses and reviews those designs, and solutions...
When an application portfolio is too large to pen-test, an inquiry-based maturity assessment gets you a defensible, board-ready picture in weeks...
It's tempting to centralize identity by buying a platform, but I leave the platform for last. Below is my approach to solutioning centralized...
Security architecture is the practice of designing how people, process, and technology work together to protect an organization's systems. It is not...
Security architecture is the practice of understanding a system component by component and connection by connection. In practice it comes down to two...
A security architecture diagram is a boxes-and-arrows drawing of a system: boxes for the key components, arrows for the data flows or network flows...
Advice on security architecture and design should come from someone with a deep understanding of cybersecurity practice: ideally ten or more years in...
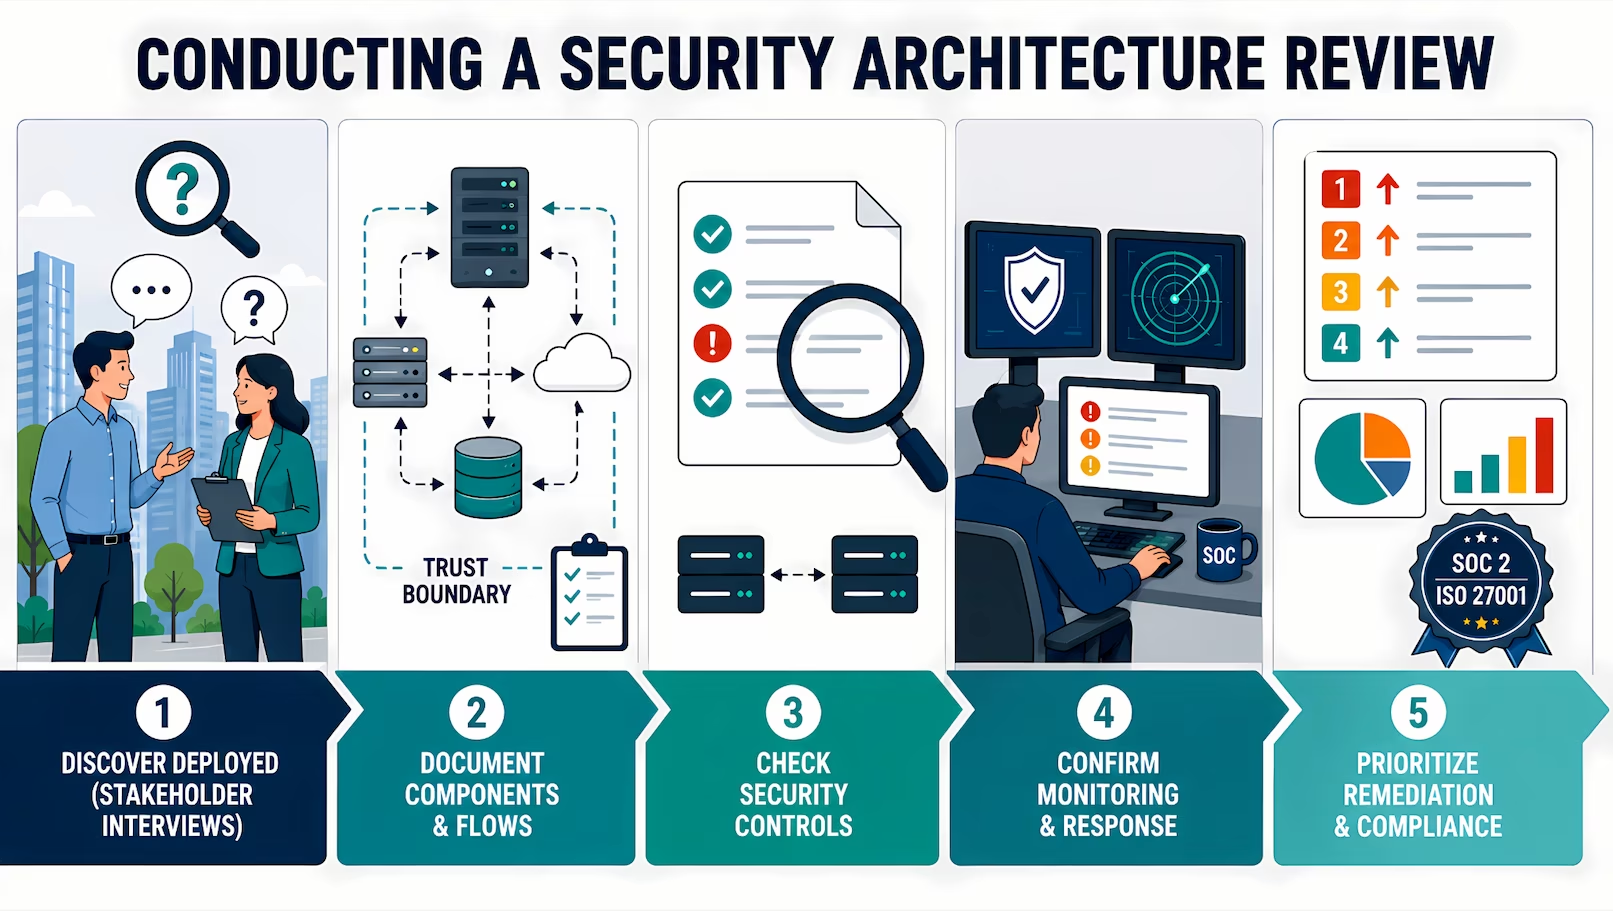
A security architecture review is a structured walk through a system's components and connections, checking each against security best practices and...
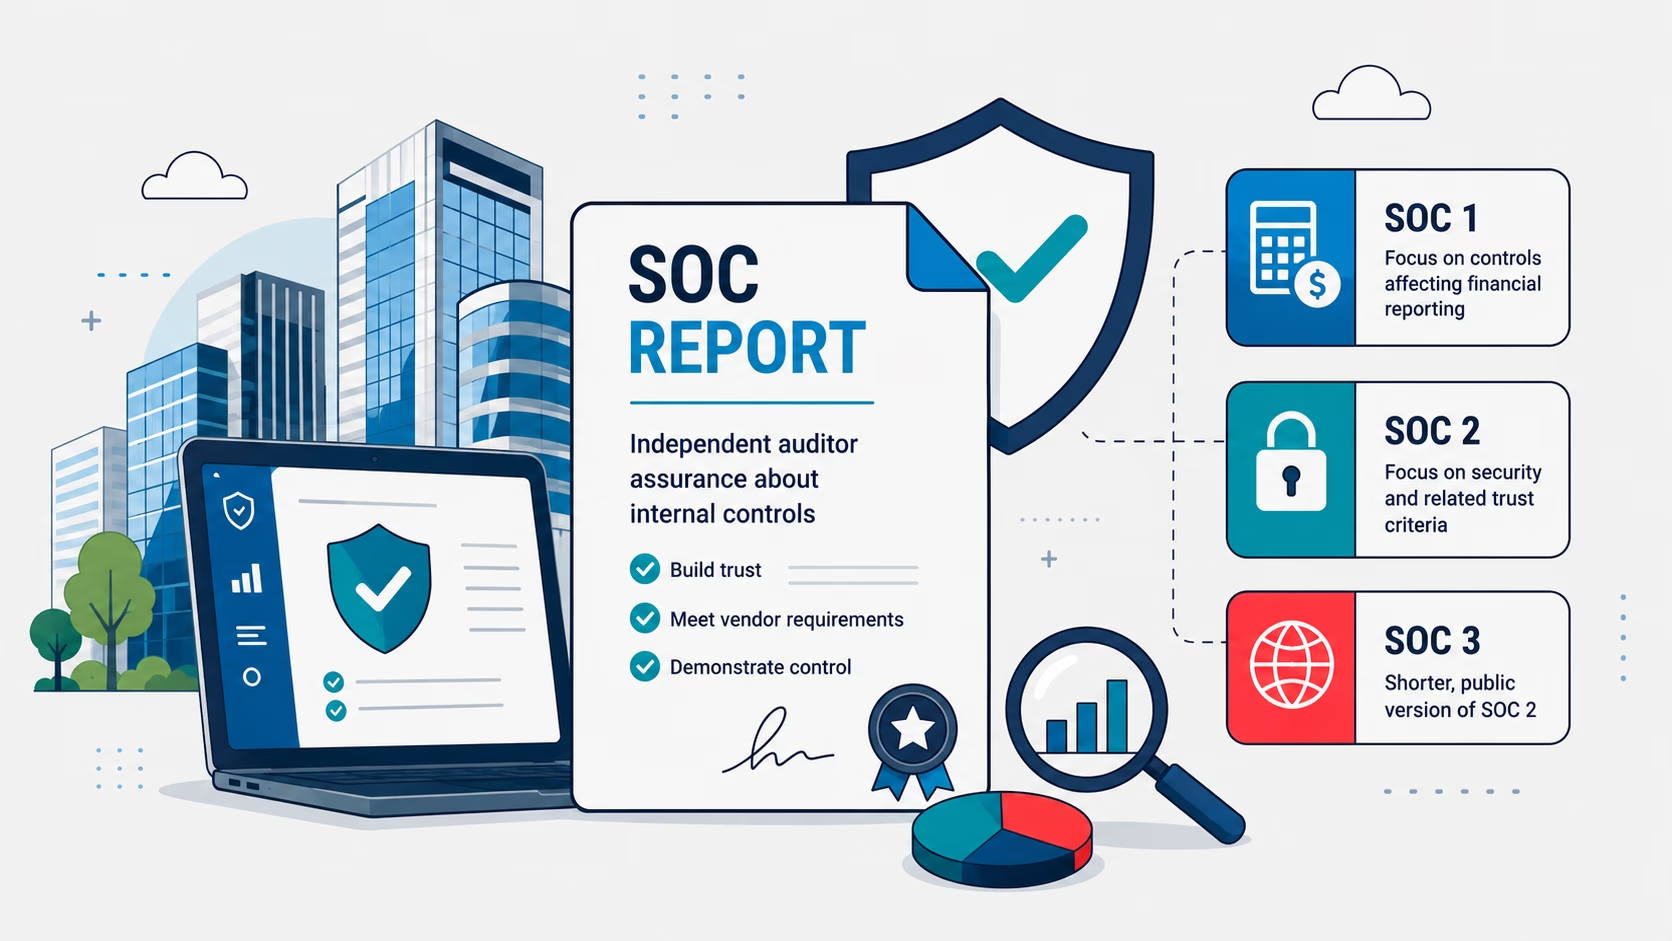
A SOC report (System and Organization Controls report) is an independent auditor's attestation report on a service organization's controls, issued by...
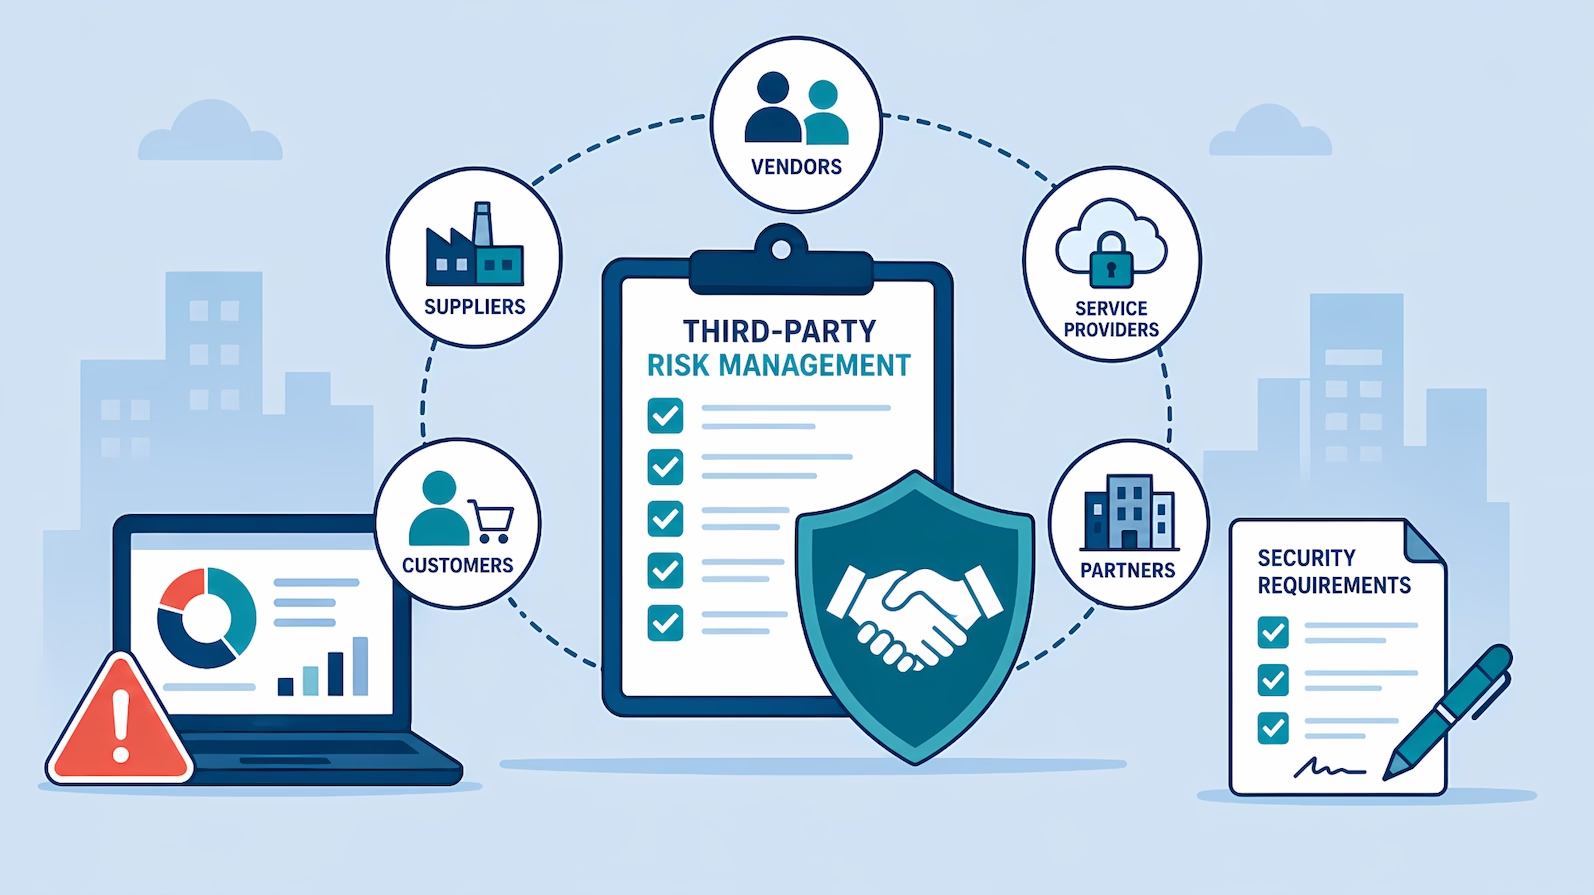
Third party risk management (TPRM) is the discipline of identifying, assessing, and controlling the risks that come from the external organizations a...
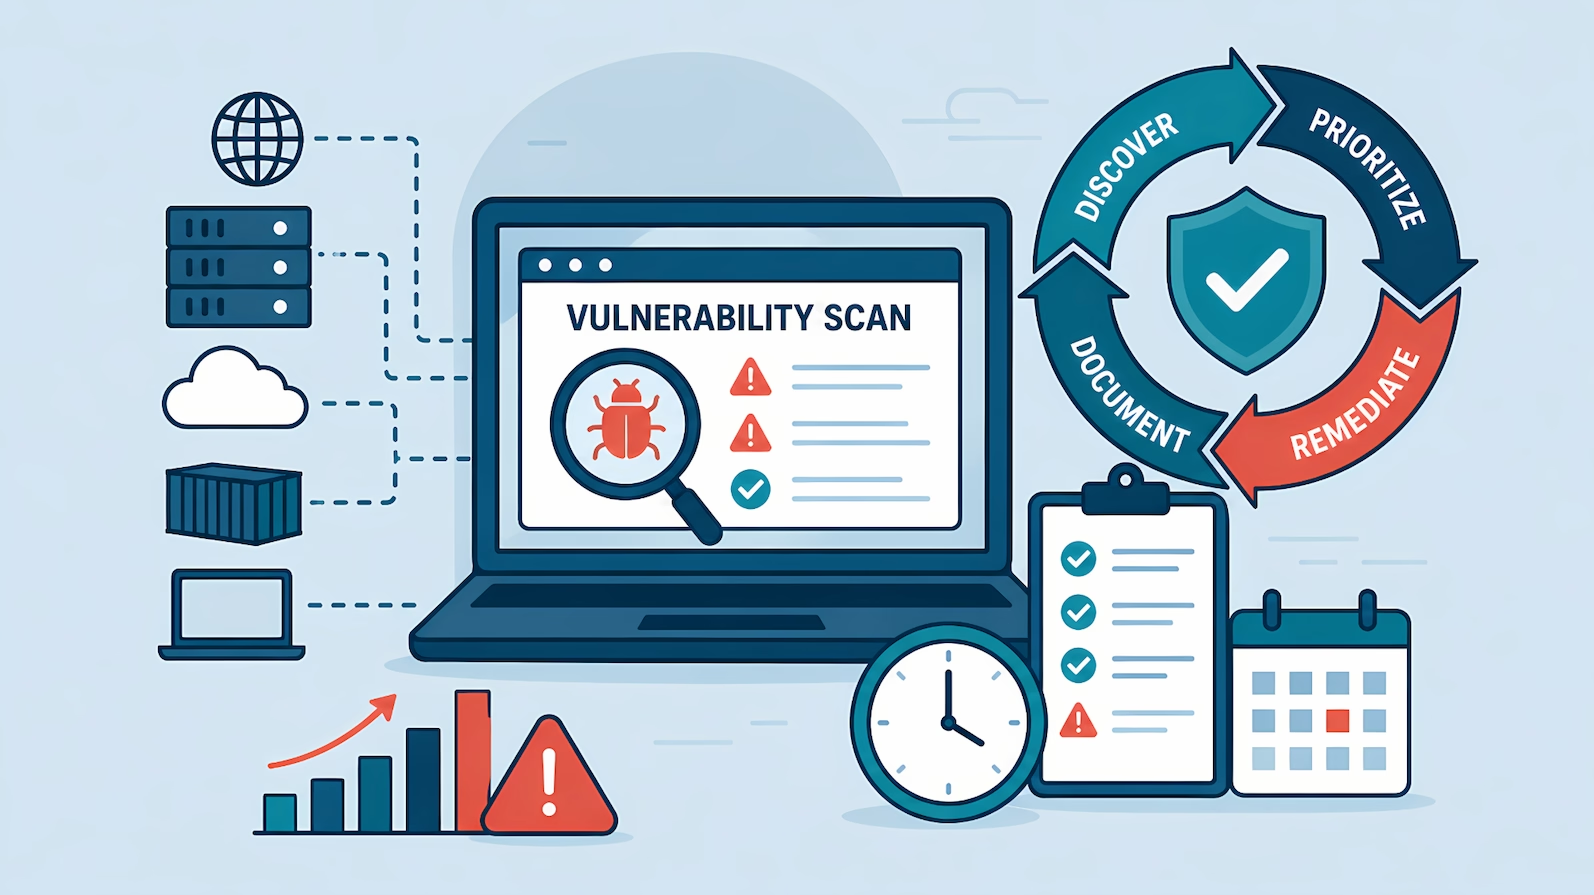
A vulnerability scan is an automated check that compares systems, software, and configurations against a database of known security weaknesses and...
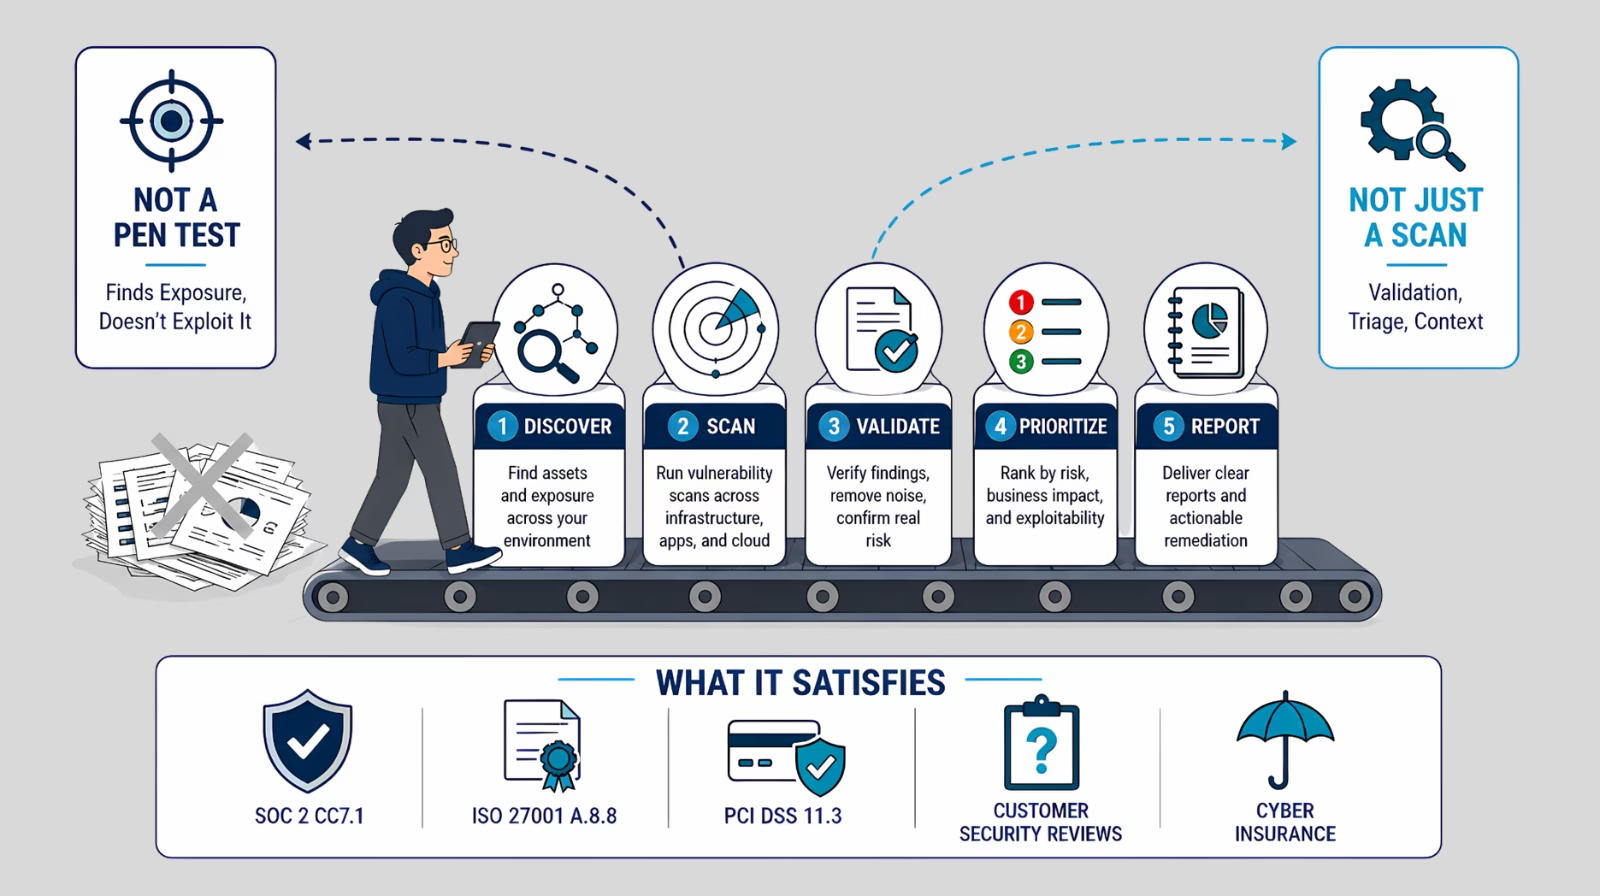
Vulnerability assessment services are engagements where a third party inventories an environment, scans it for known security weaknesses, validates...
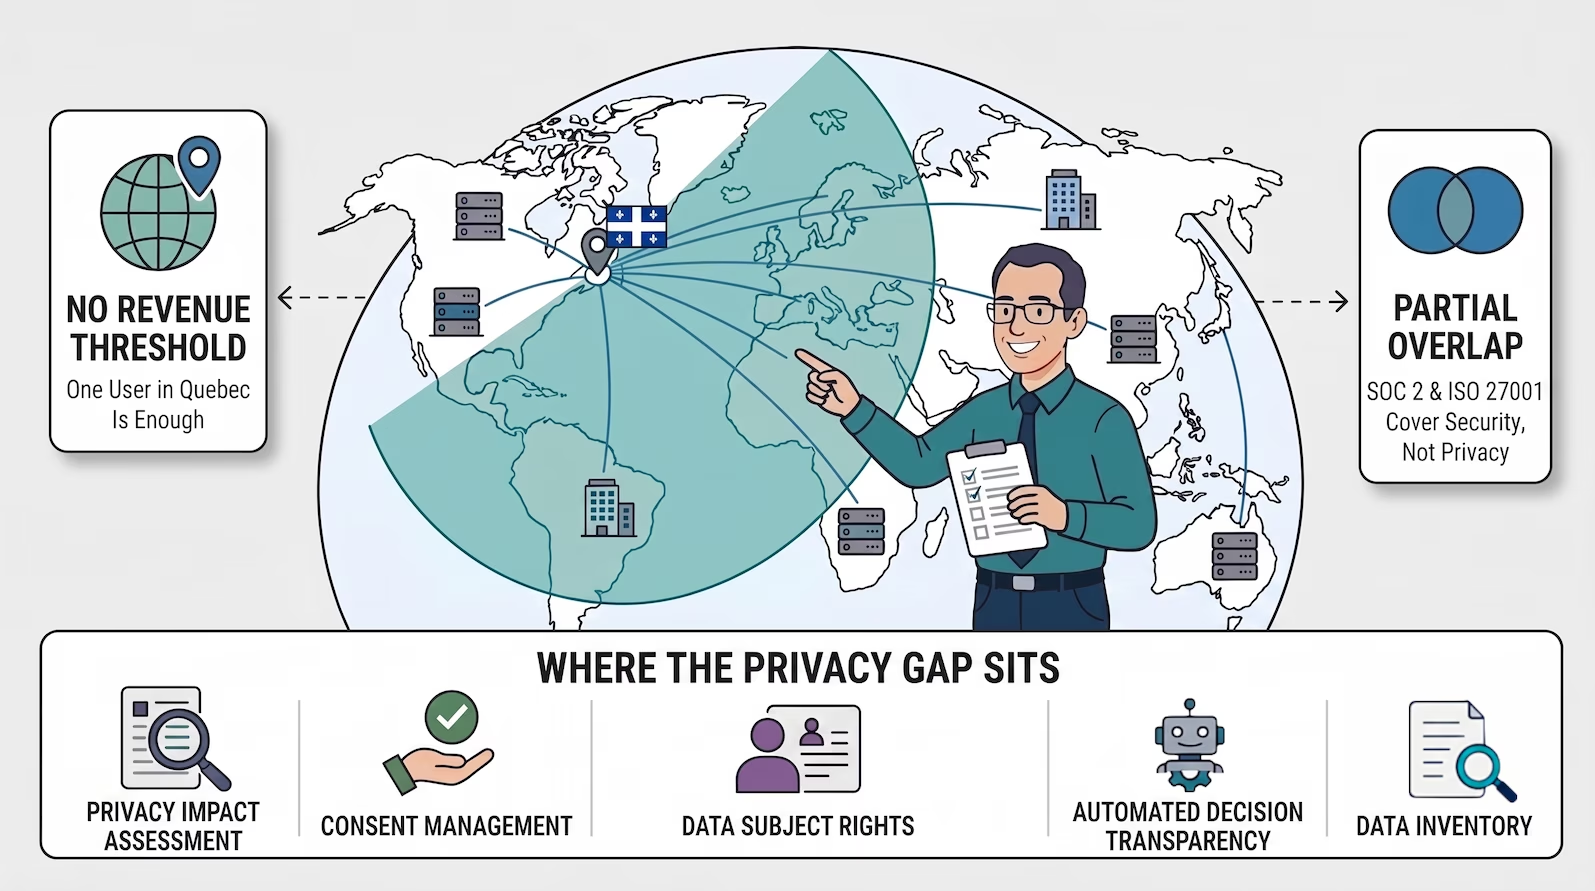
Quebec Law 25 is the province's modernized private-sector privacy law: a set of amendments (adopted in 2021 as Bill 64) to the Act respecting the...