Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

Close-up of dual computer monitors with green coding interfaces in a dark room, highlighting cyber security themes, illustrating Datadog Cloud Security Management: Vulnerability and Misconfiguration Scanning for SOC 2 and ISO 27001

Datadog Cloud Security Management: Vulnerability and Misconfiguration Scanning for SOC 2 and ISO 27001

Datadog Cloud Security Management checks hosts, containers, and cloud accounts for software vulnerabilities and insecure settings. It uses the same...
Aerial view of rows of rail freight cars in a rail yard, illustrating supply chain and third-party risk

EU Cyber Resilience Act (CRA): What It Is, Timeline and Requirements for Hardware and Software Makers

The EU Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, is an EU law that sets mandatory cybersecurity requirements for hardware and software...
Dynamic urban scene showcasing interconnected light trails representing digital communication networks, illustrating What Is a Neocloud? Definition, Examples, and What It Means for Compliance

What Is a Neocloud? Definition, Examples, and What It Means for Compliance

A neocloud is a cloud provider built around renting GPU compute for AI training and inference, often on bare metal servers, with far fewer managed...
How to Secure Your Jobber Account

How to Secure Your Jobber Account

A Jobber account holds client names, addresses, job history, and, for businesses using Jobber Payments, saved payment details. It is also the system...
Top Google Workspace Security Recommendations

Top Google Workspace Security Recommendations

A Google Workspace account is not secured by default just because Google operates the infrastructure behind it. Google secures the servers; the...
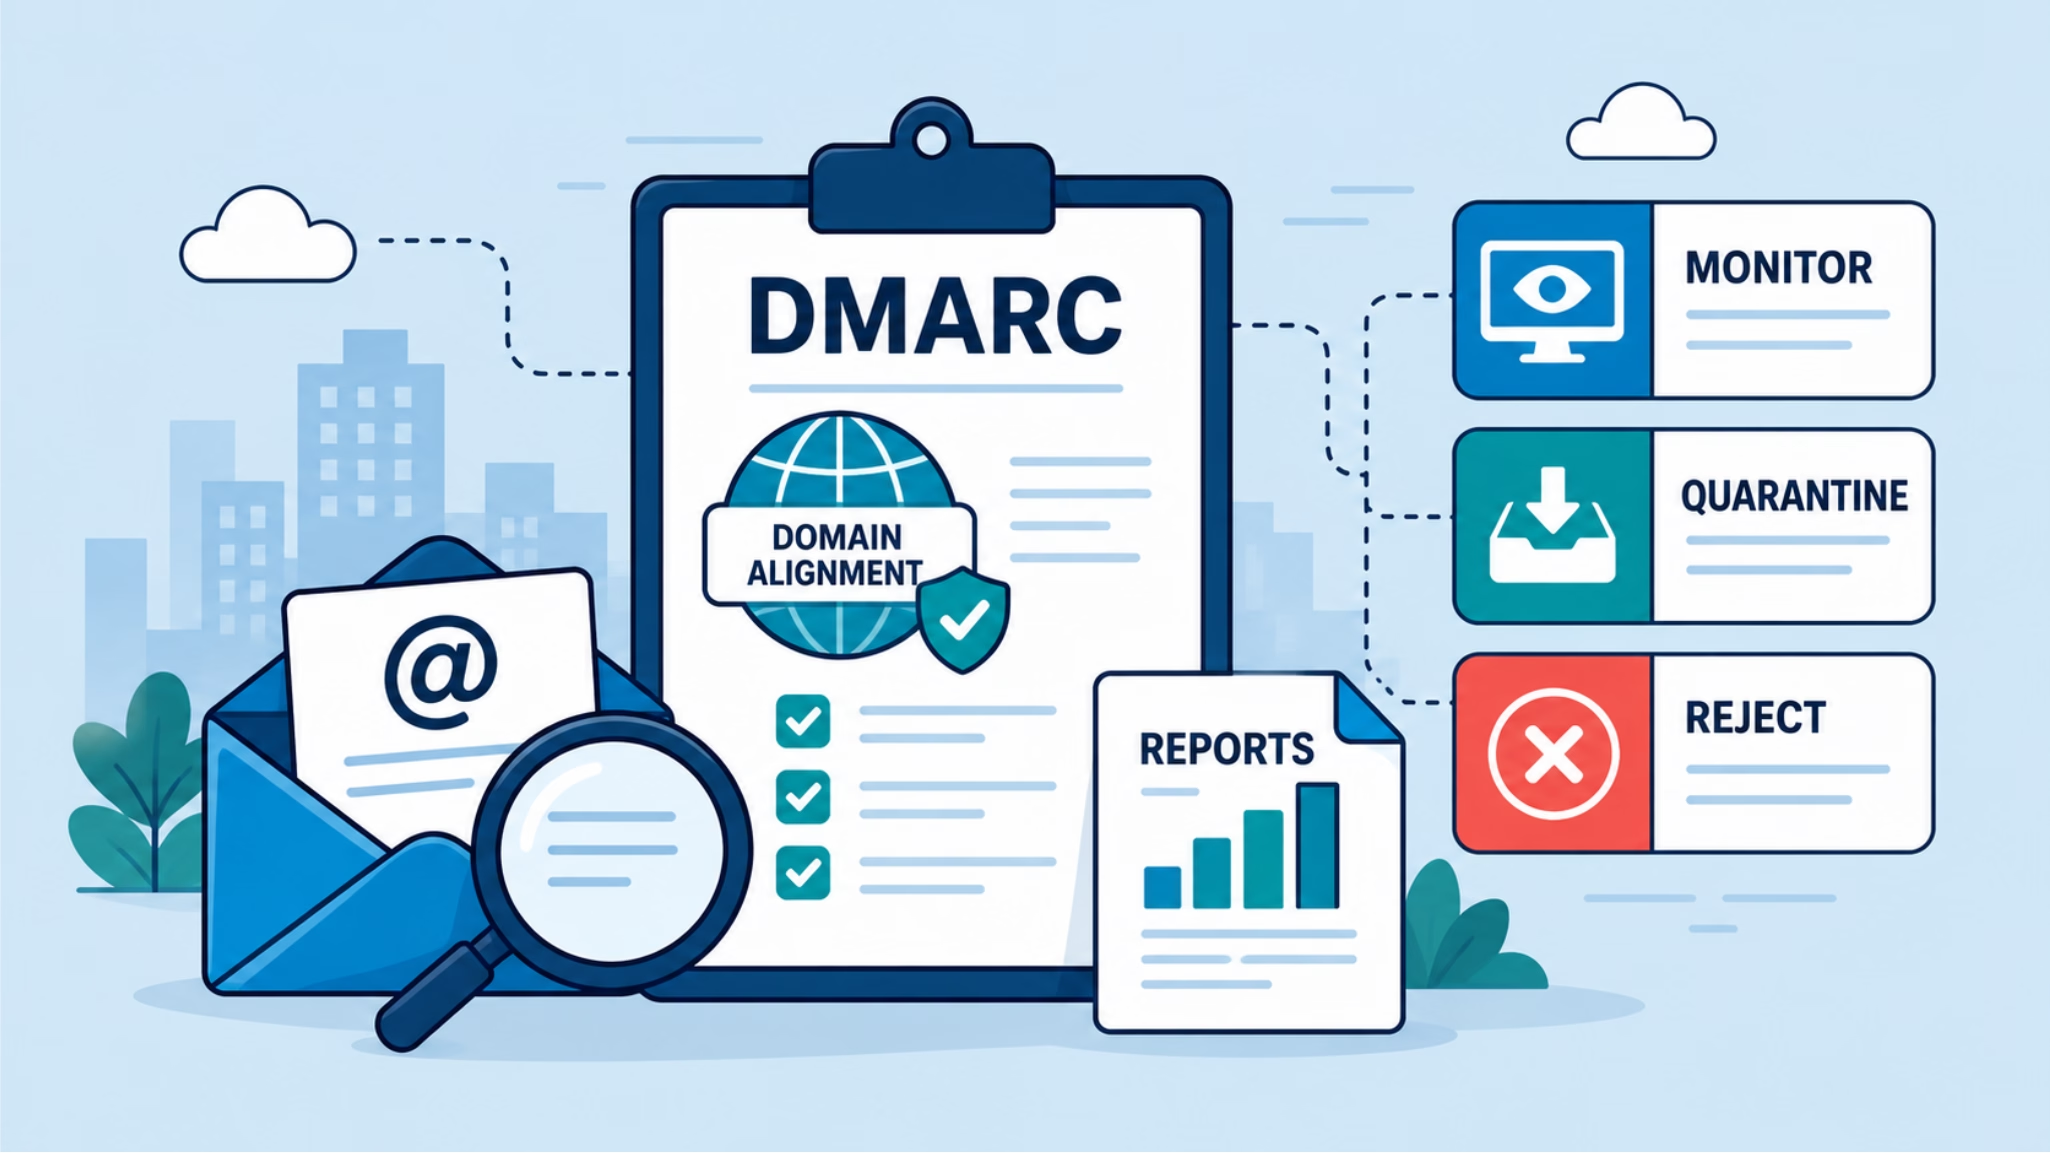
How Does a DMARC Check Work? A Step-by-Step Guide to DMARC Validation

How Does a DMARC Check Work? A Step-by-Step Guide to DMARC Validation

A DMARC check looks at a message that has already gone through SPF and DKIM, and asks one more question: does the domain that passed either of those...
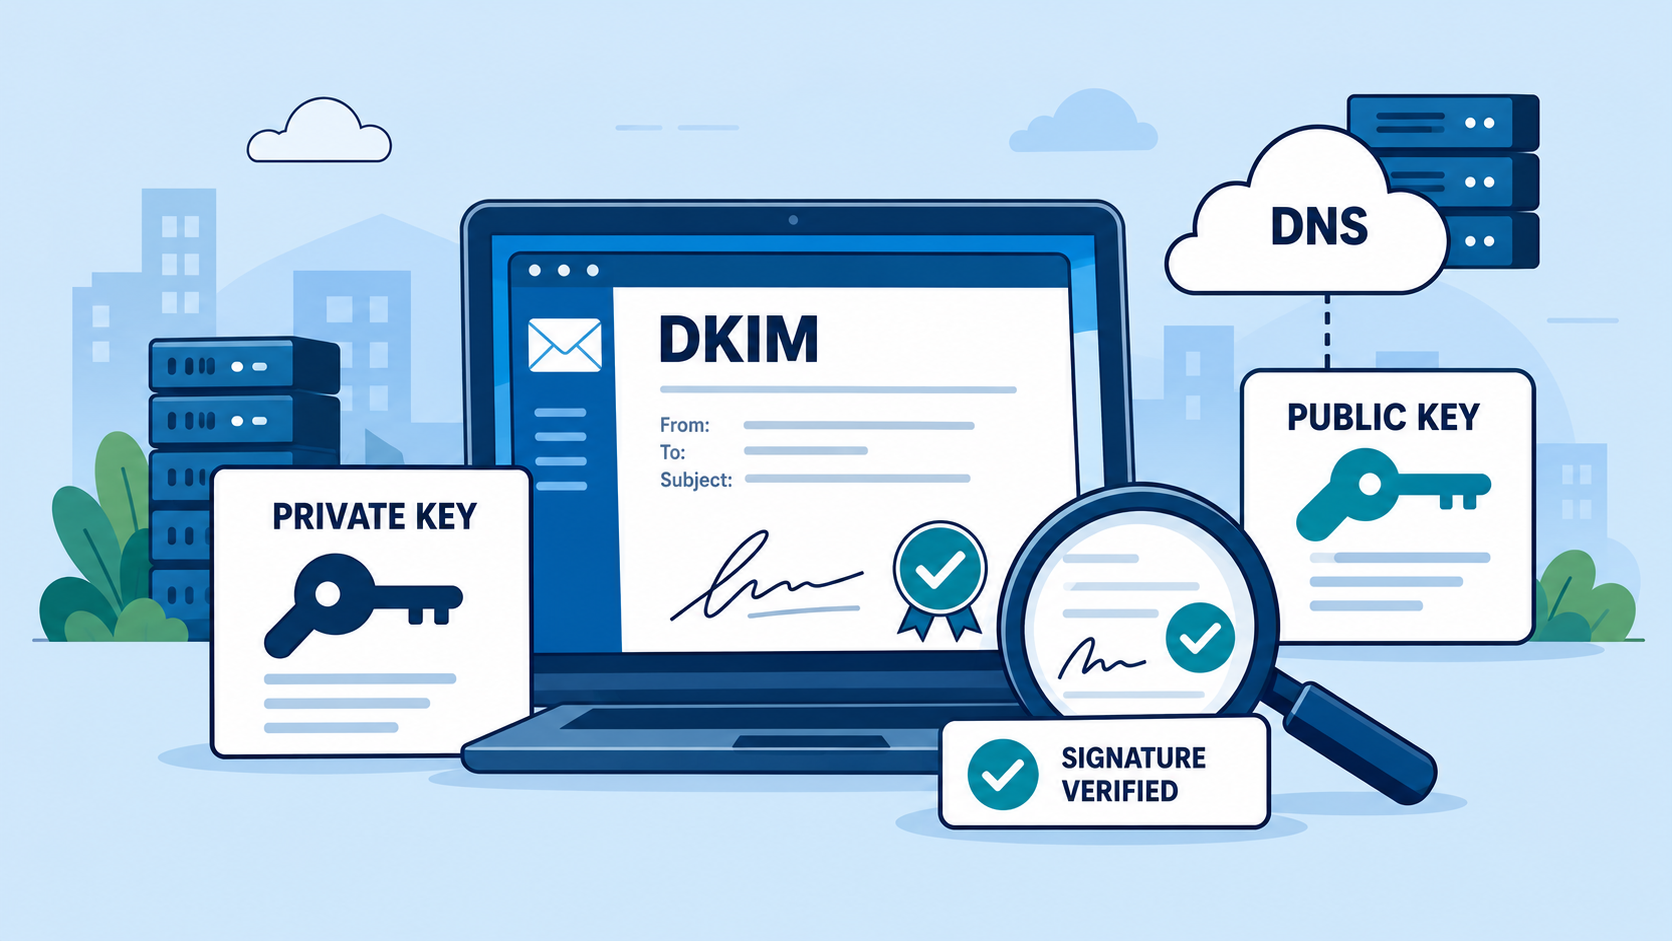
How Does a DKIM Check Work? A Step-by-Step Guide to DKIM Verification

How Does a DKIM Check Work? A Step-by-Step Guide to DKIM Verification

A DKIM check confirms two things about a message: 1) that a system holding the sending domain's private key signed it, and 2) that the signed parts...
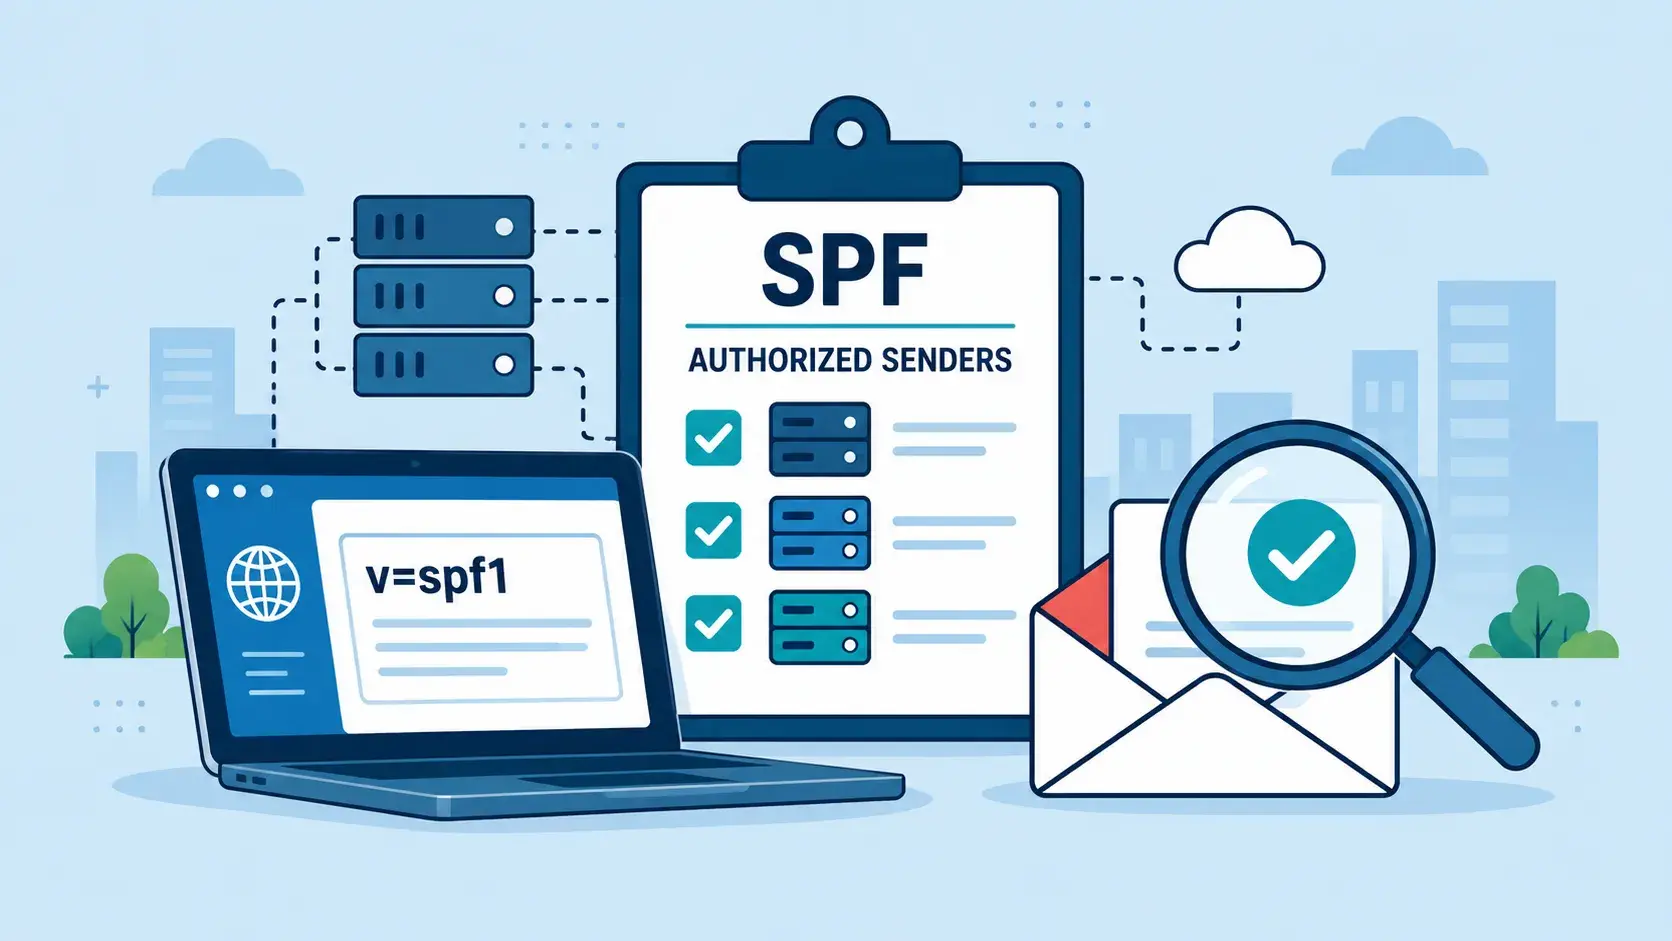
How Does an SPF Check Work?

How Does an SPF Check Work?

When a message arrives, the receiving mail server checks the sending domain's SPF record before it does almost anything else with the message. It...
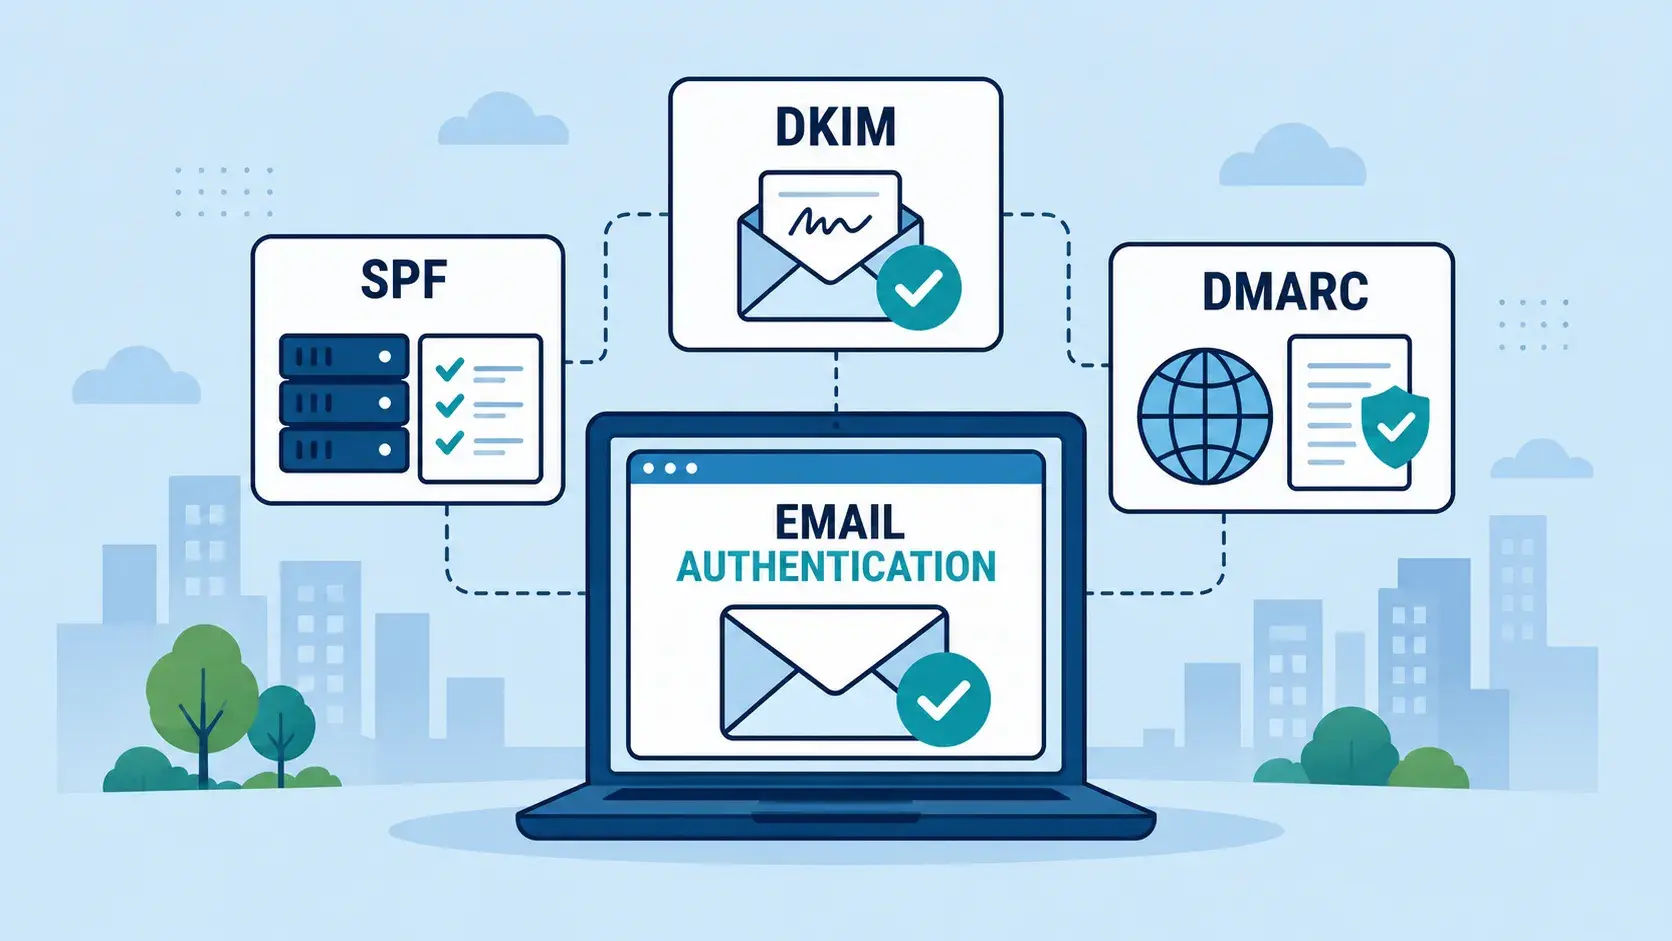
SPF, DKIM and DMARC: How the Three Email Authentication Records Work Together

SPF, DKIM and DMARC: How the Three Email Authentication Records Work Together

SPF, DKIM and DMARC work as a team to stop attackers from sending email that looks like it comes from a domain they do not control. SPF checks...
Stock photo by CDC via Pexels, illustrating security operations center team (temporary placeholder pending custom hero design).

Top 8 vCISO Services for Mid-Market SaaS in 2026

The right vCISO service for a mid-market SaaS company is the one that owns and runs the security program end to end, on a fractional basis, the way a...
Architectural blueprint and floor plan, representing security requirements sourced from a system design

What Does a Security Architect Do?

A security architect does three jobs: sets security requirements for systems other people design, assesses and reviews those designs, and solutions...
Analytics dashboard on a laptop screen, representing a maturity scorecard across applications

How to Run a Security Assessment Across 90 Applications in 90 Days

When an application portfolio is too large to pen-test, an inquiry-based maturity assessment gets you a defensible, board-ready picture in weeks...
Server hardware illuminated in blue, representing identity synchronized across hybrid environments

Hybrid Identity Management: How to Centralize IGA

It's tempting to centralize identity by buying a platform, but I leave the platform for last. Below is my approach to solutioning centralized...
Stock photo by Brett Sayles via Pexels, illustrating data center server room network security (temporary placeholder pending custom hero design).

Security Architecture in Practice: The Questions Teams Actually Ask

Security architecture is the practice of designing how people, process, and technology work together to protect an organization's systems. It is not...
Stock photo by panumas nikhomkhai via Pexels, illustrating data center network servers blue (temporary placeholder pending custom hero design).

What Is Security Architecture? A Practitioner's Guide

Security architecture is the practice of understanding a system component by component and connection by connection. In practice it comes down to two...
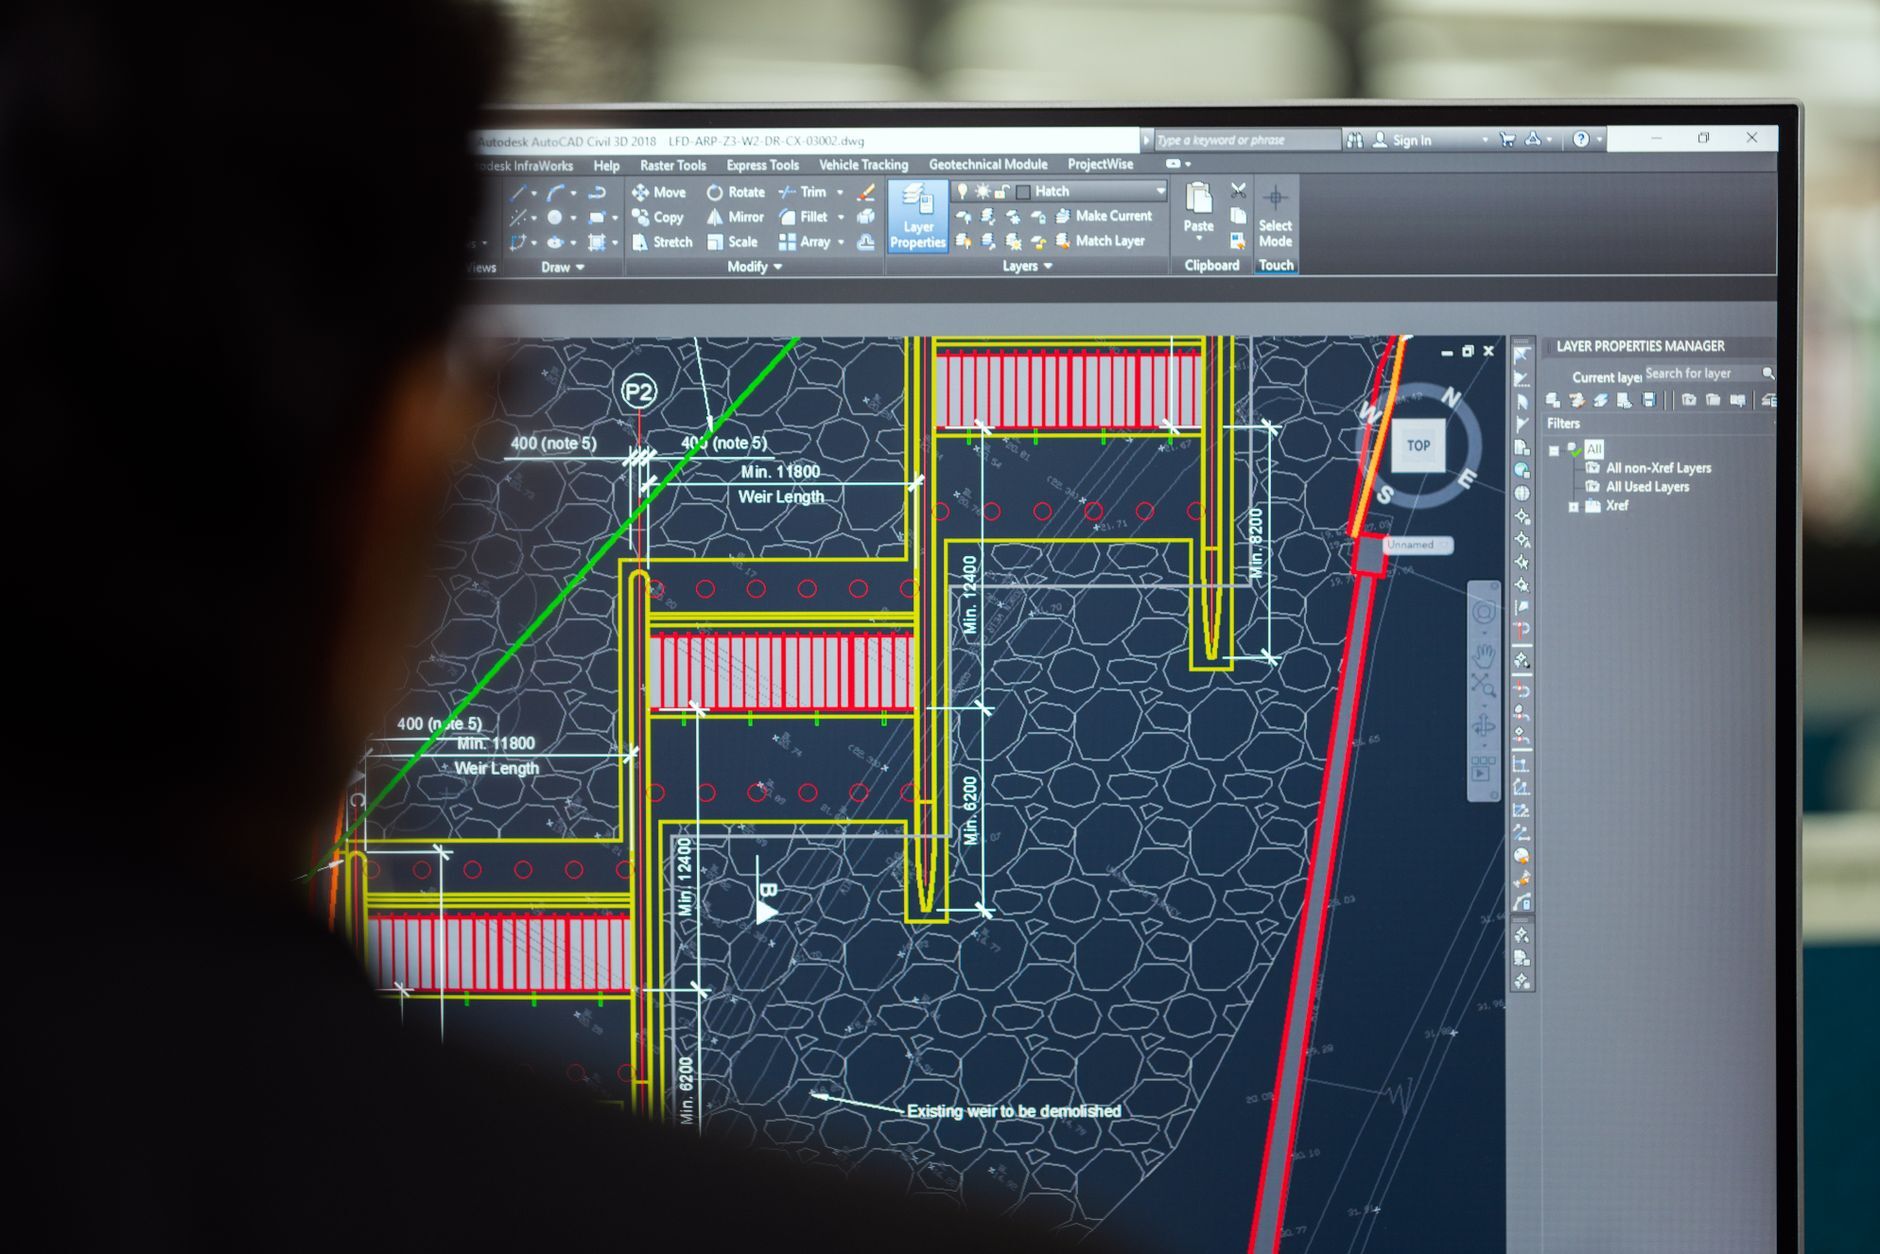
Stock photo by ThisIsEngineering via Pexels, illustrating drawing technical diagram computer screen (temporary placeholder pending custom hero design).

How to Create a Security Architecture Diagram (With a Worked Example)

A security architecture diagram is a boxes-and-arrows drawing of a system: boxes for the key components, arrows for the data flows or network flows...
Stock photo by Vlada Karpovich via Pexels, illustrating security consultant advising executives boardroom (temporary placeholder pending custom hero design).

Who Advises on Security Architecture and Design? The Five Options Compared

Security architecture and engineering consulting comes from five kinds of providers: boutique security consultancies, fractional security teams...
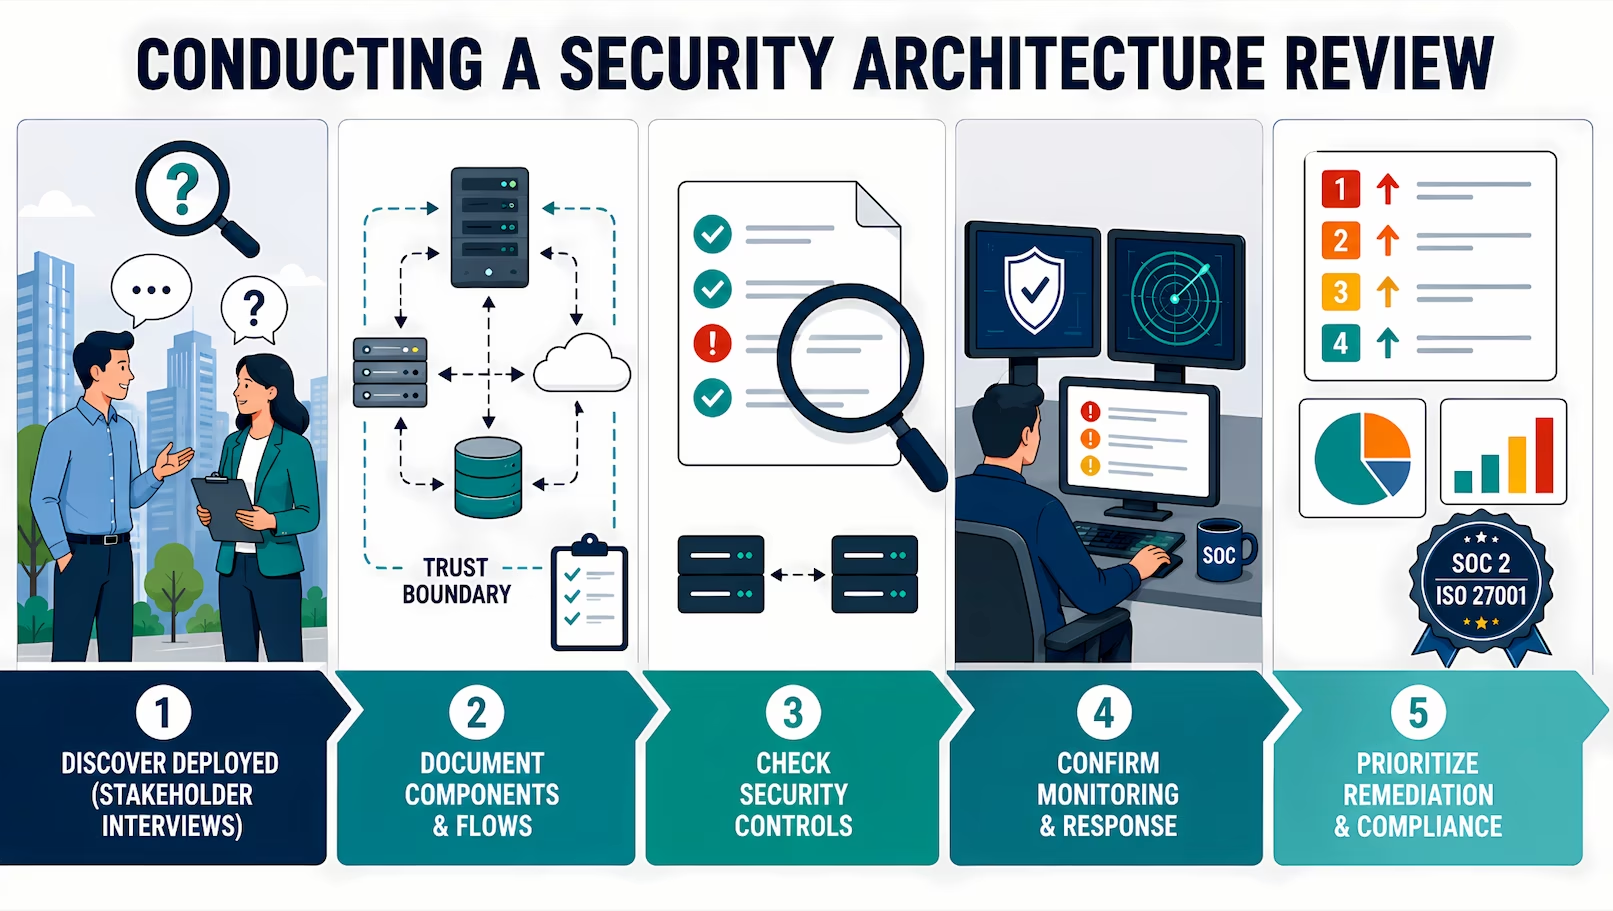
What a security architecture review covers, the five phases from discovery to control mapping, the deliverables to expect, and when to commission one.

The Security Architecture Review Process: Phases, Checklist, and Deliverables

A security architecture review is a structured walk through a system's components and connections, checking each against security best practices and...
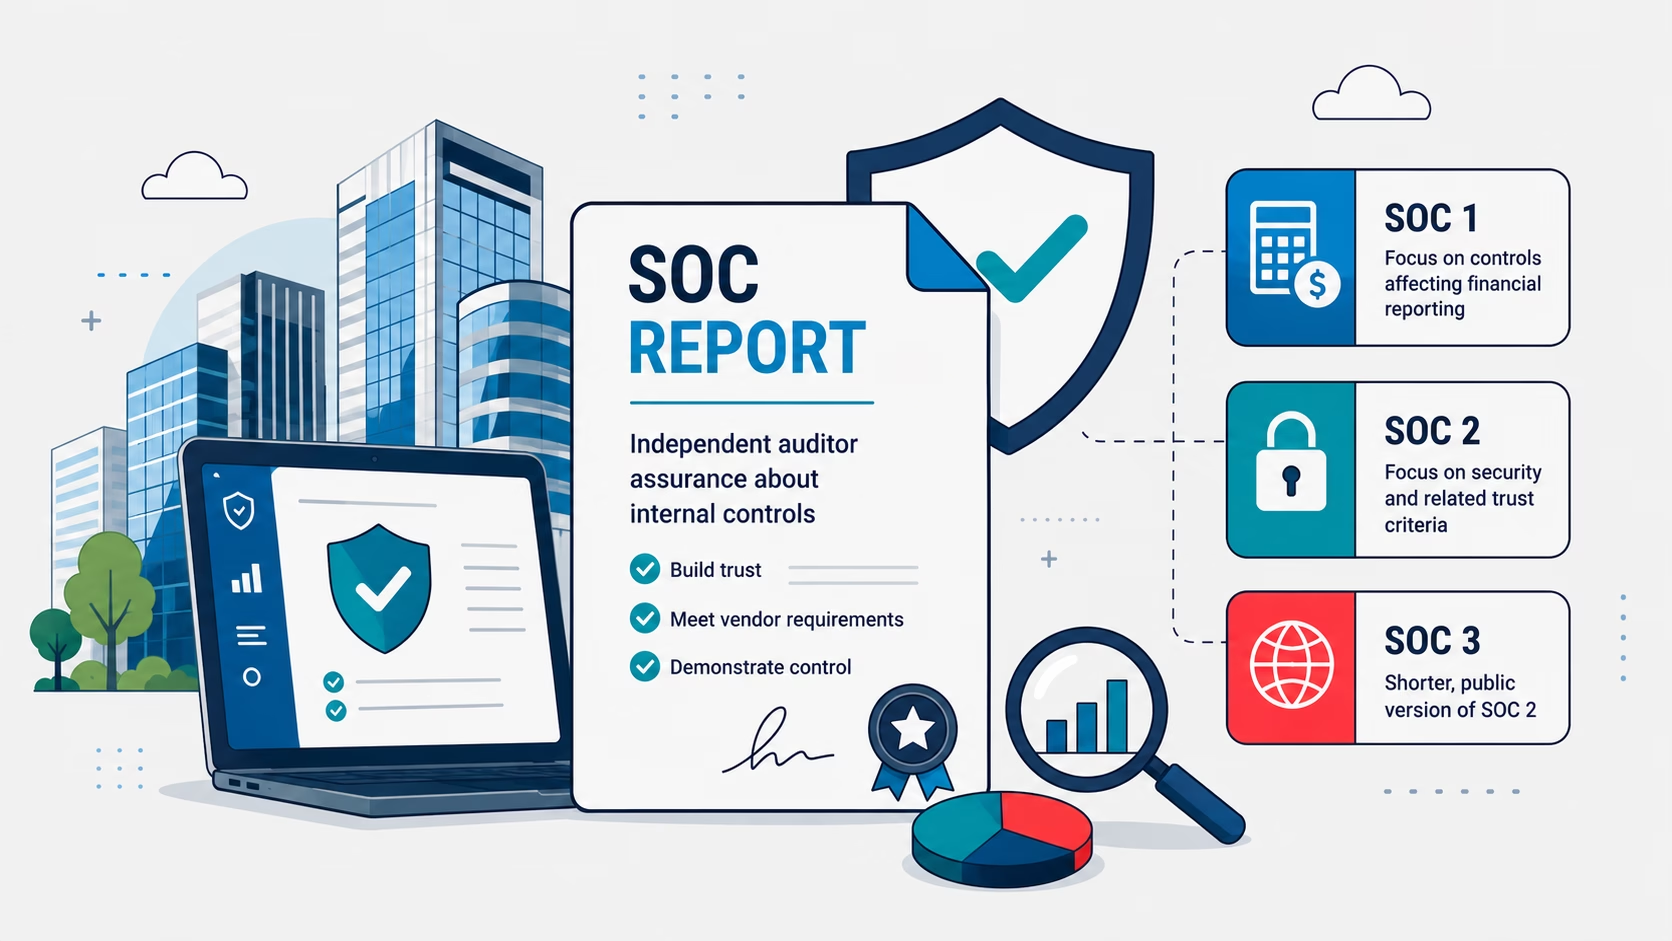
SOC report infographic showing a modern tech city, laptop, security shield, and auditor’s report. It highlights SOC 1 financial controls, SOC 2 security and trust criteria, and SOC 3 as a shorter public version, with a clean flat-vector style.

What Is a SOC Report? SOC 1, SOC 2, and SOC 3 Explained

A SOC report (System and Organization Controls report) is an independent auditor's attestation report on a service organization's controls, issued by...
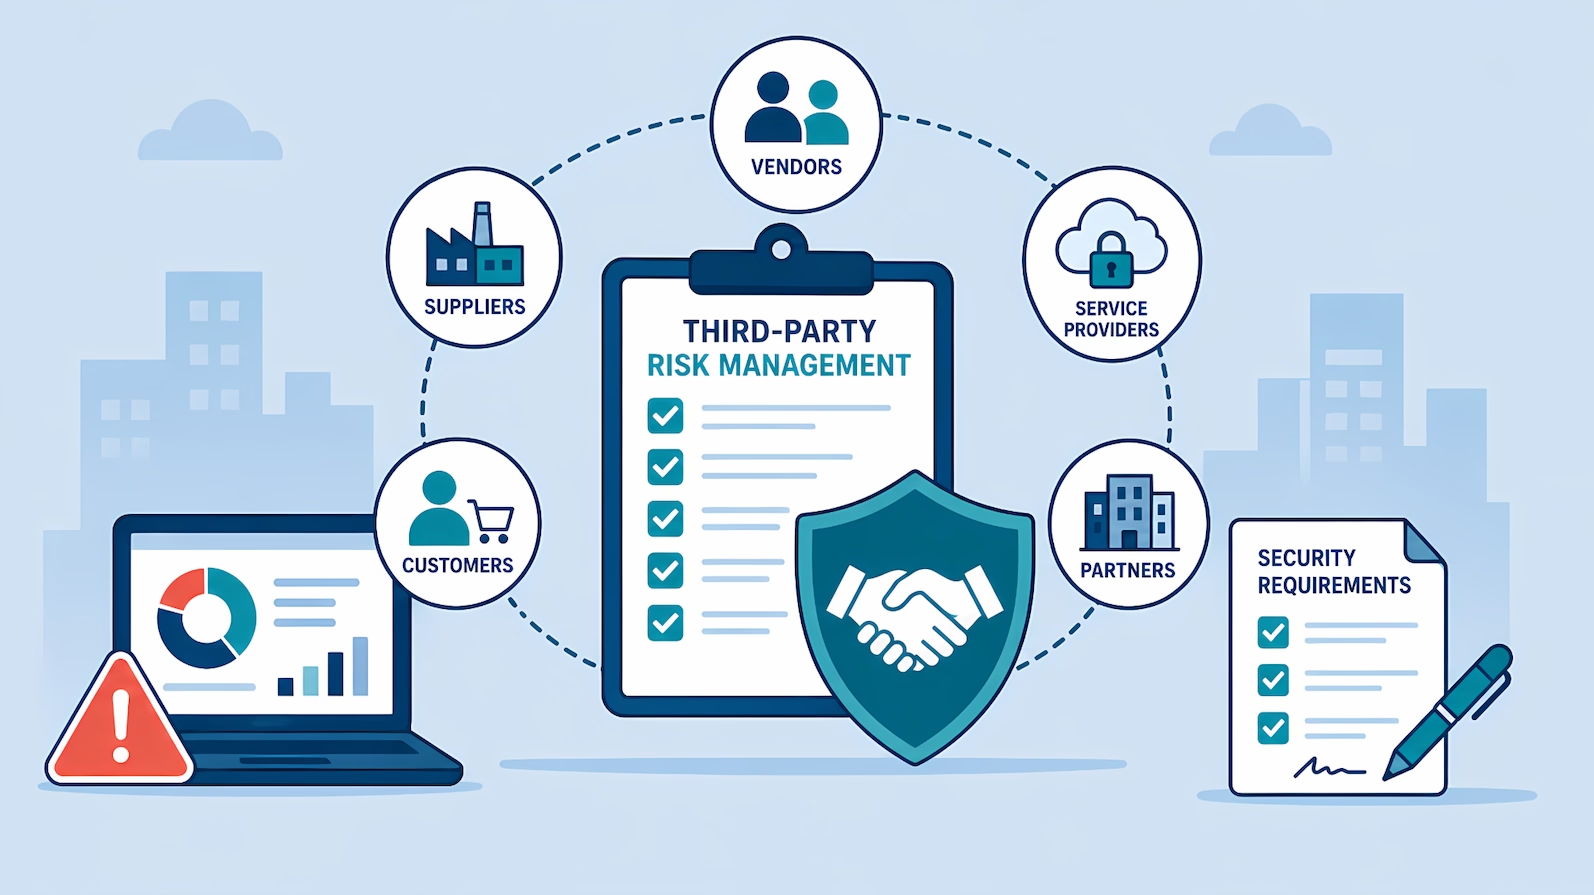
Third-party risk management illustration showing a central security checklist and handshake shield connected to vendors, suppliers, service providers, customers, and partners, with security requirements and risk monitoring represented by supporting icons.

Third Party Risk Management (TPRM): What It Is and How to Build a Program

Third party risk management (TPRM) is the discipline of identifying, assessing, and controlling the risks that come from the external organizations a...
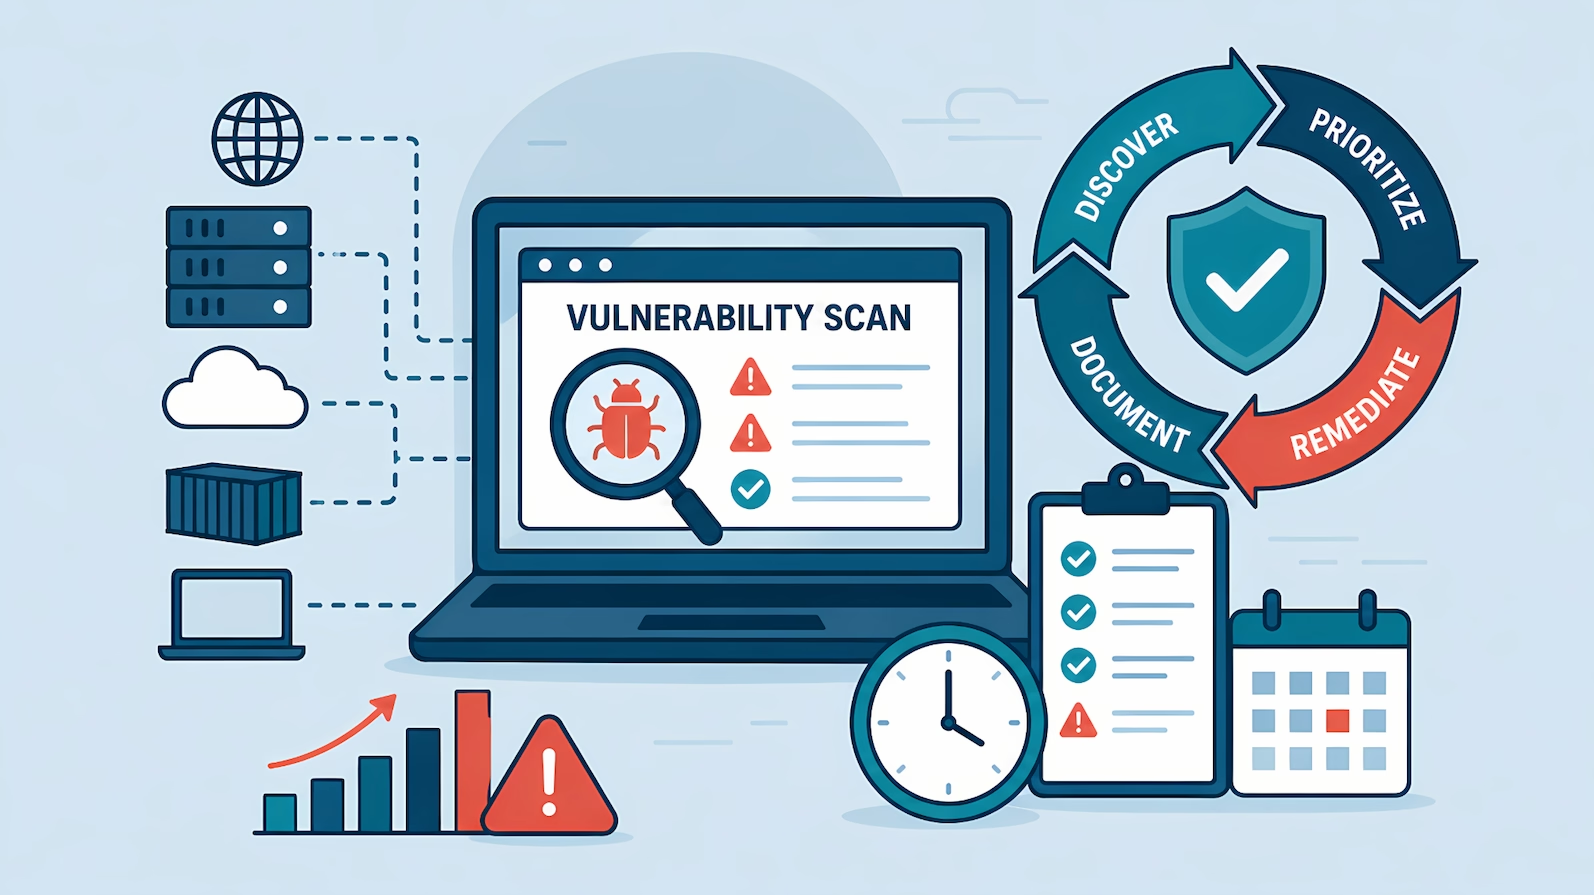
Vulnerability scan on a laptop identifies security weaknesses across servers, cloud, containers, and endpoints, with a cycle showing discovery, prioritization, remediation, and documentation.

What Is a Vulnerability Scan? What It Finds, What It Misses, and How Often to Run One

A vulnerability scan is an automated check that compares systems, software, and configurations against a database of known security weaknesses and...
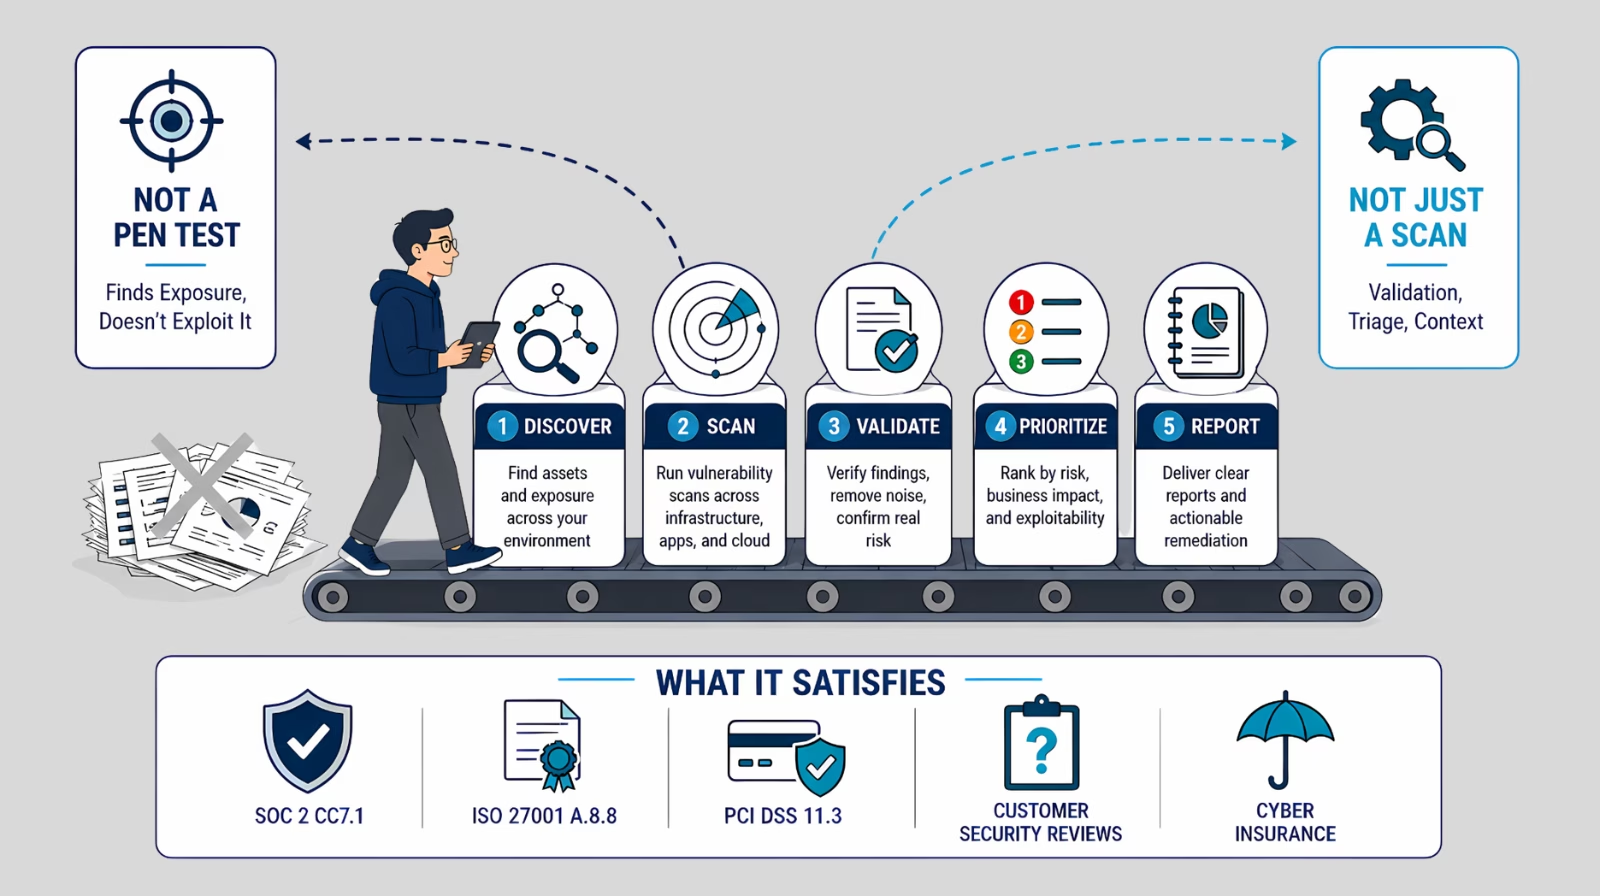
**Alt text (294 characters):** Flat vector infographic showing a five-stage vulnerability management workflow: Discover, Scan, Validate, Prioritize, and Report. An analyst walks beside a conveyor-style pipeline, with callouts explaining “Not a Pen Test” and “Not Just a Scan,” plus compliance outcomes including SOC 2, ISO 27001, PCI DSS, customer security reviews, and cyber insurance.

Vulnerability Assessment Services: What They Include, What They Cost, and How to Choose a Provider

Vulnerability assessment services are engagements where a third party inventories an environment, scans it for known security weaknesses, validates...
Stock photo by Kampus Production via Pexels, illustrating two business people signing contract agreement office (temporary placeholder pending custom hero design).

Trust as a Competitive Advantage: The Moat AI Can't Clone

When any competent team can clone a B2B SaaS product in a weekend, trust as a competitive advantage is the moat that remains: the certifications,...
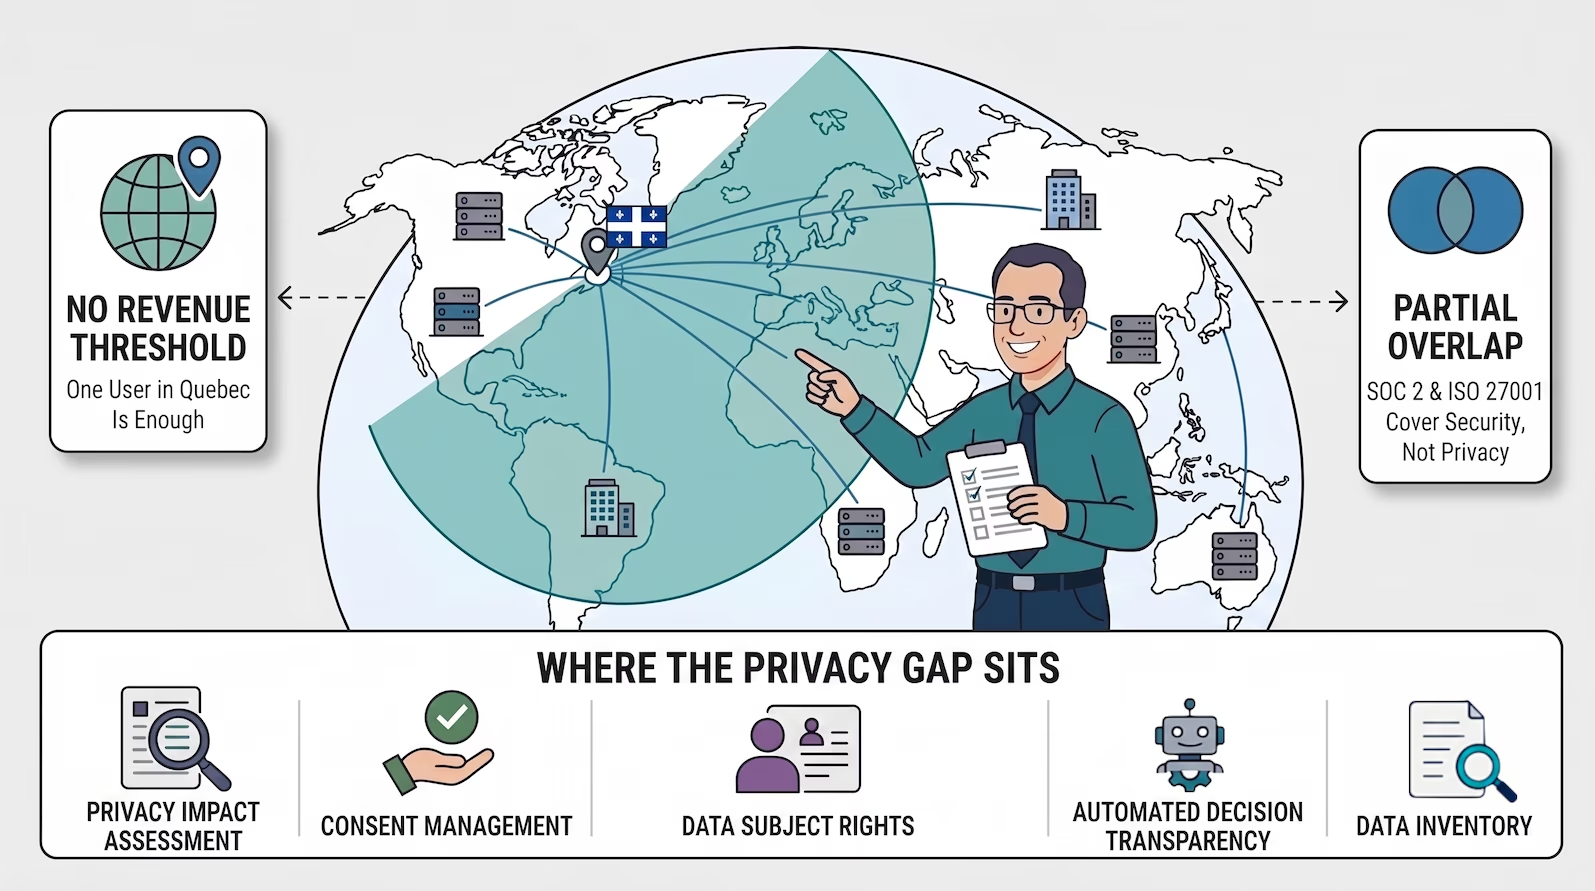
Vector infographic: A man with glasses points to Quebec on a globe, where a teal radius connects to global servers. Side panels read "No Revenue Threshold" and "Partial Overlap." A bottom banner titled "Where the Privacy Gap Sits" displays five privacy compliance icons.

Quebec Law 25 Compliance: The Privacy Law Every SaaS Company Should Know About (But Probably Doesn't)

Quebec Law 25 is the province's modernized private-sector privacy law: a set of amendments (adopted in 2021 as Bill 64) to the Act respecting the...
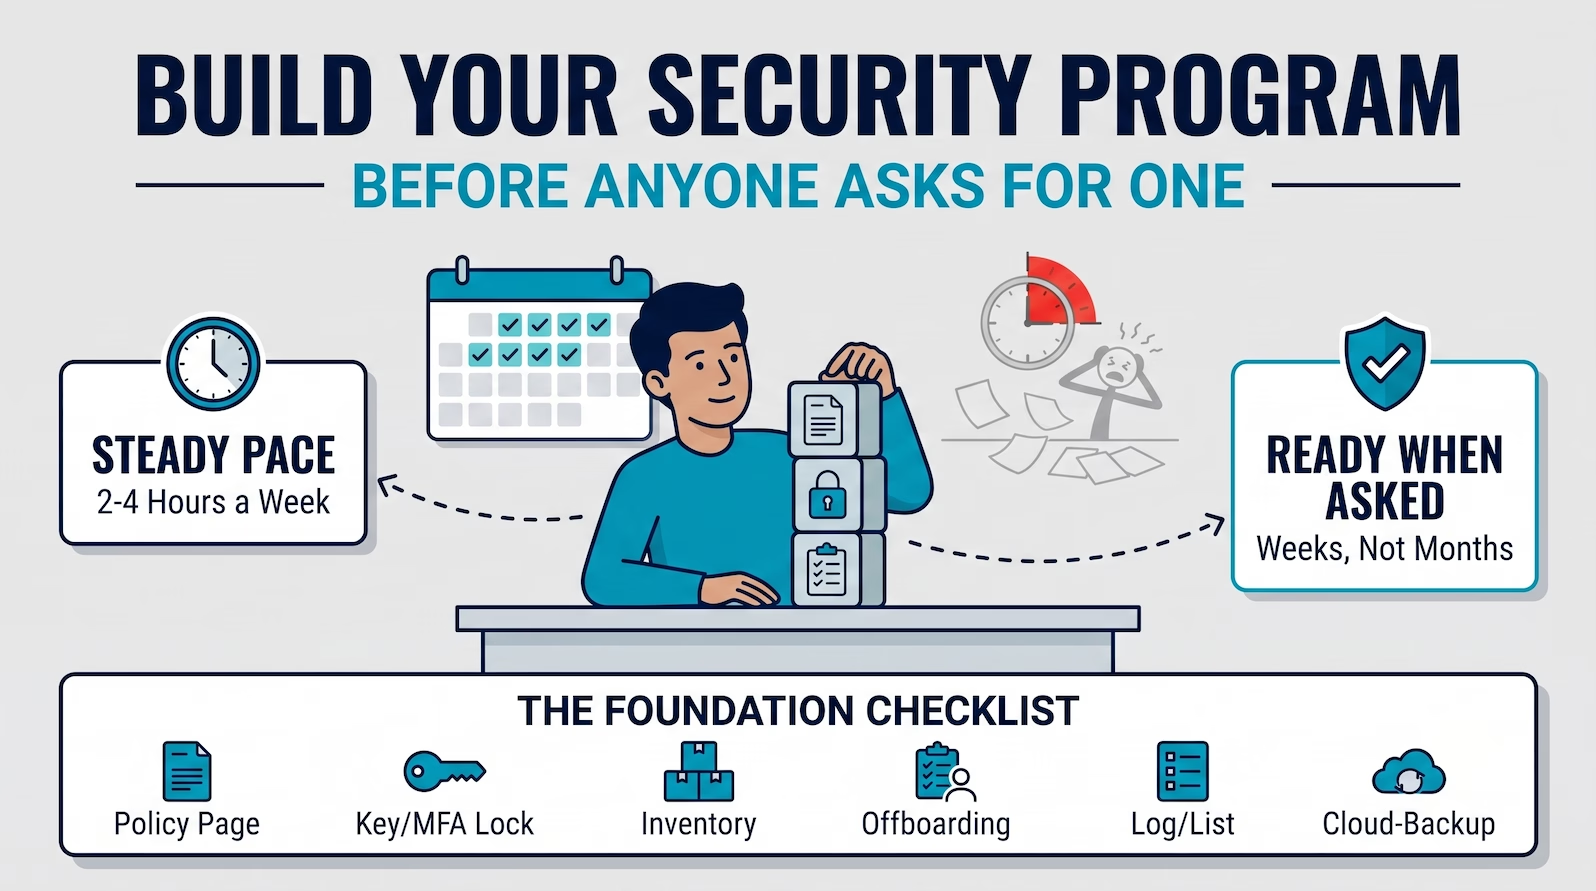
Infographic titled "BUILD YOUR SECURITY PROGRAM BEFORE ANYONE ASKS FOR ONE." It contrasts a calm man working at a "STEADY PACE" (2-4 Hours a Week) against a panicked scenario, resulting in being "READY WHEN ASKED." The bottom features a 6-item "FOUNDATION CHECKLIST."

Build a Security Program Before Anyone Asks For One

Almost every first call I get starts the same way. Someone outside the company is suddenly asking for a security artifact. A prospect sent a...
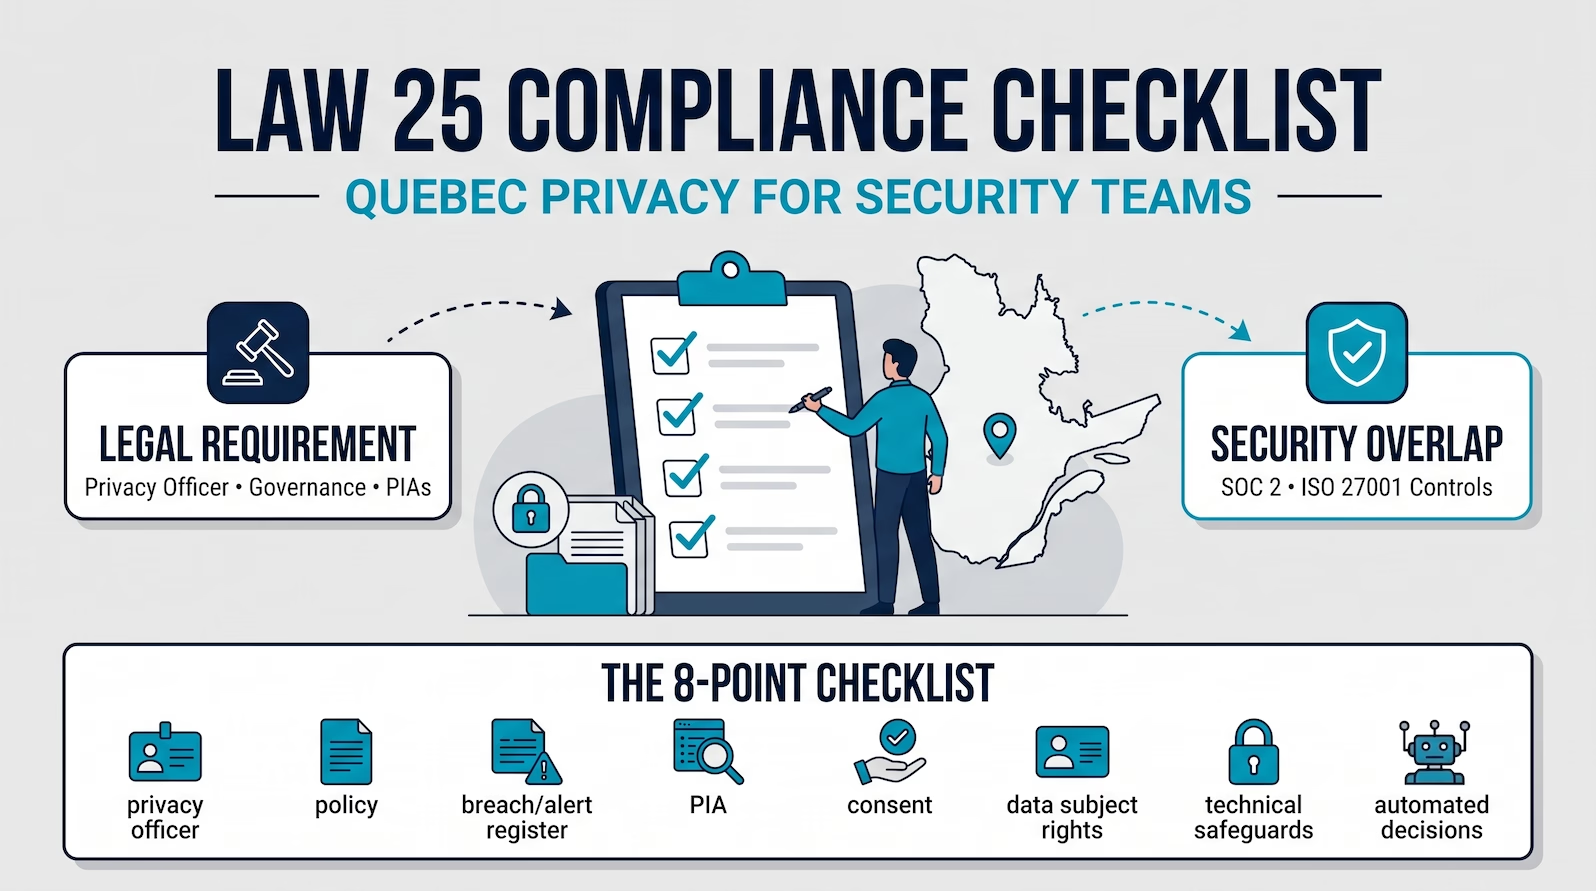
An infographic titled 'LAW 25 COMPLIANCE CHECKLIST' for Quebec security teams. It links 'LEGAL REQUIREMENT' and 'SECURITY OVERLAP' (SOC 2, ISO 27001) as a man checks a large clipboard list. The bottom outlines 'THE 8-POINT CHECKLIST' with 8 key icons, such as privacy officer, PIA, and safeguards.

Law 25 Compliance Checklist: What Security Teams Actually Need to Do

Quebec's Law 25 has been fully in force since September 2024, and the penalties are no longer theoretical. Under the Act respecting the protection of...
ISO 42001 Cost in 2026: The 4 Factors

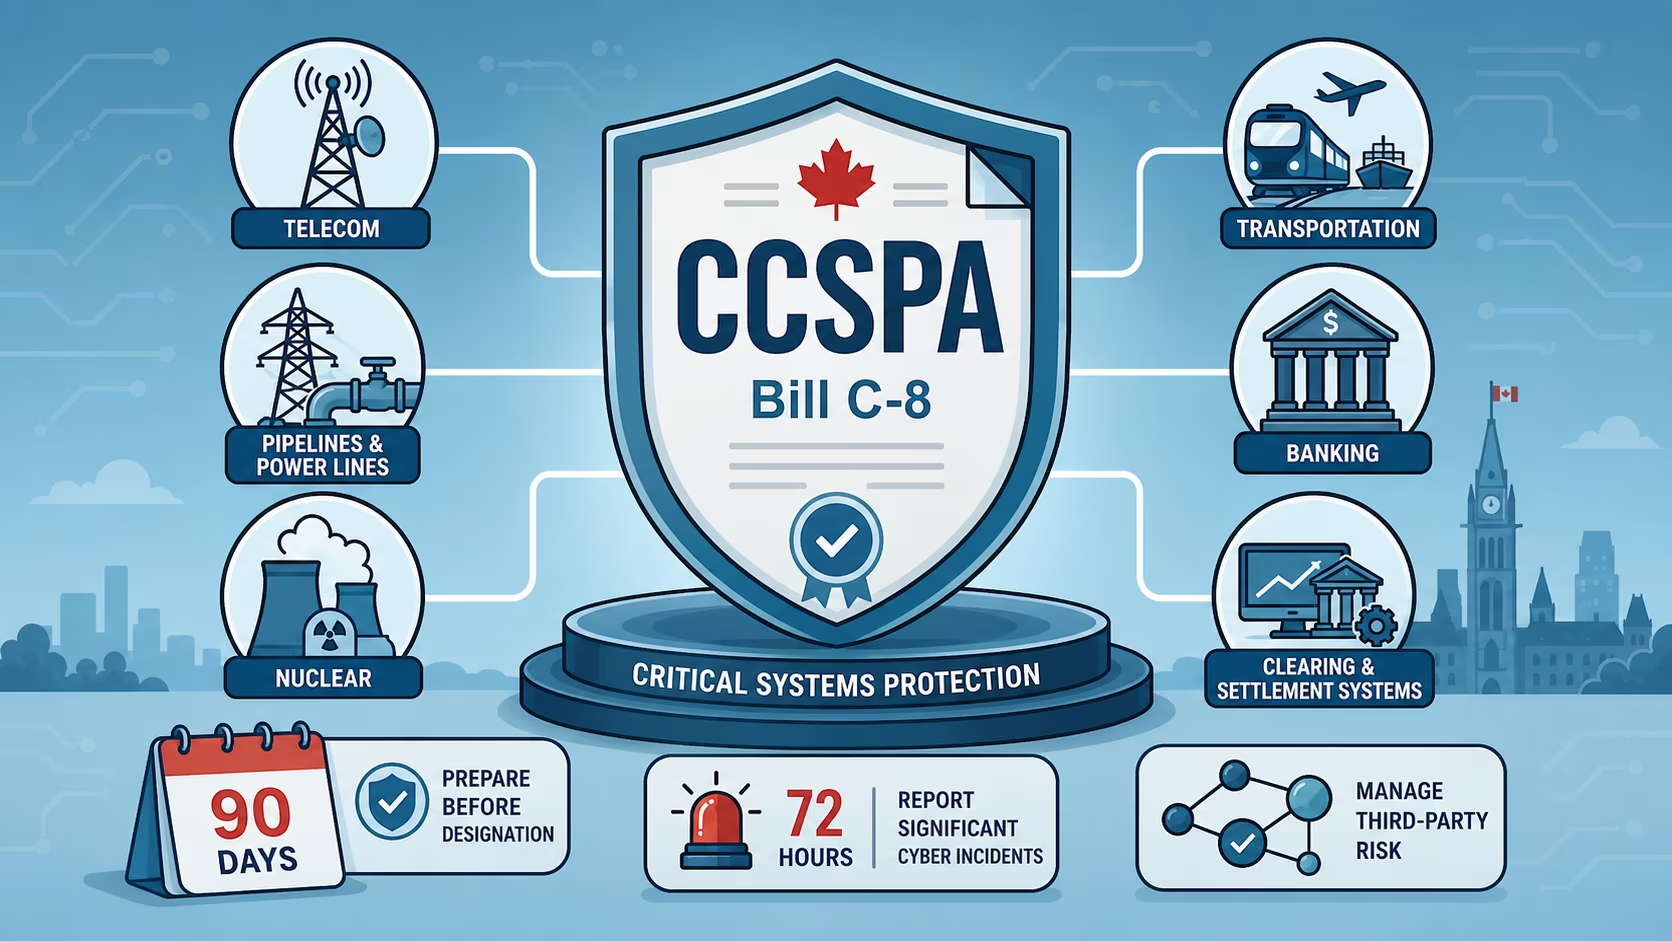
Bill C-8 Is Law: What Canada's Critical Cyber Systems Protection Act Requires, and Who It Reaches

Bill C-8 is law. The Act received Royal Assent on June 15, 2026 (S.C. 2026, c. 9). The centrepiece, the Critical Cyber Systems Protection Act...
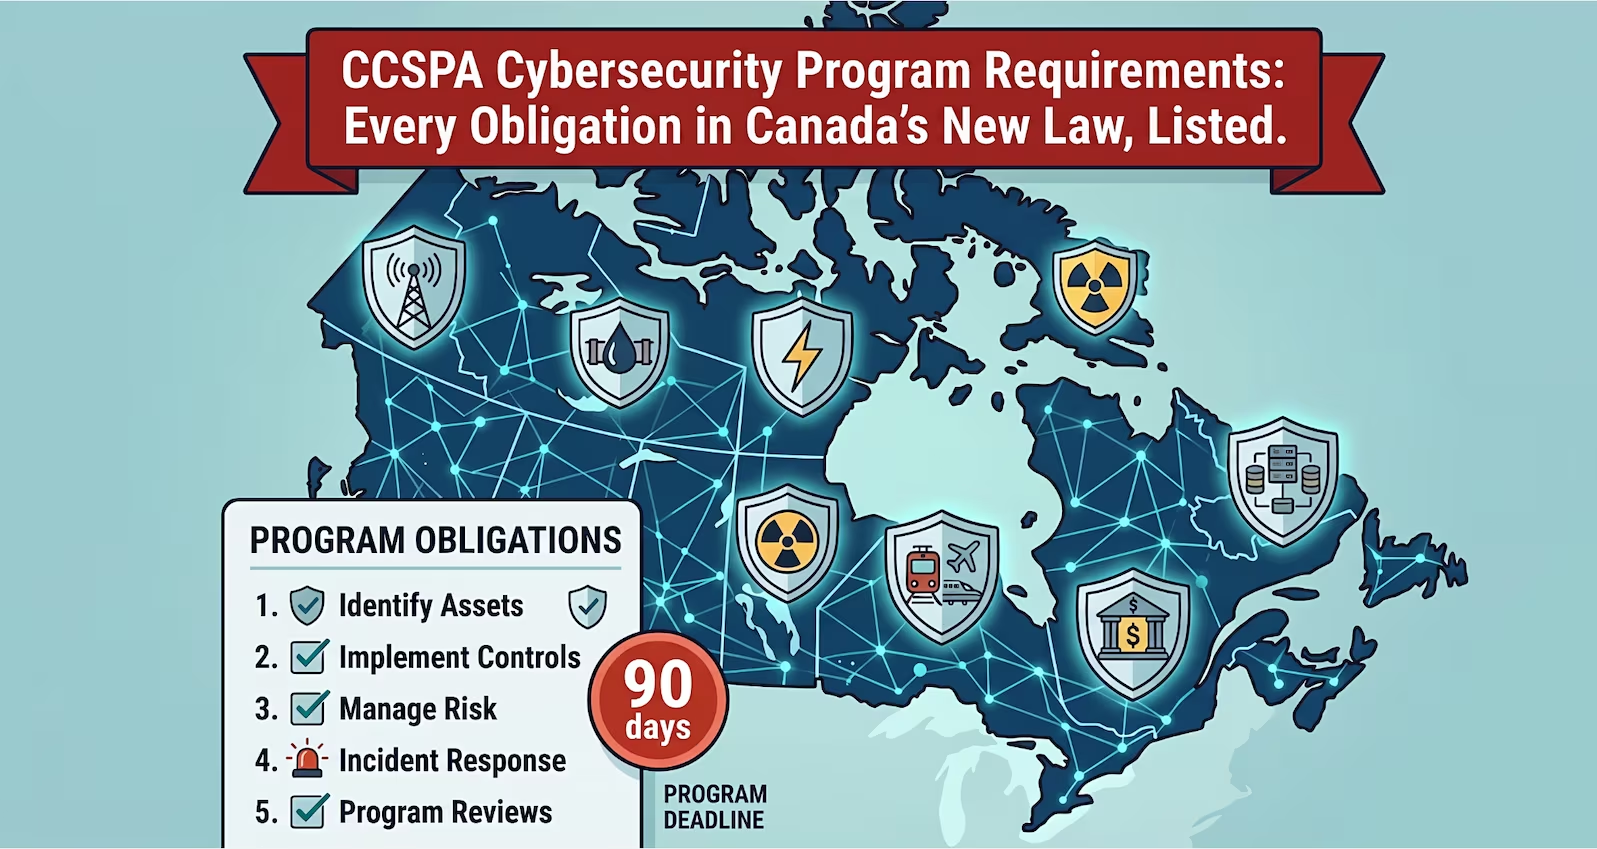
Infographic titled “CCSPA Cybersecurity Program Requirements.” A map of Canada shows networked shields over critical sectors. Features a 5-step checklist of obligations (Identify Assets to Program Reviews) and a red “90 days” program deadline badge.

CCSPA Cybersecurity Program Requirements: Every Obligation in Canada's New Law, Listed

A CCSPA cyber security program is a documented set of reasonable steps to identify and manage cyber security risk, protect critical cyber systems,...
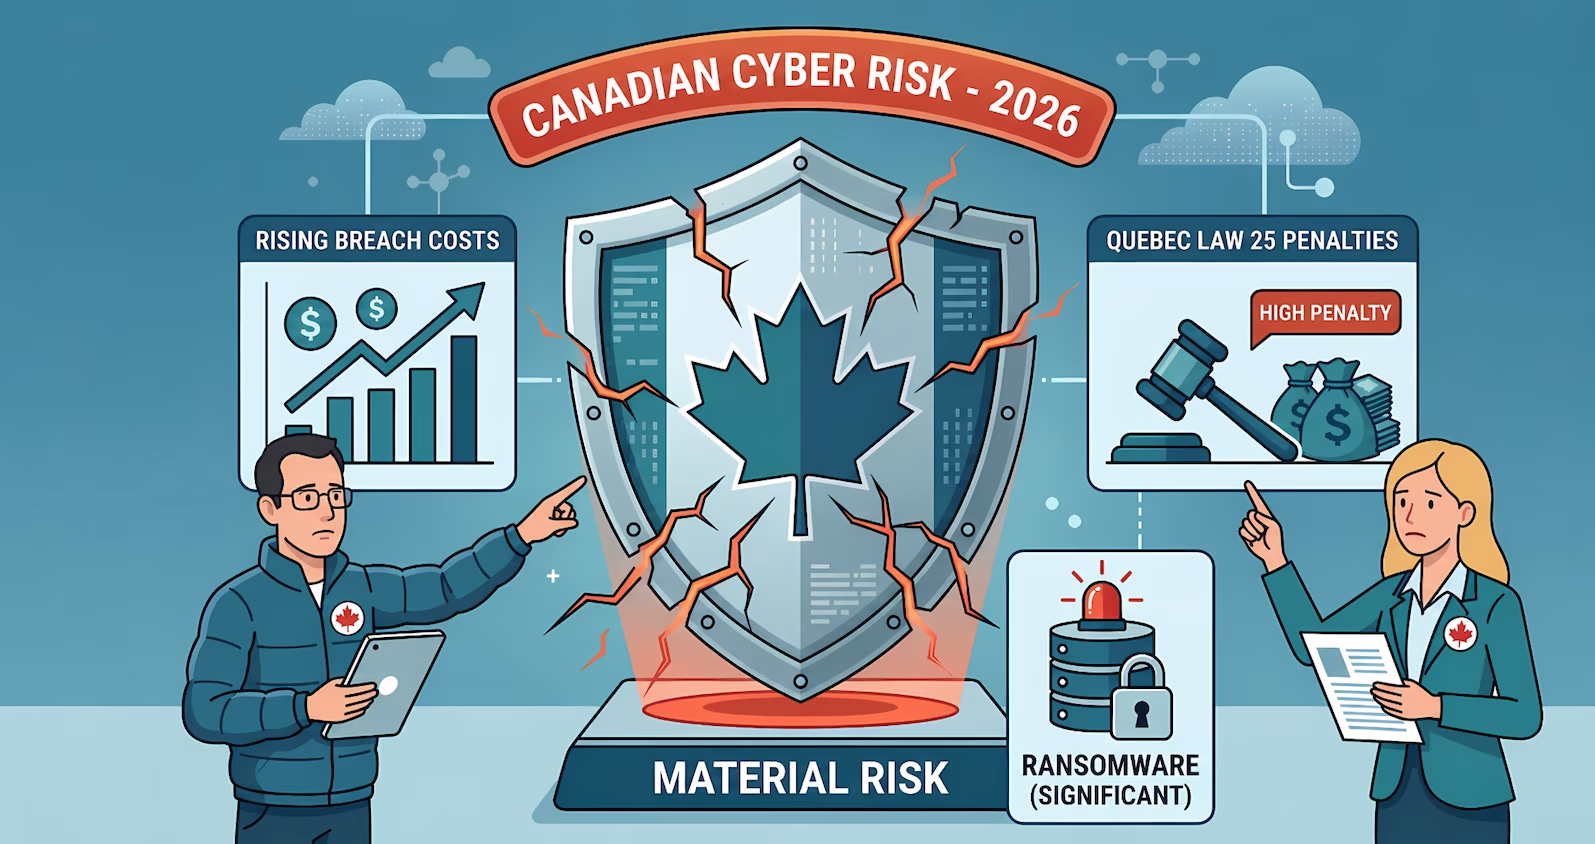
Infographic "Canadian Cyber Risk - 2026" with a central fractured maple leaf shield representing "Material Risk". Surrounding data panels cover "Rising Breach Costs", "Quebec Law 25 Penalties", and "Ransomware (Significant)". Analysts point to key threats.

Canadian Cybersecurity & Compliance Statistics 2026

The bottom line for 2026: Canadian data breach costs rose 10.4% to CA$6.98 million even as the global average fell. Canada is the outlier, and the...
What Vanta and Drata Can't Automate

What Vanta and Drata Can't Automate

Companies that implement Vanta or Drata expecting near-complete automation of their SOC 2 compliance work tend to hit the same wall. The integrations...
