
Build & Respond

Breach response services

Customer or employee data may have left your systems. We contain the breach, establish which records were accessed and for whom, and give your counsel the facts behind every notification decision under PIPEDA, Quebec Law 25 and your customer contracts.

In an active breach? Call (877) 250-4443.

Ali Aleali

Ali Aleali, CISSP, CCSP

Co-Founder & Principal Consultant

Former security architect for Bank of Canada and Payments Canada. CISSP, CCSP, more than twenty years in enterprise security. Leads every engagement.

Connect on LinkedIn

What Truvo's breach response services cover

From the first containment call to the breach record you keep afterwards, built on a SANS-based incident response methodology.

icon-2

Contain the breach

Read-only access to cloud log sources and application security logs, malicious sources blocked, exploited endpoints disabled. A dedicated Slack channel and status calls every few hours from the first hour.

icon-5

Scope the affected data

Forensic analysis of which systems, records and people were affected, and over what period. The risk assessments under PIPEDA and Law 25 depend on these facts: how sensitive the information is and how likely it is to be misused.

icon-6

Notification evidence for your counsel

The facts, timeline and evidence package your counsel uses to file the report to the Office of the Privacy Commissioner of Canada under PIPEDA, the notice to Quebec's Commission d'accès à l'information under P-39.1 and the notices to affected individuals, organized around what each regulator asks for. Your counsel drafts, decides and files.

icon-4

Customer and platform communications

Status updates and a forensic report written for the enterprise customers, platform review teams and insurers who will ask how the breach happened and how it was closed.

icon-7

Vulnerability assessment and penetration test

Across the attack surface, alongside recovery, so the report can show that the way in is closed and that adjacent weaknesses were checked.

icon-3

Breach record and remediation roadmap

A breach record your team can keep for the 24 months PIPEDA requires and add to the Law 25 confidentiality incident register, plus a remediation roadmap mapped to root cause.

Related incident response services

Breach response is one engagement within Truvo's incident response practice.

icon-8

Incident response services and retainer

Pre-agreed terms and a named team that has already mapped your environment and log sources, so the first call of a breach is a status call.

icon-4

Incident response for Shopify apps

Containment, VAPT and a forensic report structured for Shopify's app-reinstatement review, from a team that works inside the Shopify app architecture.

icon-1

Privacy program after the breach

Ongoing ownership of PIPEDA and Law 25 obligations, including the confidentiality incident register and the next privacy review.

Assess, Build, Operate, applied to a data breach

Three goals in sequence, each ending with evidence your counsel, customers and regulators can use. Led by a senior architect with more than twenty years in enterprise security and a CISSP.

01

Assess

Containment, log access and a first scope of affected systems and data. Dedicated channel open from the first hour, and an early facts summary for your counsel.

02

Build

Malicious code and unauthorized access removed, penetration test across the attack surface, fixes verified, and affected records confirmed for the notification decision.

03

Operate

Forensic report, notification support, customer and platform briefings, breach record and remediation roadmap. Status calls continue until the breach is closed.

What you hold at the end of a breach response

Documents written for the people deciding whether to keep trusting you, with the evidence behind every line.

  • Forensic incident report with kill chain and indicators of compromise

  • Scope of affected records and individuals

  • Facts, timeline and evidence package for counsel's regulator filings

  • Customer and platform briefing

  • Penetration test report and closure evidence

  • Breach record and remediation roadmap

Why Truvo's breach response holds up under review

Field-tested on national payment infrastructure and on live platform incidents.

When breach response services are the right engagement

If you are in an active breach, call (877) 250-4443 or use the contact form and mark it urgent. A responder replies directly.

Breach response services: frequently asked questions

Containment, forensic analysis of which records and people were affected, a vulnerability assessment and penetration test during recovery, the facts, timeline and evidence package your counsel uses for regulator and individual notifications, customer and platform communications, a breach record and a remediation roadmap. Truvo delivers these as one engagement with one team.

Breach response is incident response for an incident where personal or customer data may have been accessed. It adds the work that follows from that: scoping affected records, supporting the notification decisions, and communicating with customers and regulators. Truvo's incident response services page covers the full practice, including retainers.

Under section 10.1 of PIPEDA, an organization must report a breach of security safeguards to the Privacy Commissioner of Canada, and notify affected individuals, if it is reasonable to believe the breach creates a real risk of significant harm. Both must happen as soon as feasible after the organization determines the breach occurred. The Breach of Security Safeguards Regulations also require a record of every breach for 24 months, whether or not it was reportable. Your counsel makes the call, and Truvo provides the facts it depends on.

Section 3.5 of Quebec's Act respecting the protection of personal information in the private sector, as amended by Law 25, requires reasonable measures to reduce the risk of injury and to prevent new incidents of the same nature. If the incident presents a risk of serious injury, the enterprise must promptly notify the Commission d'accès à l'information and the people whose information is concerned. Section 3.8 requires a register of confidentiality incidents.

You and your counsel. Truvo works beside your legal team and, where an insurer is involved, within the terms the insurer sets. We supply the scope of affected records, the timeline and the steps taken, which are the facts the risk assessment and the notices are built on.

We scope affected records by jurisdiction, for example by US state of residence, so your counsel can apply the notification rules that cover each group. The forensic report and the scope work are the same regardless of where the affected customers live.

Emergency response is available around the clock. The first working step is read-only access to your cloud log sources and application security logs, and a dedicated Slack channel opens the same day. Retainer clients skip onboarding, because the team has already mapped the environment.

Talk to the architect who would do the work

A 30-minute call. We look at your environment and tell you plainly whether we can help and what it would take.

From the blog: incident and breach response

ISO 27001 A.5.24: Information Security Incident Management Planning and Preparation

ISO 27001 A.5.24 requires an organization to plan and prepare for security incidents before they happen: define the roles, the response process, the ...
SOC 2 CC7.4: Responding to Security Incidents

SOC 2 CC7.4 requires a company to respond to security incidents through a defined incident-response program that understands, contains, remediates, ...
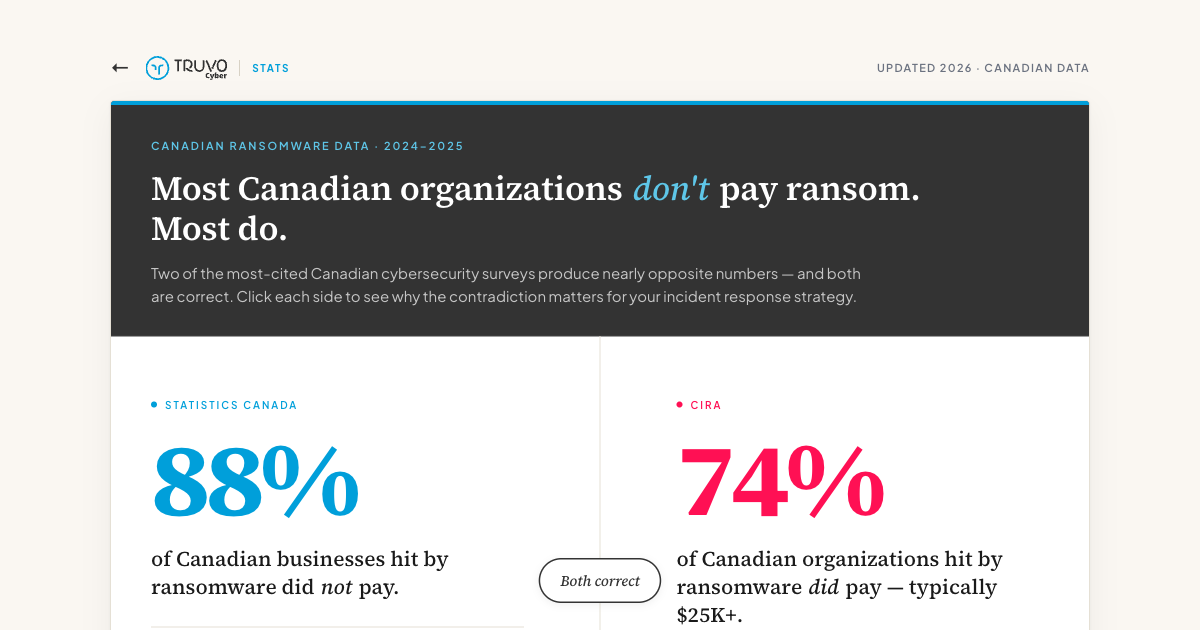
The Canadian Ransomware Paradox: Why Two Surveys Disagree on Payment

Two of the most-cited Canadian ransomware statistics flatly contradict each other.