Privacy Certification

ISO 27701 Certification Consulting

Truvo builds the privacy information management system (PIMS) that ISO/IEC 27701:2025 certification requires, as an extension of your ISO 27001 ISMS or as a standalone program. A senior lead guides your team from scoping through the certification body's Stage 2 audit.

  • A PIMS scoped to your role as PII controller, PII processor or both
  • Built on your existing ISO 27001 ISMS, or from zero
  • Led by a senior CISSP in the US or Canada

For most SMBs, ISO 27701 consulting costs USD $2,500 to $5,000 a month to build and operate the PIMS.

Talk to an ISO 27701 consultant

Share your scope and target certification date, and a consultant will follow up to book a call.

What does ISO 27701 certification involve?

Truvo follows the Assess, Build, Operate model, mapped to the clauses of ISO/IEC 27701:2025.

What do you get from an ISO 27701 engagement?

Four things you hold at the end, ready for the certification auditor.

When is Truvo the right call?

For many companies, the trigger is a customer contract, RFP or security review that asks for ISO 27701 certification.

What do clients say about Truvo's ISO work?

"Truvo Cyber conducted our ISO 27001 and ISO 27701 internal audit. They were easy to work with, communicated clearly throughout the project, and delivered a thorough, professional report on time. I would recommend them to any organization working through similar compliance requirements."

Ellipse (1) (1)
Aimee Halbert

UserTesting

"Truvo is an instrumental and integrated part of our team...
They don’t just provide recommendations; they ensure we meet our stringent ISO 27001 and SWIFT compliance goals. We trust them with projects of national importance, and they deliver."

Mask Group-1
Matt Charette

CISO, Payments Canada

Ready to plan your ISO 27701 certification?

Book a strategy call. We review your scope and your role as controller or processor, and give you a clear picture of the timeline and investment.

Book Your Free ISO Strategy Session

What do companies ask about ISO 27701 certification?

For most SMBs, ISO 27701 consulting costs USD $2,500 to $5,000 a month to build and operate the PIMS. The monthly fee depends on the PIMS scope, whether you act as a PII controller, a PII processor or both, and whether an ISO 27001 ISMS is already in place. The certification body bills the audit fee separately.

The timeline depends on scope. Adding ISO 27701 to an operating ISO 27001 ISMS is typically faster than building both from zero, because the two standards share the same Clause 4 to 10 structure and much of the evidence. We give you a dated plan after the scoping call.

ISO 27701 is a management system standard. GDPR, PIPEDA and Law 25 are laws. Certification shows an independent auditor checked how you manage personal data, and the same PIMS records support your obligations under each law. A certificate shows conformity with ISO 27701, and compliance with each law remains a separate legal question. For a program built around specific privacy laws, see our privacy program consulting page.

ISO/IEC 27701:2025, published in October 2025, is a standalone management system standard, so an organization can certify a PIMS without holding ISO 27001. The 2019 edition was an extension of ISO 27001 and required an ISMS. Companies that hold ISO 27001 can add ISO 27701 to the same management system and reuse the risk assessment, internal audit and management review.

A PII controller decides why and how personal data is processed. A PII processor handles personal data on behalf of a controller and follows the controller's instructions. ISO/IEC 27701:2025 Annex A lists controls for controllers in Table A.1, controls for processors in Table A.2, and security controls for both in Table A.3. A SaaS company is often a controller for employee data and a processor for the data customers upload.

Yes. Many certification bodies offer a combined audit when both standards share one management system. Truvo can build both standards into one management system, with one evidence set.

Clause 9.2 of ISO/IEC 27701:2025 requires internal audits, with auditors selected so the audit stays objective and impartial. Certification bodies typically expect a completed internal audit and management review before the Stage 2 audit. Truvo offers the ISO 27701 internal audit as a separate service, delivered by an auditor who did not build your PIMS.

An accredited certification body issues the certificate after the Stage 1 and Stage 2 audits. ISO/IEC 27706:2025 sets the requirements for bodies that audit and certify a PIMS, and replaced ISO/IEC TS 27006-2:2021. Truvo prepares you for the audit and supports you through both stages. The certification body is independent of Truvo.

Client data, documentation and sensitive materials are stored in secure North American cloud environments. Every engagement is led by a senior CISSP in the US or Canada with 10+ years in security, and every consultant on the engagement is an experienced, vetted professional.

How is Truvo different?

Our consultants build and operate management systems, so the PIMS fits how your team handles personal data day to day.

Ready to certify your privacy program?

ISO 27701 consulting led by practitioners who build and operate management systems.

From the blog: privacy and data protection

PIPEDA Compliance for SaaS: 10 Principles as Controls

PIPEDA (the Personal Information Protection and Electronic Documents Act) is Canada's federal privacy law for private-sector organizations that ...
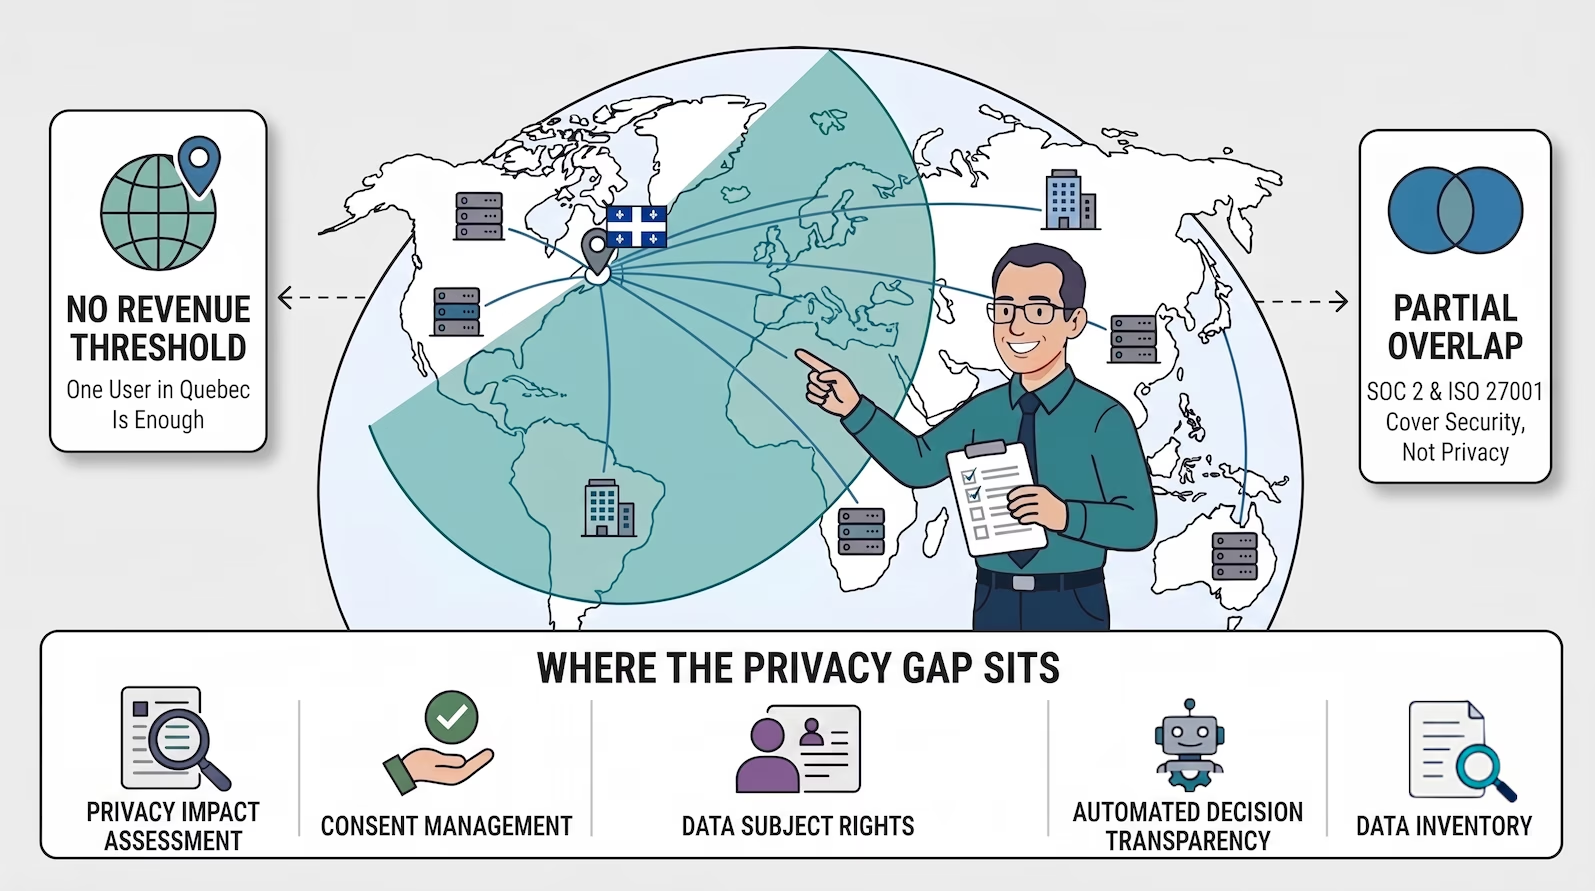
Quebec Law 25 Compliance: The Privacy Law Every SaaS Company Should Know About (But Probably Doesn't)

Quebec Law 25 is the province's modernized private-sector privacy law: a set of amendments (adopted in 2021 as Bill 64) to the Act respecting the ...
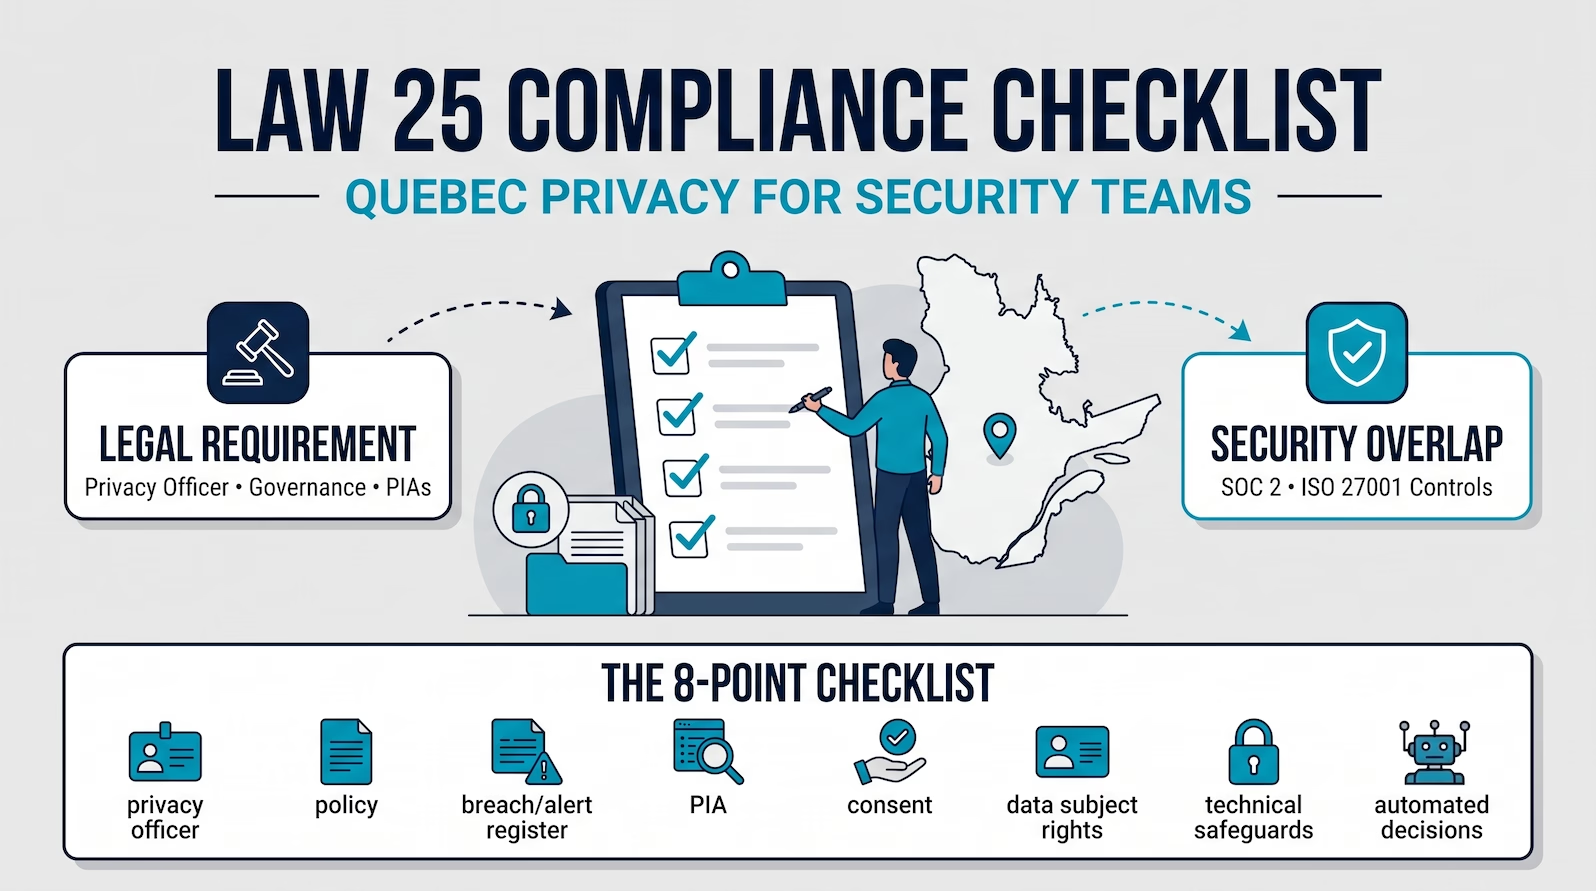
Law 25 Compliance Checklist: What Security Teams Actually Need to Do

Quebec's Law 25 has been fully in force since September 2024, and the penalties are no longer theoretical. Under the Act respecting the protection of ...