

Assess

Enterprise security architecture consulting

Bring your EDR, SIEM, identity and other security tools into one unified architectural blueprint.

We turn fragmented security controls into a coherent security program, giving you visibility over your data flows and system boundaries as your organization grows.

Advisory at USD $250 an hour in 10, 40 or 100 hour bundles. Reviews quoted as a fixed fee after the scoping call.

Talk to a security architect

Share the system in question and a senior architect will follow up to book a 30-minute scoping call.

What the engagement covers

Every engagement follows Assess, Build, Operate, scoped to the system, and follows a documented methodology. Delivered as a fixed-fee project, as a build we do with your team, or as ongoing advisory inside a fractional security team retainer. Pricing is in the FAQ below.

icon-7

Security architecture review

A component-and-connection walk of an existing system: hardening, patching, endpoint protection and privileged access per component; authentication, encryption and logging per connection. Findings ranked by business consequence, each with a concrete fix.

icon-5

Architecture assessment and target state

A current-state assessment across the security capabilities, then a target-state design with a sequenced roadmap. Diagrams and requirements engineers can implement.

icon-9

New system and cloud design advisory

Security architecture for new builds, cloud migrations and integrations, from the first whiteboard session through implementation review and the penetration test that validates the result.

icon-4

Operational handoff and detection coverage

We confirm logs ship to a central facility, detection use cases exist for the risks the design accepts, and compliance evidence is produced by normal operation.

icon-6

Controls mapped to the frameworks

Each design decision is tied to the SOC 2 criteria and ISO 27001 controls it satisfies, so the architecture answers the audit and the customer questionnaire.

icon-2

Independent of the vendor

Vendor solution engineers know their product's reference architecture. Our role is whether the product is the right control at all, where it sits in the wider design, and whether its telemetry reaches your security operations team.

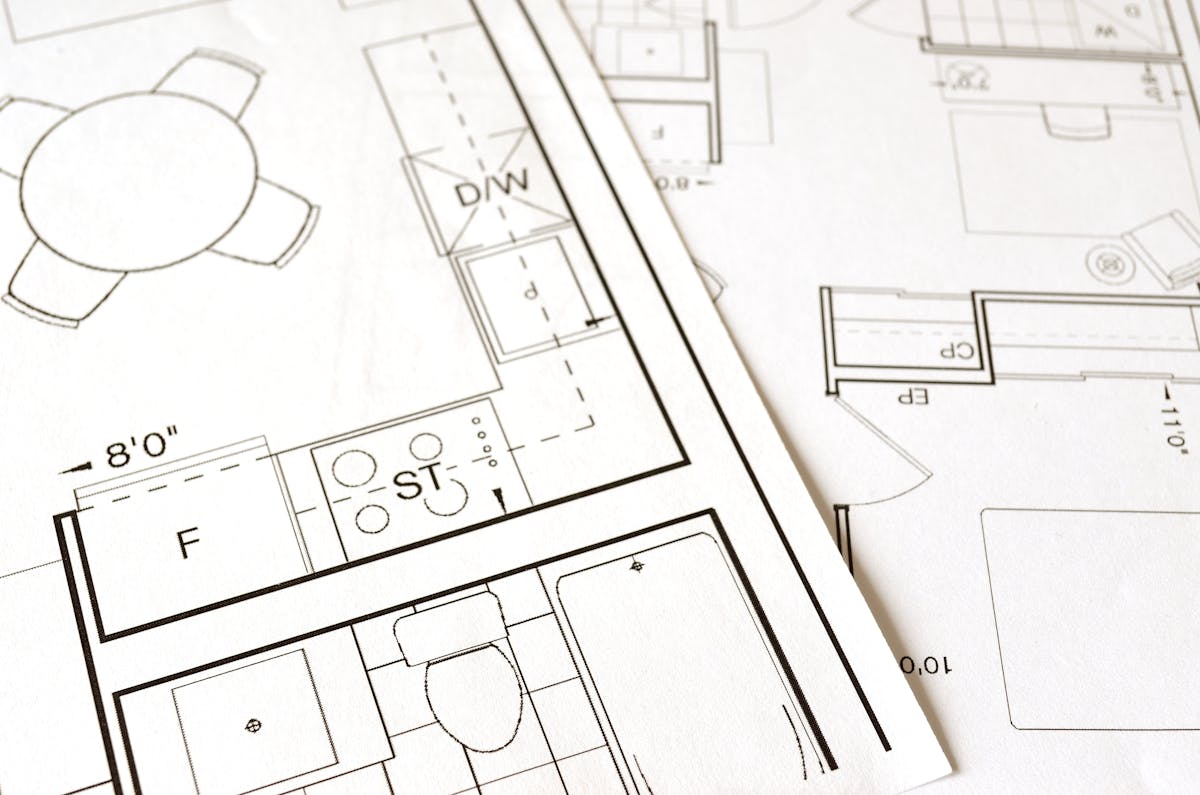
Architectural blueprint and floor plan, representing security requirements sourced from a system design

What a review found at a pre-launch SaaS company

One team we worked with had made strong design decisions before SOC 2 came up: tenant isolation, encryption at rest and in transit, protected branches with mandatory peer review, infrastructure as code, and a bastion host for external integrations. The architecture review connected those decisions to the evidence an auditor would ask for.

Found: no logging requirements written down for audit trails, and scanning tools with no remediation workflow behind them (SOC 2 CC7.1 and CC8.1).

Designed: logging and detection requirements per component and connection, a change-management flow built on the peer review already in place, and a documented customer-responsibility boundary.

Result: the controls stayed where the engineers had put them, and the evidence came from the systems instead of from a separate compliance project.

Assess, Build, Operate, applied to one system

The same model as the rest of the security program, scoped to the system in front of us. A documented methodology, led by a senior architect with more than ten years of enterprise security experience and a CISSP, whose prior work includes security architecture for the Bank of Canada and Payments Canada.

01

Assess

Interviews with the people who know the system, then a component-and-connection walk: hardening, patching and privileged access per component; authentication, encryption and logging per connection. Findings ranked by business consequence, each with a fix.

02

Build

A documented target architecture: data flows, control placement, security requirements, and the SOC 2 criteria and ISO 27001 controls each design decision satisfies. Your engineers can build from it, or our team builds it with you.

03

Operate

Handoff to security operations: logs reach a central facility, detection use cases exist for the risks the design accepts, and compliance evidence comes from normal operation. Ongoing advisory continues inside a fractional security team retainer when you want it.

What you hold at the end

Boxes and arrows your engineers can build from and your auditors can read.

  • Architecture diagram with data flows

  • Control placement per component and connection

  • Ranked findings, each with a fix

  • Target-state design and sequenced roadmap

  • SOC 2 and ISO 27001 control mapping

  • Logging and detection coverage map

  • Security requirements for the build team

  • Operational handoff notes for security operations

What changes once the architecture exists

One architecture, every framework. The controls live in the systems, so the evidence comes from the systems.

When an architecture engagement is the right call

Frequently asked questions

Enterprise security architecture is the documented design of how security capabilities protect an organization's systems: which controls exist, where they sit on each component and connection, and how they map to the business processes the systems serve. The working artifact is an architecture diagram with data flows and control placement, kept current as systems change.

A review examines one system or platform in depth: its components, connections and the controls on each, producing ranked findings and fixes. An assessment measures the architecture function across the organization against the security capabilities and produces a maturity view with a target state and roadmap. A review answers whether this system is designed securely. An assessment answers whether security is designed into how the organization builds.

Two pricing forms. Advisory is billed at USD $250 an hour in bundles of 10, 40 or 100 hours, with the larger bundles discounted, and the same rate applies inside a fractional security team retainer. Reviews and assessments are quoted as a fixed fee after the scoping call: a single-system security architecture review typically falls between USD $9,000 and $25,000, and a target-state assessment across several platforms is scoped above that. The price follows the number of components and connections in scope, how much of the architecture is already documented, and whether our team also builds the design. The scoping call is free and ends with a written quote.

Four stages. Discovery first: interviews with the people who know the system from a technical and a business-value point of view, a read of existing diagrams and documentation, and technical discovery with scripts or tooling where documentation is thin. Then the walk: every component checked for hardening, patching, endpoint protection and privileged access, every connection checked for authentication, encryption and logging. Then design: ranked findings with a fix each, a target architecture, and the SOC 2 and ISO 27001 mapping. Then handoff to your engineers and security operations. A single-system review is measured in weeks and a multi-platform target-state assessment in months; the scoping call sets the timeline for your system.

Five things. A senior architect doing the work, with ten or more years in cybersecurity, five in architecture, and credentials such as CISSP or CCSP. A documented method that walks components and connections rather than a slide of tools. Deliverables engineers can build from: diagrams with data flows, control placement and written requirements. A handoff to security operations, so logs, detection use cases and compliance evidence come from the finished design. And independence from the technology vendors whose products the design places. Ask any firm you evaluate for a sample diagram and a sample findings page before you sign.

Access to the people who know the system, an executive who owns the risk decisions the design will raise, and whatever documentation exists: diagrams, data-flow descriptions, cloud account layouts, the list of security tools in place. A current diagram helps and is optional; when none exists, producing it is the first deliverable. Read-only access to cloud consoles or network observation is arranged during discovery when technical discovery is needed, and Truvo takes no custody of production data.

Accountability rests with the senior technology or security leader, typically the CTO or CISO, regardless of who provides the advice. The advising security architect, whether in-house, fractional or consulting, designs and reviews. The accountable executive decides and owns the risk the design accepts.

A typical bar is ten or more years of cybersecurity experience with at least five in security architecture, supported by certifications such as CISSP, CCSP, CISA, CISM or GIAC. Beyond credentials, the consultant needs a working understanding of the technology being secured, the business processes it serves, and what security operations requires to run the system day to day.

At the first of: a compliance requirement with system implications (SOC 2, ISO 27001, a customer security review), a new platform build or cloud migration, or the first serious security technology deployment such as EDR or SIEM. Advice before these moments decides the design. Advice after them audits it, and redesign costs more than design.

No. Vendor solution engineers know their product's reference architecture better than anyone, and their hours are already paid for. Our role is independent: whether the product is the right control at all, where it sits in the wider design, and whether its telemetry reaches your security operations team.

Talk to the architect who would do the work

A 30-minute scoping call. We look at your environment, tell you plainly whether we can help, and follow up with a fixed-fee quote and timeline.

From the blog: security architecture

Agentic AI Security Architecture: How to Let AI Agents Do Real Work Safely

Agentic AI security architecture starts with a map of the components of an AI agent system and the connections between them, which sets the scope, ...
What Does a Security Architect Do?

A security architect does three jobs: sets security requirements for systems other people design, assesses and reviews those designs, and solutions ...
Hybrid Identity Management: How to Centralize IGA

It's tempting to centralize identity by buying a platform, but I leave the platform for last. Below is my approach to solutioning centralized ...