IncidentIncident ResponseISO 27001

7 posts
ISO 27001 A.5.24 requires an organization to plan and prepare for security incidents before they happen: define the roles, the response process, the ...
Filter by Tag
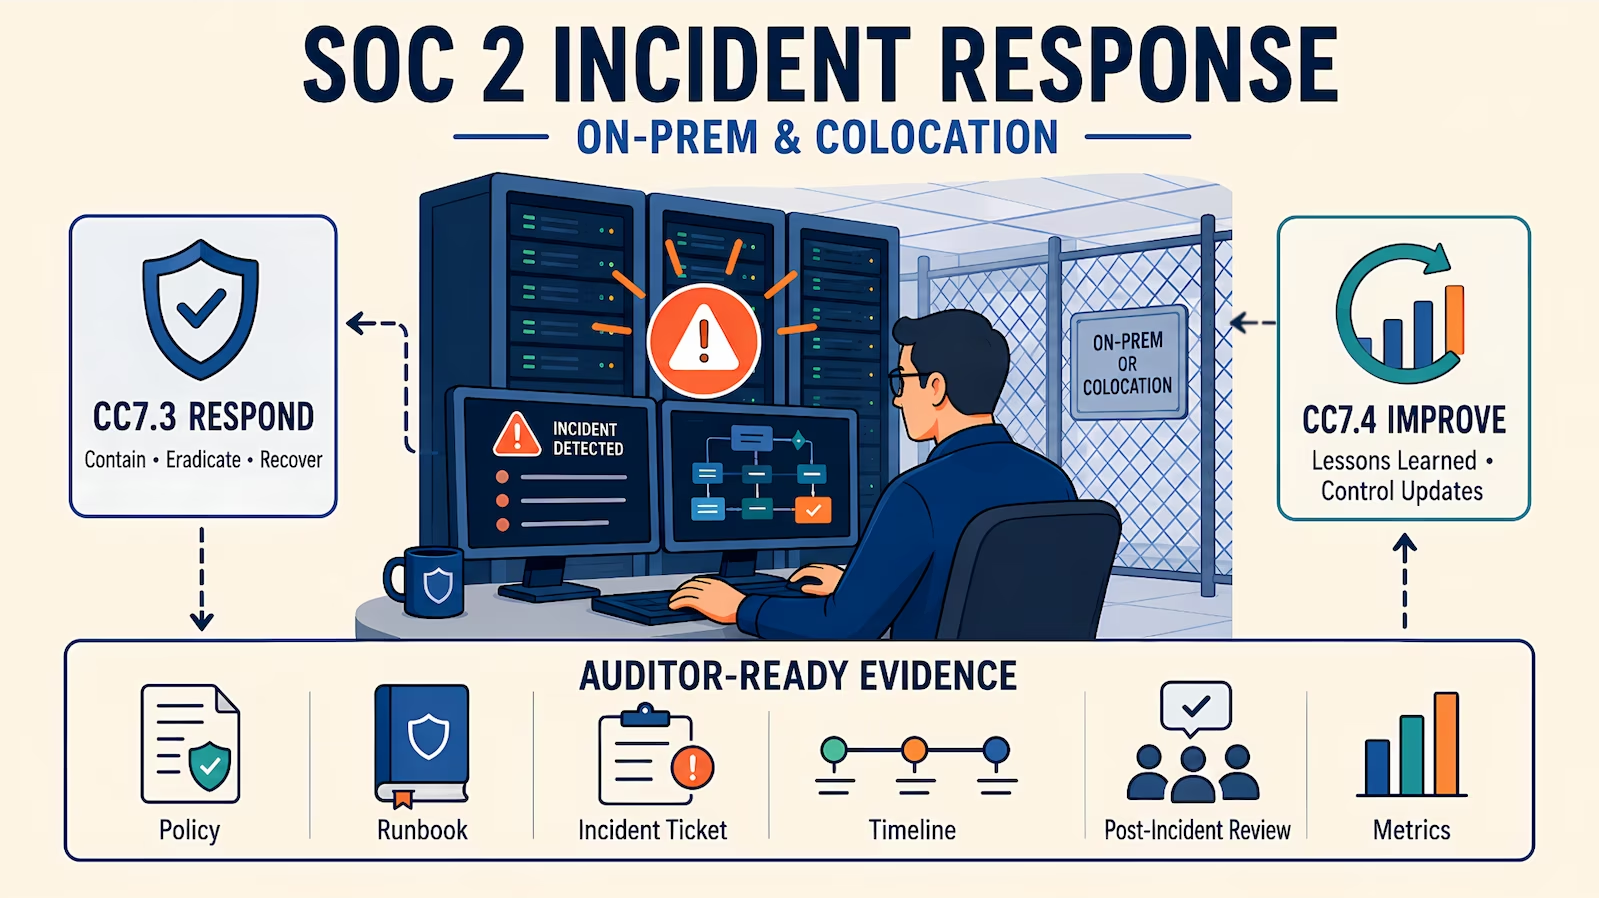
SOC 2 CC7.4 requires a company to respond to security incidents through a defined incident-response program that understands, contains, remediates,...
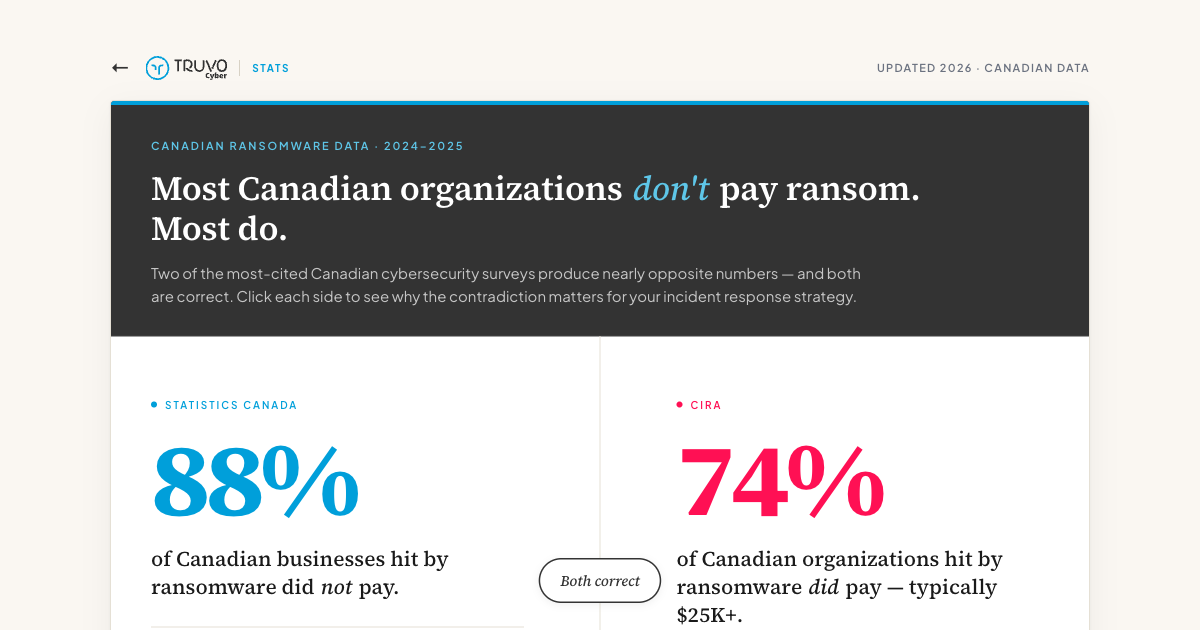
Two of the most-cited Canadian ransomware statistics flatly contradict each other.
Statistics Canada, reporting on 2023 data released in October...
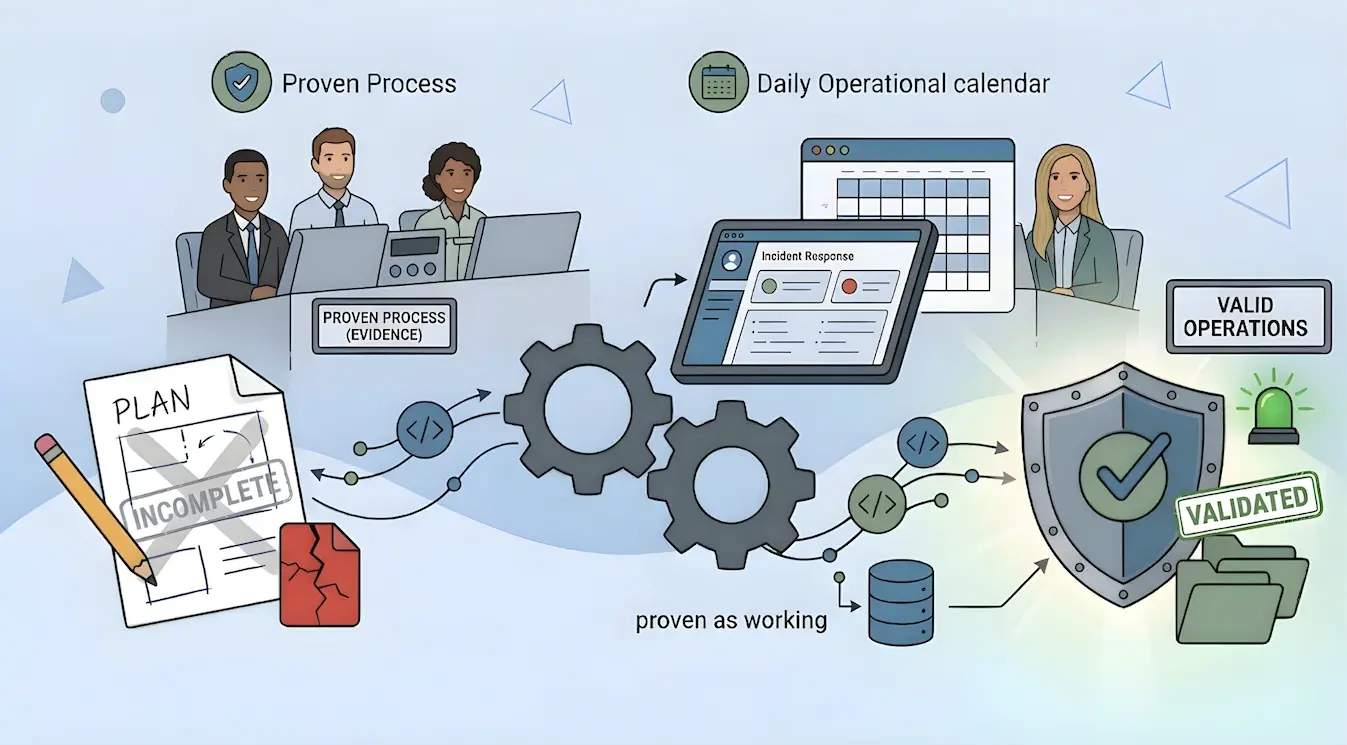
An incident response plan that exists only in a shared drive is not evidence of preparedness. It is evidence of intent, and the Canadian Program for...
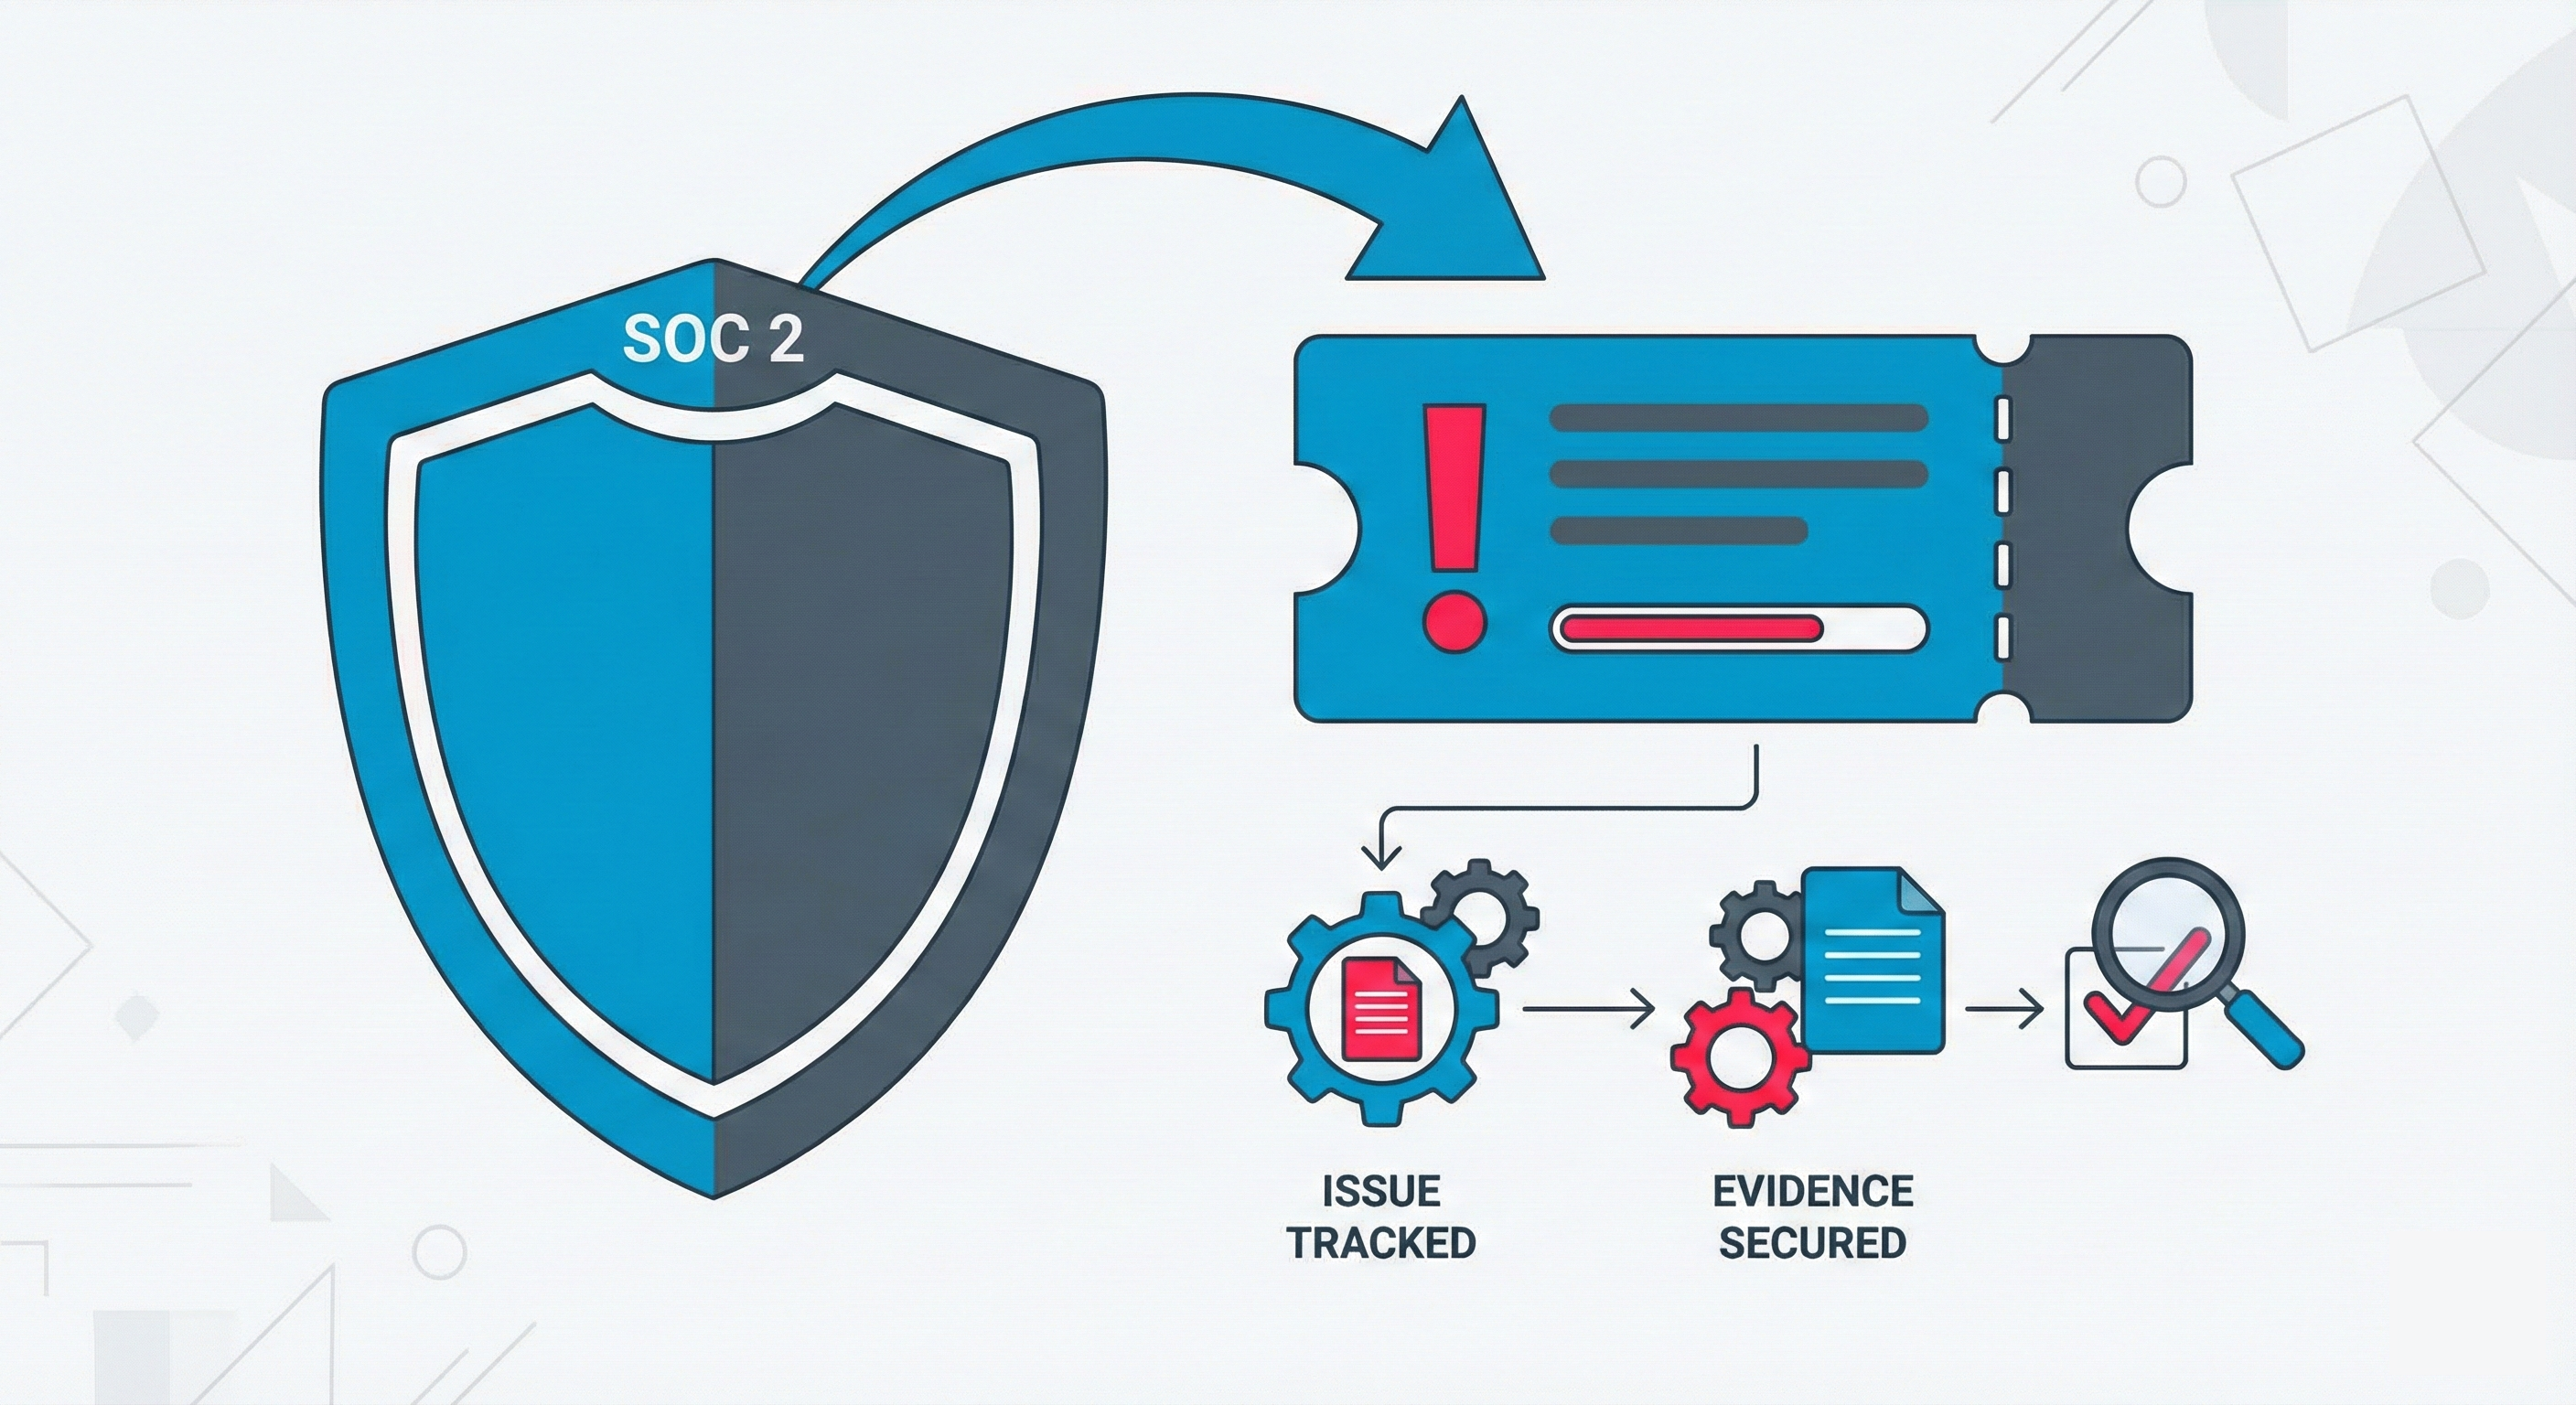
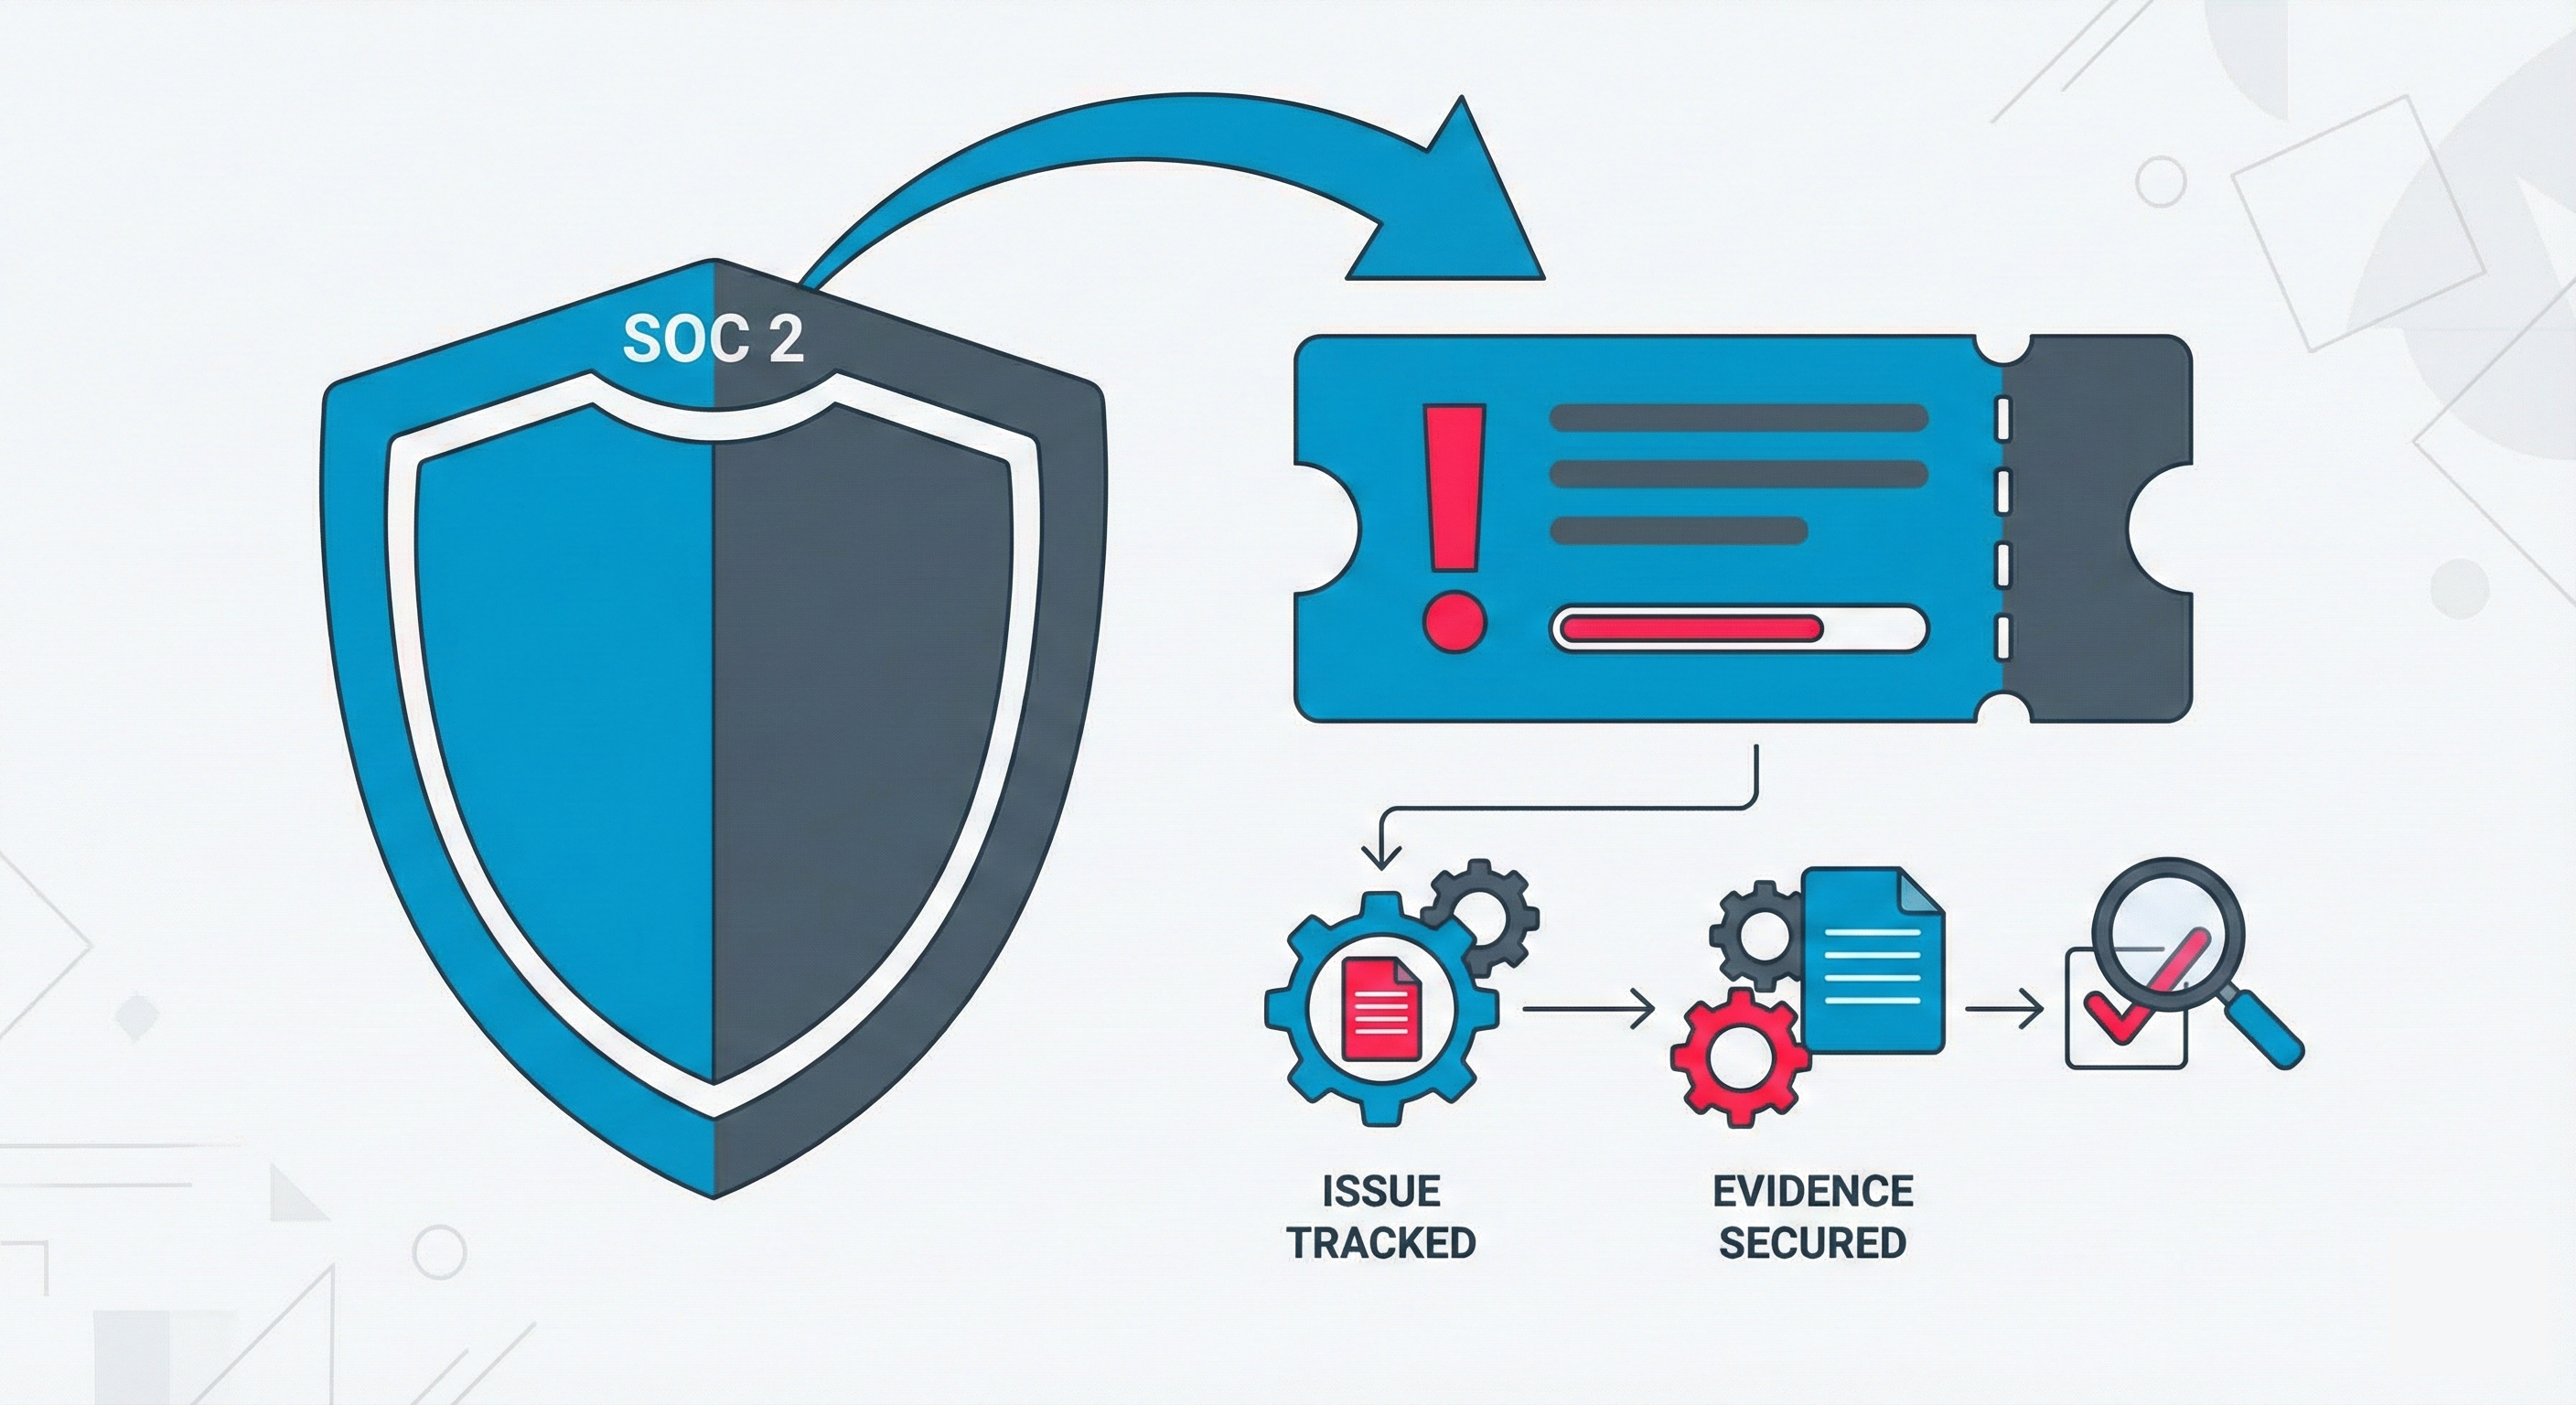
TL;DR: SOC 2 compliance requires a formal, trackable process for all security-relevant activities. Under the Trust Services Criteria, this means...

Ransomware attacks are among the most disruptive forms of cybercrime, locking businesses out of their own data and demanding ransom for its release....