GRCCanada


36 posts
RPAA compliance means a payment service provider (PSP) in scope of the Retail Payment Activities Act registers with the Bank of Canada, operates a ...
OSFI Guideline B-10 (Third-Party Risk Management) sets the rules Canadian banks, insurers, and trust and loan companies follow when they assess,...
OSFI B-13 is the Office of the Superintendent of Financial Institutions' Technology and Cyber Risk Management guideline. B-13 has been in effect...
GRC software and a security review are different. The software is the tool. The review is the work that helps a B2B SaaS deal move forward.GRC...
GRC in cyber security stands for governance, risk, and compliance: the discipline of directing a security program (governance), identifying and...
GRC engineering is the practice of building and operating a governance, risk, and compliance program with software engineering methods: evidence...
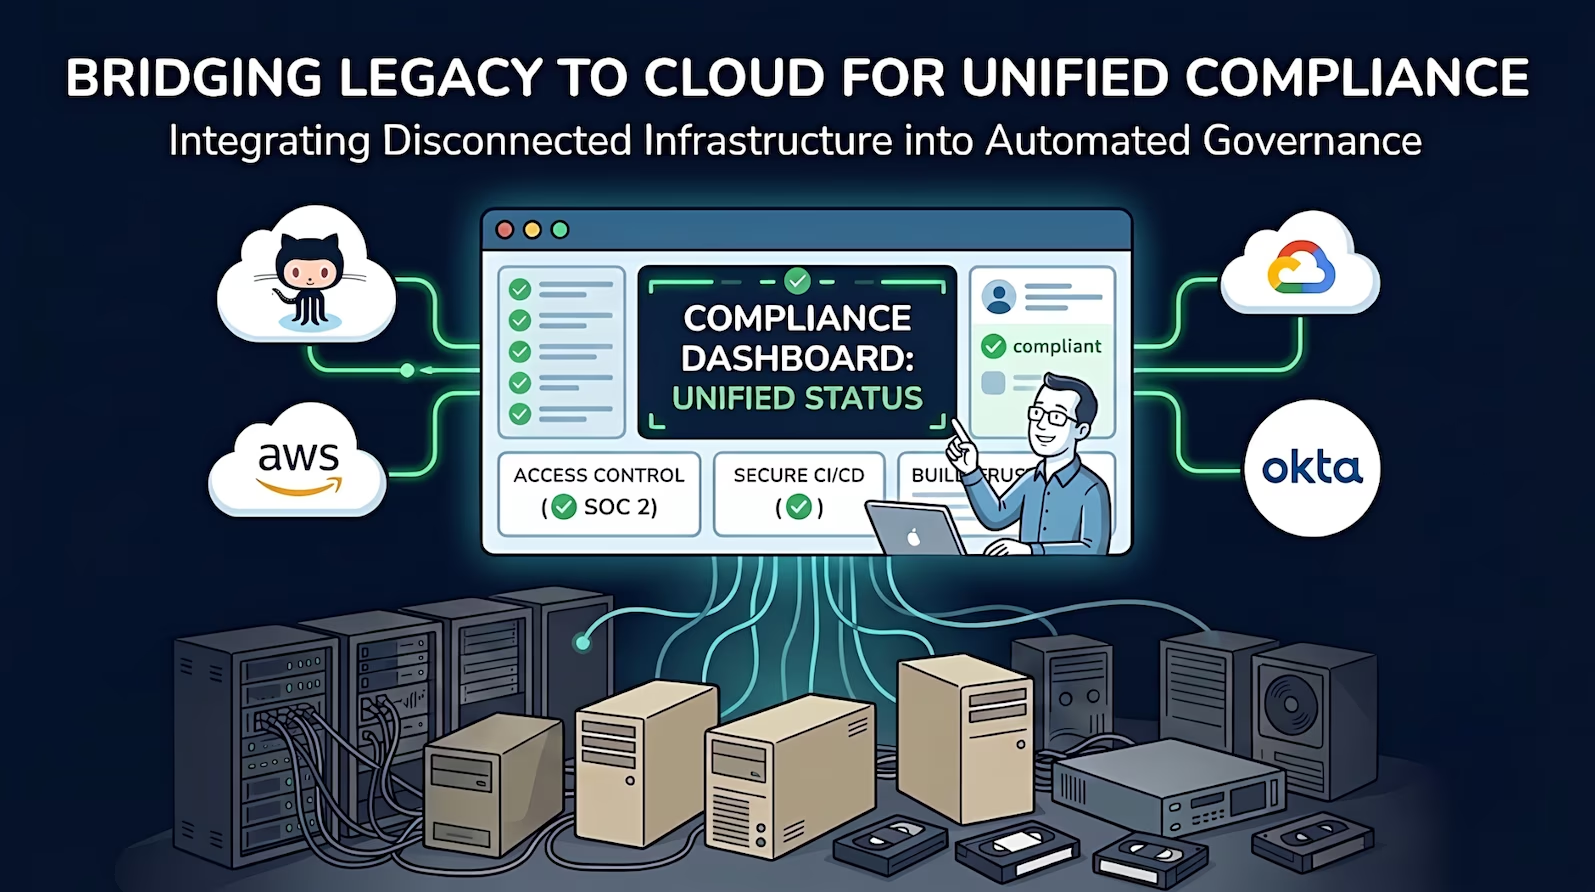
We've seen all to often. organizations that have been running a GRC platform for six to twelve months: the dashboard is green, the audit prep feels...
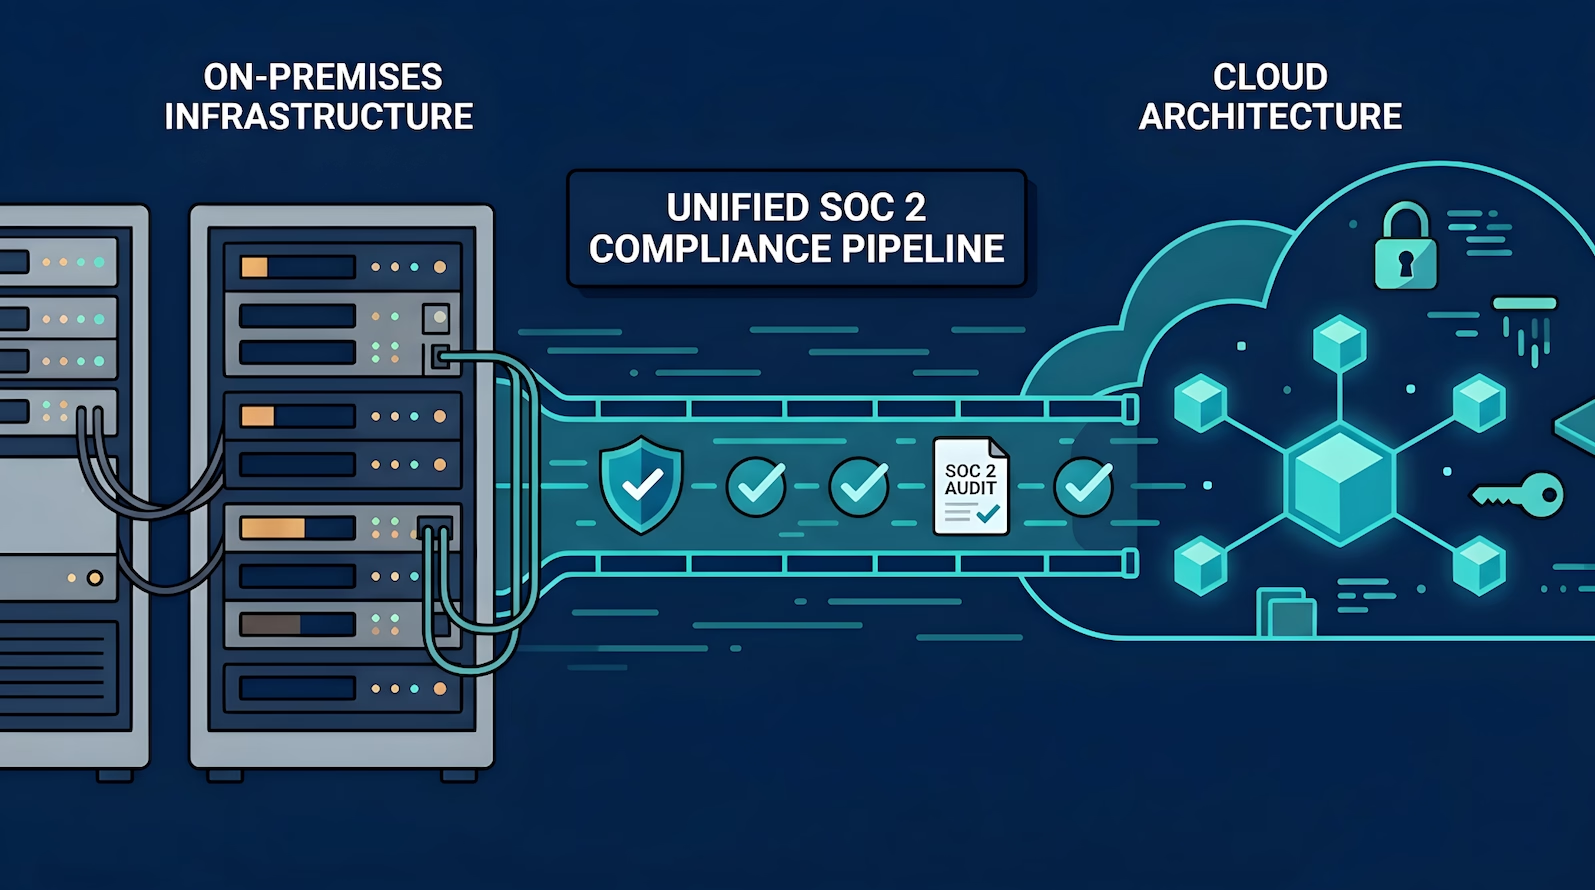
GRC platforms automate compliance evidence collection for cloud-native infrastructure. Connect your AWS account, hook in your identity provider, link...
Companies that implement Vanta or Drata expecting near-complete automation of their SOC 2 compliance work tend to hit the same wall. The integrations...
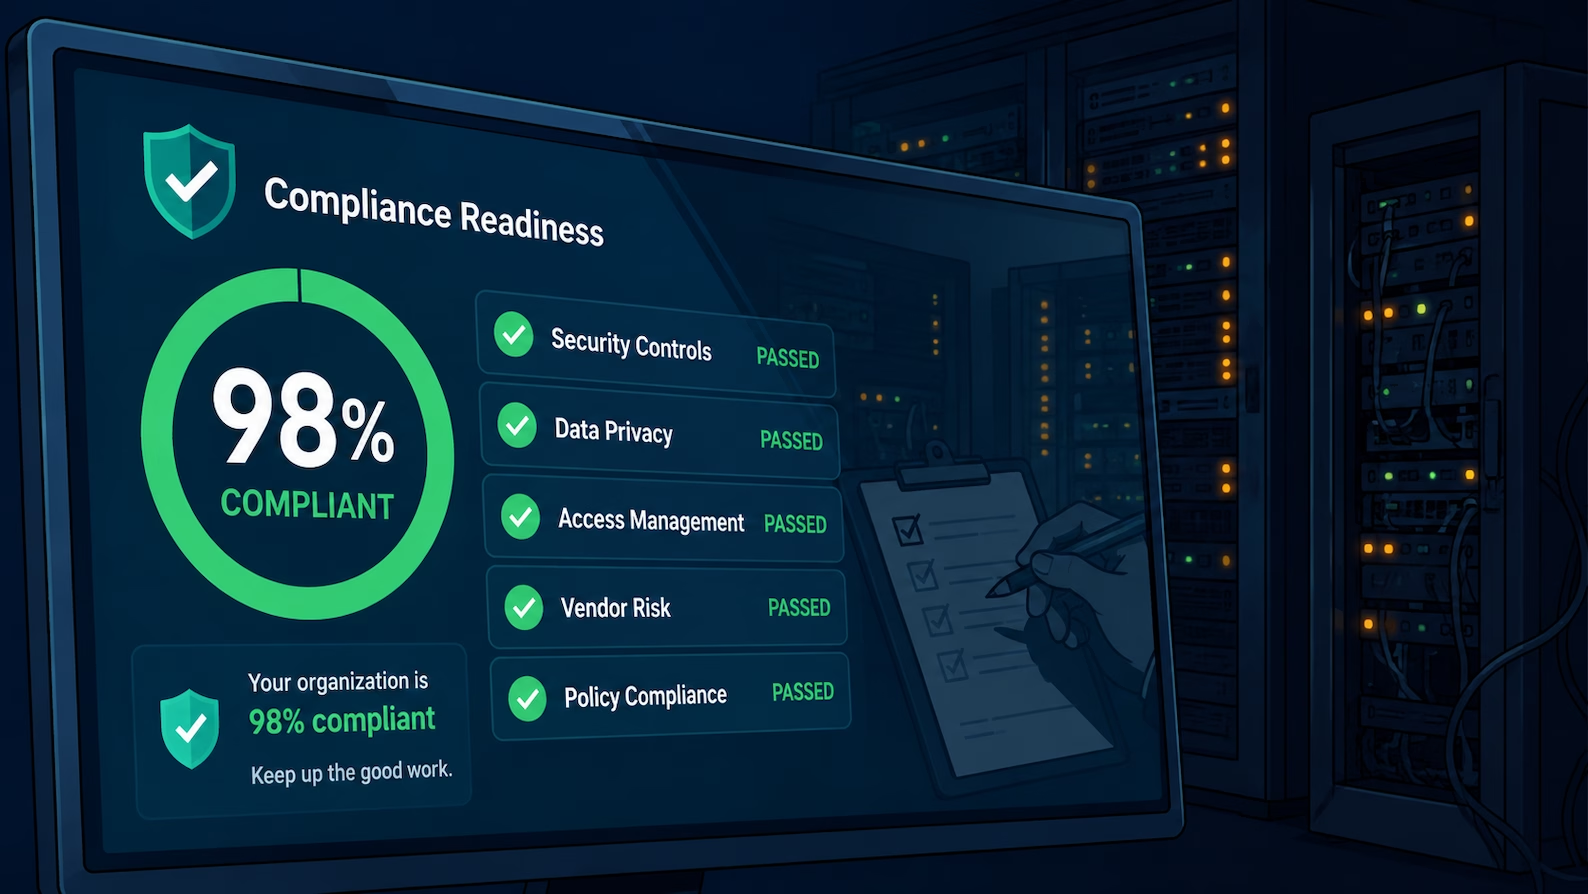
The GRC platform dashboard is green. Every automated test passes. The readiness score reads somewhere in the nineties. The team spent three months...
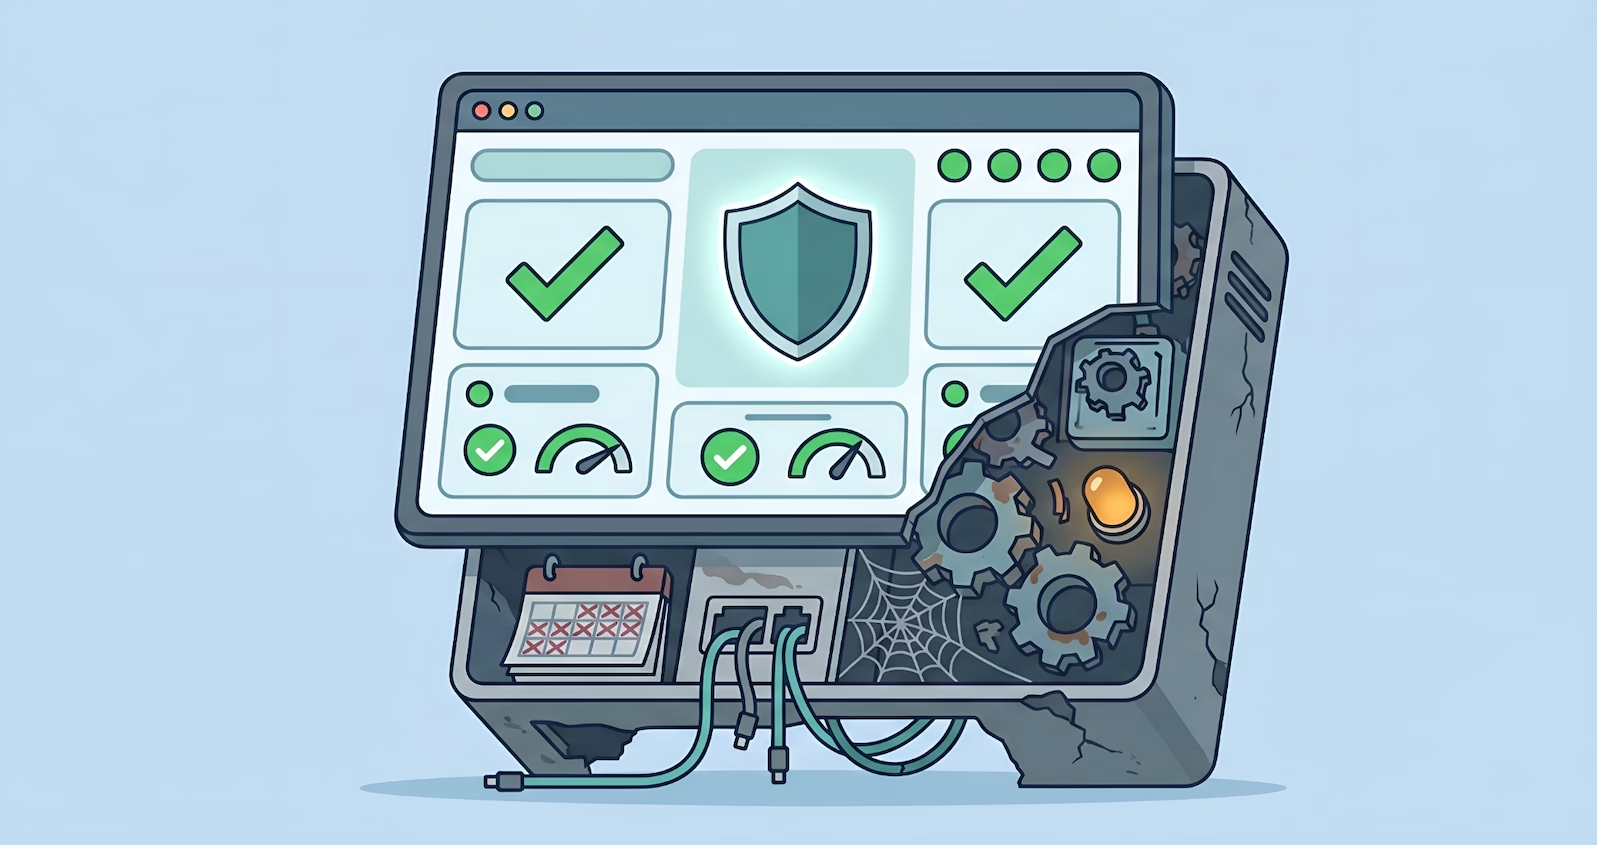
A company subscribes to a GRC platform. A consultant configures it, loads policies, maps controls, connects integrations. The dashboard turns green....
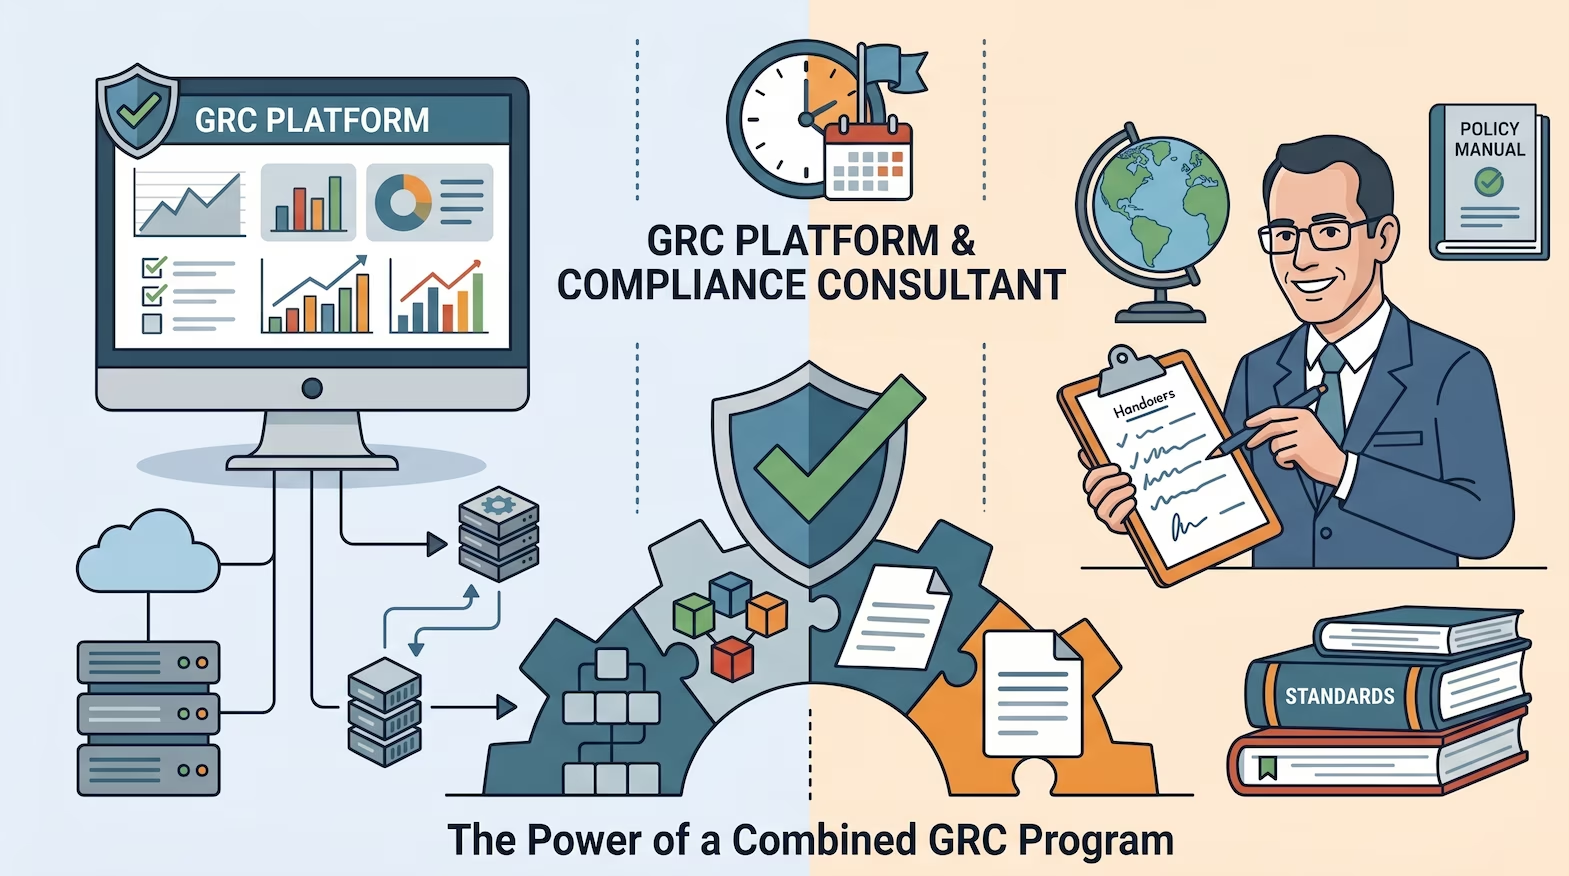
A GRC platform such as Vanta or Drata automates evidence collection, roughly 60 to 70 percent of the compliance workload for a cloud-native SaaS...
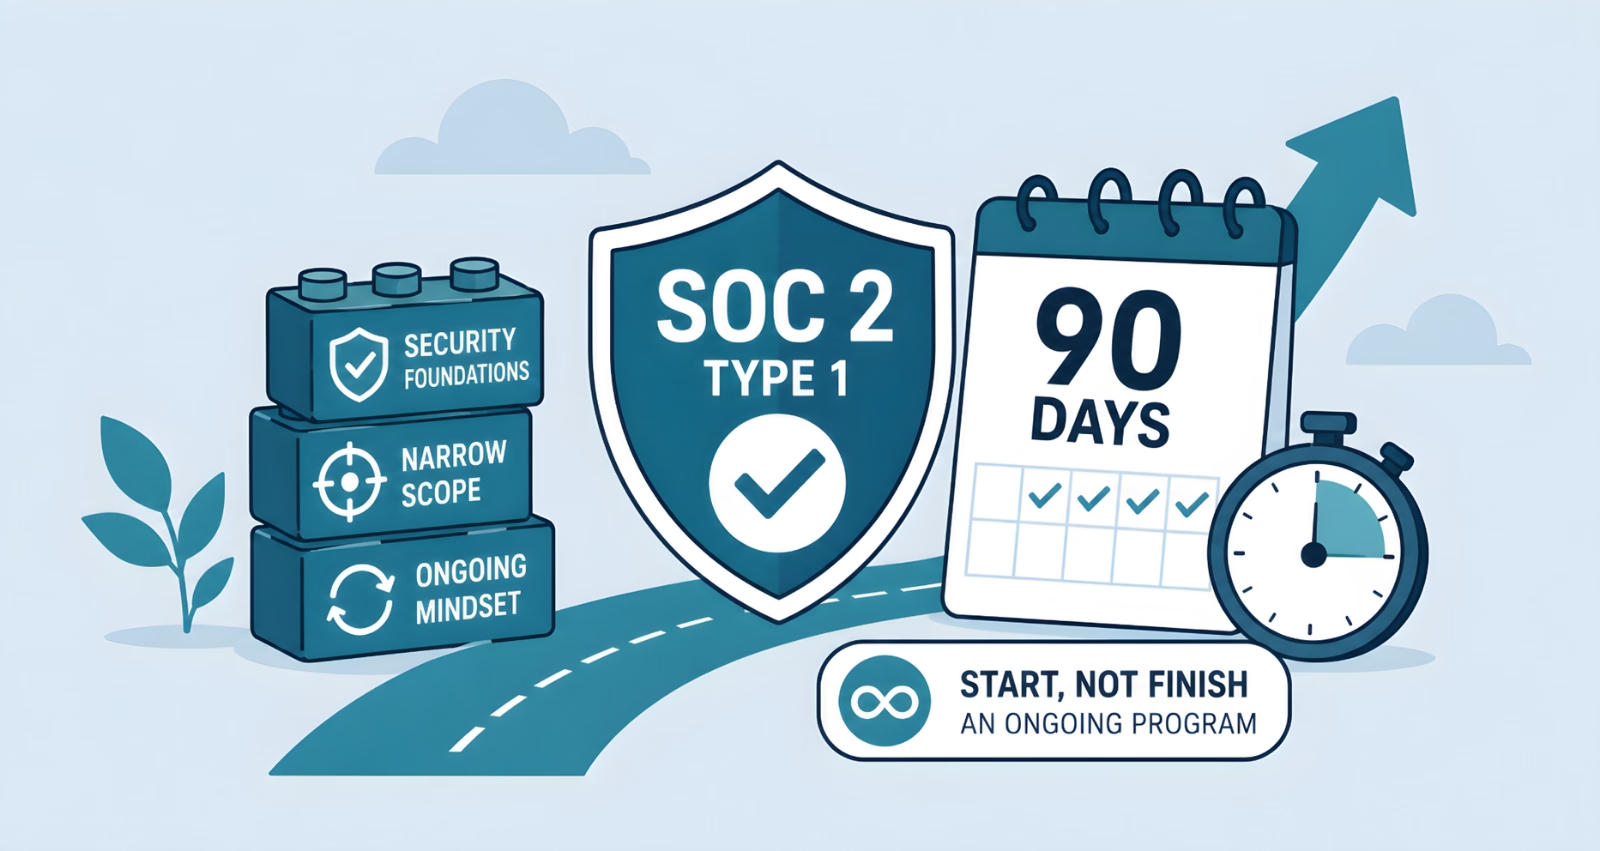
Ninety days from kickoff to a SOC 2 readiness is achievable. It is not achievable for every company, and the companies that hit it make deliberate...
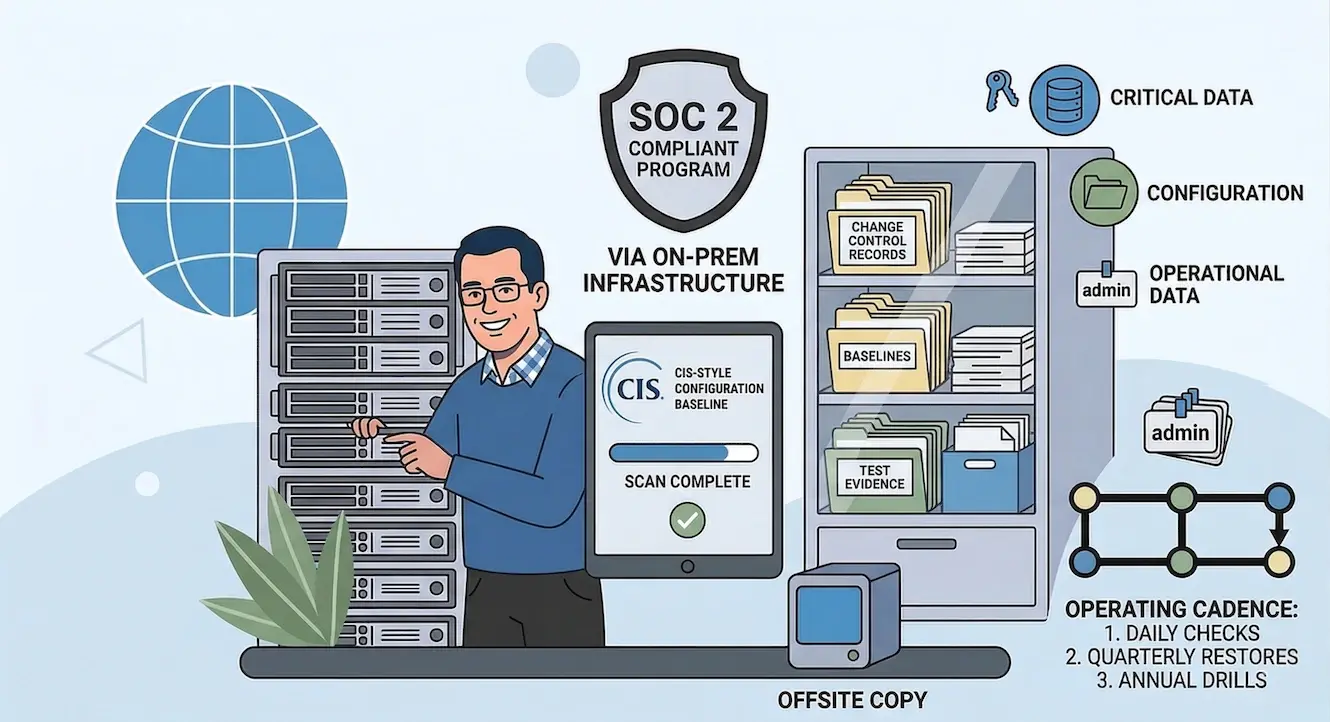
In cloud environments, configuration compliance is a toggle. Enable AWS Config, deploy a conformance pack, and the platform continuously evaluates...
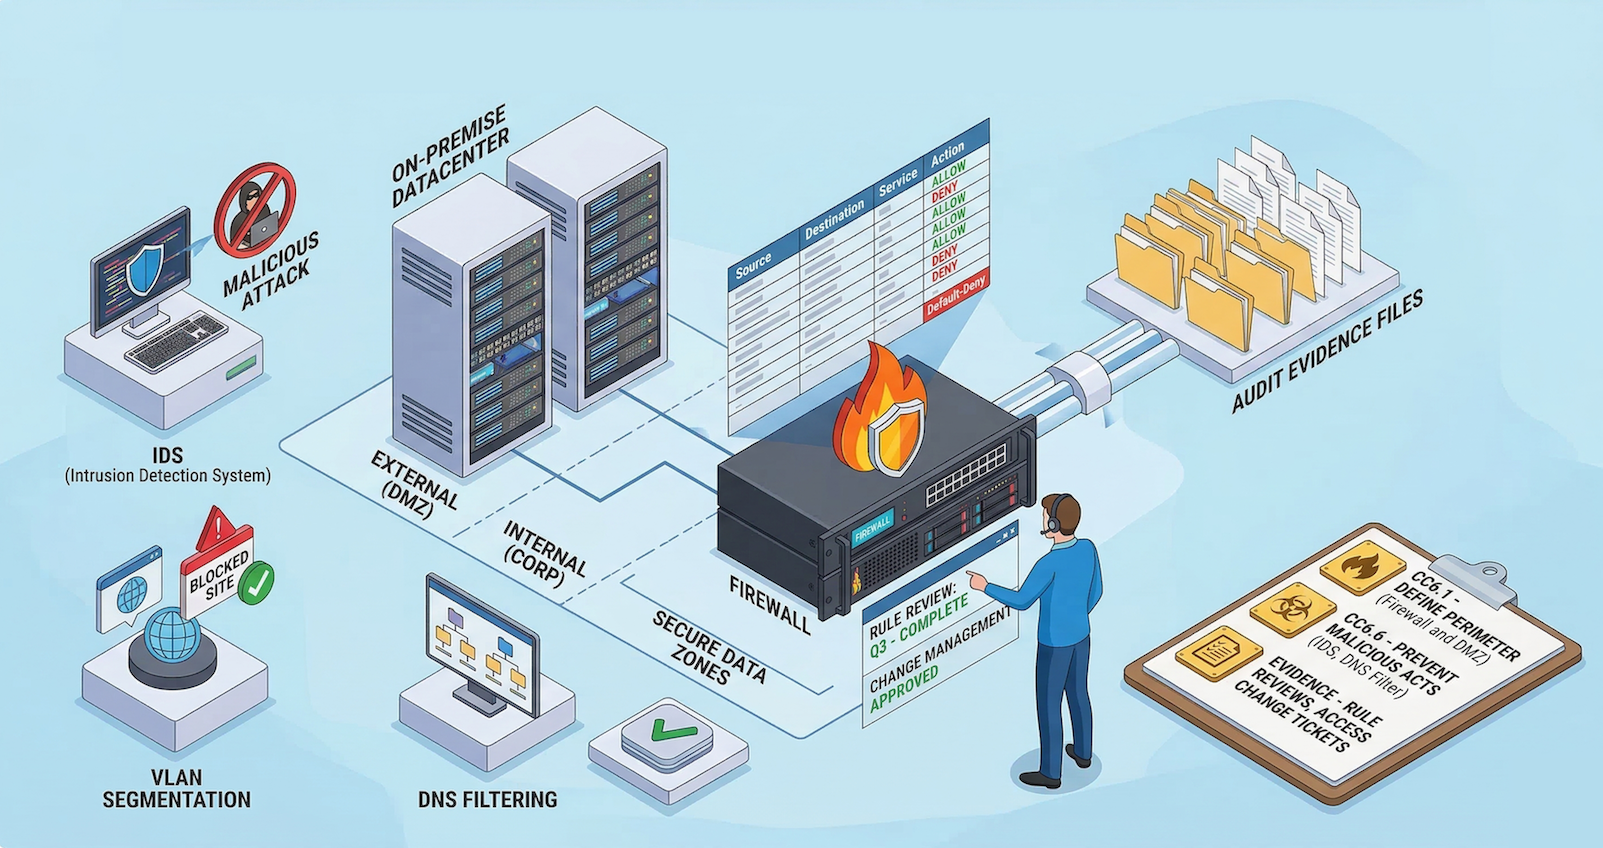
Every SOC 2 guide on network security assumes the infrastructure lives in AWS. The advice is always the same: configure security groups, enable VPC...

Supply chain cyber risk has become one of the most pressing cybersecurity challenges for businesses of all sizes. A single compromise in a supplier’s...

TL;DR: Even when SOC 2 is the only compliance requirement on the table, a compliance automation platform (Vanta, Drata, Secureframe, Scrut) pays for...

A 200-question security questionnaire lands in the sales team's inbox on a Thursday...


As a startup navigating the complexities of data security, understanding SOC 2 compliance is essential. SOC 2 (System and Organization Controls 2) is...

New business reality is that companies must prioritize cybersecurity compliance to protect customer data and demonstrate their security posture. The...

For many SaaS companies, achieving SOC 2 compliance is a major milestone, a sign that they take security and customer trust seriously. But the real...

A SOC 2 Type 2 report is a CPA firm's opinion on whether a service organization's security controls were designed well and operated effectively over...

Every SOC 2 roadmap on the internet reads the same way: pick a platform, connect your integrations, run the gap analysis, remediate, audit. Five...

SOC 2 is an attestation report a licensed CPA firm issues against the AICPA's Trust Services Criteria. The report describes whether a service...

SOC 2 CSOCs (Complementary Subservice Organization Controls) are vendor controls your system depends on but does not operate. A SOC 2 report handles...

Six months after buying Drata, Vanta, Secureframe, or any other compliance automation platform, a company realizes the dashboard is half-populated,...


