Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

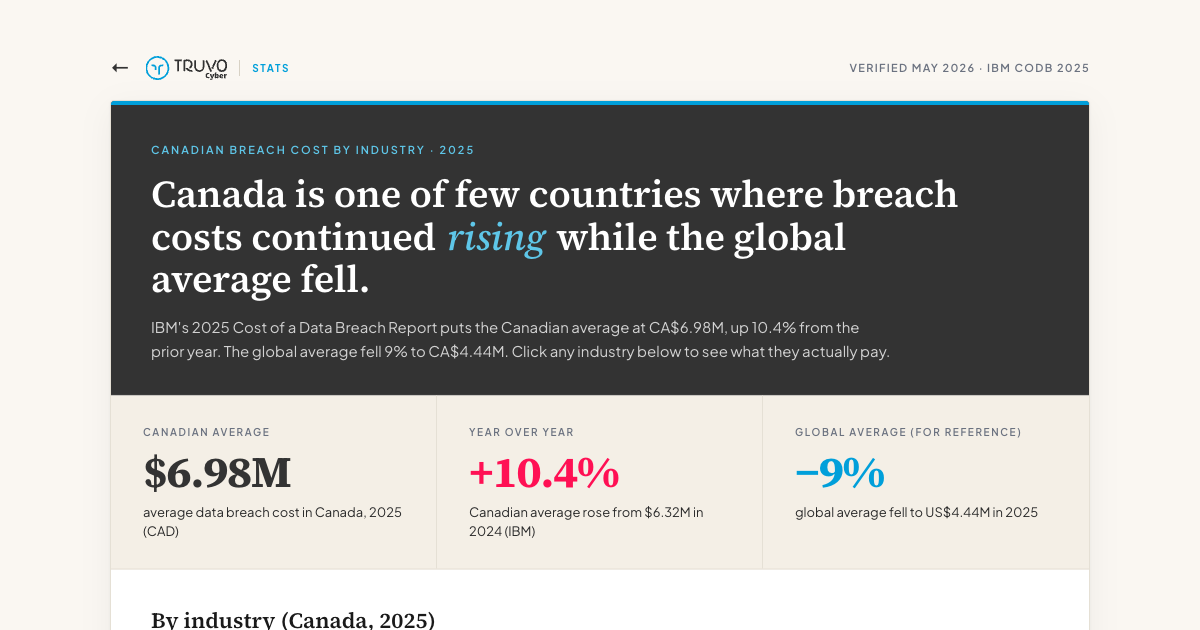
Canadian breach cost dashboard: CA$6.98 million 2025 average, up 10.4 percent year over year while the global average fell 9 percent. Truvo Cyber.

The Real Cost of a Data Breach in Canada (2025)

Canada is moving in the wrong direction on breach economics.

In 2025, the average cost of a data breach for a Canadian organization climbed to...
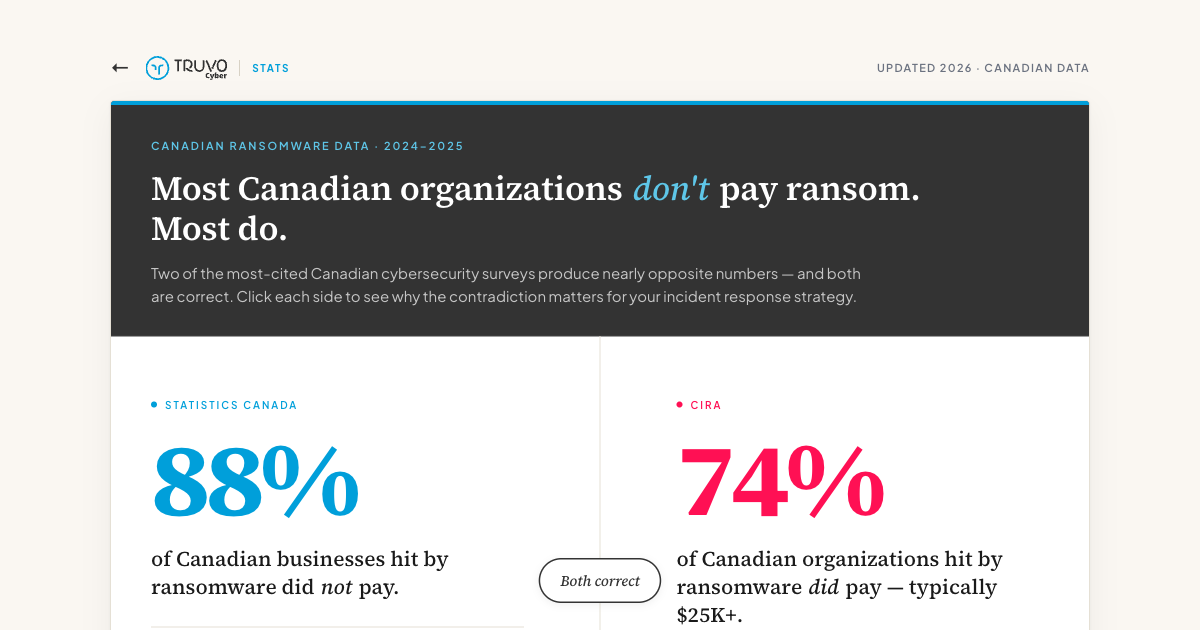
The Canadian Ransomware Paradox: Statistics Canada reports 88 percent of victims don't pay, CIRA reports 74 percent do, both surveys correct. Truvo Cyber.

The Canadian Ransomware Paradox: Why Two Surveys Disagree on Payment

Two of the most-cited Canadian ransomware statistics flatly contradict each other.

Statistics Canada, reporting on 2023 data released in October...
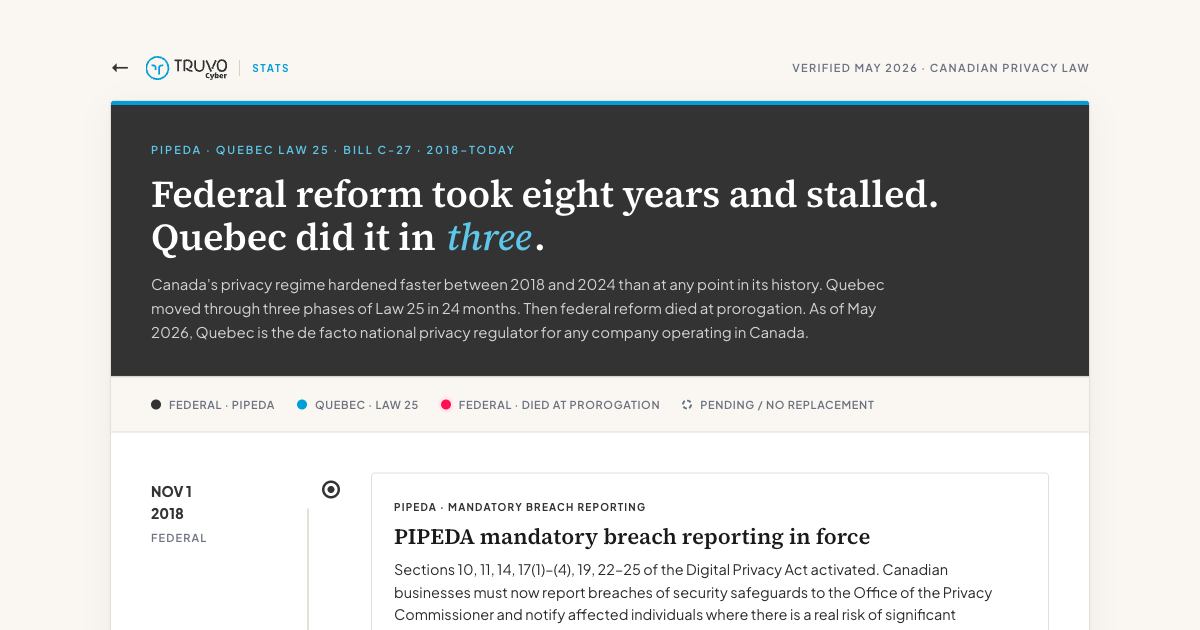
Canadian privacy law timeline 2018 to today: PIPEDA federal breach reporting, three phases of Quebec Law 25, and Bill C-27 dying at prorogation in January 2025. Truvo Cyber.

After Bill C-27: Quebec Law 25 and Canadian Privacy Costs

For three years, the dominant story in Canadian privacy law was the federal one. Bill C-27, the Digital Charter Implementation Act, was on track to...
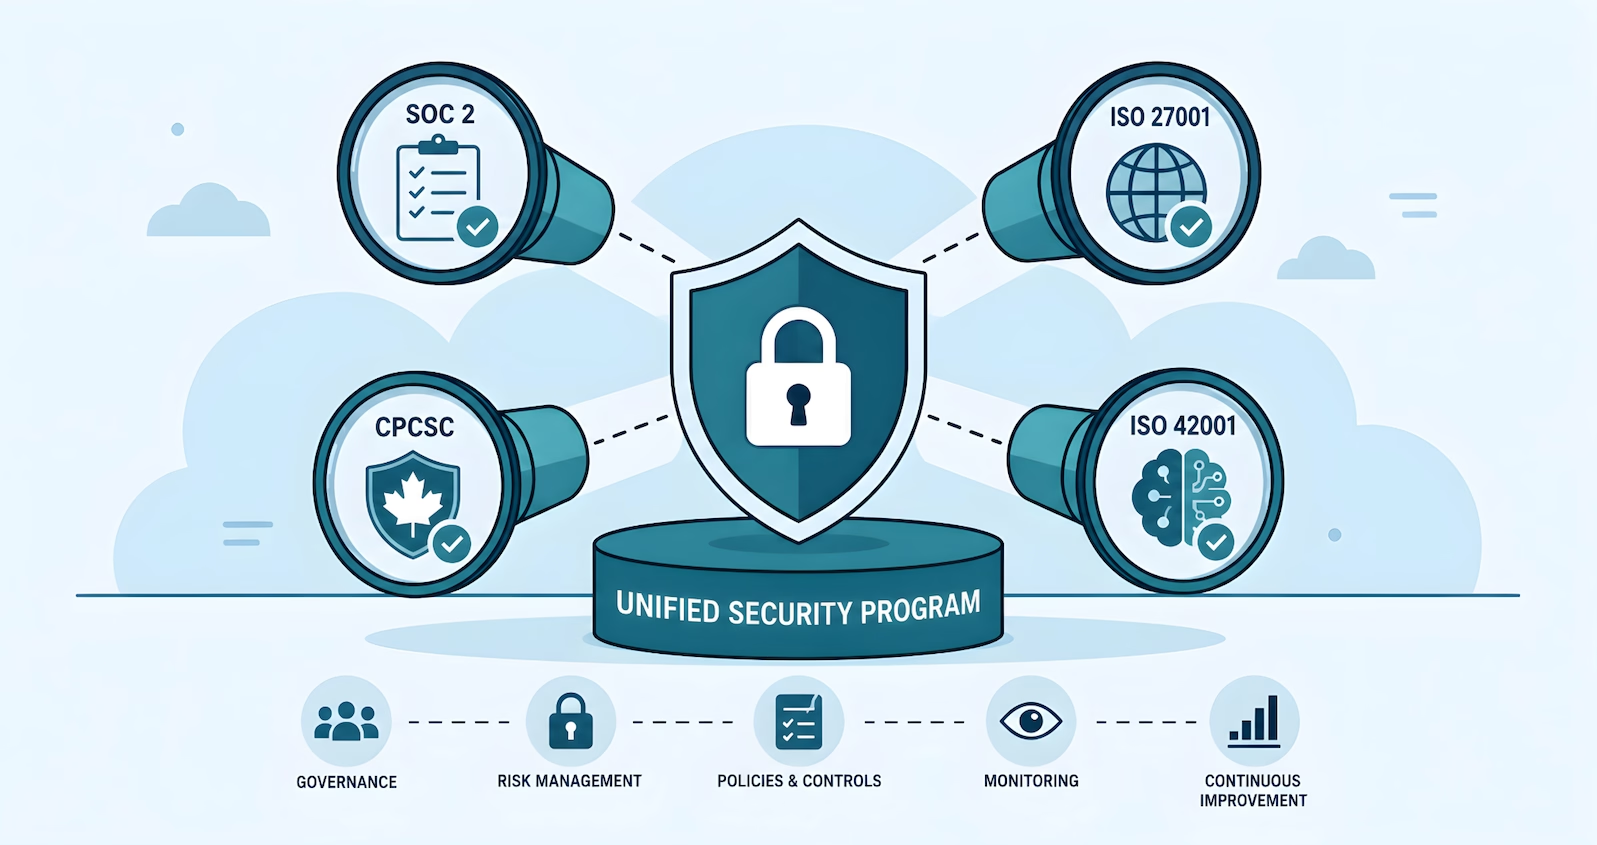
Flat vector illustration of a unified cybersecurity compliance program. A central shield icon connects to SOC 2, ISO 27001, CPCSC, and ISO 42001, showing multiple frameworks built on one shared security foundation with governance, risk management, policies, monitoring, and continuous improvement.

Why Frameworks Are Lenses on a Security Program

When the second framework arrives, most teams make the same mistake.

The first one, usually SOC 2, took nine to twelve months and a large chunk of...
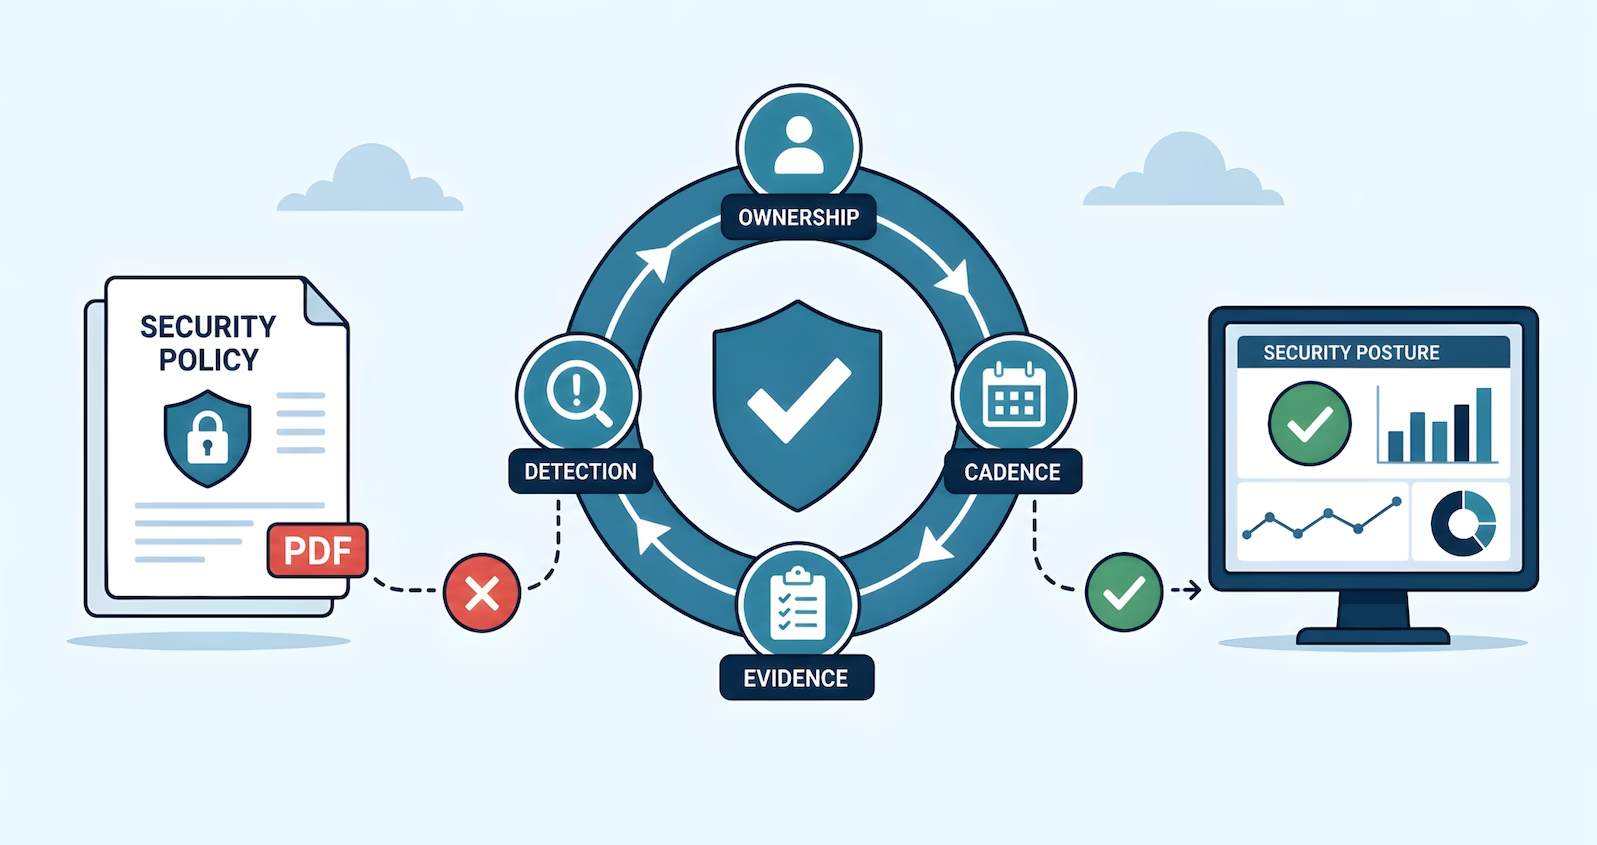
Flat vector illustration showing how security policies become operational processes. A rejected “PDF” policy document leads into a circular workflow of ownership, cadence, evidence, and detection around a security shield, ending with a compliant security posture dashboard.

Operationalizing Security Policies: From PDF to Practice

The moment that usually exposes a security program is not the audit. It is a simple question asked in a meeting.

"Who actually reviews user access...
A two-panel illustration comparing a stressed CTO with many security concerns to a calm Fractional CISO who has streamlined security and compliance.

Fractional CISO for SaaS Companies: What the Role Actually Looks Like

Security leadership at most SaaS companies follows a predictable pattern. The CTO handles it. Not because they volunteered, but because nobody else...
An illustration titled "THE EVIDENCE GAP." On the left, a person sits by a messy pile of papers, representing manual chaos. On the right, a neat stack of digital dashboards leads to a "SOC 2 Report." A blue arrow points from the clutter toward the streamlined, automated digital solution.

Bridging the Evidence Gap: How to Turn Solid Security into SOC 2 Compliance

The most common compliance gap has nothing to do with missing controls. It's missing evidence.

What we see often is that technically competent teams...

What Is Cyber Security Posture? Definition and Importance

What Is Cyber Security Posture? Definition and Importance

Like in any industry, cyber security and cybercrime is constantly evolving. To keep up, you need to remain familiar with upcoming trends and the...

How to Build a Security Program That Maps to Any Framework

How to Build a Security Program That Maps to Any Framework

Every compliance framework, SOC 2, ISO 27001, CMMC, HIPAA, asks the same fundamental question: does this organization have an effective security...