CybersecuritySOC 2ISO 27001


SOC 2 and ISO 27001 can lower cyber insurance premiums, and the effect shows up in three ways: a lower premium, better terms (lower retentions, fewer...
Canadian cyber insurers expect five controls before they quote: multi-factor authentication (MFA) on remote access and email, tested backups,...
A vulnerability management policy is the document that sets how an organization finds, rates and fixes vulnerabilities, and how long each severity...
An incident response policy is the set of management-approved rules for security incidents: who must report a suspected incident, how severity is...
An incident response plan is the document a company follows from the moment a security event is reported until the incident is closed and reviewed....
The Google Cloud IAM gaps that show up most often in baseline reviews come from Google's own defaults. Organizations created before May 2024 never...
Risk-based vulnerability management is the practice of ranking scanner findings by the risk each one carries in a specific environment (exposure,...
Security Command Center (SCC) is Google Cloud's built-in security and risk dashboard, and the Standard tier is free. Premium adds threat detection,...
Google Cloud ships a set of security services that cost nothing or a few dollars a month, and many of them are switched off by default. The best GCP...
An AI agent threat model is a written record of what the agent can access, how that access could be misused, and which control limits each case. The...
OSFI Guideline B-10 (Third-Party Risk Management) sets the rules Canadian banks, insurers, and trust and loan companies follow when they assess,...
A vCISO service in Canada is fractional security leadership that owns the security program and also covers the Canadian obligations a US-focused...
The main security considerations for MCP servers and agent skills are supply-chain risks: both deliver instructions and code that an AI agent trusts...
AI agents and identity security meet at one rule: give every AI agent its own identity, manage the agent as an insider with privileged access, and...
Prompt injection is an attack in which someone writes text that a large language model (LLM) treats as instructions, so the model follows the...
By the end of this guide, a complete beginner will be able to open a Linux terminal, move around the file system, and create, copy, and rename files...
To install OpenClaw safely on a Mac, run OpenClaw inside a macOS virtual machine, give the agent dedicated cloud credentials with a spend cap, deny...
OpenClaw is an open-source AI assistant that you host yourself and talk to through chat apps such as Slack, WhatsApp or Telegram. The OpenClaw...
We recently used frontier AI throughout an incident response engagement, from the first log query to the final incident report. This is how it went,...
Phishing-resistant MFA in Microsoft Entra ID means signing in with a passkey, Windows Hello for Business or certificate-based authentication, methods...
Microsoft Identity Manager (MIM) 2016 reaches end of support on January 9, 2029. Microsoft extended the date from January 13, 2026, and its...
An Active Directory to Entra ID migration moves the source of authority for users, groups, devices and applications from on-premises domain...
HR-driven provisioning makes the HR system the source of truth for identity: a hire in the HR platform creates the account, a change of role updates...
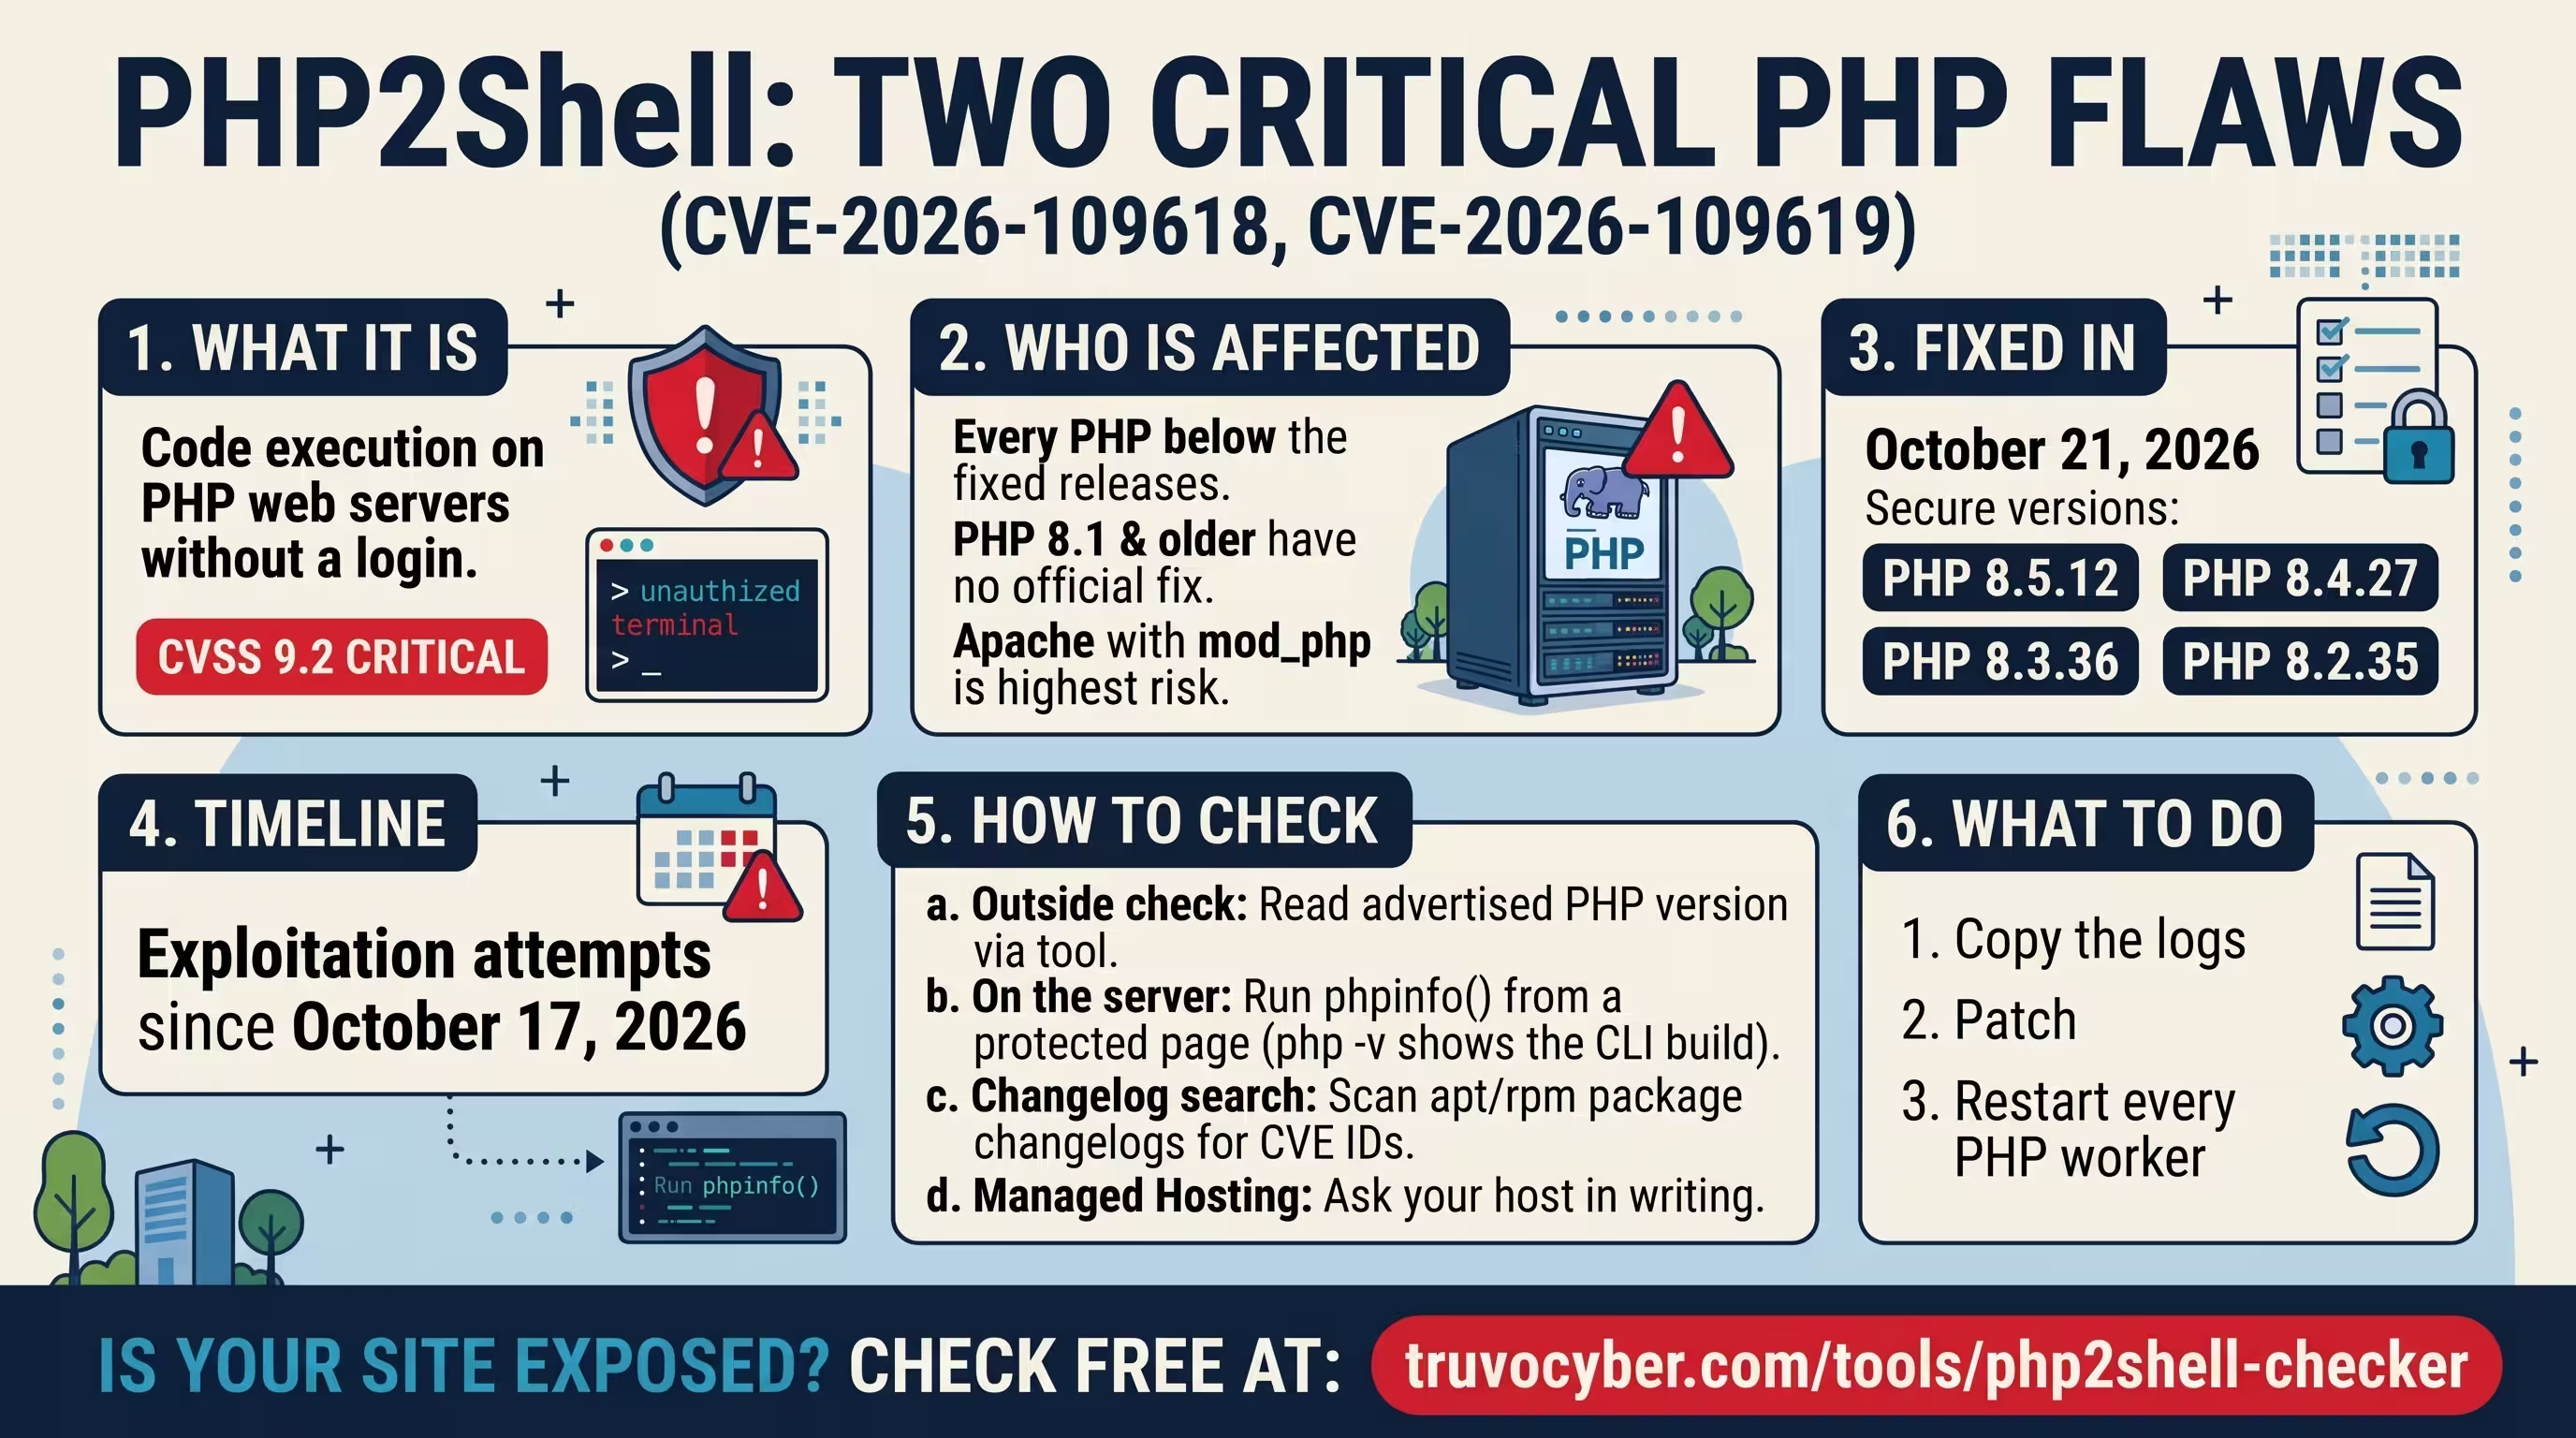
The fastest way to check a site for PHP2Shell is to run the free PHP2Shell checker, which reads the PHP version the site advertises and compares it...
On October 21, 2026, Railway disclosed that an unauthorized third party may have accessed the encrypted environment variables of its customers and,...
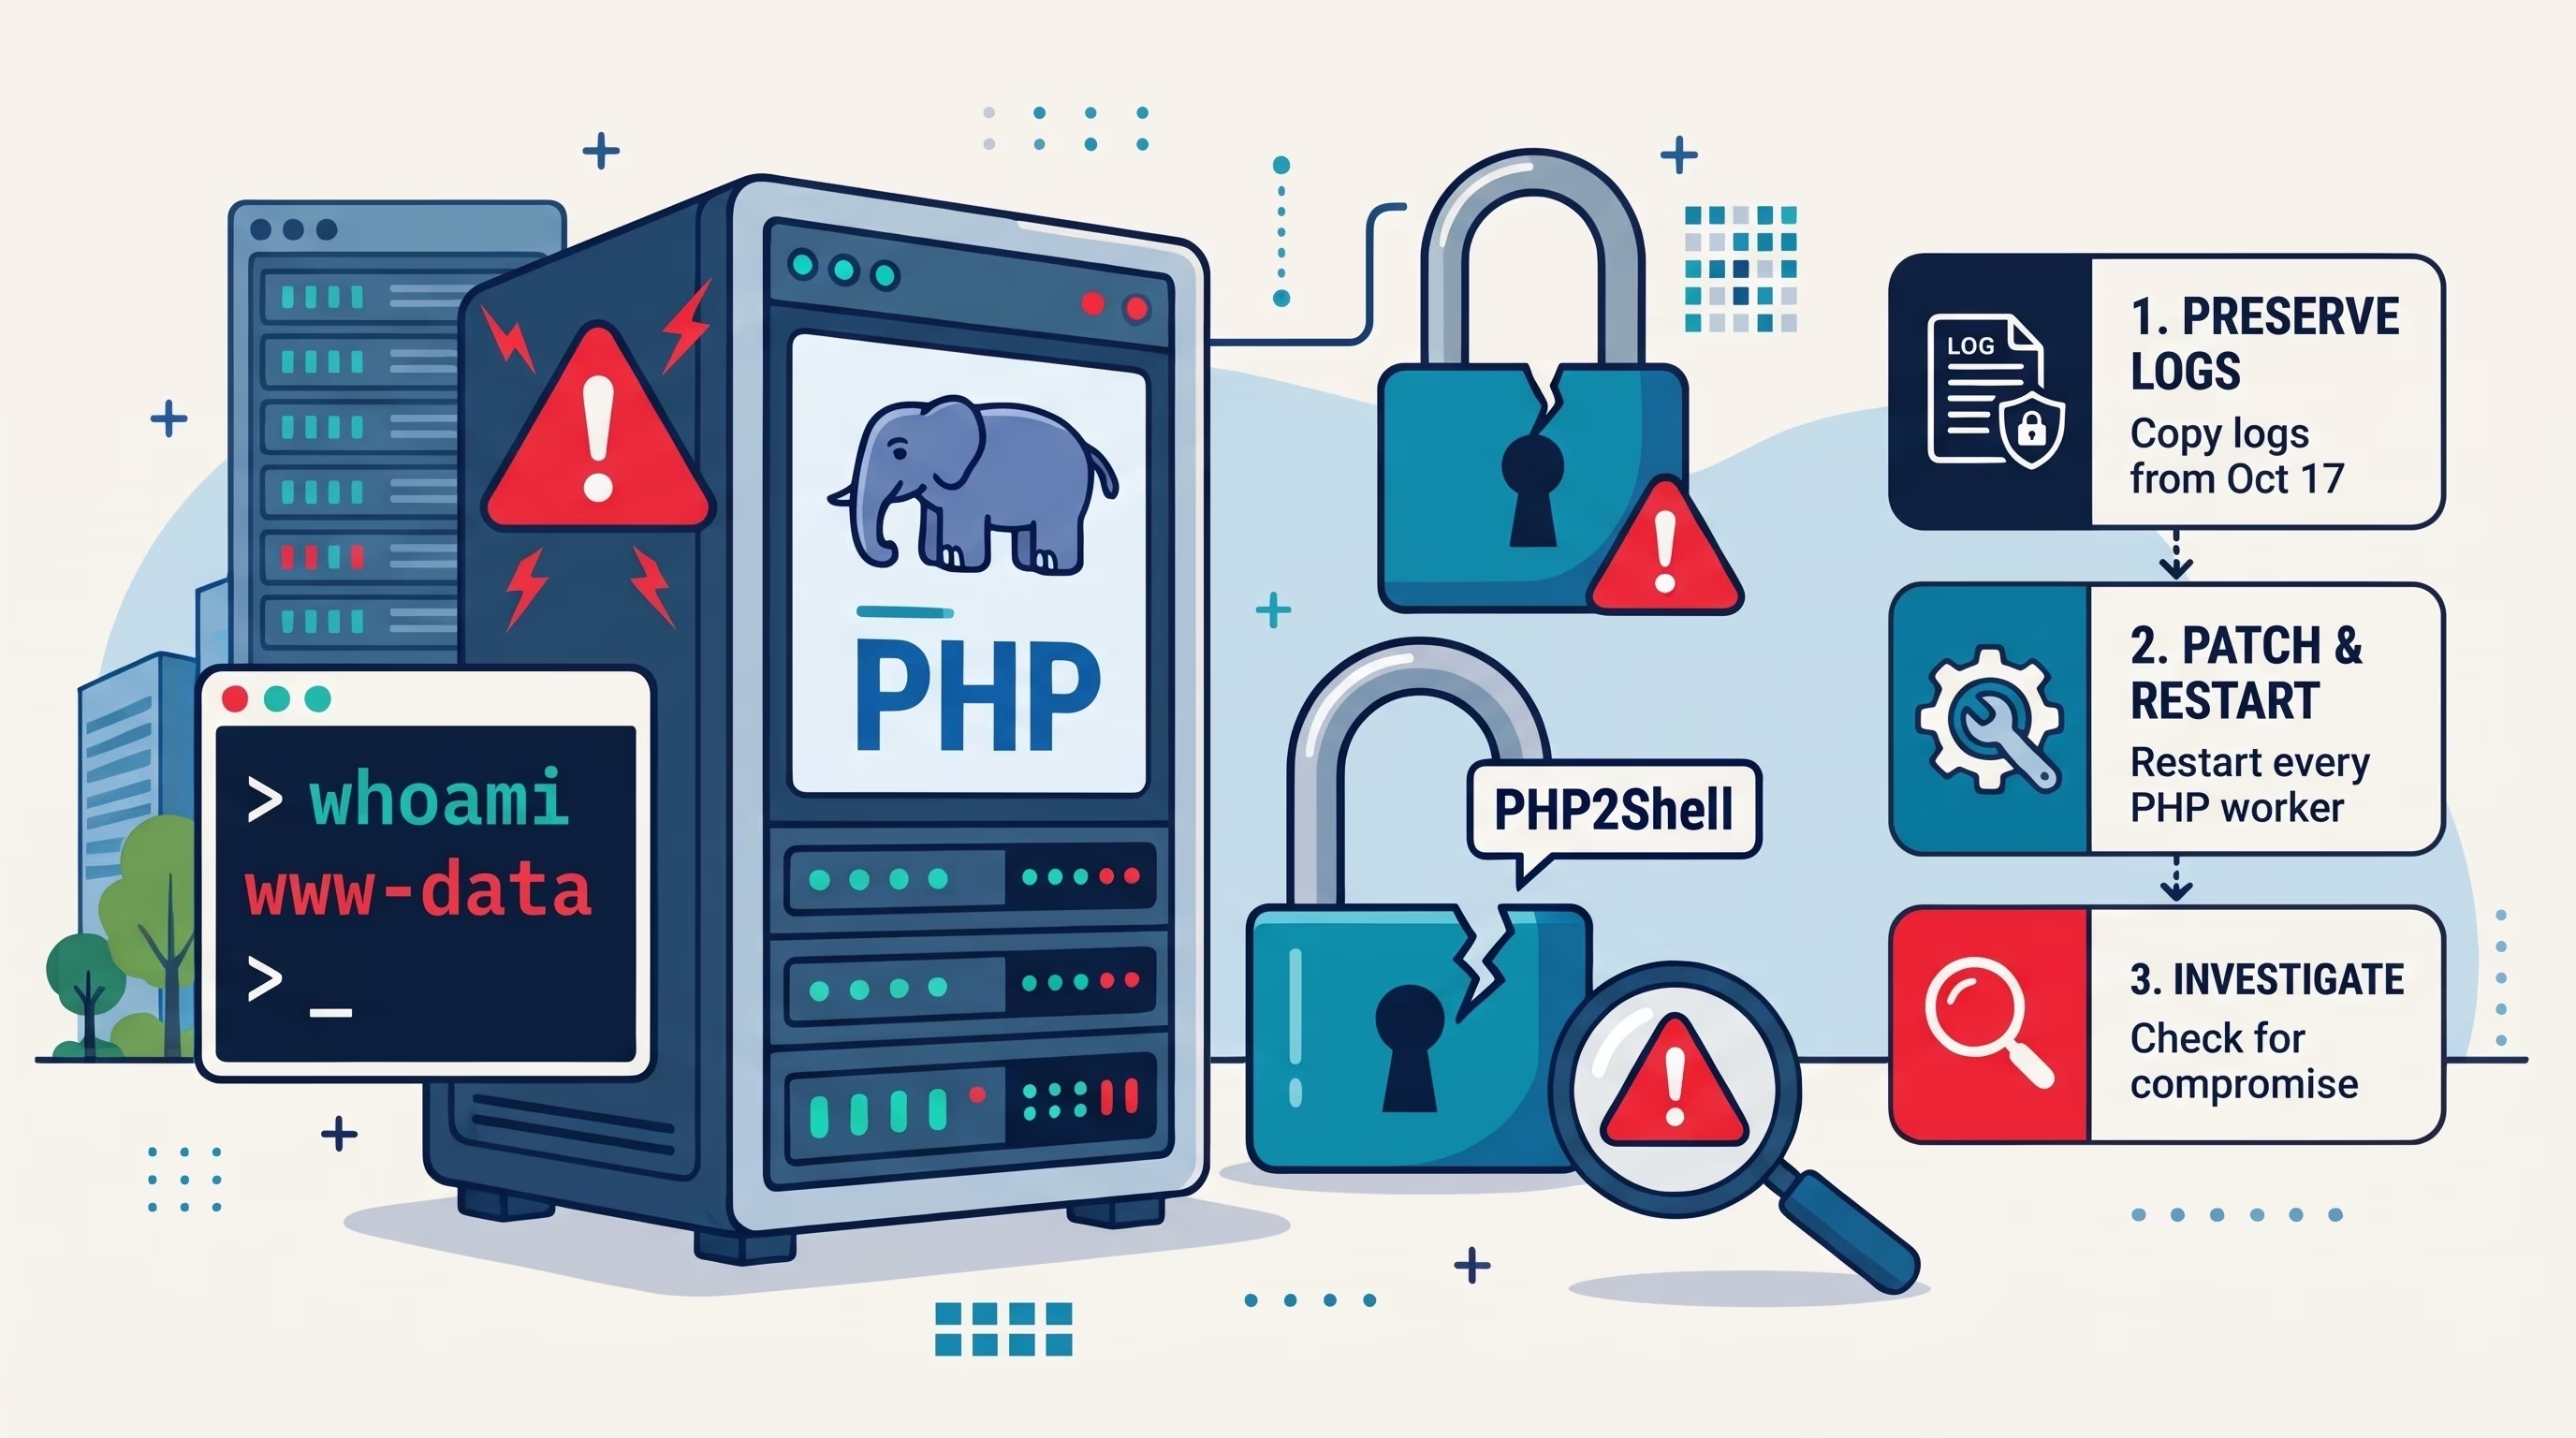
PHP2Shell is two critical flaws in the PHP engine, CVE-2026-109618 and CVE-2026-109619, that allow remote code execution without a login on PHP web...
Agentic AI security architecture starts with a map of the components of an AI agent system and the connections between them, which sets the scope,...
Datadog can supply SOC 2 evidence for vulnerability identification (CC7.1), security monitoring (CC7.2), alert evaluation (CC7.3), unauthorized or...
Hybrid cloud security monitoring applies the same detection, vulnerability scanning, and configuration checks to on-premises servers as to cloud...
Yes. Datadog Cloud SIEM is Datadog's security information and event management (SIEM) product. It applies threat detection rules to the logs already...