

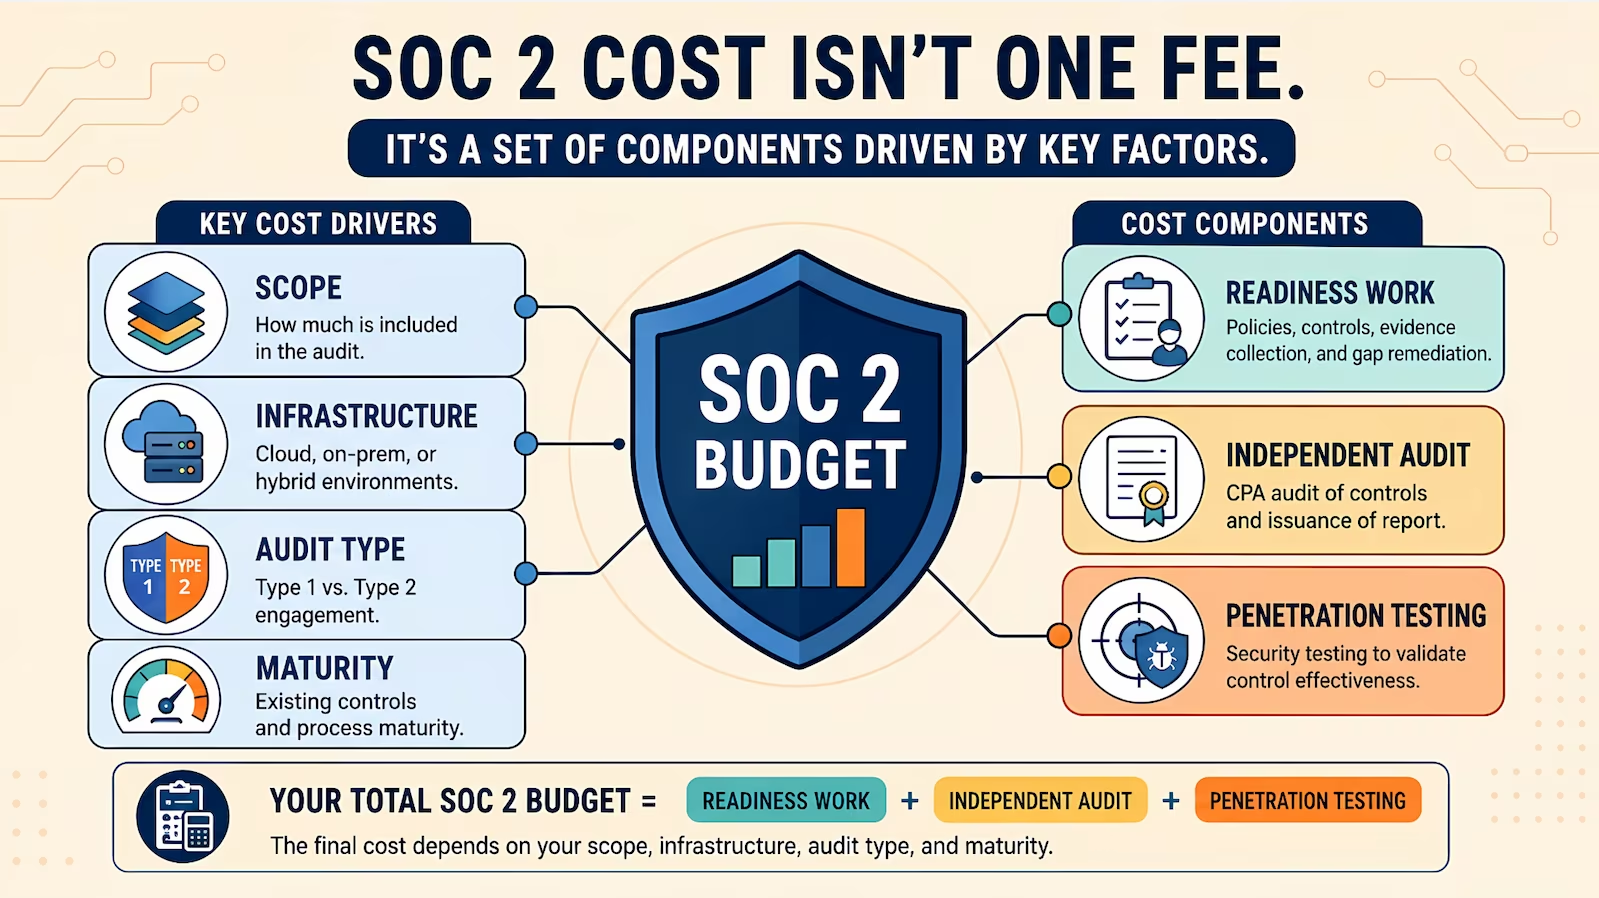
A SOC 2 audit fee alone costs roughly $7,500 to $100,000 or more in 2026, depending on report type, company size and the audit firm, with published medians near $30,000. The total first-year cost is the audit fee plus readiness work, a penetration test, tooling and internal staff time, and each of those is billed by a different party. Every price below links to the auditor, tester or standards body that published it.
Last updated: October 5, 2026. Third-party figures are in US dollars. Truvo Cyber figures are rounded US-dollar ranges for SMBs of up to 100 people, based on 2025 and 2026 engagements.
At a glance
SOC 2 cost in 2026
- SOC 2 Type 1 audit fee: $7,500 to $50,000 (published auditor ranges)
- SOC 2 Type 2 audit fee: $10,000 to $100,000+, Big Four firms from the low six figures
- Penetration test: $10,000 to $35,000 on average
- Readiness assessment and implementation help for SMBs: $6,500 to $44,000, depending on scope (Truvo Cyber)
- The CPA firm that audits you cannot also build your program, so readiness and audit are two separate invoices
SOC 2 audit fees in 2026: the published numbers
SOC 2 audit fees are the most published SOC 2 cost, and the numbers come from audit firms and directories, not independent surveys. No large survey reports SOC 2 audit cost: A-LIGN's 2025 Compliance Benchmark Report surveyed more than 1,000 organizations and publishes audit counts, not fees. Read the figures below as auditor-published ranges.
- SOC 1 and SOC 2 audits typically cost $20,000 to $150,000, with a median price around $30,000 (Linford & Co, 2026).
- Big Four SOC audits start in the low six figures and can reach the millions (Linford & Co, 2026).
- A SOC 2 Type 1 audit costs $7,500 to $15,000 for small and mid-sized organizations and $10,000 to $50,000 for larger ones (Mallette, 2026).
- A SOC 2 Type 2 audit costs $10,000 to $20,000 for small and mid-sized organizations and $25,000 to $100,000 or more for larger ones (Mallette, 2026).
- Across 192 listed audit firms, typical SOC 2 Type 2 fees are $15,500 to $50,000 at specialist firms, $30,000 to $80,000 at full-service CPA firms and $65,000 to $200,000 at Big Four firms (SOC2Auditors.org directory estimate, September 2026).
- On the same directory data, typical SOC 2 Type 1 fees are $10,000 to $35,000 at specialist firms, $20,000 to $60,000 at full-service CPA firms and $40,000 to $145,000 at Big Four firms (SOC2Auditors.org, September 2026).
- A Type 2 audit requires the most auditor time and the most client effort, which makes it more expensive than a Type 1 or a readiness assessment (Schellman).
The spread between firm tiers is wider than the spread between report types. A Type 2 at a specialist firm can cost less than a Type 1 at a Big Four firm, so the choice of auditor moves the number more than any other single decision.
SOC 2 cost by driver: what moves the price
SOC 2 cost is set by six drivers: report type, scope, auditor tier, readiness help, tooling and internal time. Each driver below is its own budget line.
SOC 2 Type 1 vs Type 2 cost
A SOC 2 Type 1 report tests whether controls are designed correctly at one point in time; a SOC 2 Type 2 report tests whether they operated over a period, so it costs more.
- A SOC 2 Type 2 report generally covers 6, 9 or 12 months, and 12-month reports are the most common (Linford & Co, 2024).
- SOC 2 reports dated on or after June 15, 2022 are issued under the AICPA attestation standard SSAE 21 (AICPA, 2022).
Enterprise buyers usually ask for Type 2. A Type 1 is useful when a deal needs a report within weeks; it then becomes a second audit fee on the way to Type 2. The trade-off is covered in why some teams start with a SOC 2 Type 1.
SOC 2 scope: which Trust Services Criteria are in the report
SOC 2 scope, meaning the Trust Services Criteria categories and the systems in the report, drives both audit fees and readiness effort.
- SOC 2 reports are built on the AICPA's 2017 Trust Services Criteria (revised points of focus, 2022), which define five categories: Security, Availability, Processing Integrity, Confidentiality and Privacy (AICPA & CIMA, 2022).
- The system description in every SOC 2 report follows the AICPA's 2018 Description Criteria, revised 2022 (AICPA & CIMA, 2022).
Security is required in every SOC 2 report; the other four categories are optional. Each added category means more controls for the auditor to test and more evidence to produce. On-premises and hybrid infrastructure also cost more than cloud-native stacks, because physical controls come into scope and evidence is collected by hand.
SOC 2 auditor tier: specialist firm vs CPA firm vs Big Four
The audit firm tier is the largest swing factor in the SOC 2 audit fee. Specialist SOC firms charge least, full-service CPA firms charge more, and Big Four firms start in six figures (Linford & Co and SOC2Auditors.org, 2026).
- In Truvo Cyber engagements in 2025 and 2026, boutique CPA firms working alongside a GRC platform quoted a combined SOC 2 Type 1 and Type 2 for SMBs of up to 100 people at about $6,500 to $12,500; mid-sized firms quoted a Type 2 alone at $12,500 to $37,500, and a large national firm quoted about $62,500 for a two-framework engagement.
- The AICPA's Journal of Accountancy warned in February 2026 that the volume of SOC reports being signed, often within days or weeks, may raise regulatory risks for the firms issuing them (Journal of Accountancy, 2026).
The cheapest SOC 2 audit fee can turn into the most expensive report if an enterprise security team rejects the auditor. Ask buyers which audit firms their vendor-risk team accepts before you sign an engagement letter.
SOC 2 readiness and implementation help
SOC 2 readiness help is a separate invoice from the audit, because an audit firm cannot audit controls it designed for you.
- A SOC 2 readiness assessment typically costs $15,000 to $25,000 (Compass IT Compliance, 2024).
- In Truvo Cyber engagements in 2025 and 2026, a SOC 2 readiness assessment for a cloud-based SMB of up to 100 people was priced at $6,500 to $12,500, and $25,000 to $44,000 for multi-site or on-premises scopes.
- In the same engagements, SOC 2 implementation (policies, controls and platform setup to audit-ready) was priced at $19,000 to $44,000 as a fixed fee for SMBs of up to 100 people, most often $25,000 to $31,000.
- Ongoing managed SOC 2 compliance in Truvo Cyber engagements is typically $2,000 to $5,000 a month for SMBs of up to 100 people: $3,000 to $5,000 a month during the build, then $2,000 to $3,000 a month once the program is in operation.
SOC 2 penetration testing cost
A penetration test is a separate SOC 2 line item. Auditors look for evidence of one, but they do not perform it.
- The average penetration test costs $10,000 to $35,000 in 2026, and SaaS and web application tests cost $5,000 to $30,000, based on roughly 900 quotes issued in 2025 (Blaze Information Security, 2026).
- Published list prices start at $10,800 for a web and API penetration test, $5,400 for an external network test and $7,700 for an internal network test (Software Secured pricing page, accessed October 2026).
- In Truvo Cyber engagements in 2025 and 2026, a compliance-driven penetration test of a single application for an SMB was priced at about $6,500, and a full-scope application test at $19,000 to $31,000.
SOC 2 tooling and internal staff time
SOC 2 tooling (a GRC platform) and internal staff time are real costs that rarely show up in a quote. GRC platform subscriptions usually scale with headcount and the number of frameworks. Staff time also adds up: audit fees are only part of SOC 2 spend, and remediation, pen testing, tooling and dozens to hundreds of hours of staff time come on top (Mallette, 2026).
- In Truvo Cyber engagements, the GRC platform is quoted at partner rates as a separate line, and the platform price varies with the platform, headcount and number of frameworks.
Total first-year SOC 2 cost: add the invoices
The total first-year SOC 2 cost is the sum of the separate invoices, and no primary source publishes a single all-in figure. Using the sourced ranges above, a first Type 2 for an SMB of up to 100 people is built like this:
| SOC 2 first-year cost line | Typical range | Source |
| SOC 2 readiness assessment | $15,000 to $25,000 | Compass IT Compliance, 2024 |
| SOC 2 implementation help (SMB, up to 100 people) | $19,000 to $44,000 | Truvo Cyber engagements, 2025-2026 |
| SOC 2 Type 2 audit fee (specialist or mid-tier firm) | $10,000 to $50,000 | Mallette 2026; SOC2Auditors.org 2026 |
| Penetration test | $10,000 to $35,000 | Blaze Information Security, 2026 |
| GRC platform subscription | Varies by platform and headcount | Quoted at partner rates |
| Internal staff time | Dozens to hundreds of hours | Mallette, 2026 |
- In Truvo Cyber engagements in 2025 and 2026, year-one Truvo fees for an SMB of up to 100 people (assessment, build and operation) were $38,000 to $69,000, and the all-in first year including the audit, the platform and a penetration test was about $50,000 to $75,000.
Key insight
The SOC 2 quote is three or four invoices, not one
A single SOC 2 price usually hides the readiness work, the CPA audit fee, the penetration test and the platform subscription. They come from different parties, and they arrive at different times.
The year-two cost is lower because readiness work is mostly done, but the Type 2 audit, the pen test and the platform renew every year. SOC 2 is an annual budget line, not a one-time project.
How to lower SOC 2 cost without weakening the report
SOC 2 cost drops most when scope, timing and auditor choice are set before any work starts.
- Scope to what buyers ask for. Start with Security only unless a customer contract names another category.
- Pick the auditor early. Confirm the firm is accepted by the buyers holding up your deals, then compare fees within that list.
- Start before a deal forces it. Compressed timelines cost more, because readiness and remediation run in parallel at premium rates.
- Plan the SOC 2 and ISO 27001 overlap once. The two frameworks share much of their control set; the SOC 2 vs ISO 27001 comparison shows how to sequence them and reuse controls.
- Reuse the report in sales. A current SOC 2 report answers a large share of the security questionnaires that otherwise stall enterprise deals.
The SOC 2 compliance hub collects the rest of the SOC 2 series, from the Trust Services Criteria to the audit itself.
Get a SOC 2 Number for Your Scope
We price readiness, build and operation as one effective security program, scoped to the report your buyers need.
How to cite this page
Truvo Cyber. (2026, October 5). SOC 2 Cost 2026: Real Price Ranges by Line Item. https://truvocyber.com/blog/soc-2-cost-4-factors
Frequently Asked Questions
How much does a SOC 2 Type 2 audit cost in 2026?
A SOC 2 Type 2 audit fee is $10,000 to $20,000 for small and mid-sized organizations and $25,000 to $100,000 or more for larger ones, according to Mallette (2026). Directory data across 192 firms puts specialist firms at $15,500 to $50,000 and Big Four firms at $65,000 to $200,000 (SOC2Auditors.org, 2026).
How much does a SOC 2 Type 1 audit cost?
A SOC 2 Type 1 audit fee is $7,500 to $15,000 for small and mid-sized organizations and $10,000 to $50,000 for larger ones (Mallette, 2026). A Type 1 costs less than a Type 2 because the auditor tests control design at one point in time.
What is the total first-year cost of SOC 2?
The total first-year SOC 2 cost is the audit fee plus readiness help, a penetration test, a GRC platform and internal staff time. No primary source publishes one all-in number; adding the sourced ranges gives the realistic budget for a given company size and scope.
Does SOC 2 require a penetration test, and what does it cost?
The AICPA Trust Services Criteria list penetration testing as one type of separate evaluation under CC4.1 without making it mandatory, and auditors and enterprise buyers commonly expect one. An average penetration test costs $10,000 to $35,000 in 2026 (Blaze Information Security, 2026).
How long is the SOC 2 Type 2 observation period?
A SOC 2 Type 2 report generally covers 6, 9 or 12 months, and 12-month reports are the most common (Linford & Co, 2024). The AICPA does not publish a fixed minimum; shorter first-year periods are agreed with the auditor.
Truvo Cyber scopes SOC 2 readiness, implementation and ongoing operation as a fractional security team working alongside the GRC platform and the audit firm. The SOC 2 compliance service page sets out what that covers.
Ready to Start Your Compliance Journey?
Get a clear, actionable roadmap with our readiness assessment.
Contact Us
Sample SOC 2 Control List
Input your email to download the list
About the Author

Former security architect for Bank of Canada and Payments Canada. 20+ years building compliance programs for critical infrastructure.