

Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

Posts tagged On-Prem

17 posts

Five Things That Slow Down On-Prem SOC 2 Audit Preparation, and How to Start Now

SOC 2 audit preparation on on-prem infrastructure slows down in five places: infrastructure scanning and logging, application and container scanning, ...
From below of long thin blue cables connected to row of small white connectors on system block in data center, illustrating Vanta and Drata for On-Prem SOC 2: What the Platform Automates and Who Collects the Rest

Vanta and Drata for On-Prem SOC 2: What the Platform Automates and Who Collects the Rest

Vanta and Drata work for an on-prem SOC 2 program, and they automate the corporate half of it: identity, HR records, code review, endpoints,...
Laptop with a spreadsheet open, representing the ISO 27001 to SOC 2 control mapping sheet

On-Prem SOC 2 Cost and Timeline: What Changes When You Run Your Own Hardware

On-prem SOC 2 costs more than a cloud SOC 2 mainly in readiness: in Truvo Cyber engagements, a readiness assessment for a cloud SMB of up to 100...
Steel framework cabinets housing servers networking devices and cables in contemporary equipped data center, illustrating SOC 2 Readiness Checklist for On-Prem and Hybrid Infrastructure

SOC 2 Readiness Checklist for On-Prem and Hybrid Infrastructure

A SOC 2 readiness checklist lists the work a company needs to finish before its audit starts: scope the system, write the policies, and build the...
Detailed view of network cables plugged into a server rack in a data center, illustrating Datadog for SOC 2 Vulnerability Scanning: Datadog vs Wazuh vs Nessus On-Prem

Datadog for SOC 2 Vulnerability Scanning: Datadog vs Wazuh vs Nessus On-Prem

A bare-metal SaaS company already paying for Datadog asked us before its first SOC 2 audit: Can Datadog be our vulnerability scanner of record, or do...
Stock photo by Mahmoud Zakariya via Pexels, illustrating hybrid cloud network (temporary placeholder pending custom hero design).

SOC 2 for Hybrid and On-Prem Infrastructure: Scoping and the System Description

A service that runs partly in a public cloud and partly on company-owned hardware is one system for SOC 2 whenever customer data or commands cross...
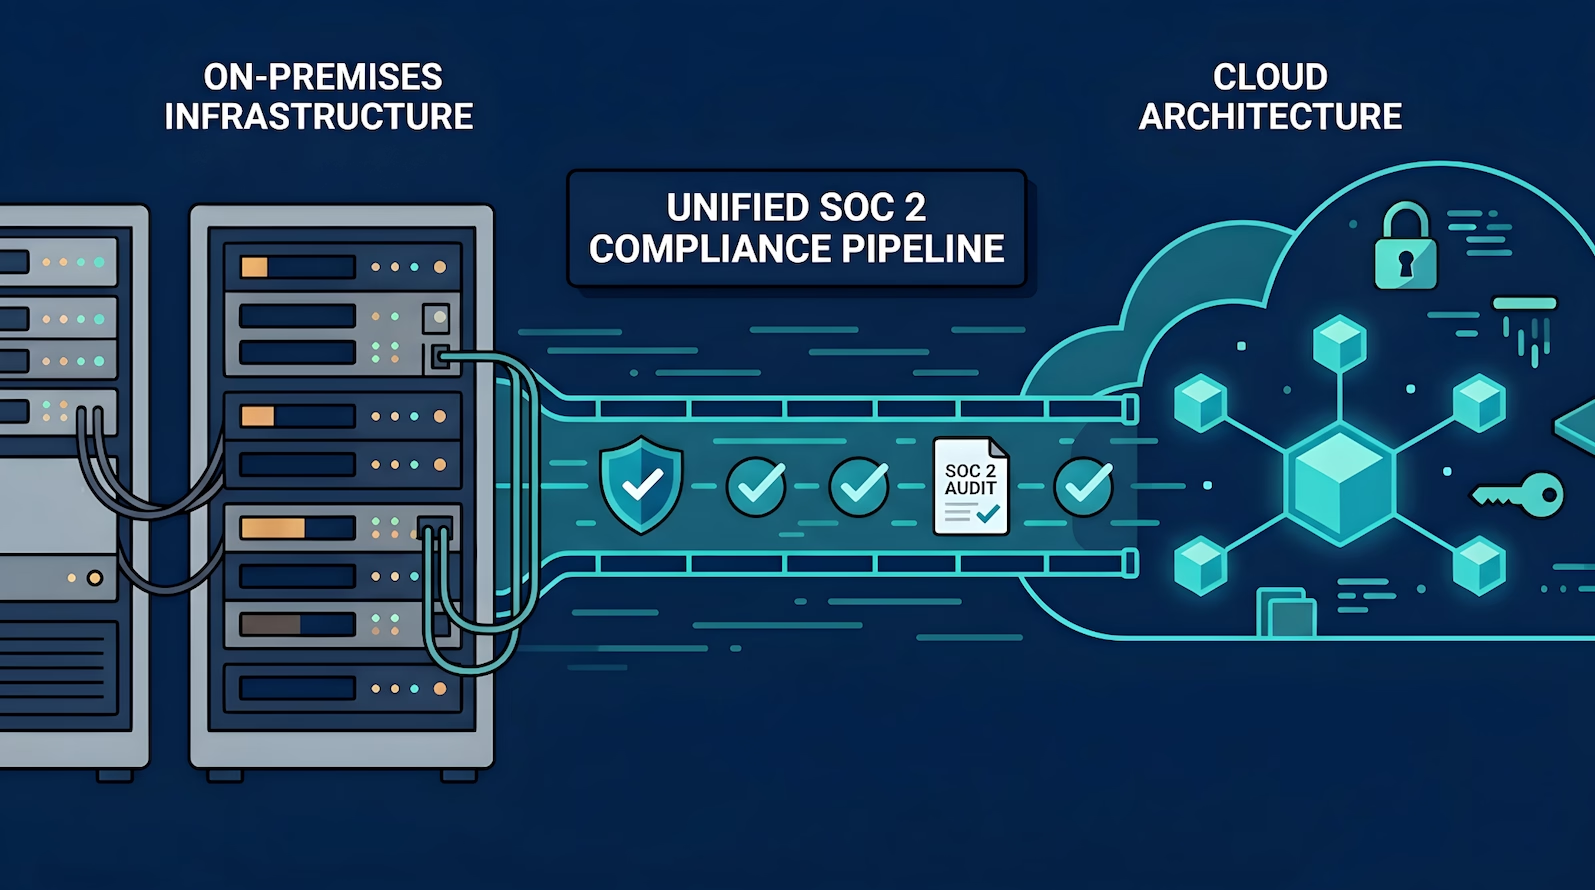
A diagram titled "Unified SOC 2 Compliance Pipeline" shows a blue arrow flowing from a two-cabinet "ON-PREMISES INFRASTRUCTURE" server to a "CLOUD ARCHITECTURE" cloud icon containing a teal cube network, a padlock, and a key. Within the arrow, a "SOC 2 AUDIT" icon is flanked by three shield checkmarks.

GRC Compliance for On-Prem and Hybrid Environments

GRC platforms automate compliance evidence collection for cloud-native infrastructure. Connect your AWS account, hook in your identity provider, link...
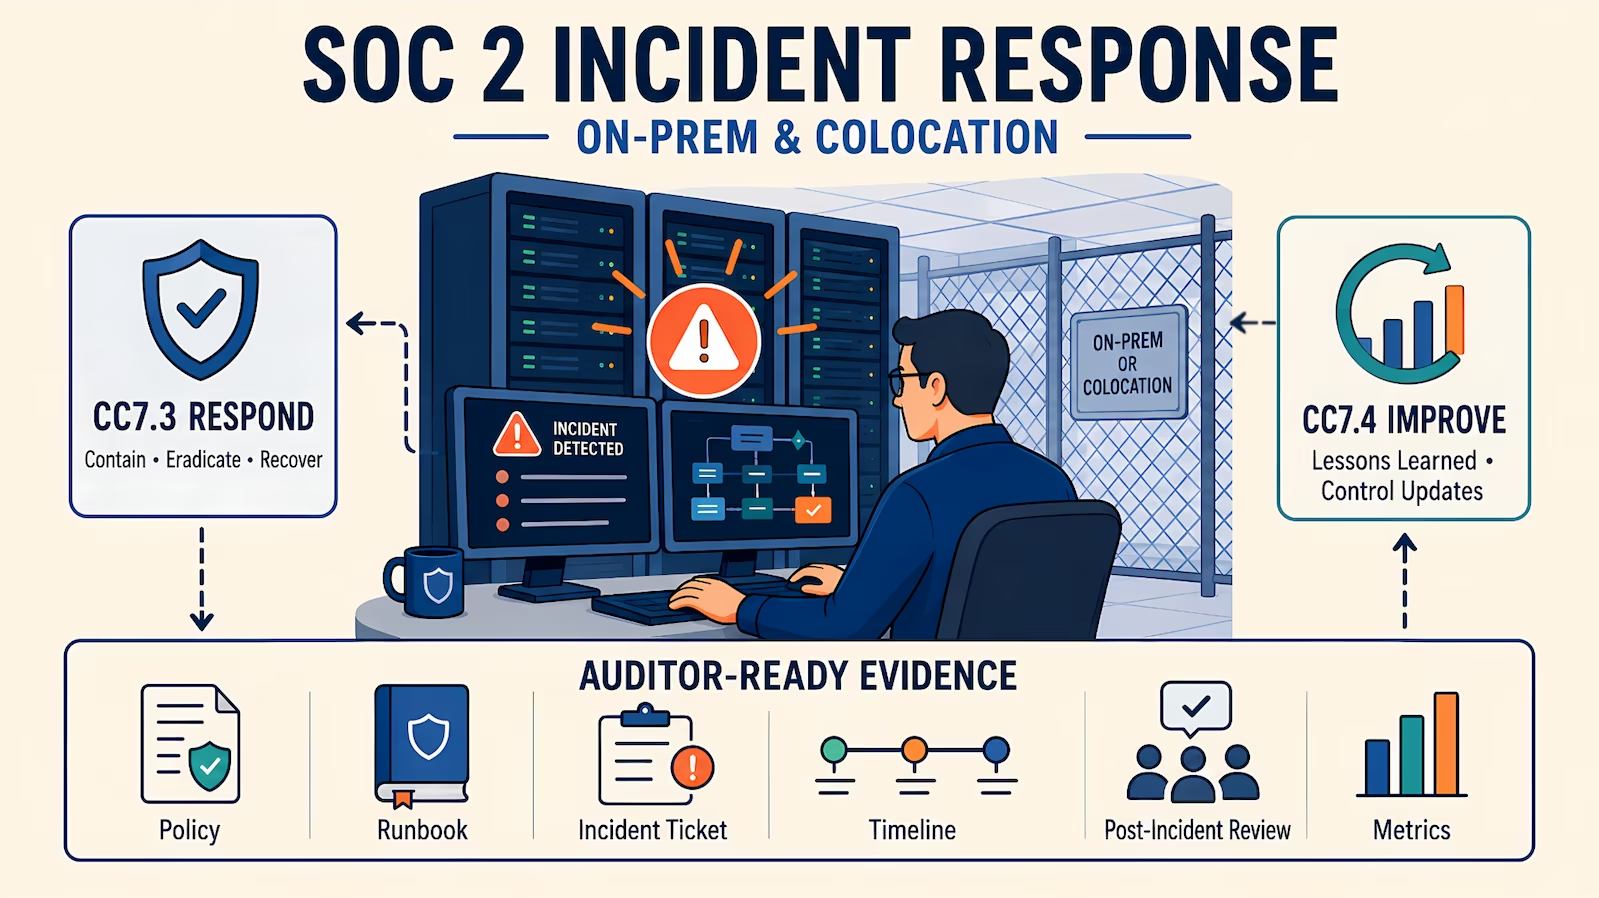
SOC 2 Incident Response for On-Premise Environments — Truvo blog hero

SOC 2 Incident Response for On-Premise Environments

TL;DR

  • IR maps to CC7.3 (security event evaluation, the triage discipline) and CC7.4 (defined response program with containment, mitigation,...
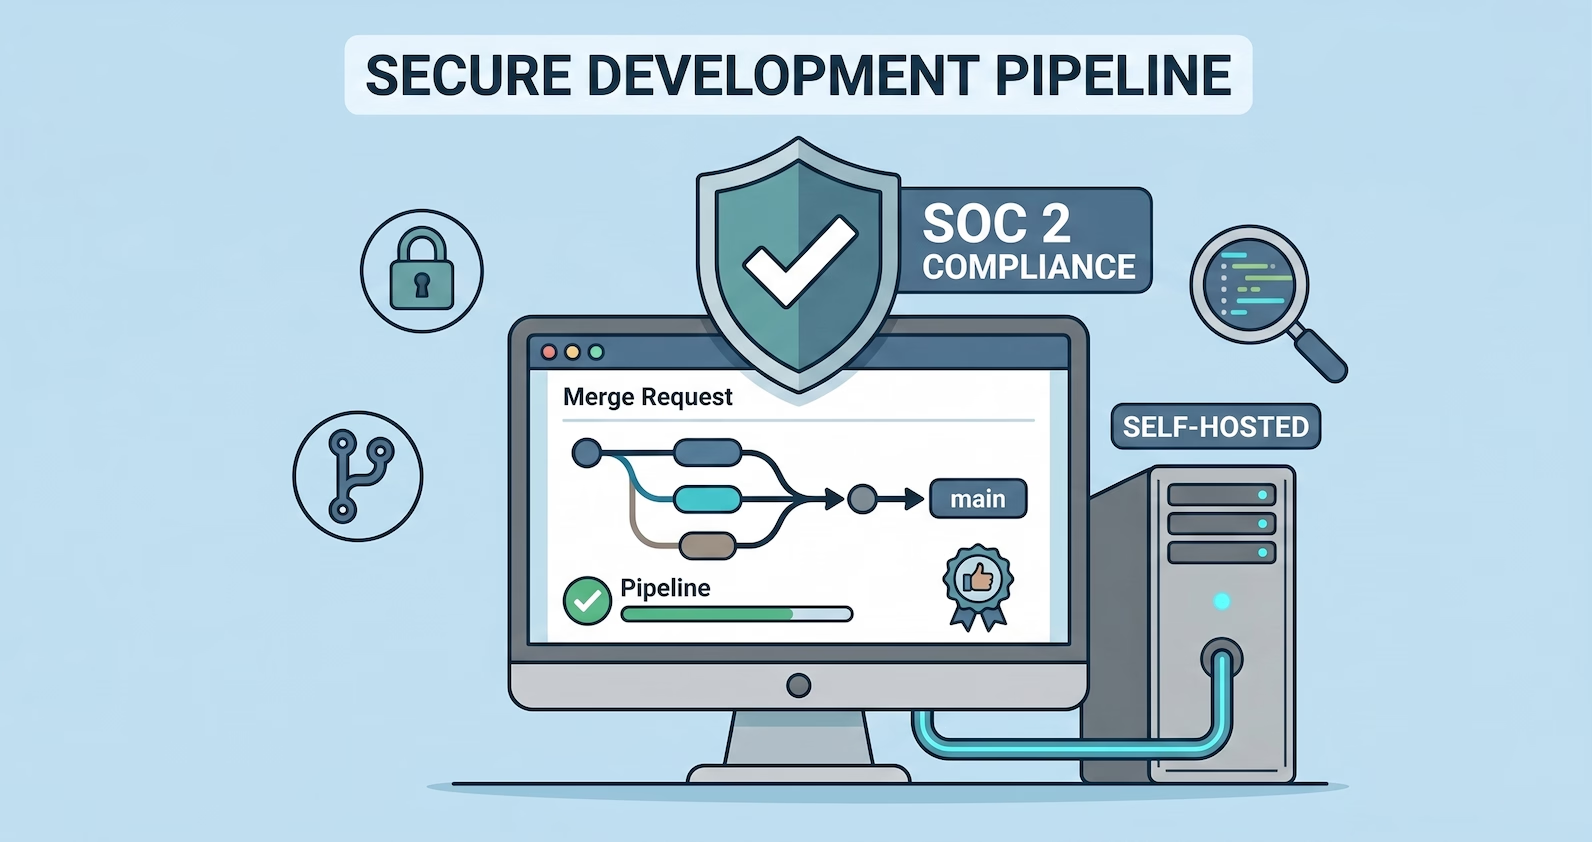
A flat 2D cartoon illustration on a powder blue background, featuring a computer monitor displaying a merge request, branch flow diagram, and a green pipeline status. A server tower is connected to the monitor, and a large shield labeled SOC 2 COMPLIANCE floats above. Icons like a lock and branch symbol orbit the scene.

SOC 2 Secure Development with Self-Hosted GitLab

TL;DR

  • The same Trust Services Criterion that governs infrastructure changes governs code changes: CC8.1, change management
  • Self-hosted GitLab is the...
Alt text: A man with glasses in a suit holds a checklist in front of a large, open server rack with colorful cables and LED lights. A large shield with a checkmark is behind him. Other staff and servers are visible in the background against a light blue, vector illustration backdrop.

SOC 2 Consultants for On-Prem and Hybrid Infrastructure

Most SOC 2 consultants know AWS. Some know Azure and GCP. Very few know what to do when your stack includes a colocation facility, a bare-metal fleet...
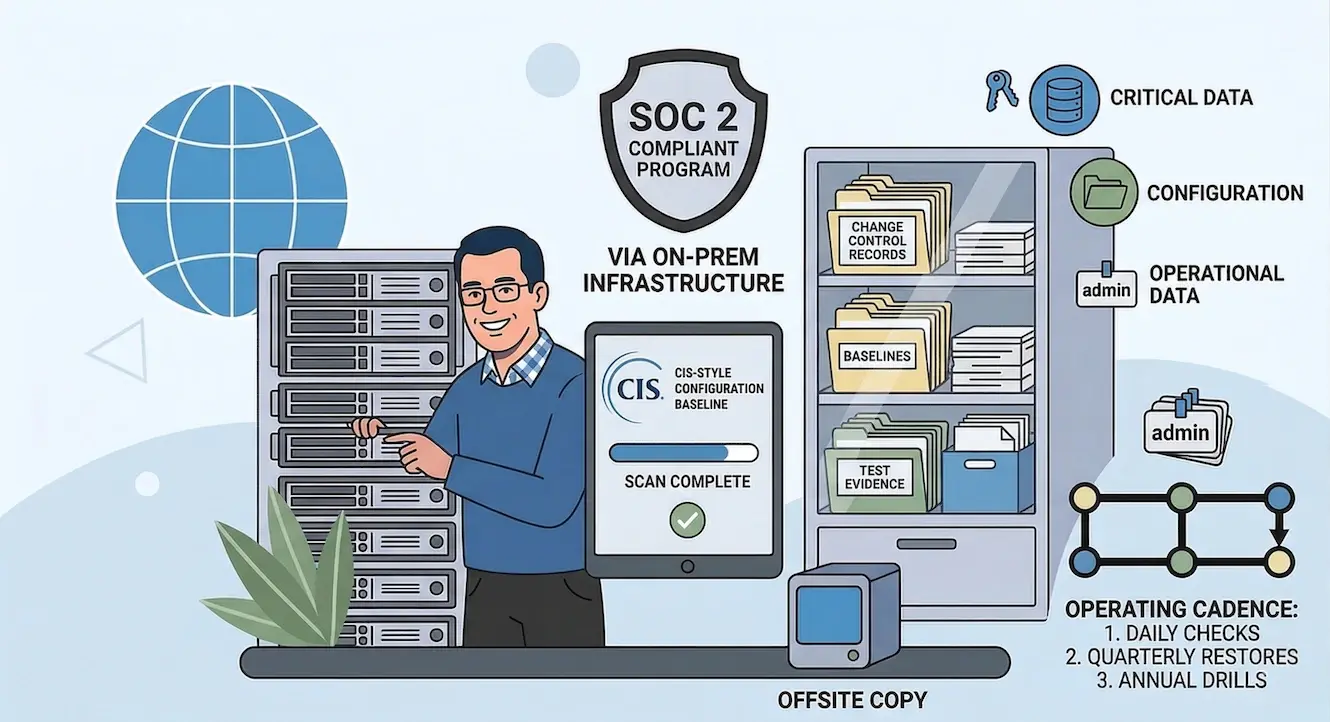
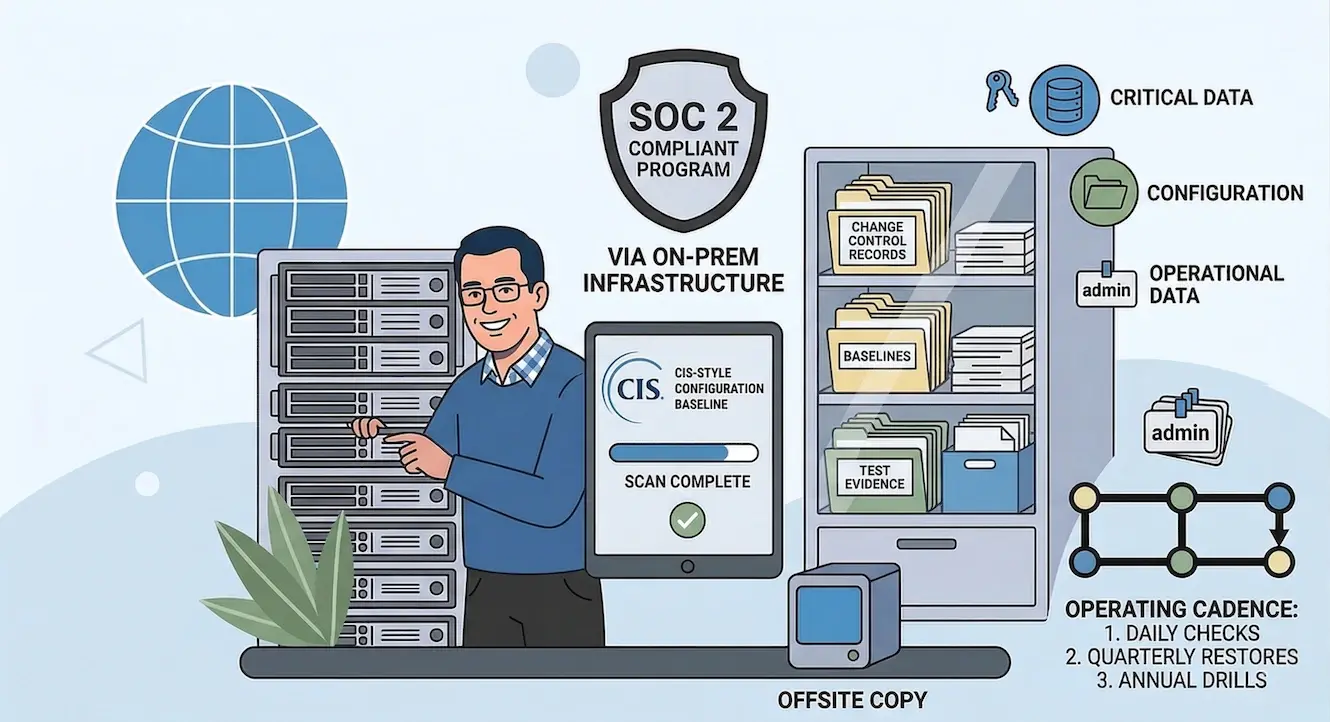
Illustration showing a SOC 2 compliant program via on-prem infrastructure. A man stands by a server rack and a tablet showing a completed CIS configuration scan. To the right, a filing cabinet stores baselines and test evidence. An "Operating Cadence" list details daily, quarterly, and annual tasks.

SOC 2 Configuration Baselines for Bare Metal: CIS Benchmarks & Beyond

In cloud environments, configuration compliance is a toggle. Enable AWS Config, deploy a conformance pack, and the platform continuously evaluates...
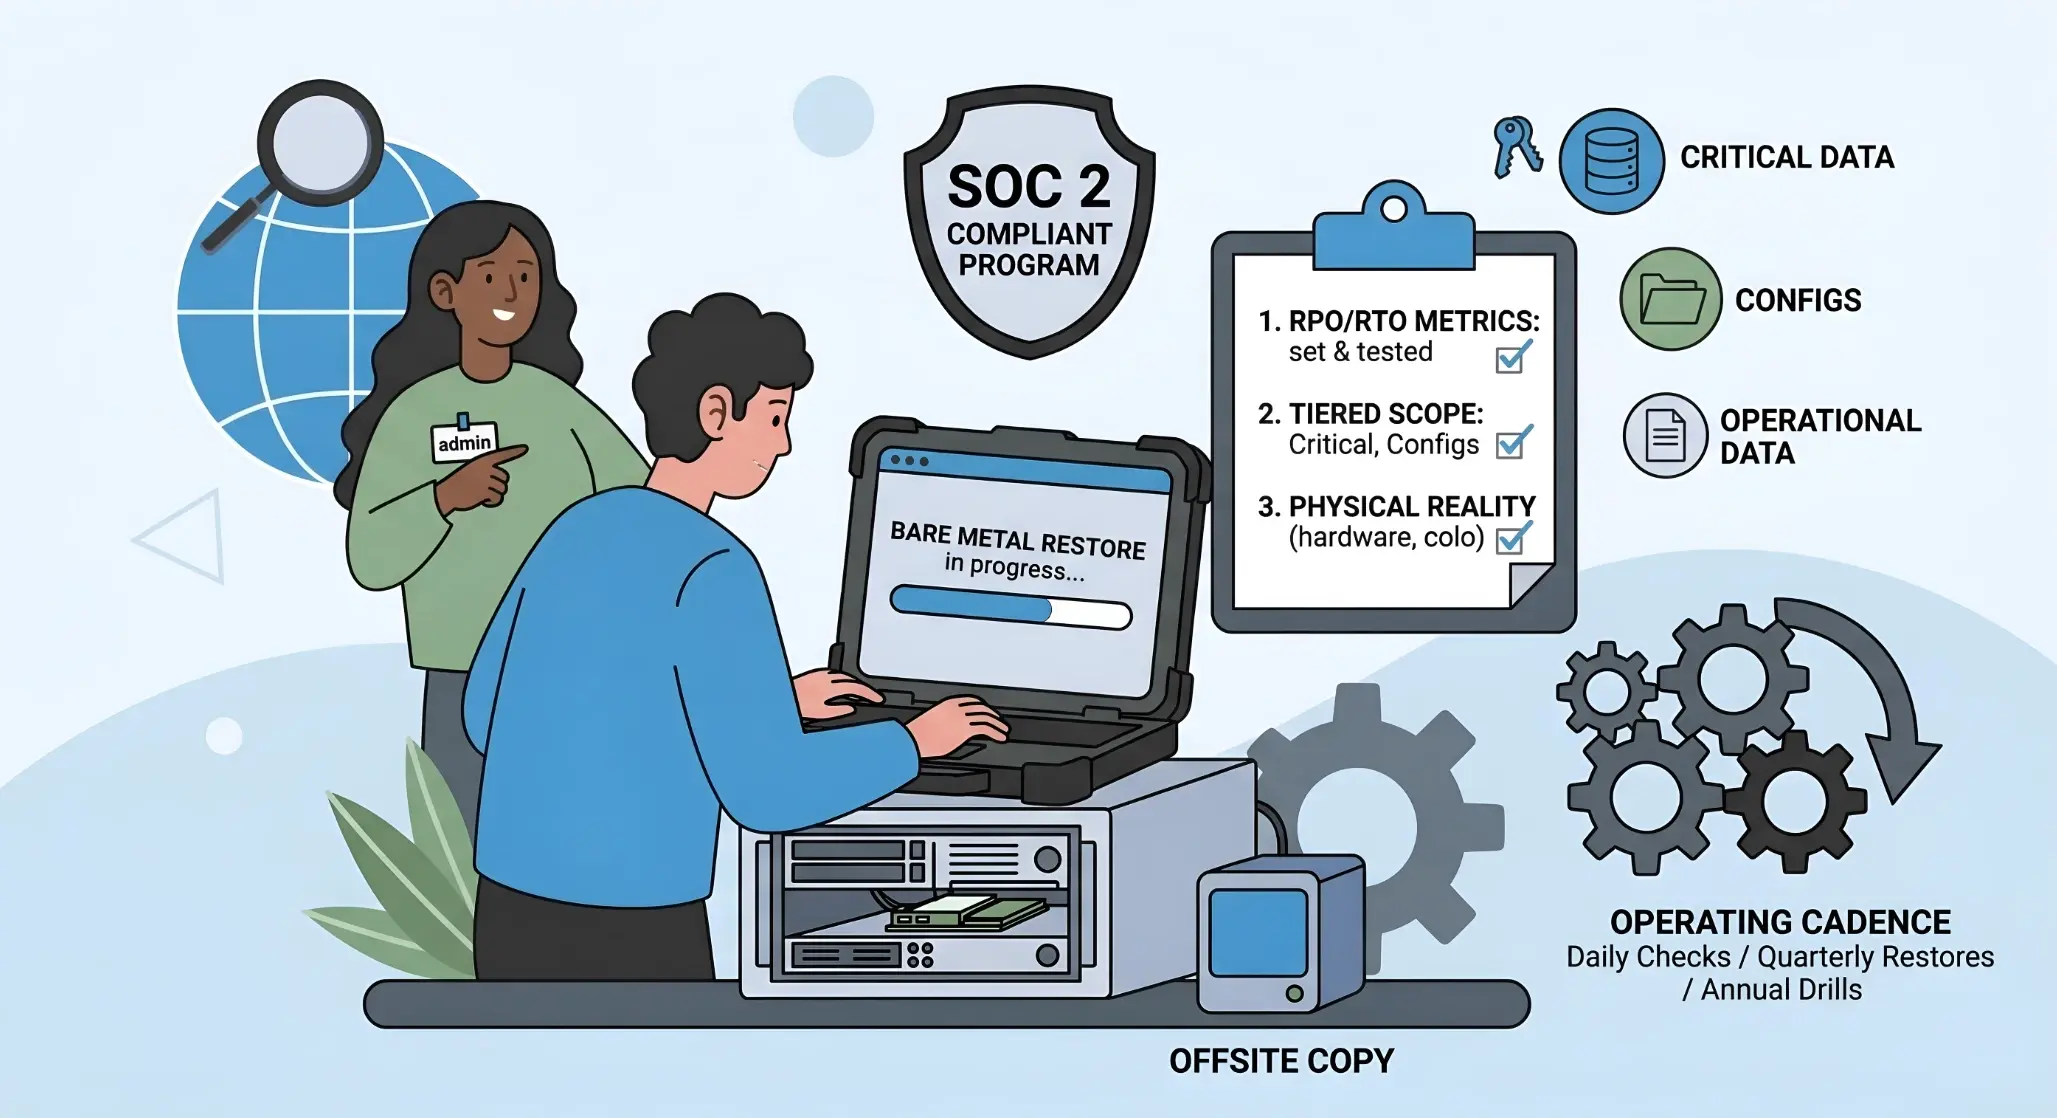
Infographic for SOC 2 Backup and Disaster Recovery. An admin watches a tech perform a "Bare Metal Restore." A checklist highlights RPO/RTO metrics, tiered scope (Critical Data, Configs, Operational Data), and physical hardware. Icons show offsite copies and an operating cadence for drills.

SOC 2 Backup and Disaster Recovery for On-Premise Infrastructure

Cloud disaster recovery is a region failover. Click a button, spin up infrastructure in another availability zone, and the platform handles...
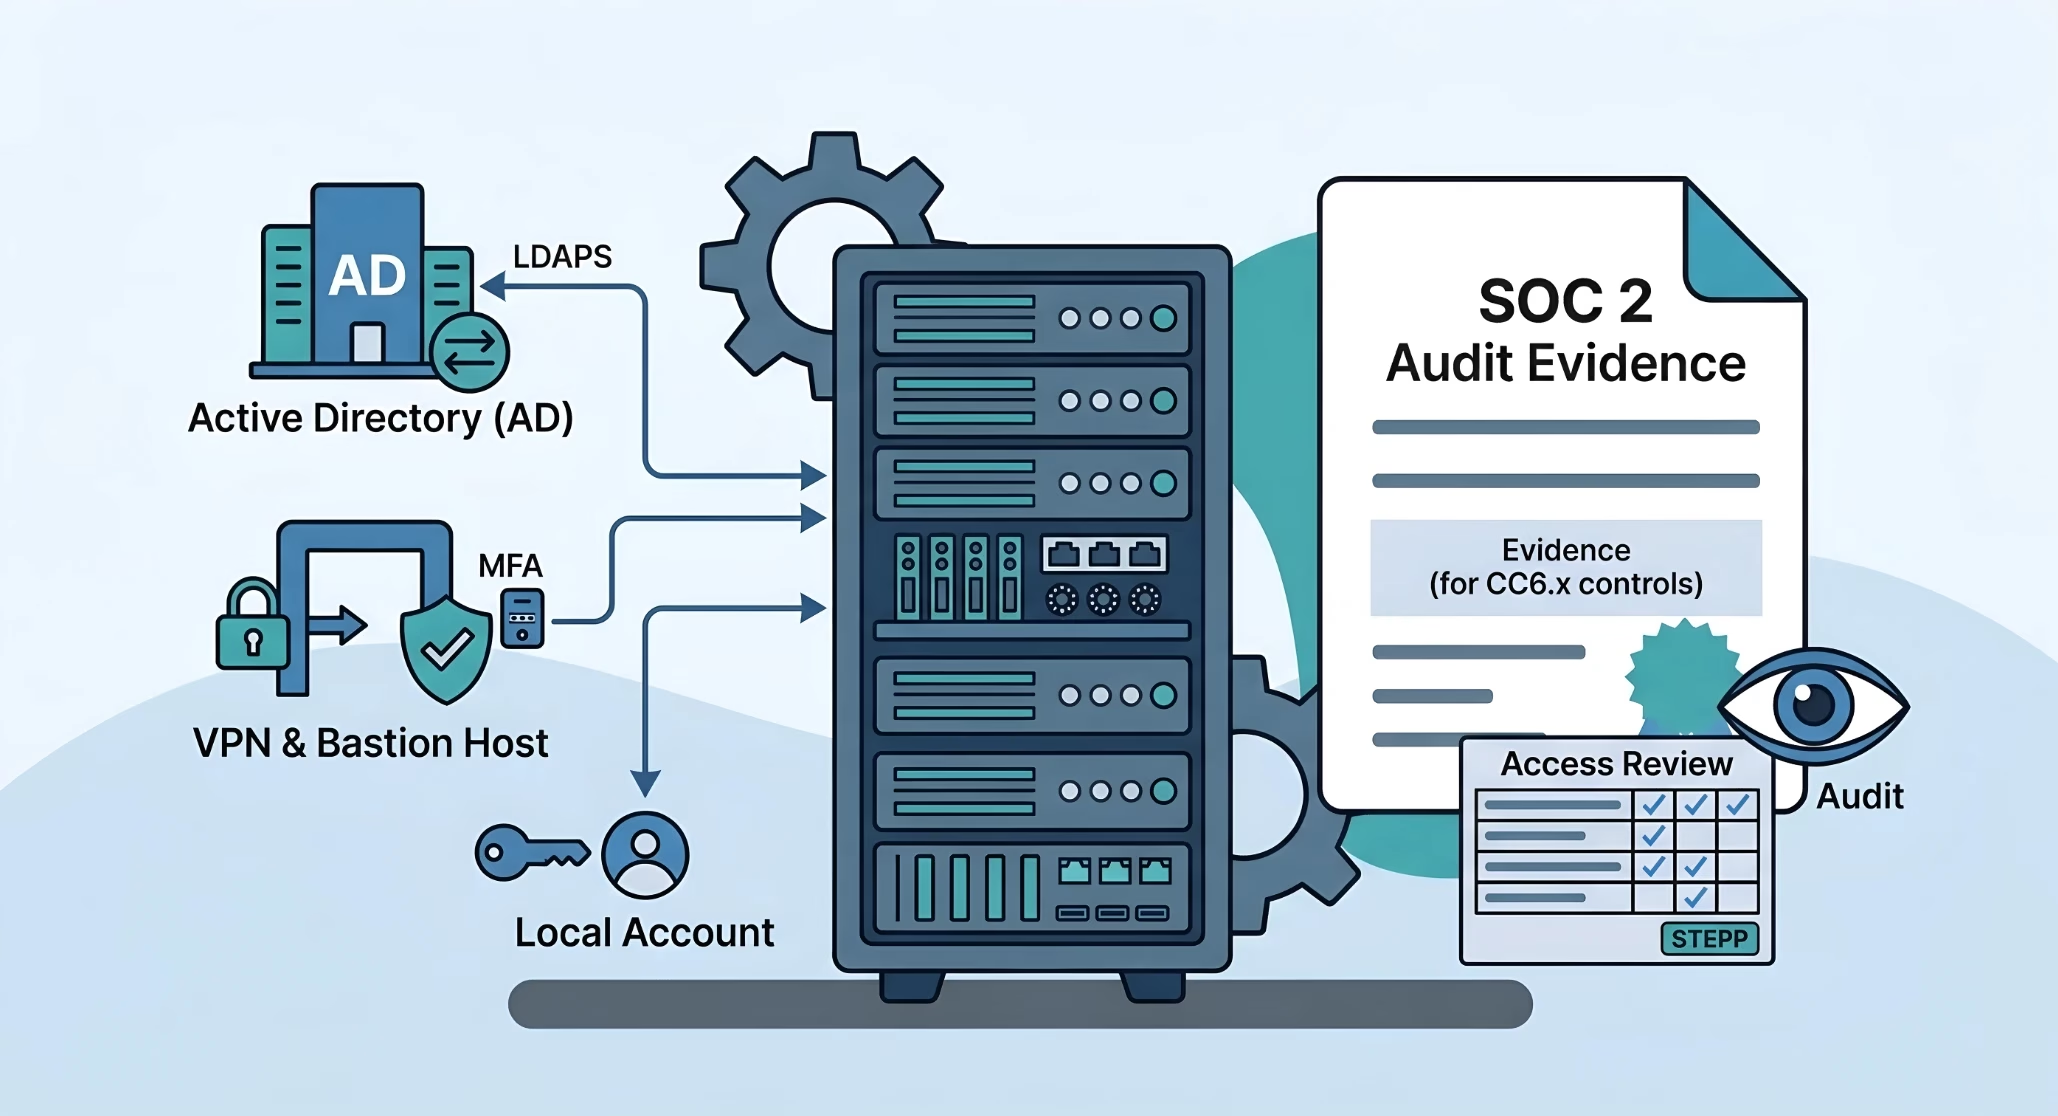
An illustration showing SOC 2 access control for on-premise servers. It depicts Active Directory via LDAPS, VPN and Bastion hosts with MFA, and local accounts connecting to a server rack. A "SOC 2 Audit Evidence" document for CC6.x controls and an access review checklist are shown on the right.

SOC 2 Access Control for On-Premise and Bare Metal Environments

In cloud environments, access control is a managed service. AWS IAM provides centralized identity, Okta handles SSO across every SaaS tool, and the...
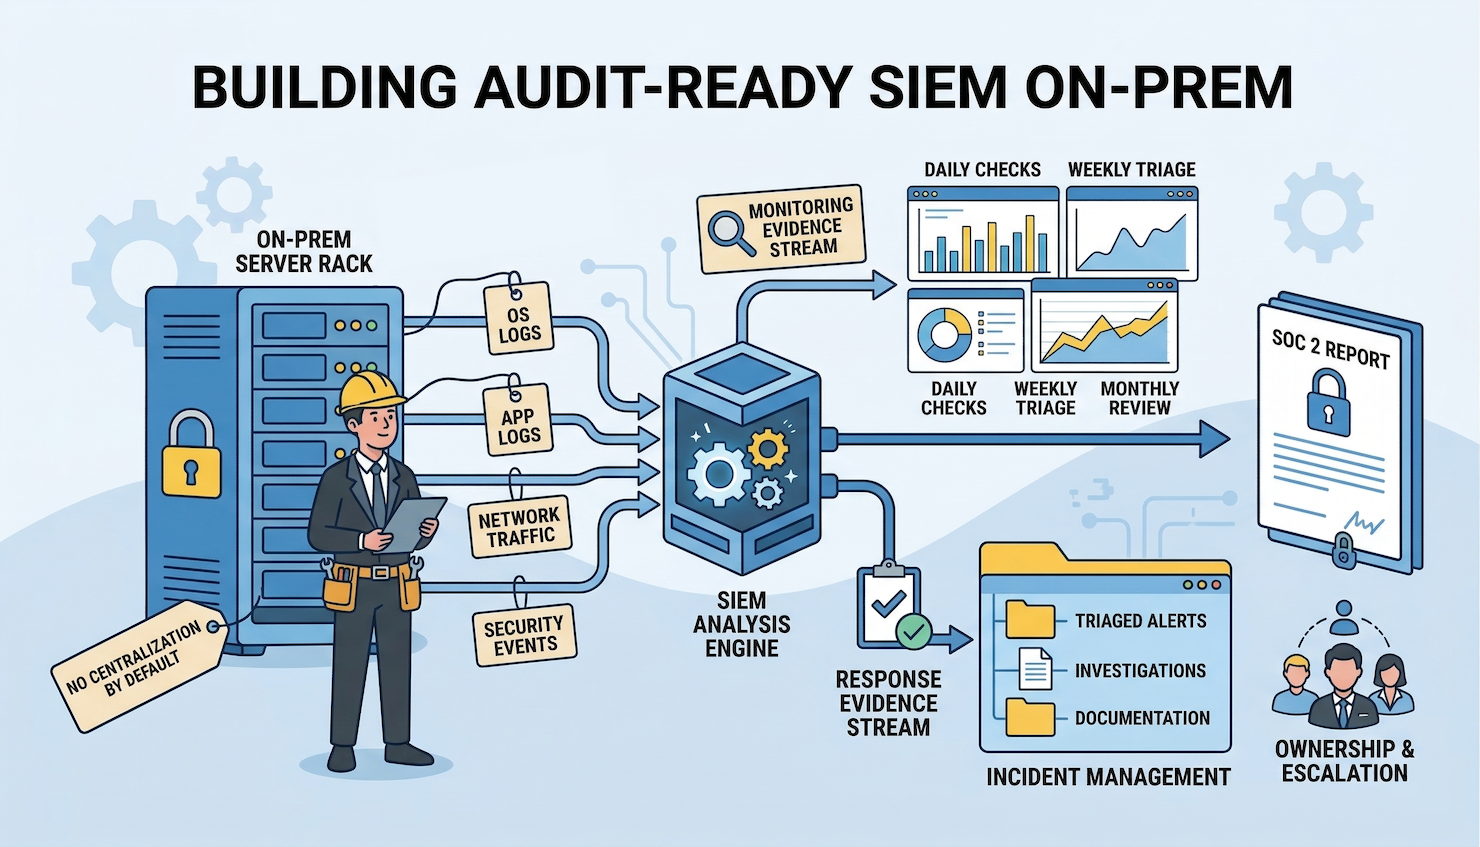
Infographic titled "Building Audit-Ready SIEM On-Prem." It shows logs (OS, App, Network, Security) flowing from a server rack into a SIEM Analysis Engine. This feeds into monitoring streams, incident management (triaged alerts, investigations), and ownership escalation to produce a SOC 2 Report.

SOC 2 Logging and SIEM for Bare Metal Servers

In a cloud environment, centralized logging is a toggle. Enable CloudTrail, turn on VPC Flow Logs, configure GuardDuty, and the compliance platform...
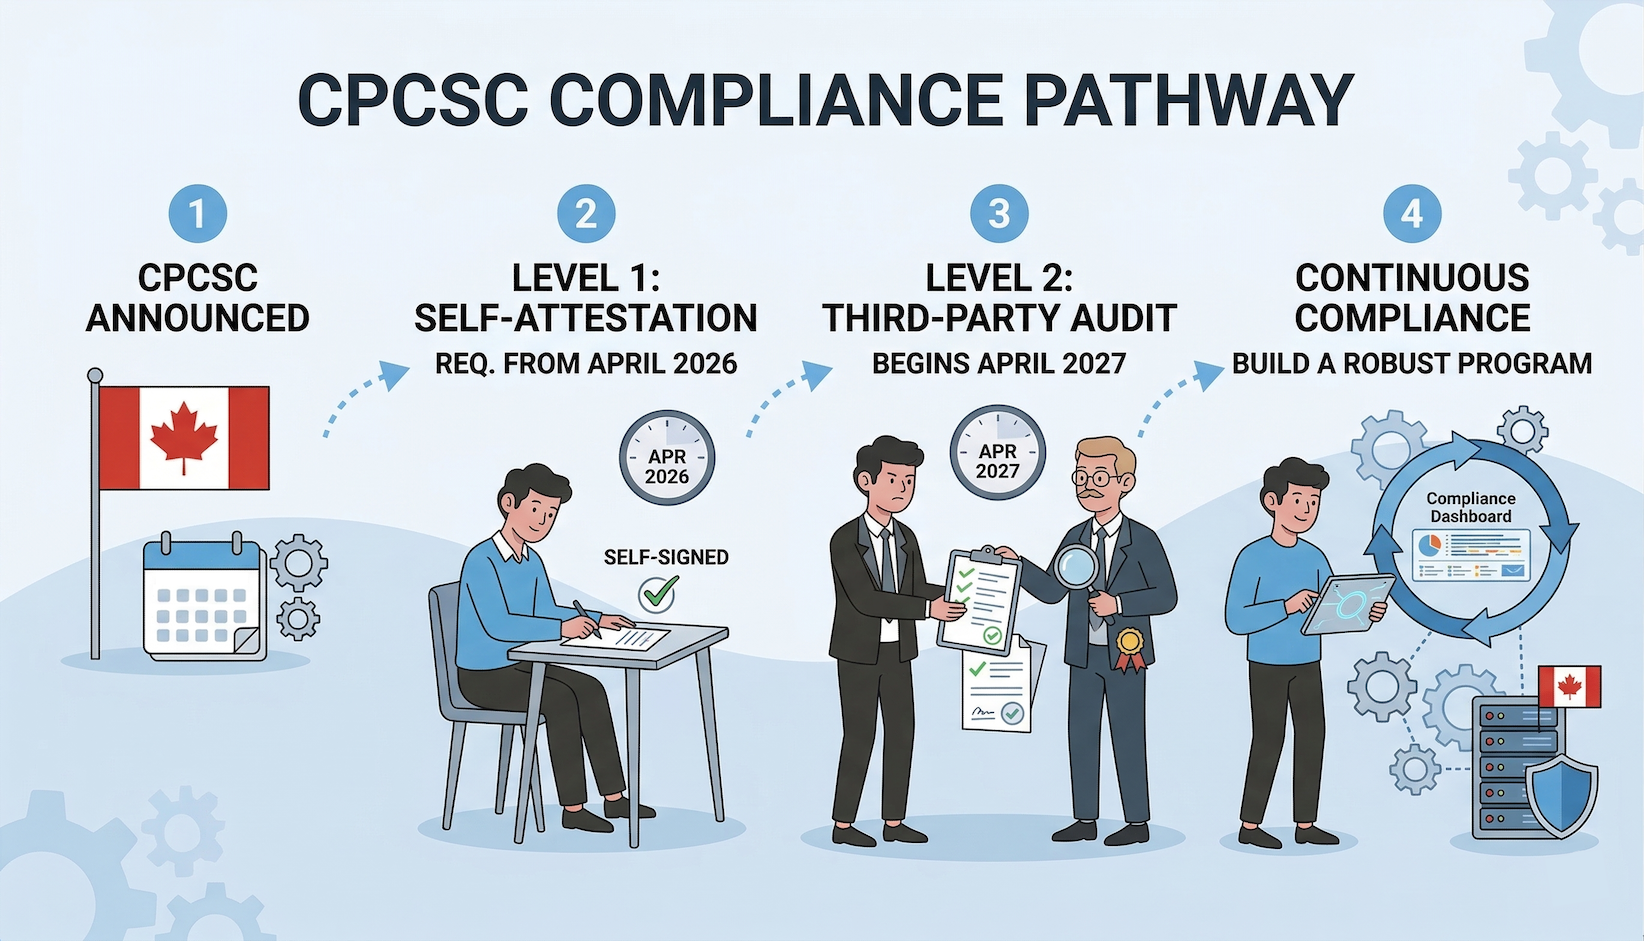
Infographic titled "CPCSC Compliance Pathway" outlining four stages for Canadian defence contractors: 1. CPCSC Announced, 2. Level 1 Self-Attestation (April 2026), 3. Level 2 Third-Party Audit (April 2027), and 4. Continuous Compliance via a robust program and digital dashboard.

CPCSC: What Defence Contractors Need Before April 2026

The Canadian Program for Cyber Security Certification (CPCSC) is Canada's mandatory cybersecurity certification for companies bidding on Department...
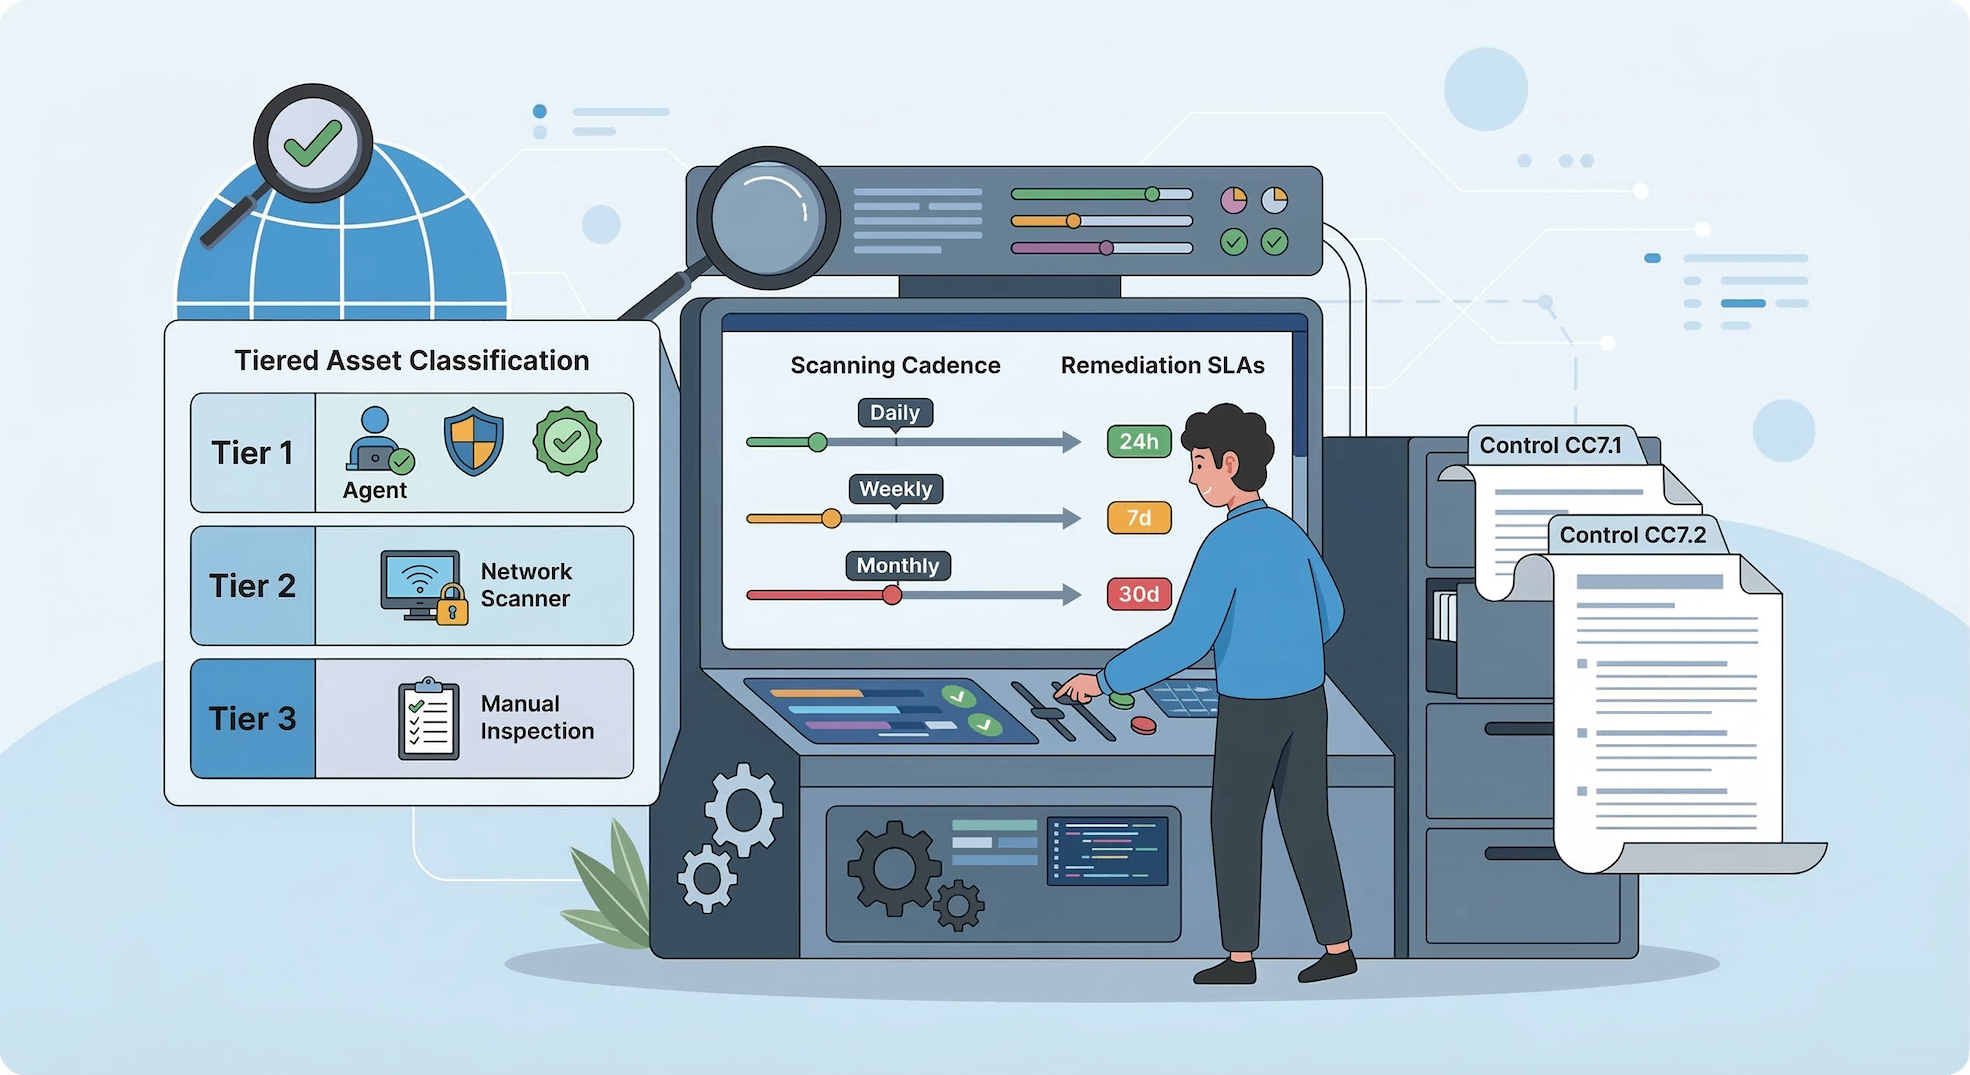
An illustration of a technician managing a security operations center for SOC 2 compliance. It features a tiered asset classification chart (Agent, Network Scanner, Manual Inspection), a dashboard showing scanning cadences and remediation SLAs, and filing cabinets with audit control documents.

SOC 2 Vulnerability Scanning for On-Prem Servers

Every SOC 2 vulnerability scanning guide assumes the same starting point: connect a cloud-native scanner, enable automated assessments, and let the...
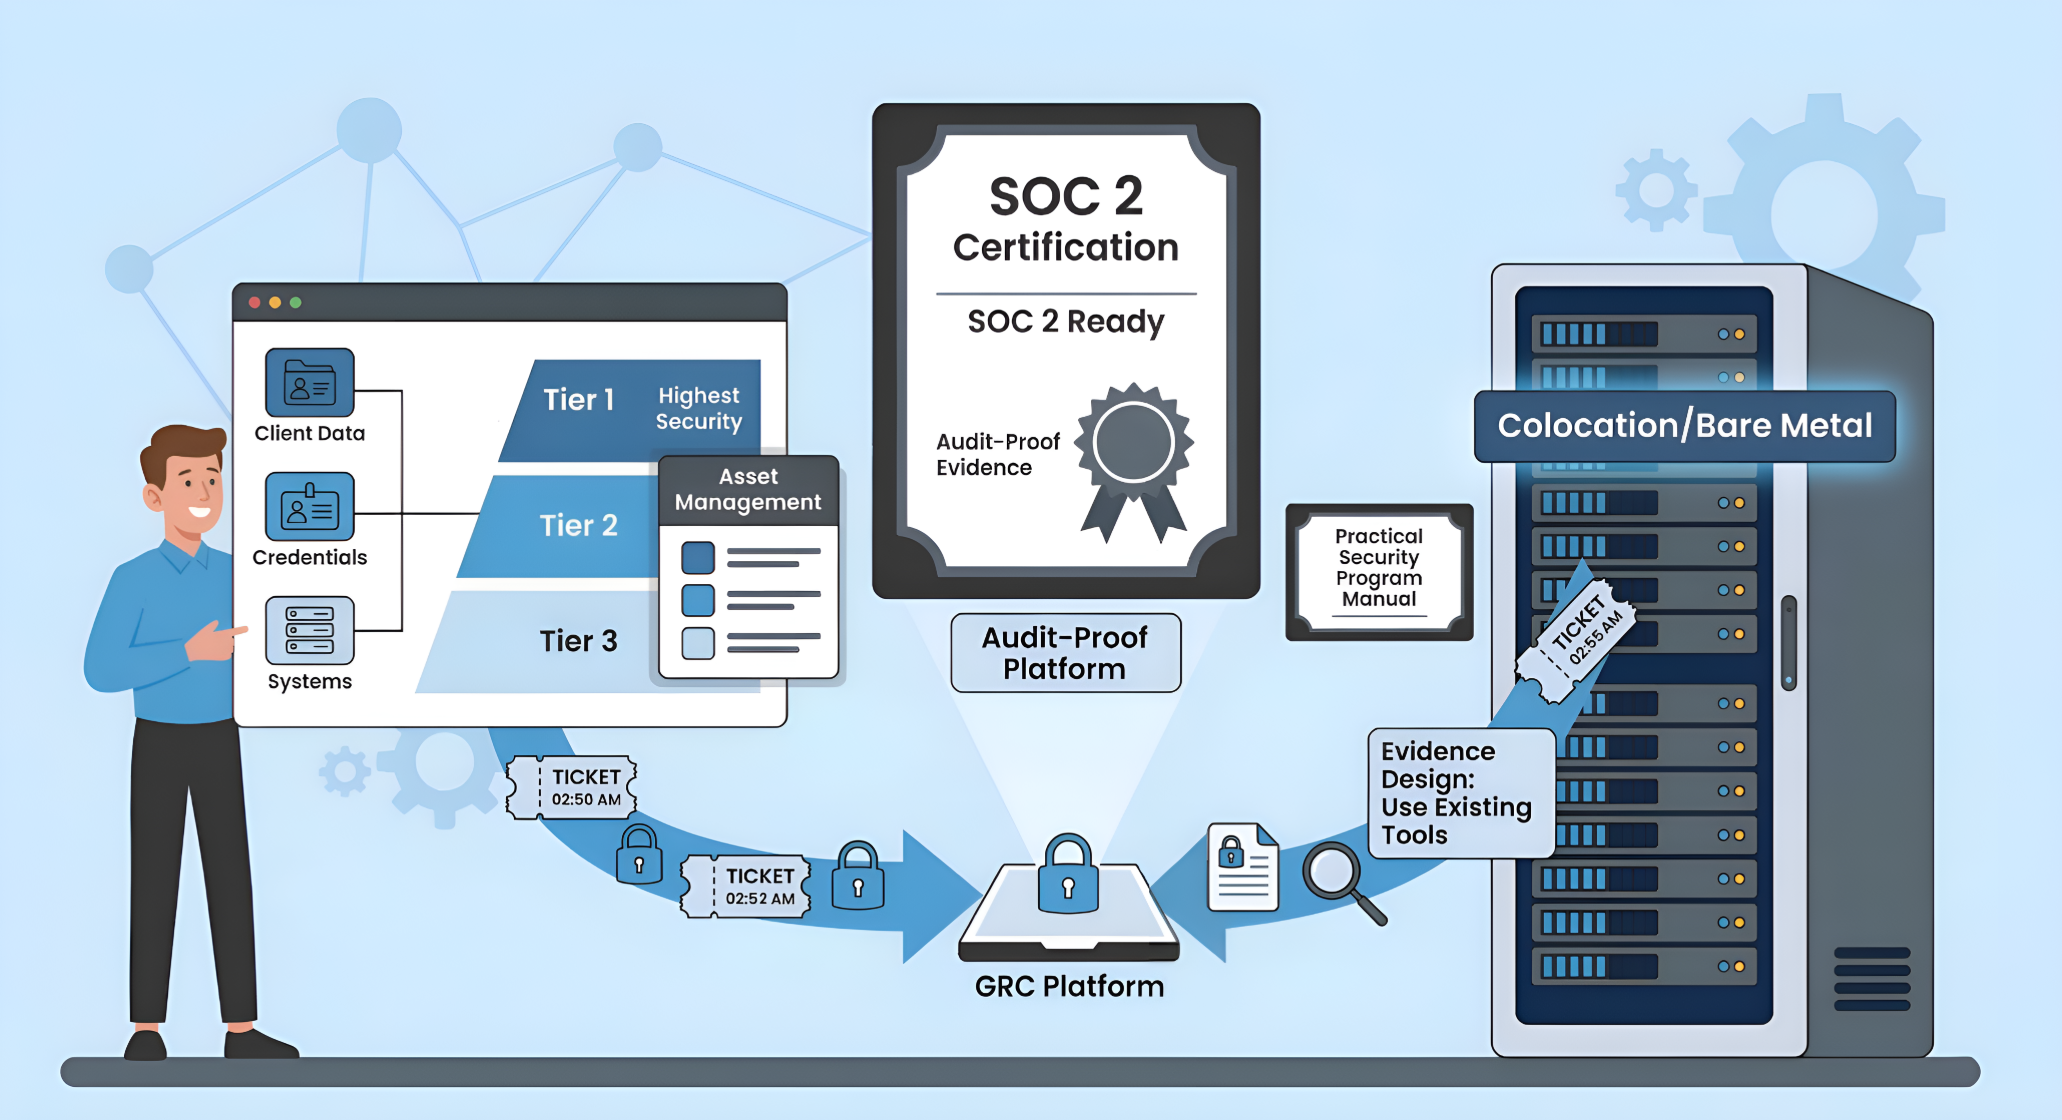
Infographic showing SOC 2 certification for Colocation/Bare Metal environments. It depicts an Audit-Proof Platform (GRC) collecting evidence like tickets and asset management data to achieve "SOC 2 Ready" status outside of standard AWS-style clouds.

SOC 2 Readiness for Bare Metal SaaS: What to Expect

A pattern keeps showing up. A SaaS company that has been running successfully for years, sometimes a decade or more, gets a call from a major...