

Build

Certificate lifecycle management

Public TLS certificates now last 200 days, 100 days from March 15, 2027 and 47 days from March 15, 2029. We find every certificate, build the automation that renews it, and can run it for you after go-live.

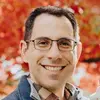
Ali Aleali

Ali Aleali, CISSP, CCSP

Co-Founder & Principal Consultant

Former security architect for Bank of Canada and Payments Canada. CISSP, CCSP, more than twenty years in enterprise security. Leads every engagement.

Connect on LinkedIn

What the engagement covers

Assess, design and build, with an optional ongoing operate service. You choose where Truvo stops.

icon-6

Inventory with an owner on every certificate

Built from Certificate Transparency logs (crt.sh, Censys), cloud accounts, load balancers such as F5 BIG-IP and NetScaler, and an internal network scan. Each certificate is rated by what breaks if it expires.

icon-7

Renewal design per platform

ACME clients such as Certbot, acme.sh and Caddy, cert-manager on Kubernetes, AWS Certificate Manager, Azure Key Vault and Google Certificate Manager, with a named fix for every system that cannot run ACME.

icon-3

Domain validation ready for 2029

DNS-01 through Route 53, Cloudflare or Azure DNS with scoped API credentials, CAA records and ACME account key handling, ready for the 10-day validation reuse window.

icon-5

Built in your environment

Truvo engineers install and configure the automation, starting with the systems most likely to cause an outage, alongside your team.

icon-2

Monitoring and a runbook

Expiry alerts in the tools your team already watches, such as Datadog, Prometheus or PagerDuty, plus a runbook for a failed renewal.

icon-9

Vendor-neutral platform advice

Whether you need CyberArk Certificate Manager (formerly Venafi), Keyfactor Command, DigiCert Trust Lifecycle Manager, Sectigo Certificate Manager or AppViewX, or whether open-source tools and cloud services cover your estate.

Assess, Build, Operate, applied to certificates

Scope is set before the engagement starts. Led by a senior architect with more than ten years of enterprise security experience.

01

Assess

Every public and internal certificate found, owned and rated, plus a decision on tooling. Access happens inside your environment and Truvo takes no custody of production data.

02

Build

Renewal automation designed per platform and installed, starting with the highest-risk systems, with monitoring, alerting and a runbook in place.

03

Operate

Optional. Truvo runs the certificate program after go-live: failed renewals, new systems and domains, inventory reviews, CA/Browser Forum changes and audit evidence.

What you hold at the end

Certificates that renew on their own, and the records to prove it.

  • Certificate inventory with an owner and a risk rating on every certificate

  • Renewal design per platform, including a fix for every system that cannot run ACME

  • Automation installed and tested on the in-scope systems

  • Expiry monitoring and alerting in your existing tools

  • Runbook for a failed renewal

  • Evidence for SOC 2 CC6.7 and ISO 27001 Annex A 8.24

What the engagement settles

Four questions that come up the day a certificate expires.

When this is the right call, and when it is not

The trigger is usually one expired certificate that took something down, or someone reading the CA/Browser Forum schedule and counting renewals.

Frequently asked questions

CA/Browser Forum Ballot SC-081v3, passed on April 11, 2025, cuts the maximum life of a publicly trusted TLS certificate in three steps: 200 days from March 15, 2026, 100 days from March 15, 2027, and 47 days from March 15, 2029. The 2029 step also cuts how long a certificate authority can reuse a domain validation to 10 days. A certificate you renew once a year today needs renewing about twice a year now, four times a year from 2027 and eight times a year from 2029.

Only to publicly trusted TLS certificates. Certificates from your own private CA follow whatever policy you set. In practice most estates mix the two, with public certificates on internal hostnames and appliances because it was easier at the time. The inventory sorts out which is which, and some certificates end up moving to a private CA as a result.

Common examples are firewalls and VPN gateways, older F5 or NetScaler load balancers, Windows servers running IIS, Java keystores and vendor-hosted SaaS platforms. The options are to move TLS termination to something that can automate, use the vendor's own API, push certificates from a central tool, or replace the system on a schedule. The plan names one option per system with an owner and a date, so nothing is left to a calendar reminder.

Not always. An estate with a few hundred certificates, mostly in cloud and Kubernetes, often runs well on cert-manager, Certbot or acme.sh, AWS Certificate Manager and good monitoring, with a private CA such as Smallstep or AWS Private CA for internal names. Larger or more mixed estates usually need a platform for discovery and push-based renewal, such as CyberArk Certificate Manager (formerly Venafi), Keyfactor Command, DigiCert Trust Lifecycle Manager, Sectigo Certificate Manager or AppViewX. Truvo does not resell any CLM product, so the recommendation follows your estate.

Any public CA that supports ACME, which today includes Let's Encrypt, DigiCert, Sectigo, GlobalSign and Google Trust Services, plus the CLM platform you already own if you have one. If you are paying for a commercial CA, the inventory often shows where a free ACME certificate would do the same job and where an organization-validated certificate is still worth paying for.

An expired certificate is an outage, and an outage is an availability and change-management finding. The same work produces the evidence auditors ask for: a cryptographic key and certificate inventory, a documented renewal process, and monitoring with alerts. Under ISO 27001:2022 that sits mainly under Annex A 8.24, use of cryptography, which expects a managed lifecycle for keys and certificates. Under SOC 2 it supports CC6.7, which covers protecting information in transmission, and the availability commitments in your system description.

Both, and you choose where Truvo stops. Some teams want the assessment and design and then build it themselves. Most want Truvo engineers to build it alongside their team, so the automation is in place and the team knows how it works. Teams without the people to own it after go-live can hand the running of it to Truvo as an ongoing service.

Watching renewals and fixing the ones that fail, bringing new systems, domains and acquired companies into the automation, a regular inventory review with owners, tracking CA/Browser Forum and browser policy changes before they land, and keeping the inventory, renewal records and alert history ready for your SOC 2 or ISO 27001 auditor. Scope and response times are agreed per client in the statement of work.

Before the 100-day step on March 15, 2027. At 200 days a team can still renew by hand and catch most misses. At 100 days the volume doubles and manual renewal is where outages come from. Starting now leaves time to fix the hard systems before the 47-day step and the 10-day validation window in 2029.

Talk to the architect who would do the work

A 30-minute call. We look at your certificate estate and say plainly what it would take to automate it before the 100-day limit.

From the blog: security architecture

Agentic AI Security Architecture: How to Let AI Agents Do Real Work Safely

Agentic AI security architecture starts with a map of the components of an AI agent system and the connections between them, which sets the scope, ...
What Does a Security Architect Do?

A security architect does three jobs: sets security requirements for systems other people design, assesses and reviews those designs, and solutions ...
Hybrid Identity Management: How to Centralize IGA

It's tempting to centralize identity by buying a platform, but I leave the platform for last. Below is my approach to solutioning centralized ...