

Managed Compliance

GDPR compliance consulting for companies with European customers

GDPR consultants for companies outside the EU with European users. Find out which GDPR obligations reach you, then build the privacy program on the security controls you already run for SOC 2 or ISO 27001.

Talk to a GDPR consultant

Share what you need and a consultant will follow up to book a call.

What a GDPR engagement covers

Find out which GDPR obligations reach you, then build the privacy program on the security controls you already run.

icon-5

Scoping read

Whether the GDPR applies under Article 3, and your role as controller, processor or both for each processing activity. In writing.

icon-9

Records of processing

Article 30 records built from a data inventory and data flow map of your real systems.

icon-6

Lawful basis and DPIAs

Lawful basis for each purpose under Article 6, and data protection impact assessments under Article 35 for high-risk processing.

icon-7

Contracts and EU data transfers

Article 28 data processing agreements, and a transfer mechanism for every flow out of the EU: the EU-US Data Privacy Framework, the Canada adequacy decision or Standard Contractual Clauses.

icon-3

Rights requests and breach response

A workflow for access, correction and deletion requests under Articles 15 to 22, and breach notification inside the 72-hour window of Article 33.

icon-4

Article 32 mapped to your existing controls

Security of processing mapped to the SOC 2 criteria and ISO 27001 controls that already produce the evidence.

Assess, Build, Operate, applied to the GDPR

A documented methodology, led by a senior CISSP in the US or Canada with 10+ years in security.

01

Assess

Article 3 scoping, data inventory, data flow map and gap analysis, built from your systems and interviews inside your environment.

02

Build

Records of processing, DPIAs, data processing agreements, transfer mechanisms and the rights request workflow.

03

Operate

Truvo runs the privacy processes every month as part of managed compliance, alongside SOC 2 or ISO 27001. A fractional privacy officer is available when a DPO is required.

What you hold at the end

A GDPR program built on the security controls you already operate.

  • GDPR applicability and role determination, in writing

  • Records of processing activities (Article 30)

  • Data flow and EU transfer map

  • DPIA register and process

  • Data processing agreements (Article 28)

  • Control mapping to SOC 2 and ISO 27001

  • Rights request and breach notification workflows

  • Questionnaire answer set

What changes with a GDPR program

European customers get GDPR answers backed by records and running processes.

Who GDPR consulting is for

Truvo Cyber is a cybersecurity consulting firm. Where an obligation turns on a contested legal reading, the assessment names it for your counsel.

Frequently asked questions

The GDPR follows the people. Article 3 brings a company based in Canada or the US inside the regulation when it offers goods or services to people in the EU or monitors their behaviour there. A SaaS company with European users or an app available in the EU is usually in scope. The scoping read settles the answer for each product in writing, and identifies whether you also need an EU representative under Article 27.

Article 37 requires a DPO when your core activities involve large-scale, regular and systematic monitoring of people, or large-scale processing of special categories such as health data. Many B2B SaaS companies fall below that line. Health tech, health and safety platforms and companies that track user behaviour at scale often fall above it. Truvo offers a fractional privacy officer when the role is required.

A controller decides why and how personal data is processed. A processor handles personal data on a controller's behalf. Most B2B SaaS companies are processors for their customers' data and controllers for their own marketing, sales and employee data. Article 28 requires a written contract between the two, and Truvo maps your role for each processing activity before writing any documents.

SOC 2 and ISO 27001 cover most of Article 32, the security of processing article: access control, encryption, logging, vendor management, backup and incident response. The rest of the GDPR is privacy work those frameworks leave open: records of processing, lawful basis, retention, rights requests, DPIAs and international transfers. Truvo maps your existing controls first, so the GDPR work adds only the privacy layer.

Article 83 allows fines up to 20 million euros or 4 percent of worldwide annual turnover, whichever is higher, for the most serious infringements, and up to 10 million euros or 2 percent for others. For most companies outside the EU, the more immediate cost is commercial: European customers ask for GDPR evidence in procurement, and a missing answer stalls the deal.

Talk to the architect who would do the work

A 30-minute call. We look at your environment and say plainly whether we can help and what it would take.

From the blog: privacy and data protection

Quebec Law 25 Compliance: The Privacy Law Every SaaS Company Should Know About (But Probably Doesn't)

Quebec Law 25 is the province's modernized private-sector privacy law: a set of amendments (adopted in 2021 as Bill 64) to the Act respecting the ...
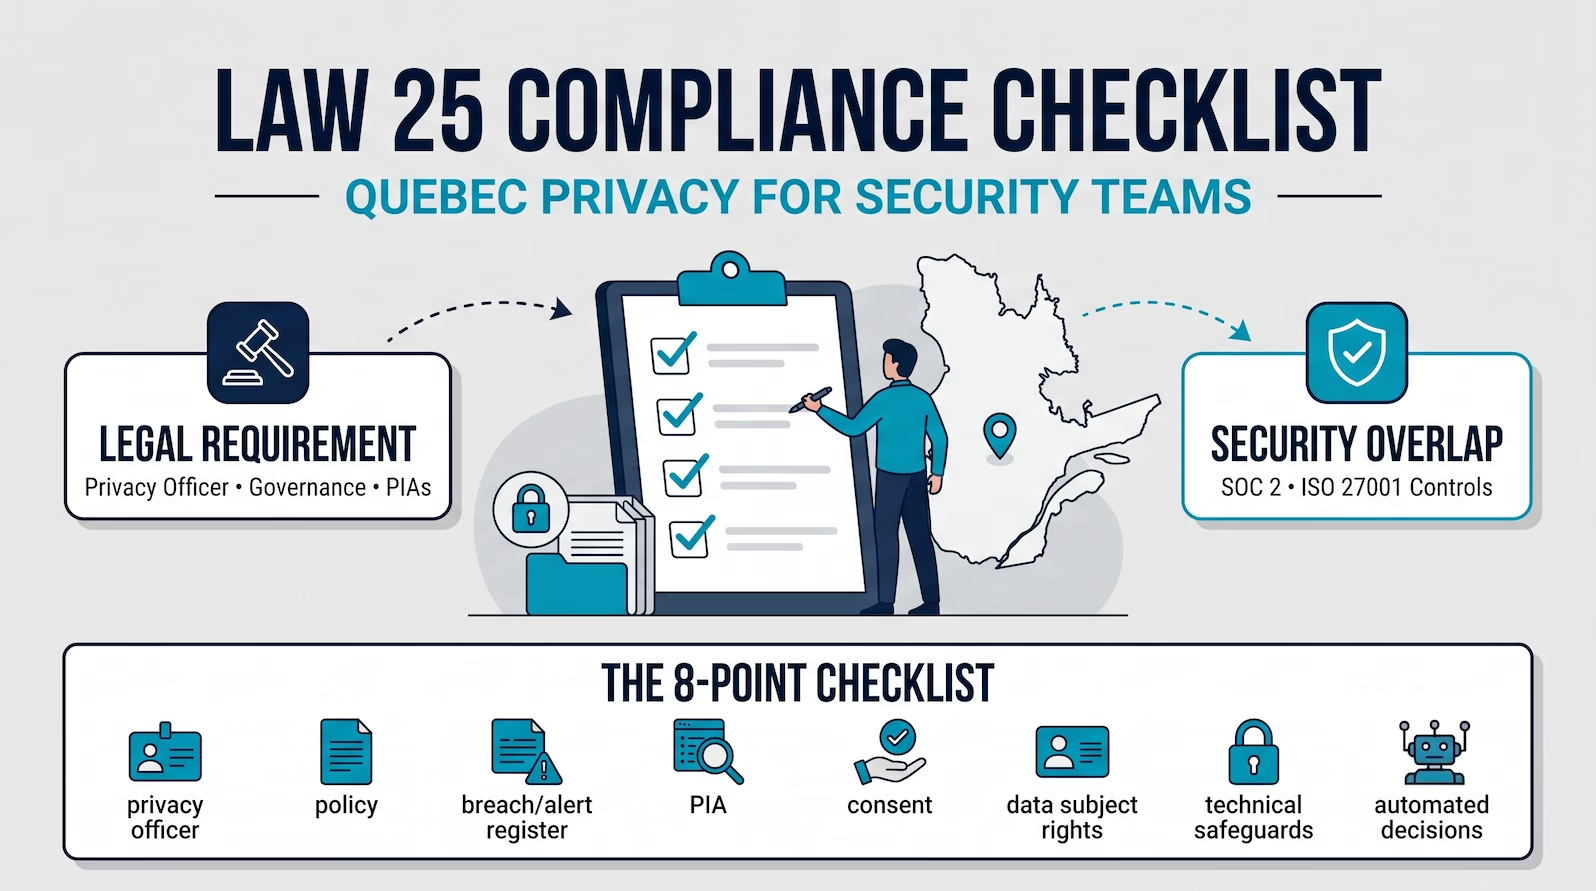
Law 25 Compliance Checklist: What Security Teams Actually Need to Do

Quebec's Law 25 has been fully in force since September 2024, and the penalties are no longer theoretical. Under the Act respecting the protection of ...
After Bill C-27: Quebec Law 25 and Canadian Privacy Costs

For three years, the dominant story in Canadian privacy law was the federal one. Bill C-27, the Digital Charter Implementation Act, was on track to ...