Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

Stock photo by Mikhail Nilov via Pexels, illustrating team reviewing deployment pipeline screens (temporary placeholder pending custom hero design).

ISO 27001 A.8.32: Change Management

To satisfy ISO 27001 A.8.32, put every change to production systems, applications, and infrastructure through one documented path: a request, a risk...
Stock photo by Brett Sayles via Pexels, illustrating network cables switch data center (temporary placeholder pending custom hero design).

ISO 27001 A.8.20: Network Security

ISO 27001 A.8.20 requires that the networks carrying an organization's information are secured, managed, and controlled to protect the systems and...
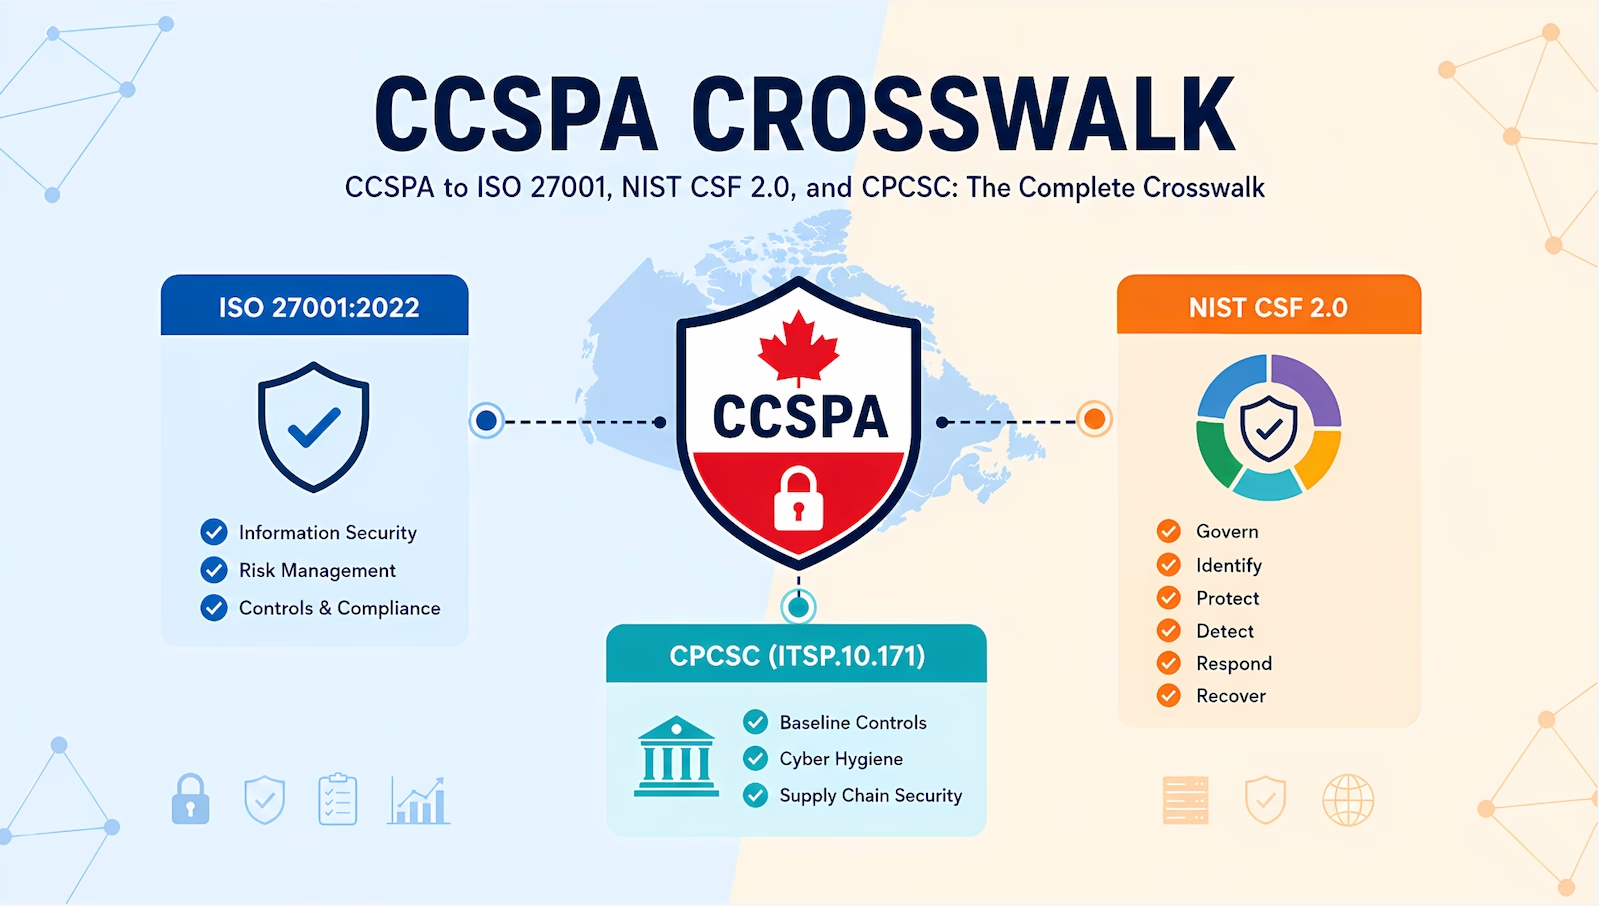
CCSPA crosswalk infographic showing a central Canadian shield connected to ISO 27001:2022, NIST CSF 2.0, and CPCSC ITSP.10.171, with compliance controls, cybersecurity icons, and a map of Canada in a clean blue, teal, orange, and red design.

Mapping the CCSPA to ISO 27001, NIST CSF 2.0, and CPCSC: The Complete Crosswalk

This crosswalk maps the seven obligation areas of the Critical Cyber Systems Protection Act (CCSPA), enacted June 15, 2026 as Part 2 of Bill C-8,...
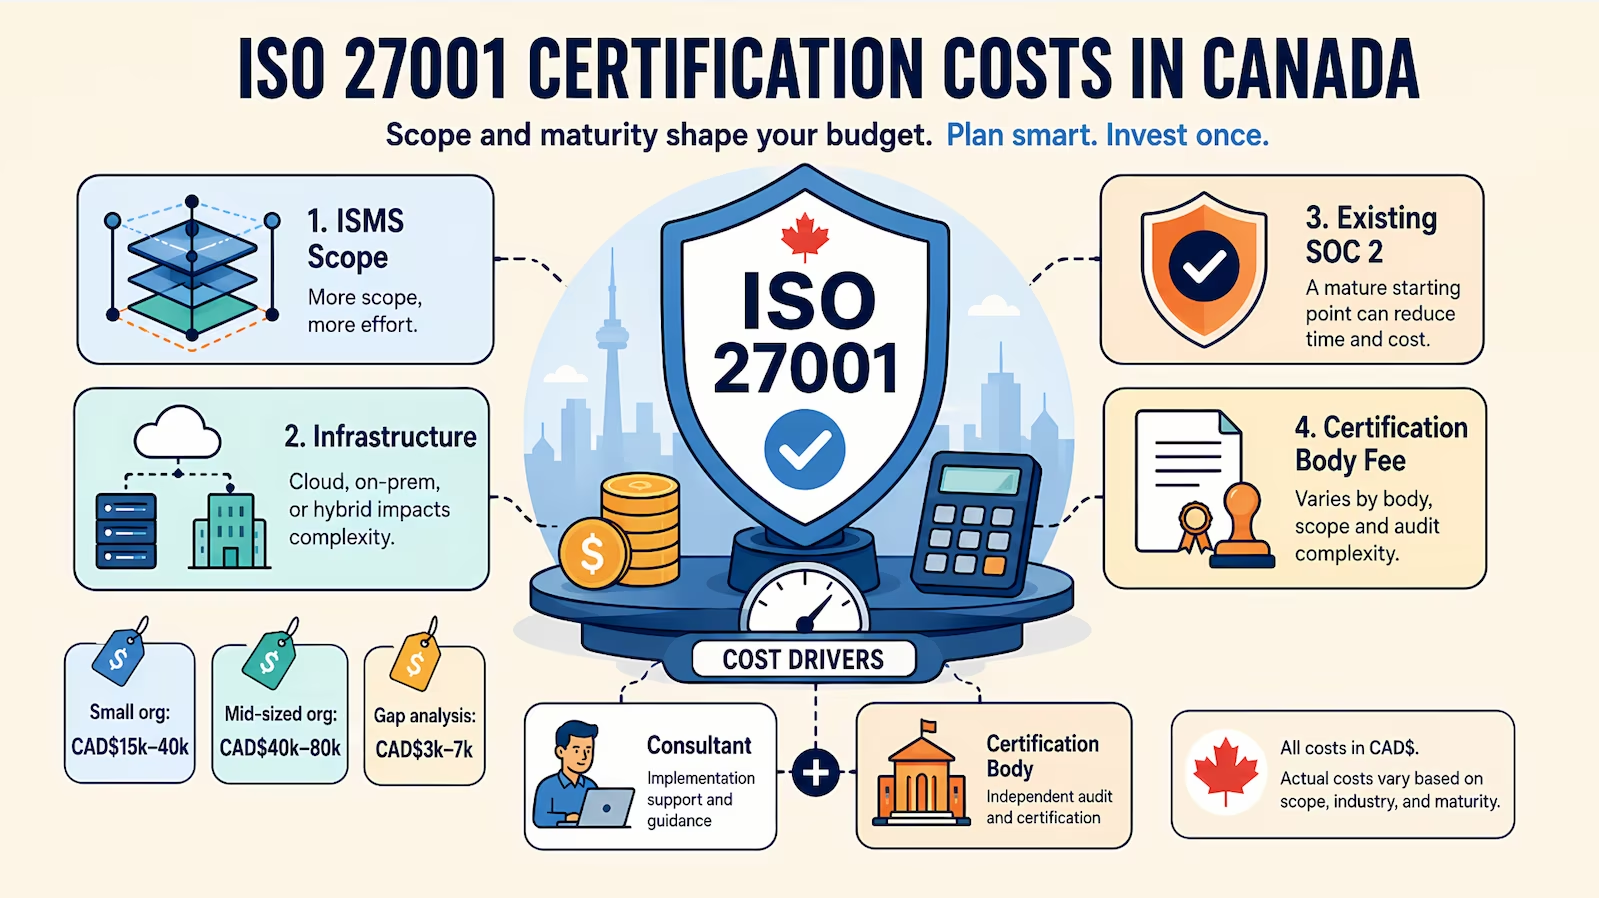
ISO 27001 cost in 2026 for Canadian companies

ISO 27001 Cost 2026: Real Price Ranges by Line Item

ISO 27001 certification cost in 2026 is set mostly by audit days: an accredited certification body needs 5 auditor days for a 10-person organization...
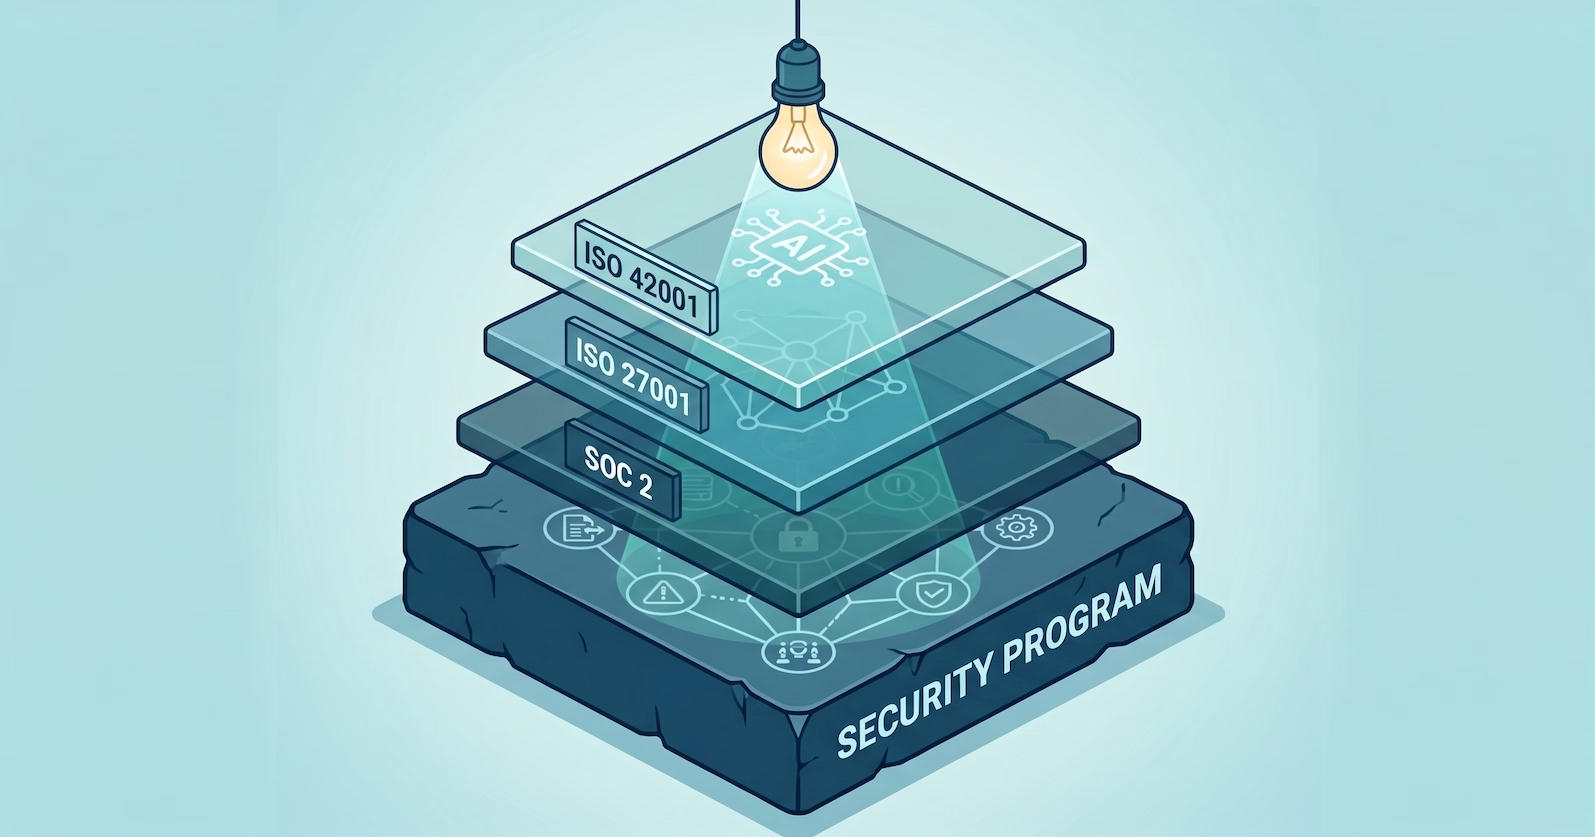
Most of ISO 42001 Is Already Built

Most of ISO 42001 Is Already Built

How much of an existing SOC 2 or ISO 27001 program carries into ISO 42001, and why the framework tax is mostly imaginary for teams that built a real...
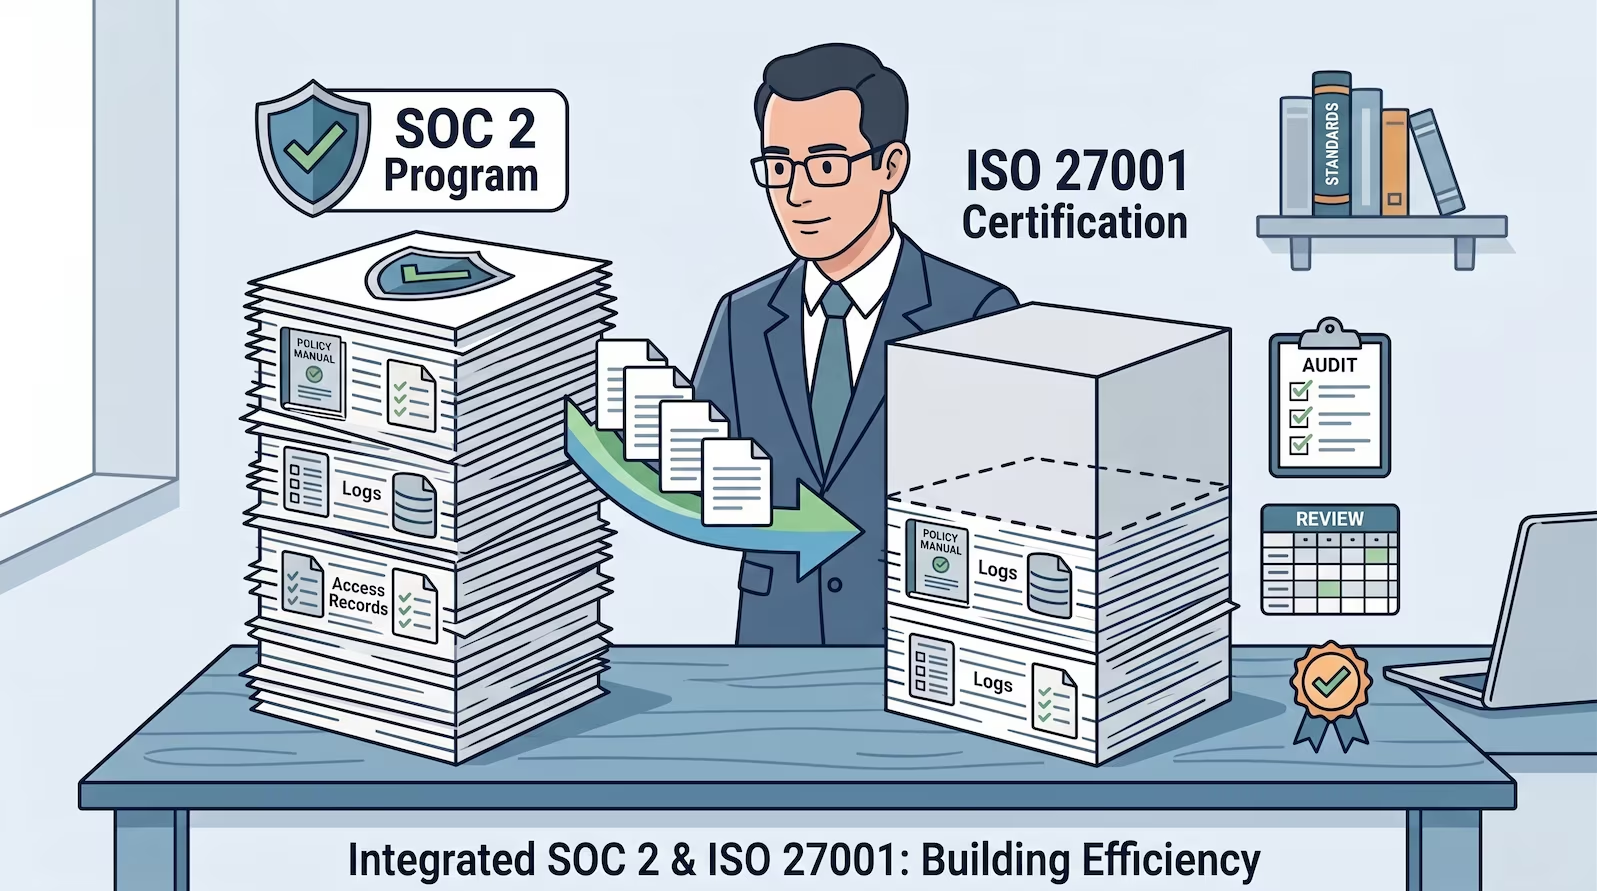
Illustration of SOC 2 program documents (policy manual, logs, access records) carrying over into an ISO 27001 certification

SOC 2 to ISO 27001 Control Mapping: What Transfers and What's Net-New

In our experience, a SOC 2 program covers roughly 70 percent of the work for ISO 27001 certification. The policies carry over, and most controls need...
Truvo Cyber blog hero — ISO 27001 Internal Audit Process: a practitioner walkthrough of what gets reviewed and how evidence works.

ISO 27001 Internal Audit: What Gets Reviewed

Most organizations pursuing ISO 27001 know they need an internal audit before the external stage 2. What they're less clear on is what that audit...
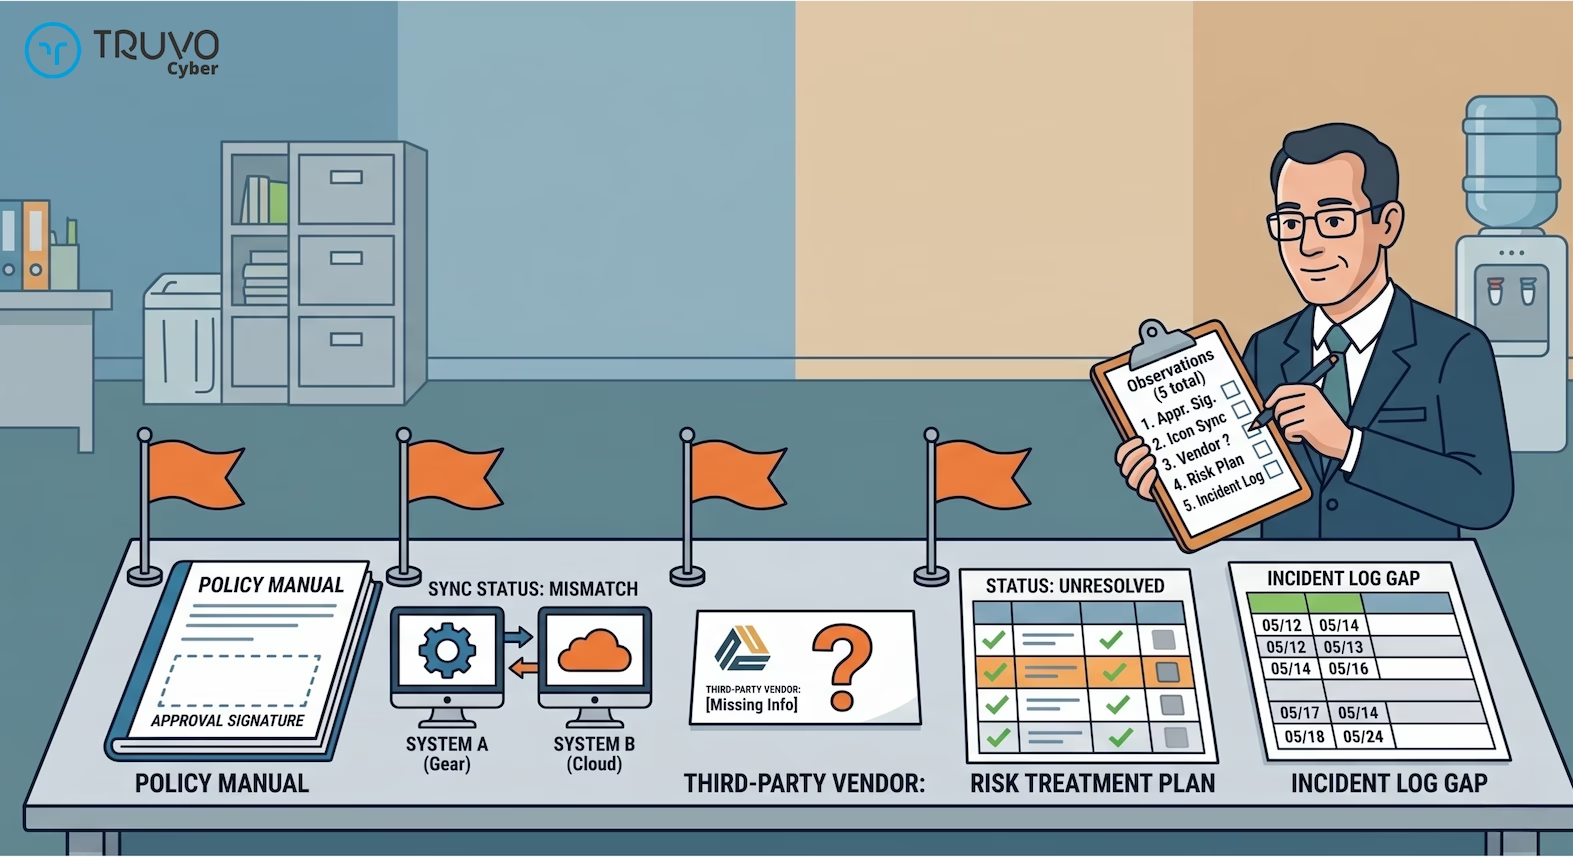
Truvo Cyber blog hero — ISO 27001 Internal Audit Findings: the five recurring gaps found before almost every external certification.

Five ISO 27001 Internal Audit Findings Before Certification

An ISO 27001 internal audit with no major nonconformities is a good result. It means the ISMS is documented, controls are operating, and the evidence...
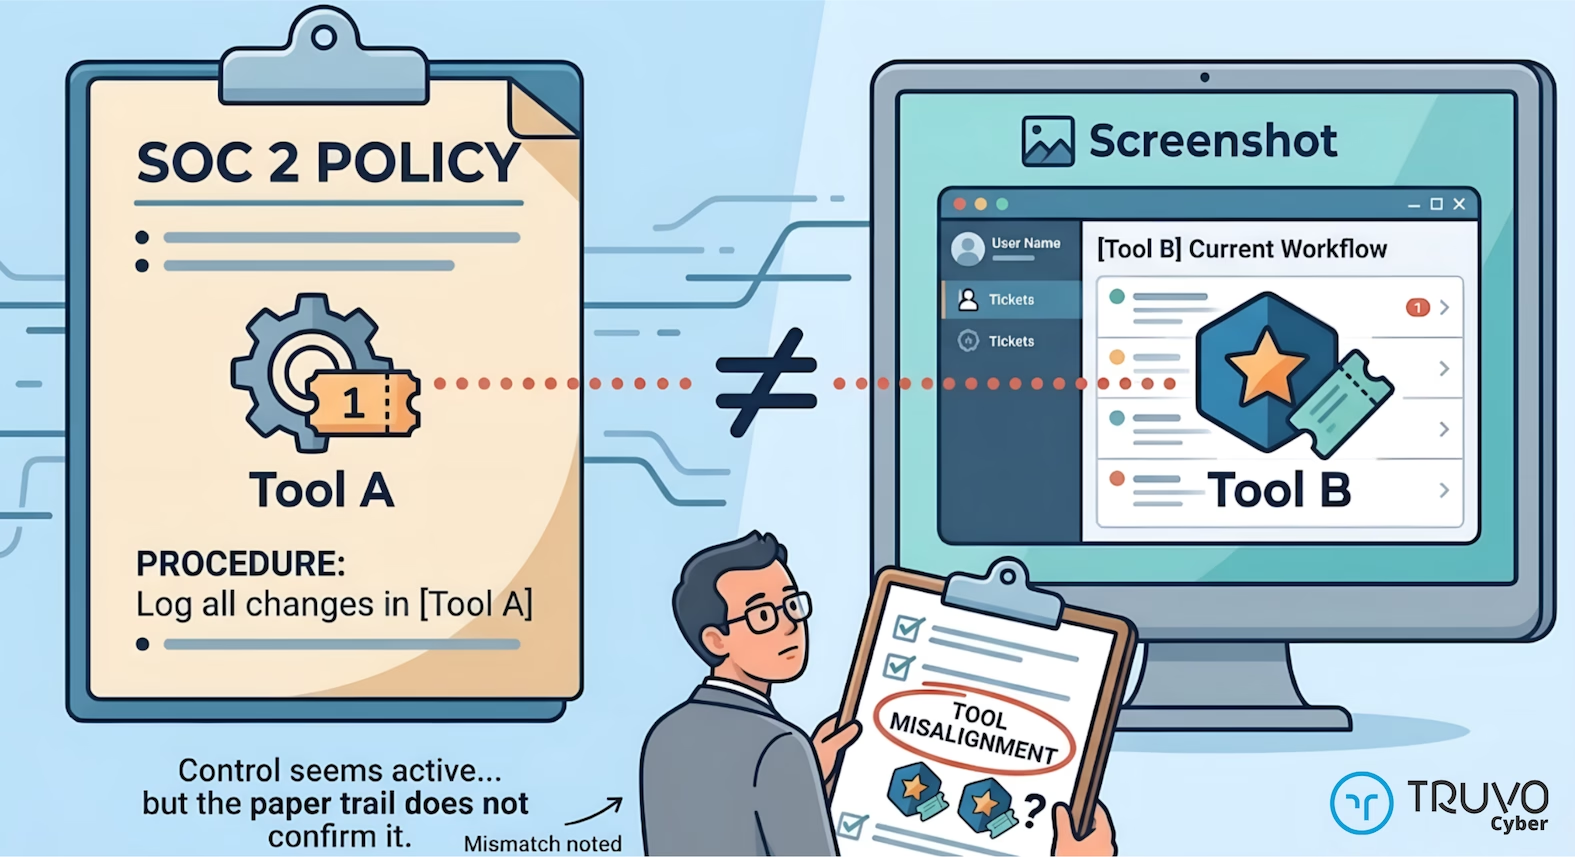
Truvo Cyber blog hero — ISO 27001 Policy Evidence Gap: why policies and evidence drift apart and how to close it before the auditor arrives.

ISO 27001 Evidence Gap: Policy vs Reality

Building an ISO 27001 ISMS is largely an exercise in documentation. You write policies, implement controls, collect evidence, and upload everything...
Truvo Cyber blog hero — ISO 27001 Internal Audit Consulting in Canada: scope, timeline, and what an external audit engagement covers.

ISO 27001 Internal Audit Consulting in Canada

Most Canadian organizations preparing for ISO 27001 certification have the same question at the internal audit stage: who should run this, and what...
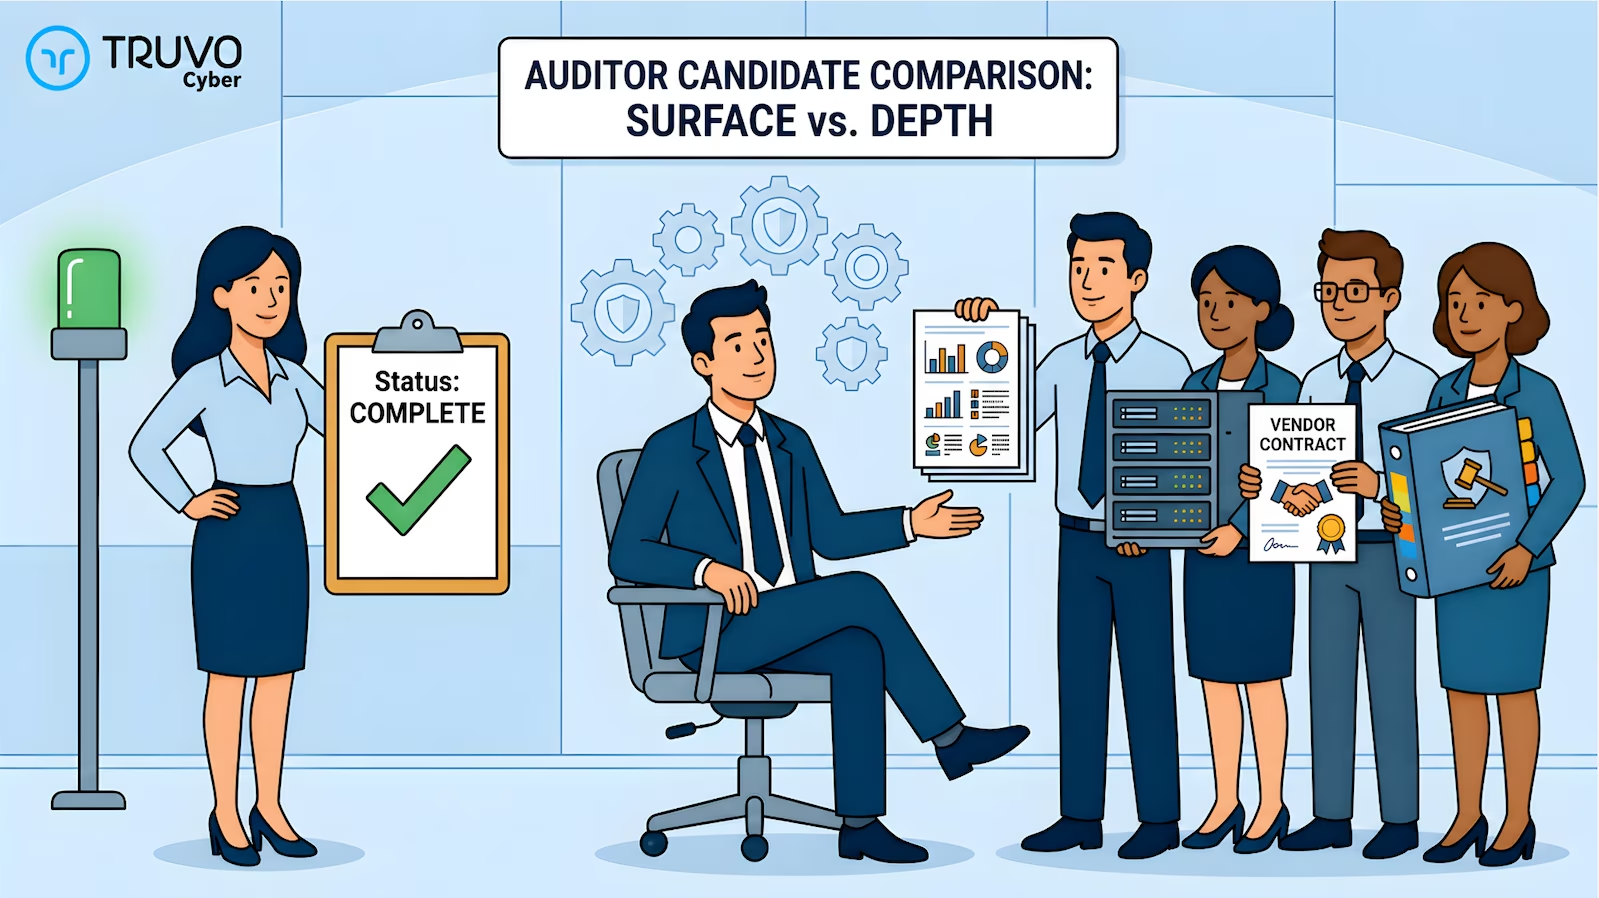
Illustration titled "AUDITOR CANDIDATE COMPARISON: SURFACE vs. DEPTH". A hiring manager looks towards a team presenting specialized controls: a server rack, vendor contract, and comprehensive binder. On the left, a single candidate holds a simple "Status: COMPLETE" clipboard with a green checkmark, near a green light.

What to Look for in an ISO 27001 Internal Auditor

When you are preparing for ISO 27001 certification, the internal audit is not a formality. It is the last structured opportunity to identify gaps...
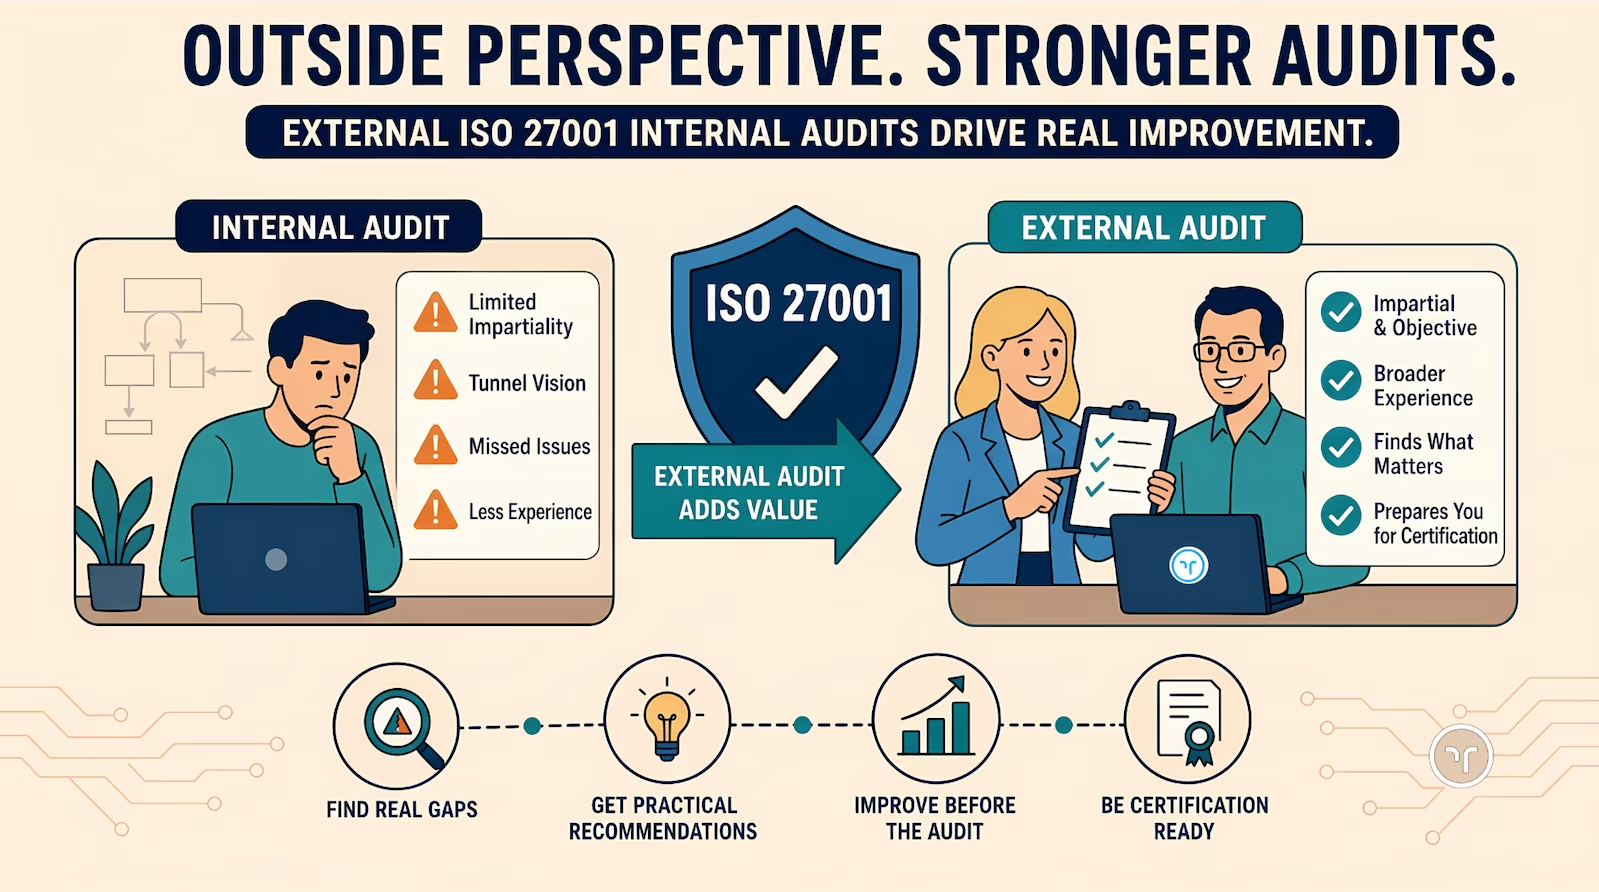
Truvo Cyber blog hero — Outsourcing Your ISO 27001 Internal Audit: when it makes sense and what to expect from an external engagement.

Outsourcing Your ISO 27001 Internal Audit: When It Makes Sense

Short answer: yes, you can outsource the ISO 27001 internal audit, and you don't need an internal audit team to do so. Clause 9.2 asks for an auditor...
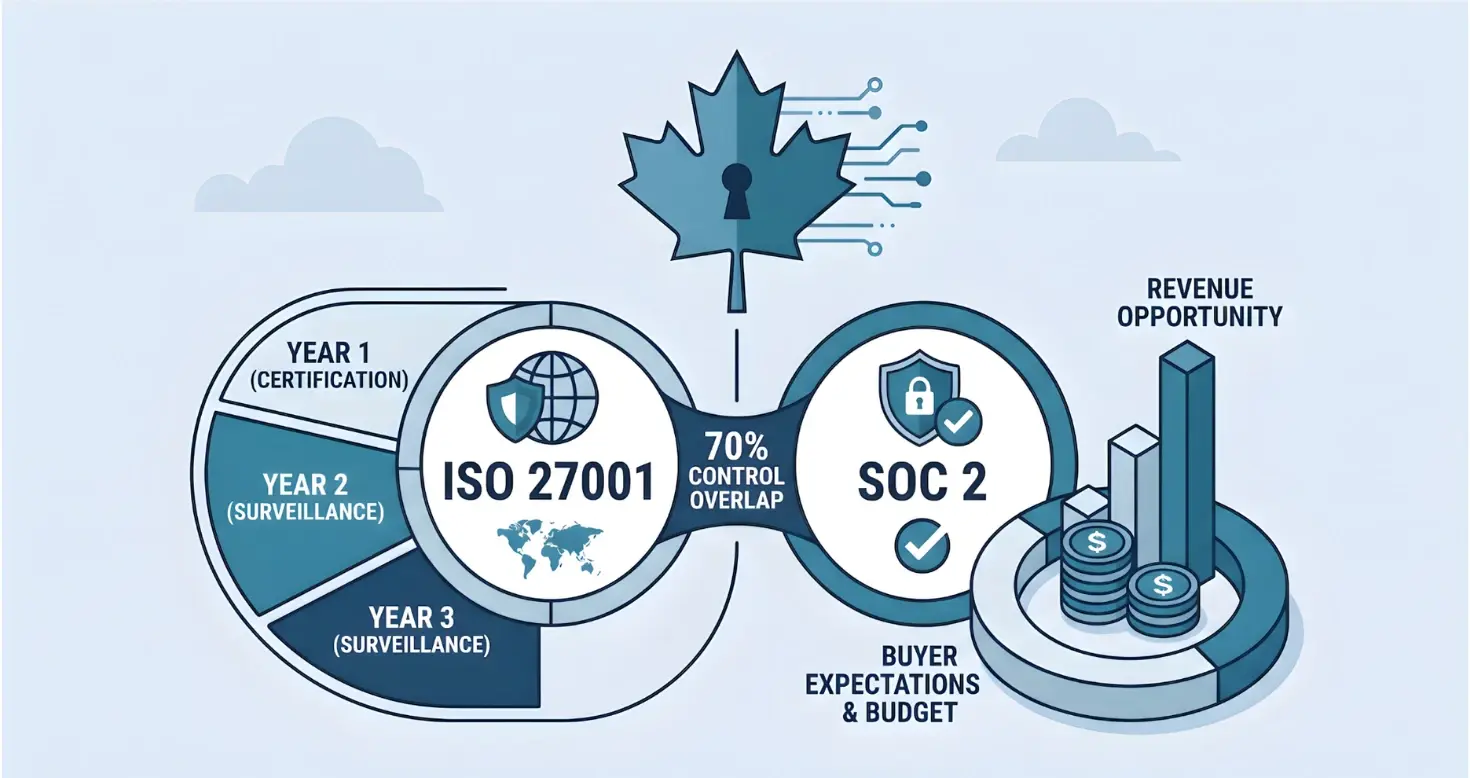
An infographic for Canadian SaaS, in blue vector style, showing how ISO 27001 and SOC 2 frameworks overlap by 70%. It details the 3-year ISO audit cycle and highlights "Revenue Opportunity" tied to "Buyer Expectations & Budget."

ISO 27001 Consultant in Canada: When It Makes Sense and What It Actually Takes

ISO 27001 certification gives you a one-to-two-page certificate. SOC 2 gives you a 40-to-50-page report describing every control, how it was tested,...

SOC 2 vs ISO 27001: What Carries Over and How to Do Both

SOC 2 vs ISO 27001: What Carries Over and How to Do Both

SOC 2 is an attestation report a licensed CPA firm issues against the AICPA's Trust Services Criteria. The report describes whether a service...

SOC 2 Compliance Automation: What Platforms Do and Don't Cover

SOC 2 Compliance Automation: What Platforms Do and Don't Cover

Achieving SOC 2 compliance is a major milestone for SaaS companies and service providers handling sensitive customer data. Yet, for many startups and...

ISO 42001 vs ISO 27001: What's Different and When You Need Both

ISO 42001 vs ISO 27001: What's Different and When You Need Both

ISO 27001 protects information through an Information Security Management System (ISMS). ISO 42001 governs AI systems through an Artificial...
