Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

Posts tagged TPRM

6 posts

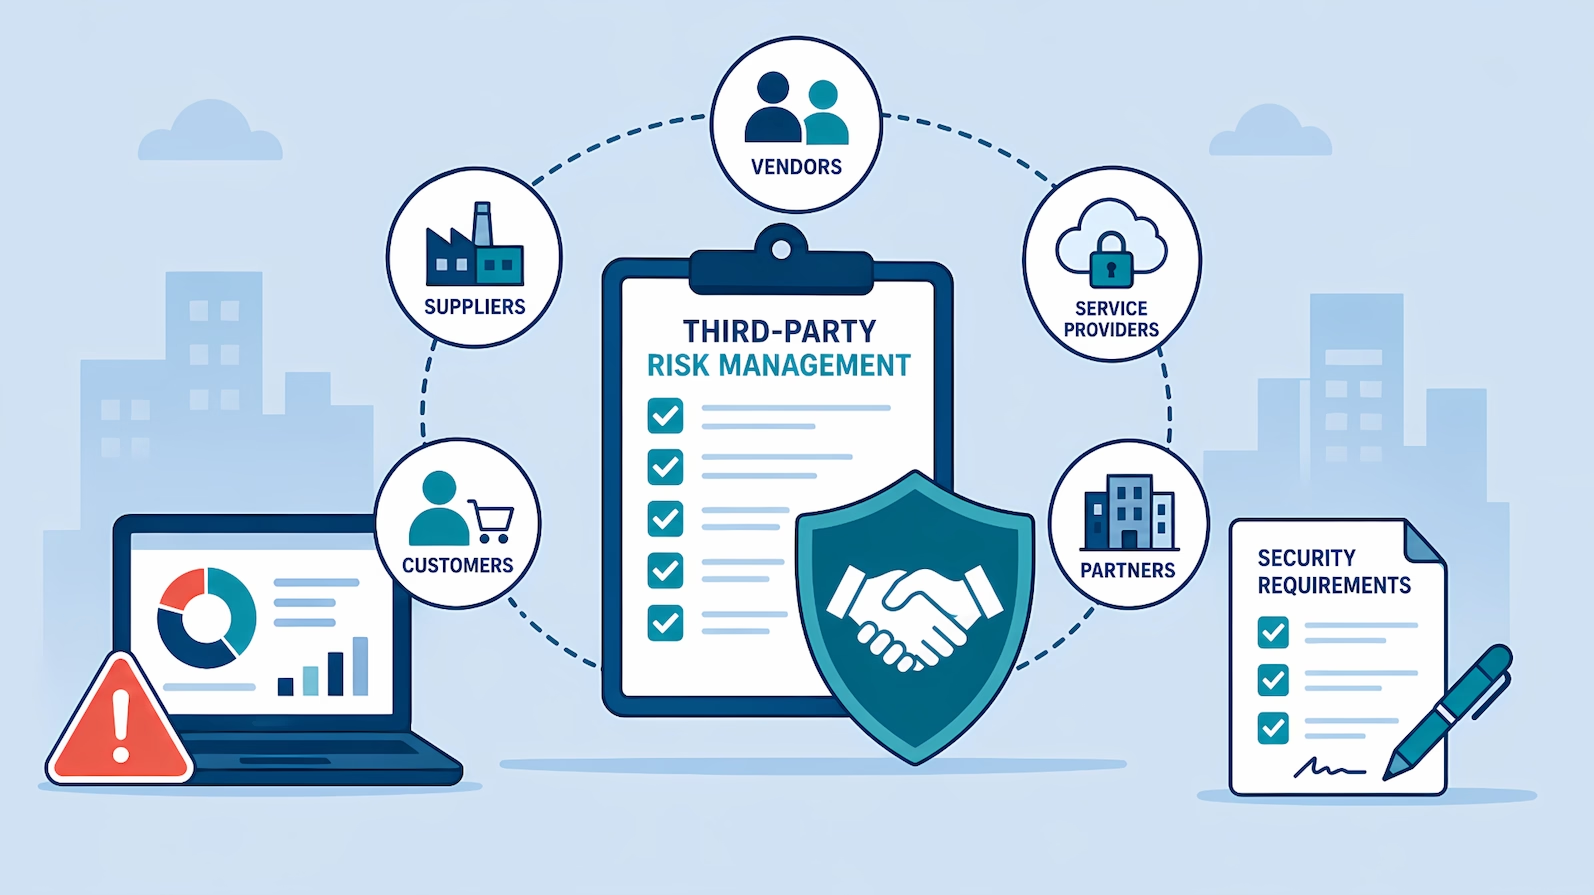
Third Party Risk Management (TPRM): What It Is and How to Build a Program

Third party risk management (TPRM) is the discipline of identifying, assessing, and controlling the risks that come from the external organizations a ...

Filter by Tag
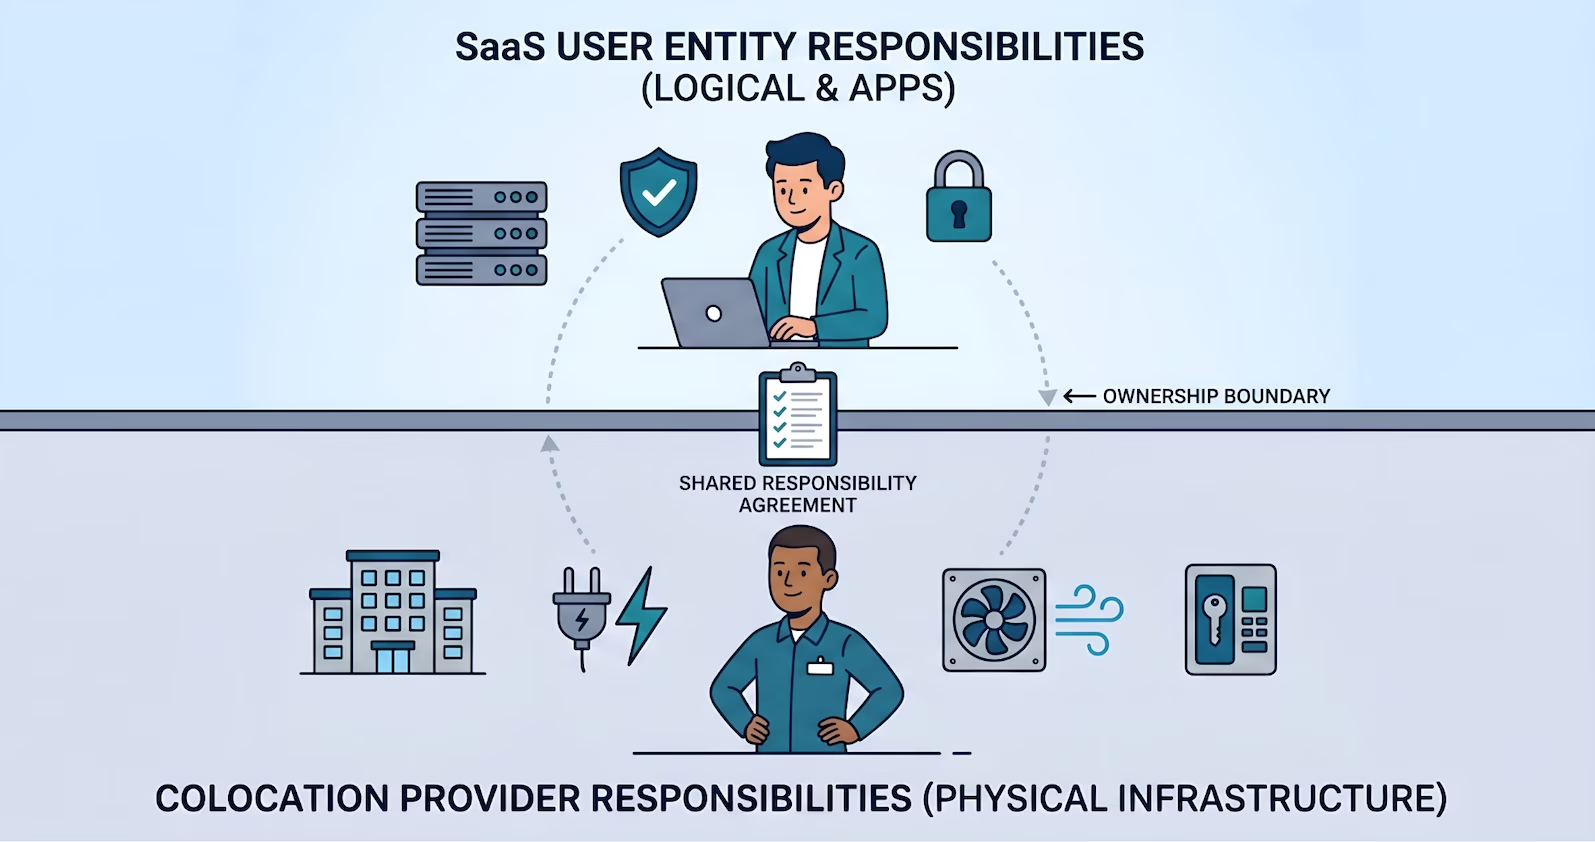
A flat 2D illustration showing a horizontal dividing line labeled "OWNERSHIP BOUNDARY". Above, a person with a laptop manages "SaaS USER ENTITY RESPONSIBILITIES," including logical and app controls. Below, a person stands by icons for a building, power, and cooling for "COLOCATION PROVIDER RESPONSIBILITIES." A document links the two.

SOC 2 Vendor Management: Data Center as Subservice

TL;DR

  • When your data center is operated by another organization (a colocation or hosting provider), that organization is a subservice organization...
Supply Chain Cyber Risk: Why Your Vendors' Security Is Your Problem

Supply Chain Cyber Risk: Why Your Vendors' Security Is Your Problem

Supply chain cyber risk has become one of the most pressing cybersecurity challenges for businesses of all sizes. A single compromise in a supplier’s...

ISO 27001 and SOC 2: How They Work Together

ISO 27001 and SOC 2: How They Work Together

ISO 27001 and SOC 2 are complementary, not competing. ISO 27001 certifies that an organization runs a documented, risk-based information security...

AI Governance in GRC: How ISO 42001 Fits Into Your Compliance Program

AI Governance in GRC: How ISO 42001 Fits Into Your Compliance Program

As artificial intelligence (AI) rapidly embeds itself into core business processes, from customer support to code generation, enterprises face a...

SOC 2 Trust Service Criteria Guide

AICPA SOC 2 Trust Services Criteria Explained: CC1 to CC9 (2026)

The SOC 2 Trust Services Criteria (TSC) are the control requirements the AICPA defines for a SOC 2 audit. They are organized into the Common Criteria...