
Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

Truvo Cyber blog hero — ISO 27001 Internal Audit Consulting in Canada: scope, timeline, and what an external audit engagement covers.

ISO 27001 Internal Audit Consulting in Canada

Most Canadian organizations preparing for ISO 27001 certification have the same question at the internal audit stage: who should run this, and what...
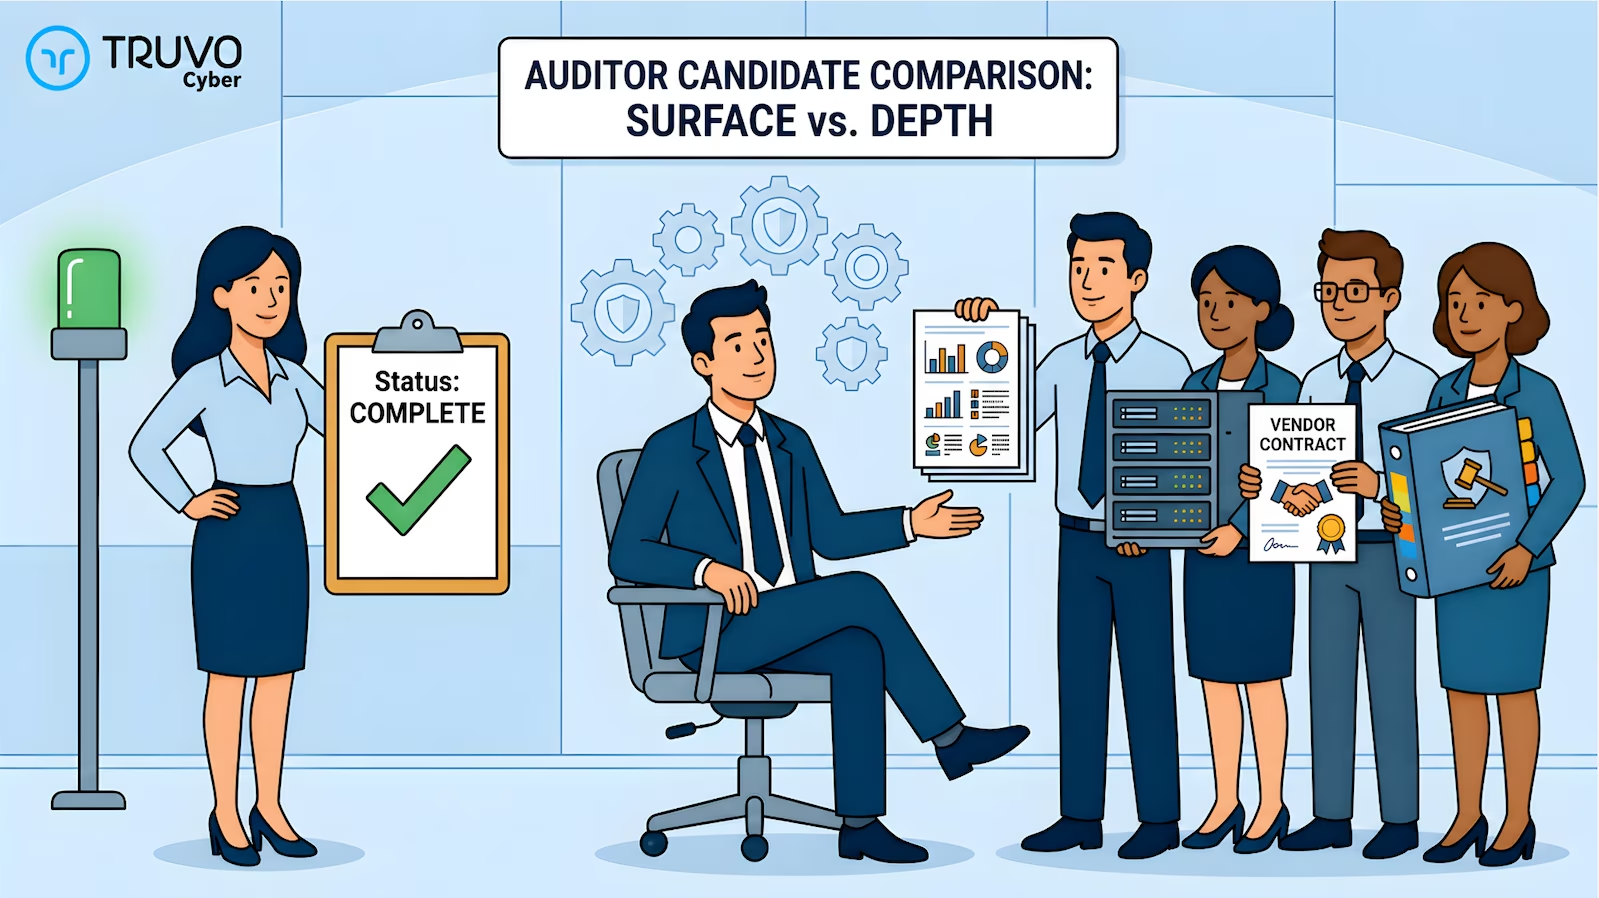
Illustration titled "AUDITOR CANDIDATE COMPARISON: SURFACE vs. DEPTH". A hiring manager looks towards a team presenting specialized controls: a server rack, vendor contract, and comprehensive binder. On the left, a single candidate holds a simple "Status: COMPLETE" clipboard with a green checkmark, near a green light.

What to Look for in an ISO 27001 Internal Auditor

When you are preparing for ISO 27001 certification, the internal audit is not a formality. It is the last structured opportunity to identify gaps...
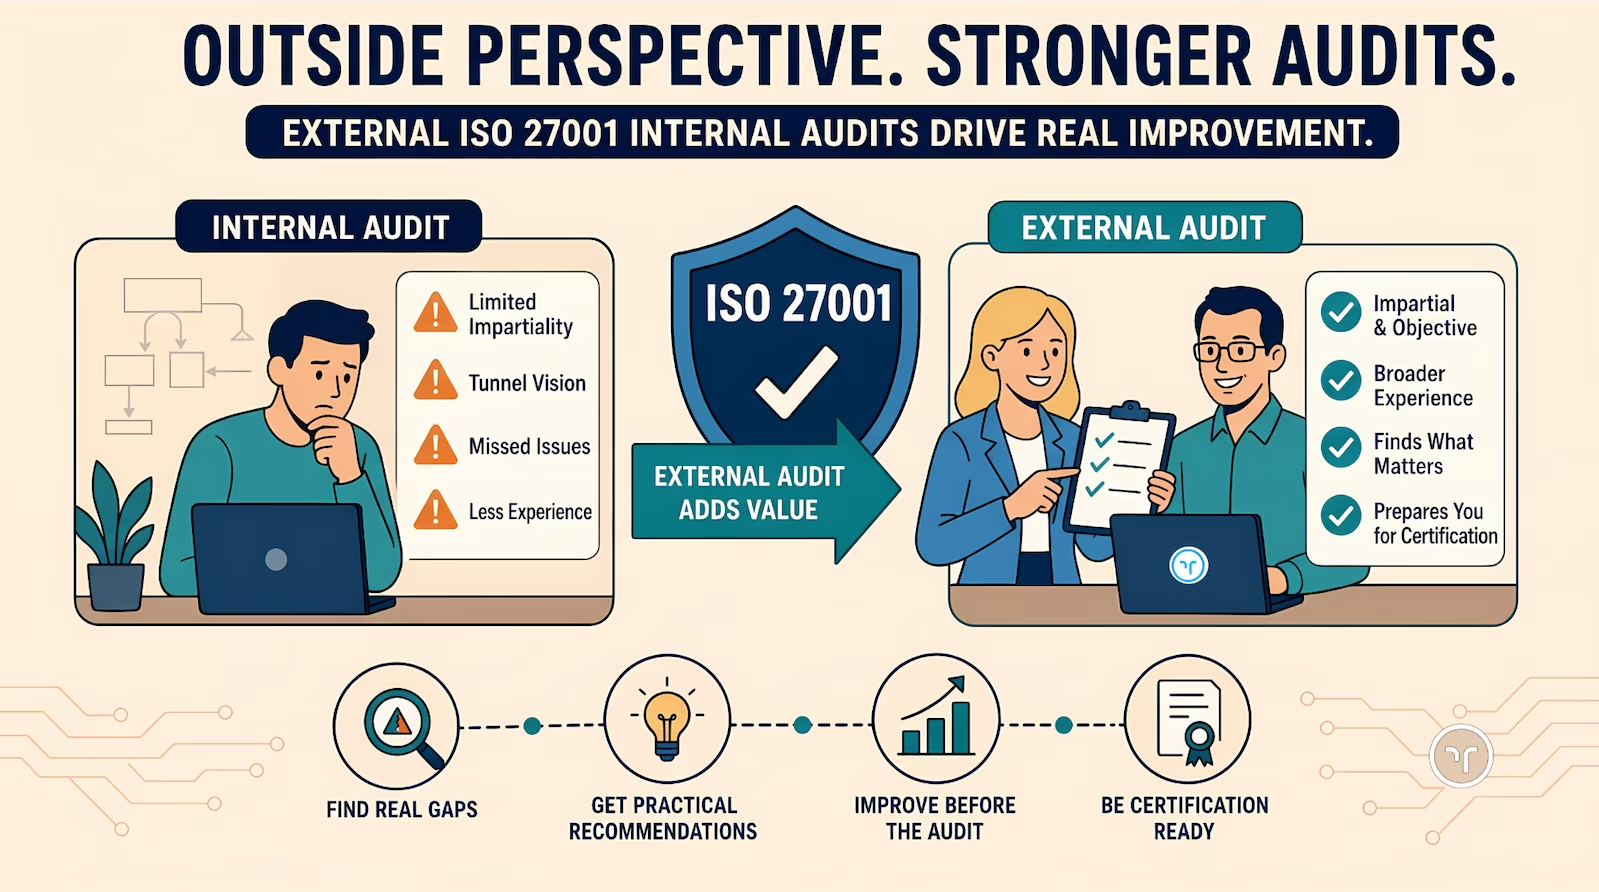
Truvo Cyber blog hero — Outsourcing Your ISO 27001 Internal Audit: when it makes sense and what to expect from an external engagement.

Outsourcing Your ISO 27001 Internal Audit: When It Makes Sense

Short answer: yes, you can outsource the ISO 27001 internal audit, and you don't need an internal audit team to do so. Clause 9.2 asks for an auditor...

ISO 42001 Software Costs: What to Budget for Certification

ISO 42001 Software Costs: What to Budget for Certification

The Cost of AI Governance: Benchmarking Investment in ISO 42001 Compliance Software

Implementing ISO/IEC 42001 is a strategic necessity for AI SaaS...

Web Summit Vancouver: Gary Marcus on AI Limitations and Risks

Web Summit Vancouver: Gary Marcus on AI Limitations and Risks

Key Takeaways from the Web Summit Keynote: A Reality Check on the AI Hype

AI dominated the conversation at this 2025's Web Summit, and for good...

NRC IRAP Funding for SOC 2 Compliance in Canada

NRC IRAP Funding for SOC 2 Compliance in Canada

Yes. NRC IRAP has funded SOC 2 and ISO 27001 projects for Canadian companies: public federal grant records show IRAP contributions of $40,000 to...

ISO 42001 vs ISO 27001: What's Different and When You Need Both

ISO 42001 vs ISO 27001: What's Different and When You Need Both

ISO 27001 protects information through an Information Security Management System (ISMS). ISO 42001 governs AI systems through an Artificial...

ISO 42001 Compliance Software: 2026 Platform Review

ISO 42001 Compliance Software: 2026 Platform Review

The Platforms Compared

Vanta, Drata, Secureframe, and Scrut have all added dedicated ISO 42001 framework support. All four automate evidence...

Drata vs Vanta for ISO 42001 (2026 Comparison)

Drata vs Vanta for ISO 42001 (2026 Comparison)

How They Compare

Both Drata and Vanta offer dedicated ISO 42001 framework support with automated evidence collection, control cross-mapping to ISO...

SOC 2 Trust Services Criteria: All 33 Criteria Listed

SOC 2 Trust Services Criteria: All 33 Criteria Listed

The SOC 2 Trust Services Criteria (TSC) are the control requirements the AICPA sets for a SOC 2 audit. Older guides call them the SOC 2 trust...