Effective Security & Compliance Insights

Get practical, no-fluff advice for building a security program that wins deals and reduces risk.

Want practical security templates, checklists, and expert tips delivered to your inbox?

An engineer points at code on a screen while a colleague types, reviewing an AI-written script during human-in-the-loop incident response

How to Use AI for Incident Response: Lessons Learned From a Real Engagement

We recently used frontier AI throughout an incident response engagement, from the first log query to the final incident report. This is how it went,...
Modern control room with people monitoring large digital displays and computer systems, illustrating Agentic AI Security Architecture: How to Let AI Agents Do Real Work Safely

Railway Security Incident (October 2026): What to Do, and What SOC 2, ISO 27001, GDPR and HIPAA Require

On October 21, 2026, Railway disclosed that an unauthorized third party may have accessed the encrypted environment variables of its customers and,...
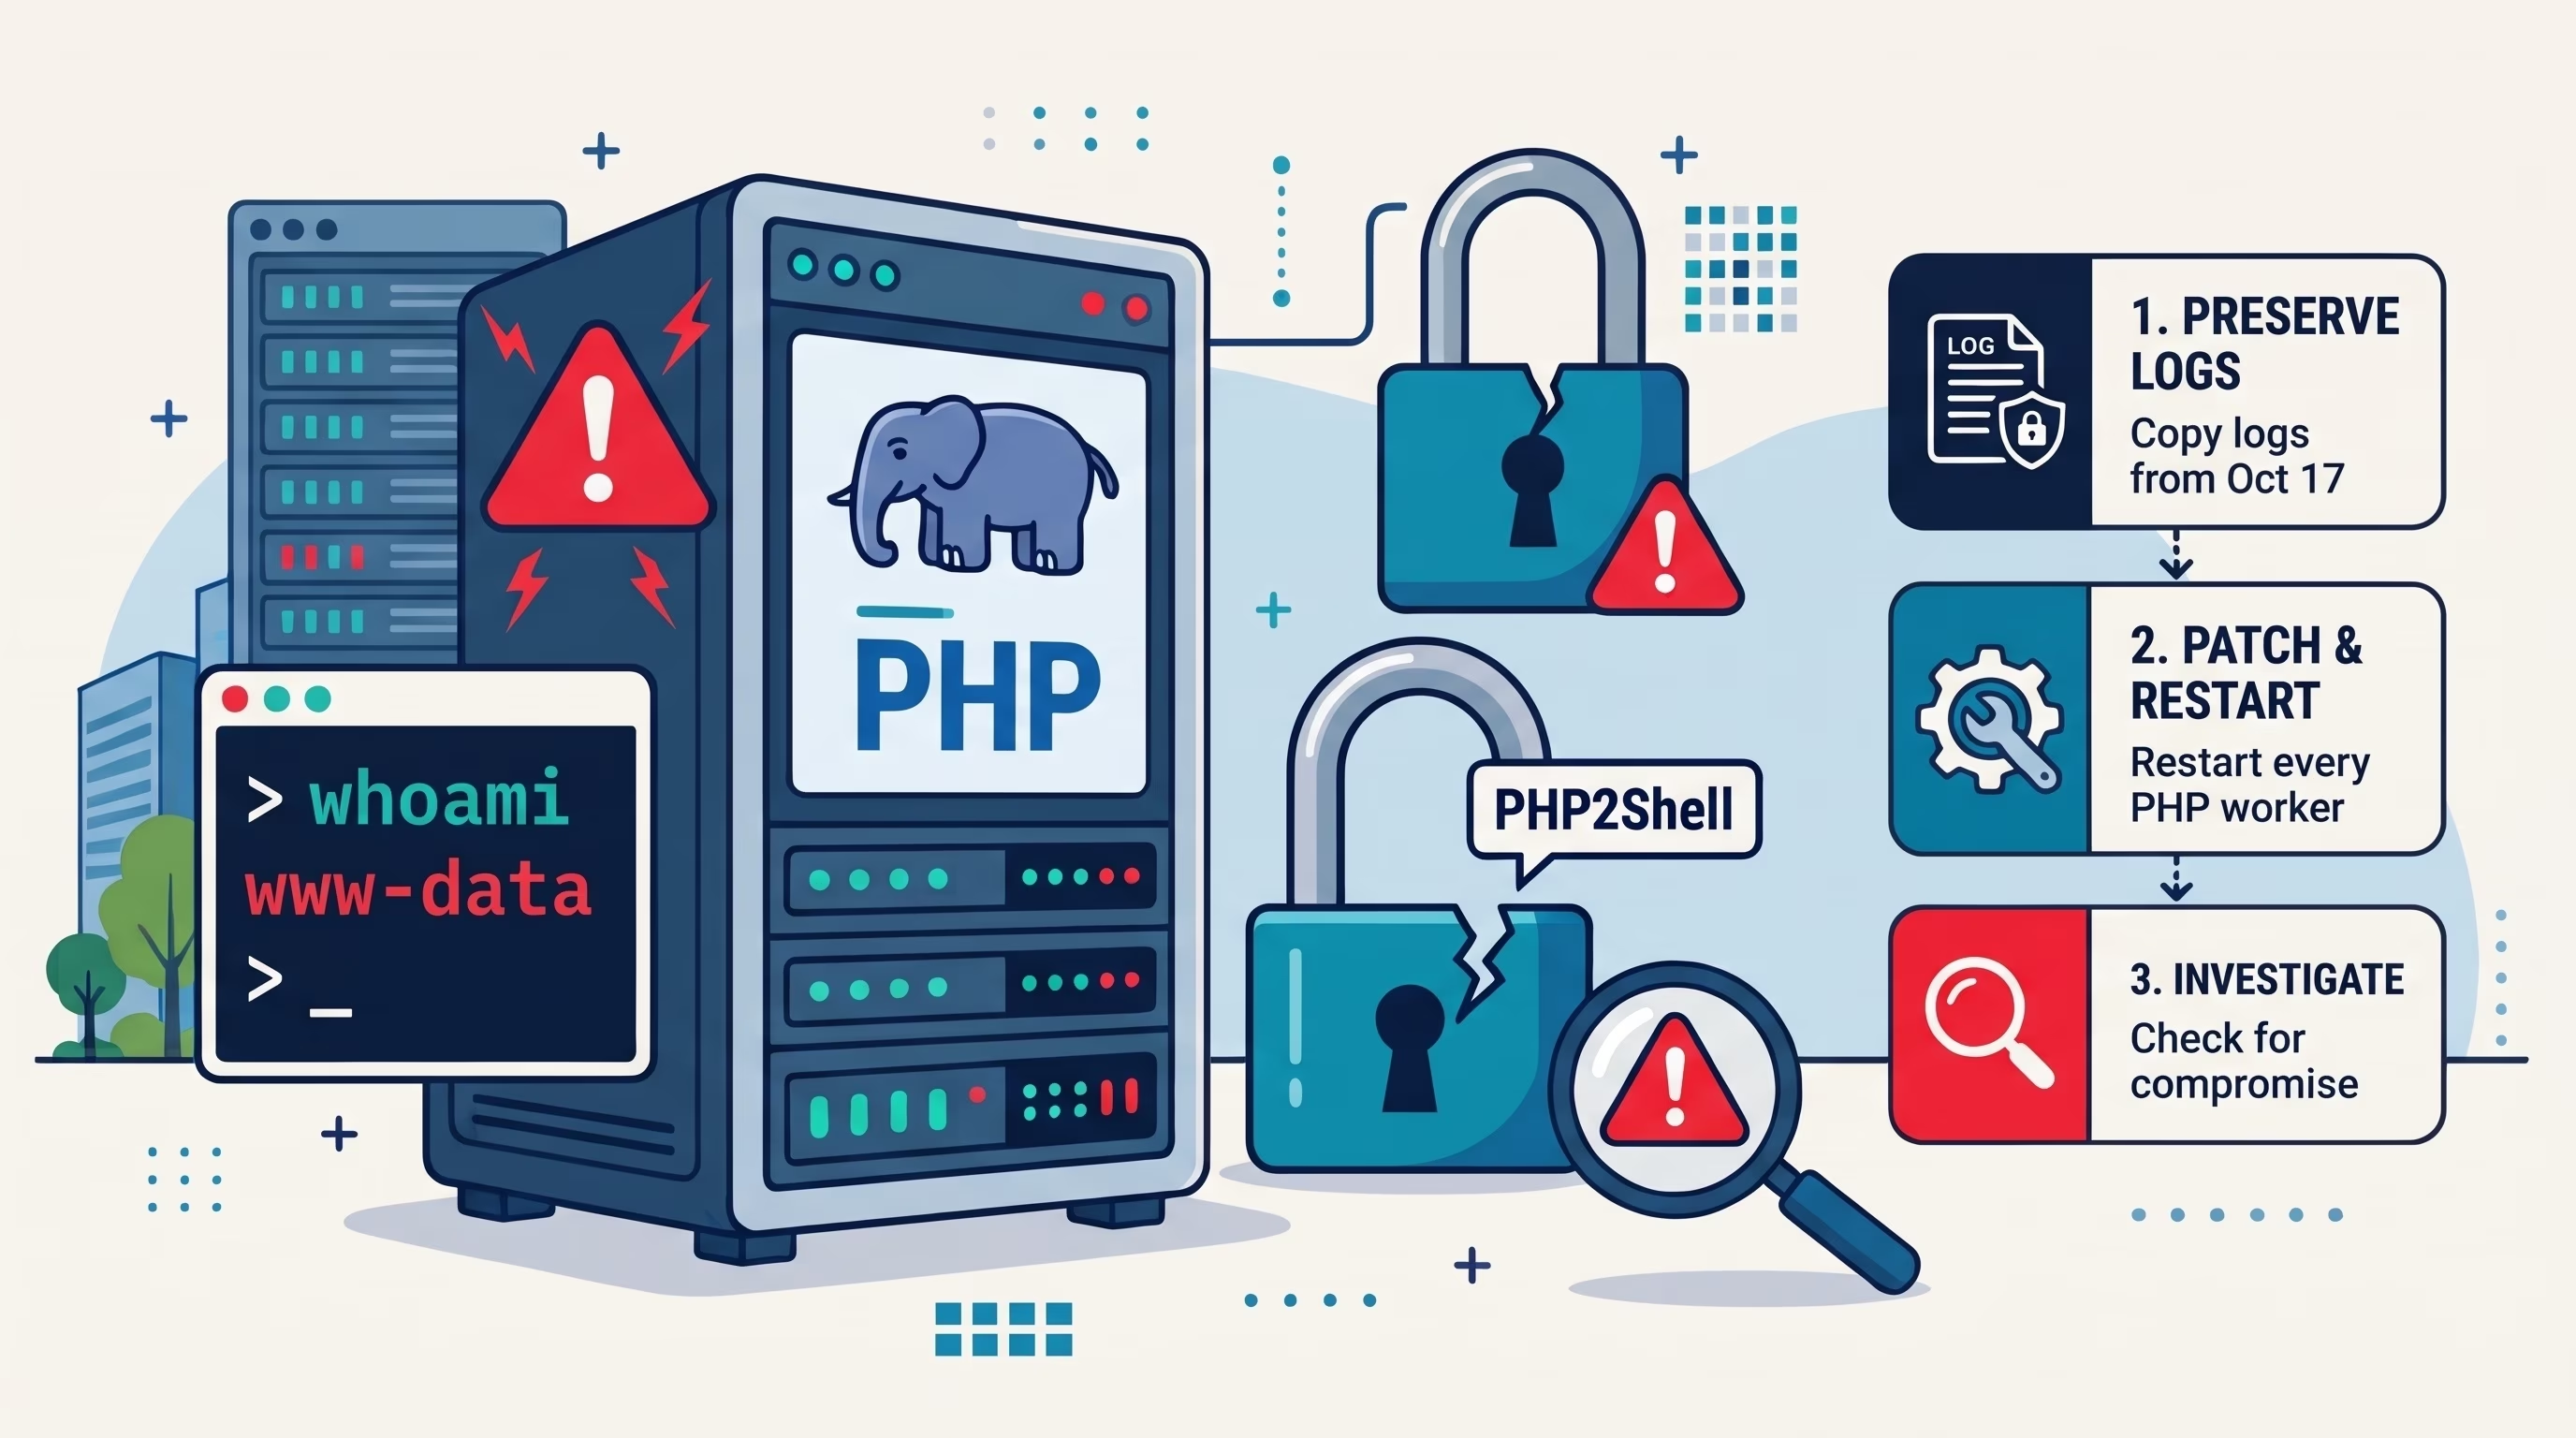
Illustration of the PHP2Shell vulnerability response. A compromised PHP server and broken padlocks are shown alongside three action steps: 1. Preserve Logs (Copy logs from Oct 17), 2. Patch & Restart (Restart every PHP worker), and 3. Investigate (Check for compromise).

PHP2Shell (CVE-2026-109618, CVE-2026-109619): What to Do, and When It Becomes an Incident

PHP2Shell is two critical flaws in the PHP engine, CVE-2026-109618 and CVE-2026-109619, that allow remote code execution without a login on PHP web...
Stock photo by panumas nikhomkhai via Pexels, illustrating server room red lights emergency (temporary placeholder pending custom hero design).

ISO 27001 A.5.24: Information Security Incident Management Planning and Preparation

ISO 27001 A.5.24 requires an organization to plan and prepare for security incidents before they happen: define the roles, the response process, the...
Stock photo by panumas nikhomkhai via Pexels, illustrating data center disaster recovery (temporary placeholder pending custom hero design).

SOC 2 CC7.5: Recovering From Identified Security Incidents

SOC 2 CC7.5 requires a company to identify, develop, and implement the activities that recover the environment after a security incident, and to...
Stock photo by Markus Winkler via Pexels, illustrating cybersecurity incident response team (temporary placeholder pending custom hero design).

SOC 2 CC7.4: Responding to Security Incidents

SOC 2 CC7.4 requires a company to respond to security incidents through a defined incident-response program that understands, contains, remediates,...
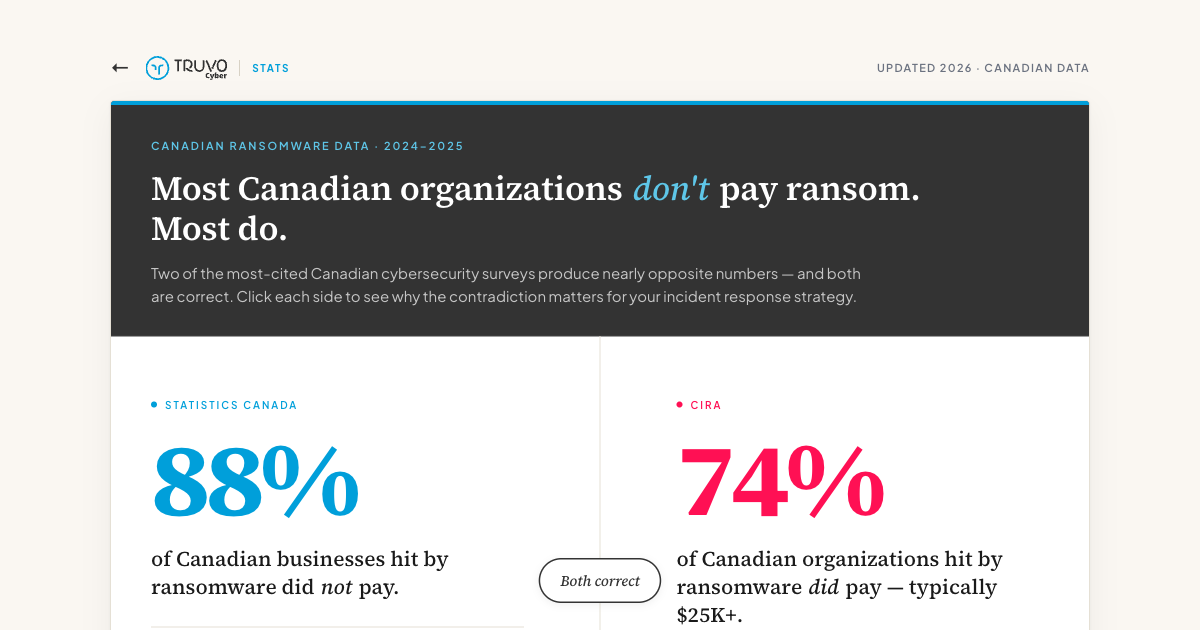
The Canadian Ransomware Paradox: Statistics Canada reports 88 percent of victims don't pay, CIRA reports 74 percent do, both surveys correct. Truvo Cyber.

The Canadian Ransomware Paradox: Why Two Surveys Disagree on Payment

Two of the most-cited Canadian ransomware statistics flatly contradict each other.

Statistics Canada, reporting on 2023 data released in October...
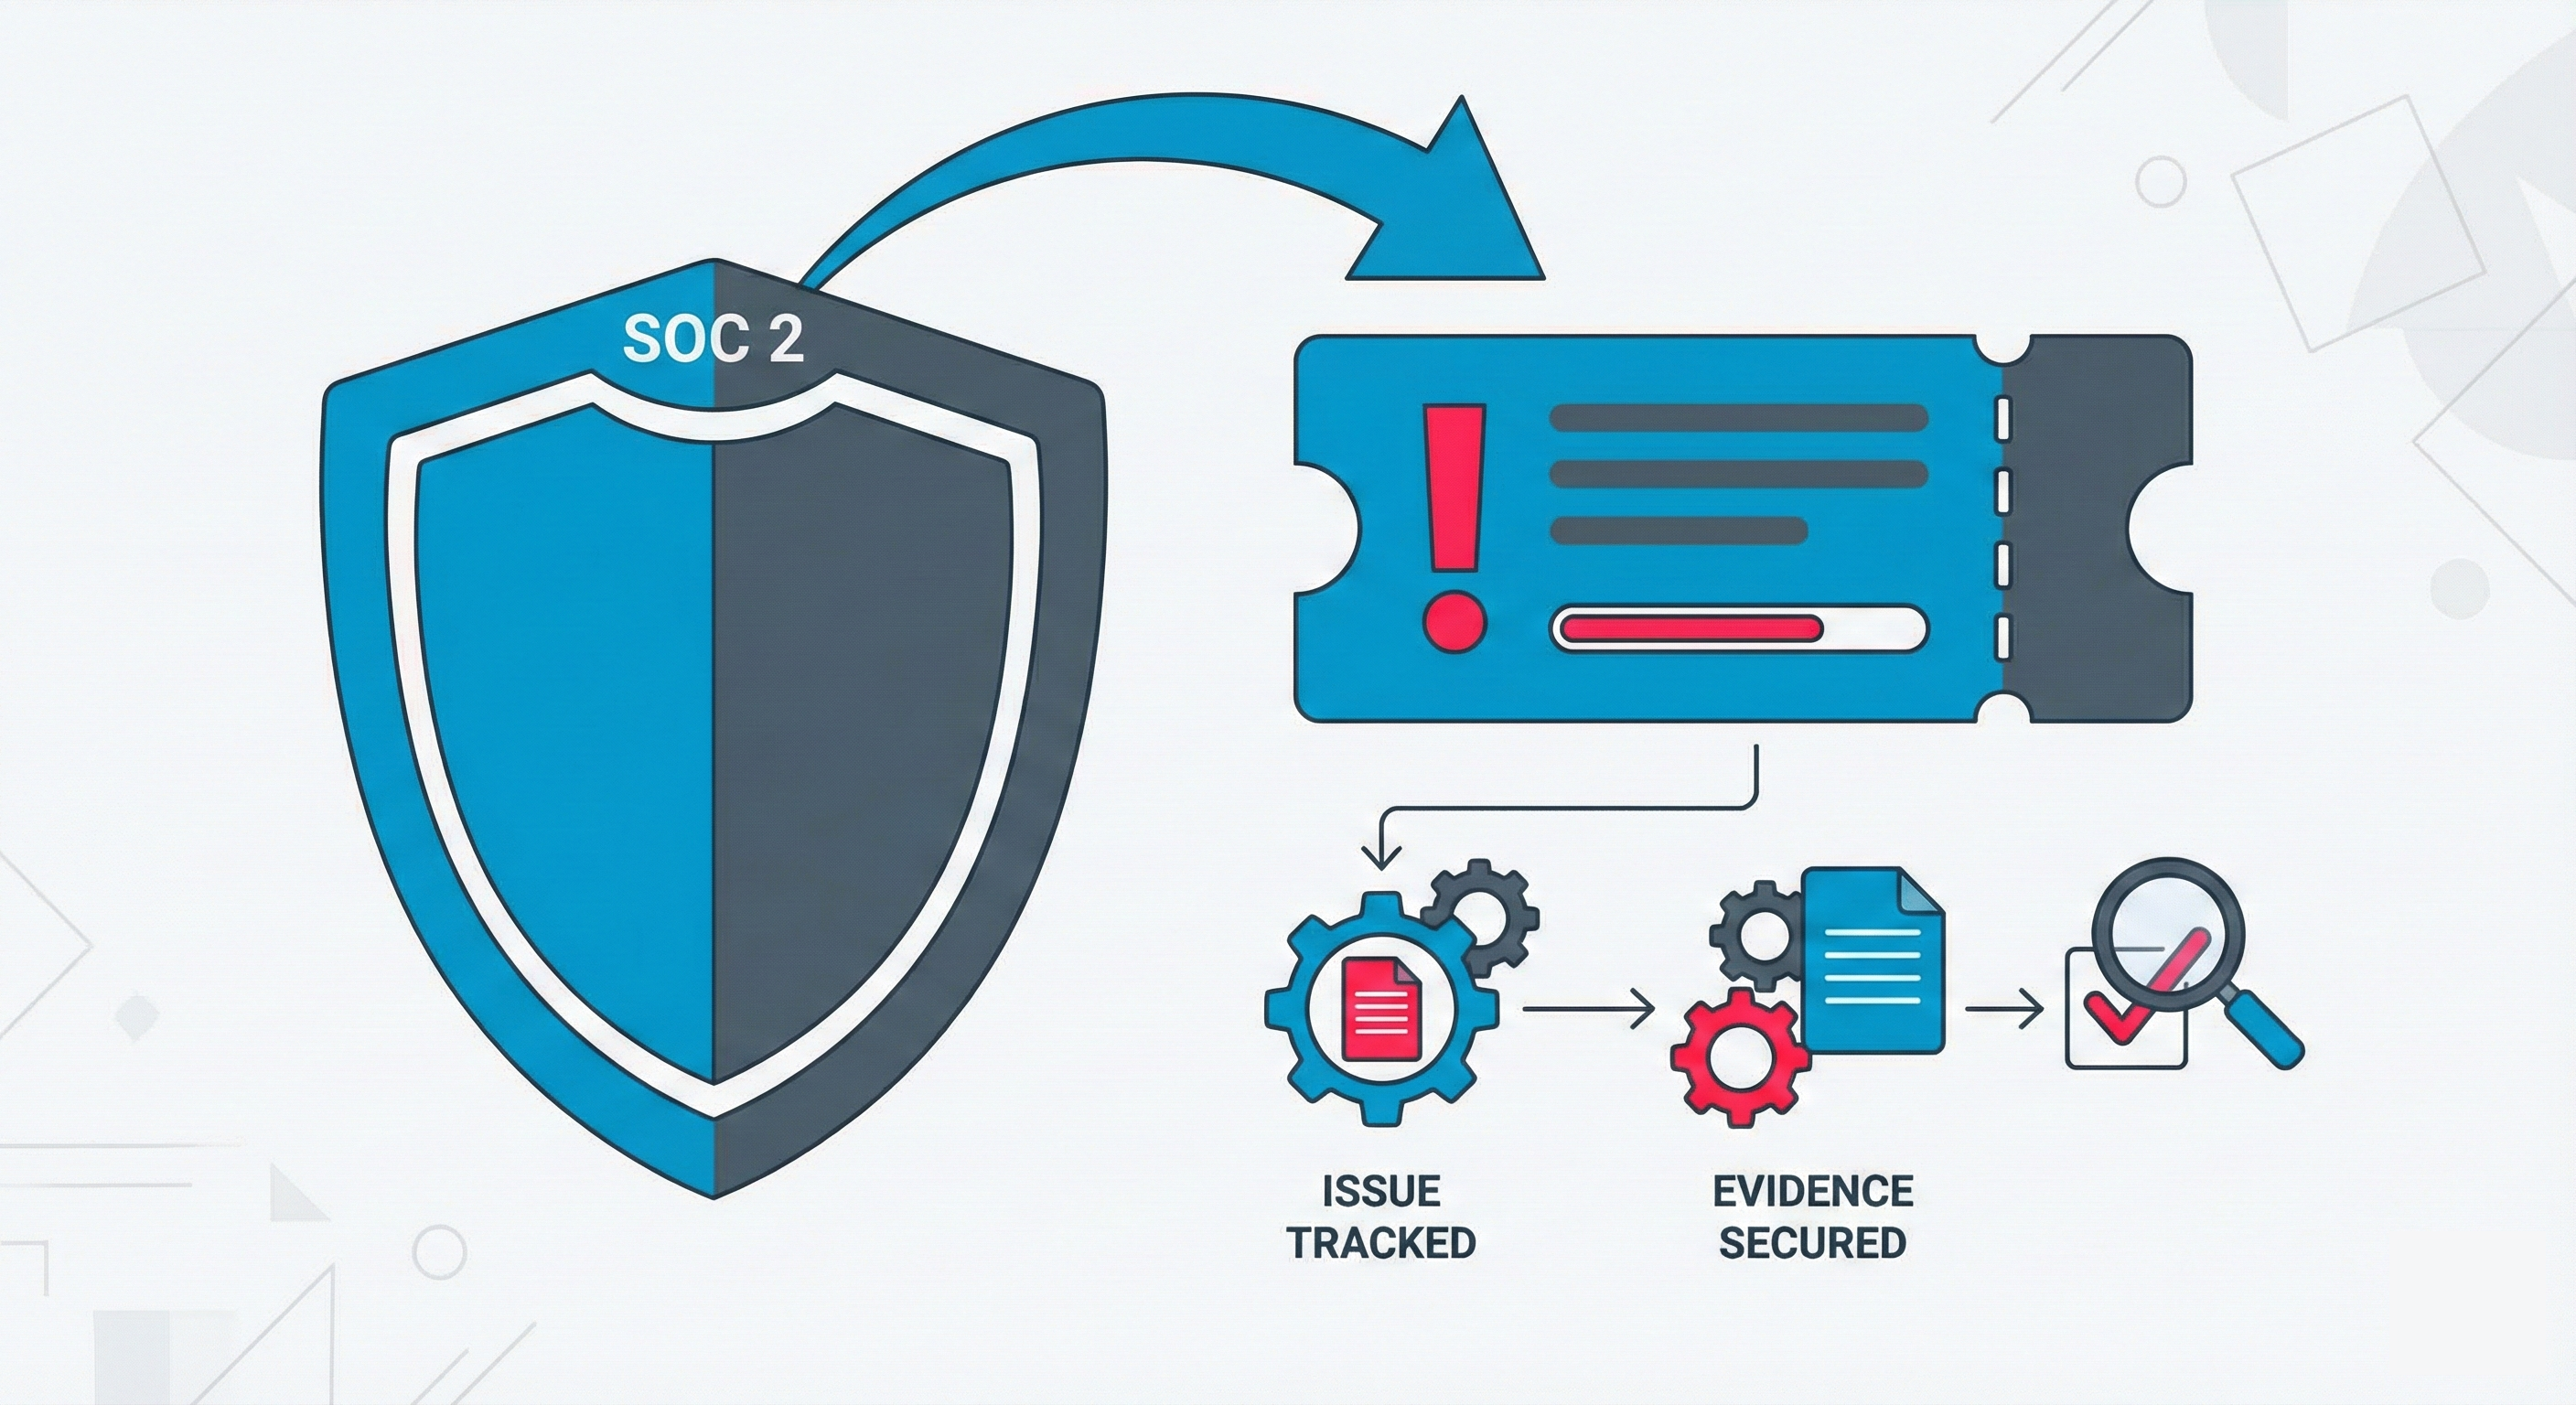
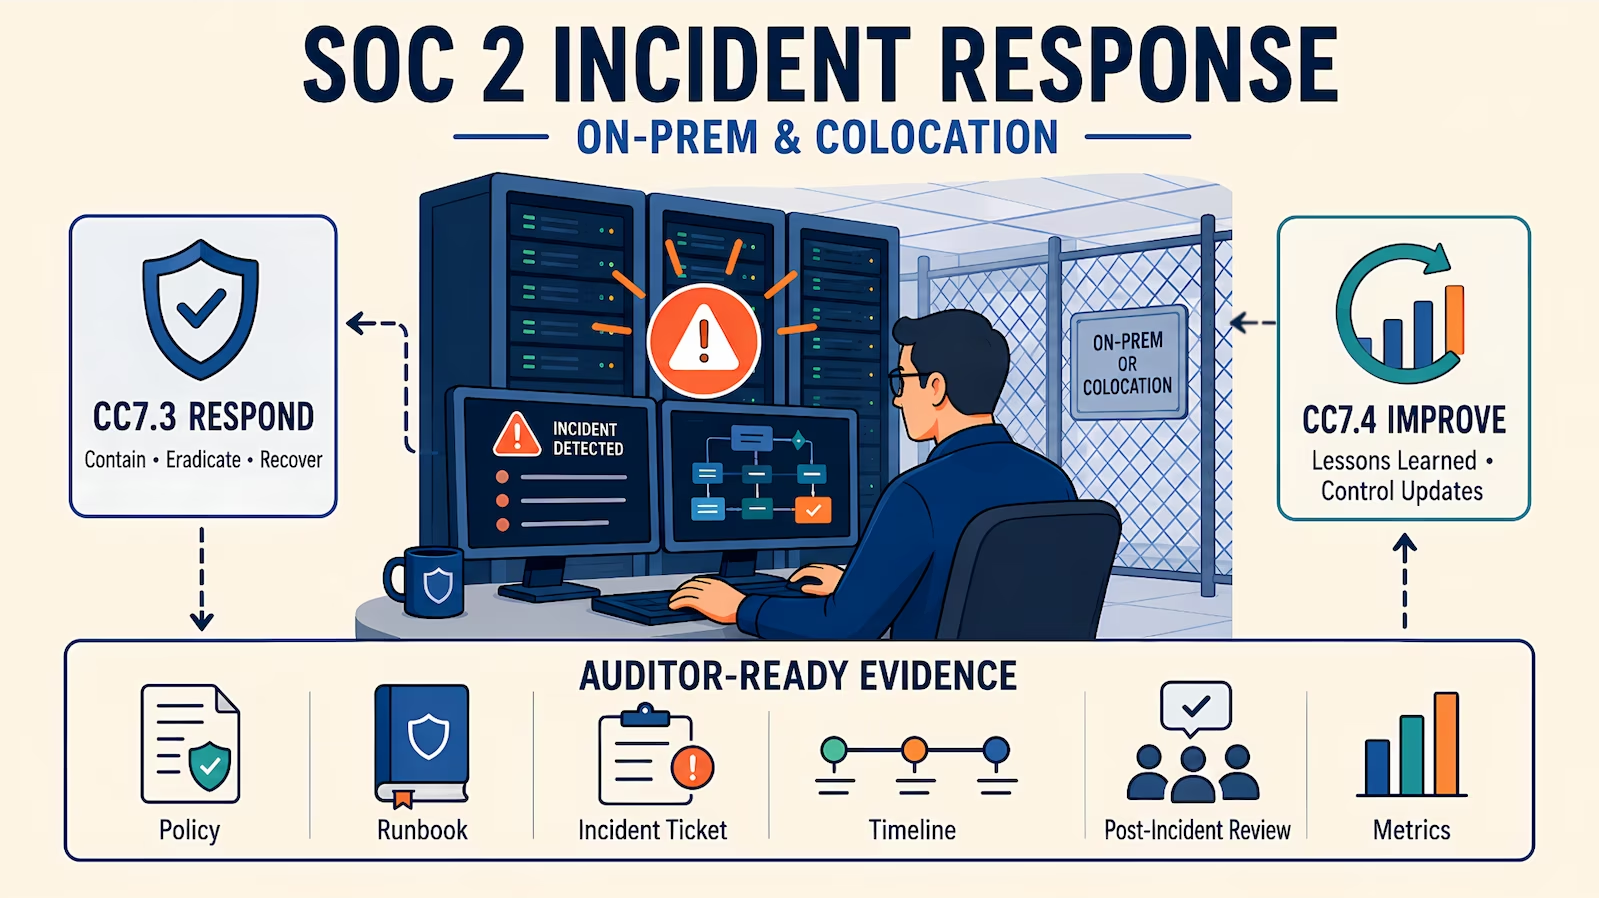
SOC 2 Incident Response for On-Premise Environments — Truvo blog hero

SOC 2 Incident Response for On-Premise Environments

TL;DR

  • IR maps to CC7.3 (security event evaluation, the triage discipline) and CC7.4 (defined response program with containment, mitigation,...
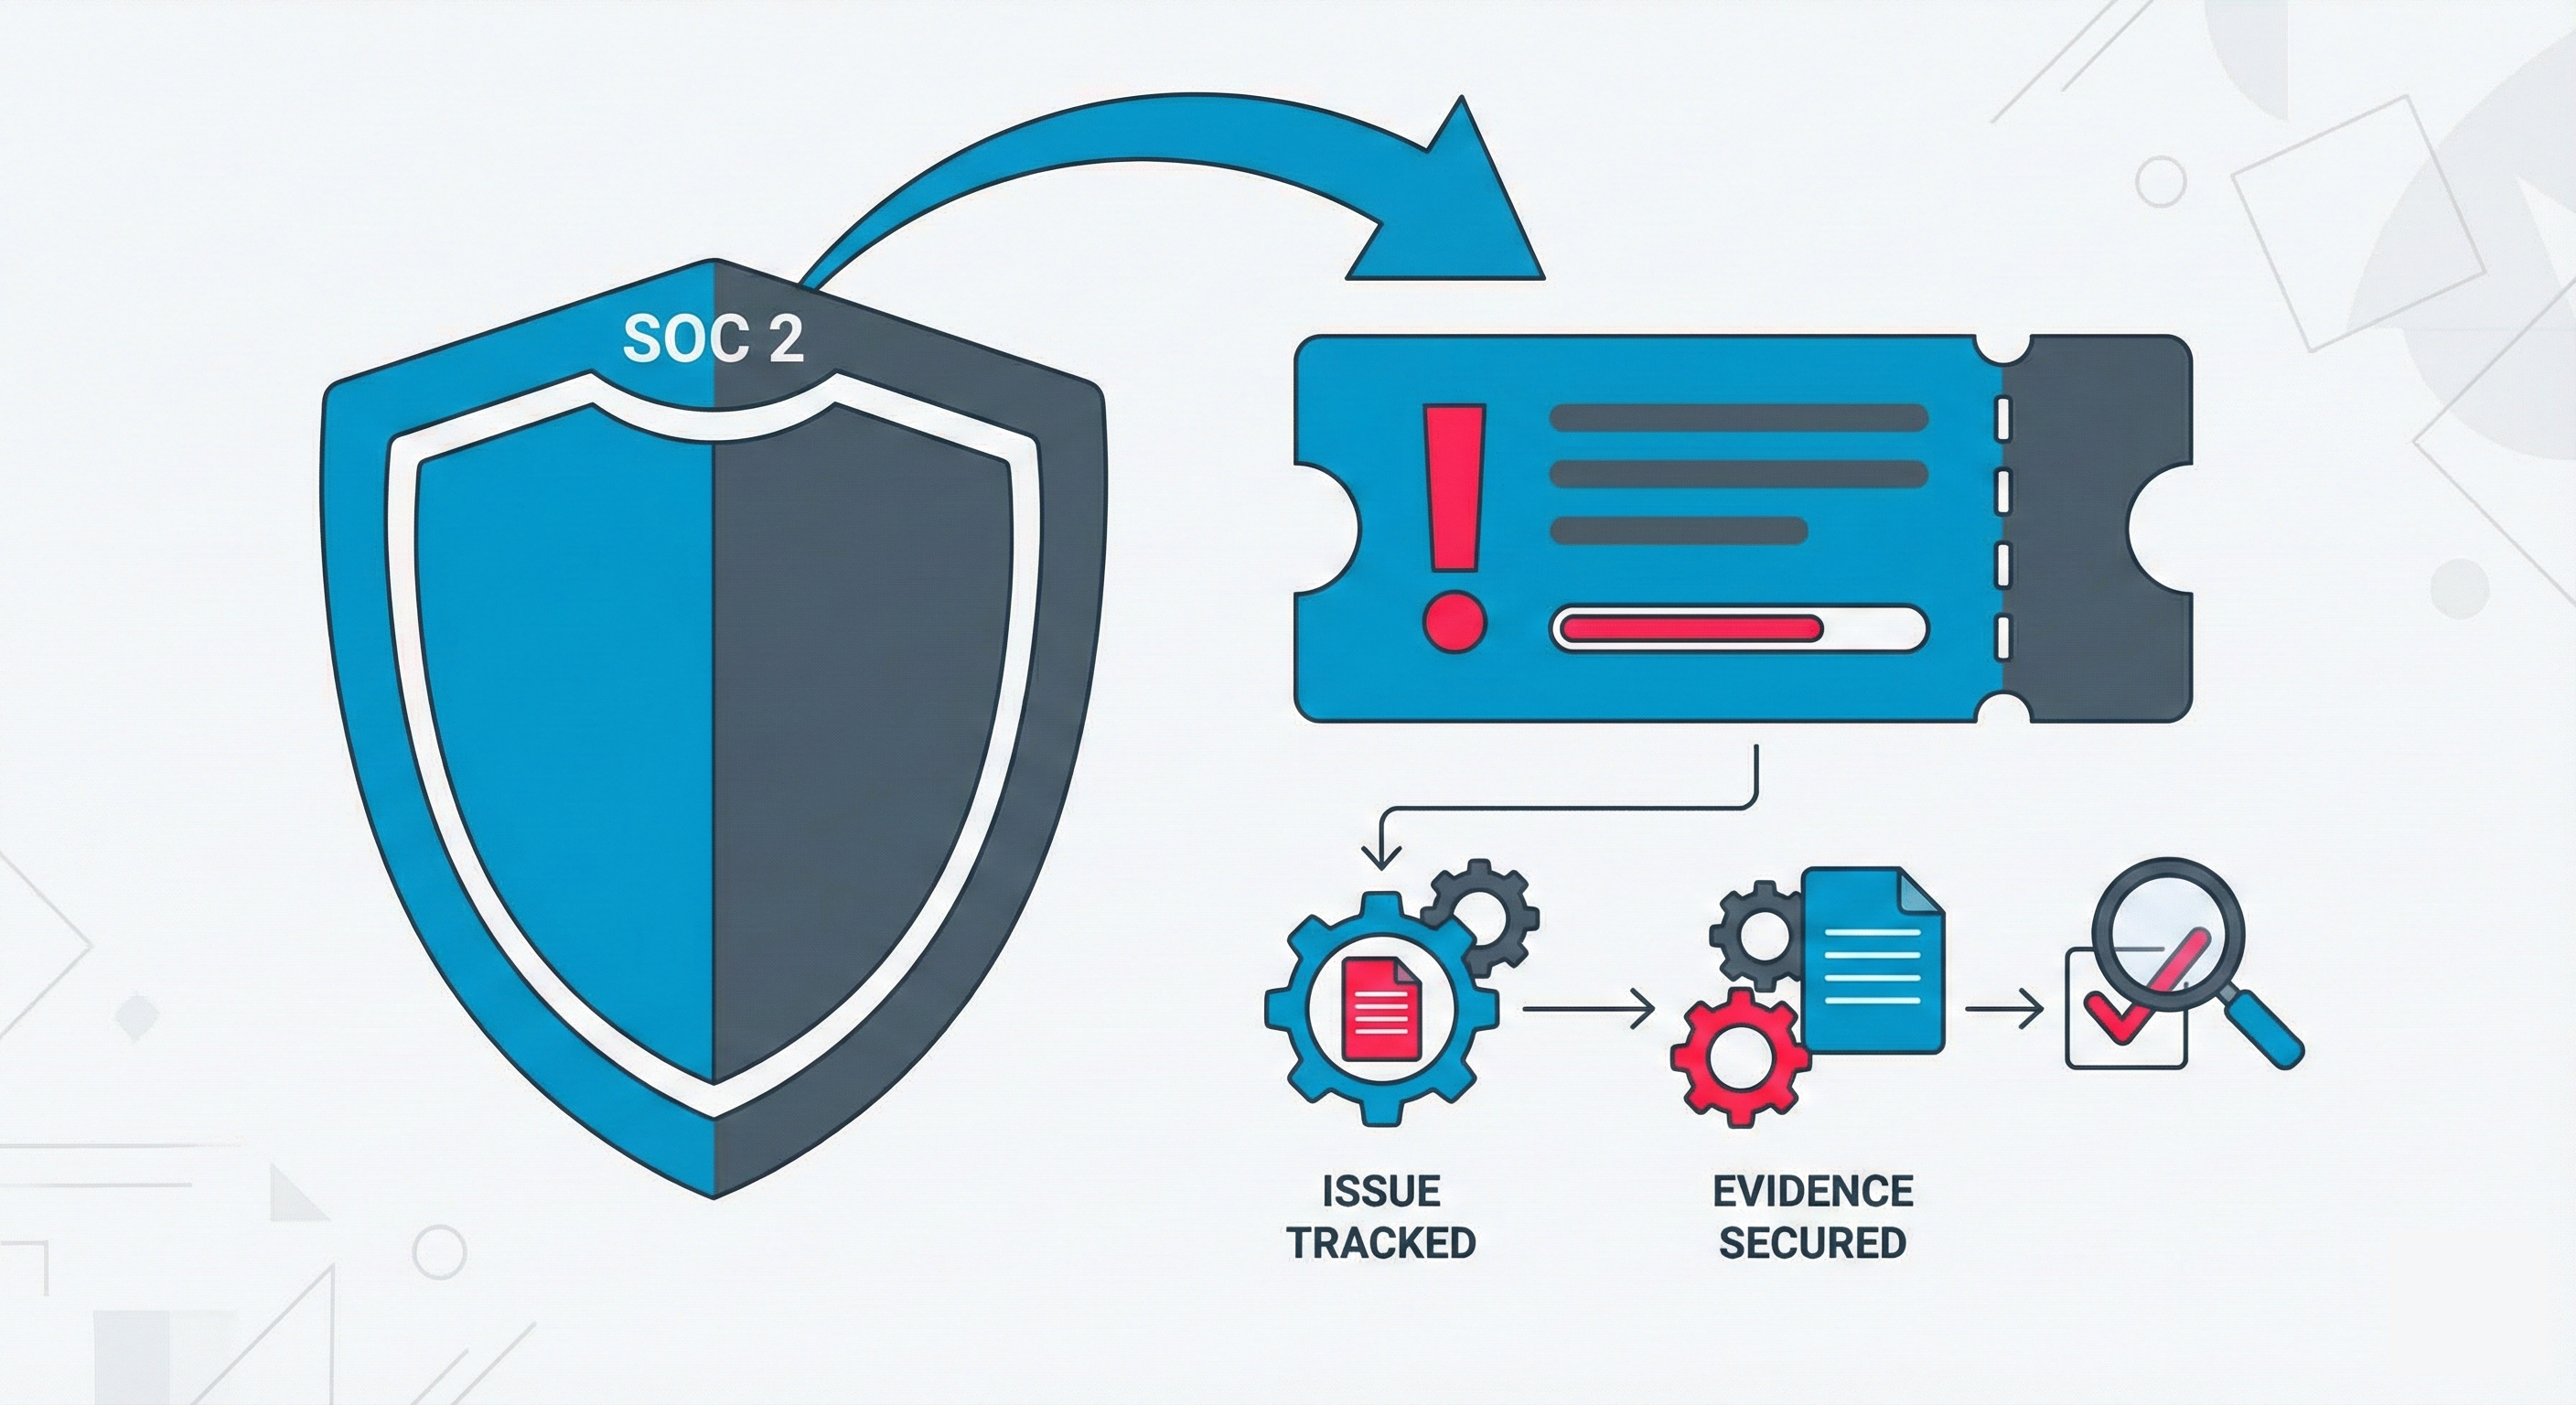
Featured image for SOC 2 SLA for vulnerability patching

SOC 2 Ticketing & SLAs: Vulnerability Patching & Incident Response

TL;DR: SOC 2 compliance requires a formal, trackable process for all security-relevant activities. Under the Trust Services Criteria, this means...